
pefile
 erocarrera/pefile
pefile is a Python module to read and work with PE (Portable Executable) files
binary-analysisforensicsmalware-analysis+3
erocarrera/pefilepefile is a Python module to read and work with PE (Portable Executable) files
 blackberry/pe_tree
Python module for viewing Portable Executable (PE) files in a tree-view using pefile and PyQt5. Can also be used with IDA Pro and Rekall to dump…
 pstirparo/machofile
machofile is a module to parse Mach-O binary files
 fuzzinglabs/octopus
Security Analysis tool for WebAssembly module (wasm) and Blockchain Smart Contracts (BTC/ETH/NEO/EOS)
 theopolis/uefi-firmware-parser
Parse BIOS/Intel ME/UEFI firmware related structures: Volumes, FileSystems, Files, etc
 trailofbits/trailmark
Build and query a graph database representation of source code
 kagancapar/cve-2021-47881
PoC and analysis of a local stack-buffer-overflow in dataSIMS Avionics ARINC 664-1 v4.5.3, with payload breakdown, reproduction script, and CVE…
 mattifestation/powershellarsenal
A PowerShell Module Dedicated to Reverse Engineering
 theflink/hunt-sleeping-beacons
Callstack scanner that identifies IOCs of unpacked or injected C2 agents by analyzing thread idle behavior, unbacked memory, module stomping, APCs,…
 dsecurity/efiseek
Ghidra plugin that automates UEFI firmware analysis by identifying known GUIDs, protocols, SMI handlers, and interrupt functions, with headless…
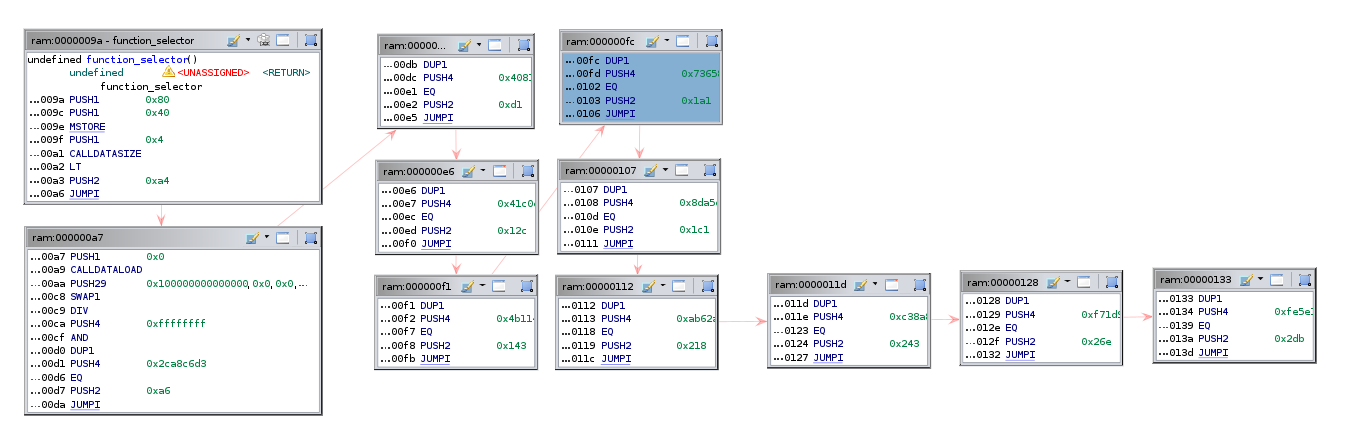 adelapie/ghidra-evm
Ghidra module for disassembling, decompiling, and analyzing Ethereum smart contract bytecode. Detects insecure instructions, extracts hidden methods,…
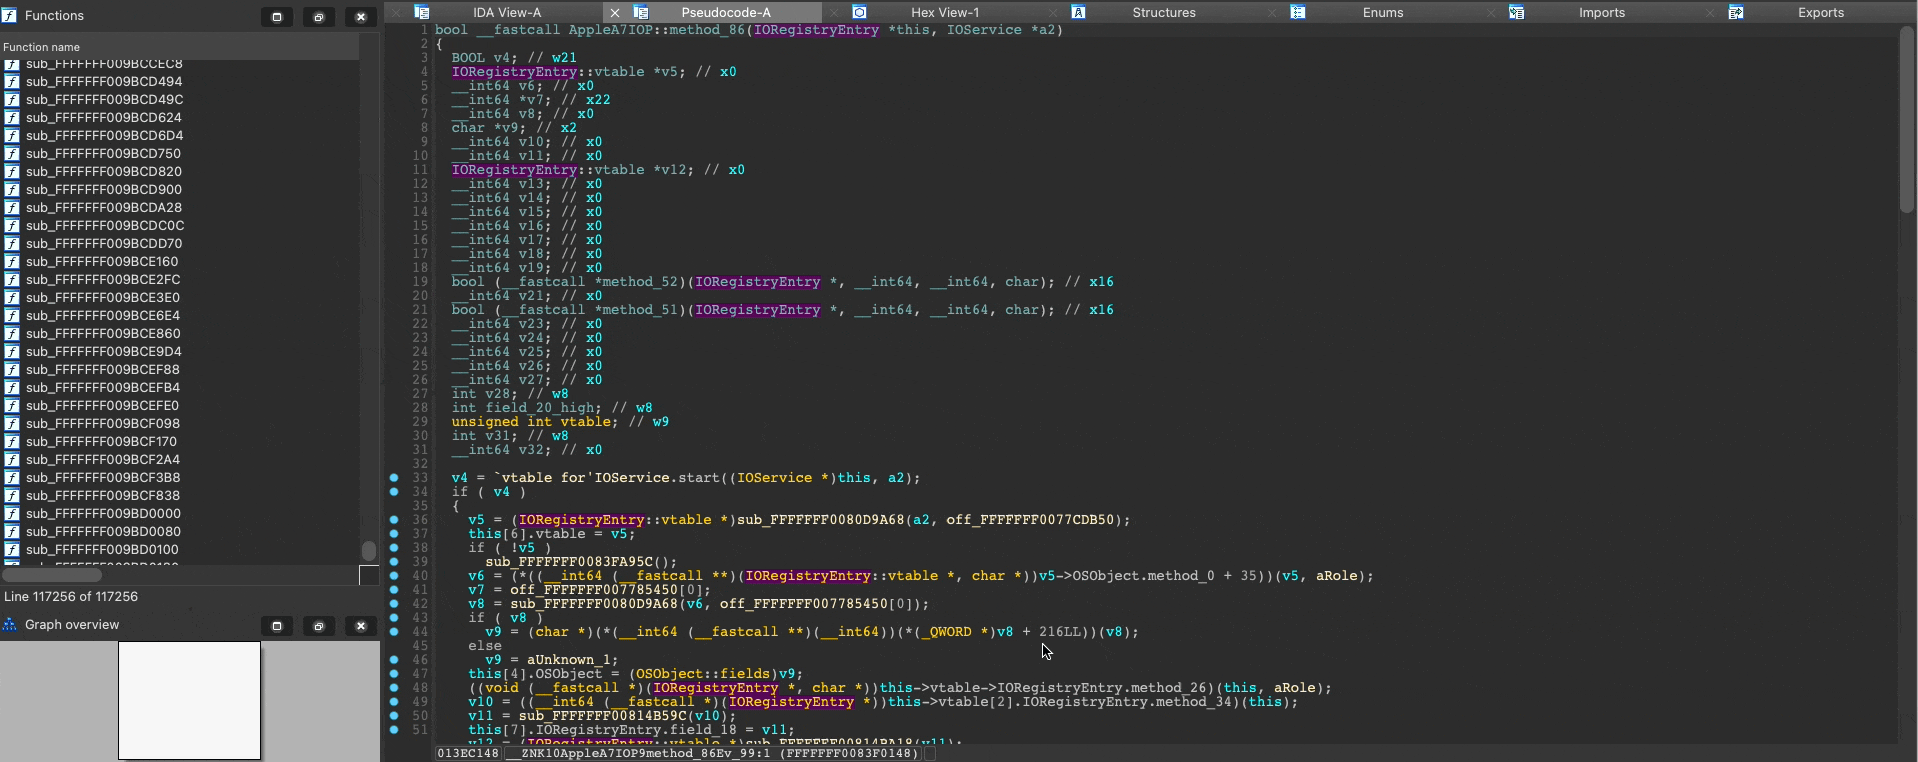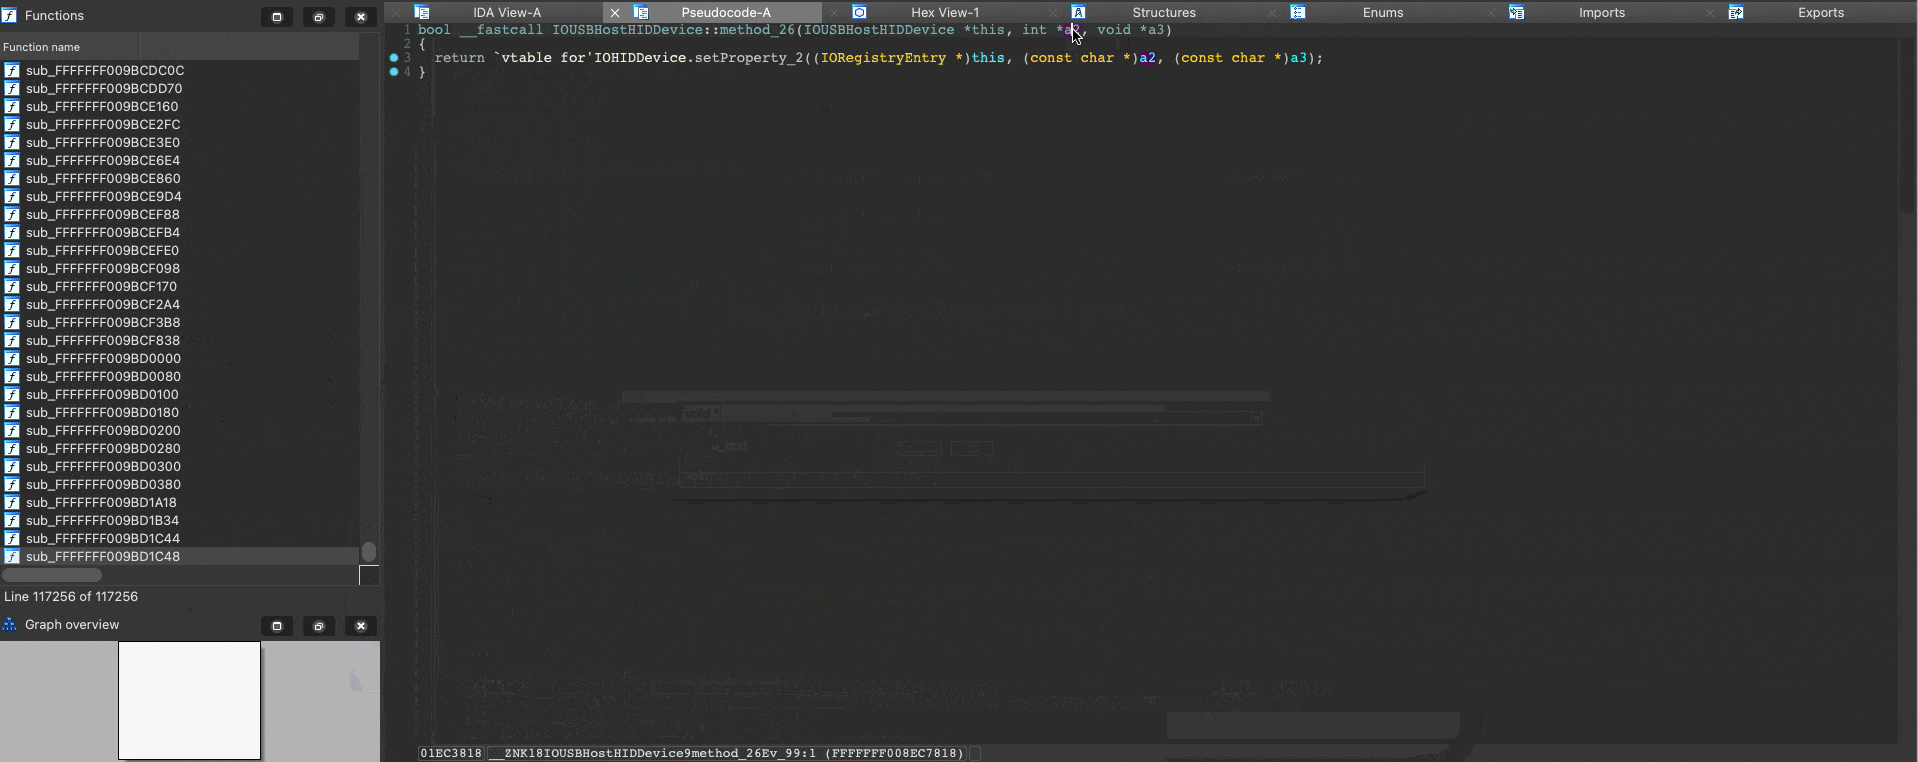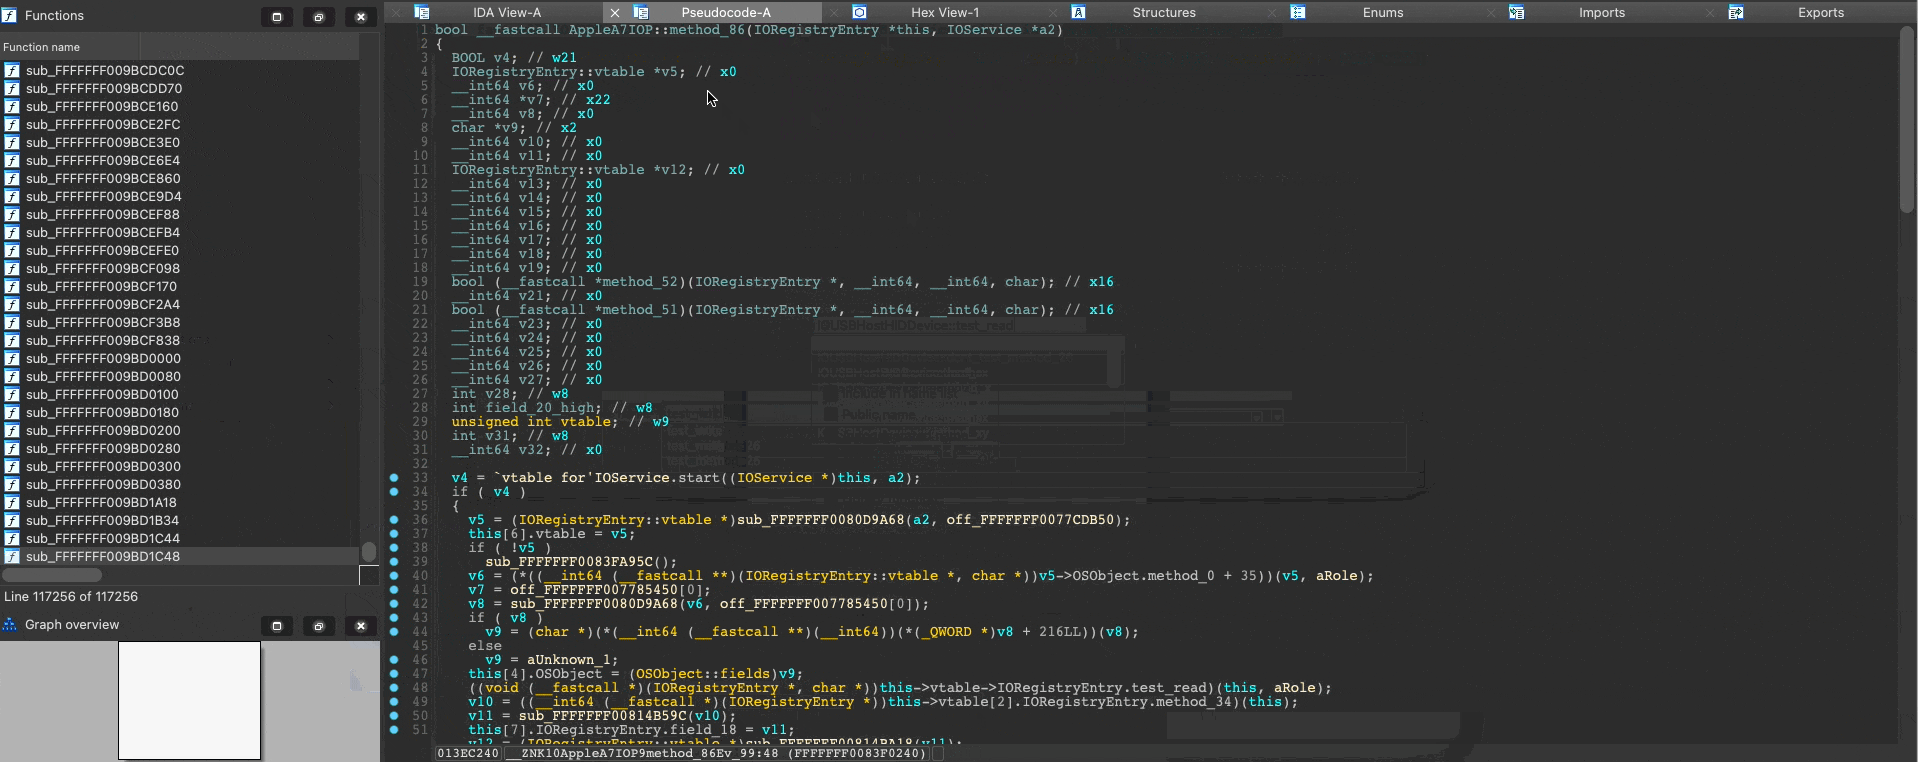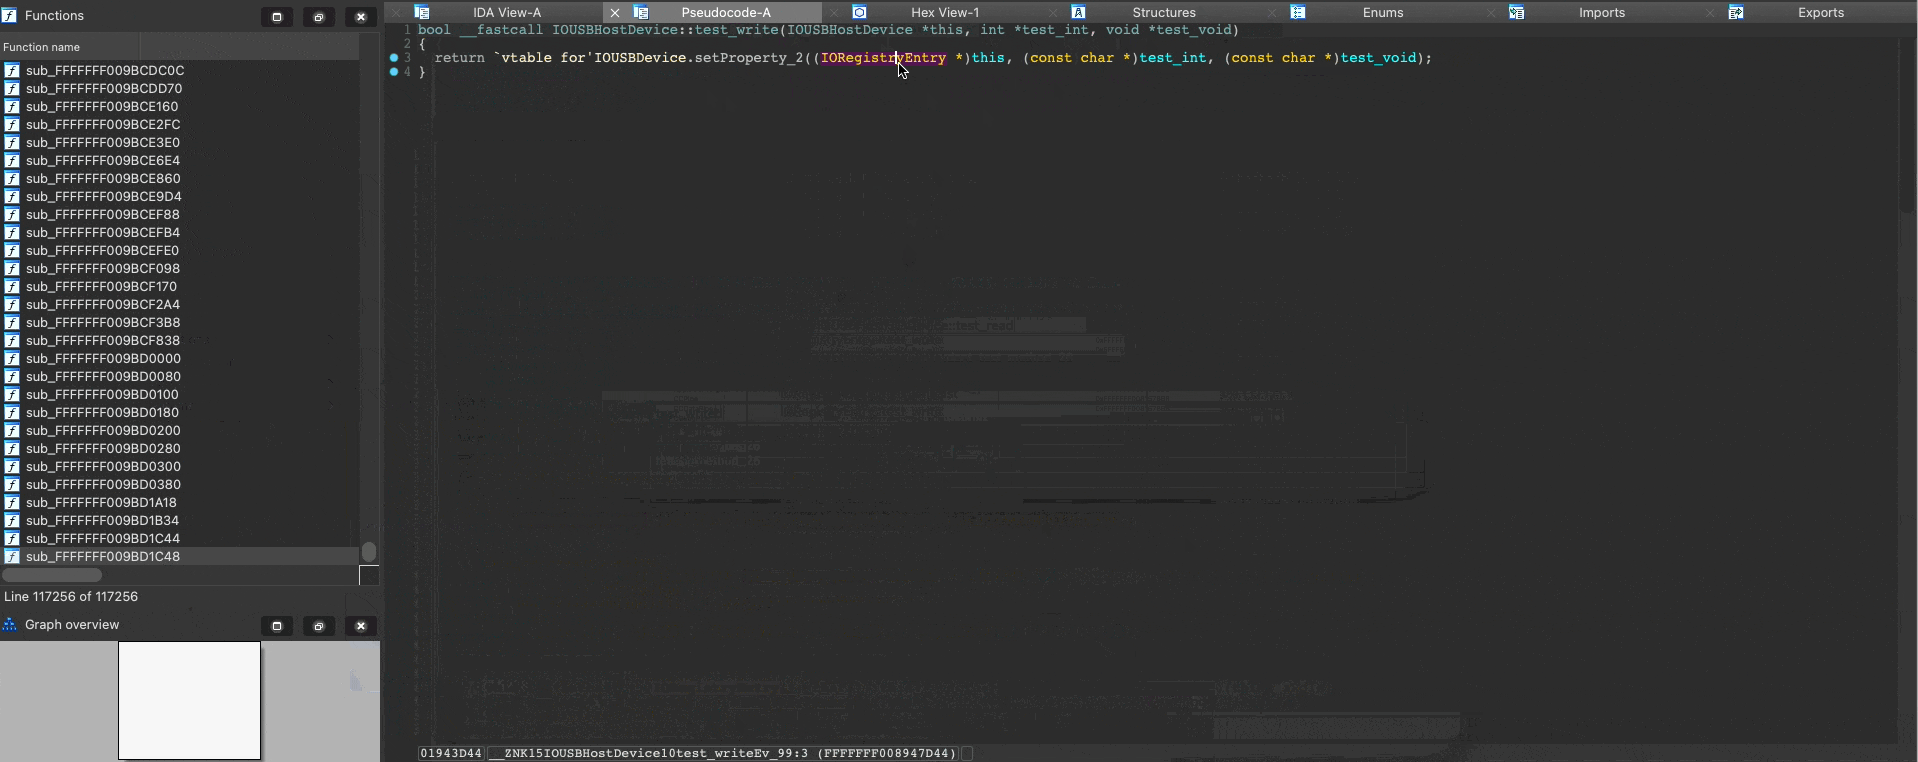 cellebrite-labs/ida_kcpp
An IDAPython module for enhancing c++ support on top of ida_kernelcache
 withsecurelabs/modulestomping
Research and proof-of-concept for module stomping, a technique to hide malicious code in legitimate Windows modules, with documentation and…
 blacksnufkin/maverick
Adaptix C2 agent using Crystal Palace PIC linker and PICO module system
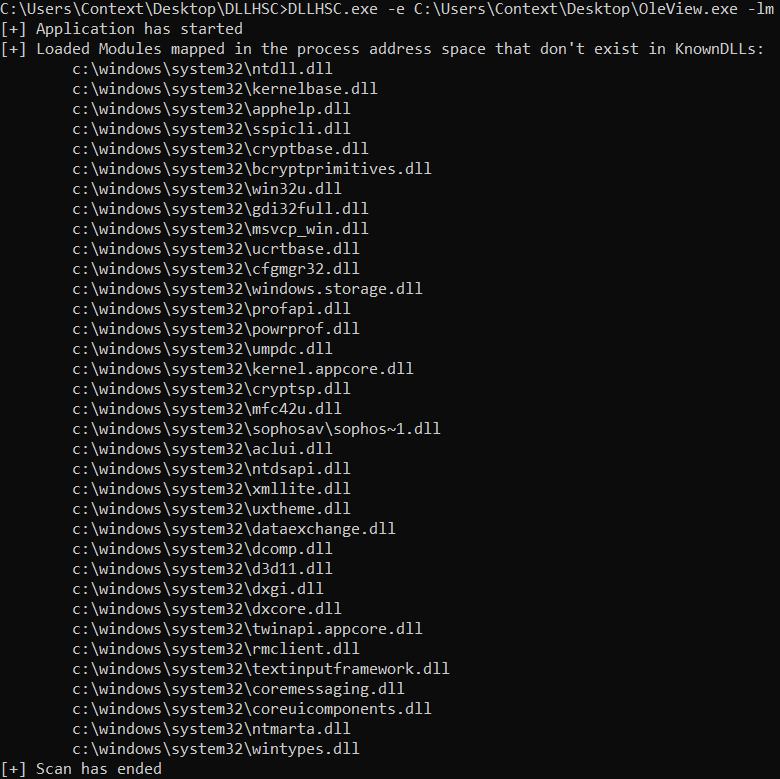 ctxis/dllhsc
Automated scanner for discovering DLL search order hijacking candidates in Windows executables, featuring import table parsing, runtime module…
 joe-desimone/patriot
In-memory stealth detection tool that identifies process hollowing, module stomping, unbacked executable regions, and anomalous CONTEXT structures…
 dump-guy/get-pdinvokeimports
PowerShell module for automatic detection of P/Invoke, Dynamic P/Invoke, and D/Invoke in .NET assemblies. Reveals unmanaged API calls, MDTokens, and…
 nccgroup/ghidra-nanomips
nanoMIPS module for Ghidra