

wtf
 0vercl0k/wtf
Distributed, code-coverage guided snapshot-based fuzzer for user and kernel-mode targets on Windows and Linux, with emulator and hypervisor backends.
binary-analysisdynamic-analysis-sandboxingexploitation+2
1.8k
0vercl0k/wtfDistributed, code-coverage guided snapshot-based fuzzer for user and kernel-mode targets on Windows and Linux, with emulator and hypervisor backends.
 mandiant/flare-qdb
Command-line and Python debugger for instrumenting and modifying native software behavior on Windows and Linux.
 nnonickreal/openqore
unleash the full power of your BES-based headphones! :)
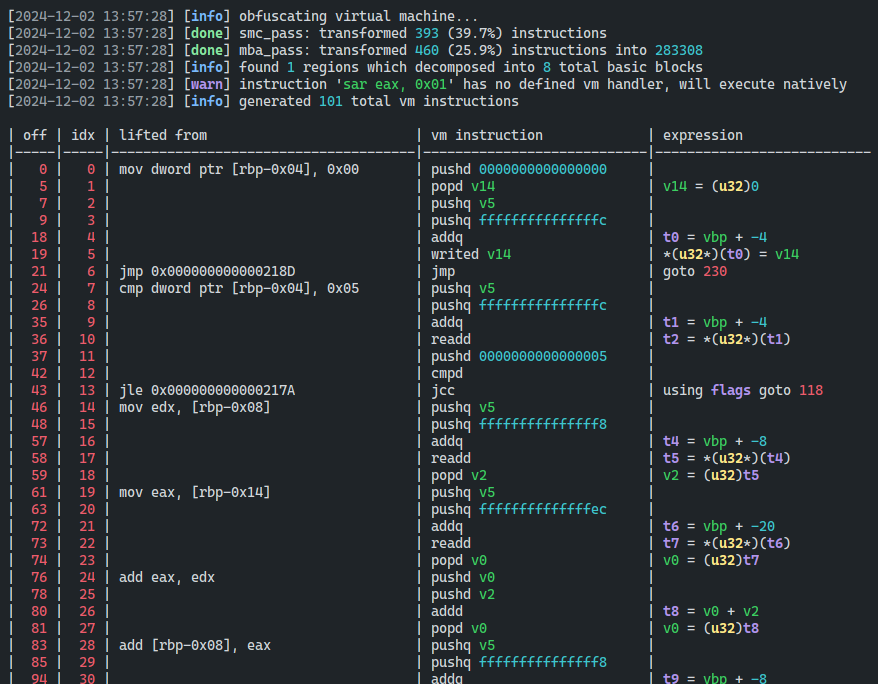 dmaivel/covirt
An x86-64 code virtualizer for VM based obfuscation
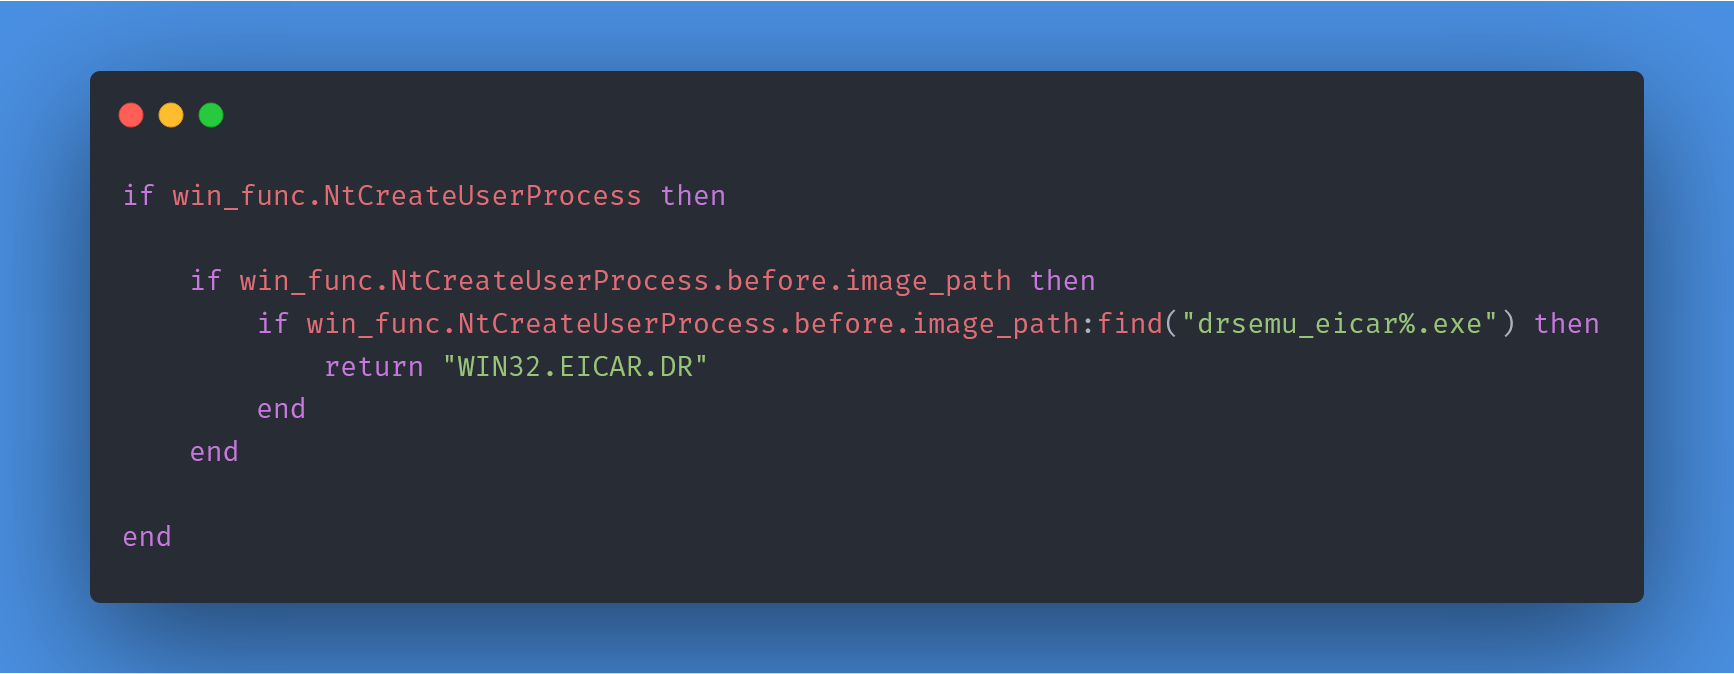 secrary/drsemu
DrSemu - Sandboxed Malware Detection and Classification Tool Based on Dynamic Behavior
 avast/retdec
RetDec is a retargetable machine-code decompiler based on LLVM.
 v-p-b/pecloakcapstone
Platform independent peCloak fork based on Capstone
 unicorn-engine/unicorn
Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)
 vaibhavpandeyvpz/apkstudio
Open-source, cross platform Qt6 based IDE for reverse-engineering Android application packages. It features a friendly IDE-like layout including code…
 gmh5225/frida-stalker-ntstrace
frida-stalker based system call tracer on windows(x64).
 gmh5225/ntstrace
frida-stalker based system call tracer on windows(x64).
 colton1skees/dna
LLVM based static binary analysis framework