
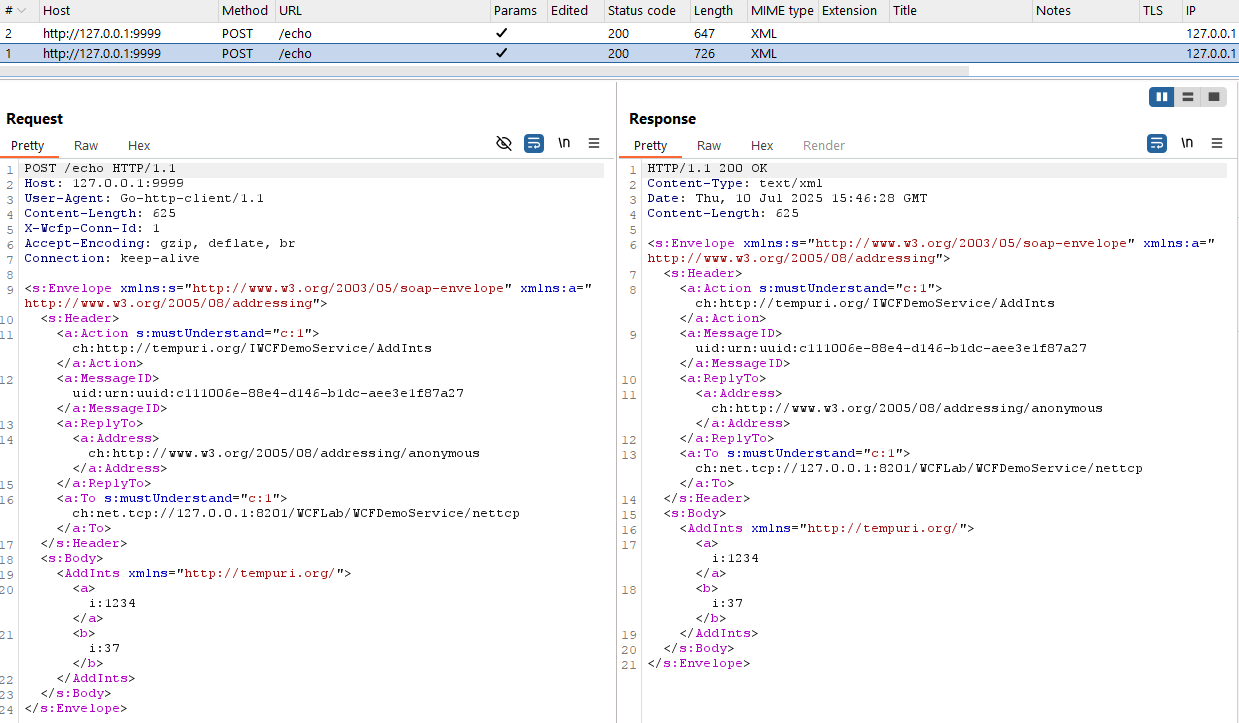
wcfproxy
 syss-research/wcfproxy
A proxy for net.tcp-based WCF traffic.
api-security-testingauthenticationbinary-analysis+3
8
syss-research/wcfproxyA proxy for net.tcp-based WCF traffic.
 ttdennis/fpicker
Frida-based in-process fuzzing suite with AFL++ proxy, standalone active/passive modes, and shared memory communication for high-performance…
 metrodango/pip3line
Swiss Army knife for raw bytes manipulation & interception
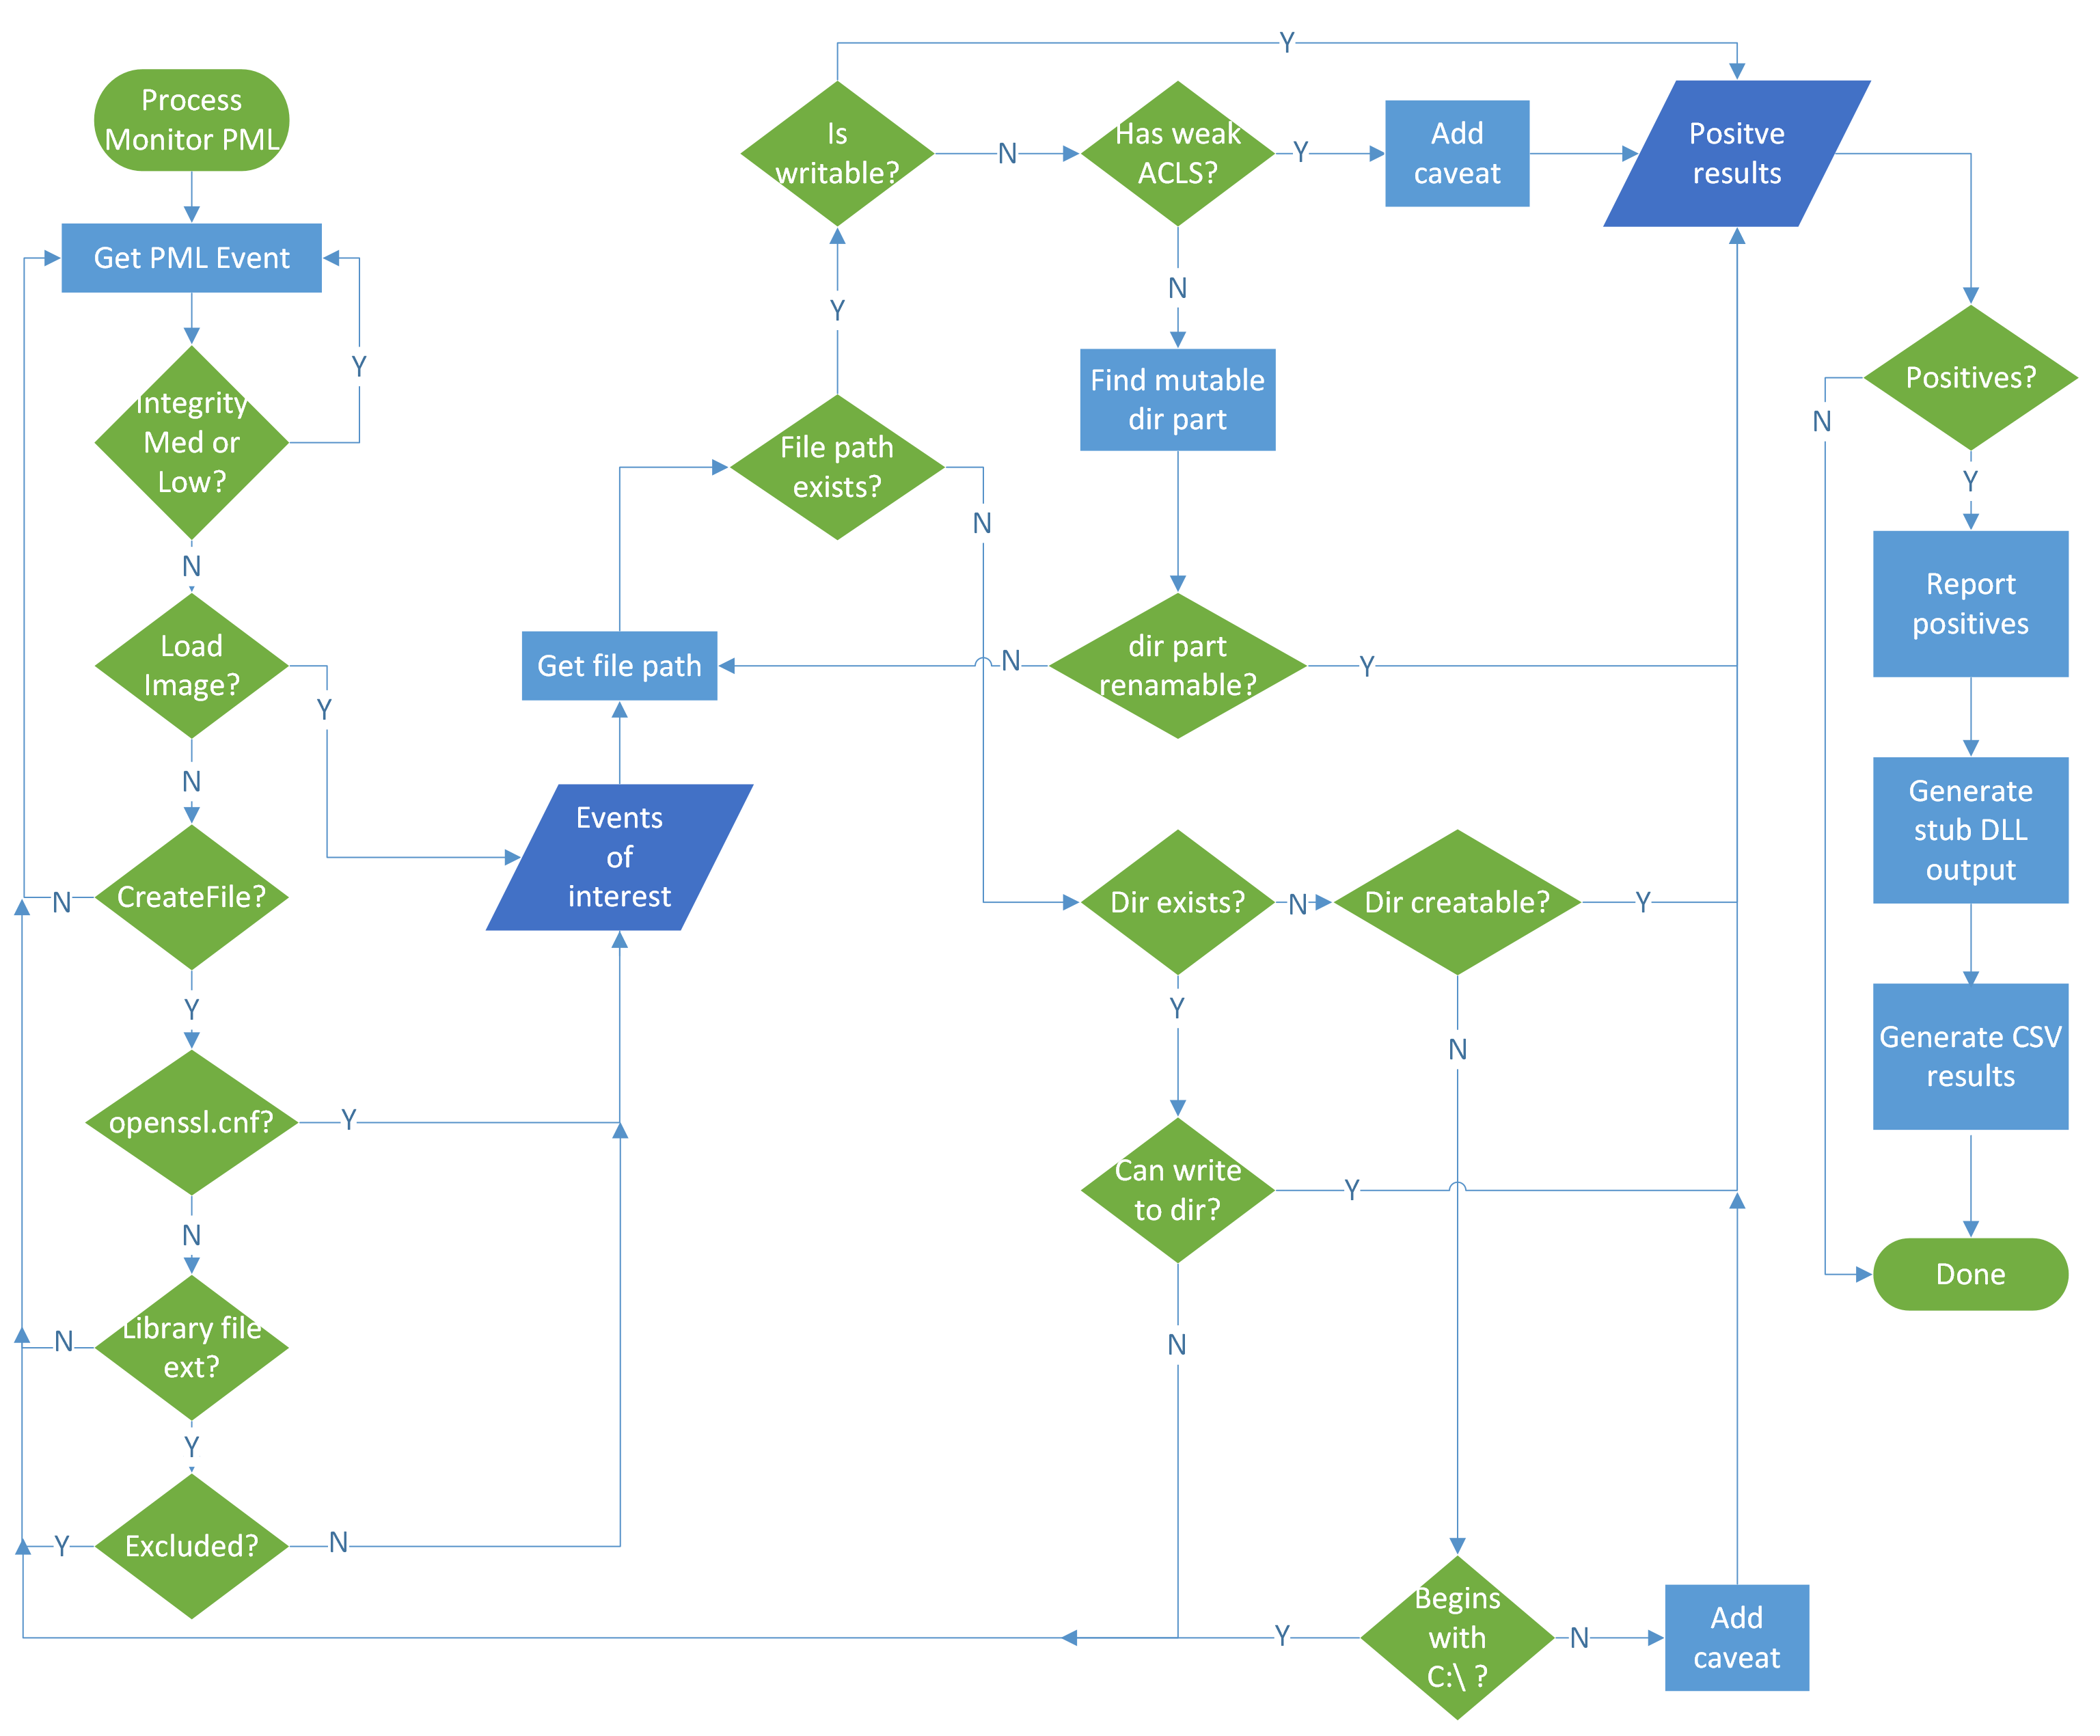 vu-ls/crassus
Windows privilege escalation discovery tool that parses Process Monitor boot logs to identify DLL hijacking, weak ACLs, and other elevation paths,…
 trailofbits/polytracker
An LLVM-based instrumentation tool for universal taint tracking, dataflow analysis, and tracing.
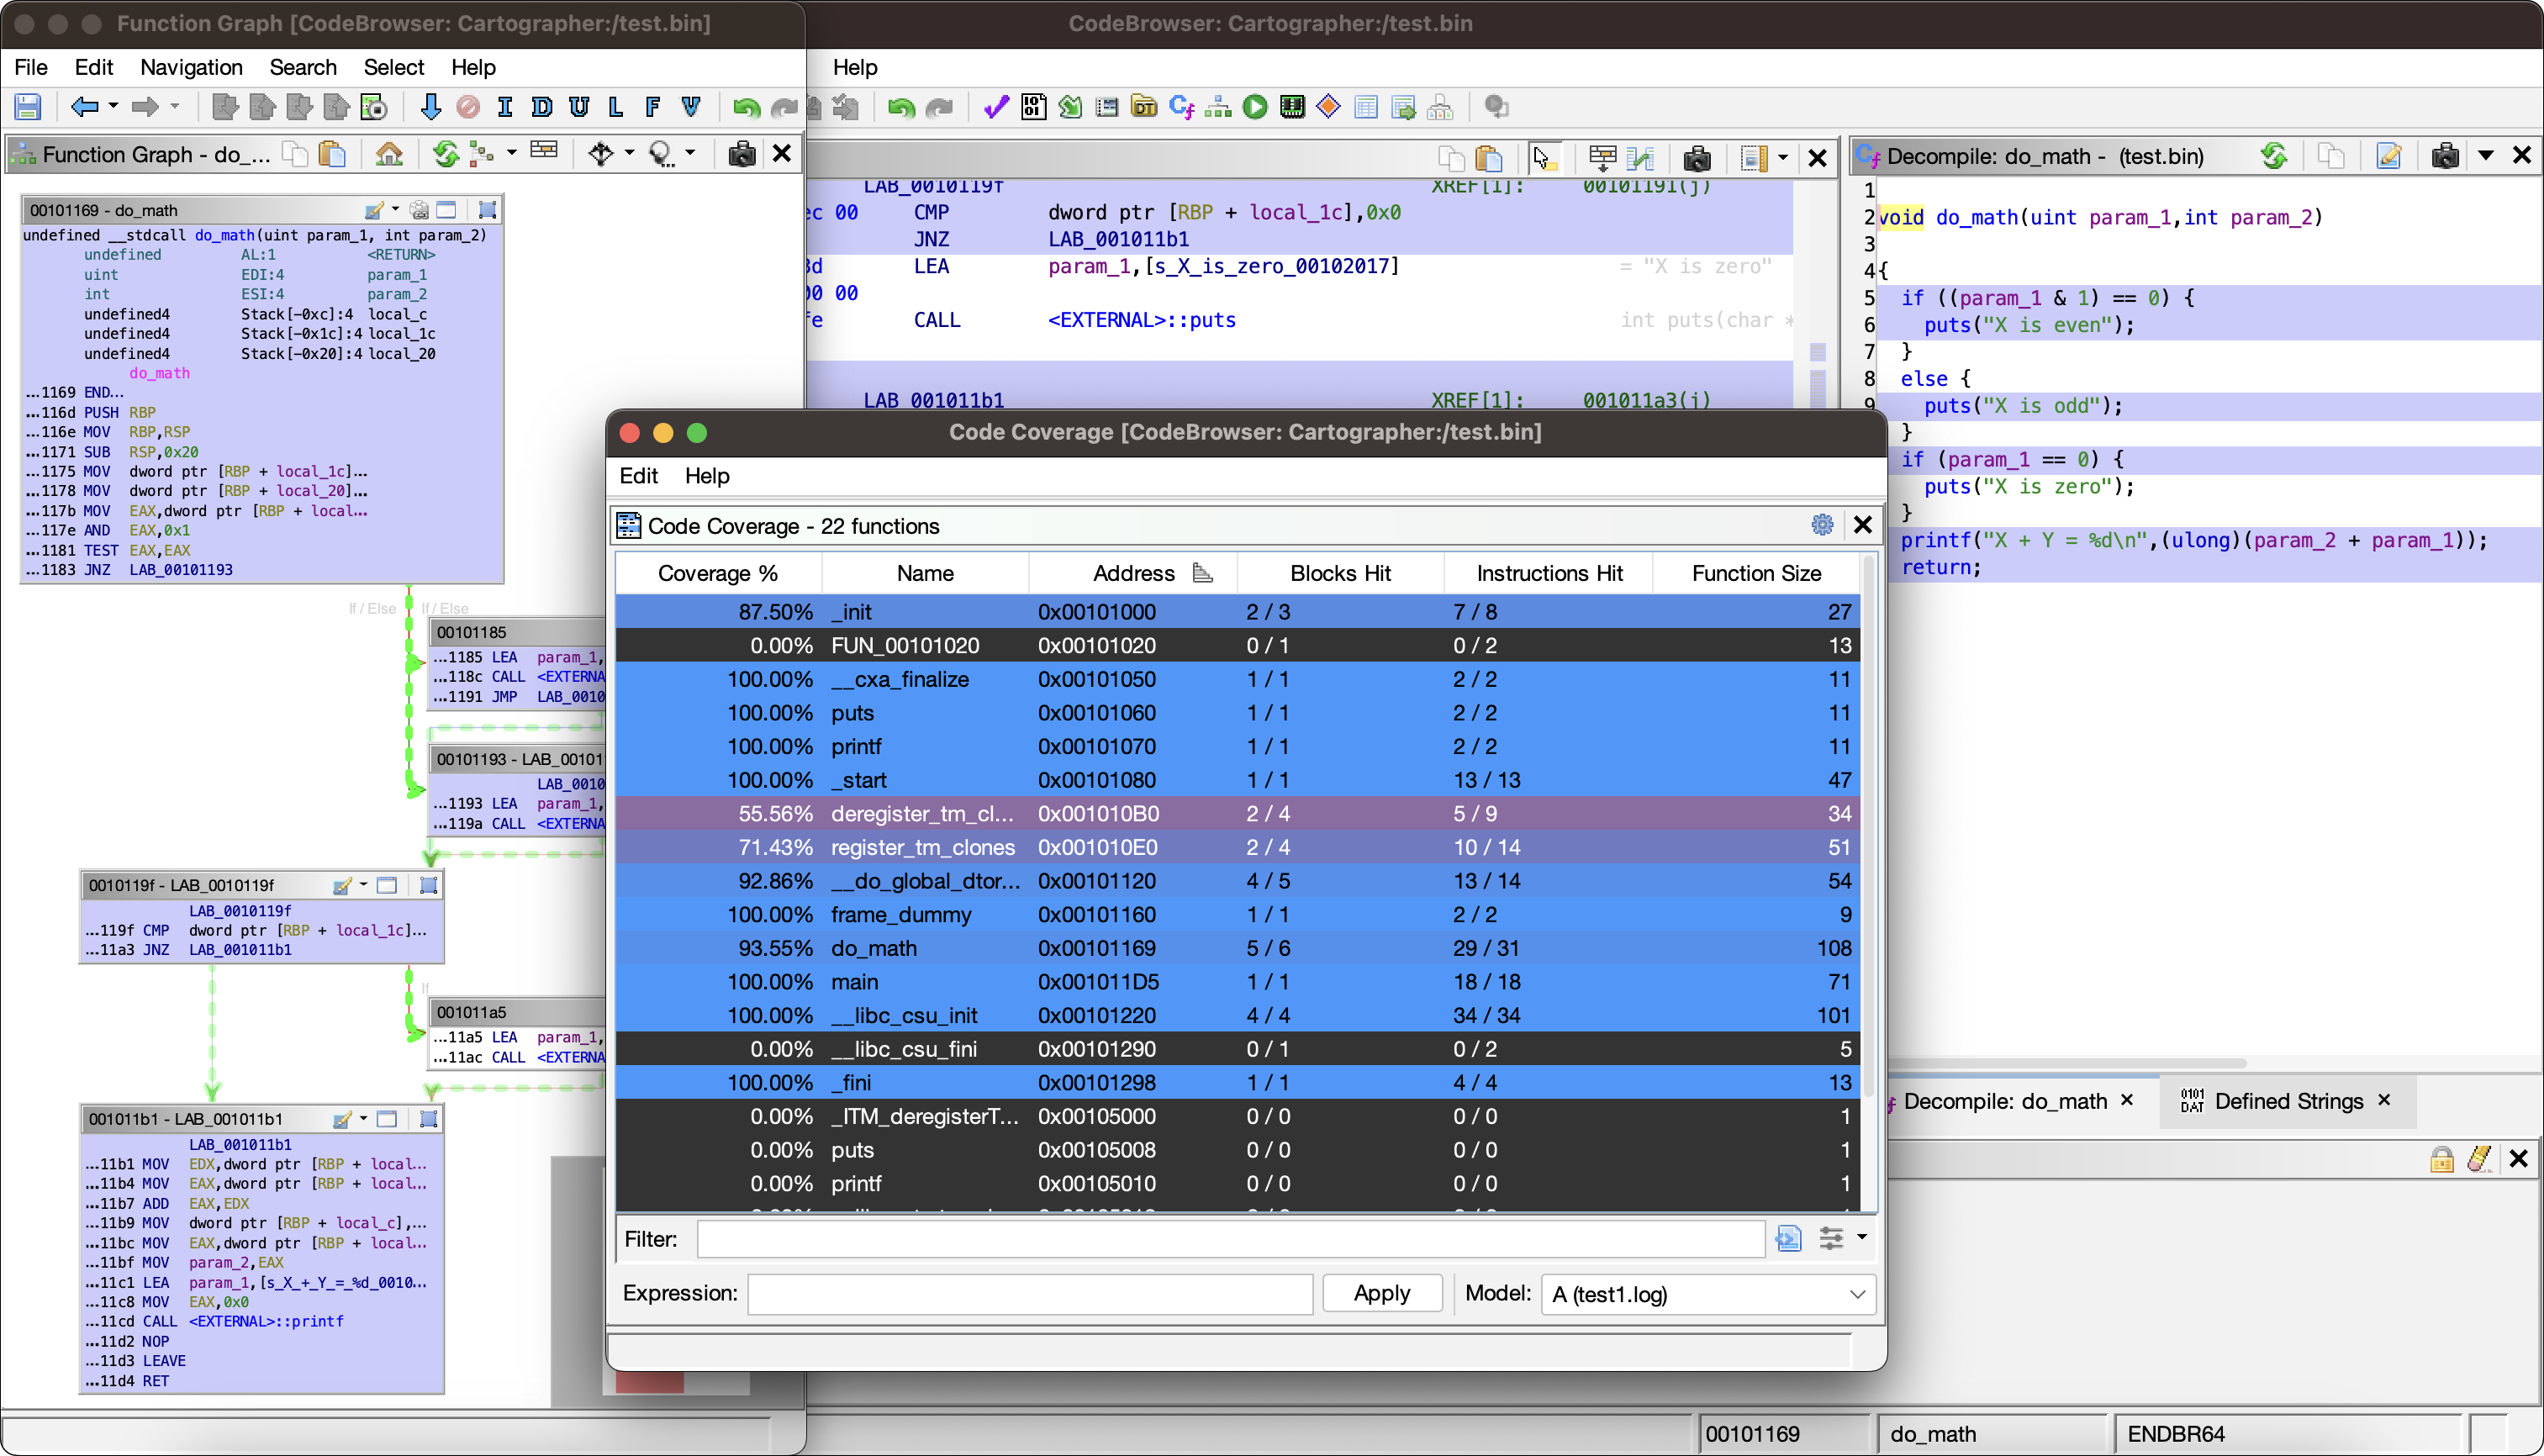 nccgroup/cartographer
Code Coverage Exploration Plugin for Ghidra
 tca-iscas/cooper-ndss-2022
A tool for effective testing the binding layer of scripting languages
 nccgroup/winstrument
Winstrument is a framework of modular scripts to aid in instrumenting Windows software using Frida for reverse engineering and attack surface…
 hasherezade/pesieve-go
Golang bindings for PE-sieve
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications
 starrynightsecurity/cve-2025-54574-squid-heap-buffer-overflow
Vulnerability Found on Squid Proxy.
 sentinel-one/peafl64
Static Binary Instrumentation tool for Windows x64 executables
 synacktiv/thats_no_pipe
Windows named pipe hooking toolkit
 ghostvectoracademy/dllhijackhunter
Automated DLL Hijacking Discovery, Validation, and Confirmation. Turning local misconfigurations into weaponized, confirmed attack paths.
 zer0condition/reversekit
x64 Dynamic Reverse Engineering Toolkit
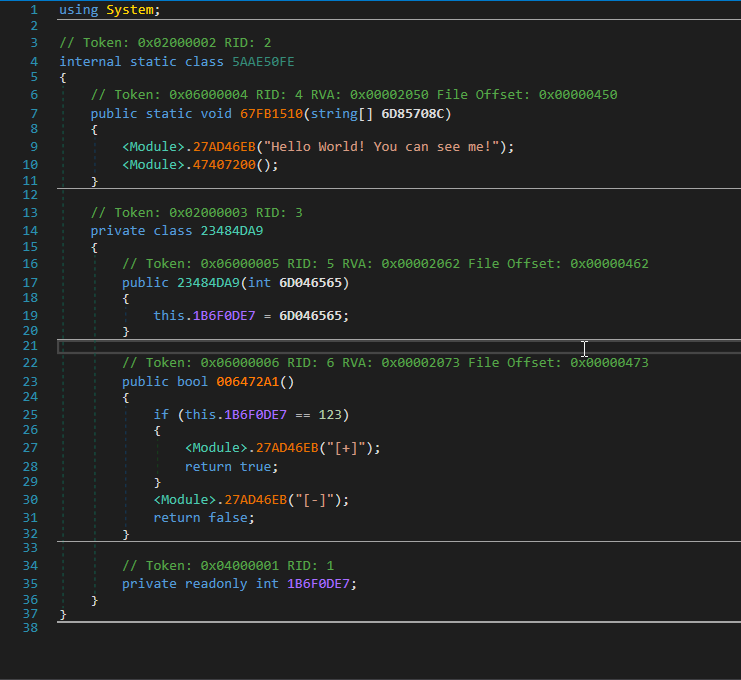 void-stack/vmunprotect.dumper
VMUnprotect.Dumper can dynamically untamper VMProtected Assembly.
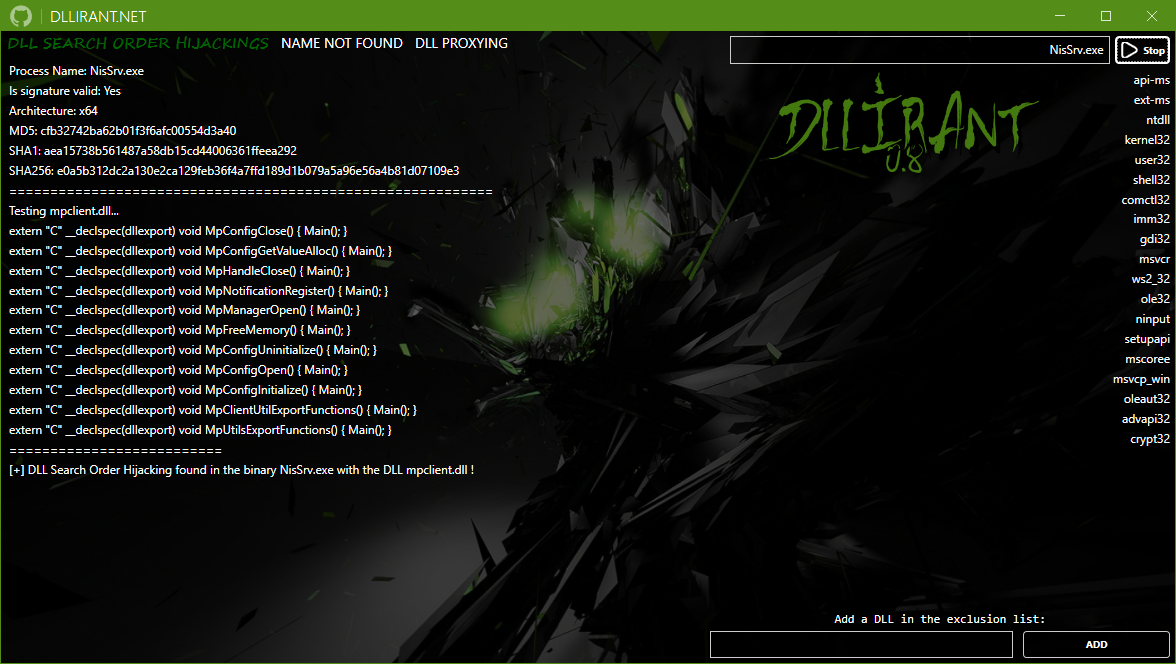 redteamsocietegenerale/dllirant
DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.
 1rhino2/fnprint
match functions in binaries by what they do, not what their bytes look like. behavioral function fingerprinting via microexecution.