
PrivKit
 mertdas/privkit
PrivKit is a simple beacon object file that detects privilege escalation vulnerabilities caused by misconfigurations on Windows OS.
binary-analysisexploitationpenetration-testing+4
627
mertdas/privkitPrivKit is a simple beacon object file that detects privilege escalation vulnerabilities caused by misconfigurations on Windows OS.
 fabrimagic72/malware-samples
A collection of malware samples caught by several honeypots i manage
 blacksnufkin/rusty-playground
Some Rust program I wrote while learning Malware Development
 farukalpay/neurocore
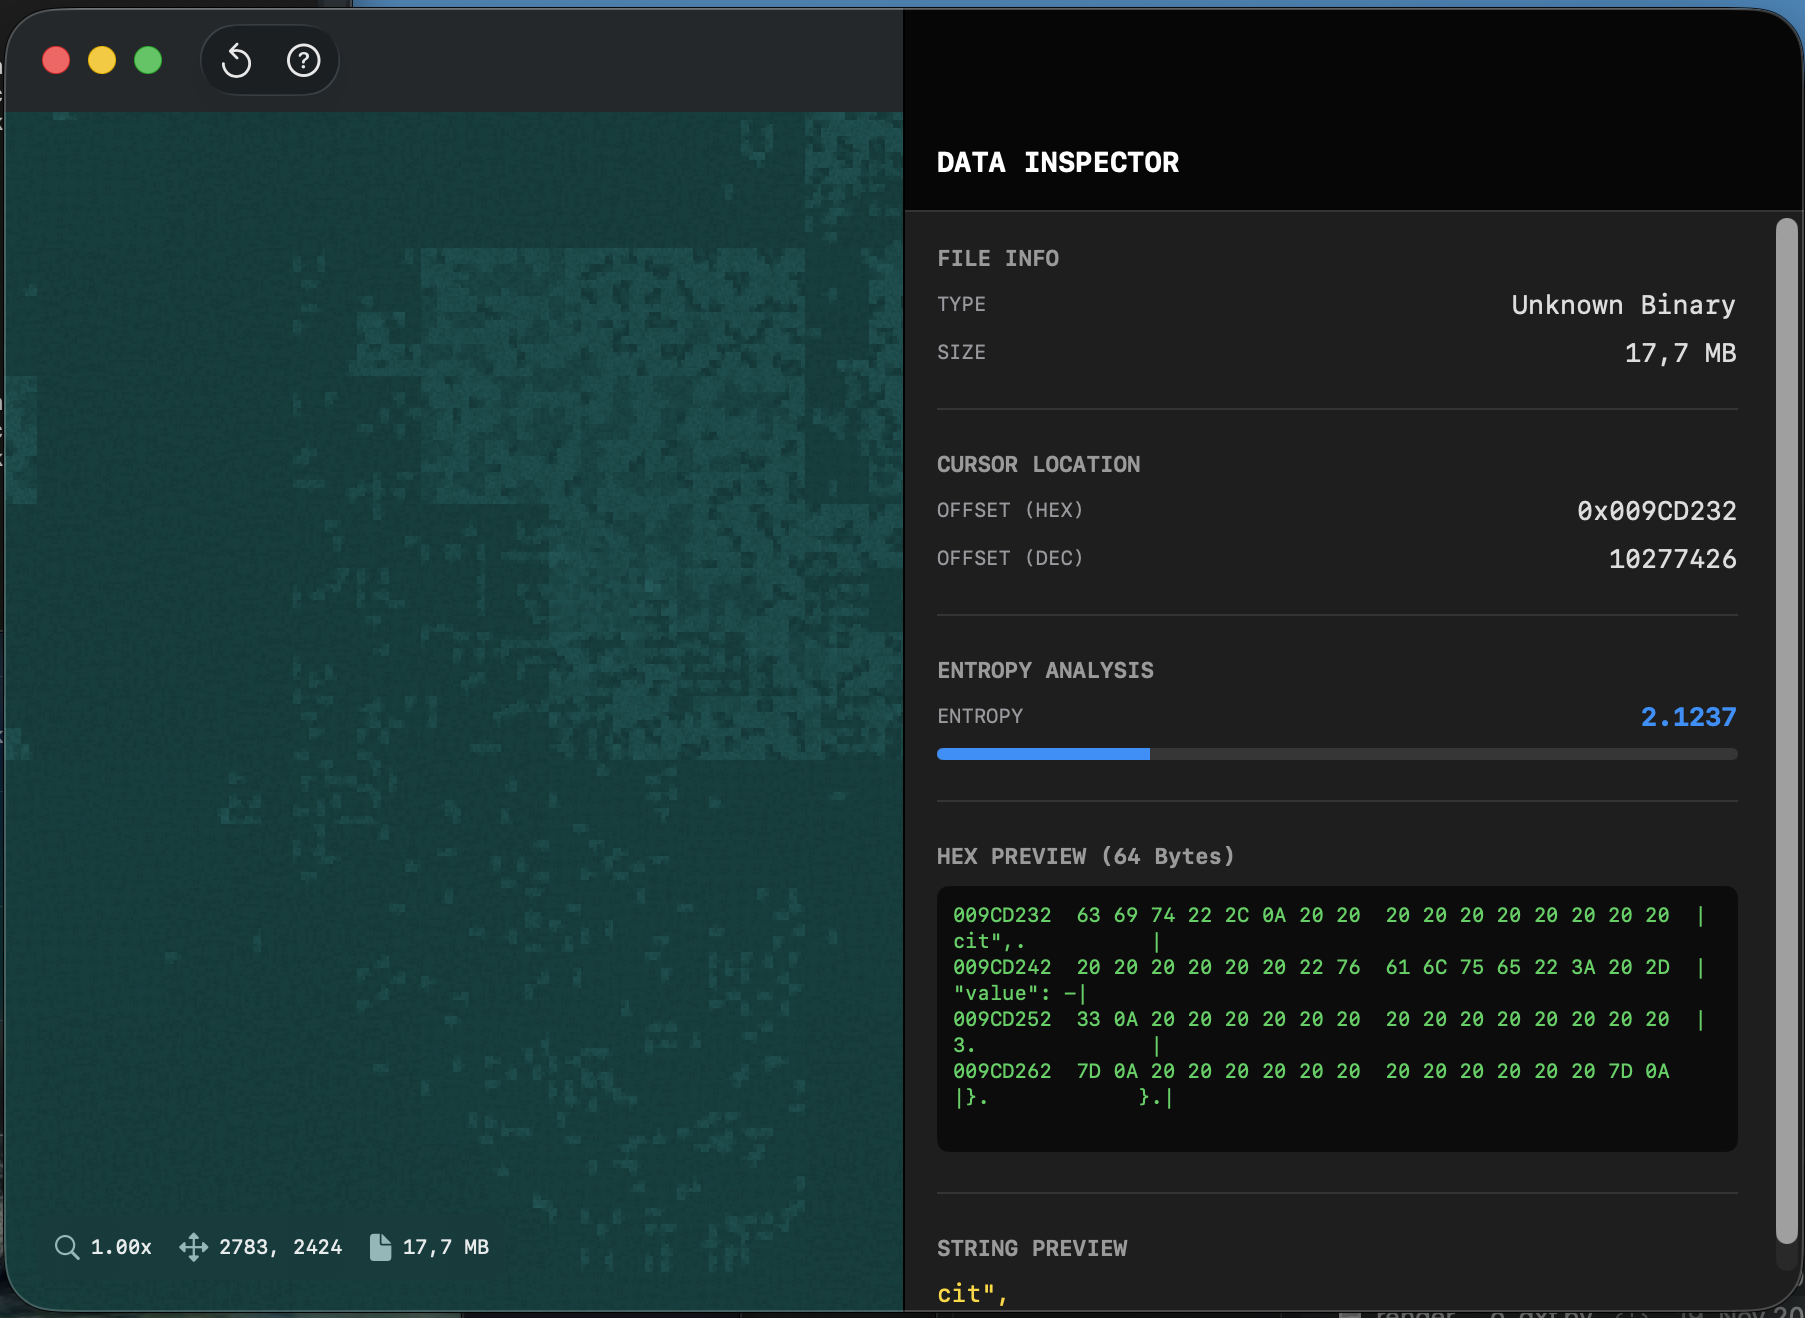
NeuroCore is a native macOS application that visualizes the internal structure of binary files using a Hilbert Curve mapping and Shannon Entropy…
 paul-tew/lifer
Windows link file (shortcuts) examiner
 airbus-cert/cve-2025-24985
Detection of malicious VHD files for CVE-2025-24985
 struppigel/portex
Java library to analyse Portable Executable files with a special focus on malware analysis and PE malformation robustness
 sandflysecurity/sandfly-entropyscan
Entropy scanner for Linux to detect packed or encrypted binaries related to malware. Finds malicious files and Linux processes and gives output with…
 glmcdona/process-dump
Windows tool for dumping malware PE files from memory back to disk for analysis.
 seekbytes/ipa
GUI analyzer for deep-diving into PDF files. Detect malicious payloads, understand object relationships, and extract key information for threat…
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
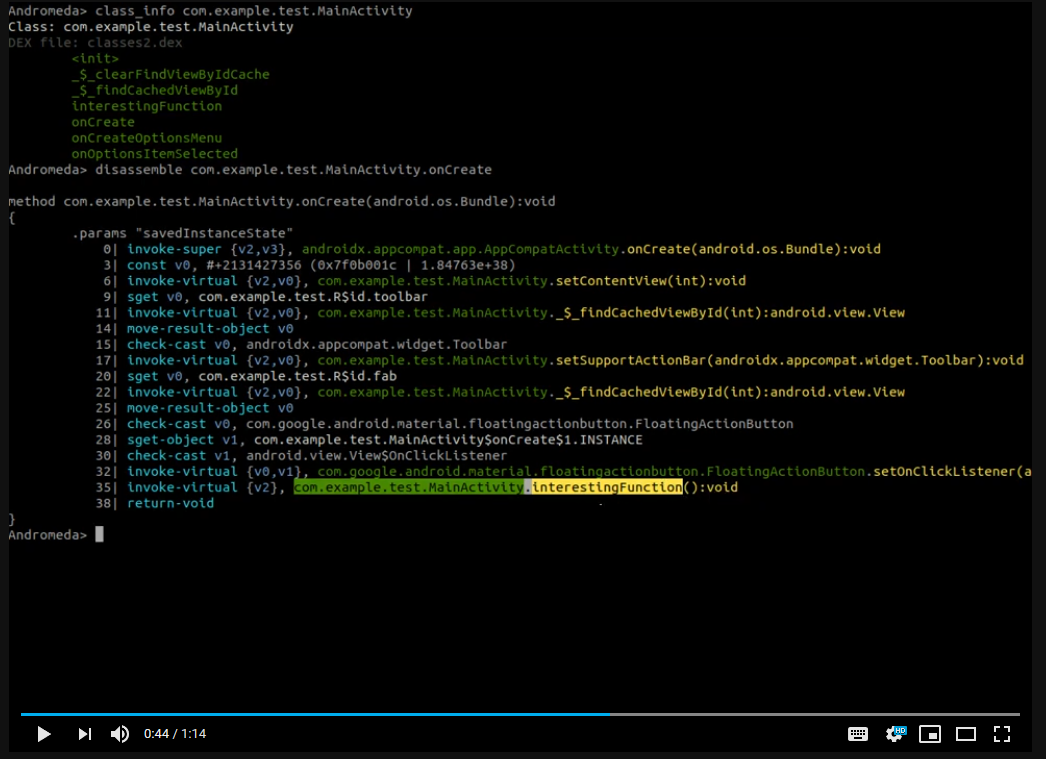 secrary/andromeda
C/C++ interactive reverse engineering tool for Android applications, enabling fast static analysis and binary inspection of APK files.
 jfmaes/lazysign
Create fake certs for binaries using windows binaries and the power of bat files
 iilegacyyii/exportdumper
A small tool I made to dump the export table of PE files. The primary use case was intended for use within DLL proxying.
 13m0n4de/pngcheck-vulns
A repository of proof-of-concept files demonstrating disclosed and patched vulnerabilities in pngcheck (2.4.0 - 3.0.1), including CVE-2020-27818,…
 mandiant/flashmingo
Automatic analysis of SWF files based on some heuristics. Extensible via plugins.
 jstrosch/malware-samples
Malware samples, analysis exercises and other interesting resources.
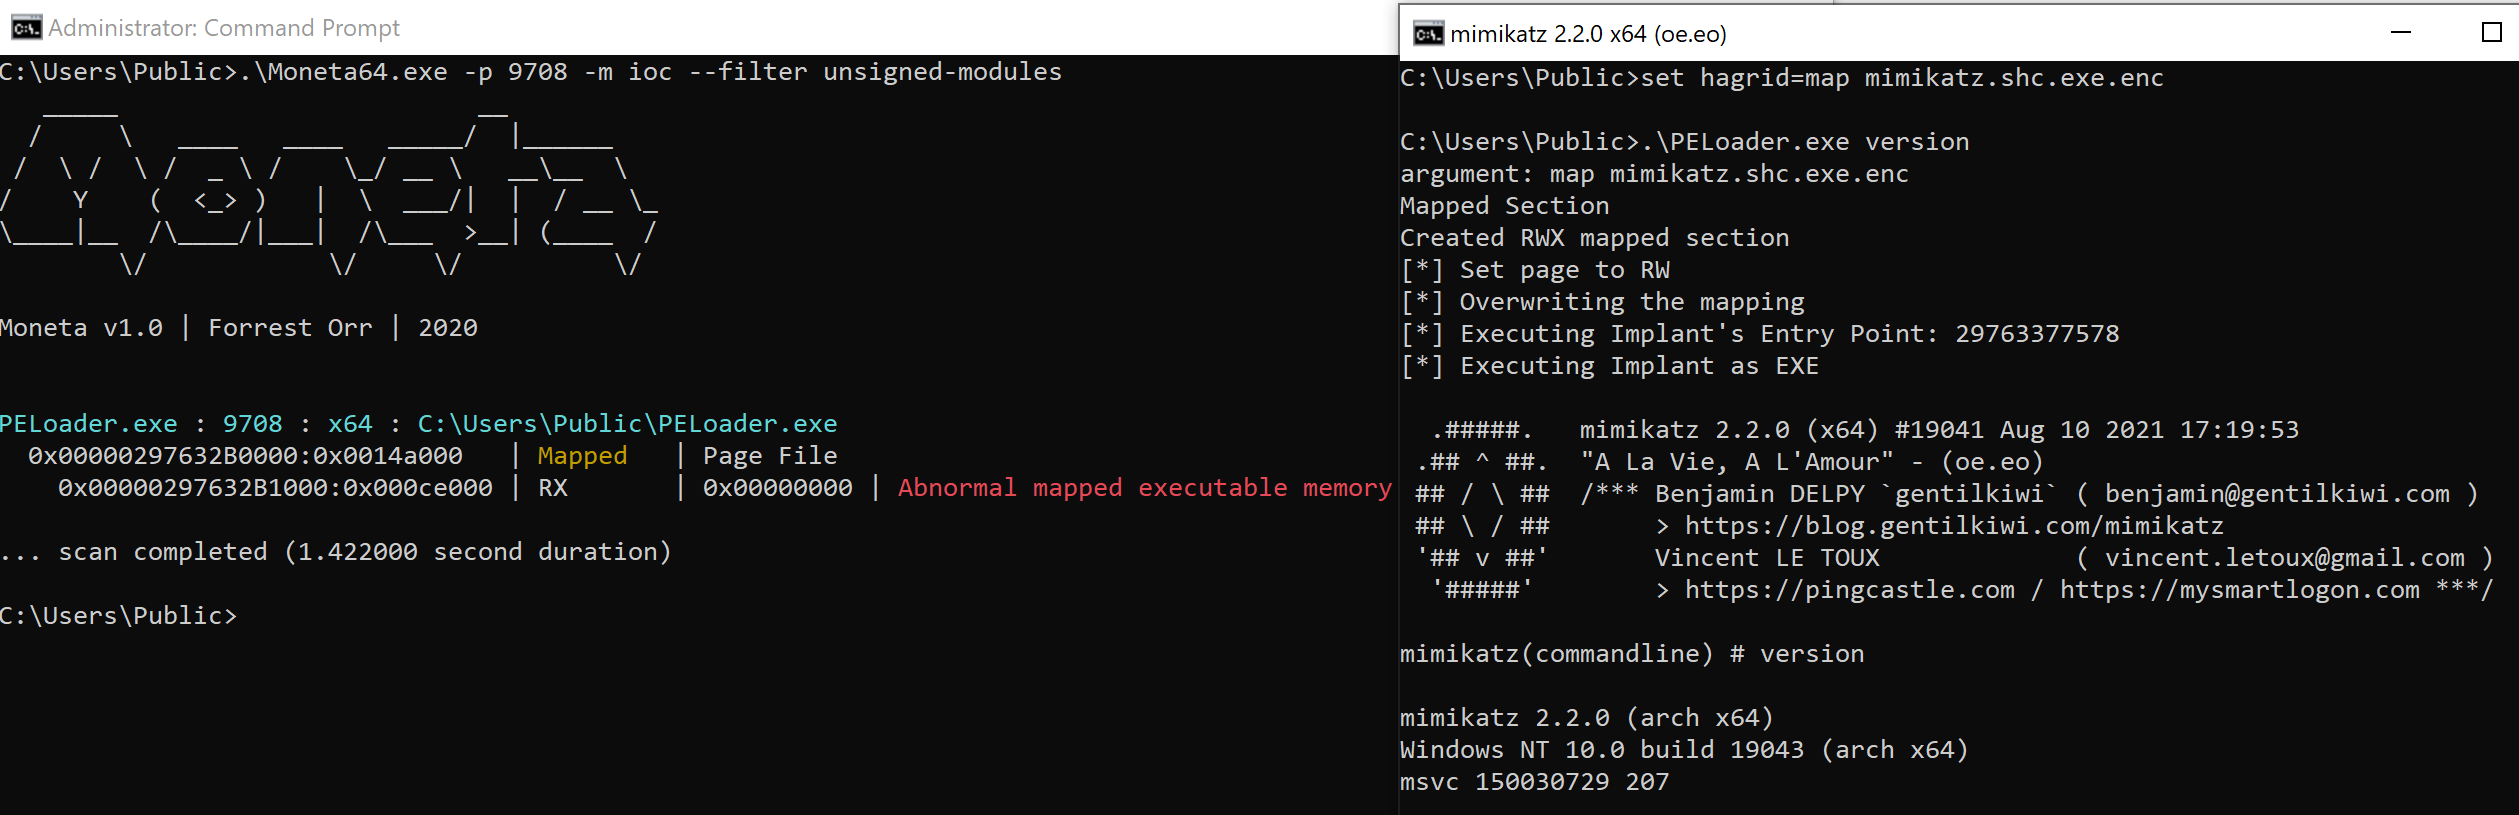 hagrid29/peloader
PE loader with various shellcode injection techniques