

sharem
 bw3ll/sharem
SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…
ai-securitybinary-analysisdebuggers+5
4927 months ago
bw3ll/sharemSHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…
 therealdreg/shellex
C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…
 oldboy21/shgenob
Python based tool for generating Shellcode from PIC C
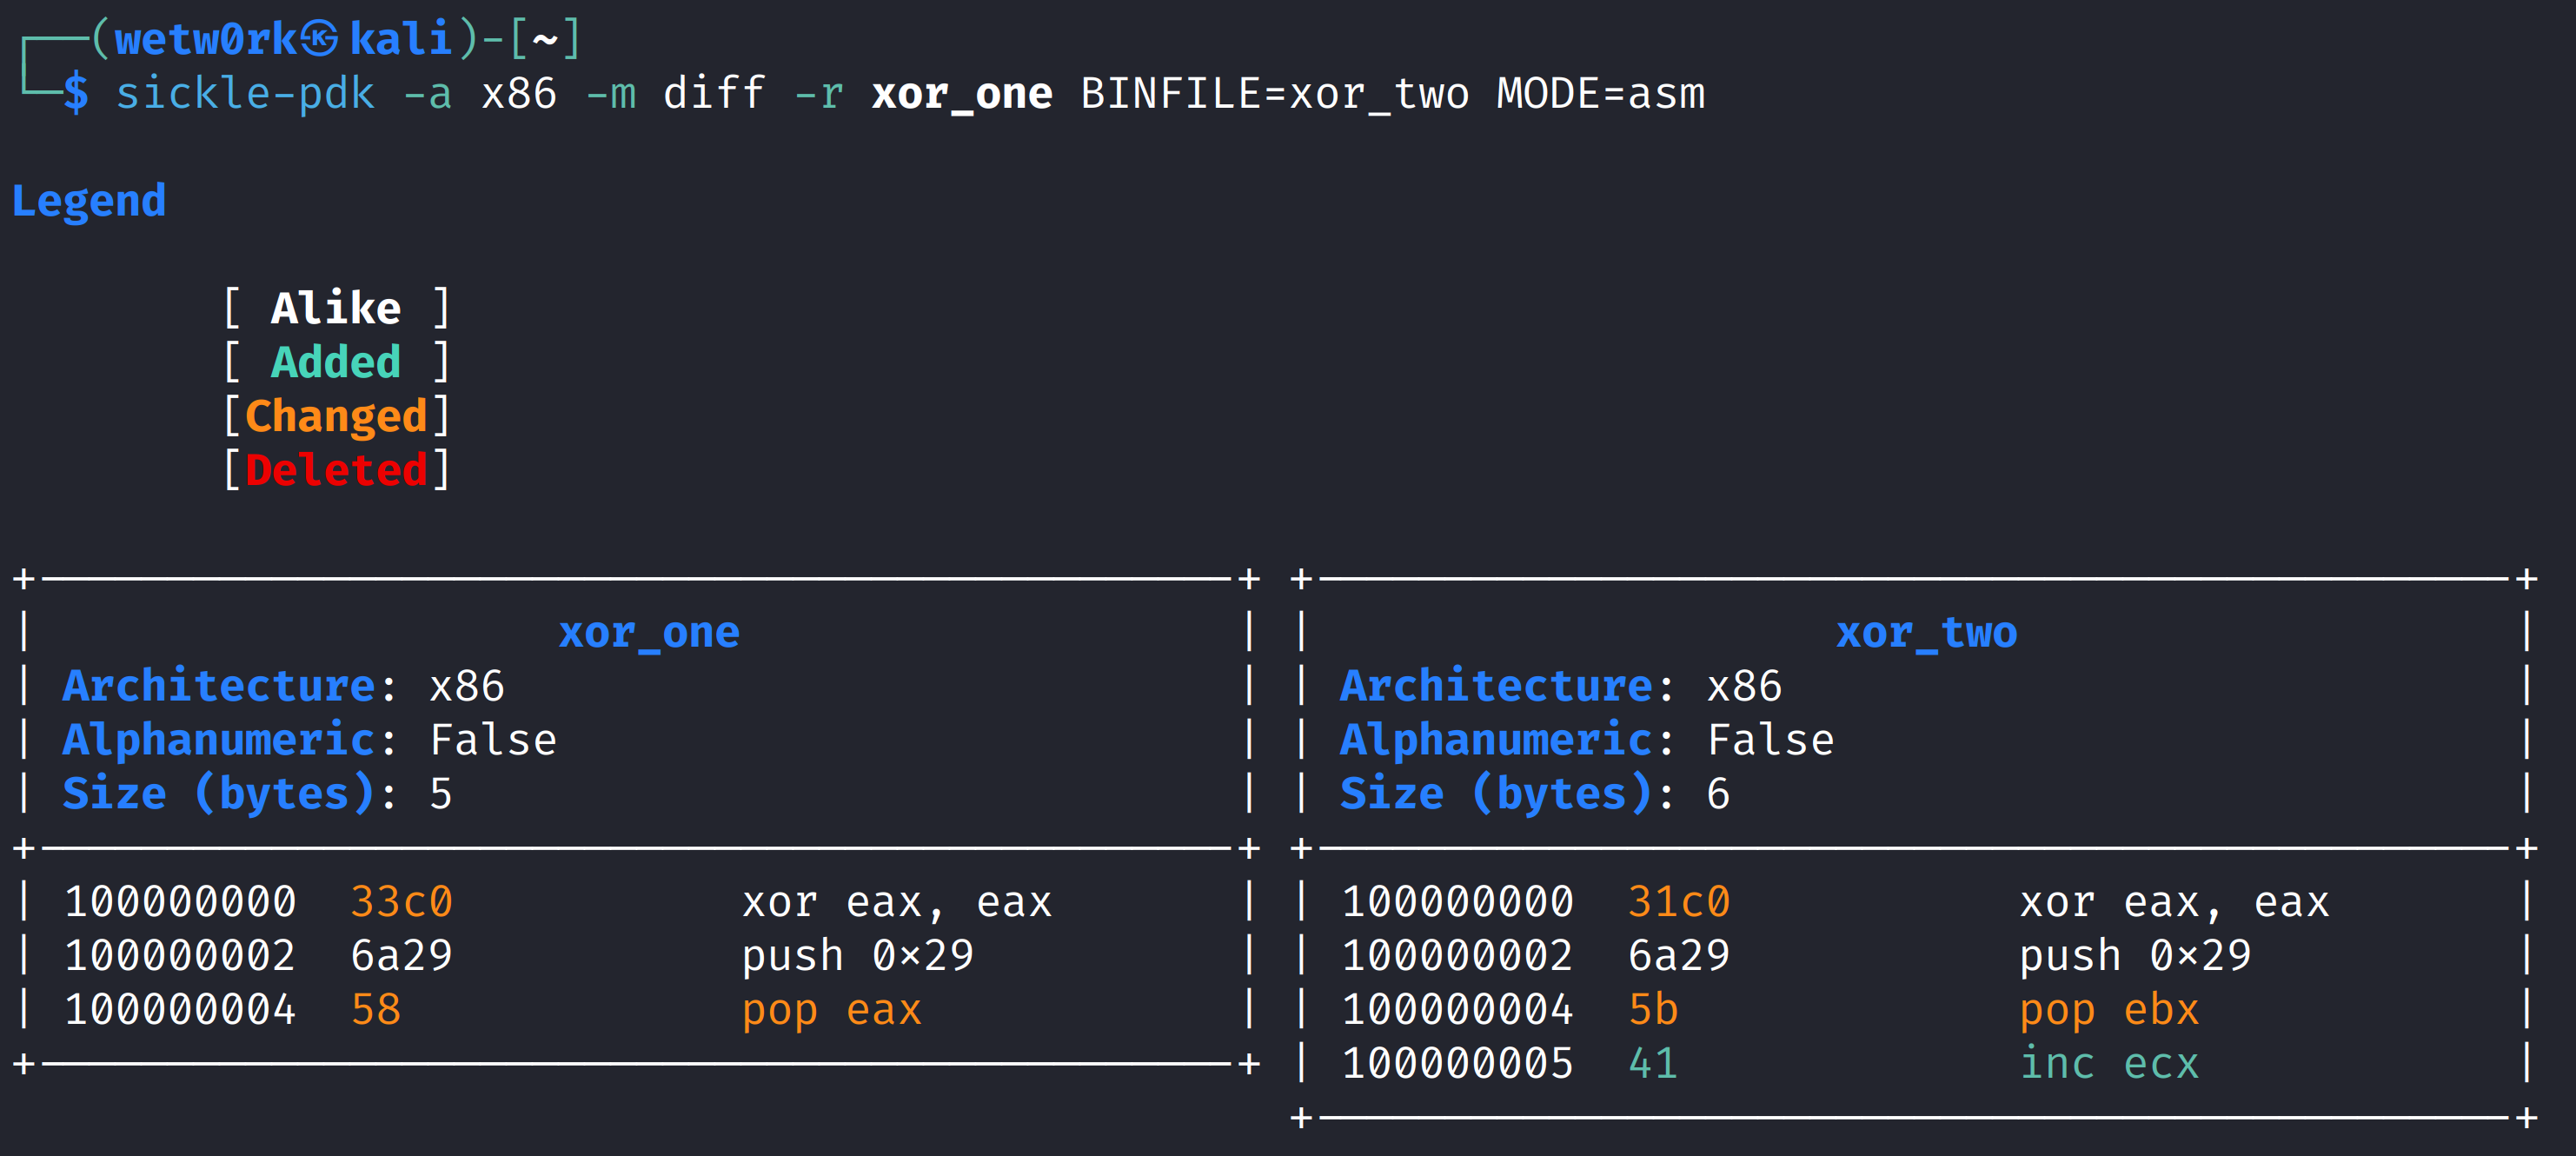 wetw0rk/sickle-pdk
Sickle - Payload Development Kit
 cybereason/siofra
Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…
 s3cur3th1ssh1t/nimgetsyscallstub
Dynamically extracts fresh syscall stubs from ntdll.dll to evade signature-based detection, with a shellcode execution template for Nim-based…
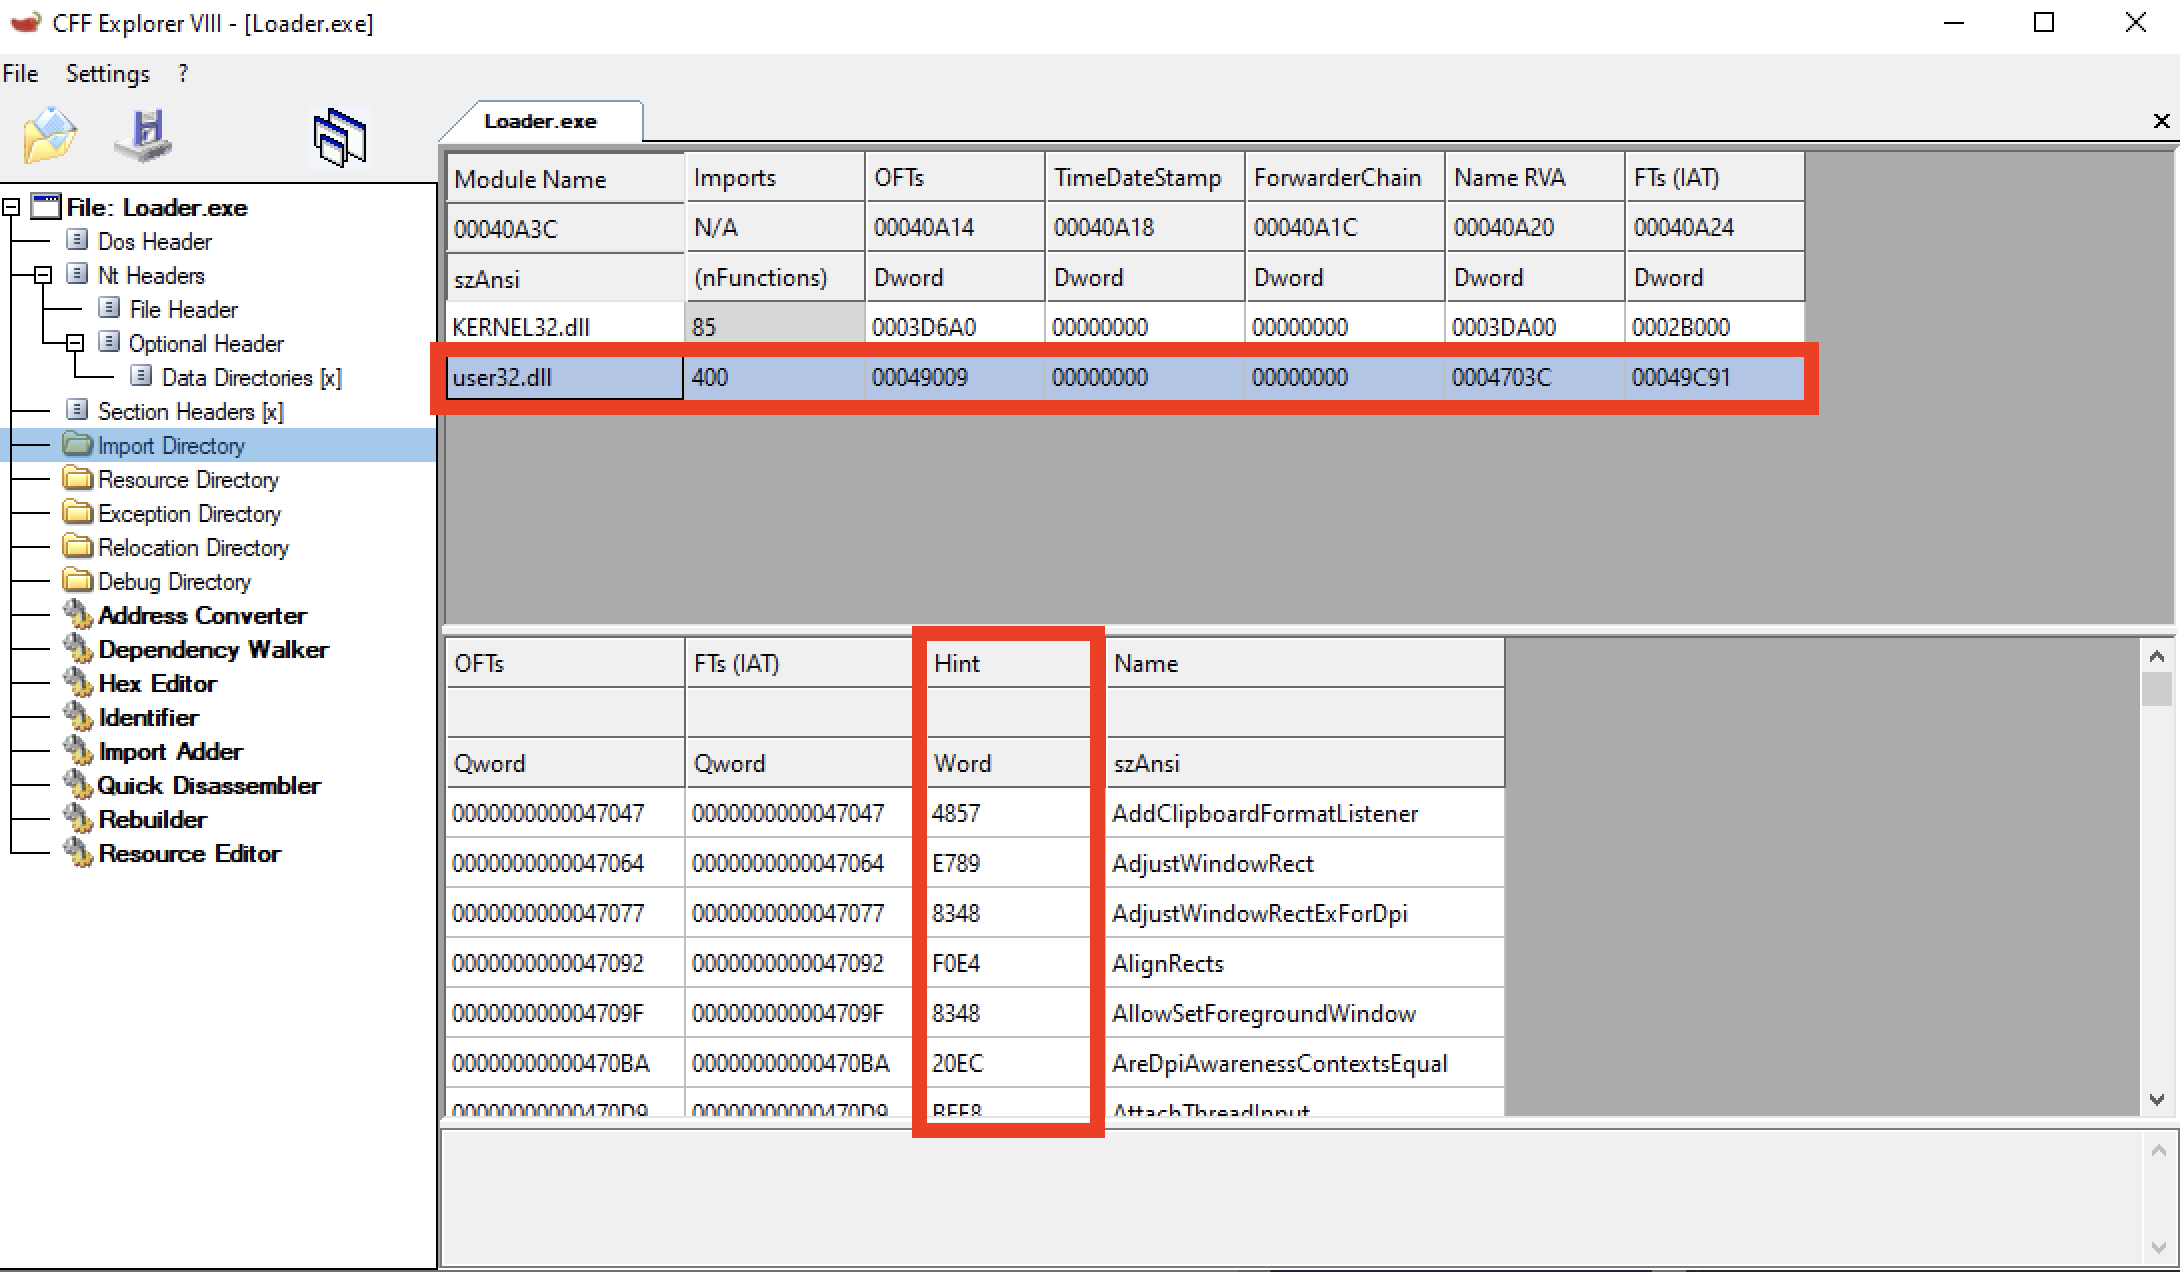 frkngksl/hintinject
A PoC project for embedding shellcode to Hint/Name Table
 helviojunior/shellcodetester
An application to test windows and linux shellcodes
 nul0x4c/manualrsrcdatafetching
Get your data from the resource section manually, with no need for windows apis
 spiralbl0ck/analysis-for-stage1-shellcode-loader-from-hacking-
Analysis for stage1 shellcode loader from hacking
 e3prom/bst
Binary String Toolkit (BST). Quickly and easily convert binary strings for all your exploit development needs. 😎
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
 gamozolabs/elfloader
An architecture-agnostic ELF file flattener for shellcode
 trustedsec/lazzzy_dump
Statically extracts and decrypts AES-CBC/XOR-obfuscated shellcode from laZzzy-wrapped PE binaries via signature matching and RIP-relative address…