
emba
 e-m-b-a/emba
EMBA - The firmware security analyzer
binary-analysisdynamic-analysis-sandboxingembedded-systems-security+8
3.7k
e-m-b-a/embaEMBA - The firmware security analyzer
 attify/firmware-analysis-toolkit
Firmware security research platform combining binary analysis, taint tracing, and emulation across IoT, edge AI, mobile devices, and robotics.
 redballoonsecurity/ofrak
Binary analysis and modification platform for unpacking, analyzing, modifying, and repacking firmware and executable formats via GUI and Python API.
 rehints/efixplorer
IDA plugin and loader for UEFI firmware analysis and reverse engineering automation
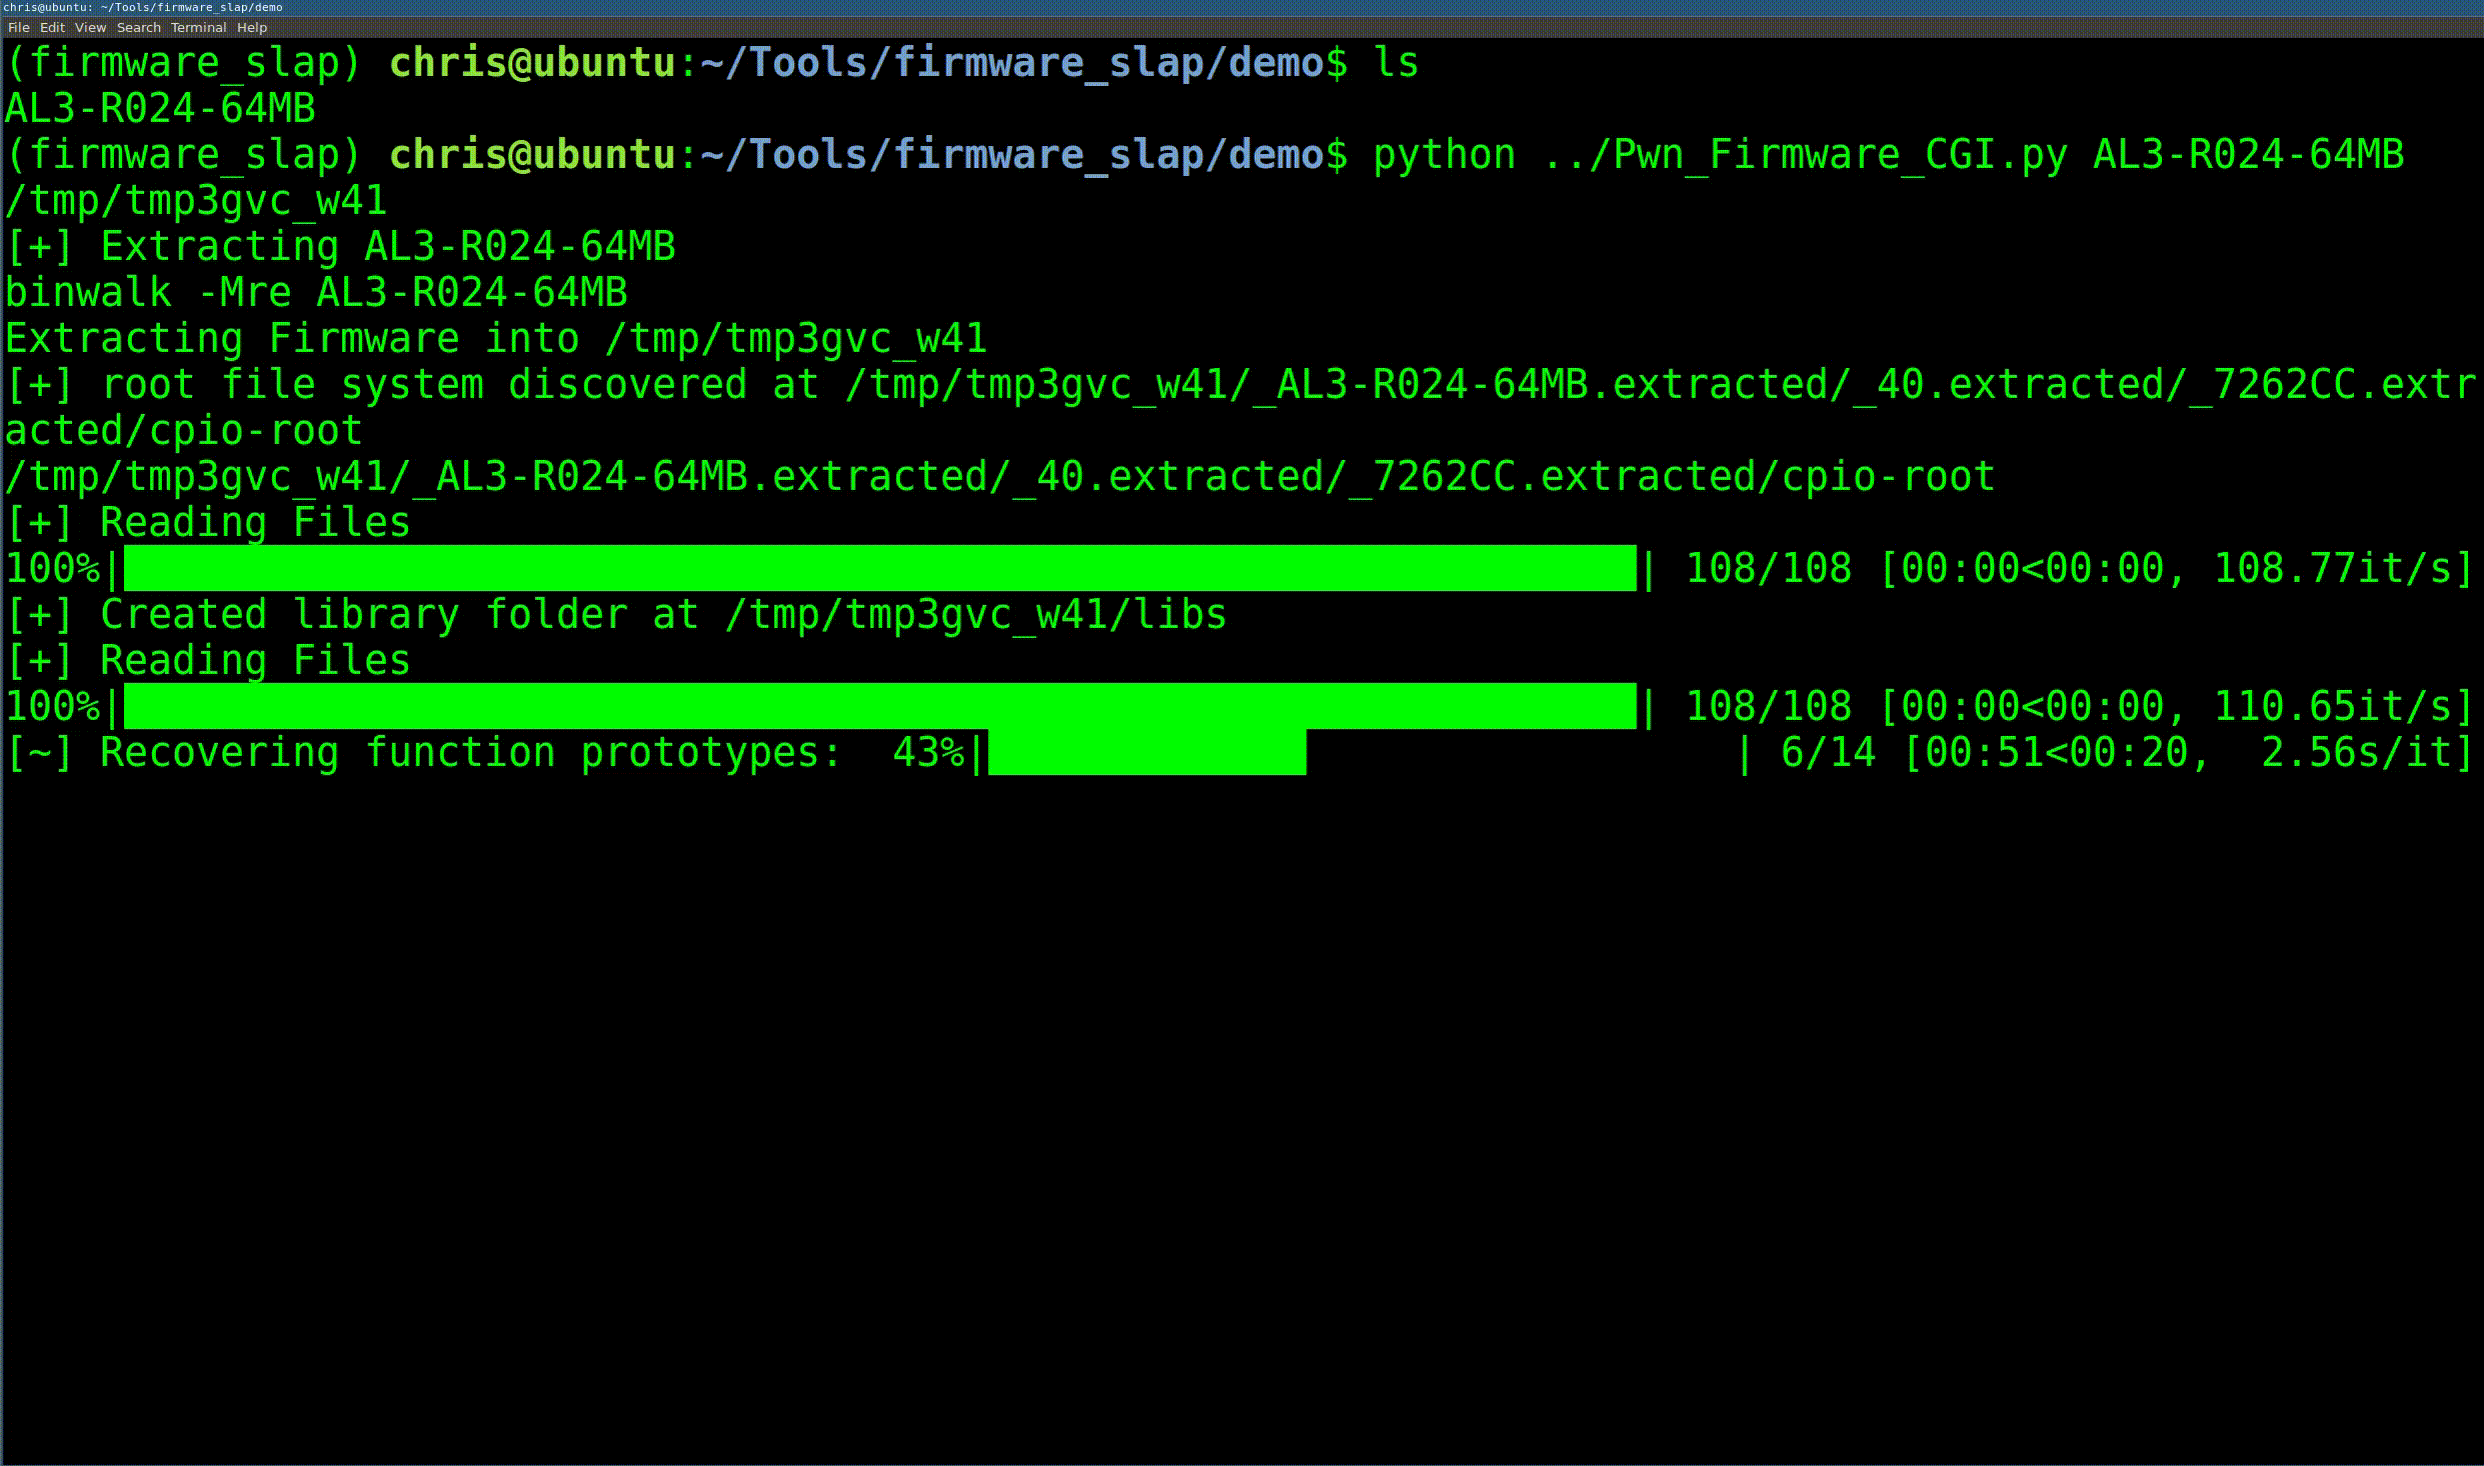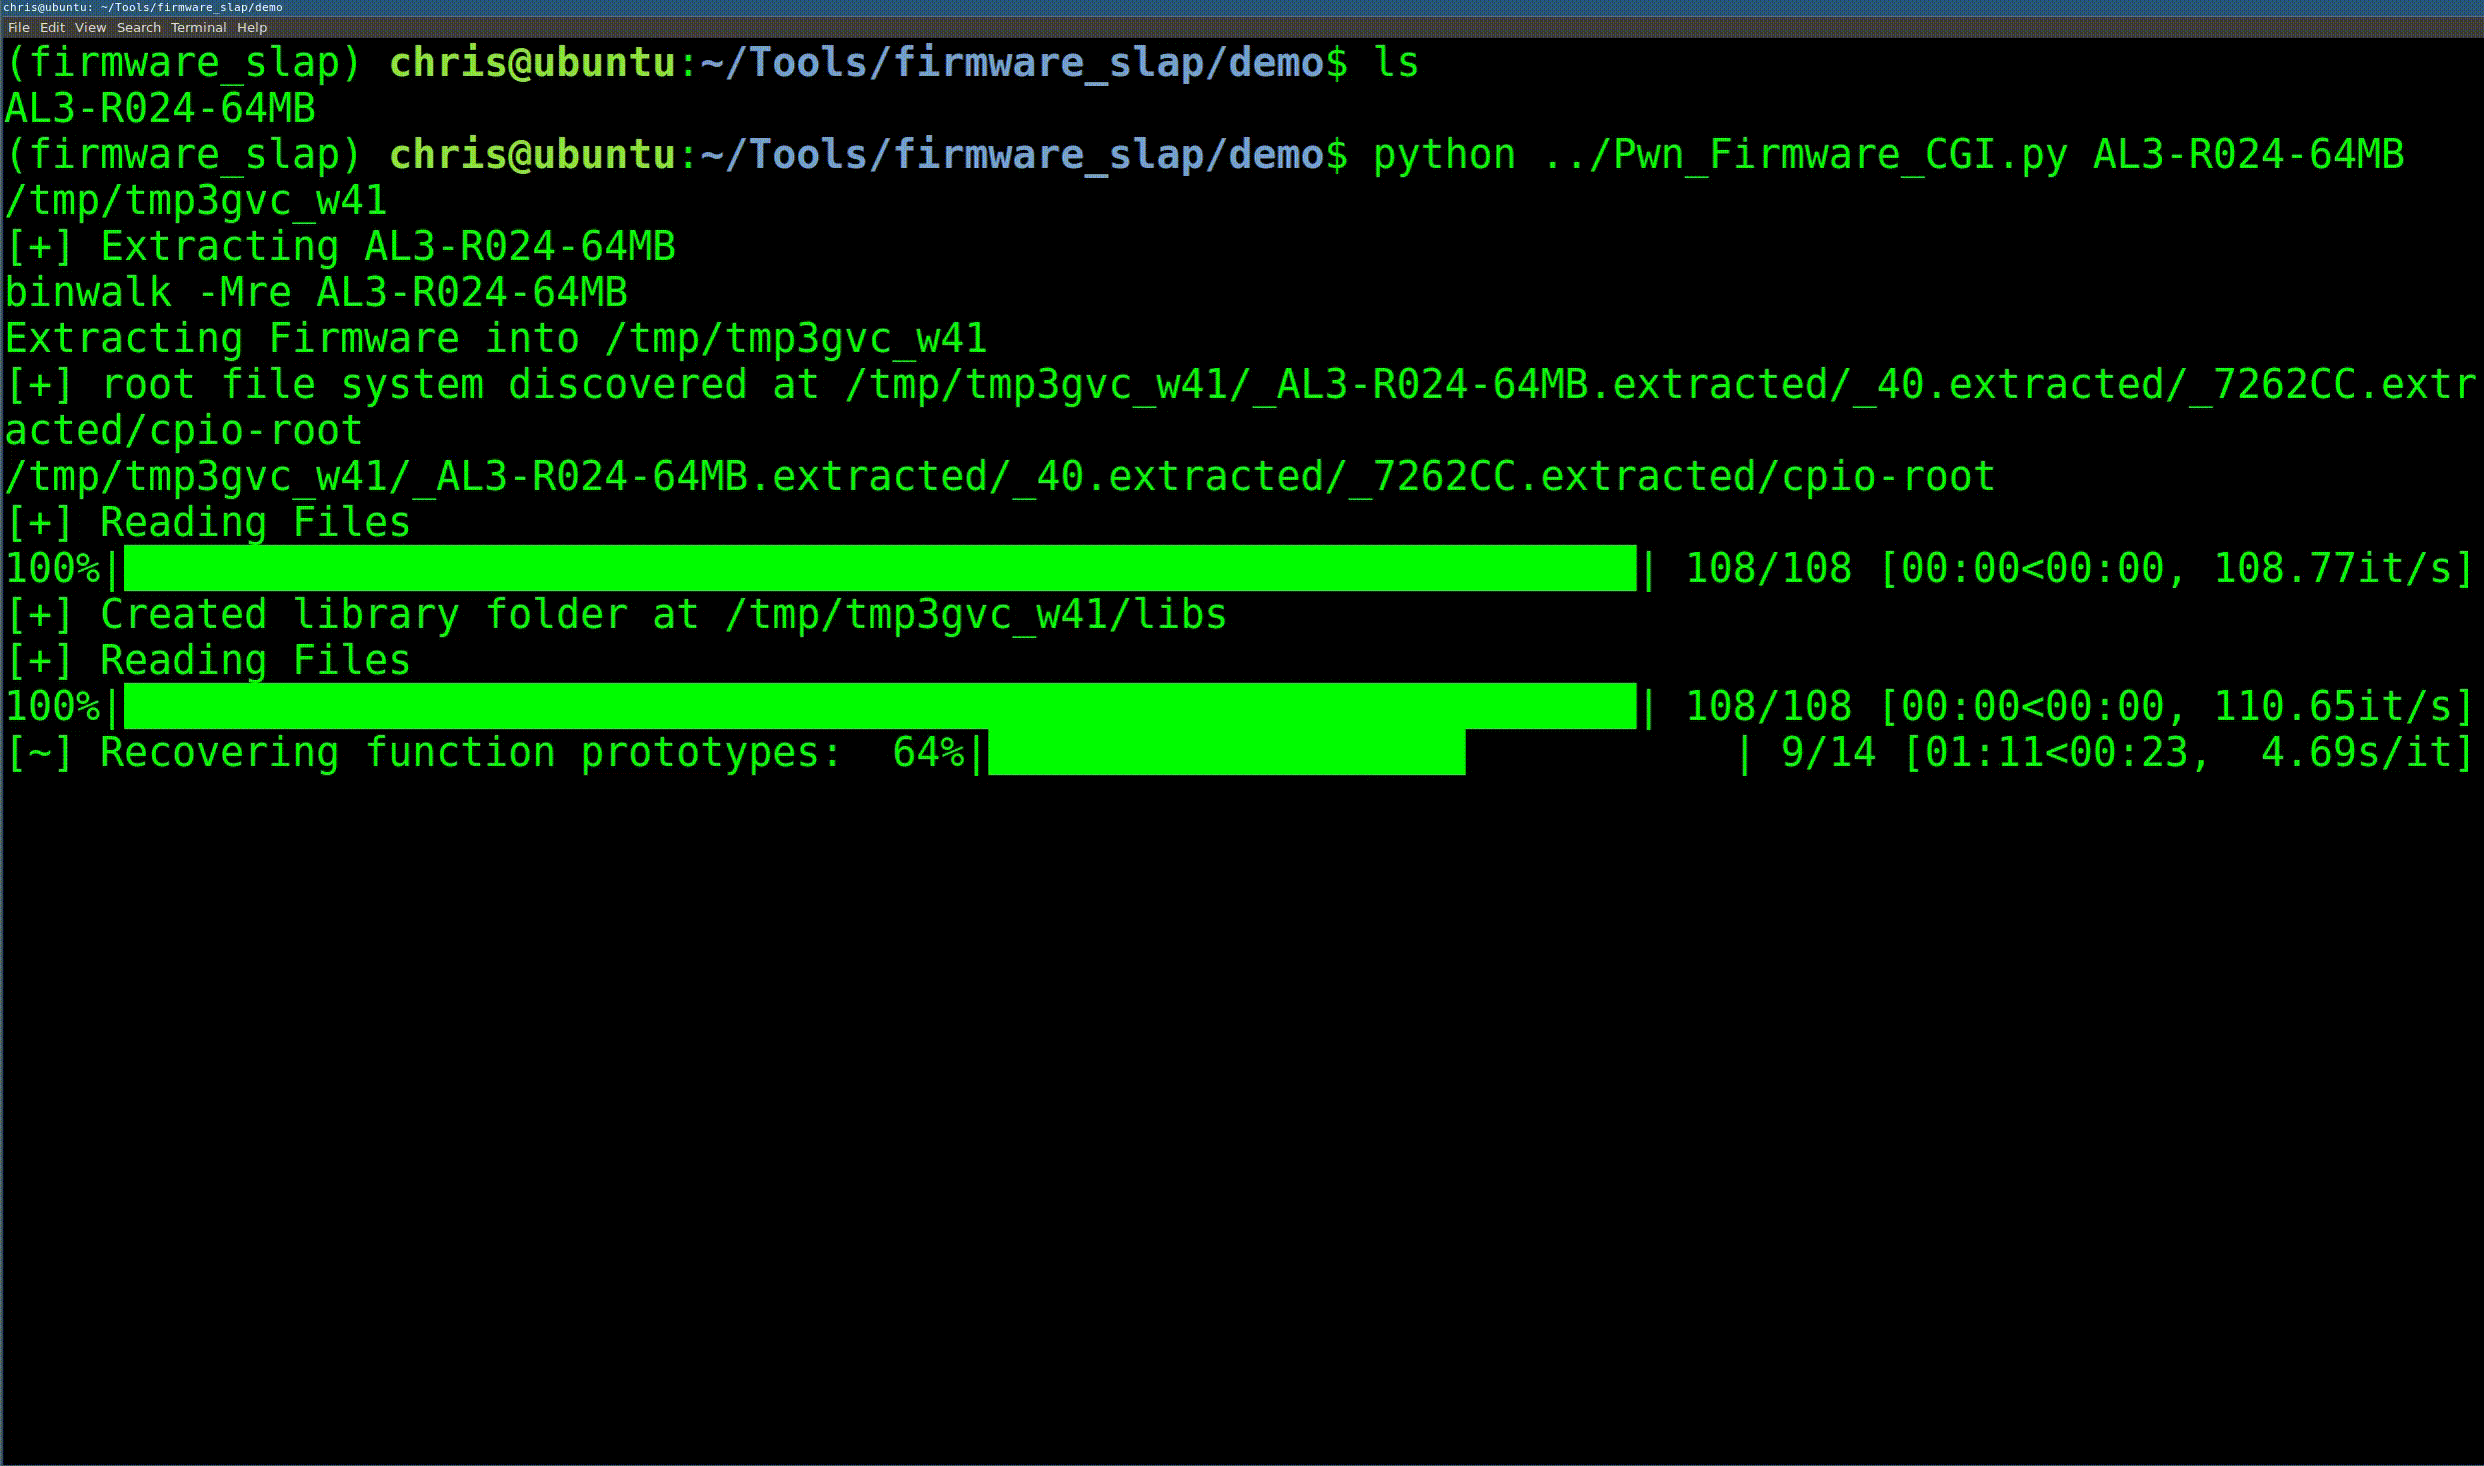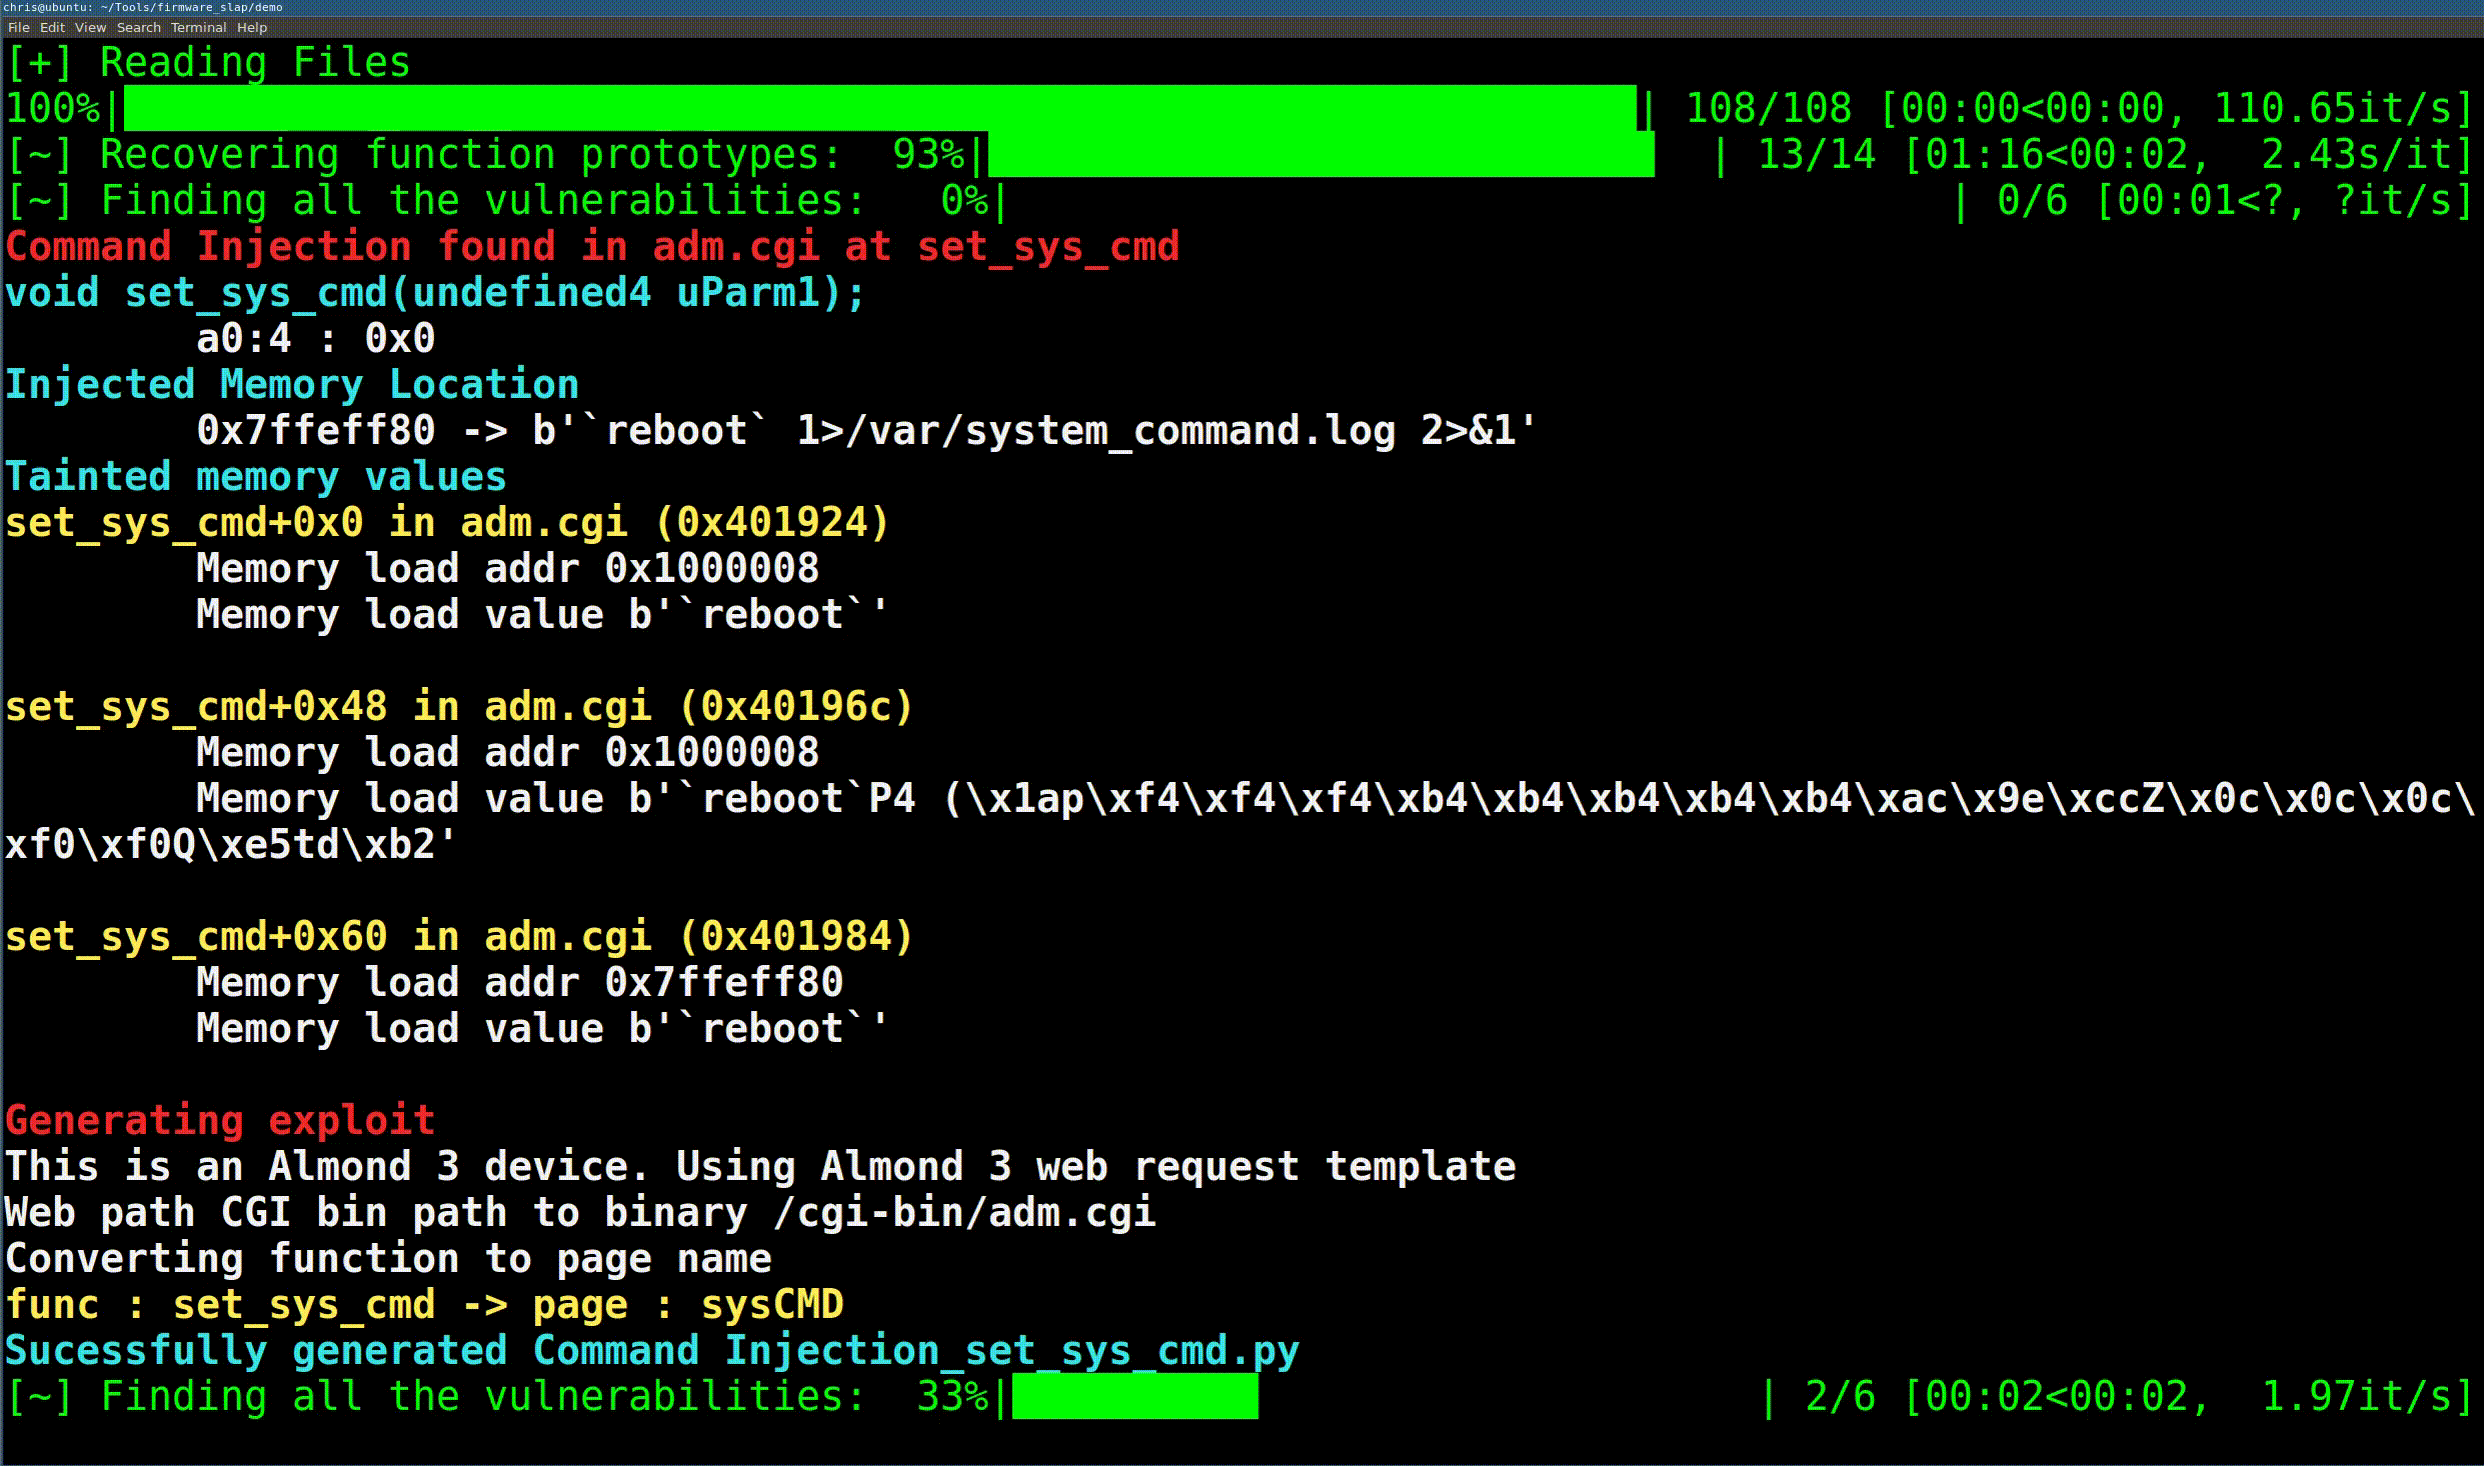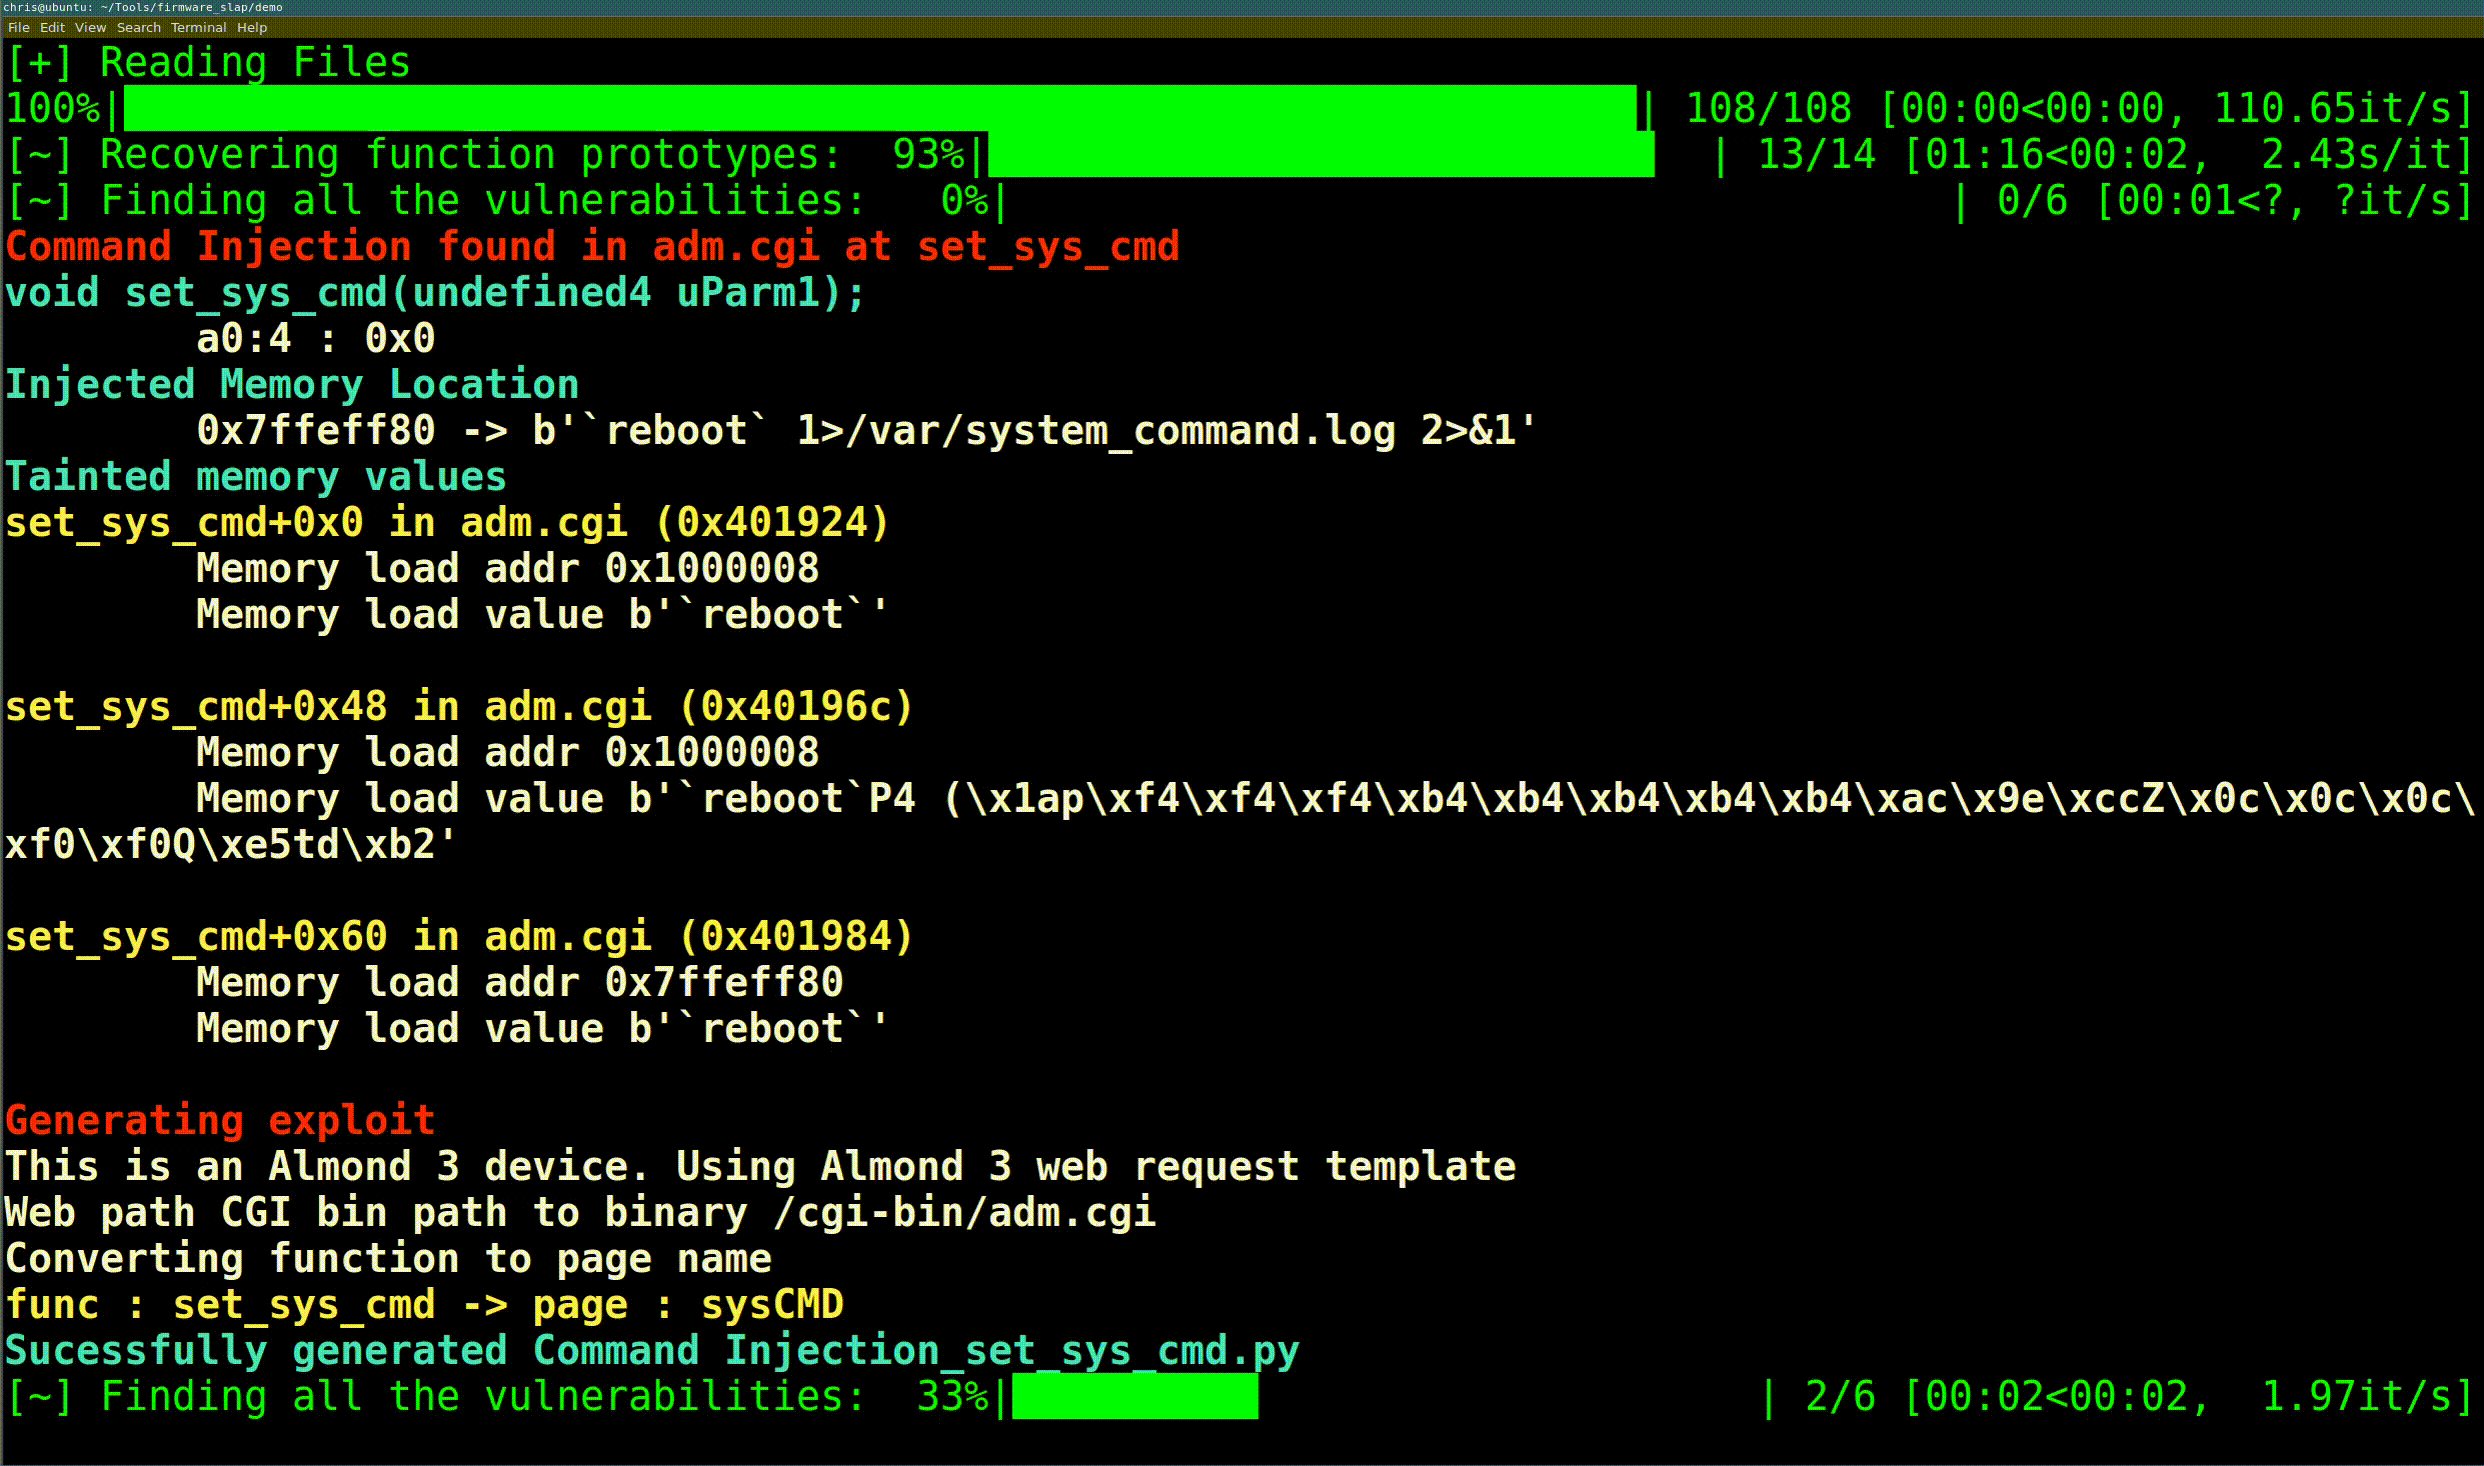 christhecoolhut/firmware_slap
Discovering vulnerabilities in firmware through concolic analysis and function clustering.
 al3xtjames/ghidra-firmware-utils
Ghidra extension for PC firmware reverse engineering, providing loaders for PCI option ROMs, Intel Flash Descriptor, coreboot CBFS, and UEFI firmware…
 dsecurity/efiseek
Ghidra plugin that automates UEFI firmware analysis by identifying known GUIDs, protocols, SMI handlers, and interrupt functions, with headless…
 quarkslab/binbloom
Raw binary firmware analysis software
 flopz-project/flopz
Pure Python assembler toolkit for creating shellcode, dynamically patching binaries, and instrumenting firmware images for debugging and fuzzing on…
 doctormord/philips-pm-5139-5138a-5136-firmware-project
Firmware reverse engineering of the Philips PM5139 / PM5138A / PM5136 function generators: 8051 emulators used as measuring instruments, 35 sections…
 yeggor/uefi_retool
A tool for UEFI firmware reverse engineering
 nnonickreal/openqore
unleash the full power of your BES-based headphones! :)

 theldus/bread
Injectable real-mode x86 debugger for BIOS reverse engineering and arbitrary real-mode code debugging via serial cable, with GDB integration and…
 zx41r/awesome-reverse-engineering-and-malware-analysis
A verified map of reverse engineering and malware analysis. Disassemblers, unpacking, exploit dev, fuzzing, DFIR, and the deep-cut writeups other…
 infobyte/draytek-arsenal
Reverse Engineering and Observability toolkit for Draytek firewalls
 1rhino2/fnprint
match functions in binaries by what they do, not what their bytes look like. behavioral function fingerprinting via microexecution.
 kuleuven-cosic/starlink-fi
Voltage fault-injection modchip for black-box security evaluation of Starlink terminals, bypassing bootloader signature verification to execute…