
FakeMBR
 malwaretech/fakembr
TDL4 style rootkit to spoof read/write requests to master boot record
binary-analysisexploitationmalware-analysis+2
malwaretech/fakembrTDL4 style rootkit to spoof read/write requests to master boot record
 burrowers/garble
Obfuscates Go builds by wrapping the Go toolchain, replacing identifiers, package paths, and position data with hashes and stripping debug and build…
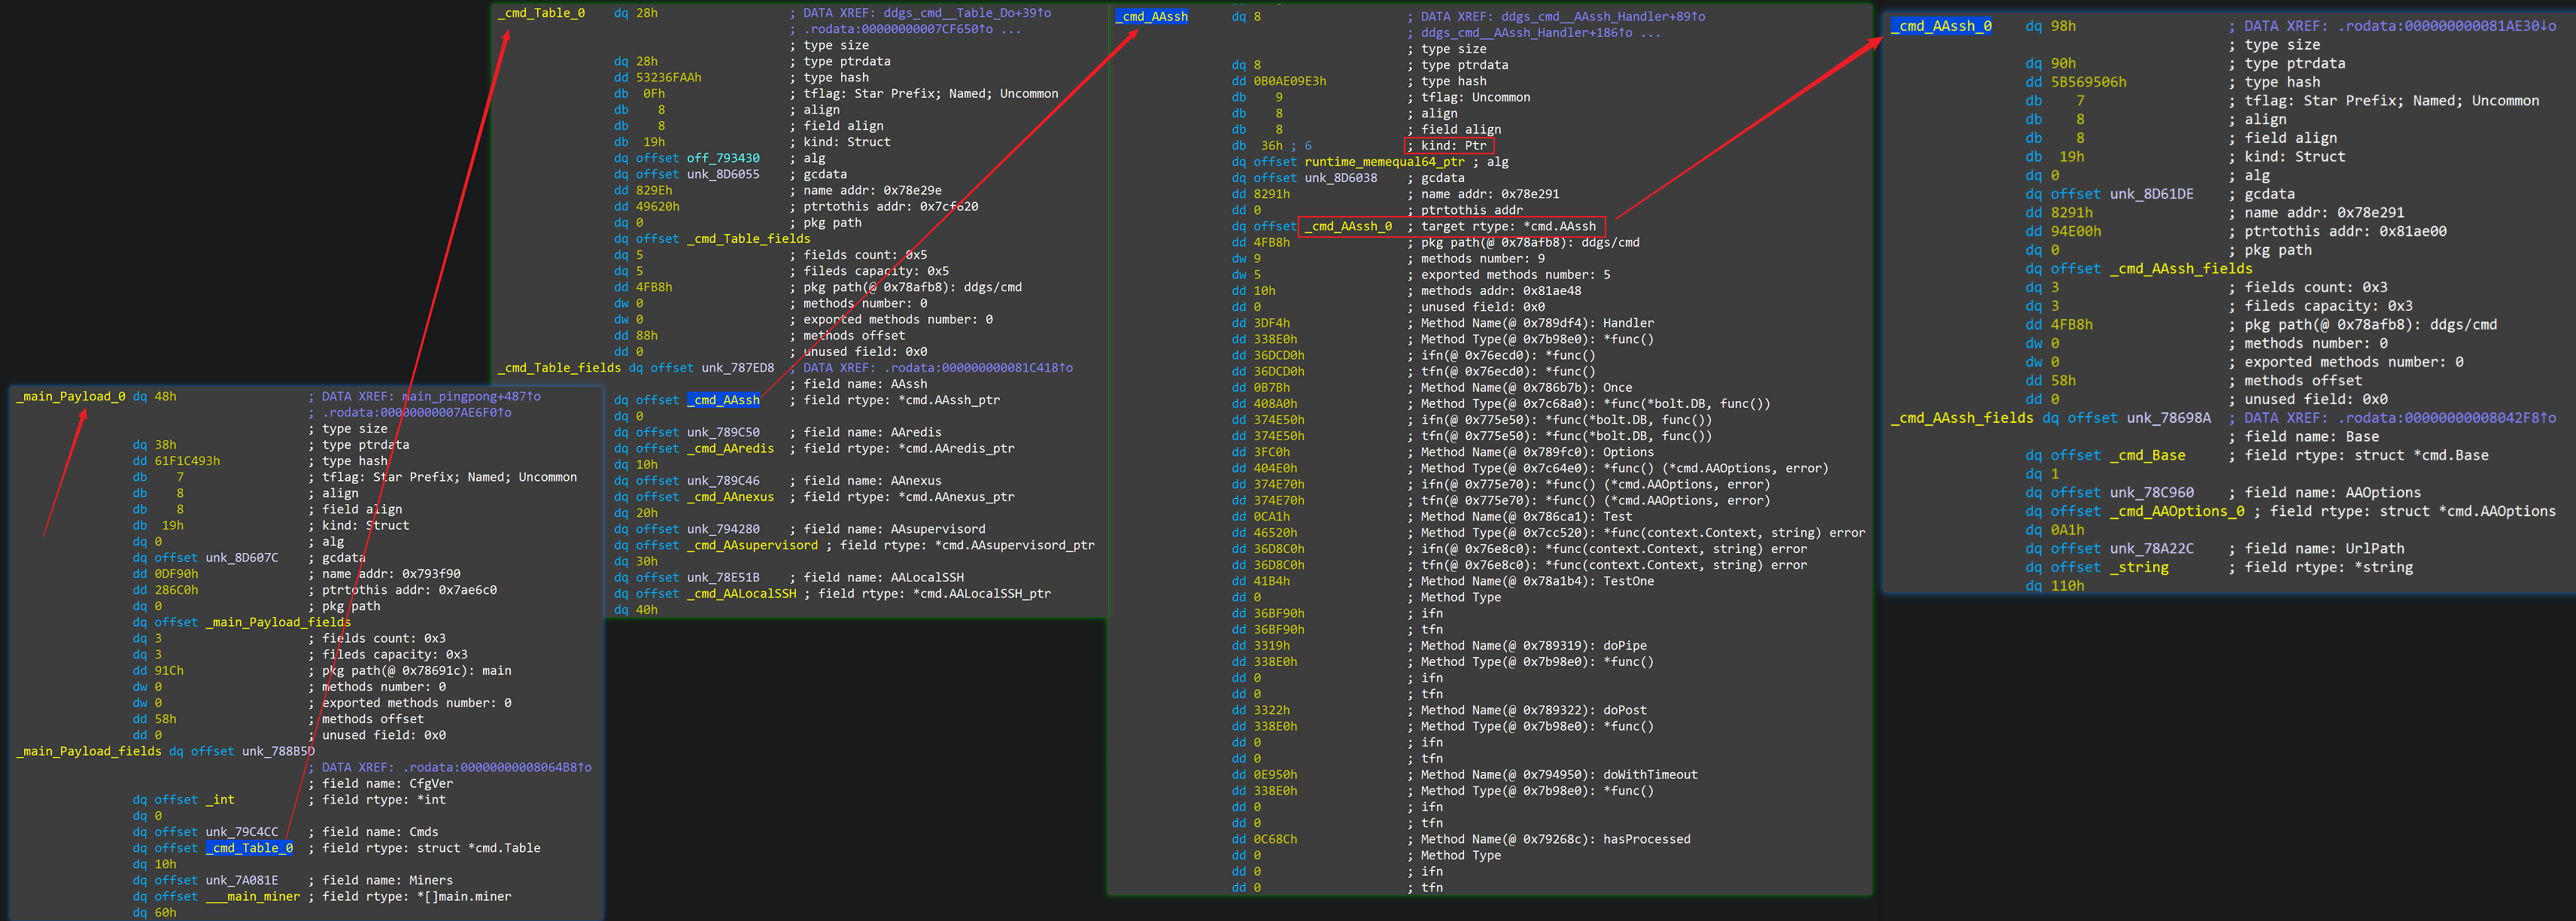 0xjiayu/go_parser
Yet Another Golang binary parser for IDAPro