grapefruit
 chichou/grapefruit
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
android-securitybinary-analysisdynamic-code-analysis+5
1.4k
chichou/grapefruitOpen-source mobile security testing suite for iOS and Android. Previously Passionfruit
 iddoeldor/frida-snippets
Hand-crafted Frida examples
 0xdea/frida-scripts
A collection of my Frida instrumentation scripts to reverse engineer mobile apps and more.
 igio90/dwarf
Full featured multi arch/os debugger built on top of PyQt5 and frida
 chichou/vscode-frida
Unofficial frida extension for VSCode
 romainthomas/the-poor-mans-obfuscator
Binary & scripts associated with "The Poor Man's Obfuscator" presentation
 owasp/mas-crackmes
The MAS Crackmes aka. UnCrackable Apps, a collection of mobile reverse engineering challenges part of the OWASP MAS project.
 reversenseorg/dexcalibur
[Official] Android reverse engineering tool focused on dynamic instrumentation automation leveraging Frida. It disassembles dex, analyzes it…
 federicodotta/ghidra2frida
Ghidra extension bridging static and dynamic analysis via Frida, enabling scriptable runtime instrumentation for reverse engineering binaries on…
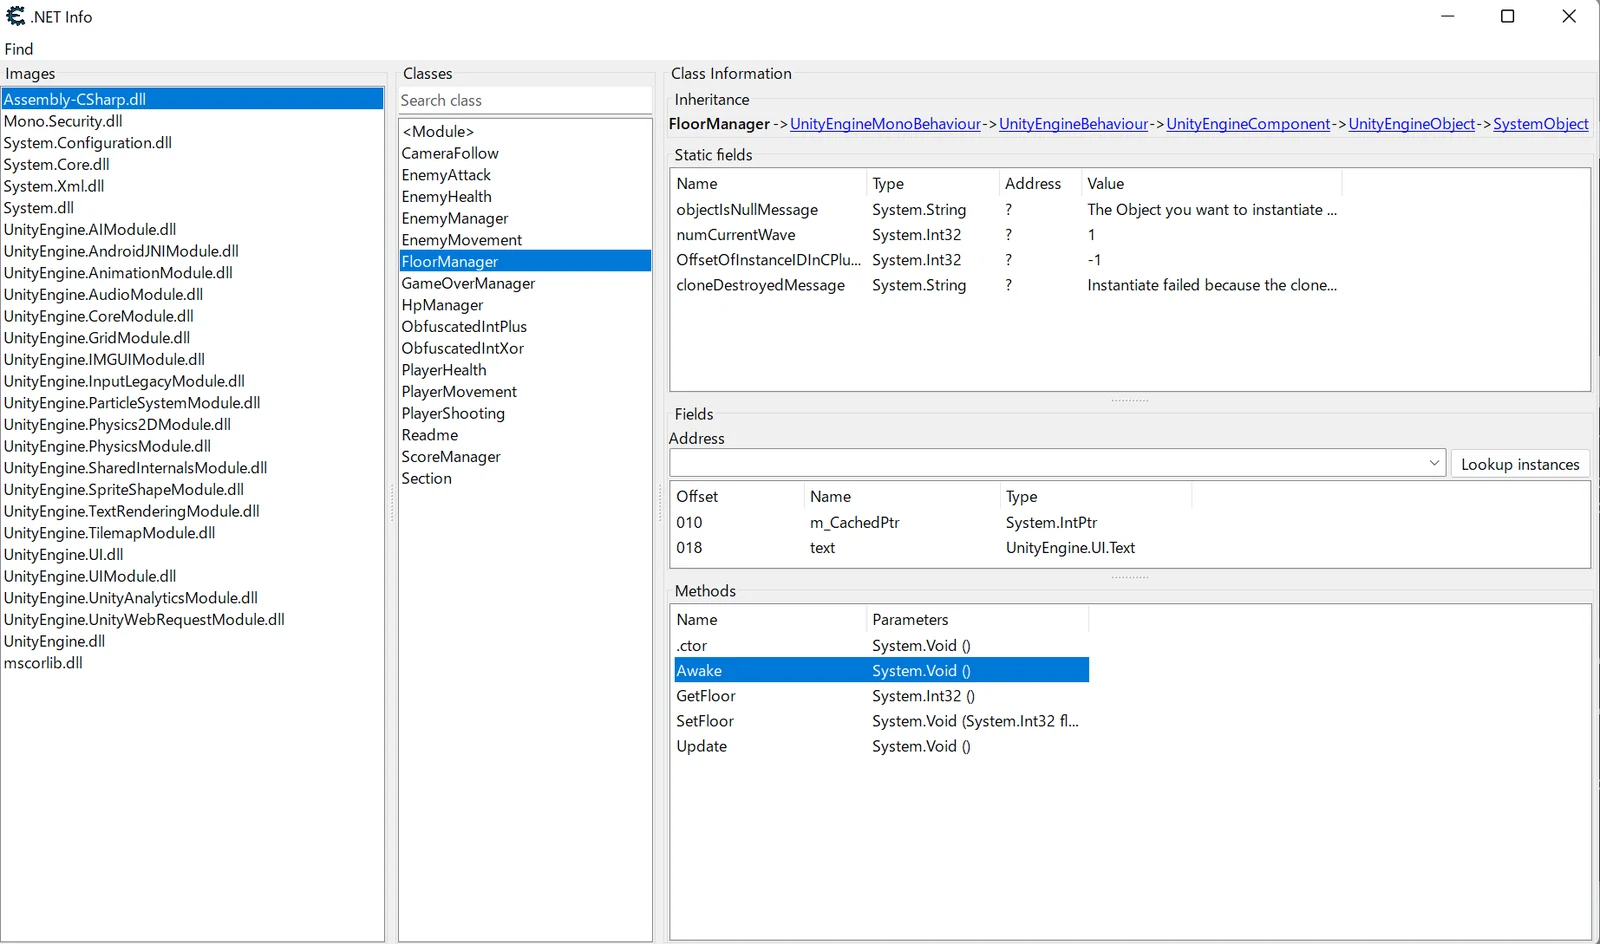 gmh5225/frida-il2cpp-datacollector
Frida-based tool that ports Cheat Engine's MonoDataCollector to Android and iOS, enabling runtime Mono/IL2CPP data collection and memory inspection…
 spiralbl0ck/learning-history-of-cff-bug-in-iphone
Dive into CFF font and coincidently learn about a bof in cff parsing from some jailbreak. just for fun
 skylot/jadx
Command-line and GUI tool for decompiling Android Dex and APK files into readable Java source code, with resource decoding, deobfuscation, and Smali…
 ibotpeaches/apktool
A tool for reverse engineering Android apk files
 frida/frida
Main repo for hosting release binaries
 konloch/bytecode-viewer
A Java 8+ Jar & Android APK Reverse Engineering Suite (Decompiler, Editor, Debugger & More)
 wtsxdev/reverse-engineering
List of awesome reverse engineering resources
 pxb1988/dex2jar
Tools to work with android .dex and java .class files