
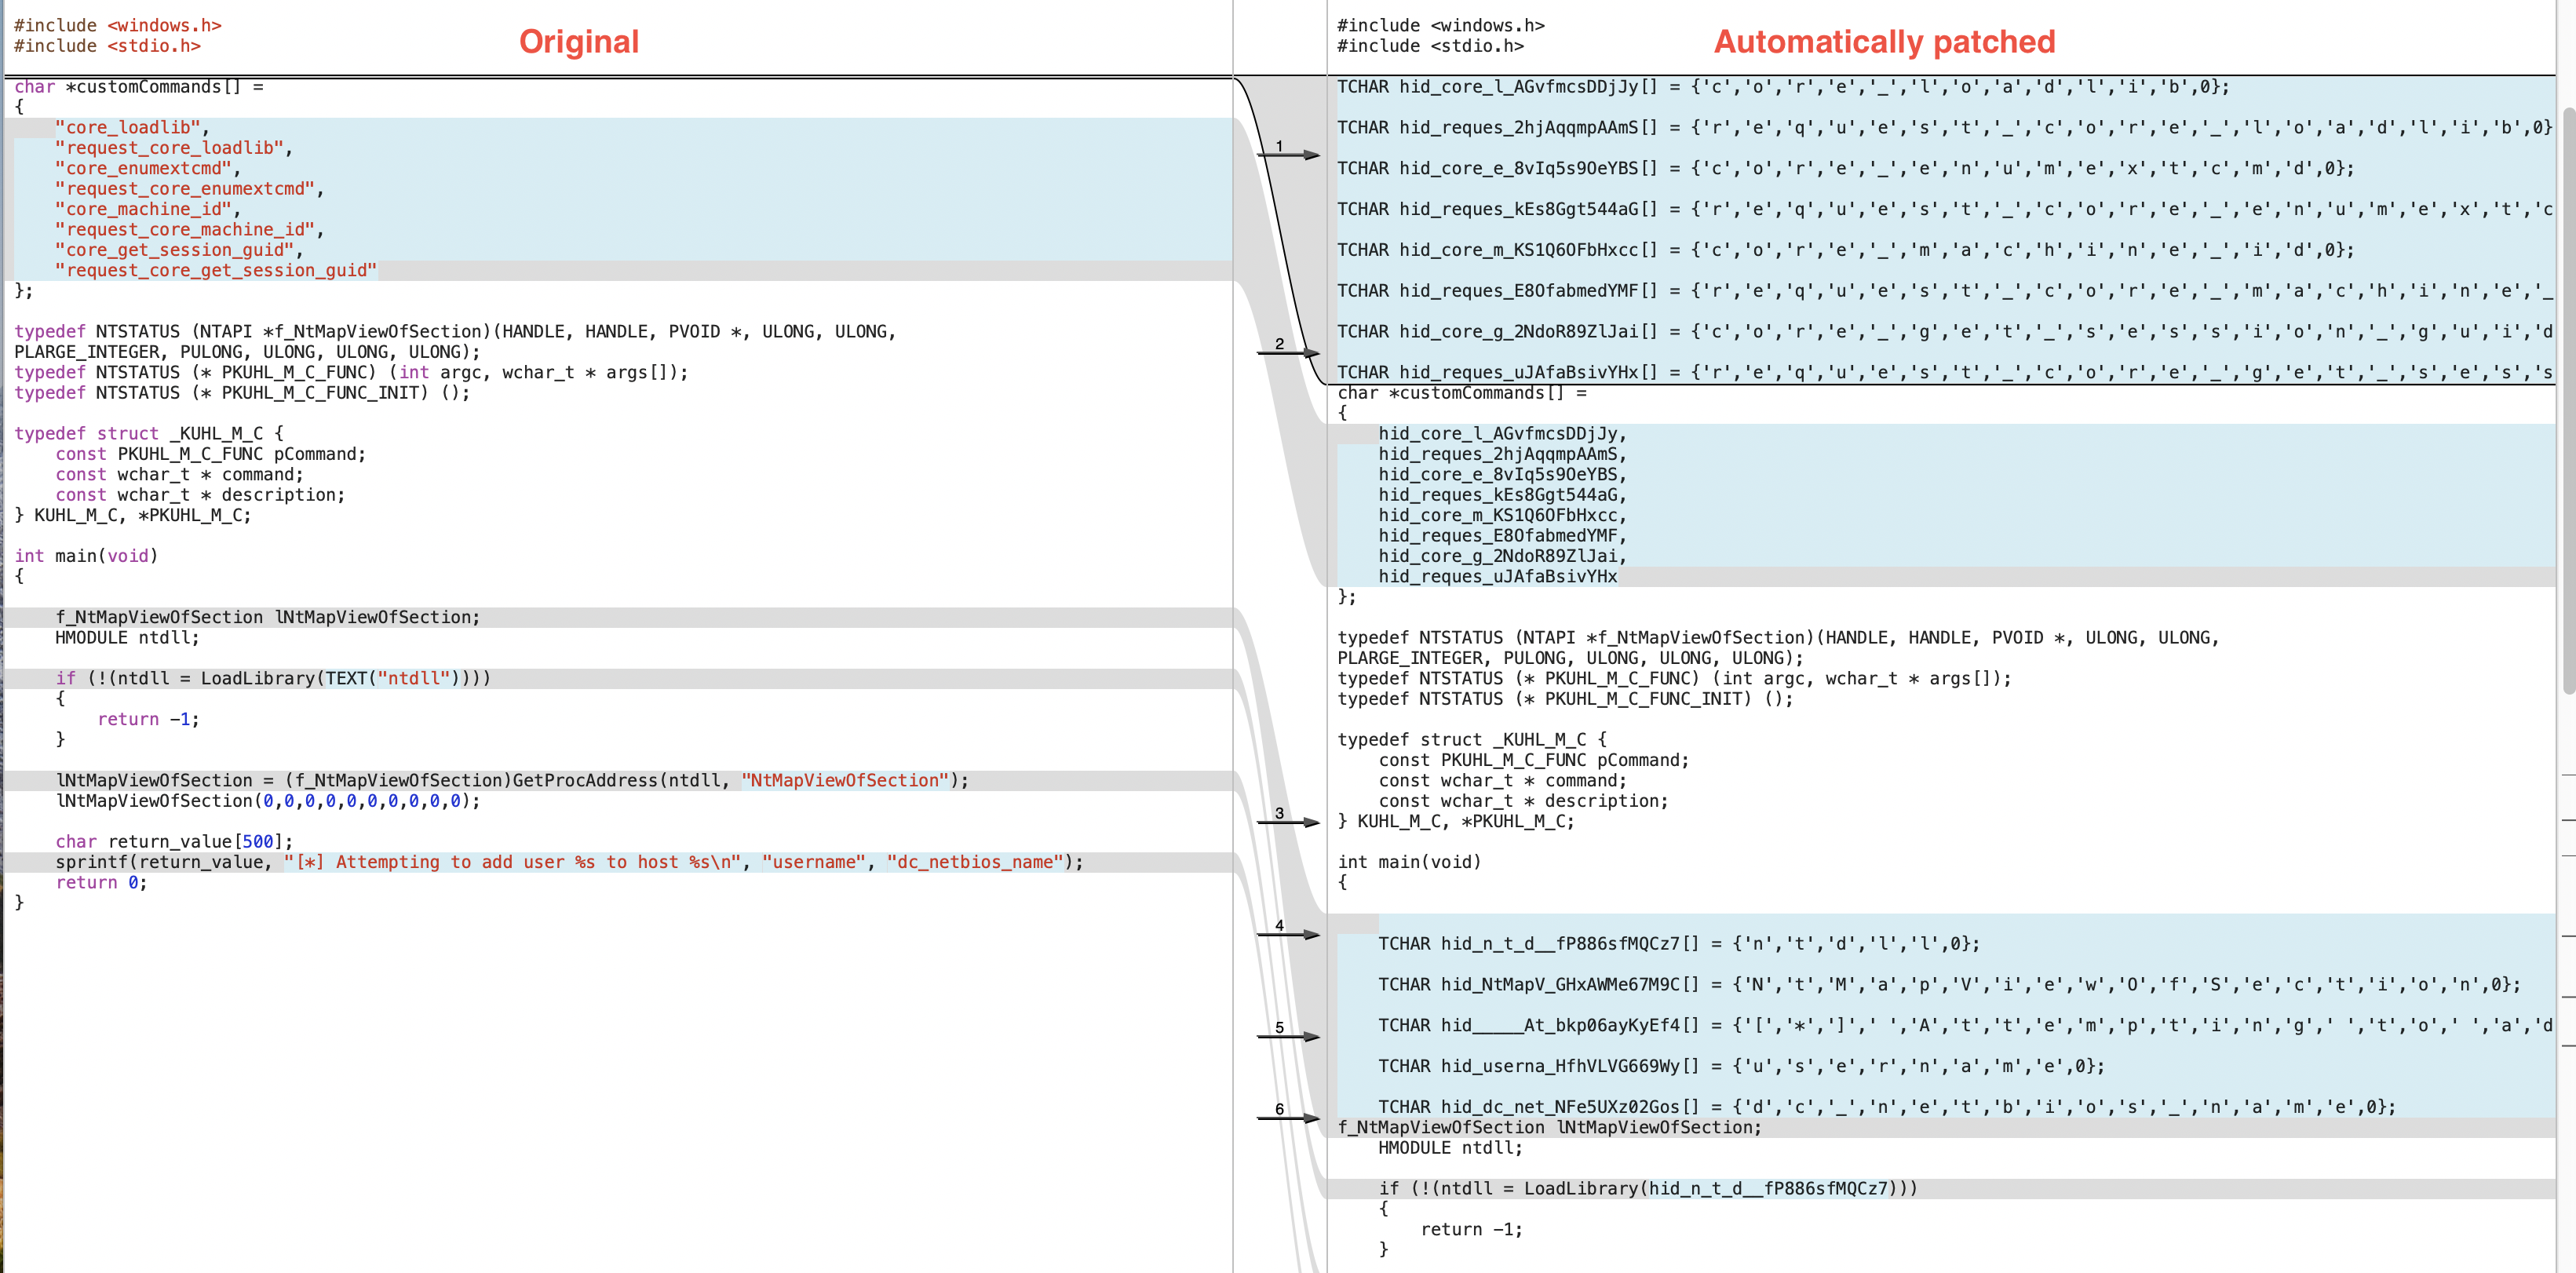
avcleaner
 scrt/avcleaner
C/C++ source obfuscator for antivirus bypass
binary-analysispayload-generation
scrt/avcleanerC/C++ source obfuscator for antivirus bypass
 hasherezade/exe_to_dll
Converts a EXE into DLL
 wetw0rk/sickle-pdk
Sickle - Payload Development Kit
 mertdas/privkit
PrivKit is a simple beacon object file that detects privilege escalation vulnerabilities caused by misconfigurations on Windows OS.
 cybereason/siofra
Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…
 phith0n/zkar
Go-based Java serialization protocol analyzer that parses, dumps, and generates deserialization payloads with ysoserial gadget support and a library…
 czs108/windows-pe-packer
🗜️ A packer for Windows x86 executable files written in C and Intel x86 Assembly. The new file after packing can obstruct reverse…
 risksense-ops/cve-2016-6366
Public repository for improvements to the EXTRABACON exploit
 s3cur3th1ssh1t/nimgetsyscallstub
Dynamically extracts fresh syscall stubs from ntdll.dll to evade signature-based detection, with a shellcode execution template for Nim-based…
 gamozolabs/elfloader
An architecture-agnostic ELF file flattener for shellcode
 blacknbunny/shellcode2assembly
💻 ARCH : ARM, ARM64, MIPS, PPC, X86
 namazso/dll-proxy-generator
Generate a proxy dll for arbitrary dll
 own2pwn/r0ak
r0ak ("roak") is the Ring 0 Army Knife -- A Command Line Utility To Read/Write/Execute Ring Zero on for Windows 10 Systems
 j0wii/cve-2026-97798_lpe_windows
CVE-2026-97798 PoC — WER Time Travel Debugging argument injection to SYSTEM (Windows 11 LPE), with an adaptive faultrep.dll resolver.
 sizeable-bingus/massdriver
Proxies sensitive API calls from shellcode to artifacts for CET-compatible clean call stacks, enabling stealthy payload execution and call stack…
 shellkraft/anvil
Anvil is a runtime-first attack surface assessment tool for Windows thick client applications, built for penetration testers and security researchers…
 exploiteoom/cve-2026-31431
Exploit for CVE-2026-31431 that escalates privileges by altering user ID, with a verification script and mitigation instructions for the algif_aead…
 s1eezer/cve-2026-8069
Technical write-up and proof-of-concept for CVE-2026-8069, a local privilege escalation in Acer NitroSense and PredatorSense services, exploiting a…