
Archived
vmp2
 aftermathlabs/vmp2
Unpack and deobfuscate VMProtect 2 protected binaries with an emulation-based VM explorer, handler profiler, and experimental LLVM recompiler for…
binary-analysiscode-analysisdynamic-code-analysis+3
 0xdea/frida-scripts
A collection of my Frida instrumentation scripts to reverse engineer mobile apps and more.
 nccgroup/blackboxprotobuf
Blackbox Protobuf is a set of tools for working with encoded Protocol Buffers (protobuf) without the matching protobuf definition.
 ed1s0nz/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 aipentest/cyberstrikeai
The system of action for AI-native cybersecurity—where intent becomes governed execution, evidence becomes operational memory, and every operation…
 dere-ad2001/frida-labs
The repo contains a series of challenges for learning Frida for Android Exploitation.
 rr-debugger/rr
Record and replay framework for deterministic debugging of multi-threaded applications, enabling reverse execution, hardware watchpoints, and…
 jaf0rk/cve-2026-3909
Proof-of-concept exploit for CVE-2026-3909, a Chromium Skia out-of-bounds vulnerability, with patches and crash analysis for reliable triggering in…
 kaisonox/apiscope
An API hooking framework for intercepting and monitoring Windows applications
 vighnesh91/omnisec-hex
Browser-local security monorepo with six modules for mobile APK/IPA triage, client-side DAST fuzzing, OSINT directories, offline AI threat scoring,…
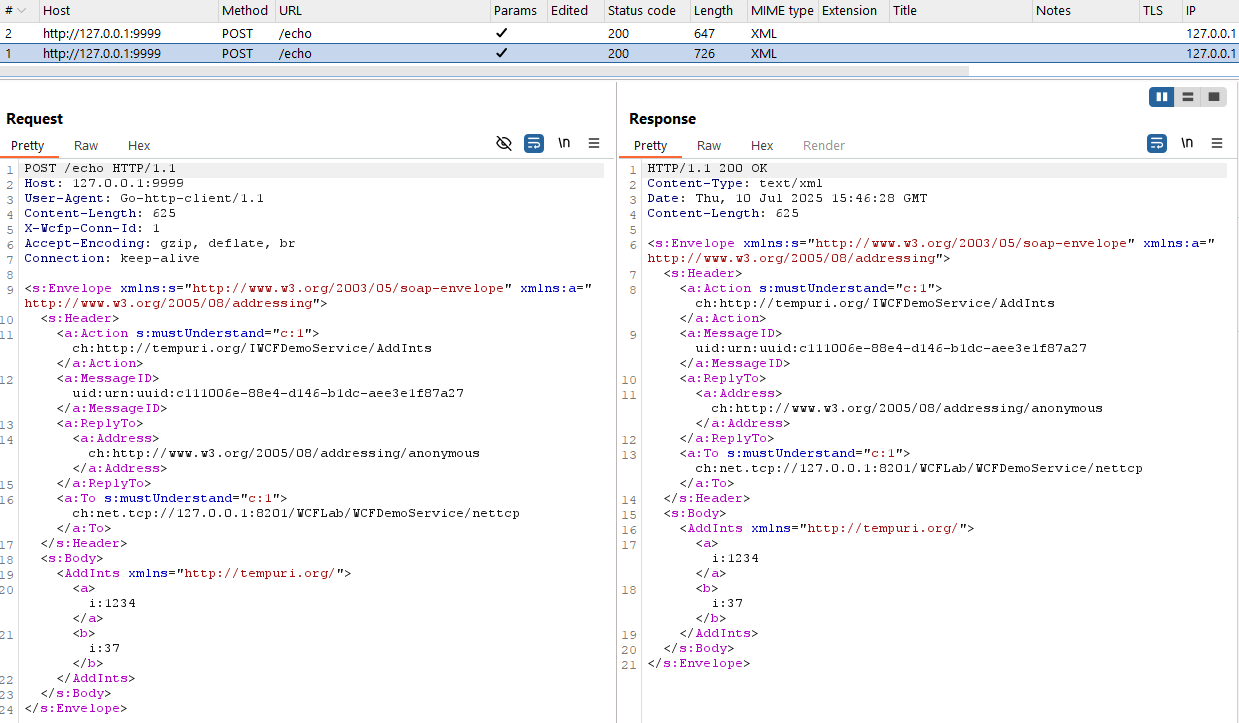 syss-research/wcfproxy
A proxy for net.tcp-based WCF traffic.
 sandi-go/ps-2017-13---cve-2018-9950
Proof-of-concept for CVE-2018-9950, an out-of-bounds read vulnerability in Foxit Reader/PhantomPDF leading to information disclosure and potential…
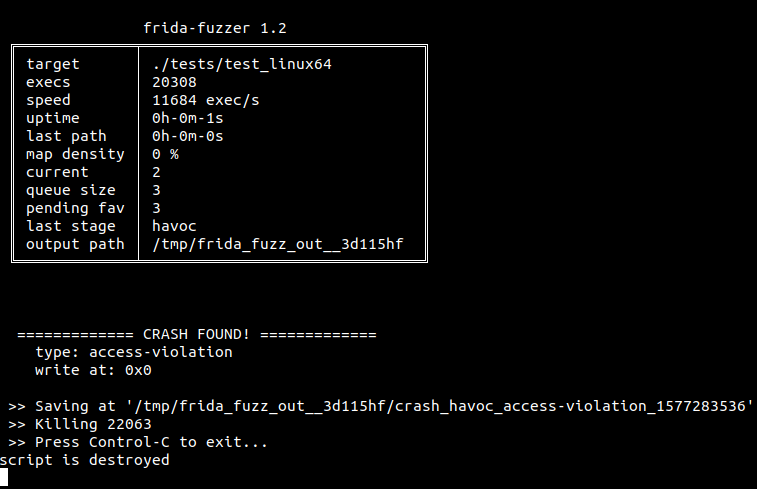 andreafioraldi/frida-fuzzer
This experimetal fuzzer is meant to be used for API in-memory fuzzing.
 gmh5225/enigma-
C++ reimplementation of Ghidra's analytical core without JVM dependencies, providing embeddable binary analysis, Pcode/Sleigh foundations, and…
 tca-iscas/cooper-ndss-2022
A tool for effective testing the binding layer of scripting languages
 hasherezade/pesieve-go
Golang bindings for PE-sieve
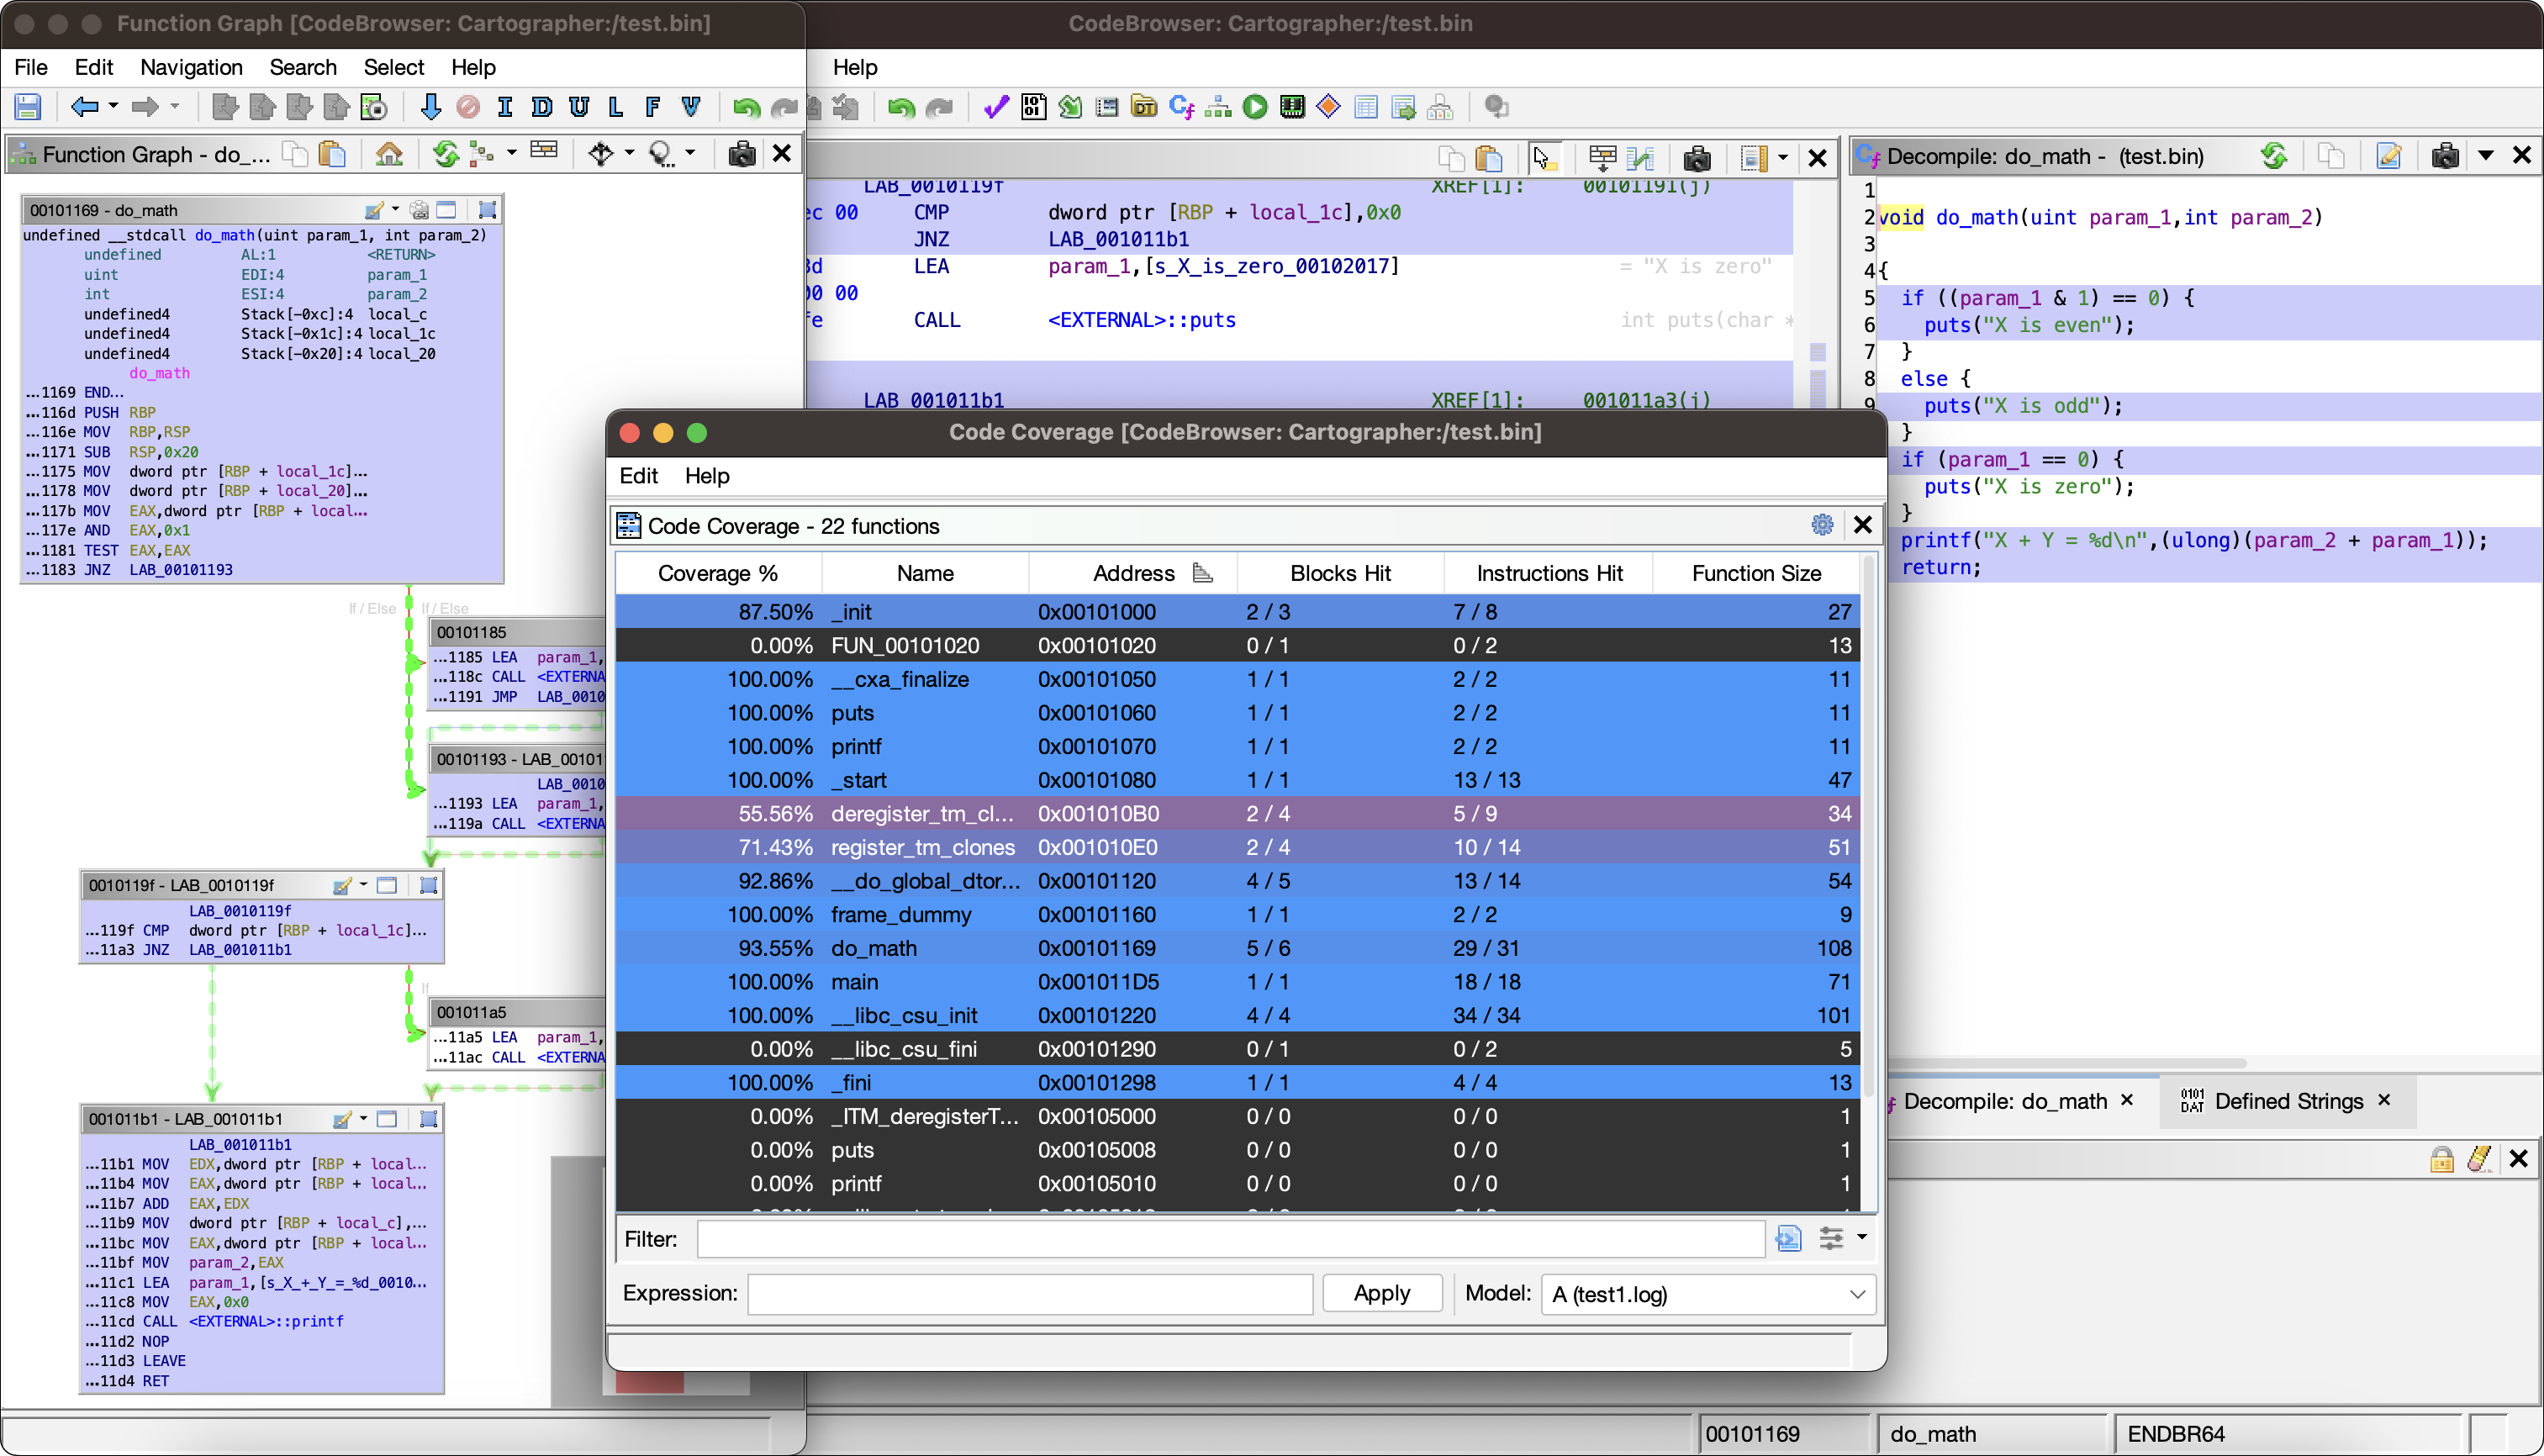 nccgroup/cartographer
Code Coverage Exploration Plugin for Ghidra
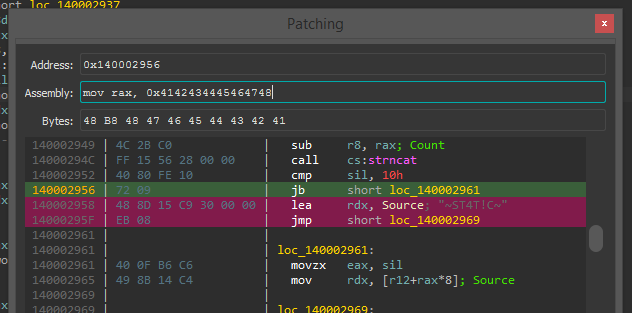 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro