
pev
 merces/pev
Moved to https://github.com/mentebinaria/readpe
binary-analysismalware-analysisreverse-engineering+1
merces/pevMoved to https://github.com/mentebinaria/readpe
 mracumen/cve-2021-40444
Microsoft-Office-Word-MSHTML-Remote-Code-Execution-Exploit
 gmh5225/driver-keattachprocess-kedetachprocess-rebuild
Rebuild of Windows kernel driver functions KeAttachProcess and KeDetachProcess, used for process attachment and anti-cheat bypass research.
 synacktiv/pridelocker-analysis
This repository contains a IDA Python script to recover PrideLocker ESX encryptor strings and a YARA rule
 llgsjsm/cve-2026-3008
Technical analysis and proof-of-concept for CVE-2026-3008, a format string injection in Notepad++ 8.9.3 via nativeLang.xml, enabling denial of…
 joakimbulow/cve-2026-23907
Proof-of-concept exploit for Apache PDFBox path traversal vulnerability (CVE-2026-23907), demonstrating arbitrary file write via malicious PDFs with…
 mohitsinghpapola/cve-2023-20052
Fixed Docker build for CVE-2023-20052 ClamAV XXE exploit. Resolves OpenSSL 3.0 compilation errors using Ubuntu 18.04 with OpenSSL 1.0 for…
 thunderstrike9090/conflicker_analysis_scripts
Scripts to analyze conflicker worm which exploits famous netapi vulnerability (CVE-2008-4250) i.e MS08-067
 blunden/unacev2.dll-cve-2018-20250
A version of the binary patched to address CVE-2018-20250
 dah4k/cve-2024-3094
Proof-of-concept and analysis tools for CVE-2024-3094, the XZ Utils backdoor vulnerability, including detection and exploitation scripts.
 morfeen01/cve-2017-1182-tn
Malware Analysis Testing
 weltregie/liblzma-scan
Scans liblzma from xu-utils for backdoor (CVE-2024-3094)
 nemo22/retrokit
Headless-Ghidra toolkit for reverse engineering 32-bit DOS and Win32 games (1993-2010): own LE/LX loader, Watcom calling conventions, library…
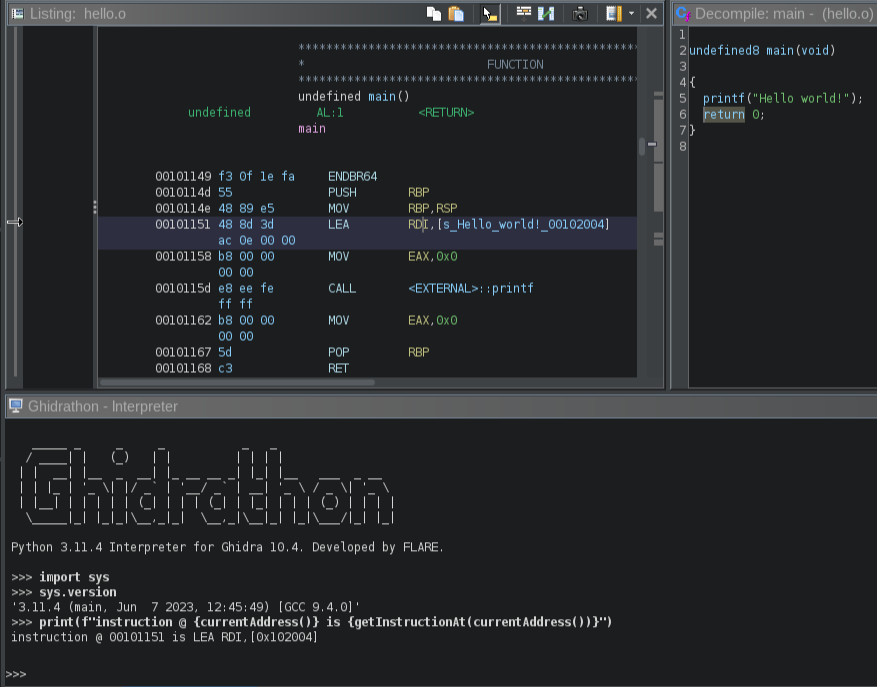 mandiant/ghidrathon
The FLARE team's open-source extension to add Python 3 scripting to Ghidra.
 memn0ps/illusion-rs
Rusty Hypervisor - Windows UEFI Blue Pill Type-1 Hypervisor in Rust (Codename: Illusion)