

santa
 northpolesec/santa
A binary and file access authorization system for macOS.
authentication-authorizationbinary-analysisdefensive-tools+2
788
northpolesec/santaA binary and file access authorization system for macOS.
 noobpk/frida-ios-hook
A tool that helps you easy trace classes, functions, and modify the return values of methods on iOS platform
 t00sh/rop-tool
A tool to help you write binary exploits
 zeze-zeze/ioctlance
A tool that is used to hunt vulnerabilities in x64 WDM drivers
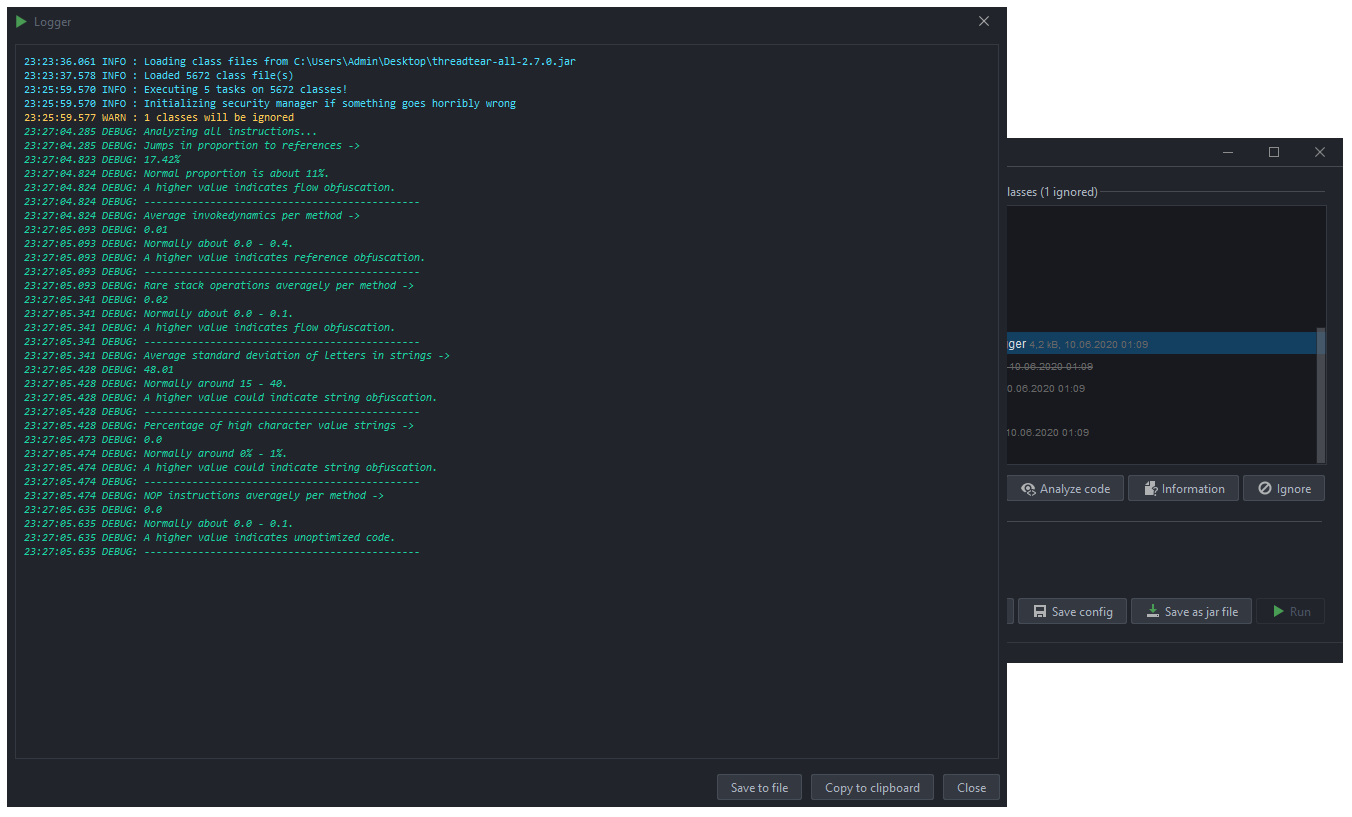 loerting/threadtear
Multifunctional java deobfuscation tool suite
 mildsunrise/protobuf-inspector
🕵️ Tool to reverse-engineer Protocol Buffers with unknown definition
 therealdreg/anticuckoo
A tool to detect and crash Cuckoo Sandbox
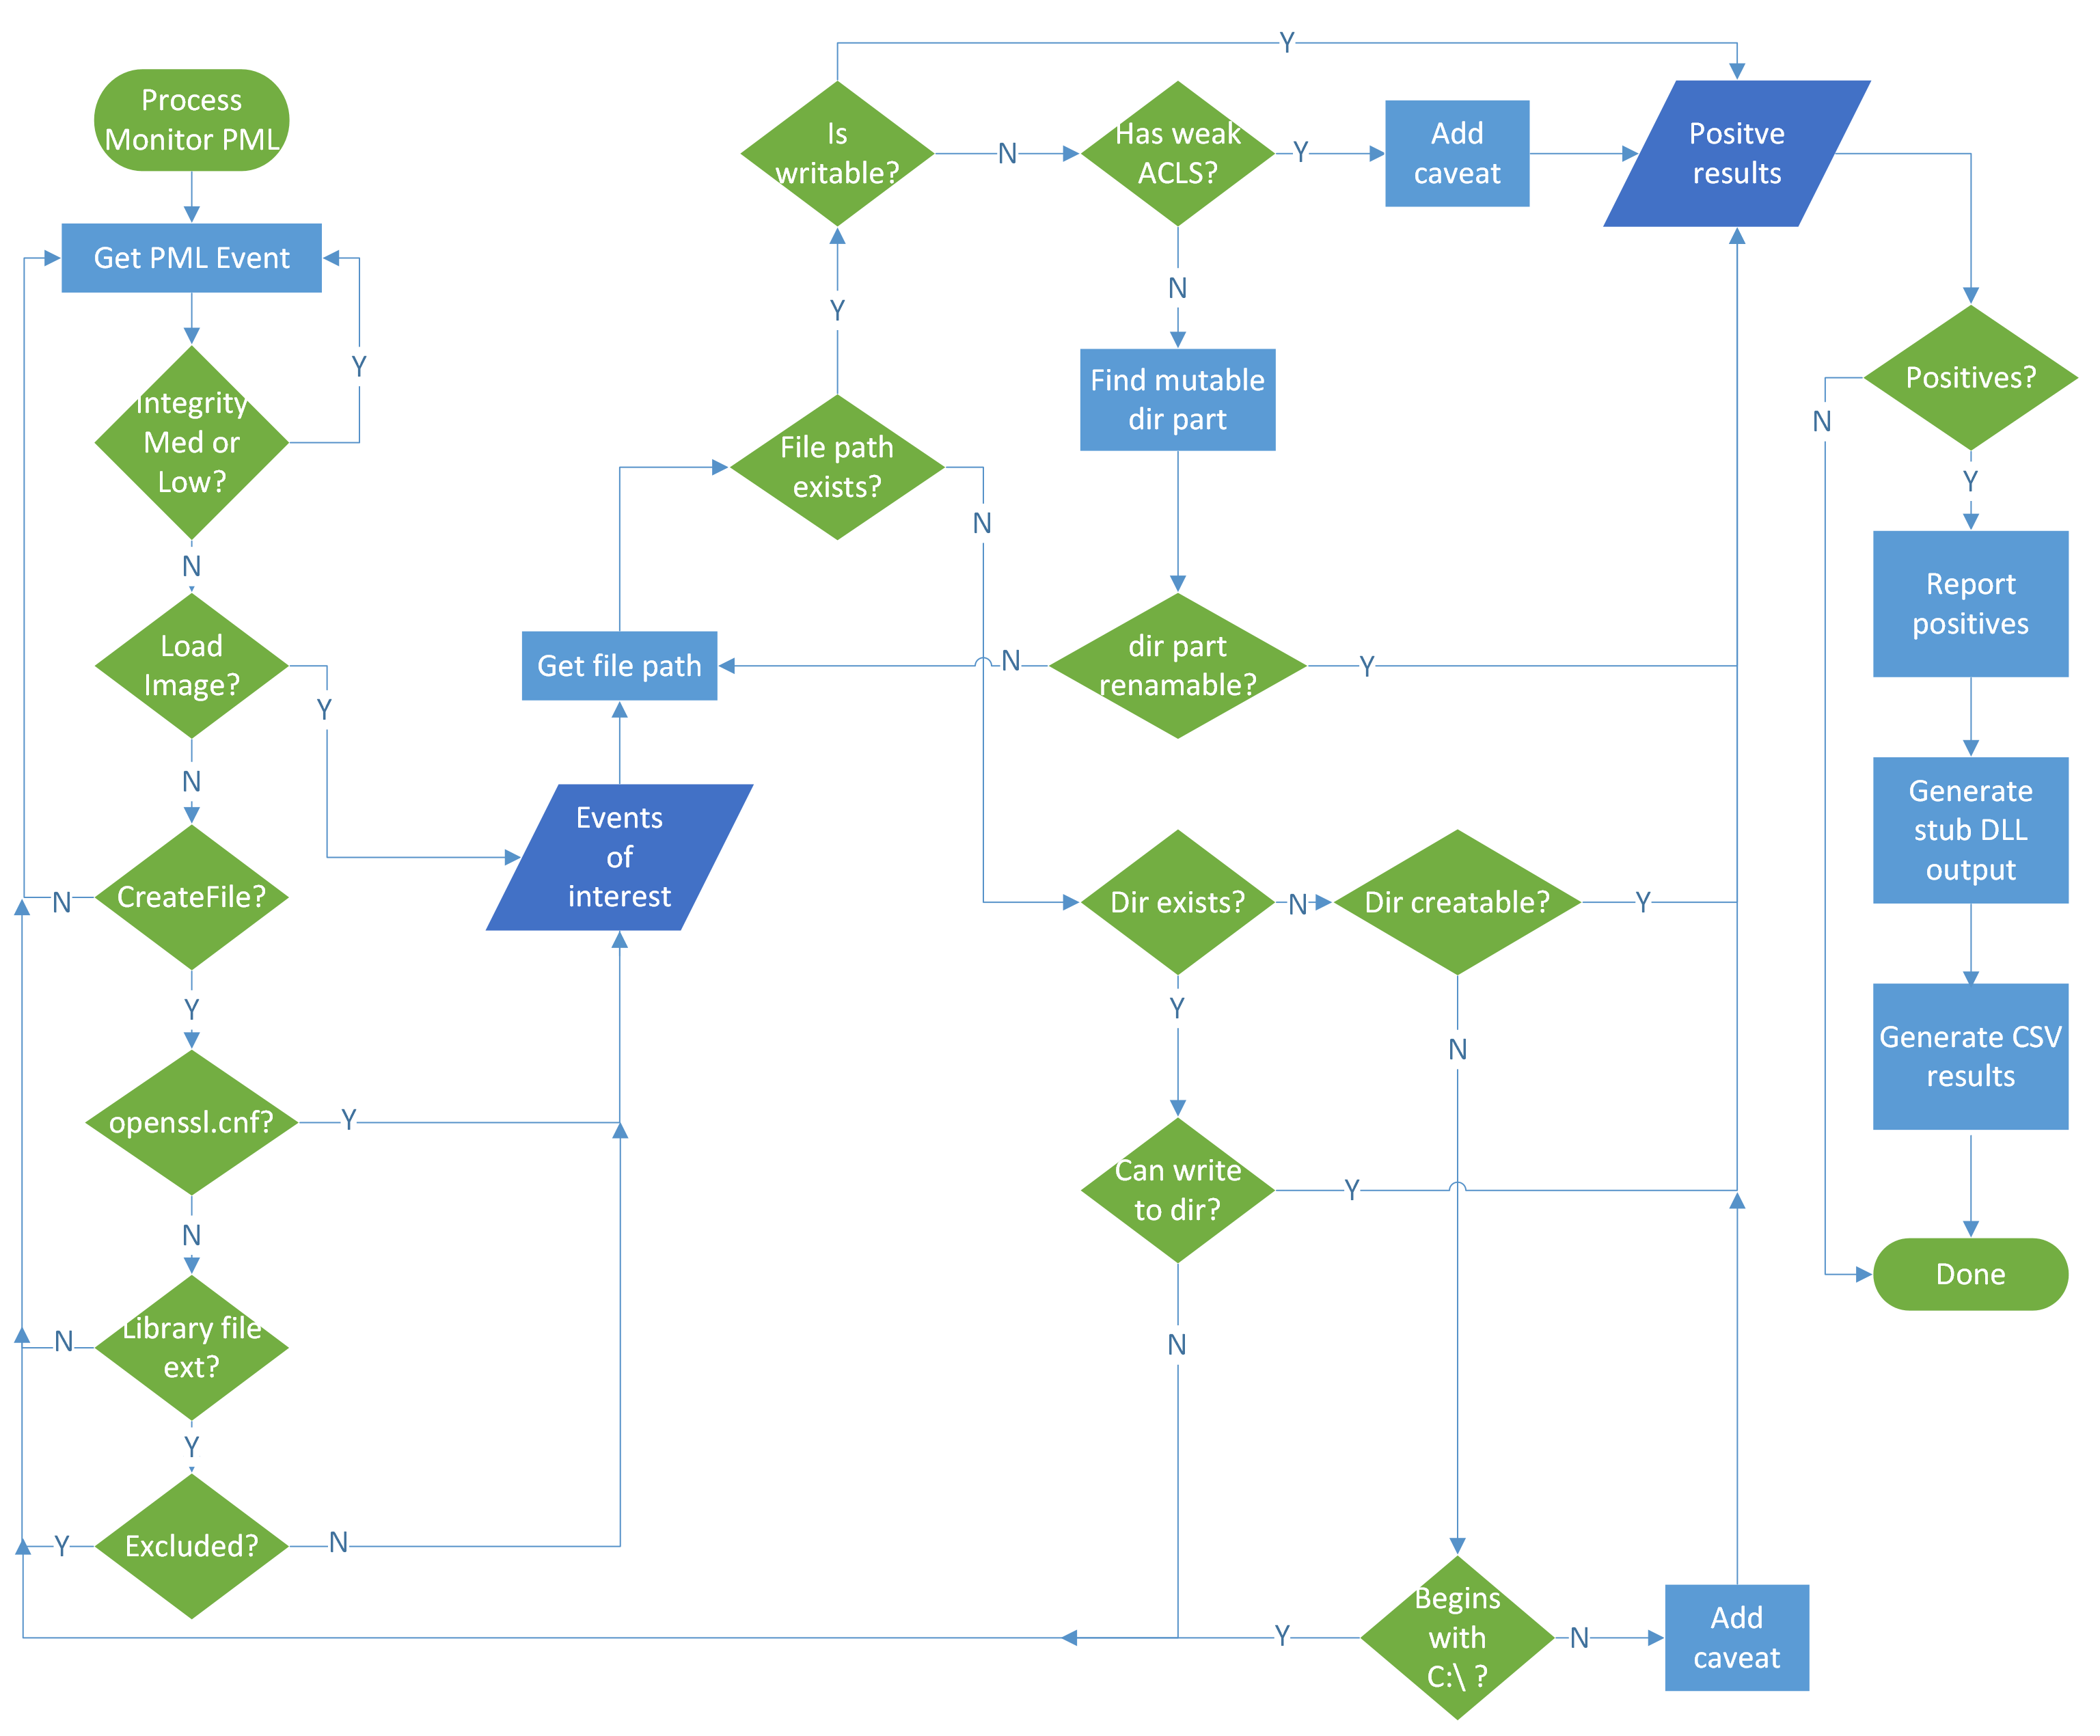 vu-ls/crassus
Windows privilege escalation discovery tool that parses Process Monitor boot logs to identify DLL hijacking, weak ACLs, and other elevation paths,…
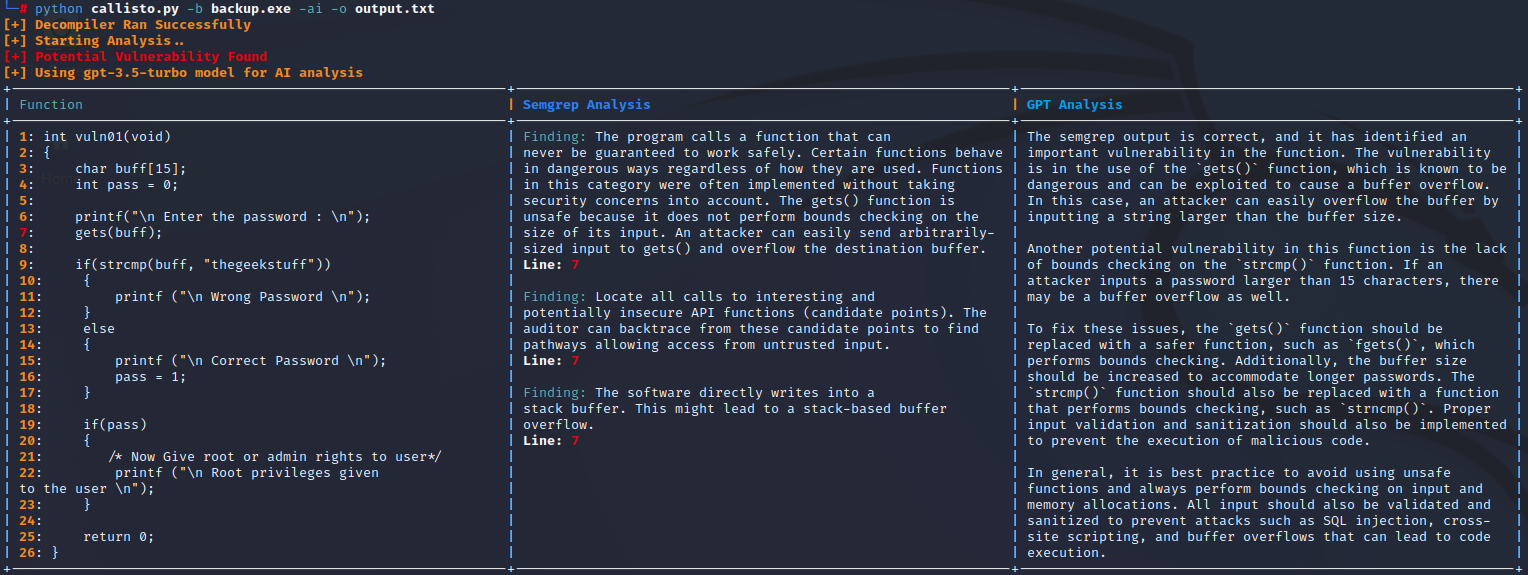 jetp1ane/callisto
Automated binary vulnerability analysis tool that decompiles executables via Ghidra, scans pseudo-C code with Semgrep, and validates findings using…
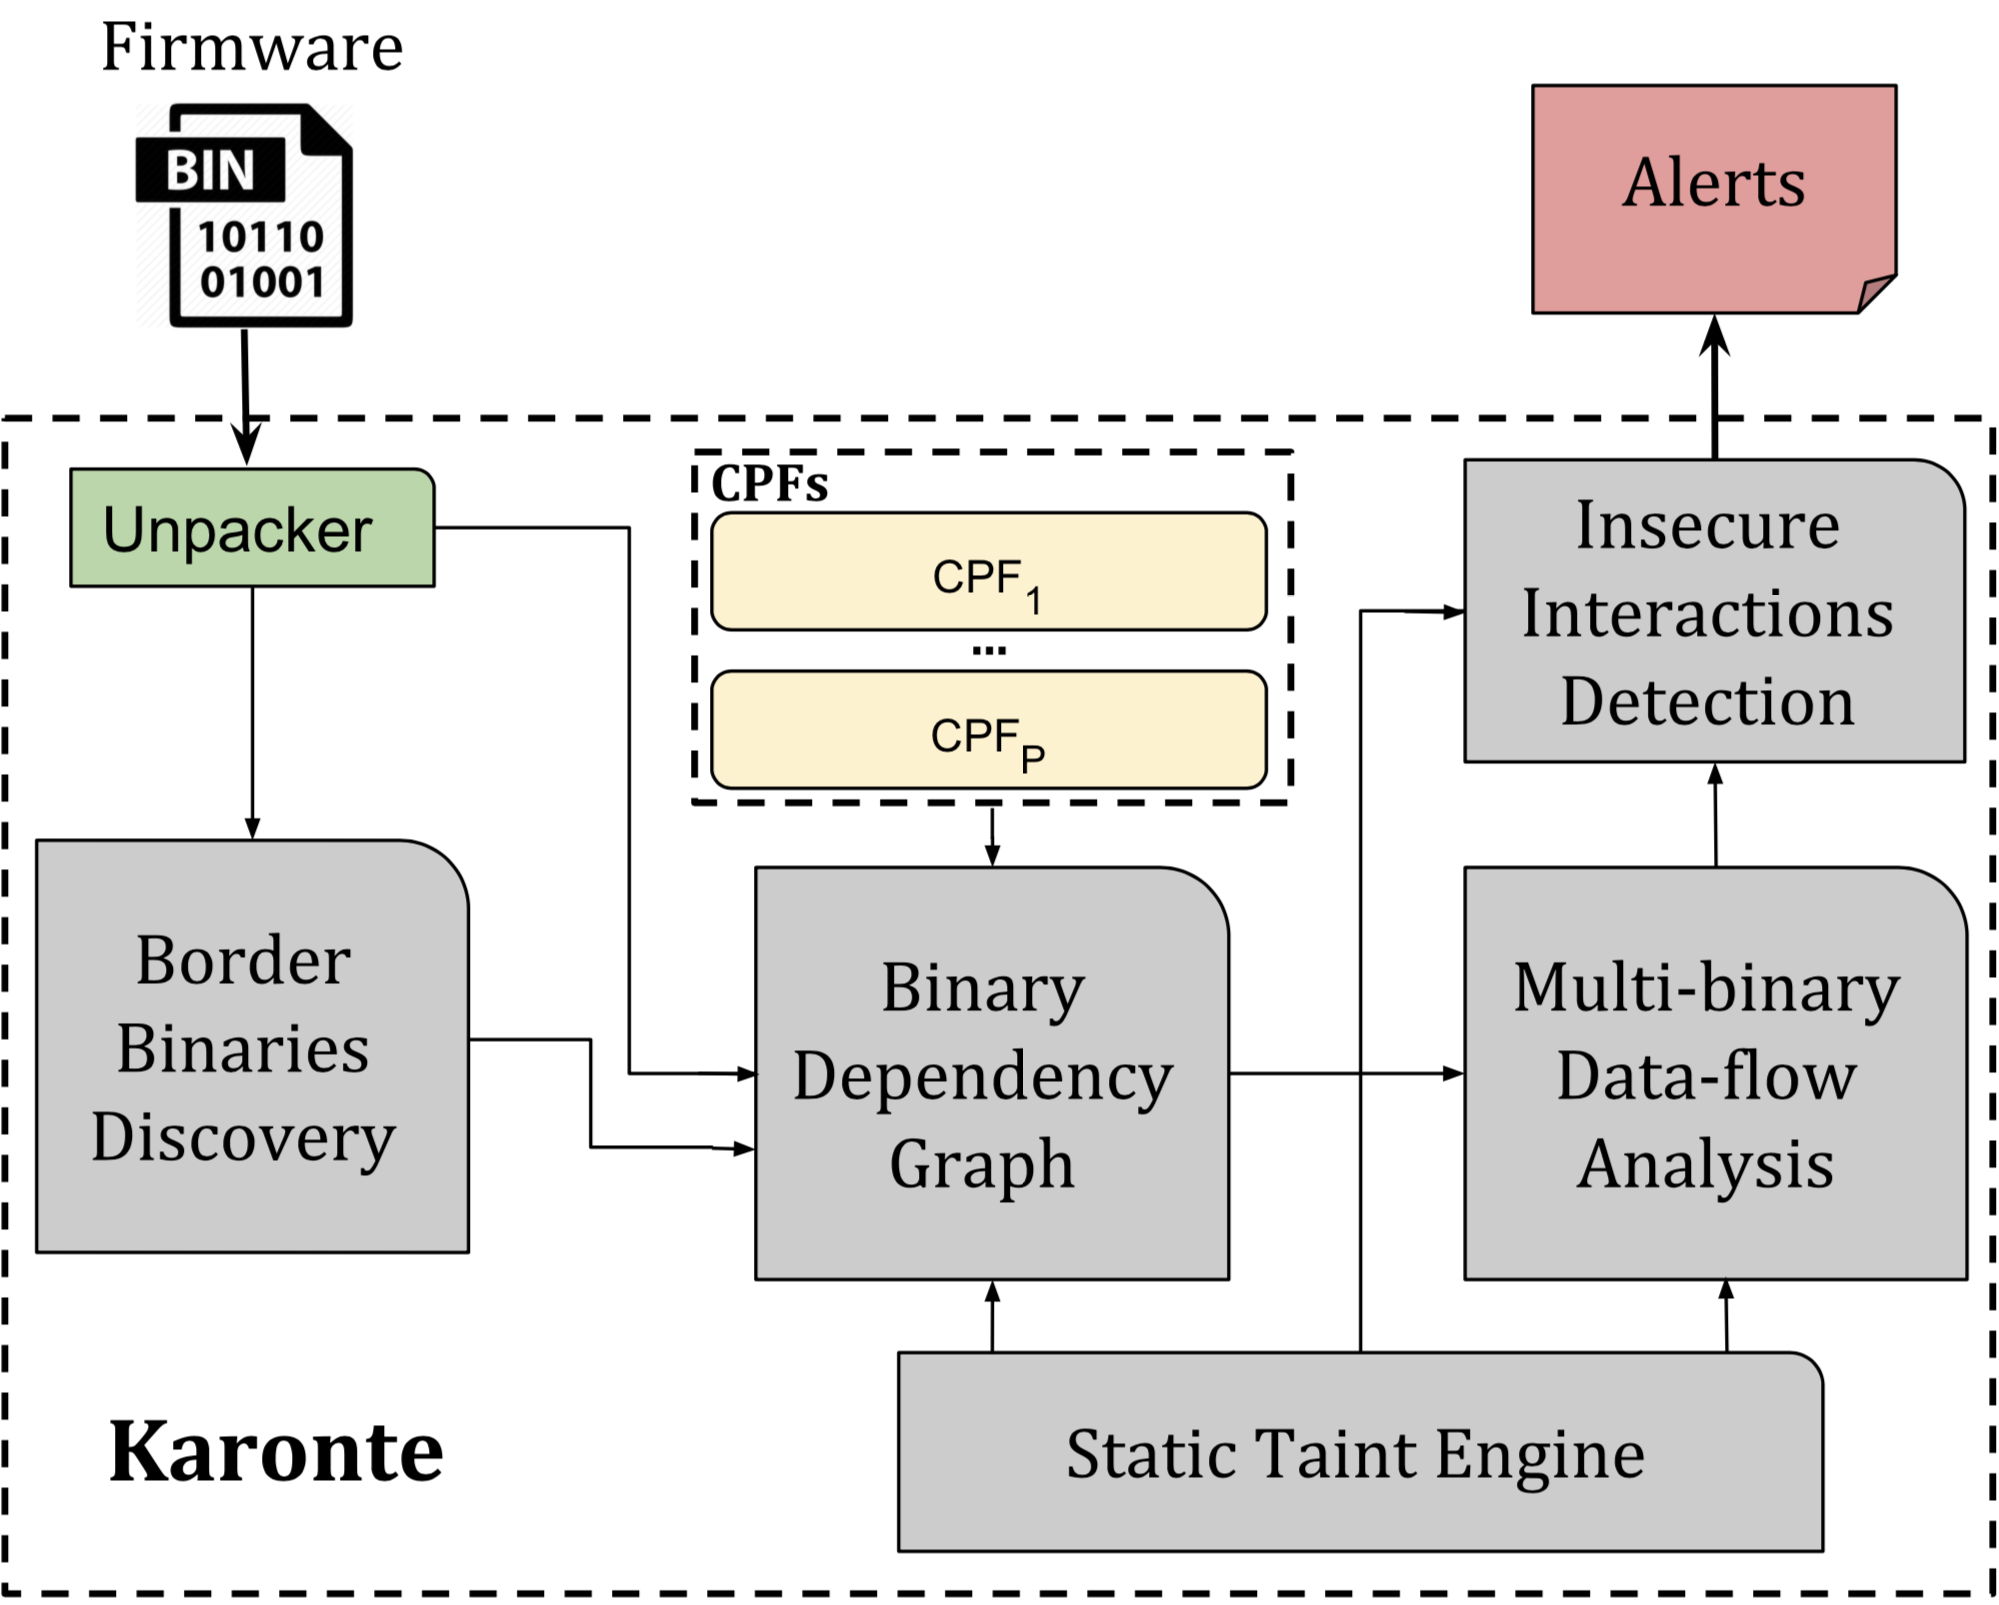 ucsb-seclab/karonte
Karonte is a static analysis tool to detect multi-binary vulnerabilities in embedded firmware
 conscioushacker/wfh
Frida-based dynamic analysis tool that automatically identifies DLL sideloading and COM hijacking vulnerabilities in Windows executables through…
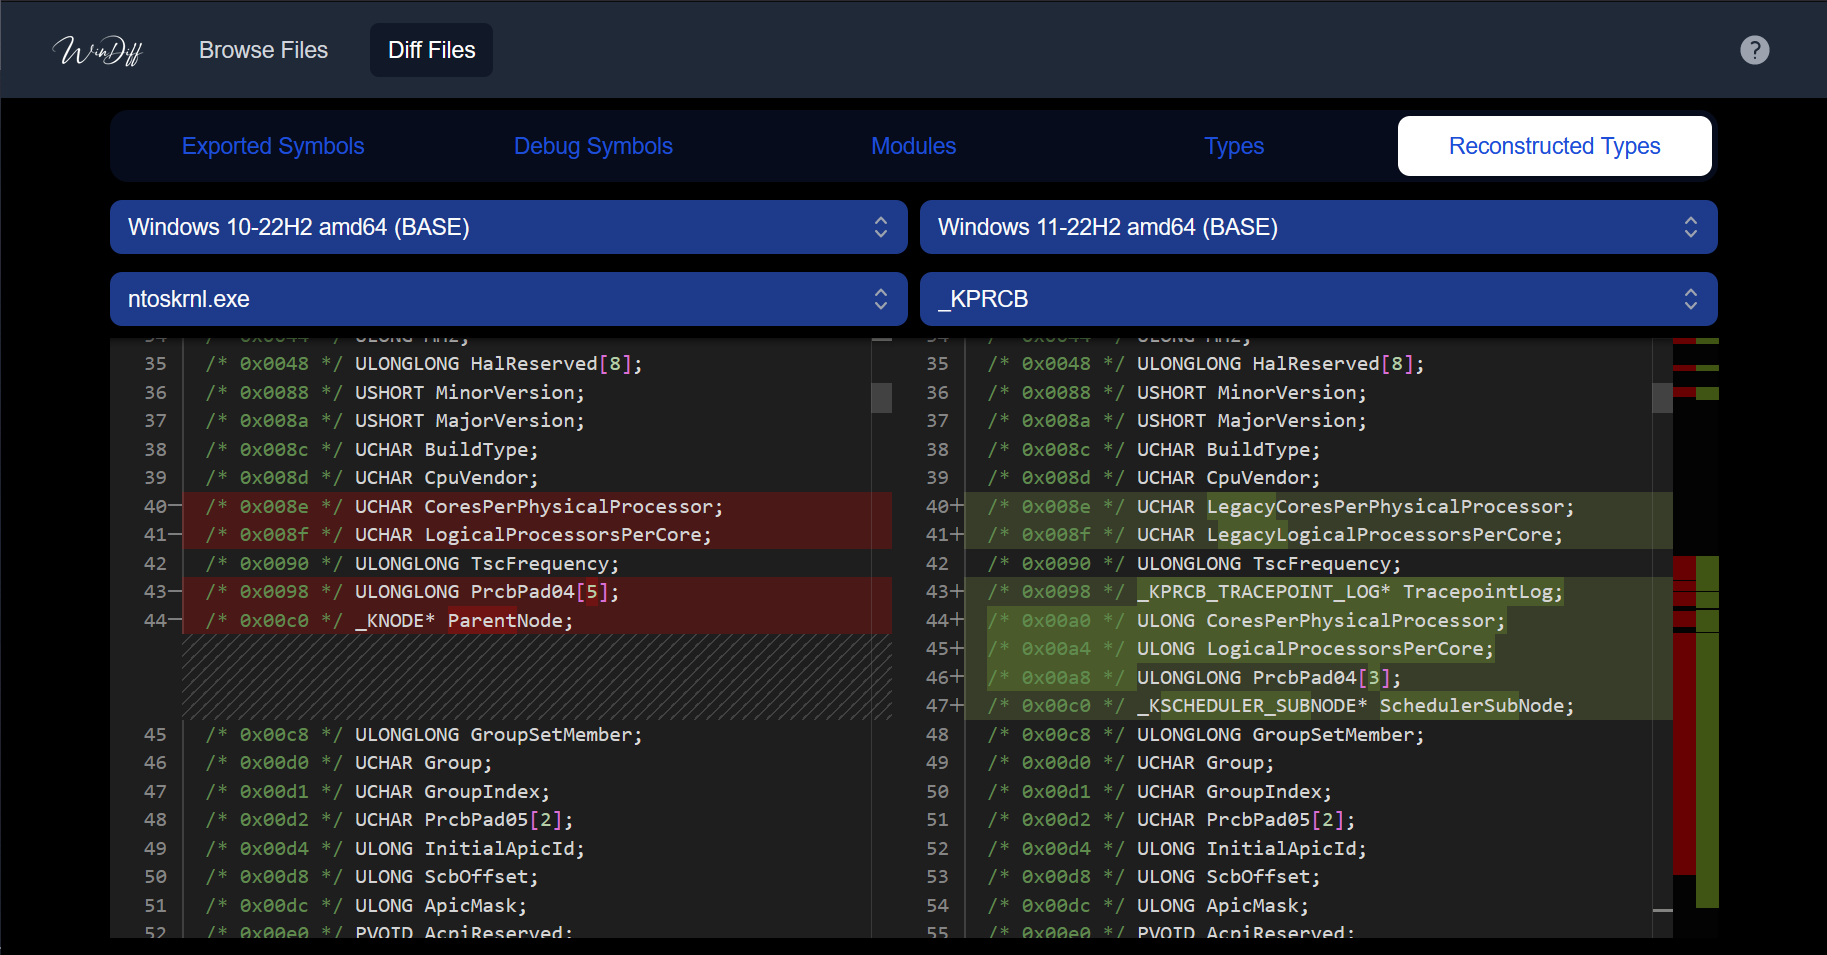 ergrelet/windiff
Tool that allows comparing symbol, type and syscall information of Microsoft Windows binaries across different versions of the OS, using a Web UI…
 netspooky/inhale
A malware analysis and classification tool.
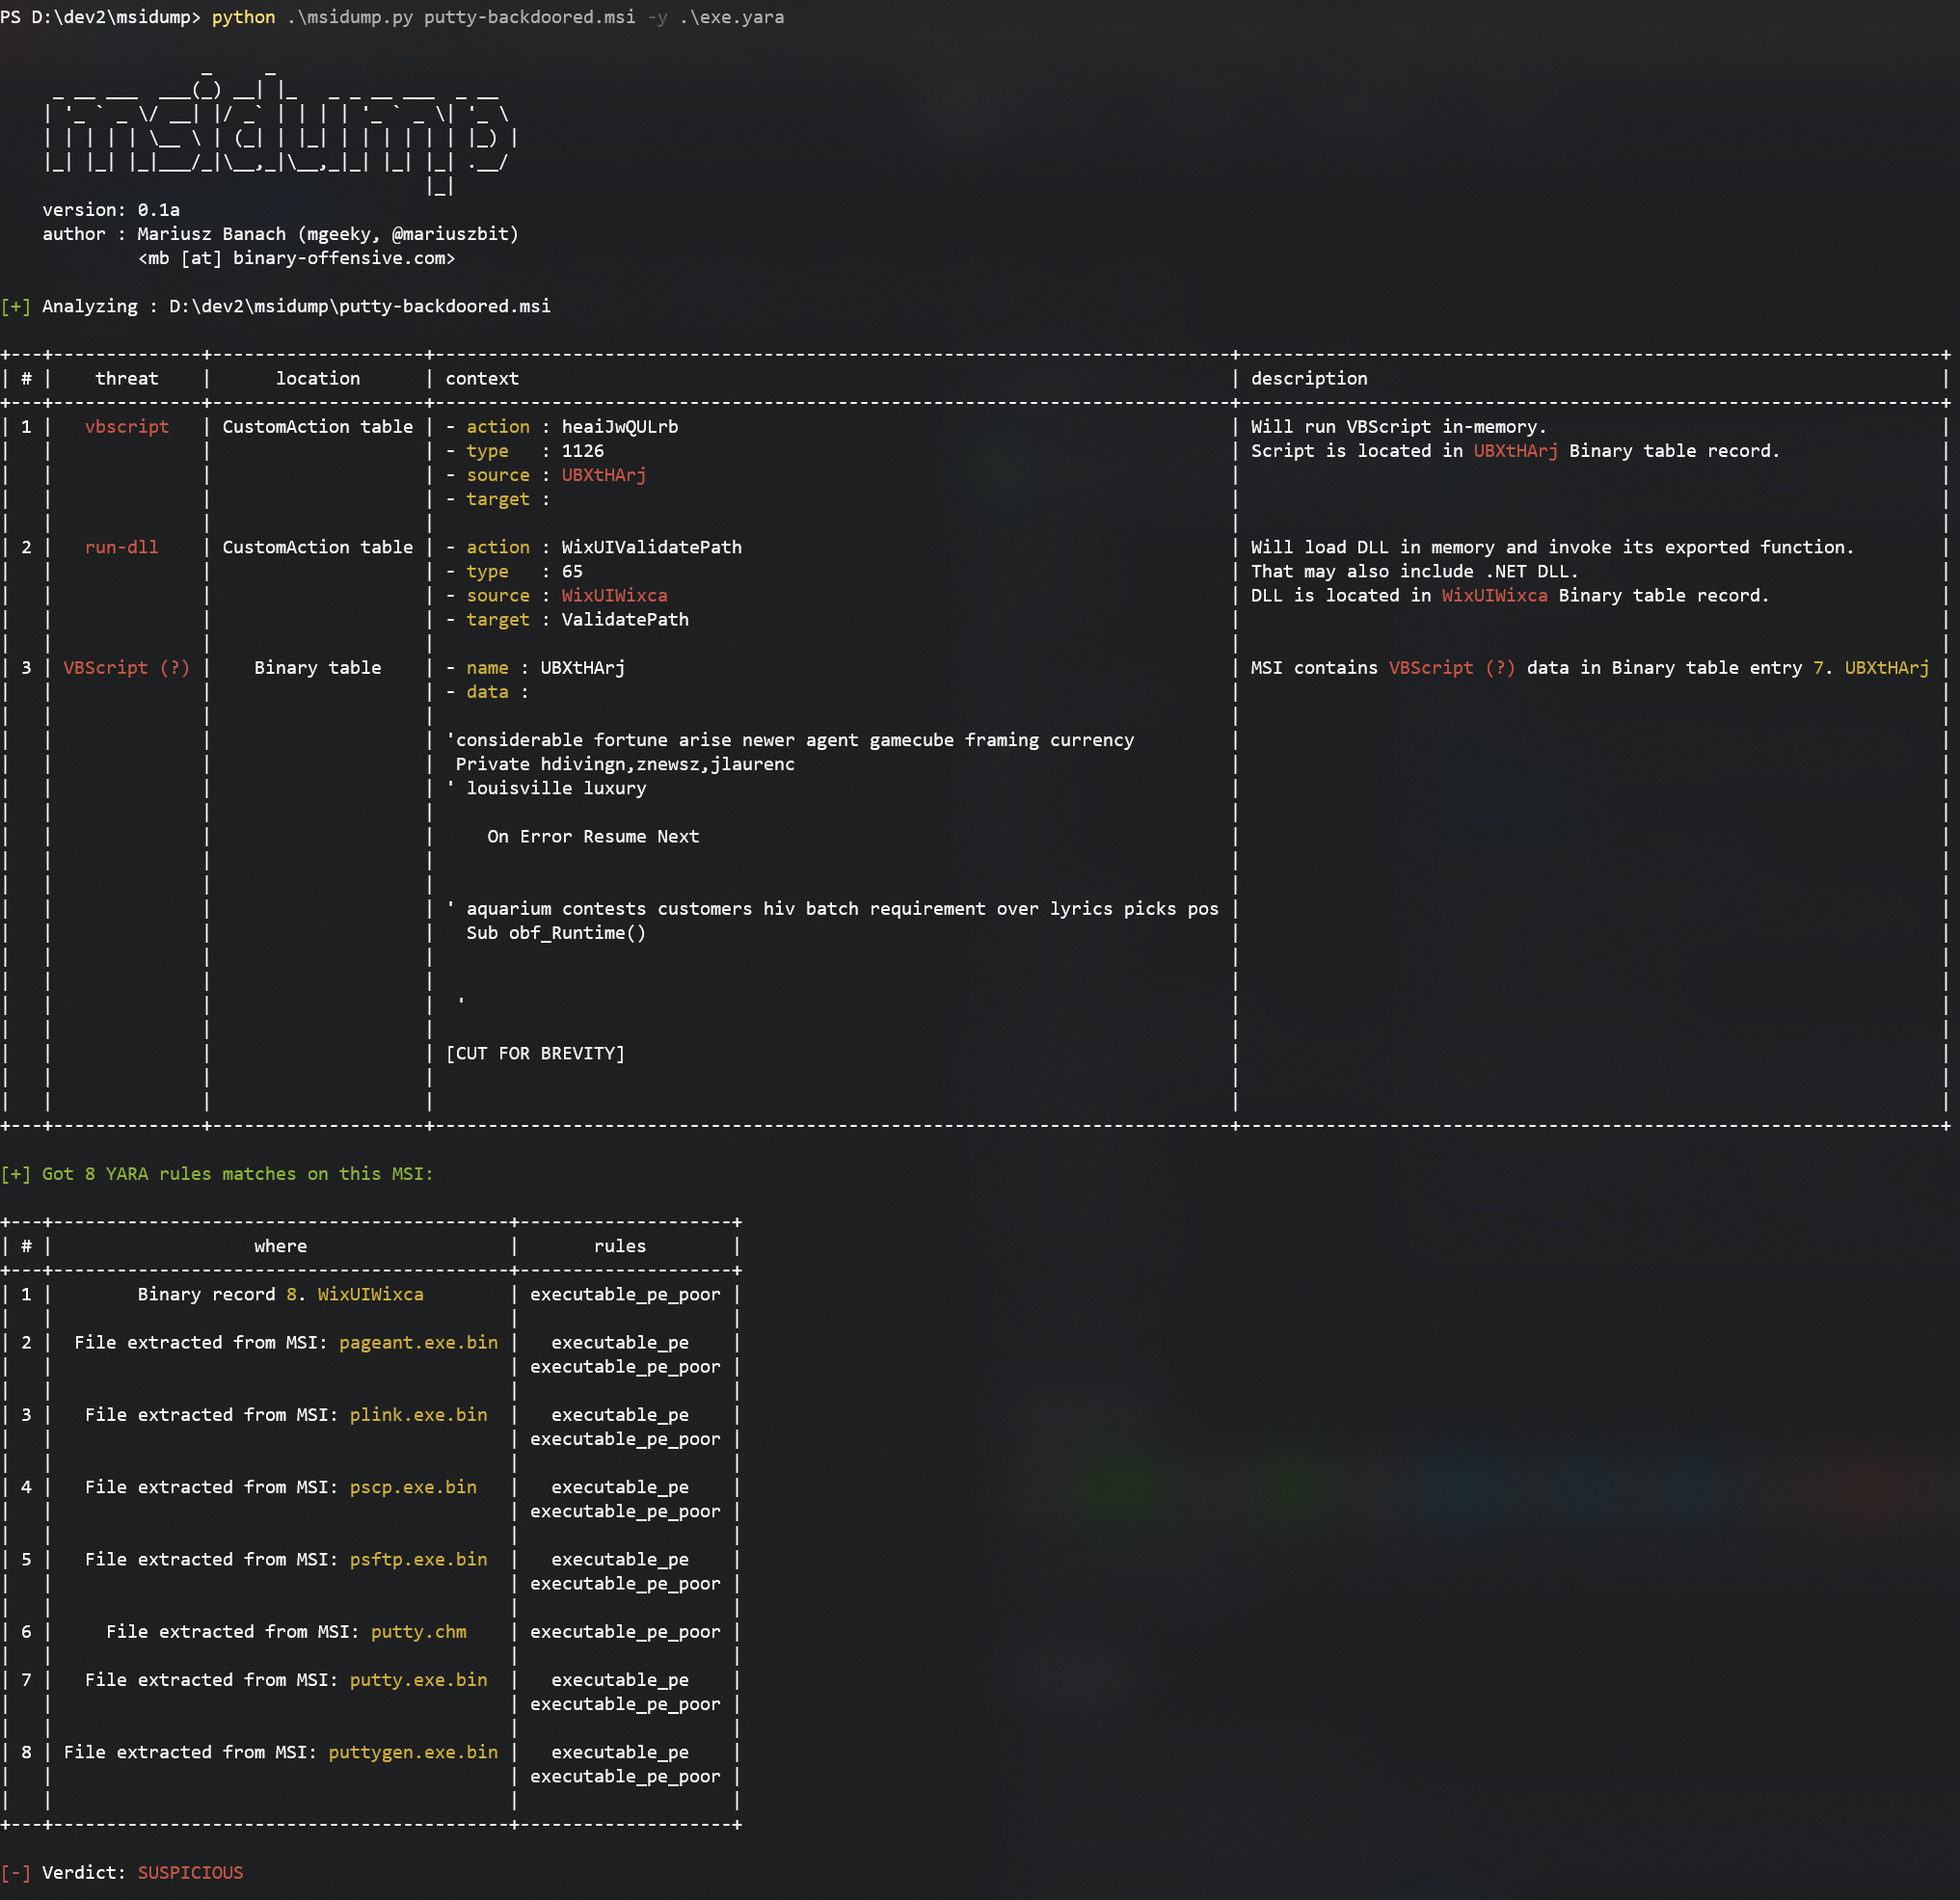 mgeeky/msidump
MSI Dump - a tool that analyzes malicious MSI installation packages, extracts files, streams, binary data and incorporates YARA scanner.
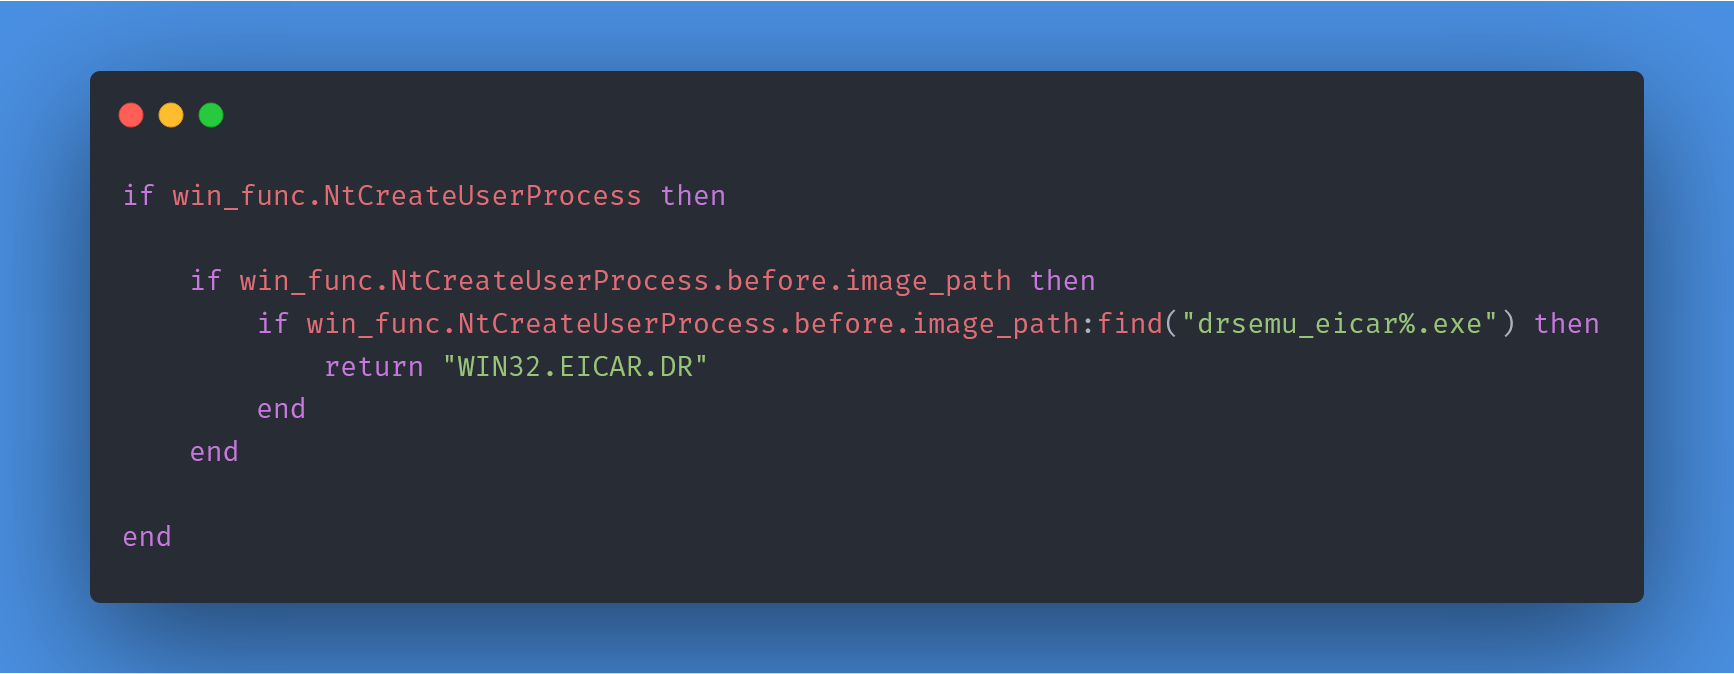 secrary/drsemu
DrSemu - Sandboxed Malware Detection and Classification Tool Based on Dynamic Behavior
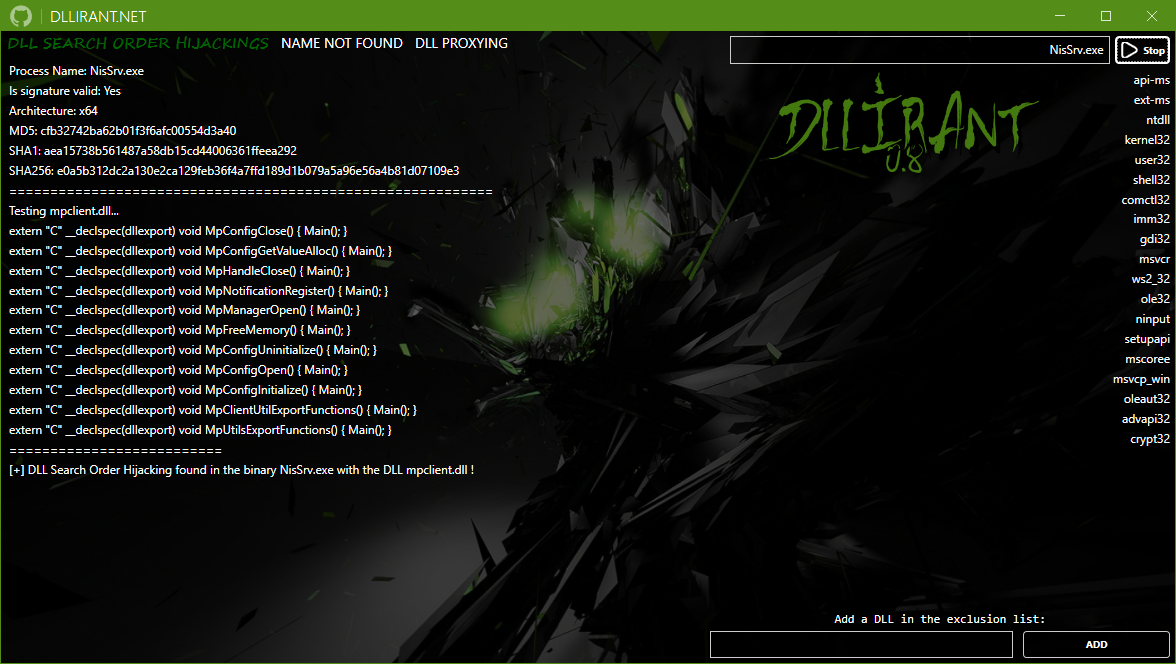 redteamsocietegenerale/dllirant
DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.