
Archived
route-sixty-sink
 mandiant/route-sixty-sink
Link sources to sinks in C# applications.
binary-analysiscode-analysisstatic-analysis+3
149
mandiant/route-sixty-sinkLink sources to sinks in C# applications.
 boschresearch/gdbfuzz
Fuzzing Embedded Systems using Hardware Breakpoints
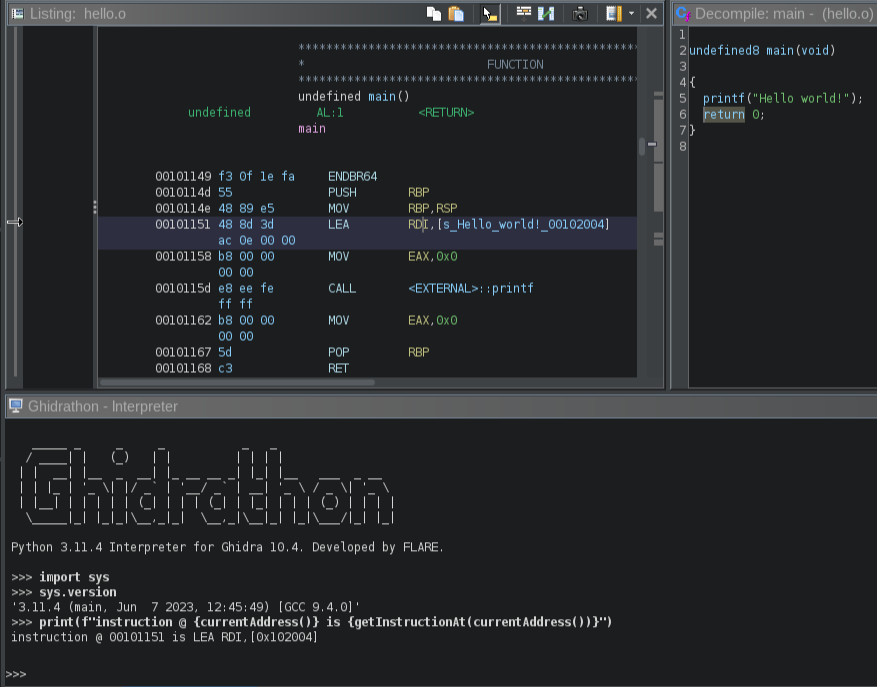 mandiant/ghidrathon
The FLARE team's open-source extension to add Python 3 scripting to Ghidra.
 cisco-talos/pyrebox
Python scriptable Reverse Engineering Sandbox, a Virtual Machine instrumentation and inspection framework based on QEMU
 das-labor/panopticon
A libre cross-platform disassembler.
 byt3bl33d3r/nimdllsideload
DLL sideloading/proxying with Nim!
 kiexitdispatcher/godefender
Anti Virtulization, Anti Debugging, AntiVM, Anti Virtual Machine, Anti Debug, Anti Sandboxie, Anti Sandbox, VM Detect package. Windows ONLY.
 optiv/mangle
Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from EDRs
 google/path-auditor
Runtime libc function auditor that detects file access race conditions and symlink vulnerabilities by hooking filesystem syscalls via LD_PRELOAD,…
 googleprojectzero/brokentype
TrueType and OpenType font fuzzing toolset
 mandiant/flare-ida
IDA Pro utilities from FLARE team
 anerruption/logic.net
A free and open-source .NET obfuscator using dnlib.
 sh0ckfr/dllirant
DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.
 szzxli/soc-home-lab
Hands-on cybersecurity lab: mini-SOC on AWS, CloudTrail IOC analyzer, phishing analysis lab, ELF binary triage, SOC agent skills
 viper-framework/viper
Binary analysis and management framework
 memn0ps/illusion-rs
Rusty Hypervisor - Windows UEFI Blue Pill Type-1 Hypervisor in Rust (Codename: Illusion)
 adrienthebo/cve-2014-2734
I think this CVE is full of lies and deceit and very confusing code.
 gmh5225/ntstrace
frida-stalker based system call tracer on windows(x64).