
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
241 results
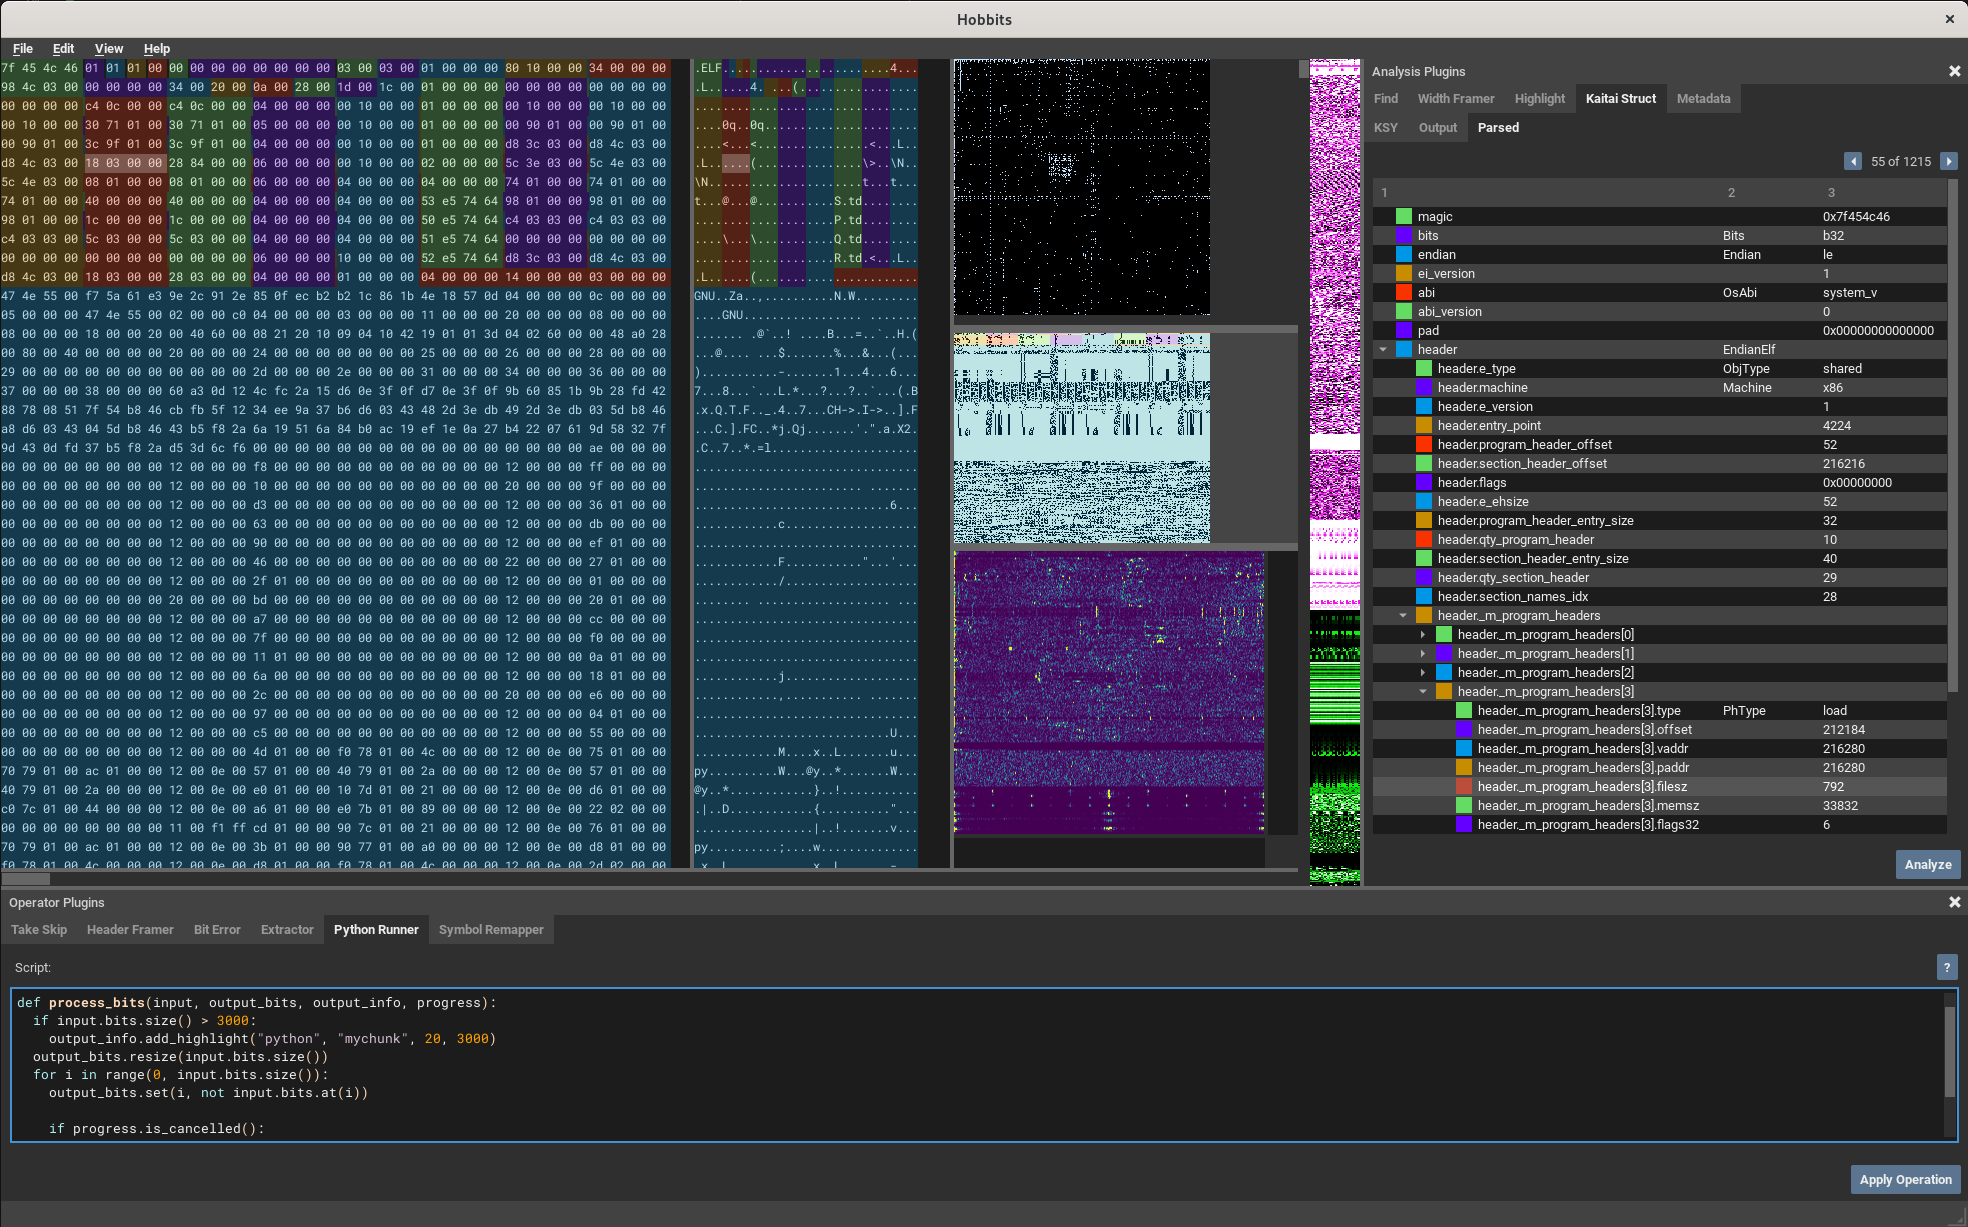
hobbits preview

hobbits

GitHubmahlet-inc/hobbits

A multi-platform GUI for bit-based analysis, processing, and visualization
binary-analysisdata-recoveryforensics+1
750
1 year ago
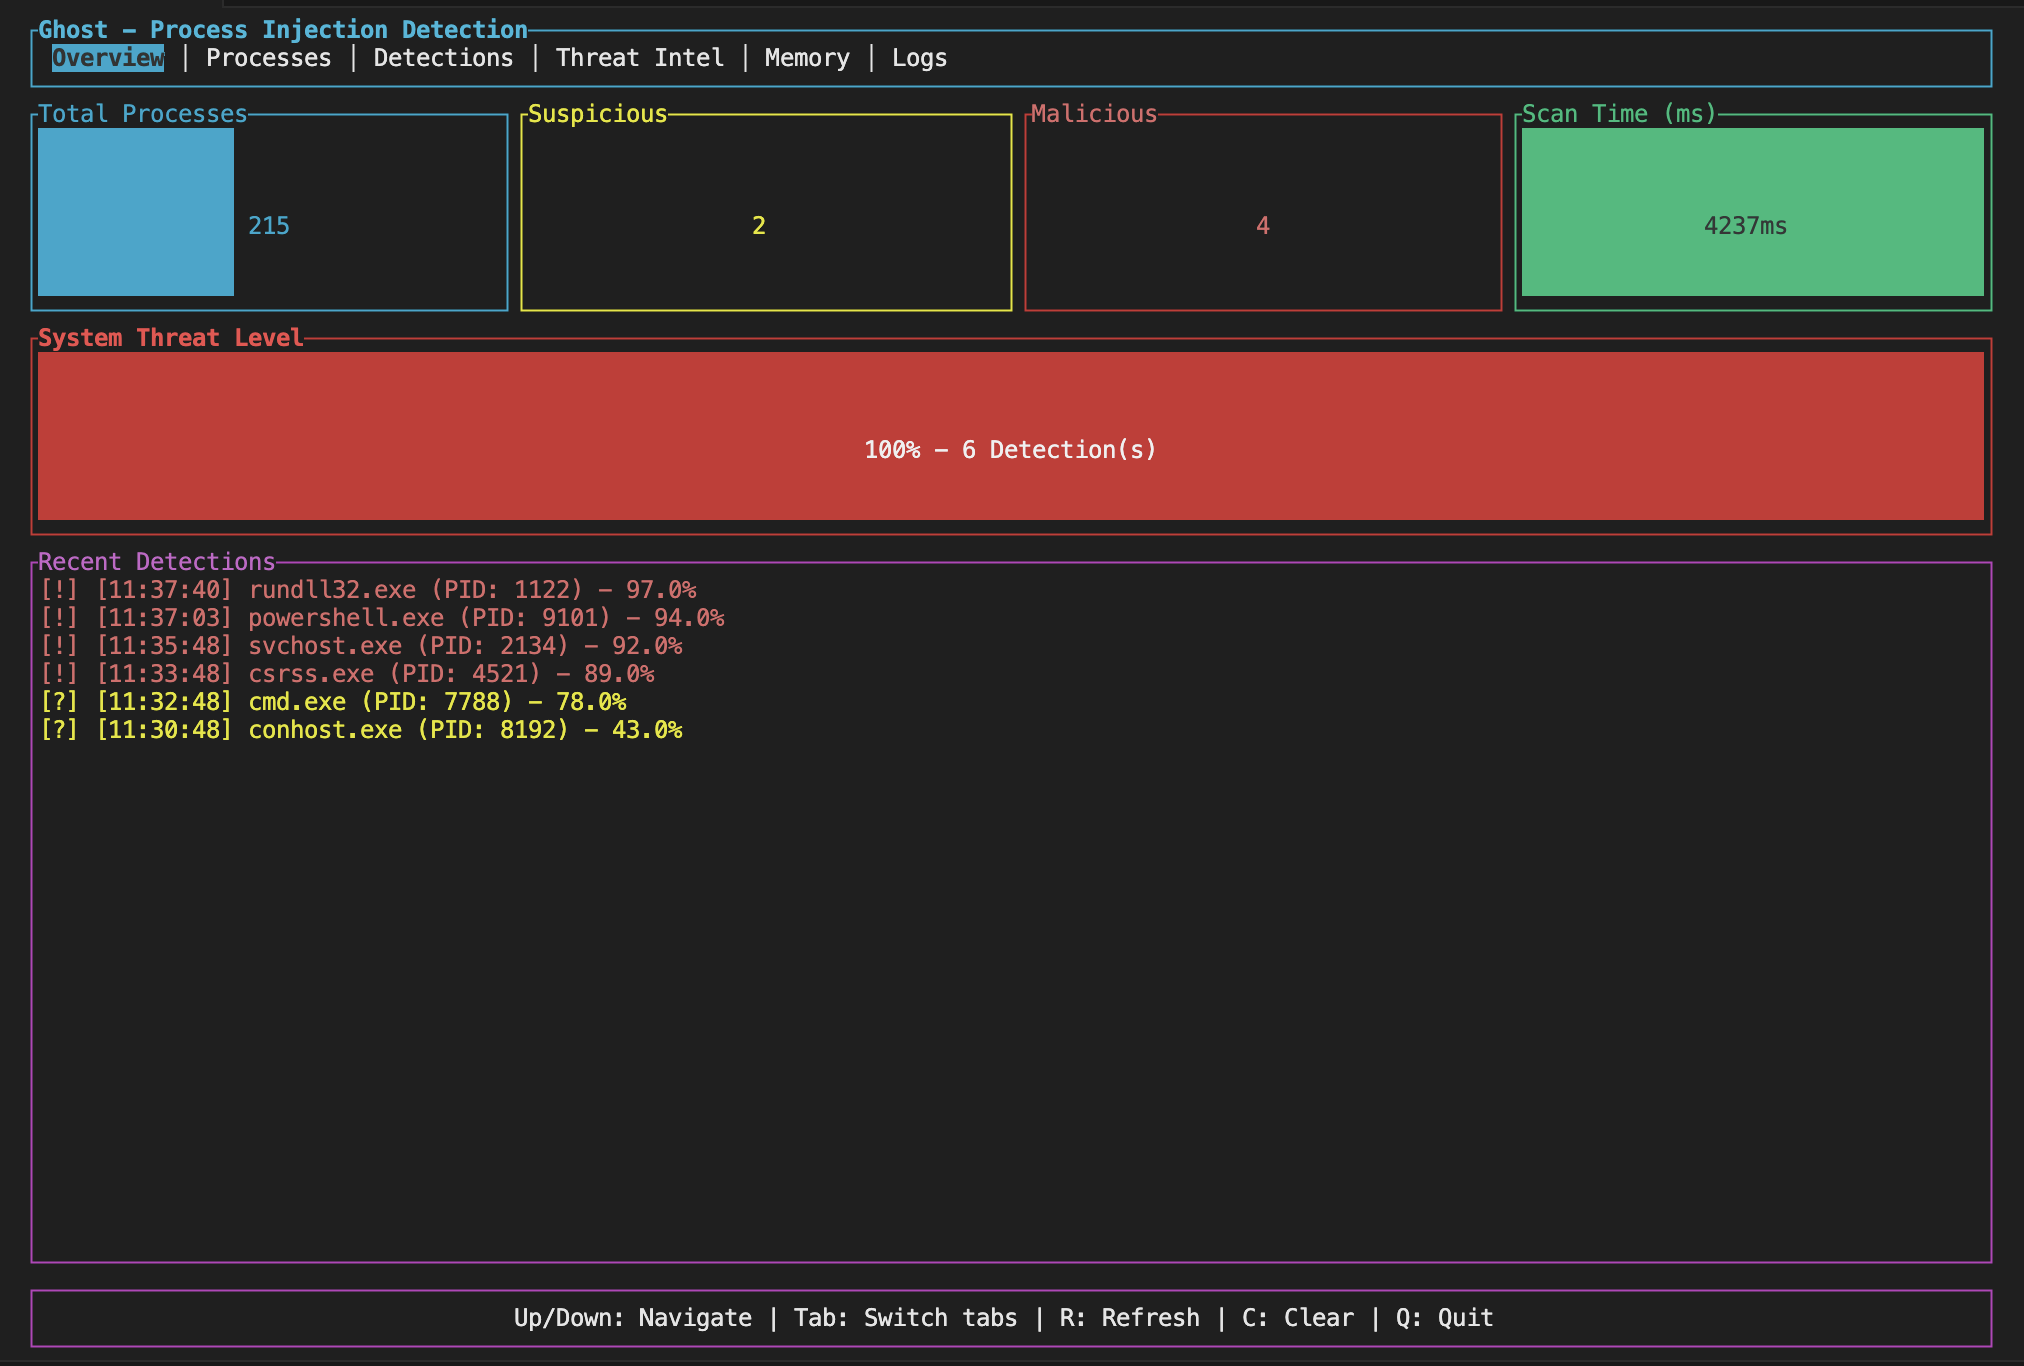
ghost preview

ghost

GitHubpandaadir05/ghost

Detects process injection and memory manipulation used by malware. Finds RWX regions, shellcode patterns, API hooks, thread hijacking, and process…

binary-analysisdefensive-toolsforensics+6
3911 month ago
themida-unmutate preview

themida-unmutate

GitHubergrelet/themida-unmutate

Static deobfuscator for Themida, WinLicense and Code Virtualizer 3.x's mutation-based obfuscation.
binary-analysisbinary-exploitationmalware-analysis+3
3912 years ago
MemITM preview

MemITM

GitHubamossys/memitm

Tool to make in memory man in the middle
binary-analysisdebuggersdynamic-analysis-sandboxing+4
1267 years ago
Log4JShell-Bytecode-Detector preview

Log4JShell-Bytecode-Detector

GitHubcodeshield-security/log4jshell-bytecode-detector

Local Bytecode Scanner for the Log4JShell Vulnerability (CVE-2021-44228)
binary-analysiscode-analysisincident-response+3
494 years ago
MappedImagesDetector preview

MappedImagesDetector

GitHubadem-hosni/mappedimagesdetector

Lightweight native Windows memory scanner for AV/EDR platforms, detecting suspicious mapped images and manual DLL injection techniques by IAT thunk

anomaly-detectionbinary-analysisdefensive-tools+4
18 months ago
ROPgadget preview

ROPgadget

GitHubjonathansalwan/ropgadget

Search for ROP gadgets in ELF, PE, Mach-O, and Raw binaries across x86, ARM, MIPS, and RISC-V architectures. Supports automated ROP chain generation…
binary-analysisbinary-exploitationctf+3
4.5k2 months ago
pe-sieve preview

pe-sieve

GitHubhasherezade/pe-sieve

Scans a given process. Recognizes and dumps a variety of potentially malicious implants (replaced/injected PEs, shellcodes, hooks, in-memory patches).
binary-analysisforensicsmalware-analysis+2
3.9k3 months ago
AllTools preview

AllTools

GitHubzodiacon/alltools

All reasonably stable tools
binary-analysisdebuggersgeneral-purpose-utilities+1
1.4k3 months ago
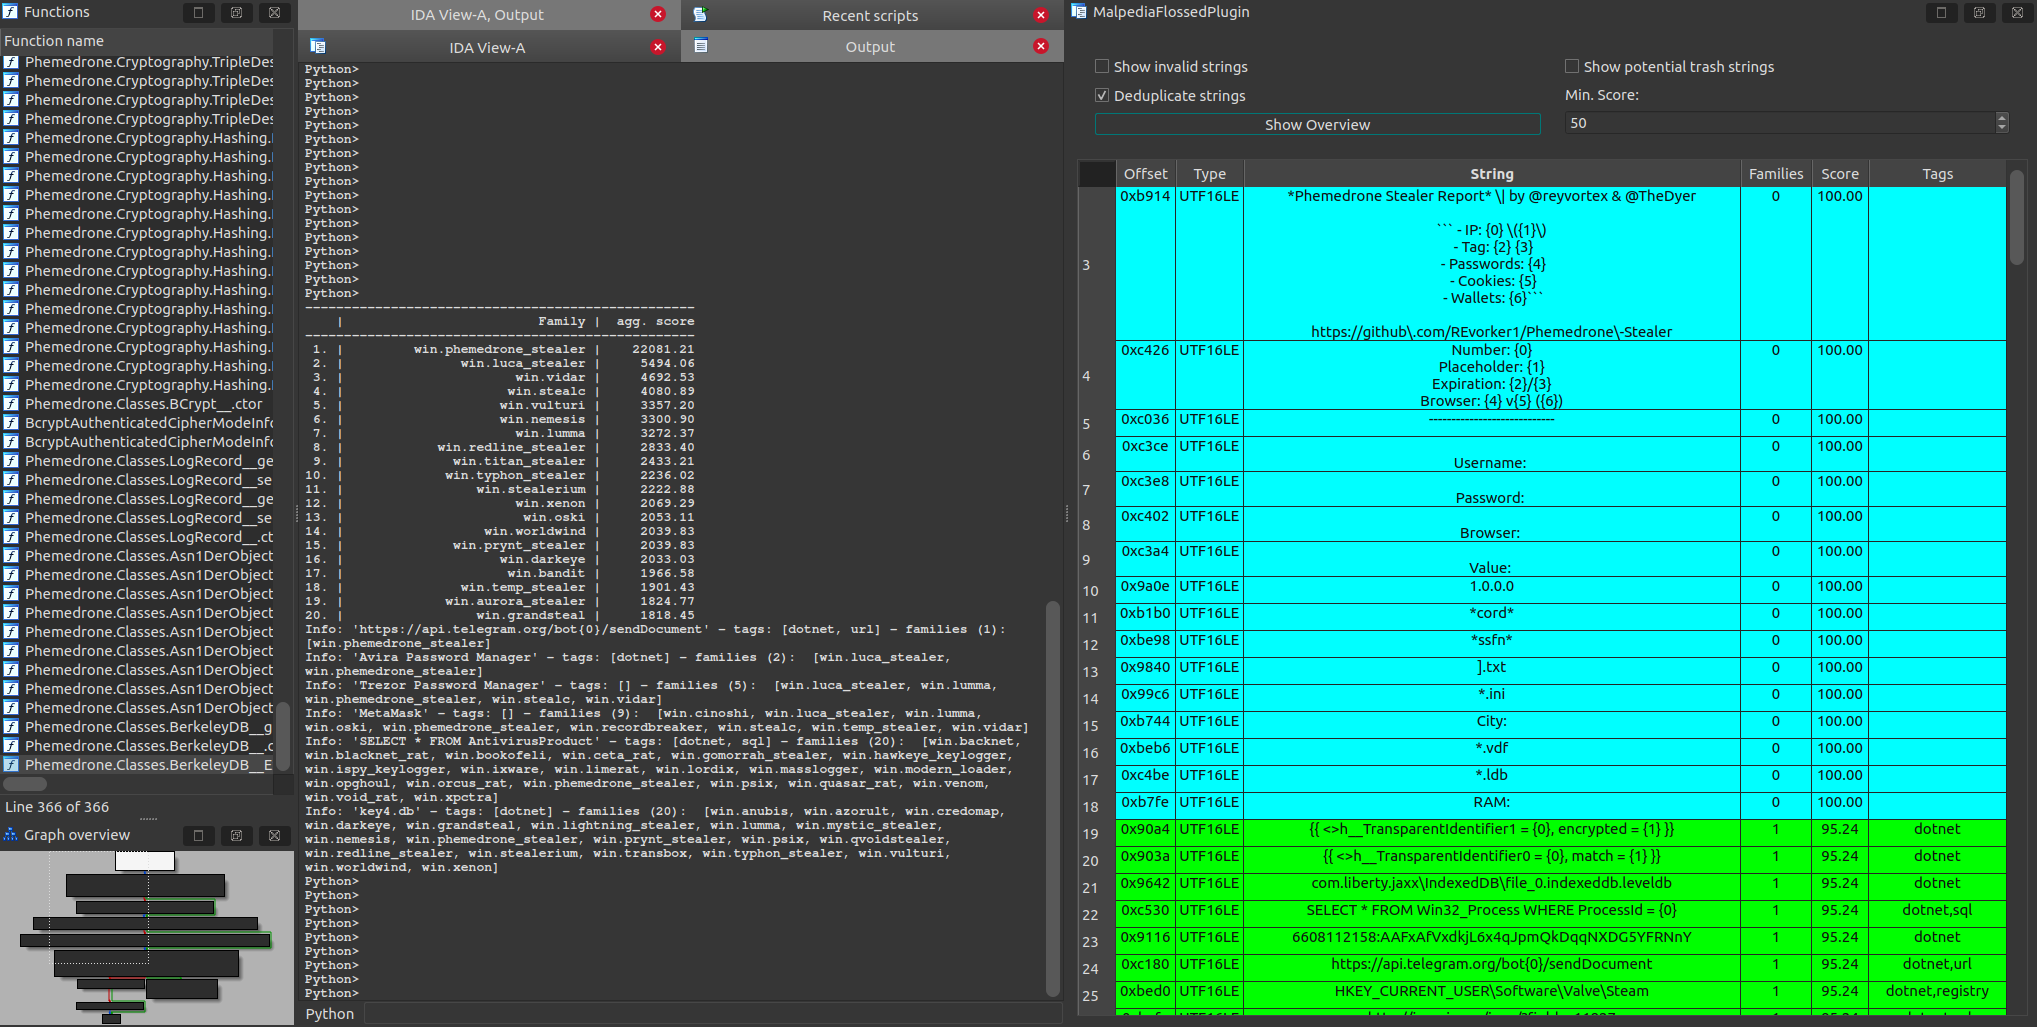
malpedia-flossed preview

malpedia-flossed

GitHubmalpedia/malpedia-flossed

FLARE floss applied to all unpacked+dumped samples in Malpedia, pre-processed for further use.
binary-analysiscurated-resourcesdynamic-analysis-sandboxing+8
838 months ago
ghidrecomp preview

ghidrecomp

GitHubclearbluejar/ghidrecomp

Python Command-Line Ghidra Decompiler
binary-analysisreverse-engineeringstatic-code-analysis+1
1578 months ago
Uchihash preview

Uchihash

GitHubn1ght-w0lf/uchihash

A small utility to deal with malware embedded hashes.
binary-analysishash-analysismalware-analysis+2
522 years ago
upx preview

upx

GitHubupx/upx

UPX - the Ultimate Packer for eXecutables

binary-analysisgeneral-purpose-utilitiesreverse-engineering
17.9k3 days ago
diaphora preview

diaphora

GitHubjoxeankoret/diaphora

Diaphora, the most advanced Free and Open Source program diffing tool.
binary-analysisreverse-engineeringvulnerability-analysis
4.4k12 days ago
keystone preview

keystone

GitHubkeystone-engine/keystone

Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…

binary-analysisbinary-exploitationgeneral-purpose-utilities+4
2.6k1 month ago
FACT_core preview

FACT_core

GitHubfkie-cad/fact_core

Firmware Analysis and Comparison Tool

binary-analysisdynamic-analysis-sandboxingembedded-systems-security+9
1.5k5 days ago
MCExtractor preview

MCExtractor

GitHubplatomav/mcextractor

Intel, AMD, VIA & Freescale Microcode Extraction Tool
binary-analysisfirmware-analysishardware-security+2
92612 days ago
vmlinux-to-elf preview

vmlinux-to-elf

GitHubmarin-m/vmlinux-to-elf

A tool to recover a fully analyzable .ELF from a raw kernel, through extracting the kernel symbol table (kallsyms)

binary-analysisembedded-systems-securityfirmware-analysis+1
1.8k3 months ago
Previous1…789…14Next