
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
131 results
IronPE preview

IronPE

GitHubiss4cf0ng/ironpe

Rust-based Windows PE manual loader that maps and executes x86/x64 executables from memory, demonstrating internal loader behavior and PE structure…
binary-analysisbinary-exploitationeducation+5
124
6 months ago
custom-bytecode-analyzer preview

custom-bytecode-analyzer

GitHubfergarrui/custom-bytecode-analyzer

Java bytecode analyzer customizable via JSON rules
binary-analysiscode-analysisstatic-analysis+1
738 years ago
DiaSymbolView preview

DiaSymbolView

GitHubdiversenok/diasymbolview

PDB file inspection tool
binary-analysisdebuggersreverse-engineering+1
13710 months ago
lifer preview

lifer

GitHubpaul-tew/lifer

Windows link file (shortcuts) examiner
binary-analysisdigital-forensicsforensics+1
682 years ago
AndroidDriveSignity preview

AndroidDriveSignity

GitHubgmh5225/androiddrivesignity

AndroidDriveSignity is a Python utility designed to bypass driver signature verification in Android kernel(ARMv8.3), facilitating the loading of…
android-securitybinary-analysisexploitation+1
632 years ago
YaraVM preview

YaraVM

GitHubmilankovo/yaravm

This repository contains an IDA processor for loading and disassembling compiled yara rules.
binary-analysisdebuggersmalware-analysis+2
521 year ago
PESTO preview

PESTO

GitHubelevenpaths/pesto

Extracts and analyzes PE file security characteristics (ASLR, DEP, CFG, NO_SEH) from DLLs and EXEs across directories, storing results in a SQLite…
binary-analysismalware-analysisstatic-analysis+1
266 years ago
dconstruct preview

dconstruct

GitHubdeepquantum/dconstruct

A disassembler & experimental decompiler for TLOU2 DC Scripts.

binary-analysisdebuggersfirmware-analysis+2
2412 days ago
TABPE preview

TABPE

GitHubonhexgroup/tabpe

A monthly Windows PE baseline dataset for Cyber security researchers
binary-analysiscurated-resourceseducation+2
243 months ago
adwind-decryptor preview

adwind-decryptor

GitHubmhelwig/adwind-decryptor

Simple decrypter for Java AdWind, jRAT, jBifrost trojan
binary-analysisdigital-forensicsencryption-decryption-tools+3
179 years ago
file-unpumper preview

file-unpumper

GitHub0x11dfe/file-unpumper

Tool that can be used to trim useless things from a PE file such as the things a file pumper would add.
binary-analysismalware-analysisreverse-engineering+1
301 year ago
CVE-2025-9491_POC preview

CVE-2025-9491_POC

GitHubamperclock/cve-2025-9491_poc

Proof-of-Concept of the CVE-2025-9491 using invisible characters in the arguments of a Windows shortcut file (.lnk)
binary-analysiseducationexploitation+3
1810 months ago
zipbrk preview

zipbrk

GitHubkvesel/zipbrk

Zip file format fuzzer and multi-tool.
binary-analysiscryptographyencryption-decryption-tools+4
124 months ago
Icedid-file-decryptor preview

Icedid-file-decryptor

GitHubembee-research/icedid-file-decryptor

Static Decryptor for IcedID Malware
binary-analysiscryptographymalware-analysis+2
183 years ago
ElectronVulnerableVersion preview

ElectronVulnerableVersion

GitHubgtgalaxi/electronvulnerableversion

Find Electron Apps Vulnerable to CVE-2023-4863 / CVE-2023-5129

binary-analysisinformation-gatheringreconnaissance+3
72 years ago
ImageMagick-CVE-2017-15277 preview

ImageMagick-CVE-2017-15277

GitHubhexrom/imagemagick-cve-2017-15277

Proof-of-concept exploit for ImageMagick CVE-2017-15277 memory leak vulnerability, designed for use with the gifoeb fuzzing framework.
binary-analysisexploitationfuzzing+2
56 years ago
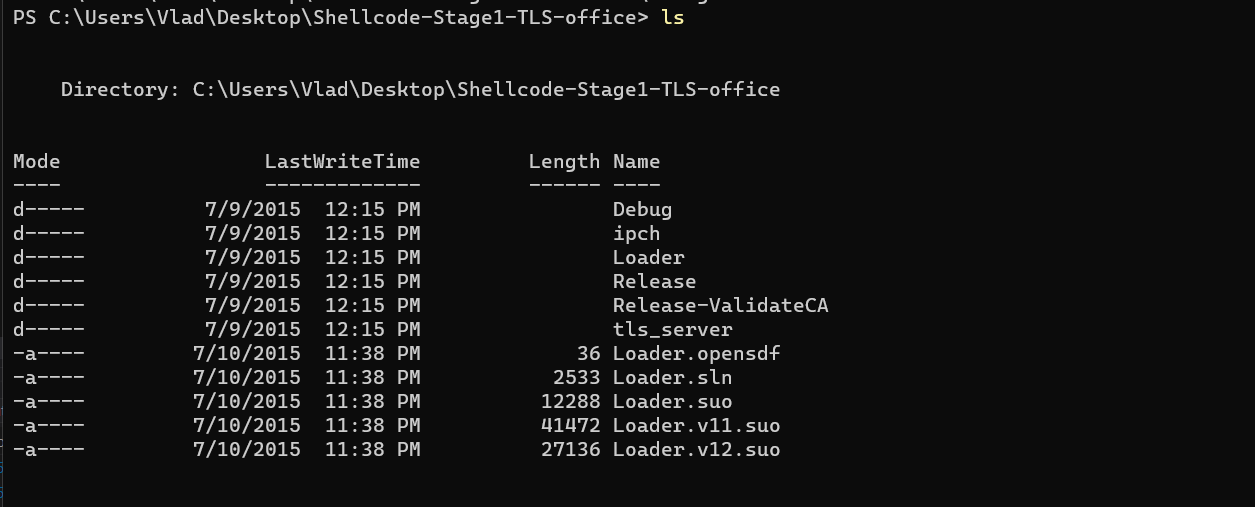
Analysis-for-stage1-shellcode-loader-from-hacking- preview

Analysis-for-stage1-shellcode-loader-from-hacking-

GitHubspiralbl0ck/analysis-for-stage1-shellcode-loader-from-hacking-

Analysis for stage1 shellcode loader from hacking
binary-analysiseducationmalware-analysis+2
31 year ago
SnipRecover-CLI preview

SnipRecover-CLI

GitHubm31r0n/sniprecover-cli

Detection and restoration of Windows Snipping Tool PNG captures vulnerable to CVE-2023-28303

binary-analysisdata-recoverydigital-forensics+3
21 year ago
Previous1…678Next