

Brovan
 advdebug/brovan
User-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
binary-analysisdebuggersdynamic-analysis-sandboxing+3
166
advdebug/brovanUser-mode x86_64 binary emulator for malware analysis and reverse engineering. Supports PE, ELF, memory dumps, and raw binaries with syscall tracing,…
 romainthomas/reverse-engineering-workshop
Slides & Hands-on for the reverse engineering workshop
 therealdreg/shellex
C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…
 trolldbois/python-haystack
Process heap analysis framework - Windows/Linux - record type inference and forensics
 oxagast/ansvif
A Not So Very Intelligent Fuzzer: An advanced fuzzing framework designed to find vulnerabilities in C/C++ code.
 gmh5225/androiddrivesignity
AndroidDriveSignity is a Python utility designed to bypass driver signature verification in Android kernel(ARMv8.3), facilitating the loading of…
 aethervm/aethervm
LLVM-native binary analysis and emulation platform that lifts AArch64 and x86_64 machine code to LLVM IR for instrumentation, deobfuscation, and…
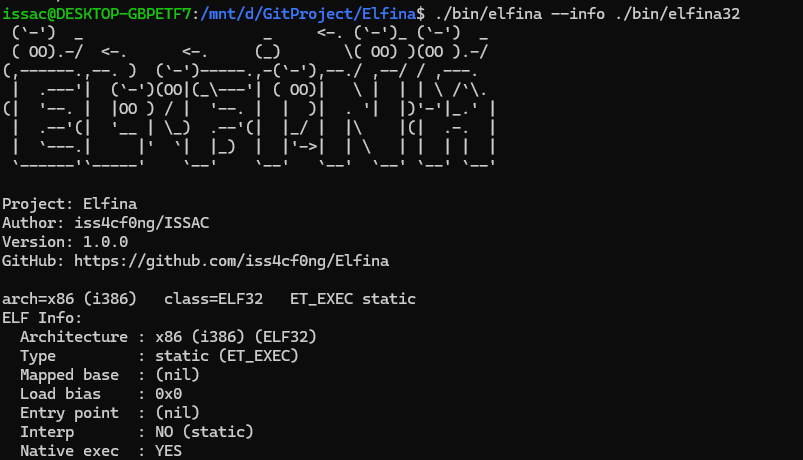 iss4cf0ng/elfina
Multi-architecture ELF loader and analysis toolkit with probing, disassembly, hexdump, entropy calculation, and mmap/memfd execution for x86 and…
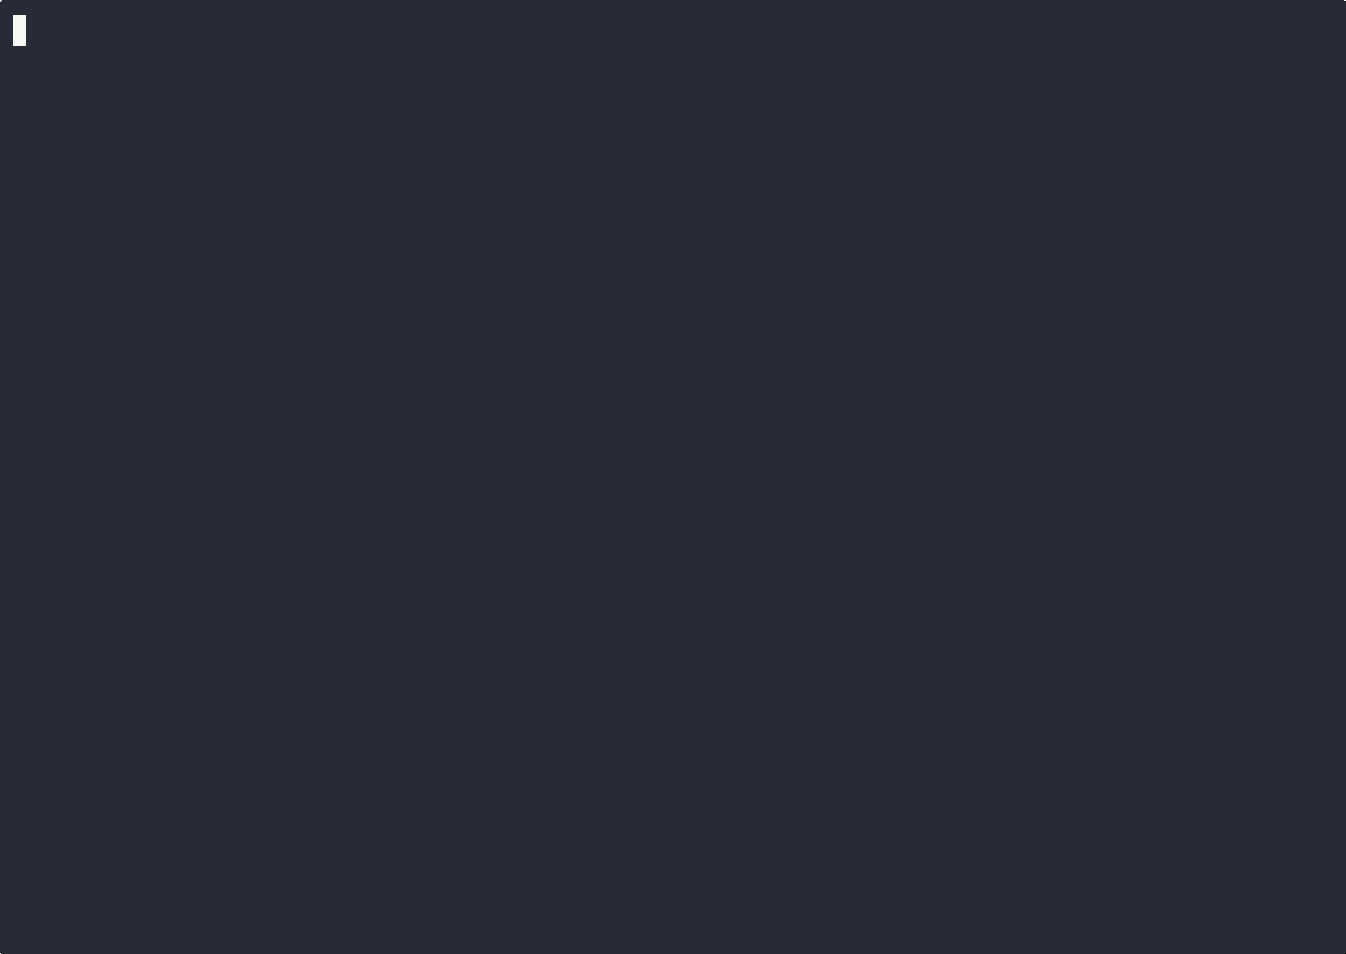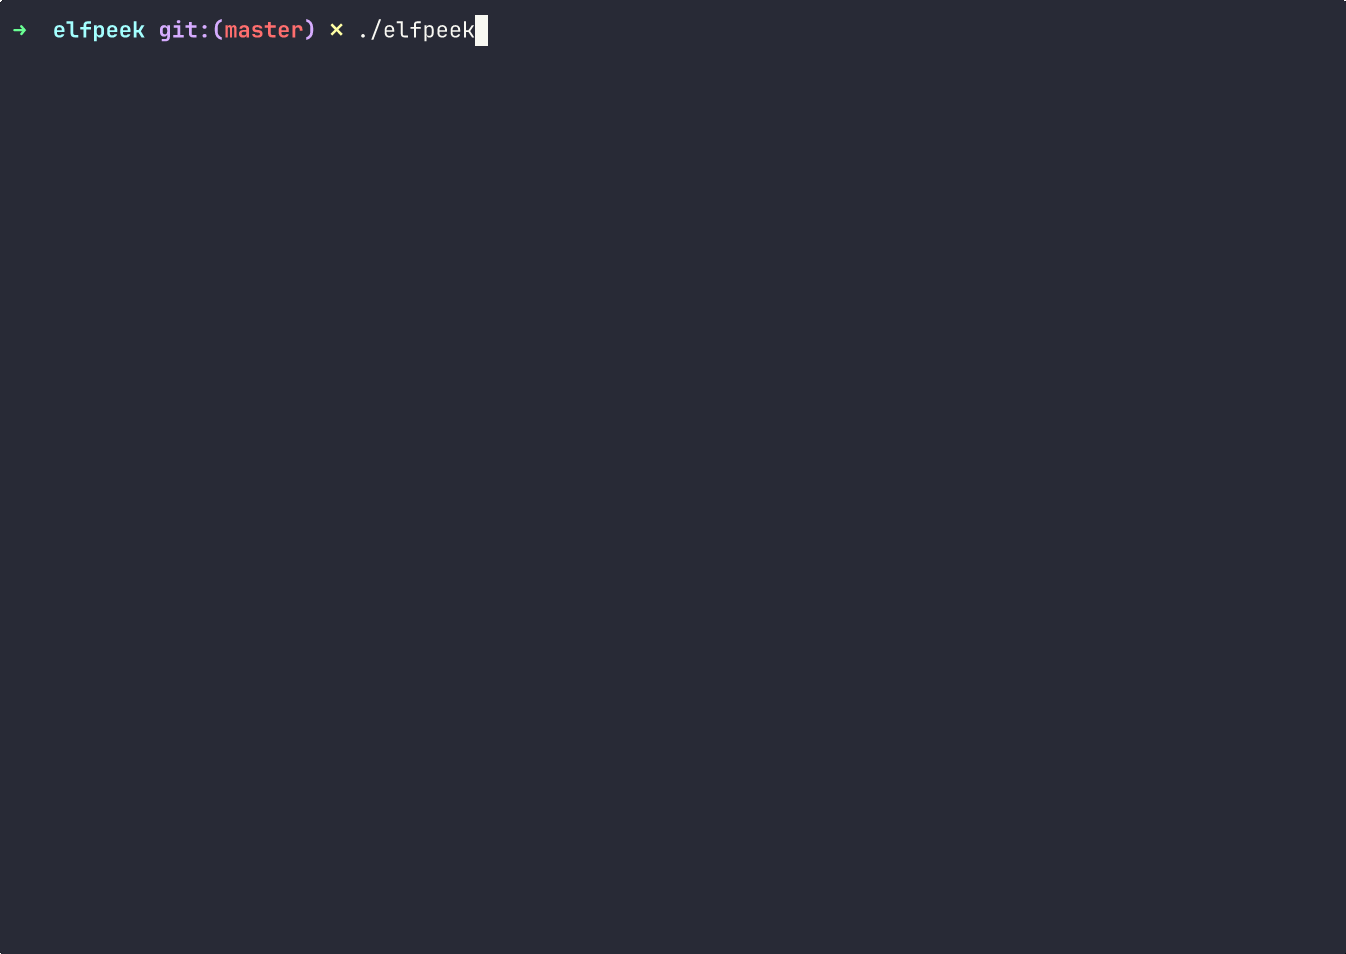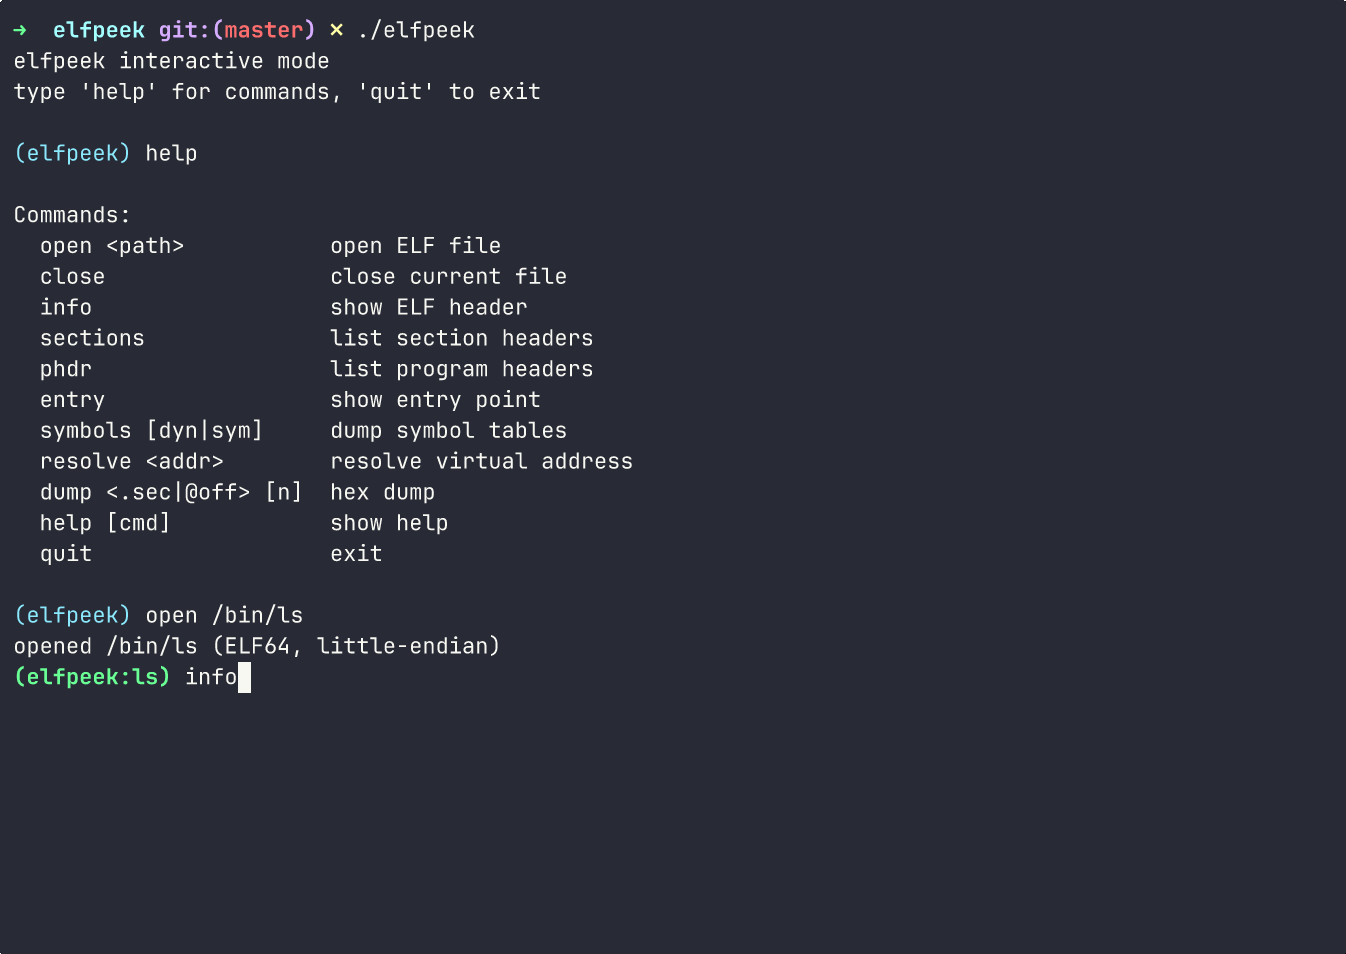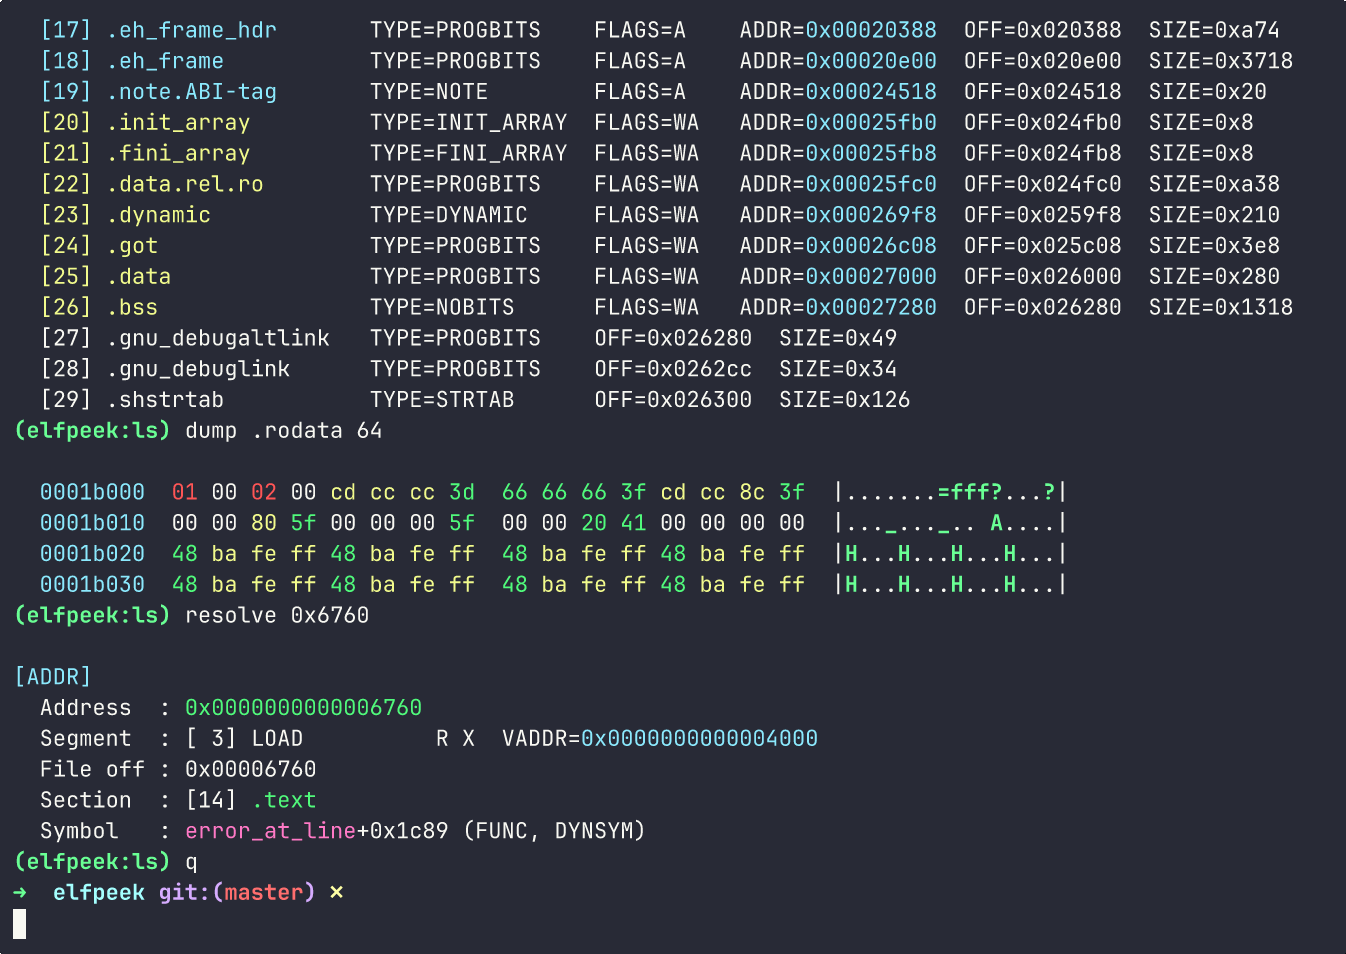 oblivionsage/elfpeek
Minimal ELF inspector written in C for quick binary layout inspection
 morluto/rea
Reverse engineer anything with agents, from app behavior down to native binaries.
 icsharpcode/ilspy
.NET Decompiler with support for PDB generation, ReadyToRun, Metadata (&more) - cross-platform!
 zhaoxuya520/reverse-skill
AI-powered skill router pack for reverse engineering, penetration testing, and security research. Routes AI agents to correct methodologies and…
 0x4m4/hexstrike-ai
MCP server enabling AI agents to autonomously execute 150+ cybersecurity tools for automated penetration testing, vulnerability discovery, bug bounty…
 rizinorg/cutter
Free and Open Source Reverse Engineering Platform powered by rizin
 0xor0ne/awesome-list
Cybersecurity oriented awesome list
 zhkl0228/unidbg
Allows you to emulate an Android native library, and an experimental iOS emulation
 albertan017/llm4decompile
Reverse Engineering: Decompiling Binary Code with Large Language Models
 avast/retdec
RetDec is a retargetable machine-code decompiler based on LLVM.