

malware-samples
 jstrosch/malware-samples
Malware samples, analysis exercises and other interesting resources.
binary-analysiscurated-resourceseducation+3
jstrosch/malware-samplesMalware samples, analysis exercises and other interesting resources.
 lauriewired/malimite
iOS and macOS Decompiler
 mertdas/privkit
PrivKit is a simple beacon object file that detects privilege escalation vulnerabilities caused by misconfigurations on Windows OS.
 hasherezade/pe-bear-old
PE-bear (builds only)
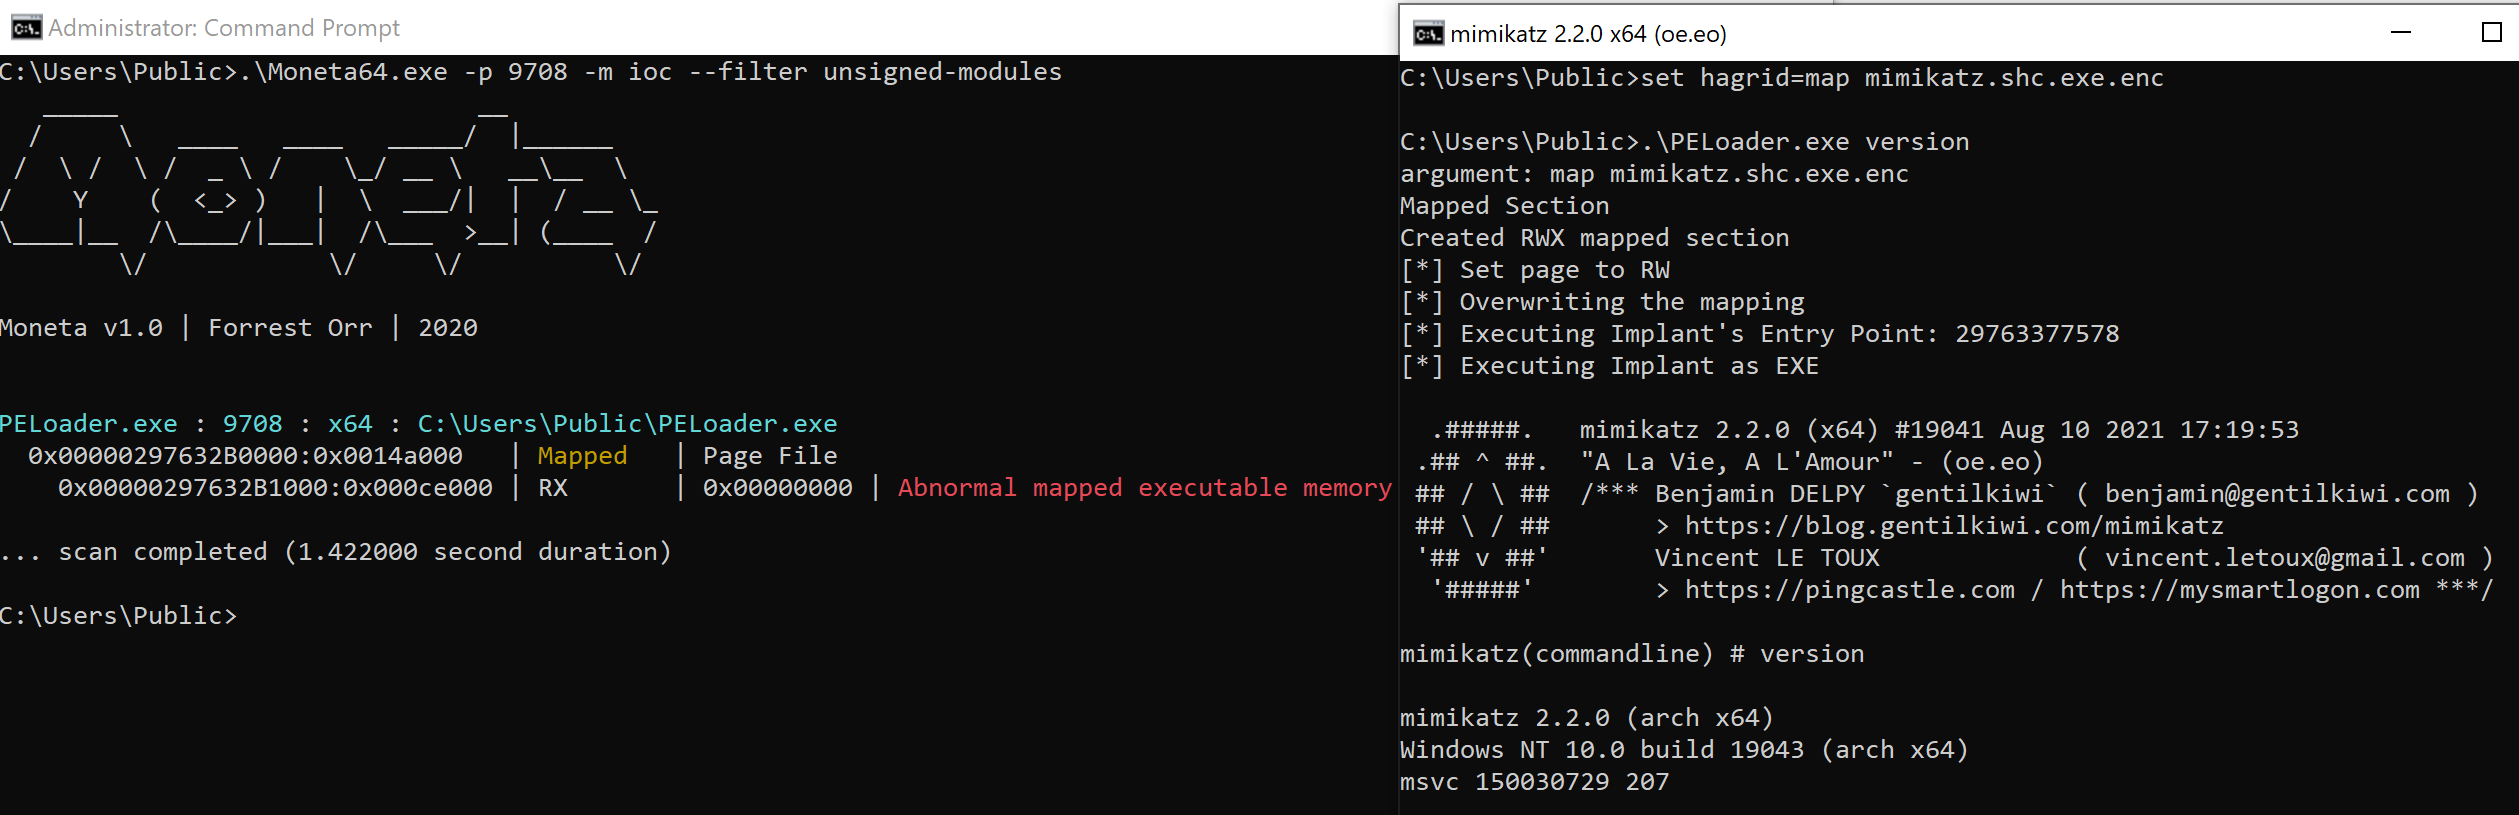 hagrid29/peloader
PE loader with various shellcode injection techniques
 nccgroup/driverbuddy
DriverBuddy is an IDA Python script to assist with the reverse engineering of Windows kernel drivers.
 dsecurity/efiseek
Ghidra plugin that automates UEFI firmware analysis by identifying known GUIDs, protocols, SMI handlers, and interrupt functions, with headless…
 jjyg/metasm
This is the main repository for metasm, a free assembler / disassembler / compiler written in ruby
 volatilityfoundation/dwarf2json
convert ELF/DWARF symbol and type information into vol3's intermediate JSON
 quosecgmbh/grap
Define and match user-defined graph patterns against binary control flow graphs using a Capstone-based disassembler, with CLI, Python bindings, and…
 blacksnufkin/rusty-playground
Some Rust program I wrote while learning Malware Development
 clearbluejar/ghidrecomp
Python Command-Line Ghidra Decompiler
 nozominetworks/upx-recovery-tool
Automates repair of malformed UPX headers in ELF binaries, restoring magic, filesize, blocksize, and overlay fields so standard unpackers can process…
 airbus-cert/yara-ttd
Use YARA rules on Time Travel Debugging traces
 bashexplode/boko
Application Hijack Scanner for macOS
 pan-unit42/dotnetfile
Python library for parsing CLR/PE metadata in .NET assemblies, exposing streams and hash fingerprints to support malware analysis and threat hunting.
 trustedsec/lnkmemaybe
Lnk crafting and research tools