

copy-as-yara
 ald3ns/copy-as-yara
This is a little plugin to copy disassembly in a way that is usable in YARA rules!
binary-analysismalware-analysisreverse-engineering+1
48
ald3ns/copy-as-yaraThis is a little plugin to copy disassembly in a way that is usable in YARA rules!
 0x11dfe/file-unpumper
Tool that can be used to trim useless things from a PE file such as the things a file pumper would add.
 talha-nazeef-ahmed/rpc-triage
A zero-symbol static analysis engine that extracts and mathematically ranks the Windows RPC attack surface using an AHP-based risk model.
 mein-0/kaspermeow
Proof-of-concept that exploits a Kaspersky driver vulnerability to leak kernel pointers and bypass KASLR on Windows, enabling kernel exploit chain…
 nccgroup/libtalloc
libtalloc is a python script for use with GDB that can be used to analyse the "trivial allocator" (talloc)
 ejfkdev/dae
Config-driven Dart AOT snapshot analyzer that exports blutter-compatible symbols and structs for IDA, radare2 and Frida, and decompiles functions…
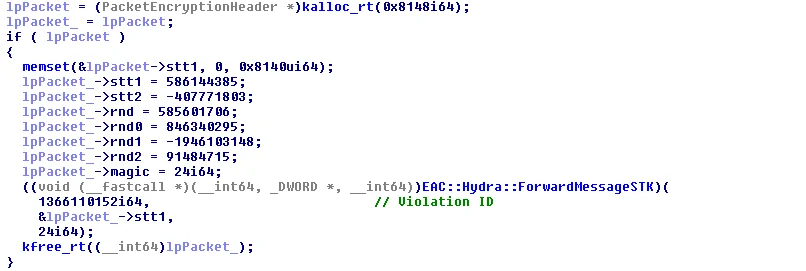 gmh5225/eac-kernel-packet-fucker
Reverse-engineered Easy Anti-Cheat kernel driver bypass that intercepts memory allocation to suppress violation packets, with report decryption…
 gmh5225/frida-il2cpp-datacollector
Frida-based tool that ports Cheat Engine's MonoDataCollector to Android and iOS, enabling runtime Mono/IL2CPP data collection and memory inspection…
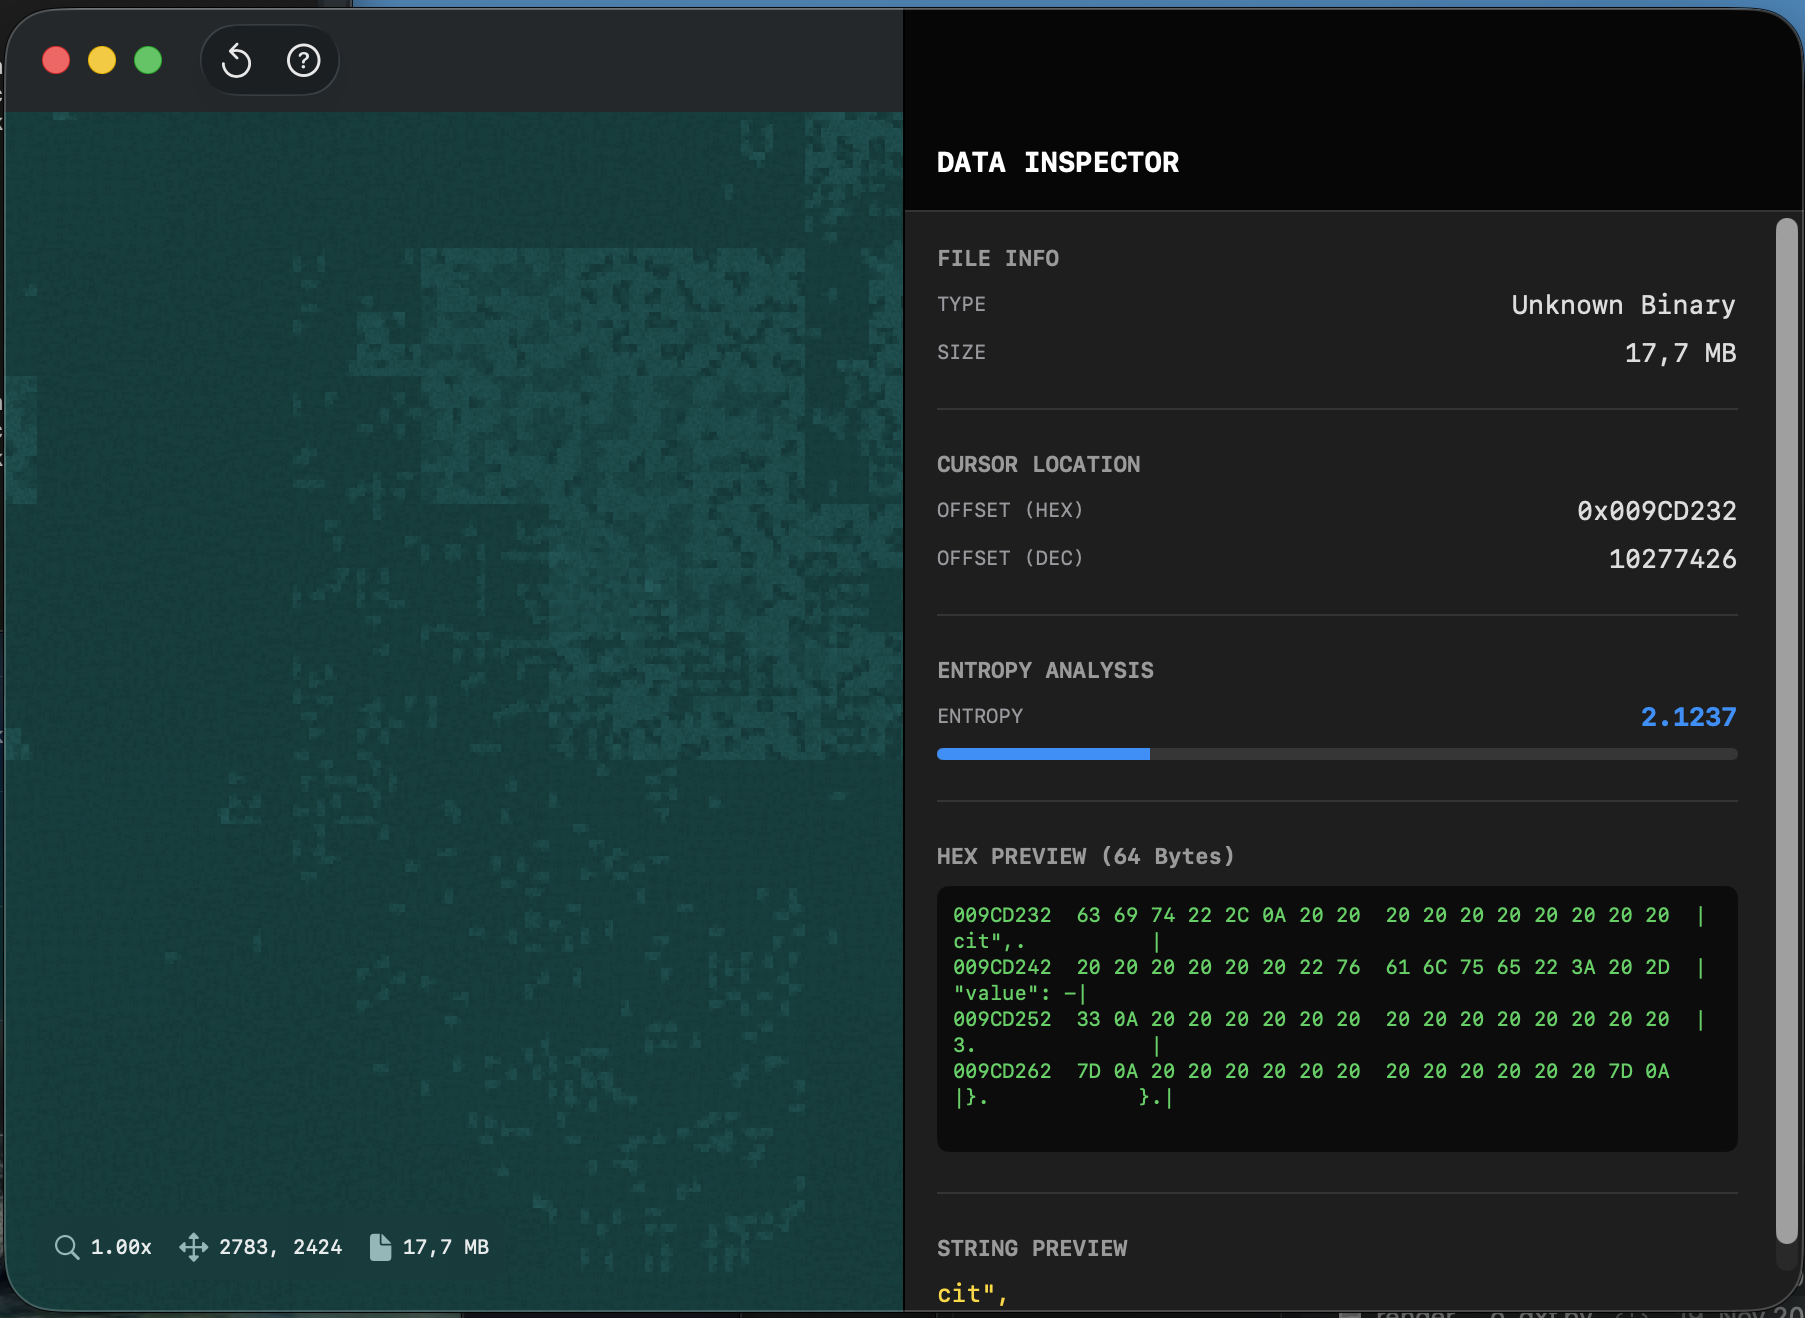 farukalpay/neurocore
NeuroCore is a native macOS application that visualizes the internal structure of binary files using a Hilbert Curve mapping and Shannon Entropy…
 gmh5225/letmegg
Windows kernel proof-of-concept demonstrating an anti-debugging technique that prevents WinDbg from breaking by manipulating the kernel exception…
 0x574r/darkcloak
Linux process identity cloaking tool that spoofs comm, argv, cmdline, environ, exe path, and VMAs via an 11-phase prctl pipeline to impersonate…
 ea/xfg_analyzer
A Binary Ninja plugin that uses bruteforced XFG hashes to recover precise function prototypes
 kaandemir993/formbook-payload-extraction-xor-decryption-net-assembly-analysis
Reverse engineering analysis of Formbook, an info-stealer that uses .NET assembly manipulation and XOR decryption. Full payload extracted via x32dbg,…
 backdoorskid/win-def-clickfix
A scanner that estimates whether Microsoft Defender is likely to flag a command as ClickFix.
 myrtus0x0/smoke_conf_extract
Static config extractor for SmokeLoader samples that deobfuscates, unpacks, and emulates protected routines to recover final-stage C2 settings.
 xf1les/fsop-finder
Binary Ninja plugin that scans glibc libio for FSOP code paths capable of hijacking control flow and stack pointer, aiding heap exploitation research.
 dump-guy/sc2elf
Simple dotnet Native AOT app that uses LibObjectFile to convert shellcode to ELF
 gmh5225/driver-hidekernelthread-iocancelirp
Windows kernel driver technique that hides kernel threads by abusing IoCancelIrp and IRP cancel routines, with detection methods for identifying…