
Manalyze
 justicerage/manalyze
Static analyzer for PE executables with plugin-based detection of packers, compilers, suspicious imports, cryptographic constants, and ClamAV…
binary-analysismalware-analysisreverse-engineering+2
1.1k
justicerage/manalyzeStatic analyzer for PE executables with plugin-based detection of packers, compilers, suspicious imports, cryptographic constants, and ClamAV…
 weak1337/alcatraz
x64 binary obfuscator for PE files with control flow flattening, anti-disassembly, import obfuscation, and instruction mutation to hinder reverse…
 hasherezade/libpeconv
Custom PE loading and manipulation library for manual mapping, IAT hooking, memory dumping, and rebuilding imports for malware analysis and reverse…
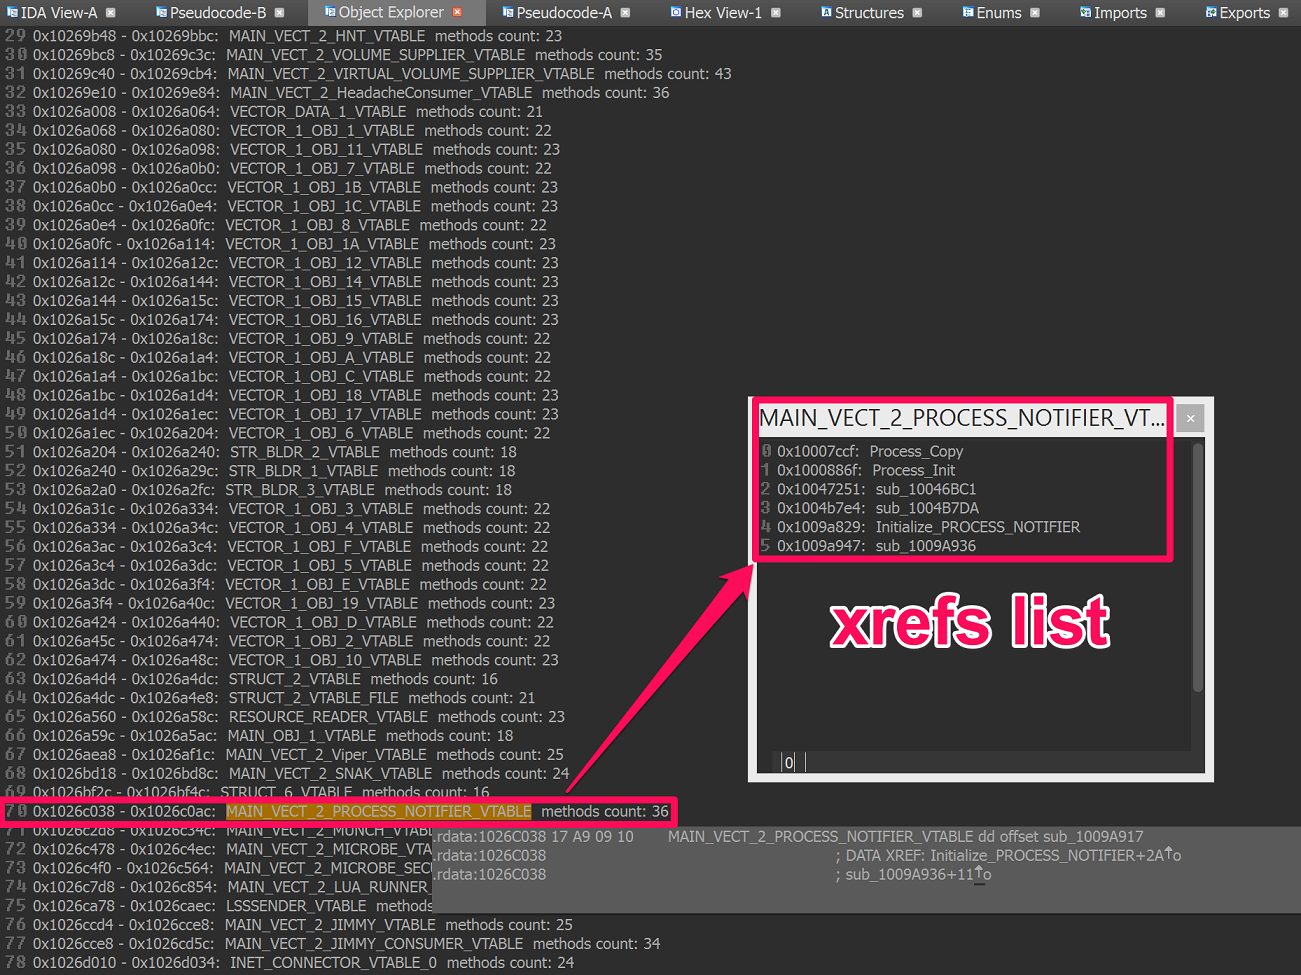 rehints/hexrayscodexplorer
Hex-Rays Decompiler plugin for better code navigation
 lifting-bits/remill
Library for lifting machine code to LLVM bitcode
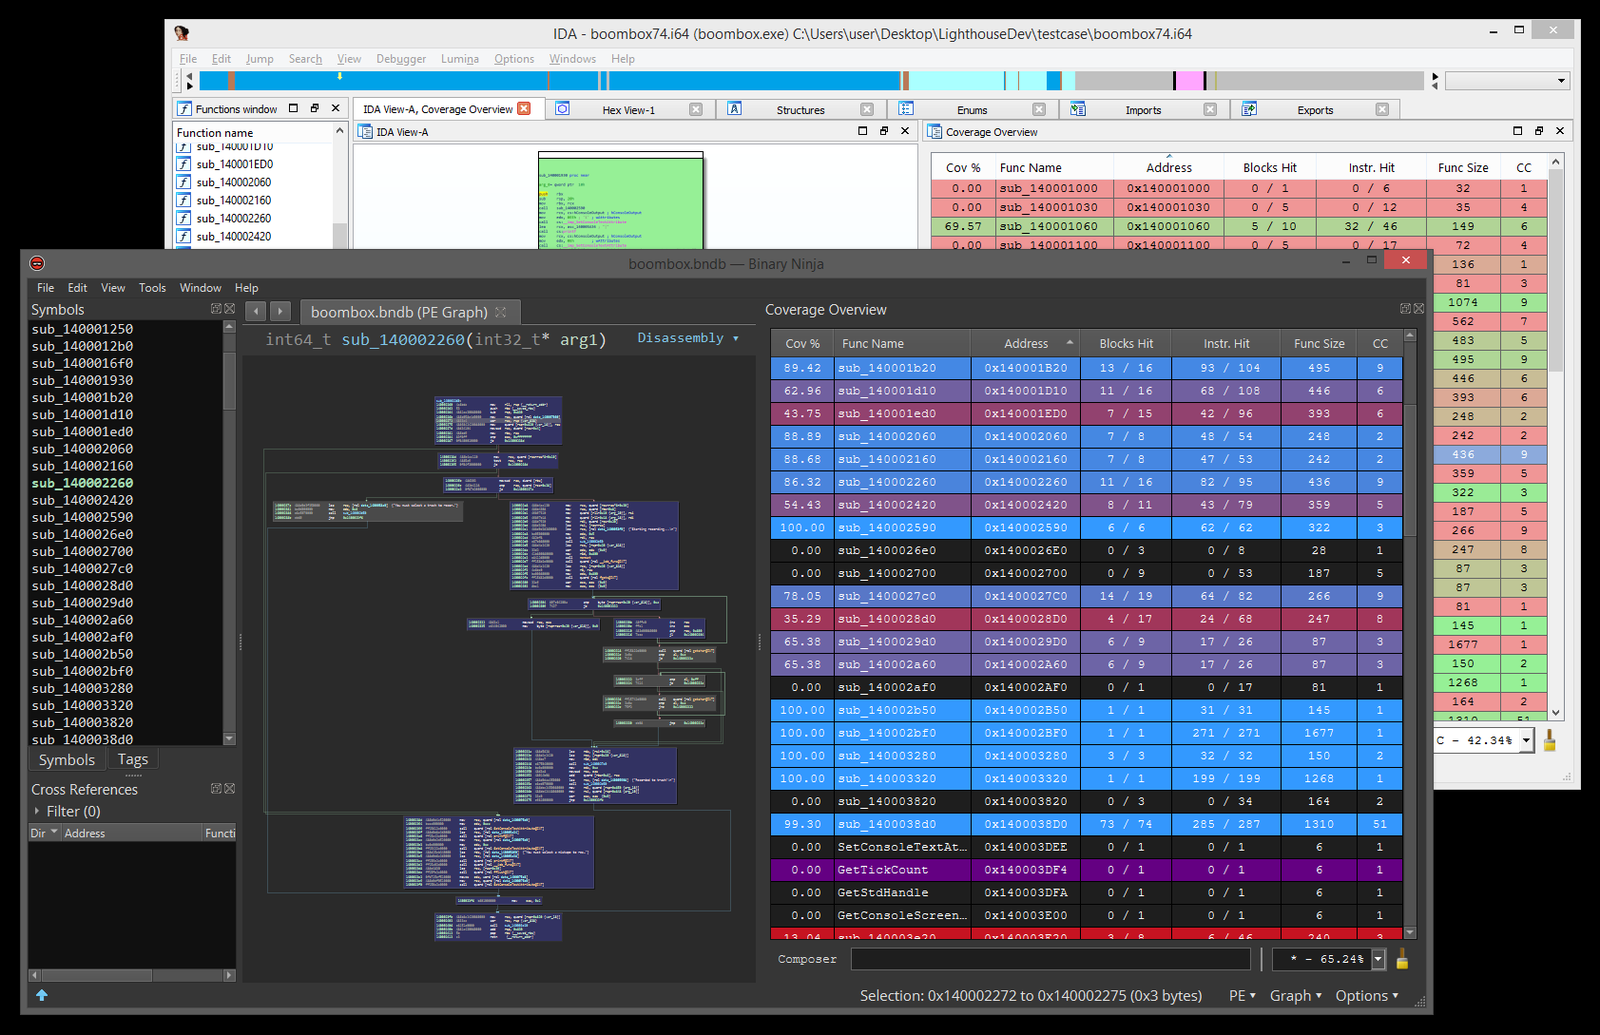 gaasedelen/lighthouse
A Coverage Explorer for Reverse Engineers
 viruscamp/luadec
Lua Decompiler for lua 5.1 , 5.2 and 5.3
 washi1337/asmresolver
A library for creating, reading and editing PE files and .NET modules.
 0vercl0k/wtf
Distributed, code-coverage guided snapshot-based fuzzer for user and kernel-mode targets on Windows and Linux, with emulator and hypervisor backends.
 intelxed/xed
Low-level library for encoding and decoding IA32/Intel64 x86 instructions, exposing APIs for instruction length, operands, categories, control-flow…
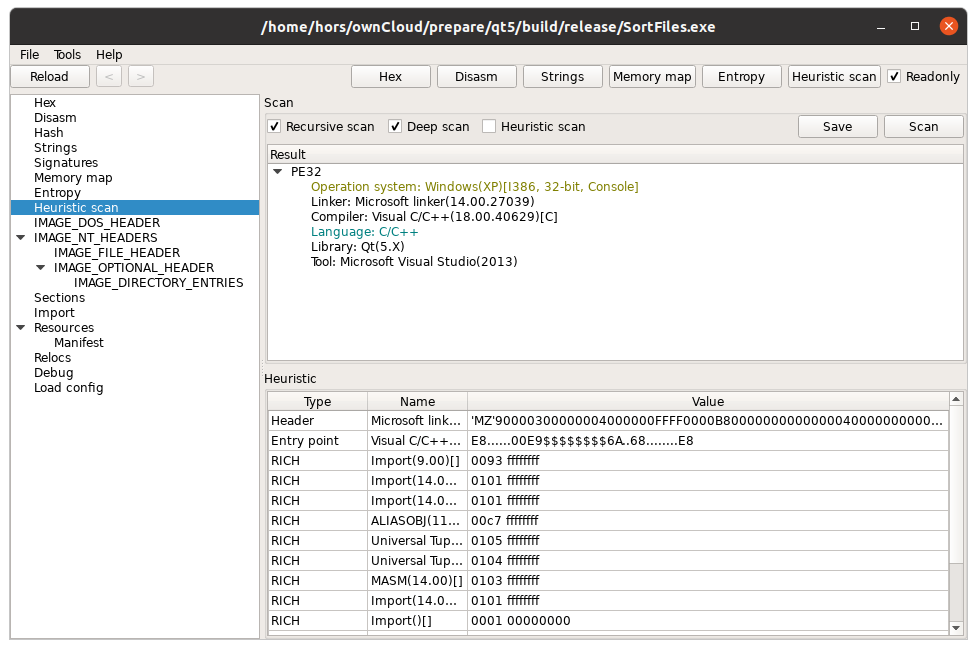 horsicq/xpeviewer
PE file viewer/editor for Windows, Linux and MacOS.
 rehints/efixplorer
IDA plugin and loader for UEFI firmware analysis and reverse engineering automation
 rizinorg/rz-ghidra
Deep ghidra decompiler and sleigh disassembler integration for rizin
 trustedsec/coffloader
Run Beacon Object Files (BOFs) outside Cobalt Strike by parsing 64-bit COFF object files, with Beacon-compatible argument generation and helper…
 med0x2e/sigflip
SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.
 withsecurelabs/python-exe-unpacker
A helper script for unpacking and decompiling EXEs compiled from python code.
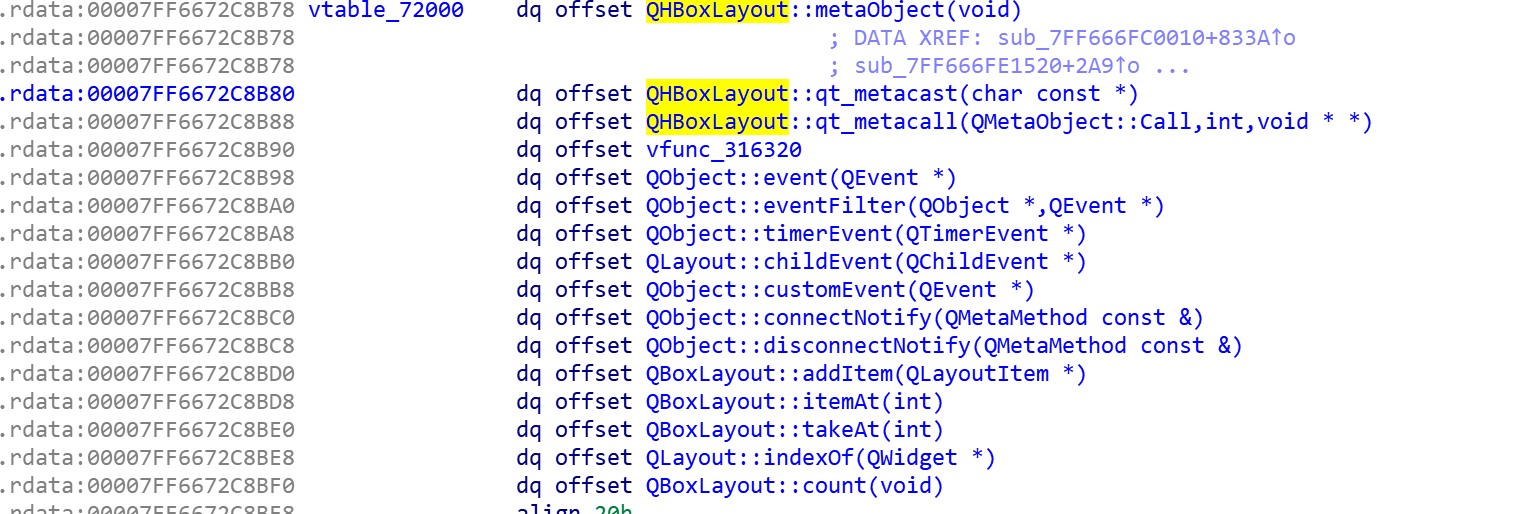 0xgalz/virtuailor
IDAPython tool for creating automatic C++ virtual tables in IDA Pro
 chip-red-pill/microcodedecryptor
Decrypts Intel Atom microcode updates and unpacks XuCode with recovered RC4 keys, revealing internal CPU microcode structures for hardware security…