
polypyus
 seemoo-lab/polypyus
Binary-only firmware historian that learns to locate functions in raw binaries by extracting known functions from similar binaries, enabling fast…
binary-analysisembedded-systems-securityfirmware-analysis+1
233
seemoo-lab/polypyusBinary-only firmware historian that learns to locate functions in raw binaries by extracting known functions from similar binaries, enabling fast…
 nccgroup/winstrument
Winstrument is a framework of modular scripts to aid in instrumenting Windows software using Frida for reverse engineering and attack surface…
 de4dot/de4dot
.NET deobfuscator and unpacker.
 google/path-auditor
Runtime libc function auditor that detects file access race conditions and symlink vulnerabilities by hooking filesystem syscalls via LD_PRELOAD,…
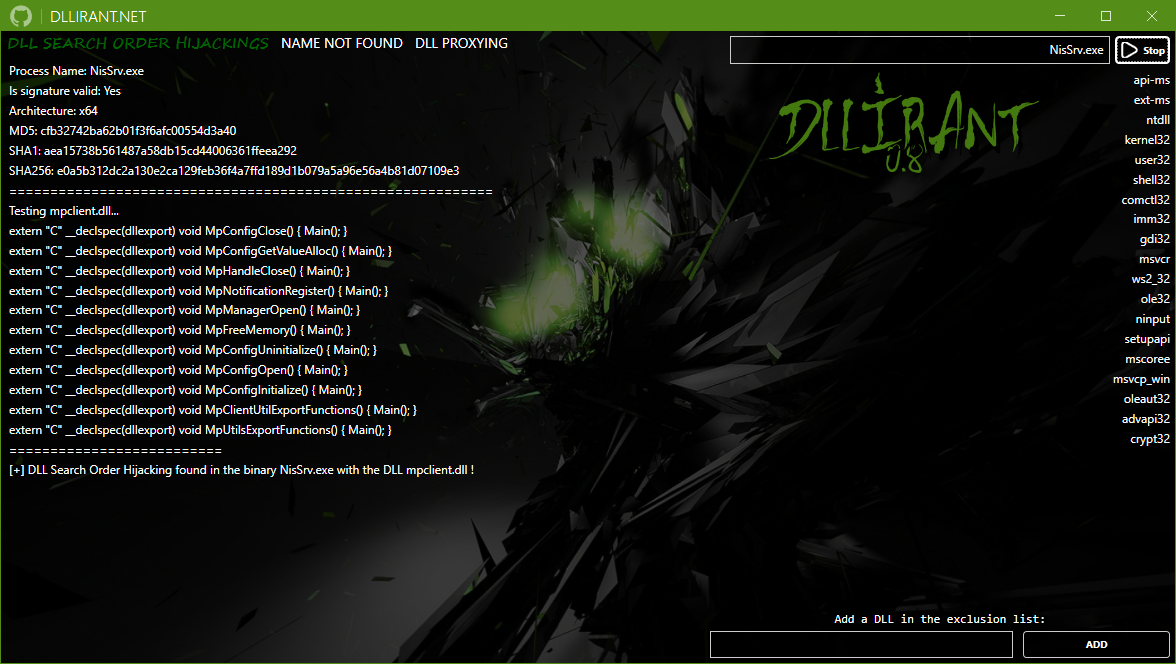 redteamsocietegenerale/dllirant
DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.
 robertdfrench/ifuncd-up
GNU IFUNC is the real culprit behind CVE-2024-3094
 1rhino2/fnprint
match functions in binaries by what they do, not what their bytes look like. behavioral function fingerprinting via microexecution.
 zer0condition/reversekit
x64 Dynamic Reverse Engineering Toolkit
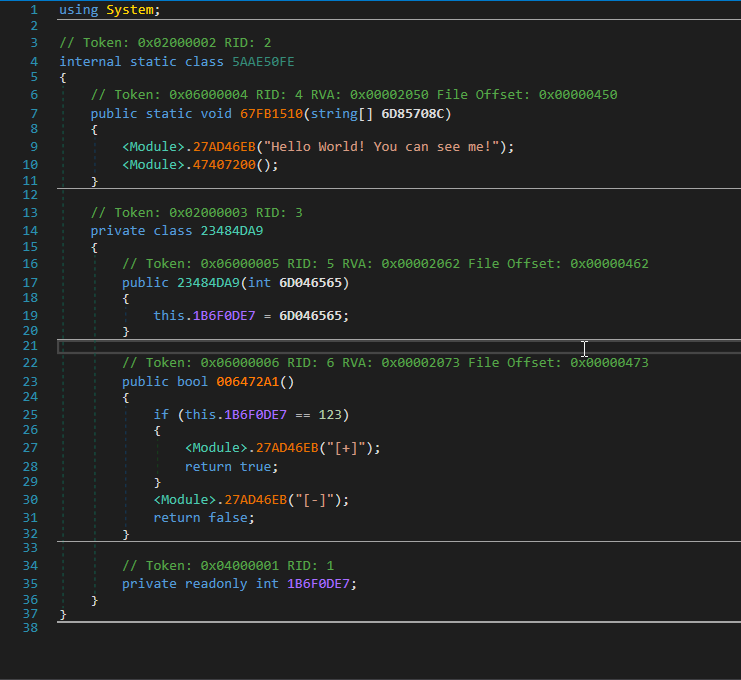 void-stack/vmunprotect.dumper
VMUnprotect.Dumper can dynamically untamper VMProtected Assembly.
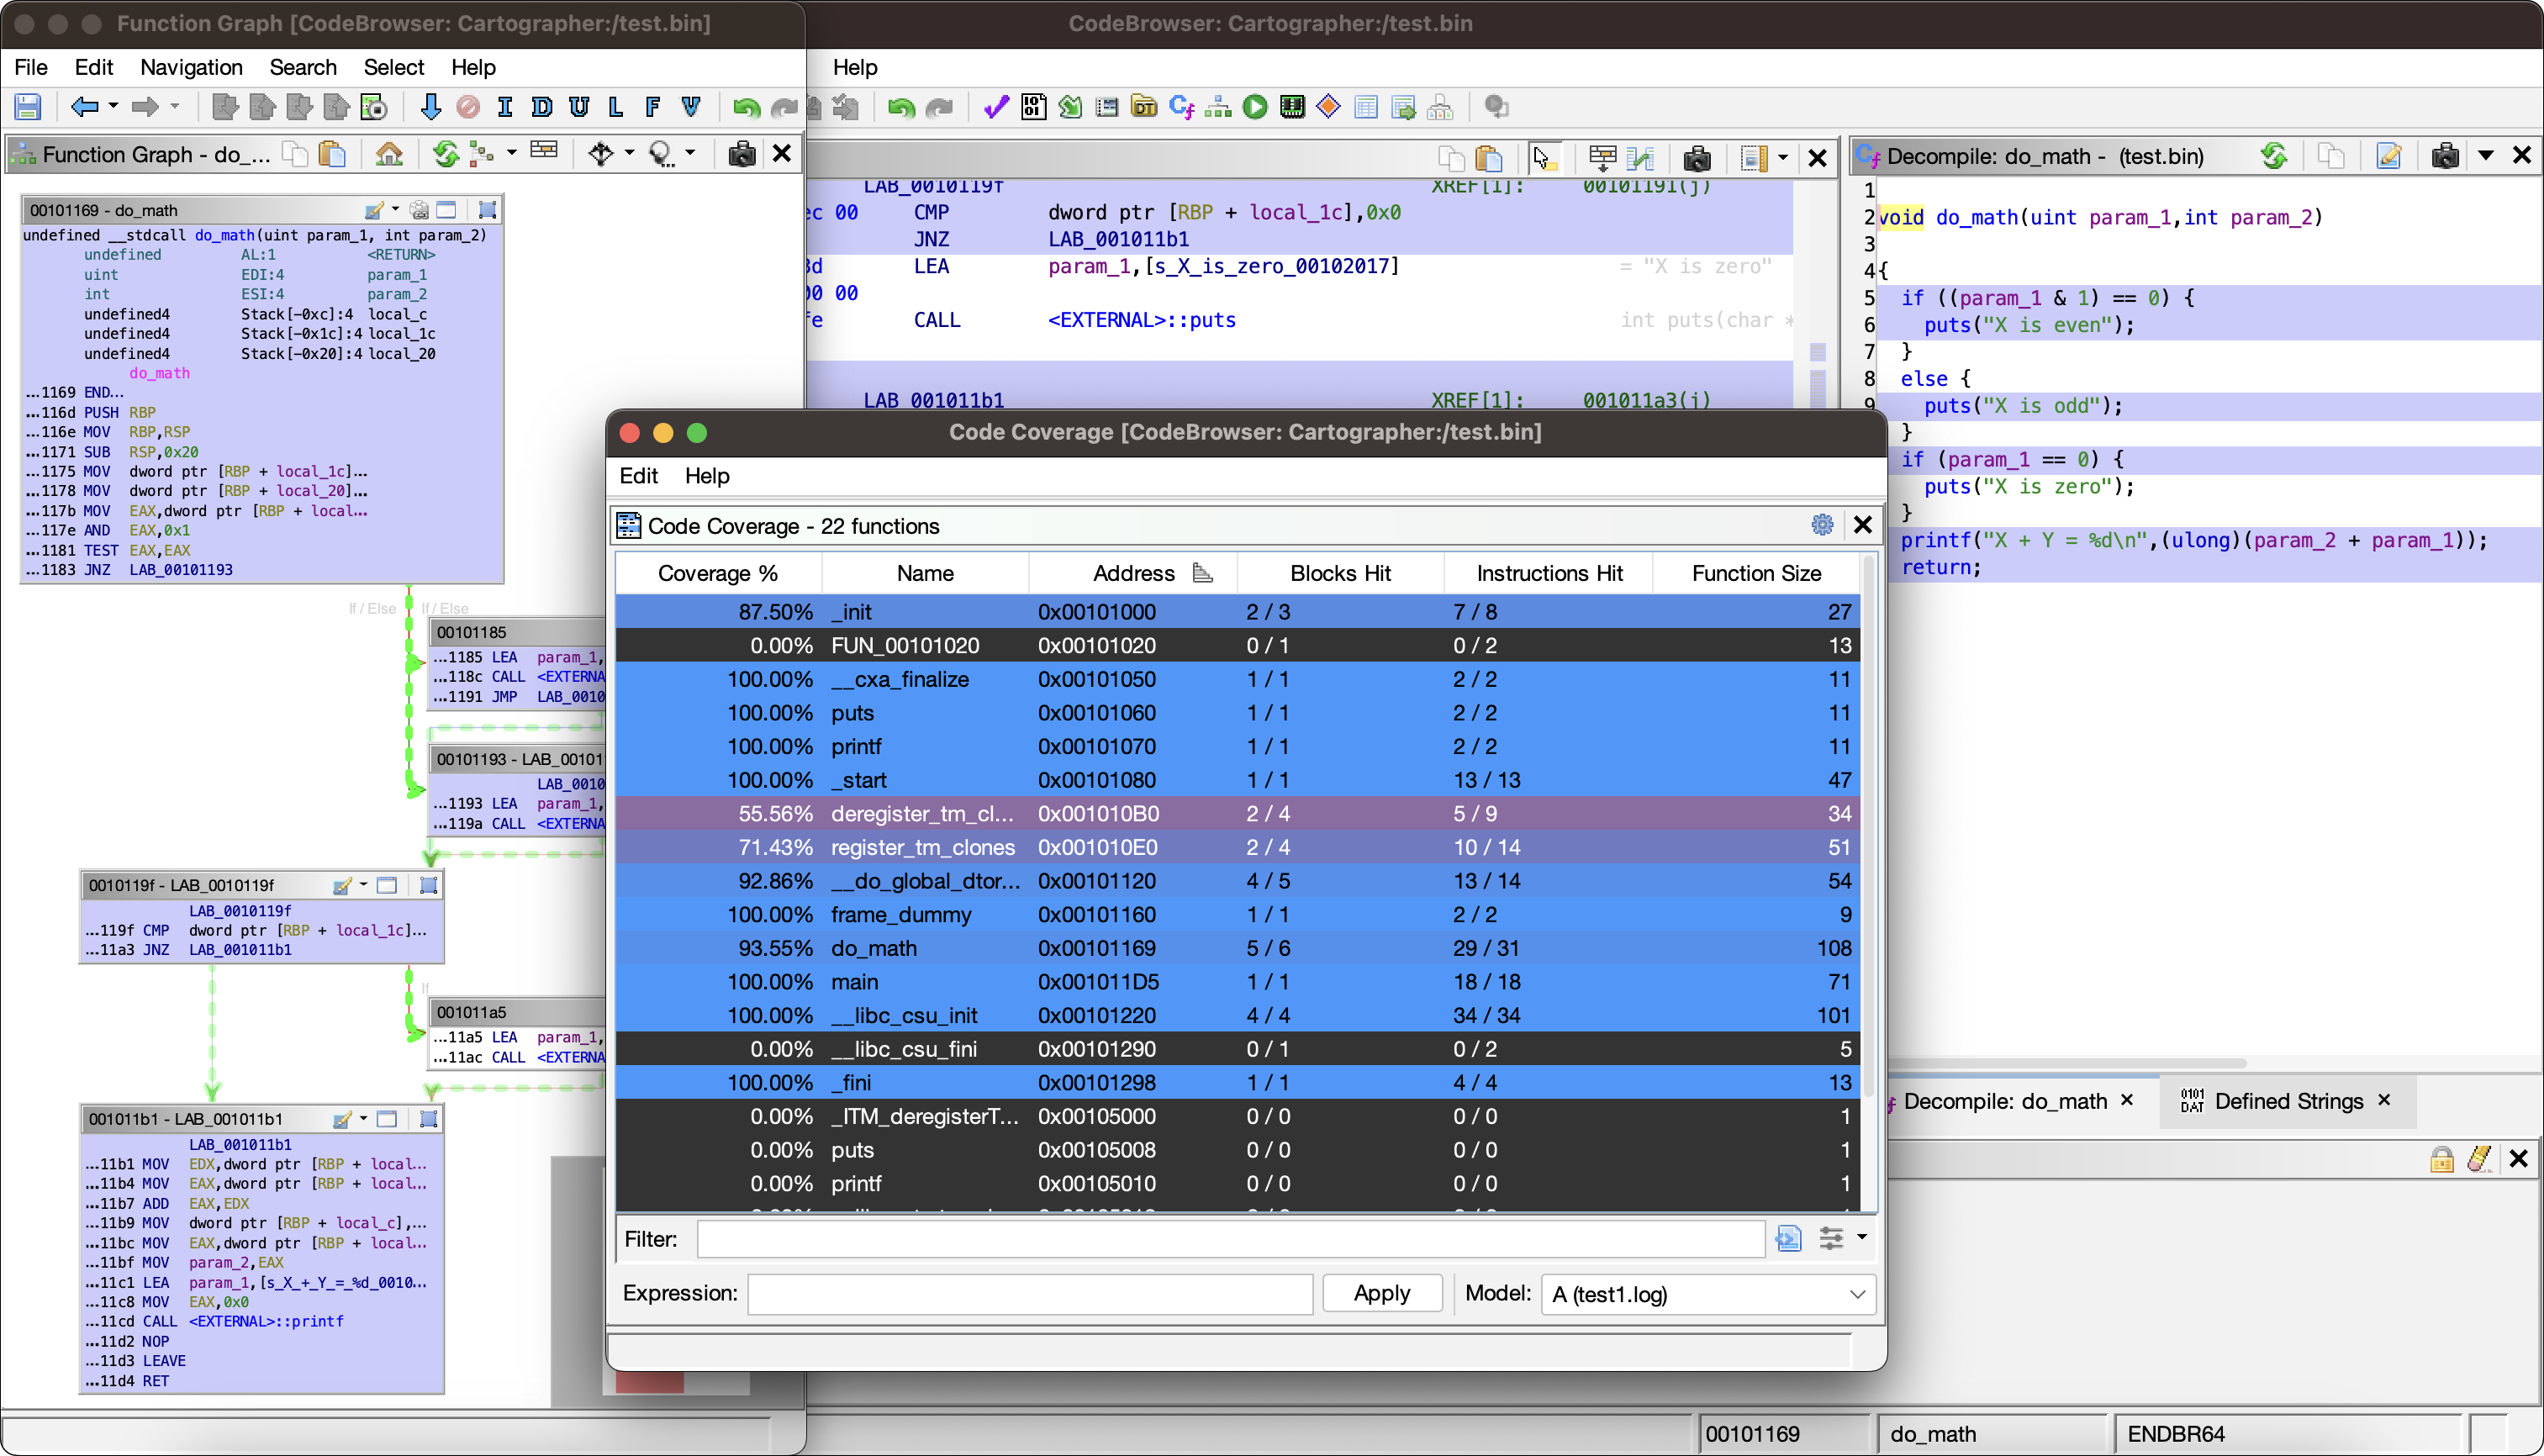 nccgroup/cartographer
Code Coverage Exploration Plugin for Ghidra
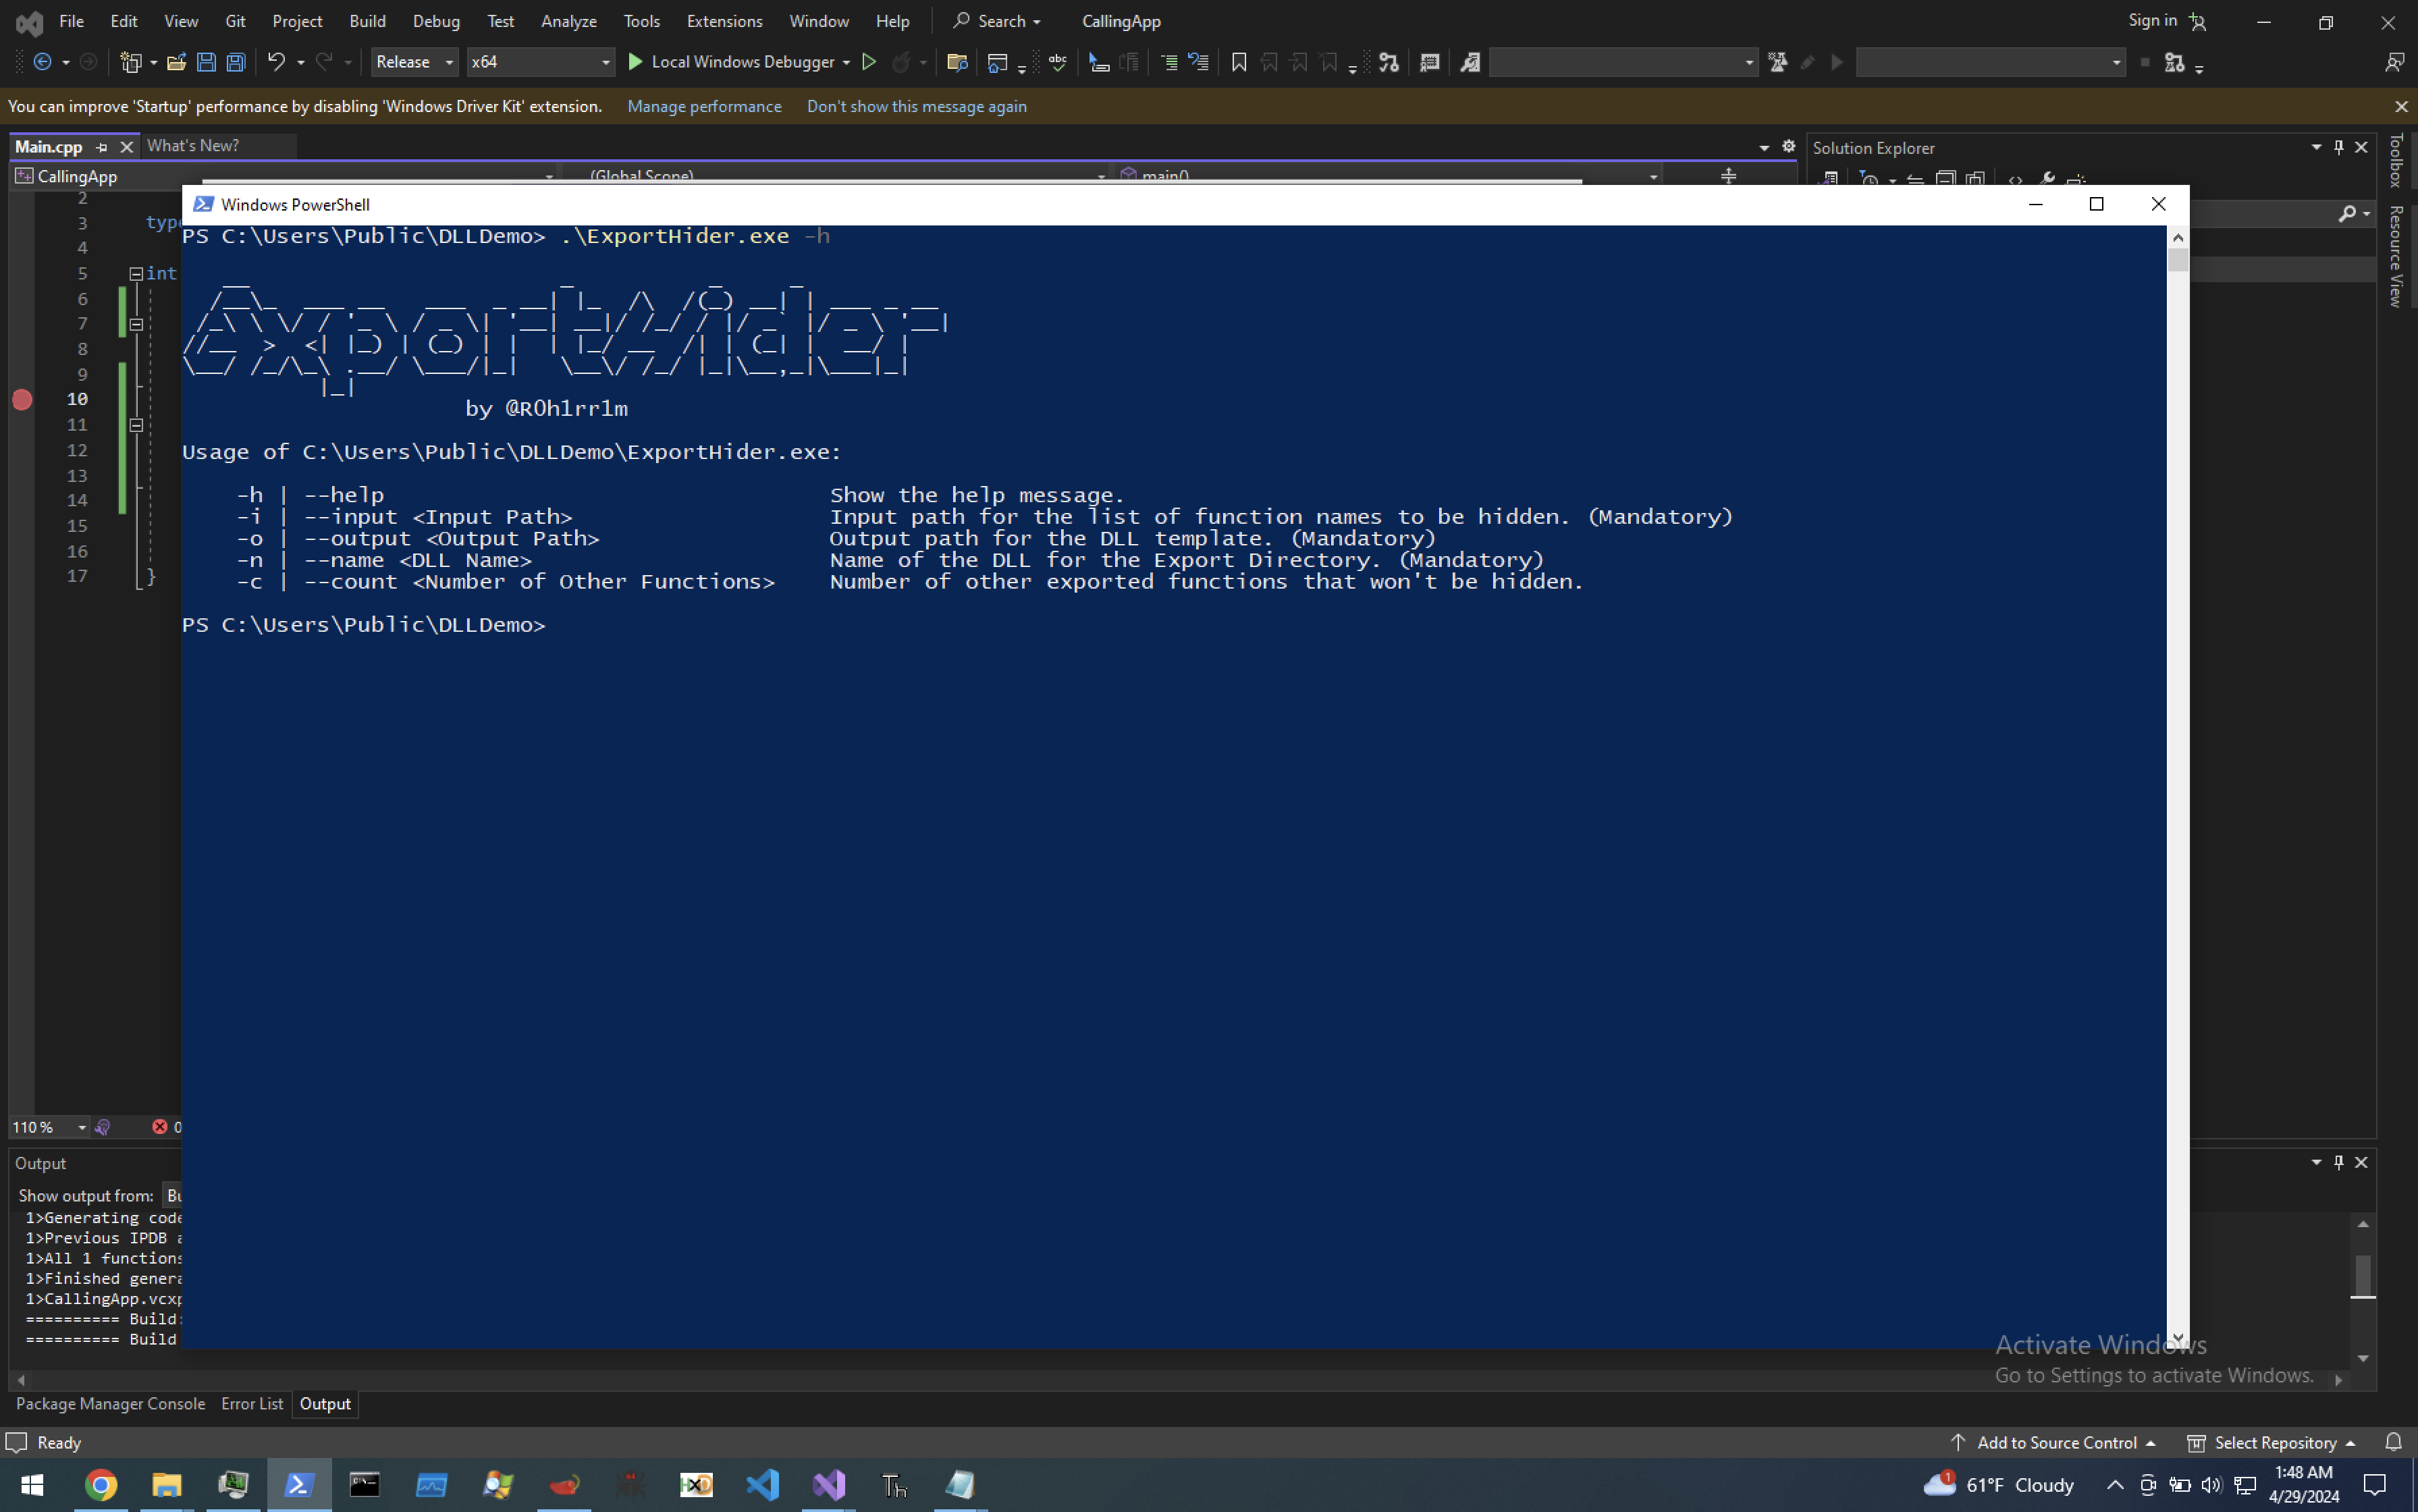 frkngksl/exporthider
ExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.
 zxgio/ghidra_stack_strings
A script to detect stack-strings by using emulation (leveraging Unicorn)
 sentinel-one/peafl64
Static Binary Instrumentation tool for Windows x64 executables
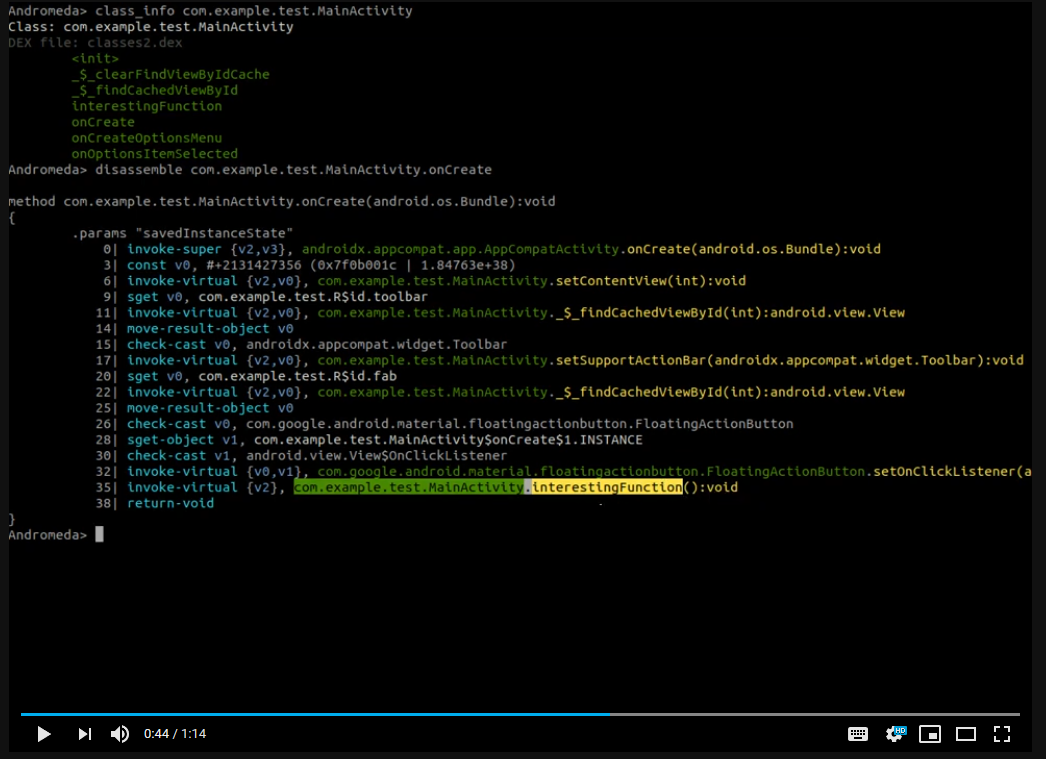 secrary/andromeda
C/C++ interactive reverse engineering tool for Android applications, enabling fast static analysis and binary inspection of APK files.
 mg1937/asc
Fast Android APK decompiler front-end that queries compiled DEX artifacts directly, extracting classes and cross-references in milliseconds without…