
apk-medit
 sterrasec/apk-medit
memory search and patch tool on debuggable apk without root & ndk
android-securitybinary-analysismemory-forensics+2
434
sterrasec/apk-meditmemory search and patch tool on debuggable apk without root & ndk
 xoreaxeaxeax/hexcymatix
Visualizes repeated byte sequences in binary files to reveal hidden structure, supporting reverse engineering and pattern discovery without…
 nccgroup/edidfuzzer
EDID (Enhanced Display Identification Data) Fuzzer
 0xusmanismail/lure
Local Linux binary analysis tool that runs untrusted ELFs in an isolated sandbox (namespaces + strace) and produces structured behavioral reports…
 lkimuk/reark
An intelligent reverse engineering analysis tool designed for multiple target platforms, currently supporting HarmonyOS (HAP/APP/ABC) and Android…
 google/enjarify
Translates Dalvik bytecode (DEX/APK) to equivalent Java bytecode, enabling Java analysis tools to process Android applications with high correctness…
 google/bindiff
Quickly find differences and similarities in disassembled code
 amperclock/cve-2025-9491_poc
Proof-of-Concept of the CVE-2025-9491 using invisible characters in the arguments of a Windows shortcut file (.lnk)
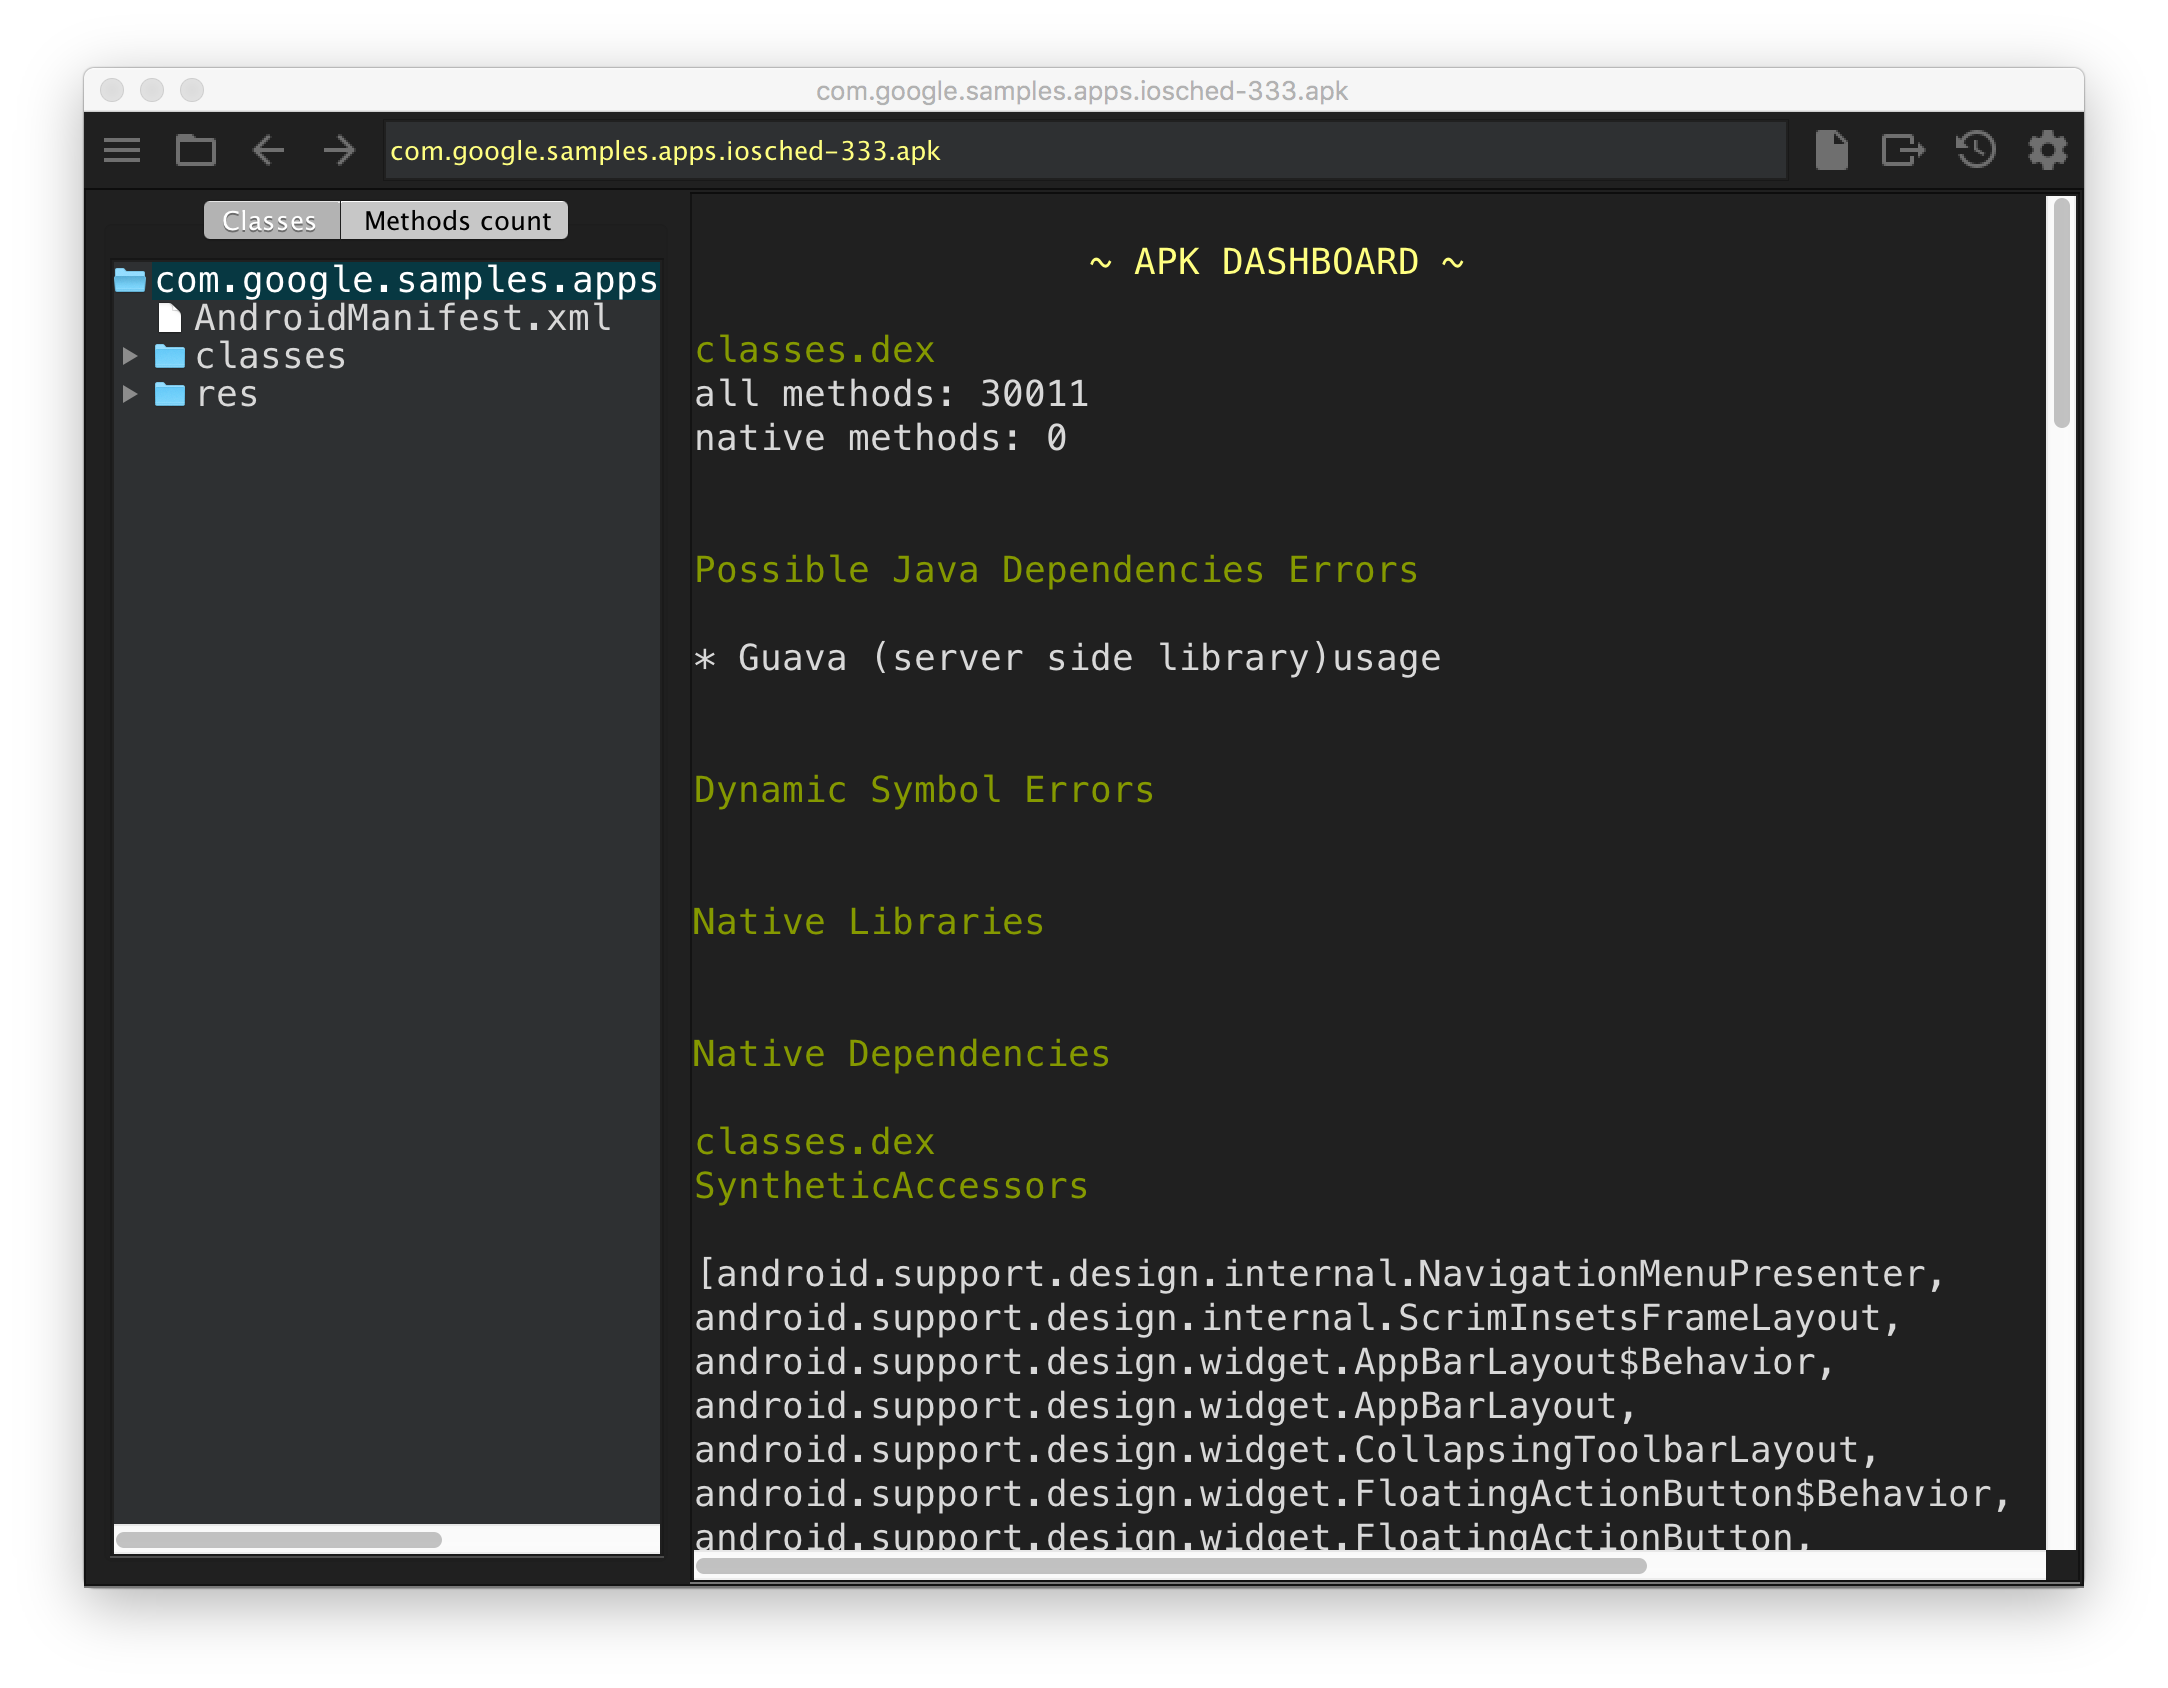 google/android-classyshark
Android and Java bytecode viewer
 trustedsec/ts_llmlib
Python library for local LLM-powered security analysis with Ghidra binary analysis, C/C++ vulnerability scanning, and MCP tool integration for…
 gamozolabs/applepie
A hypervisor for fuzzing built with WHVP and Bochs
 lab52io/leakedhandlesfinder
Leaked Windows processes handles identification tool
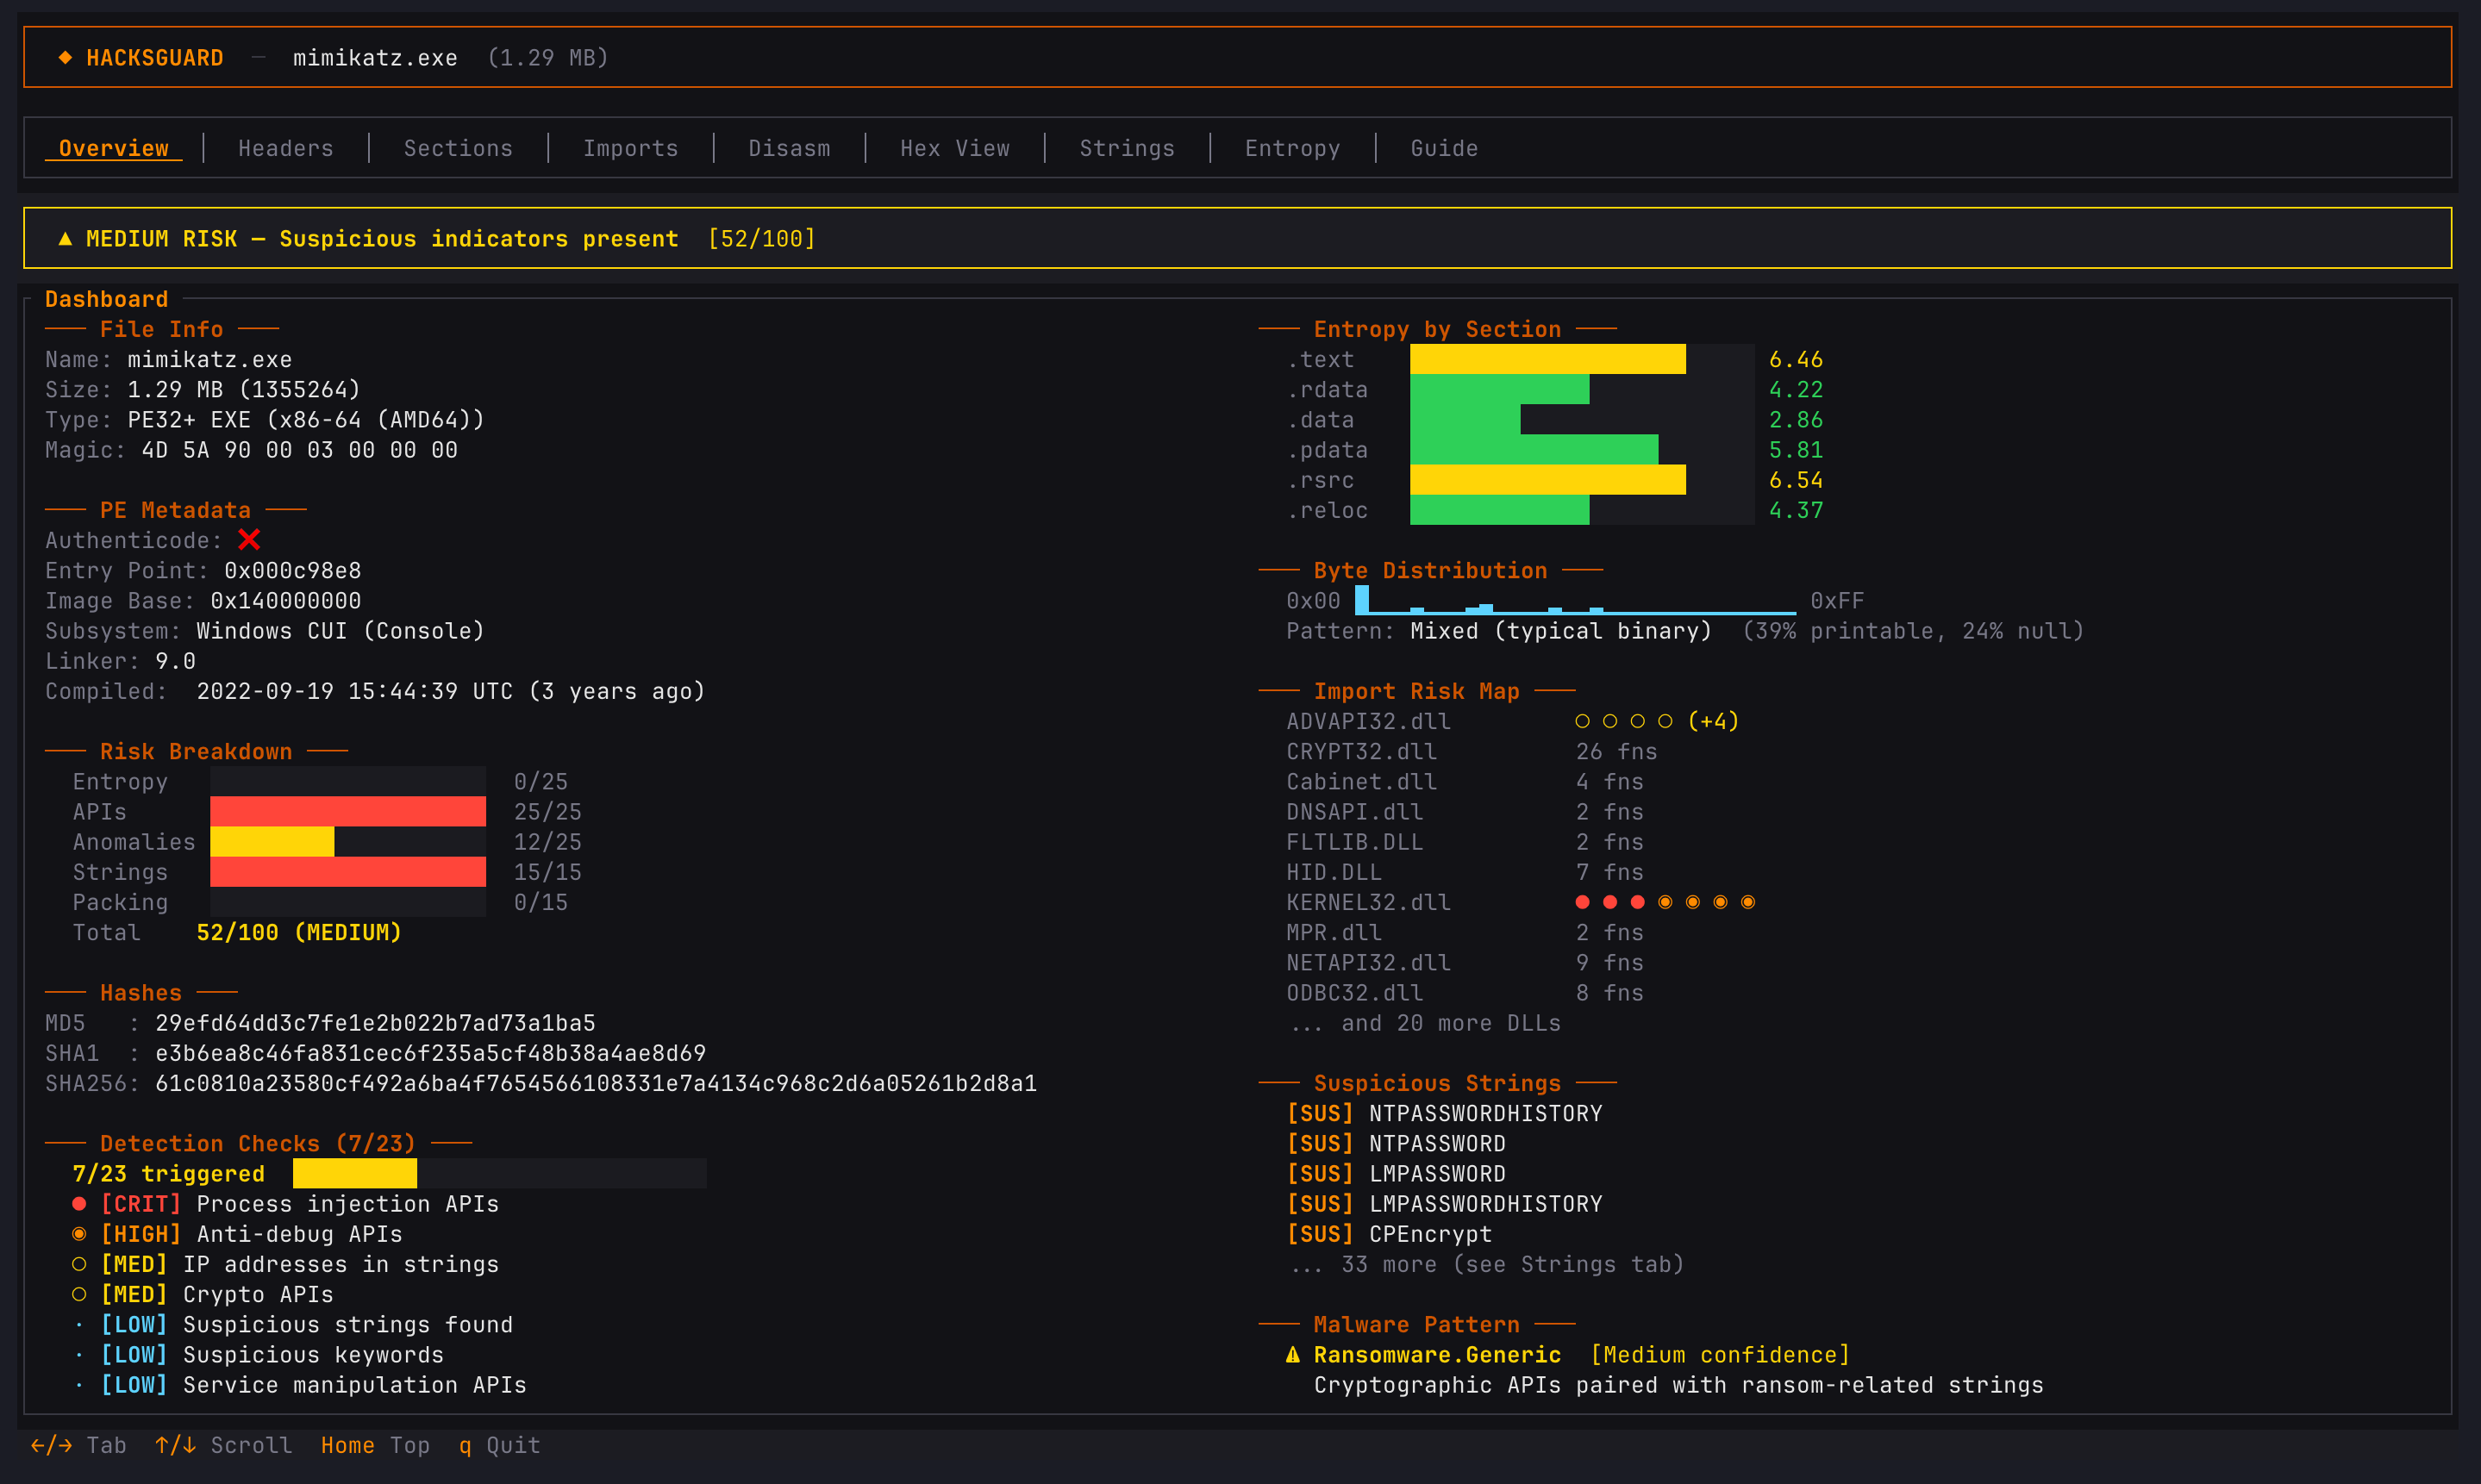 rhacknarok/hacksguard
A blazingly fast, multi-threaded TUI malware analysis tool built in Rust. Features deep PE parsing, YARA scanning, and heuristic risk scoring.
 jwalker/frida-ios-dump-modern
An updated Frida iOS dump tool supporting the latest Frida 17.5.2 APIs
 vulnex/bytesrevealer
Online Reverse Enginerring viewer
 r00tkitsmm/pishi
Pishi is a code coverage tool like kcov for macOS.
 c3rb3ru5d3d53c/mwcfg
A Feature Rich Modular Malware Configuration Extraction Utility for MalDuck
 rasetsuu/vmprotect-research
Generalized VMProtect devirtualizer supporting versions 1.x–3.x. Standalone CLI tool and Ghidra plugin for automated bytecode decoding, handler…