

speakeasy
 mandiant/speakeasy
Windows malware emulation framework that executes binaries, drivers, and shellcode in a modeled runtime, emulating APIs, process/thread behavior,…
binary-analysisdynamic-analysis-sandboxingmalware-analysis+1
2.1k
mandiant/speakeasyWindows malware emulation framework that executes binaries, drivers, and shellcode in a modeled runtime, emulating APIs, process/thread behavior,…
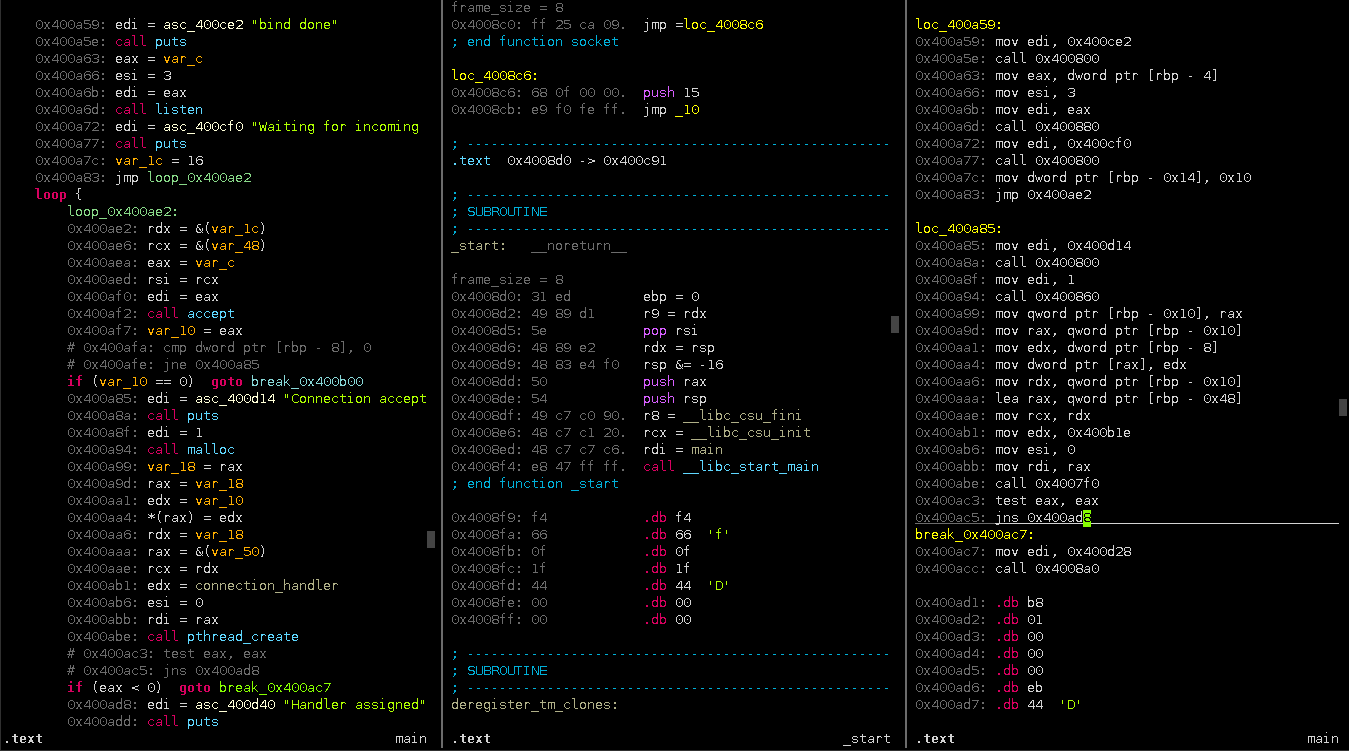 plasma-disassembler/plasma
Plasma is an interactive disassembler for x86/ARM/MIPS. It can generates indented pseudo-code with colored syntax.
 googleprojectzero/jackalope
Binary, coverage-guided fuzzer for Windows, macOS, Linux and Android
 fkie-cad/fact_core
Firmware Analysis and Comparison Tool
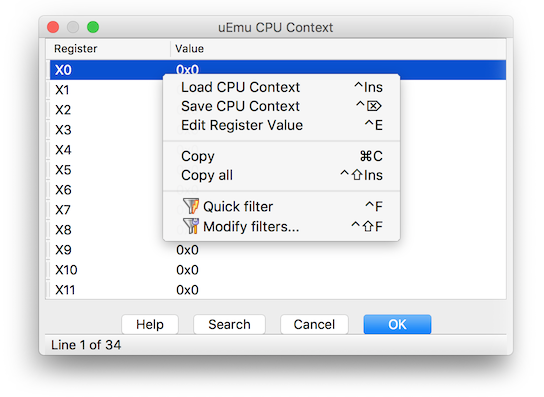 alexhude/uemu
Tiny cute emulator plugin for IDA based on unicorn.
 intelxed/xed
Low-level library for encoding and decoding IA32/Intel64 x86 instructions, exposing APIs for instruction length, operands, categories, control-flow…
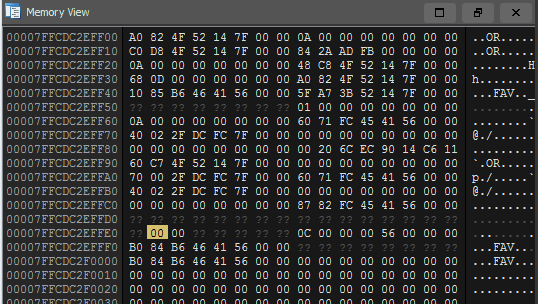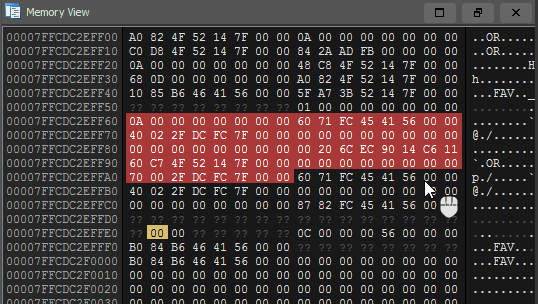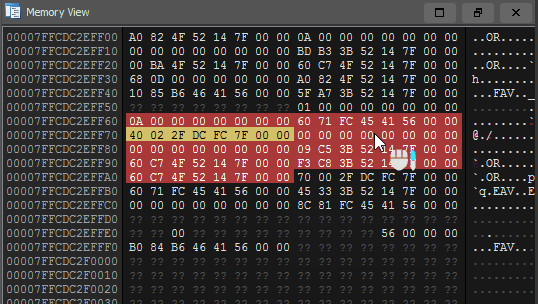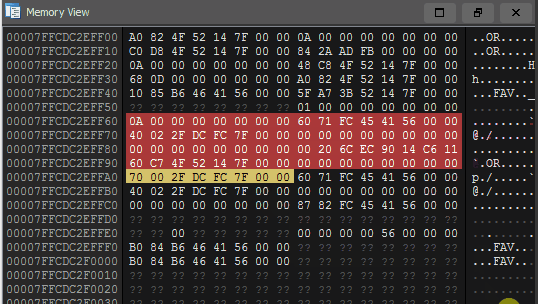 gaasedelen/tenet
A Trace Explorer for Reverse Engineers
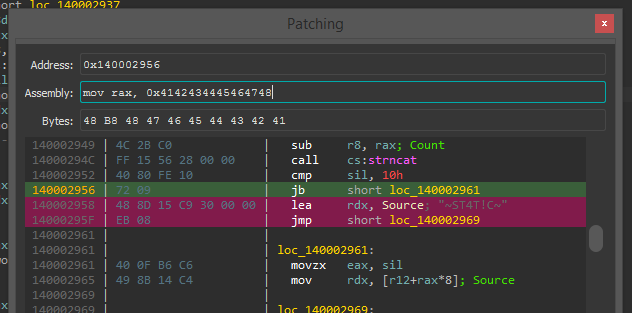 gaasedelen/patching
An Interactive Binary Patching Plugin for IDA Pro
 ant4g0nist/lisa.py
LLDB MCP Integration + other helpful commands
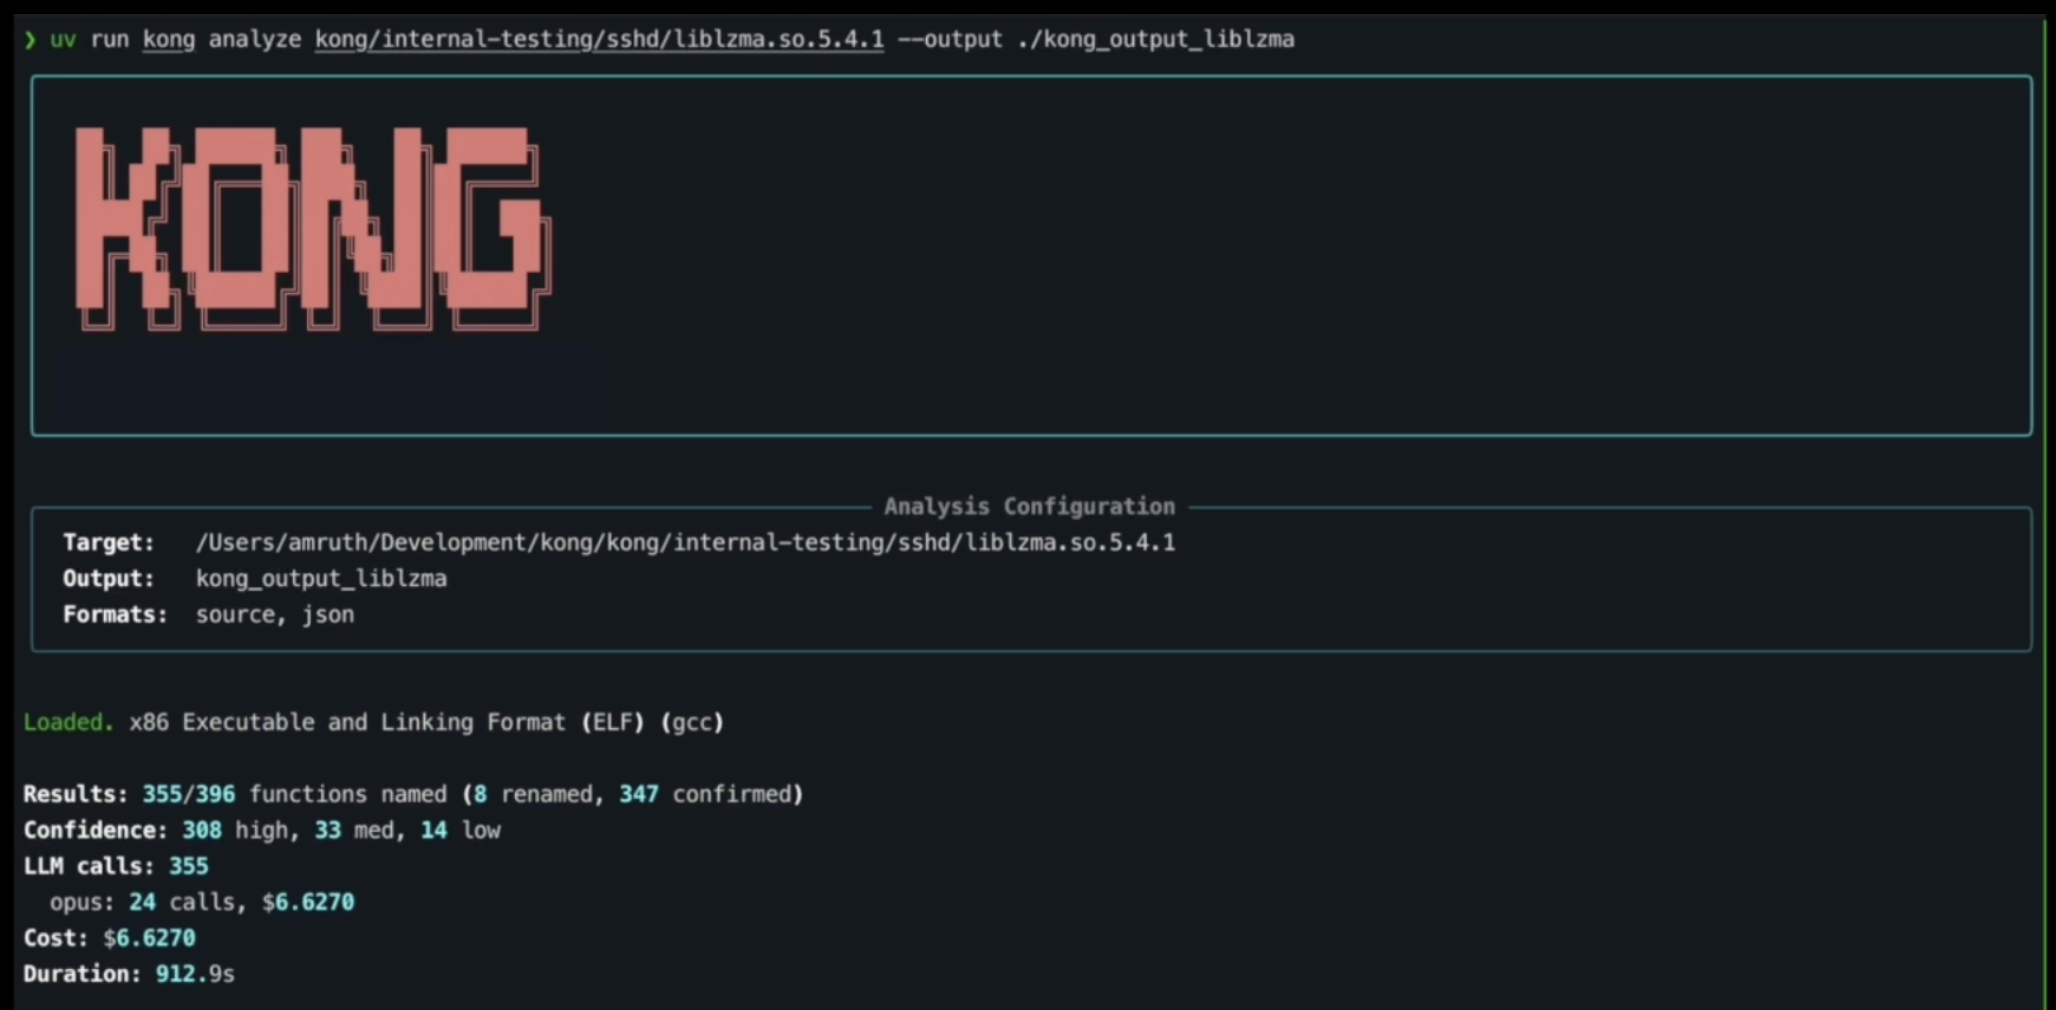 amruth-sn/kong
The world's first agentic reverse engineer.
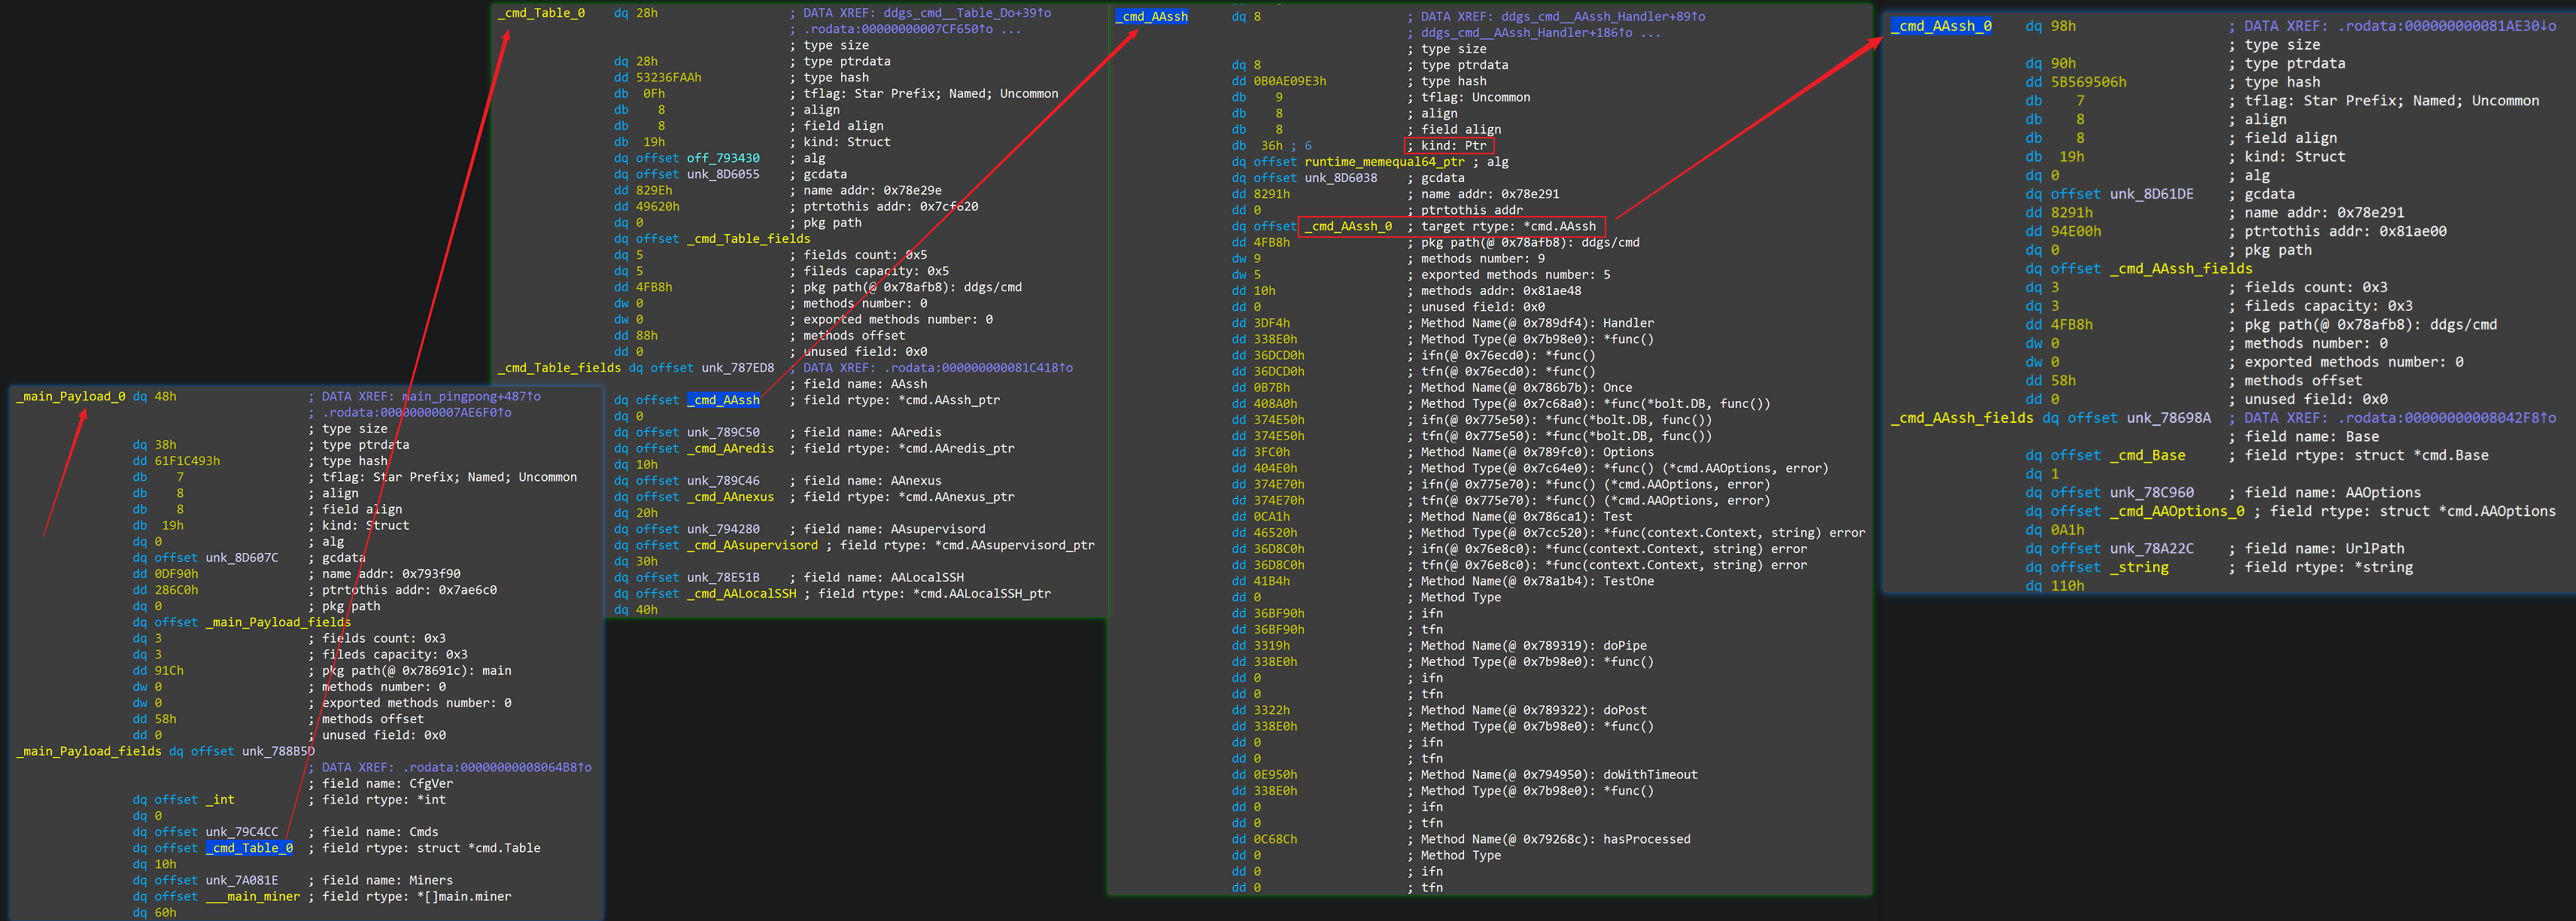 0xjiayu/go_parser
Yet Another Golang binary parser for IDAPro
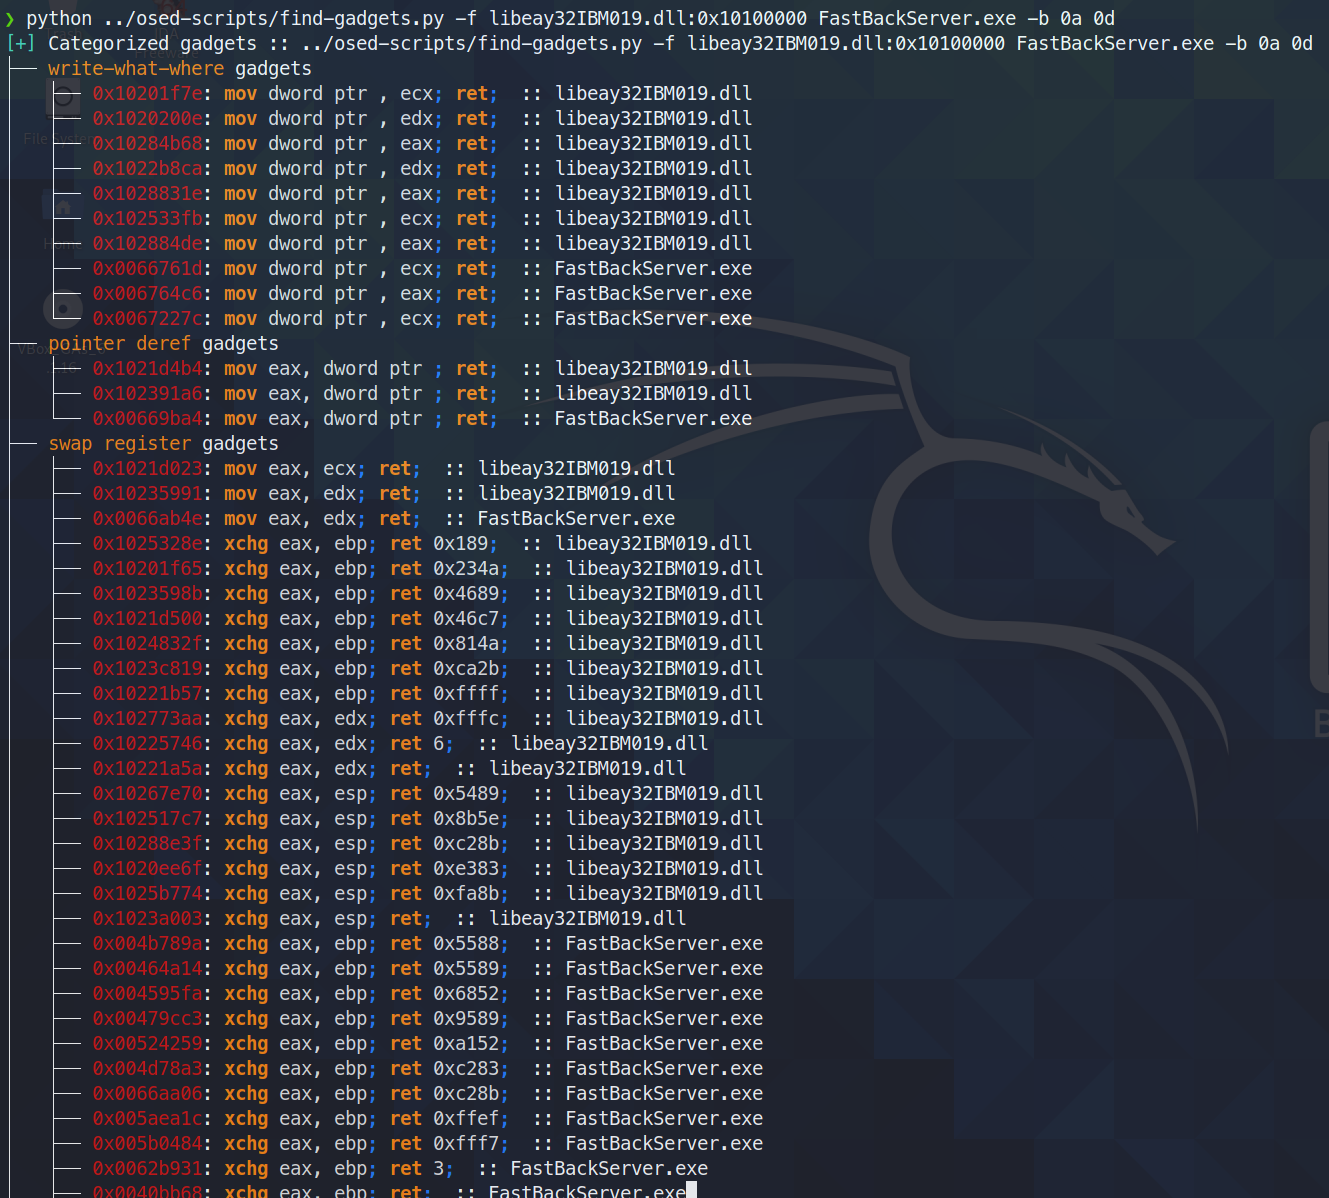 epi052/osed-scripts
bespoke tooling for offensive security's Windows Usermode Exploit Dev course (OSED)
 mandiant/flare-emu
Scriptable binary emulation framework integrating IDA Pro/Radare2 with Unicorn engine for automated malware analysis, string decryption, and code…
 isecpartners/introspy-ios
Security profiling for blackbox iOS
 robertcprice/ncpu
Research runtime for differentiable neural computers, GPU-based CPU emulation, and program synthesis. Features neural ALU, constant-time crypto, JEPA…
 hasherezade/mal_unpack
Dynamic unpacker based on PE-sieve

 mrphrazer/binary-ninja-headless-mcp
Headless Binary Ninja MCP server — giving AI agents deep reverse-engineering capabilities via 180 tools.