

aes-finder
 mmozeiko/aes-finder
Utility to find AES keys in running processes
binary-analysiscryptographyencryption-decryption-tools+2
mmozeiko/aes-finderUtility to find AES keys in running processes
 oalabs/hashdb
Assortment of hashing algorithms used in malware
 symgraph/ghidrassist
An LLM extension for Ghidra to enable AI assistance in RE.
 icyguider/nimcrypt2
.NET, PE, & Raw Shellcode Packer/Loader Written in Nim
 xtiankisutsa/mara_framework
MARA is a Mobile Application Reverse engineering and Analysis Framework. It is a toolkit that puts together commonly used mobile application reverse…
 xoreaxeaxeax/repsych
Psychological warfare in reverse engineering
 openrce/paimei
A reverse engineering framework written in Python.
 nickcano/xenoscan
Open source memory scanner written in C++
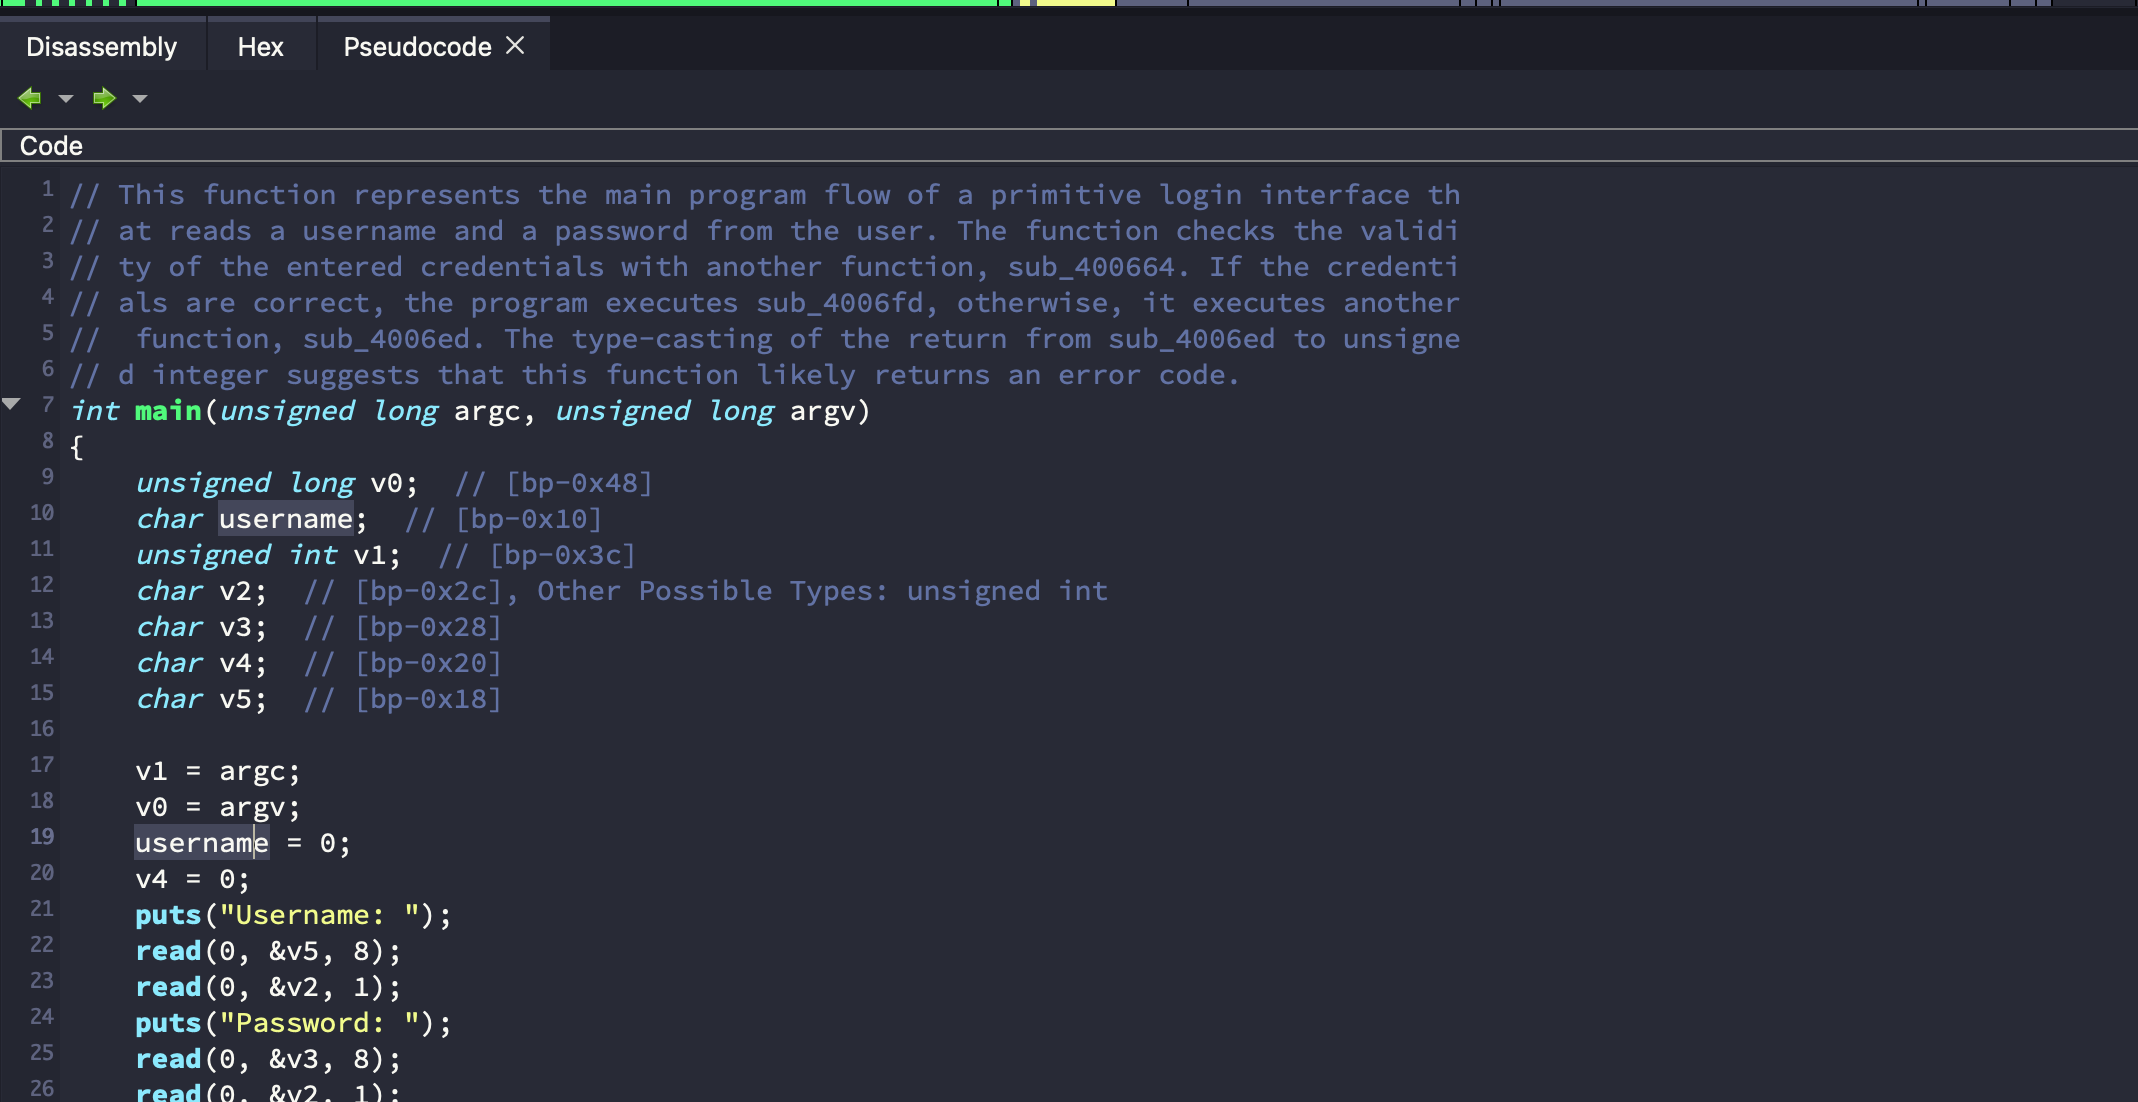 mahaloz/daila
A decompiler-agnostic plugin for interacting with AI in your decompiler. GPT-4, Claude, and local models supported!
 smackers/smack
Modular software verification toolchain that translates LLVM IR into Boogie intermediate verification language for bounded and experimental unbounded…
 checkpointsw/karta
IDA Python plugin for fast, location-driven matching of open-source library symbols in binaries, enabling efficient reverse engineering and…
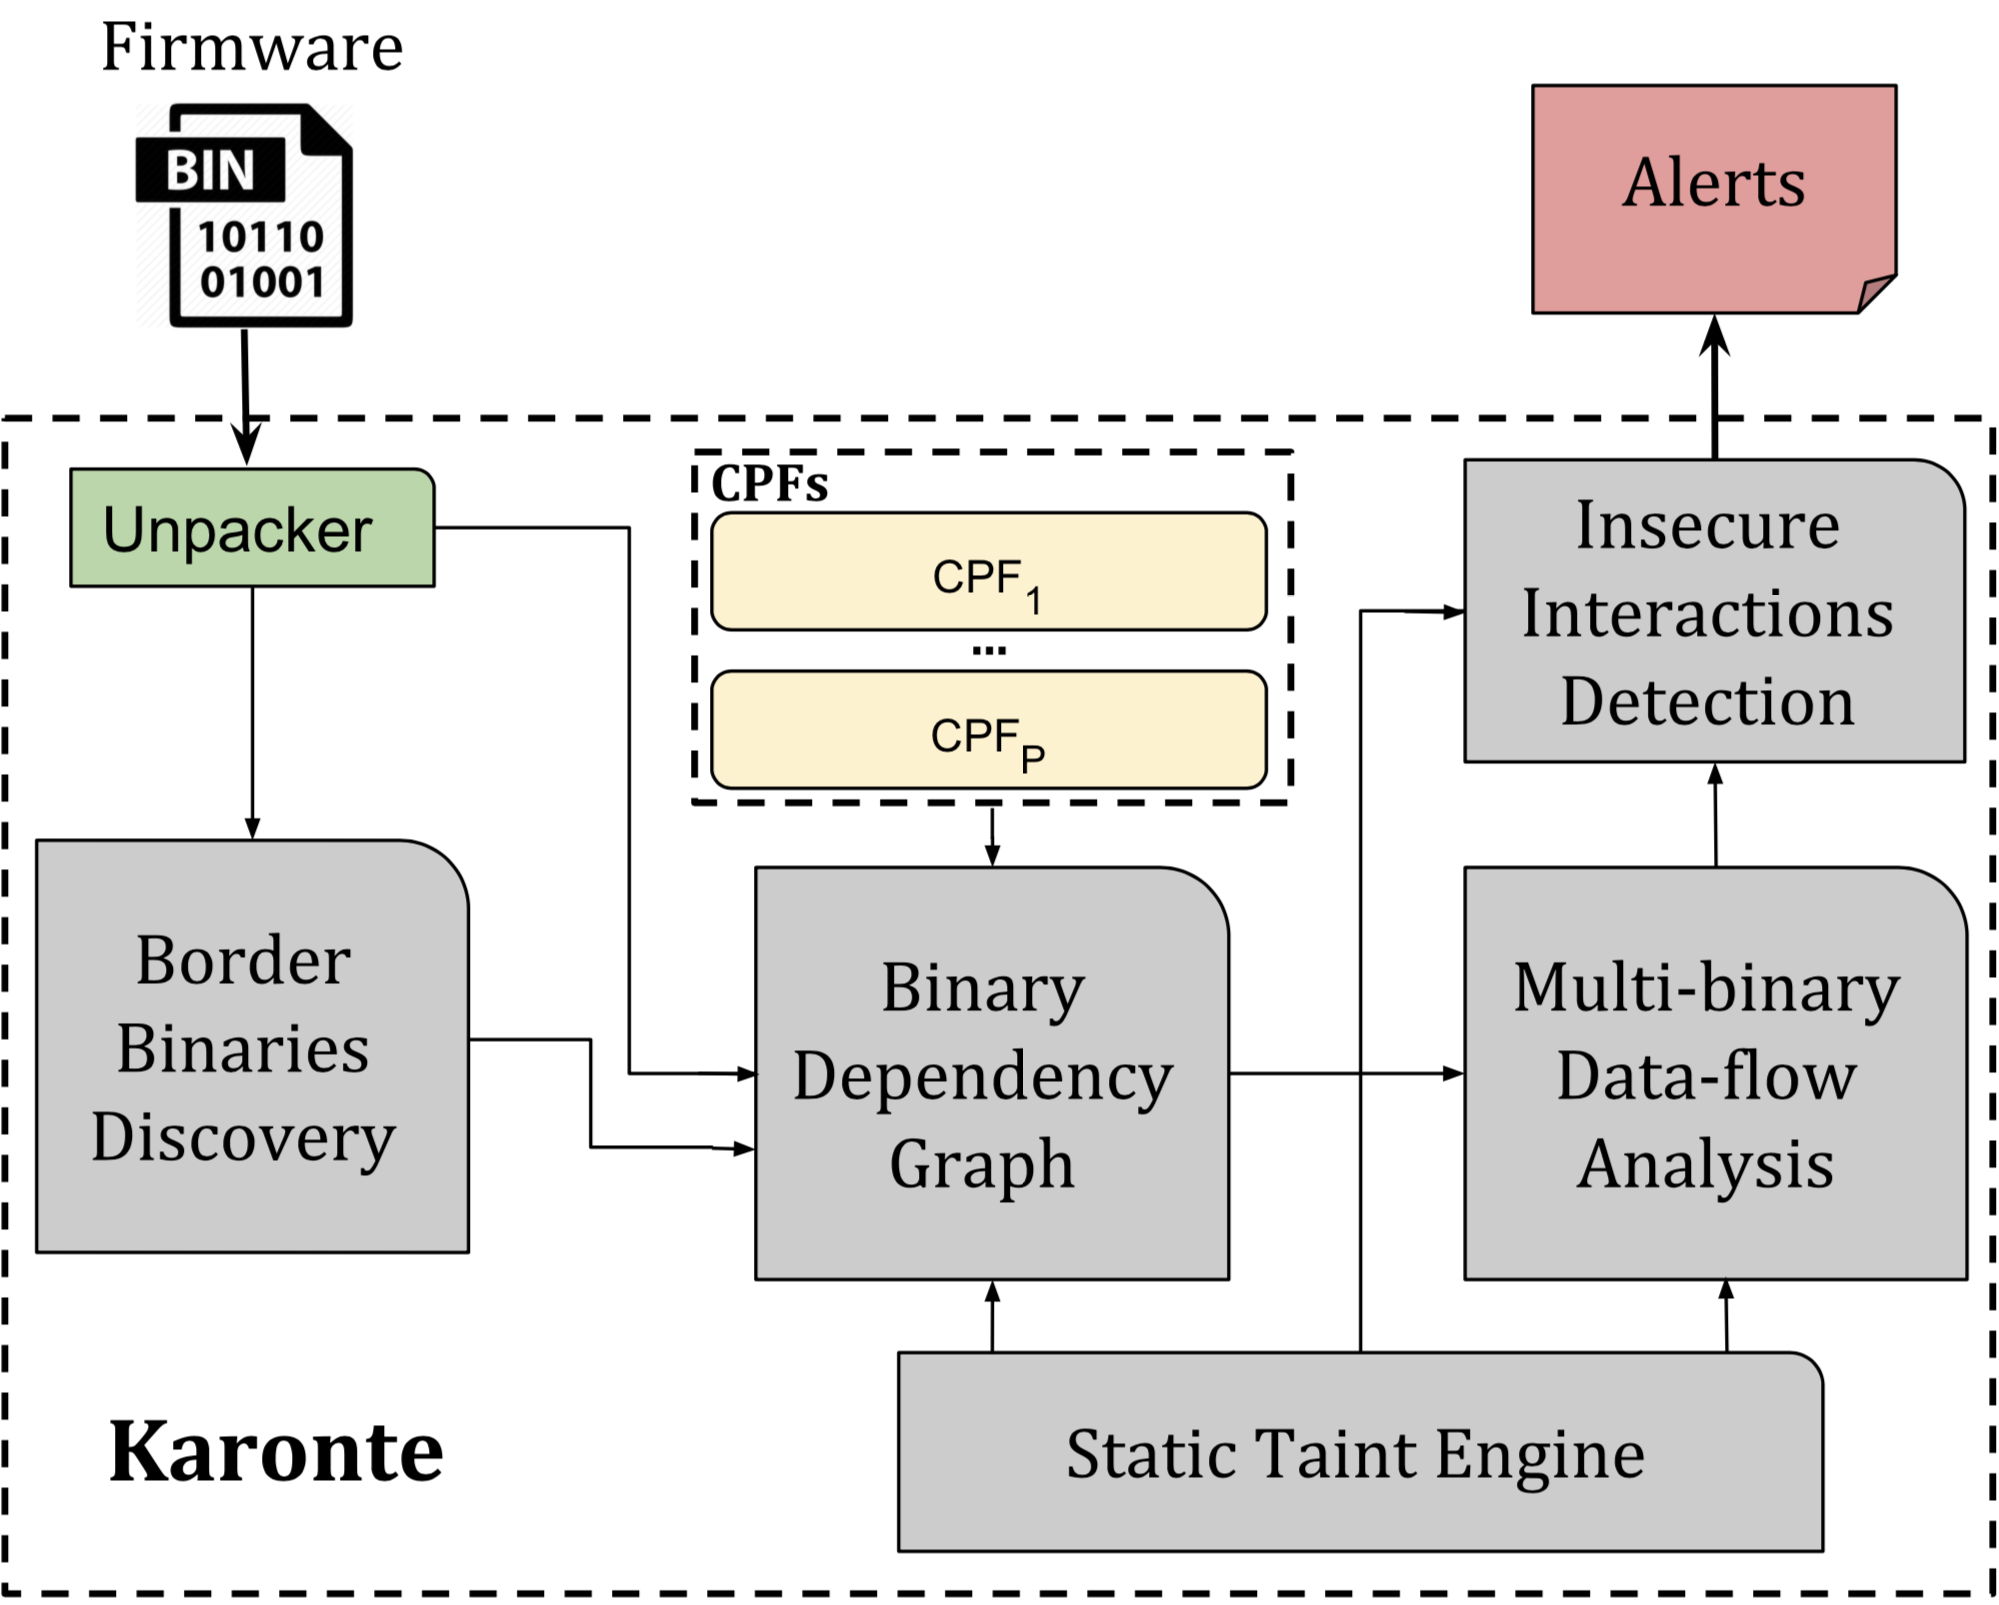 ucsb-seclab/karonte
Karonte is a static analysis tool to detect multi-binary vulnerabilities in embedded firmware
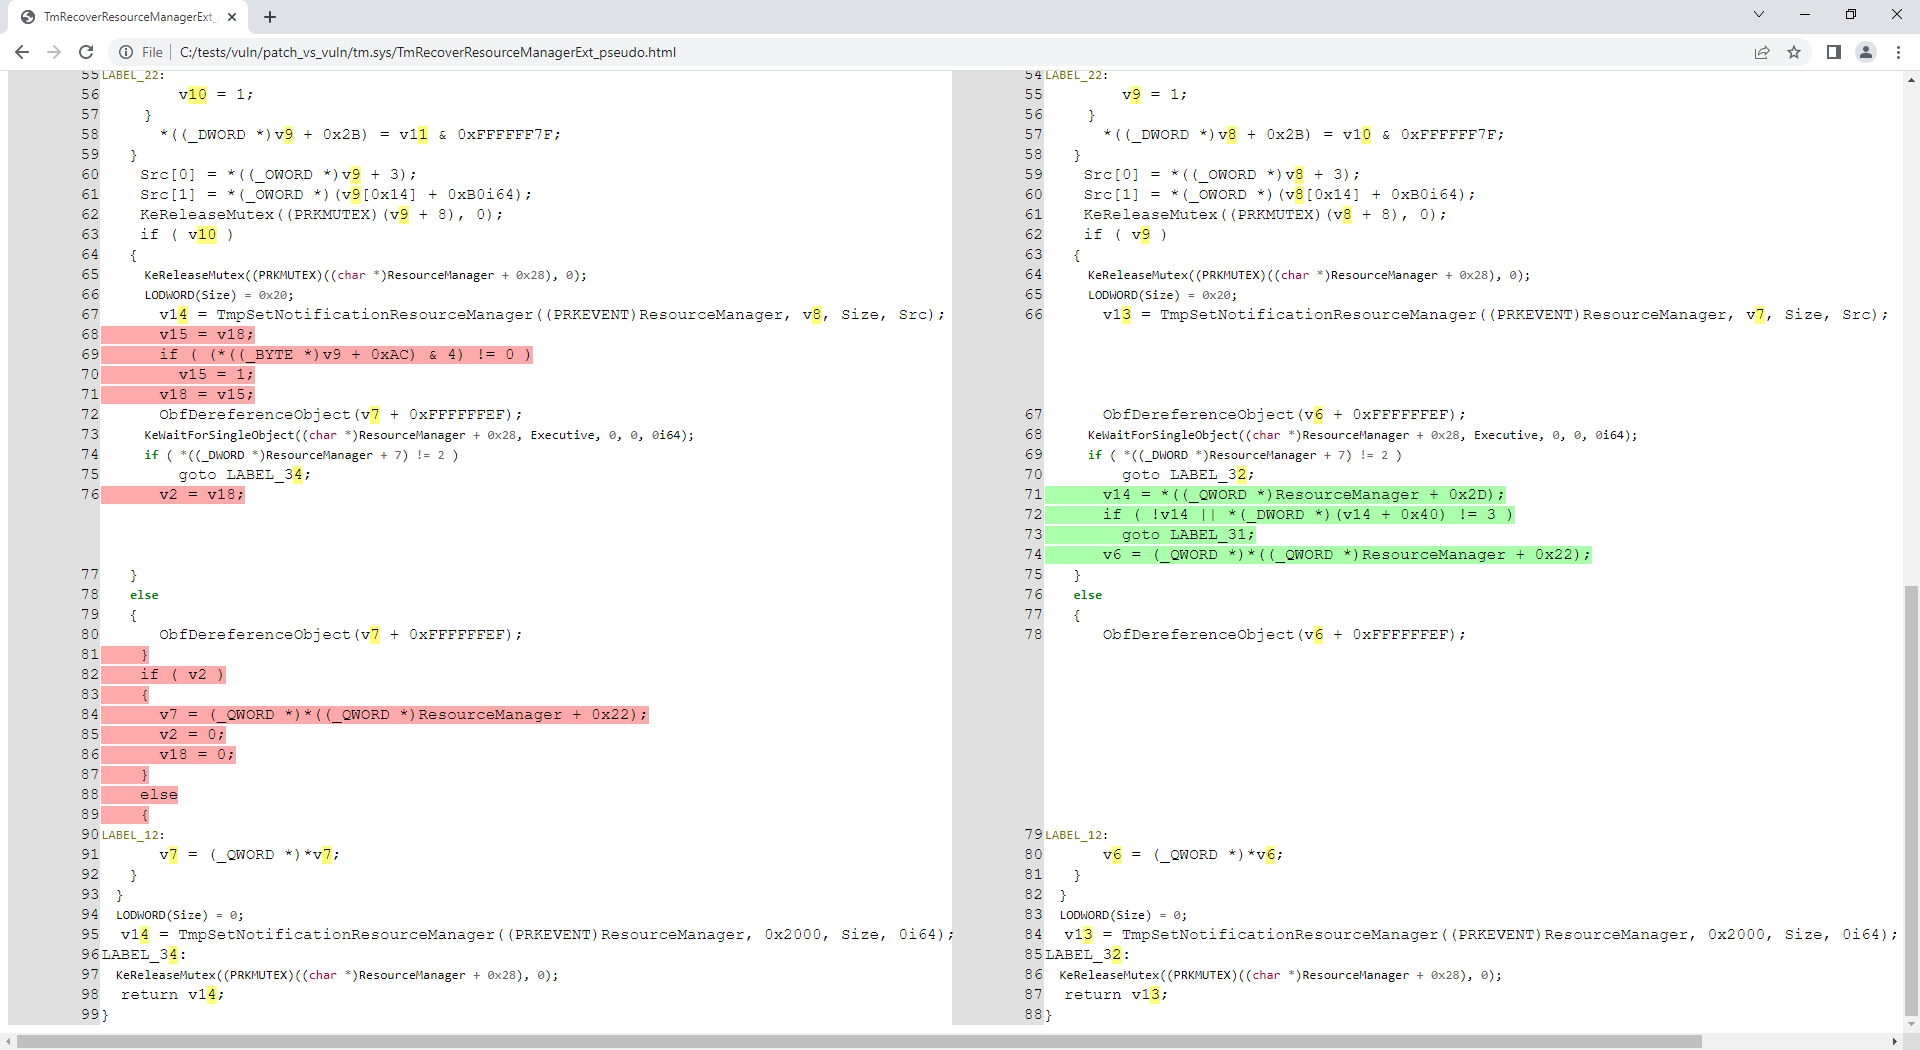 nccgroup/idahunt
idahunt is a framework to analyze binaries with IDA Pro and hunt for things in IDA Pro
 pandaadir05/ghost
Detects process injection and memory manipulation used by malware. Finds RWX regions, shellcode patterns, API hooks, thread hijacking, and process…
 skylined/bugid
Detect, analyze and uniquely identify crashes in Windows applications
 drago-96/cve-2022-0778
Proof-of-concept exploit for CVE-2022-0778, demonstrating an infinite loop in OpenSSL's BN_mod_sqrt via a crafted X.509 certificate with non-prime…
 czs108/windows-pe-packer
🗜️ A packer for Windows x86 executable files written in C and Intel x86 Assembly. The new file after packing can obstruct reverse…
 jjyg/metasm
This is the main repository for metasm, a free assembler / disassembler / compiler written in ruby