
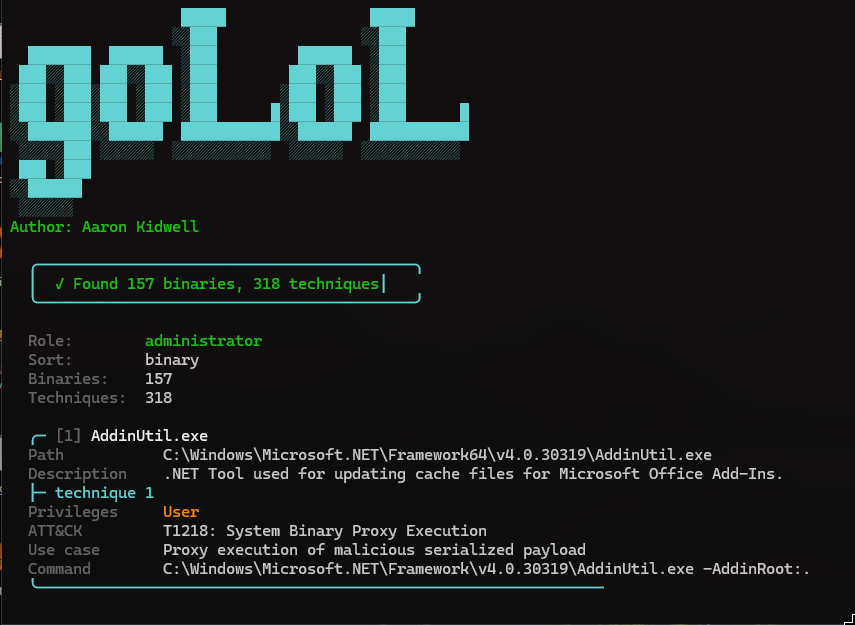
goLoL
 aaron-kidwell/golol
goLoL is a Windows host scanner with dual support for LOLBAS binaries and LOLDrivers. It lists LOLBAS techniques runnable at your current privilege…
binary-analysiseducationinformation-gathering+6
70
aaron-kidwell/gololgoLoL is a Windows host scanner with dual support for LOLBAS binaries and LOLDrivers. It lists LOLBAS techniques runnable at your current privilege…
 paul-tew/lifer
Windows link file (shortcuts) examiner
 kartoffelpflanze/odis-project-explorer
Python dumper/explorer for MCD Runtime Projects used by ODIS
 maldiohead/cve-2019-8540
Kernel Stack info leak at exportObjectToClient function
 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
 atlas0fd00m/vivisection
Analysis Plugin and Tools for Vivisect
 kaandemir993/purerat-msbuild.exe--c2-extraction--net-evasion-analysis
Reverse engineering analysis of PureRAT RAT abusing msbuild.exe, extracting C2 infrastructure, .NET evasion APIs, file system manipulation, and…
 waleedassar/cve-2021-1656
Proof-of-concept exploit for CVE-2021-1656, an information disclosure vulnerability in the Windows TPM driver (tpm.sys). Demonstrates kernel memory…
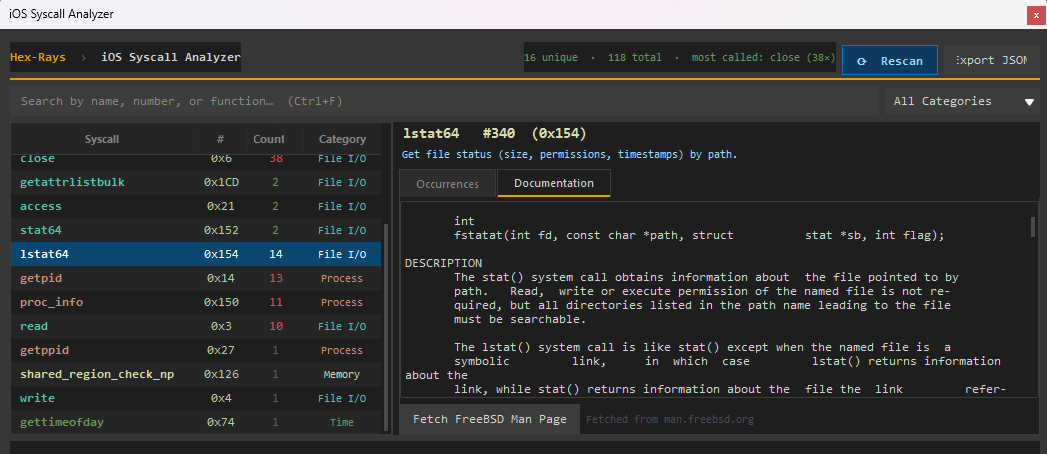 stolevchristian/sylvia
iOS Syscall Explorer for IDA 9.X
 jatinkapilaq1/intel-me-research
Talk to your Intel Management Engine directly — zero-dependency Python tool. Finds memory leaks, partition manifest, live MKHI probing. First public…
 talha-nazeef-ahmed/rpc-triage
A zero-symbol static analysis engine that extracts and mathematically ranks the Windows RPC attack surface using an AHP-based risk model.
 kaandemir993/salat-stealer-telegram-proxy-decoy-c2-analysis
"Reverse engineering analysis of Salat Stealer, a Go-based info-stealer that uses a Telegram proxy decoy, C2 communication, and encrypted memory…
 waleedassar/cve-2021-1699
POC for CVE-2021-1699
 waleedassar/cve-2022-24483
POC For CVE-2022-24483
 absholi7ly/freerdp-out-of-bounds-read-cve-2024-32459-
The FreeRDP - Out-of-Bounds Read (CVE-2024-32459) vulnerability concerns FreeRDP, a free implementation of Remote Desktop Protocol. FreeRDP-based…
 farazsth98/freebsd-dirent-info-leak-bugs
CVE-2020-25578 and CVE-2020-25579: Some FreeBSD info leak bugs I found in 2020.
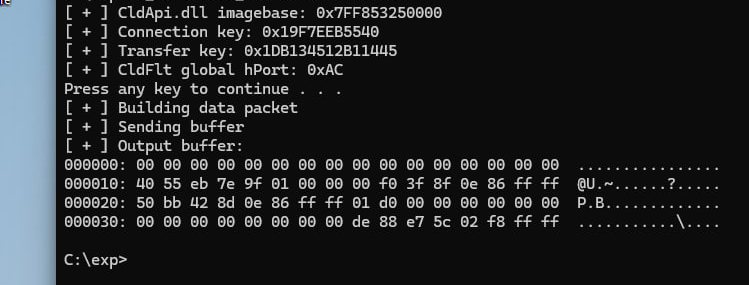 crackercat/cve-2024-26160
cldflt.sys information disclosure vulnerability (KB5034765 - KB5035853, Win 11).
 gavmor/x86-cpp-reversing-skill
Claude Code skill for reverse-engineering 32-bit little-endian x86 C++ binaries (vtables, RTTI, inheritance recovery)