
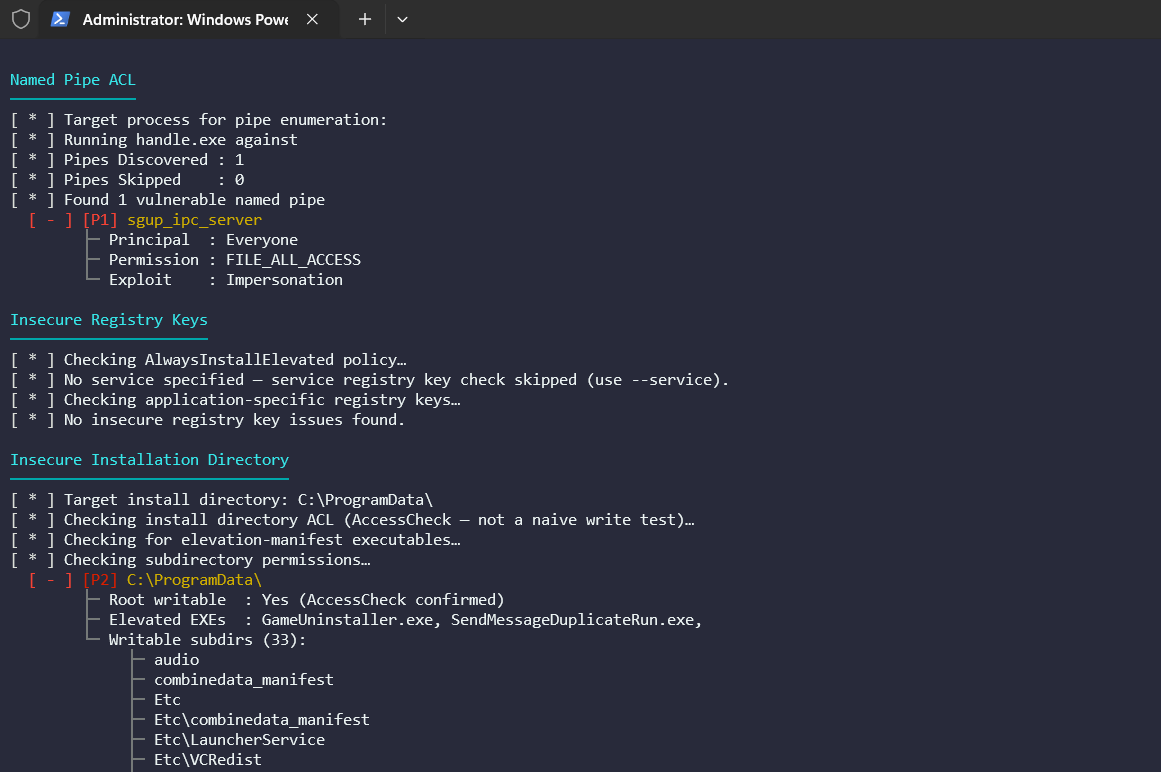
Anvil
 shellkraft/anvil
Anvil is a runtime-first attack surface assessment tool for Windows thick client applications, built for penetration testers and security researchers…
binary-analysisexploitationpenetration-testing+5
38
shellkraft/anvilAnvil is a runtime-first attack surface assessment tool for Windows thick client applications, built for penetration testers and security researchers…
 waleedassar/cve-2021-1656
Proof-of-concept exploit for CVE-2021-1656, an information disclosure vulnerability in the Windows TPM driver (tpm.sys). Demonstrates kernel memory…
 talha-nazeef-ahmed/rpc-triage
A zero-symbol static analysis engine that extracts and mathematically ranks the Windows RPC attack surface using an AHP-based risk model.
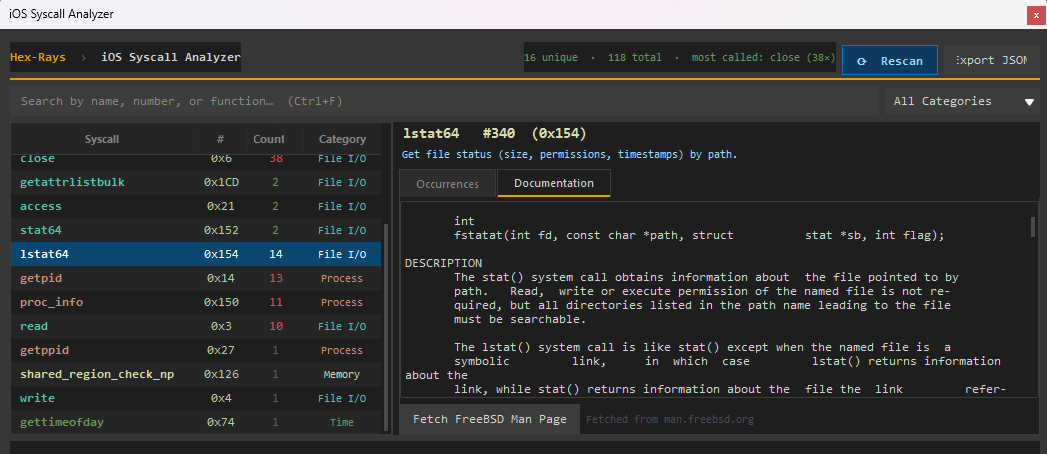 stolevchristian/sylvia
iOS Syscall Explorer for IDA 9.X
 jatinkapilaq1/intel-me-research
Talk to your Intel Management Engine directly — zero-dependency Python tool. Finds memory leaks, partition manifest, live MKHI probing. First public…
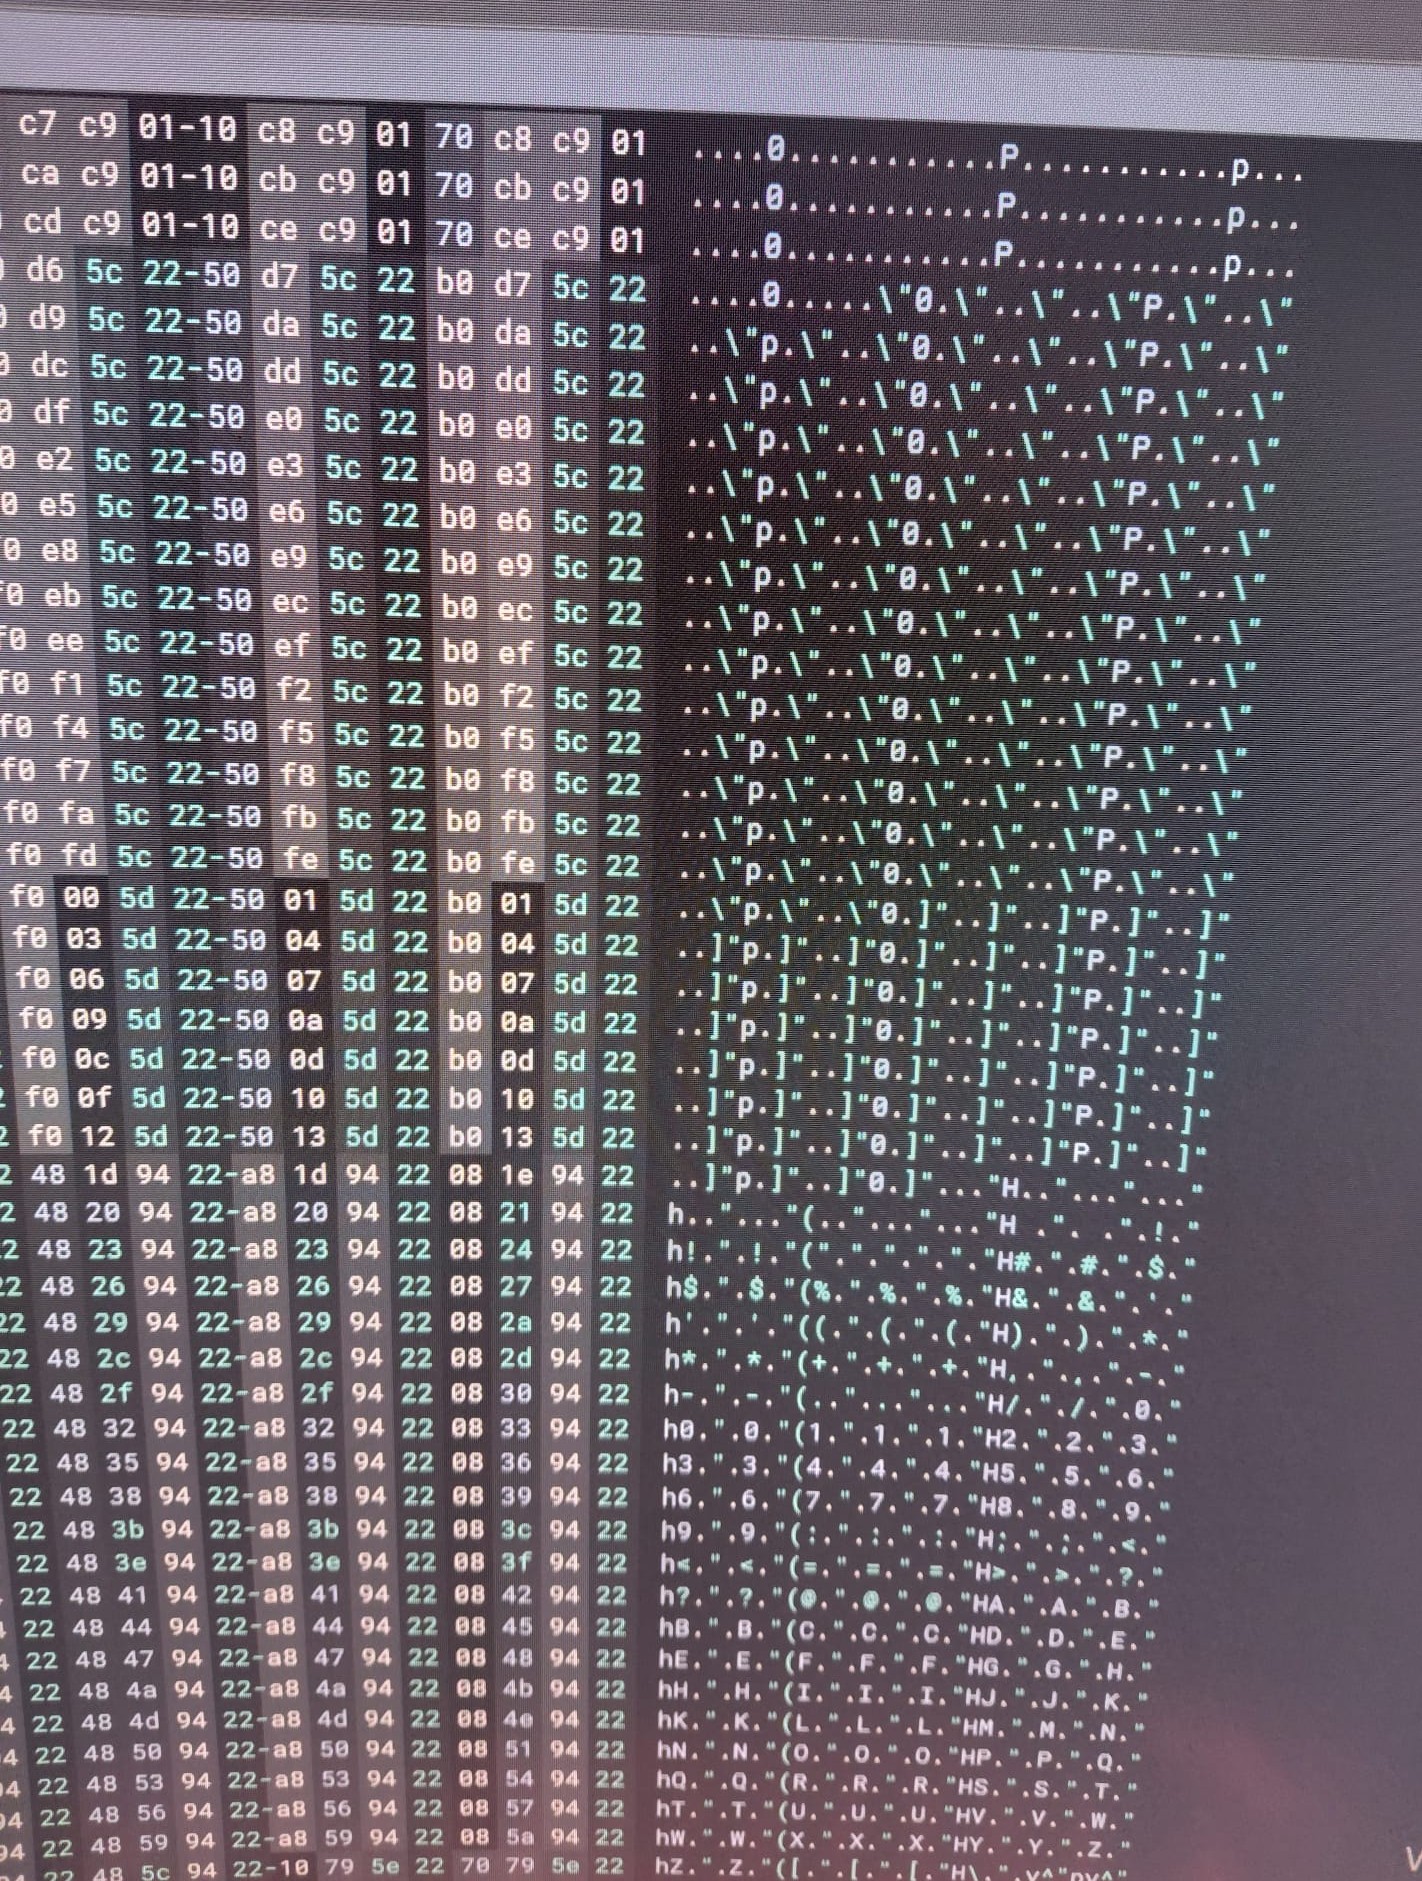 kaandemir993/salat-stealer-telegram-proxy-decoy-c2-analysis
"Reverse engineering analysis of Salat Stealer, a Go-based info-stealer that uses a Telegram proxy decoy, C2 communication, and encrypted memory…
 waleedassar/cve-2021-1699
POC for CVE-2021-1699
 waleedassar/cve-2022-24483
POC For CVE-2022-24483
 absholi7ly/freerdp-out-of-bounds-read-cve-2024-32459-
The FreeRDP - Out-of-Bounds Read (CVE-2024-32459) vulnerability concerns FreeRDP, a free implementation of Remote Desktop Protocol. FreeRDP-based…
 farazsth98/freebsd-dirent-info-leak-bugs
CVE-2020-25578 and CVE-2020-25579: Some FreeBSD info leak bugs I found in 2020.
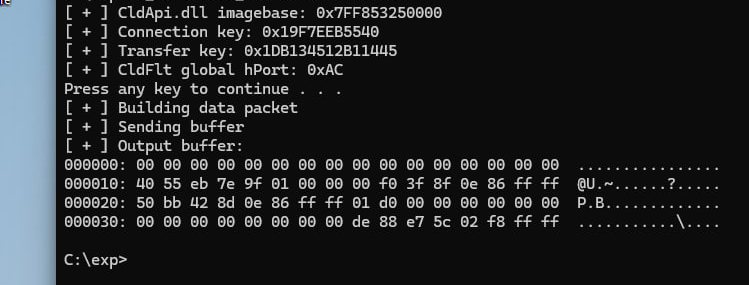 crackercat/cve-2024-26160
cldflt.sys information disclosure vulnerability (KB5034765 - KB5035853, Win 11).
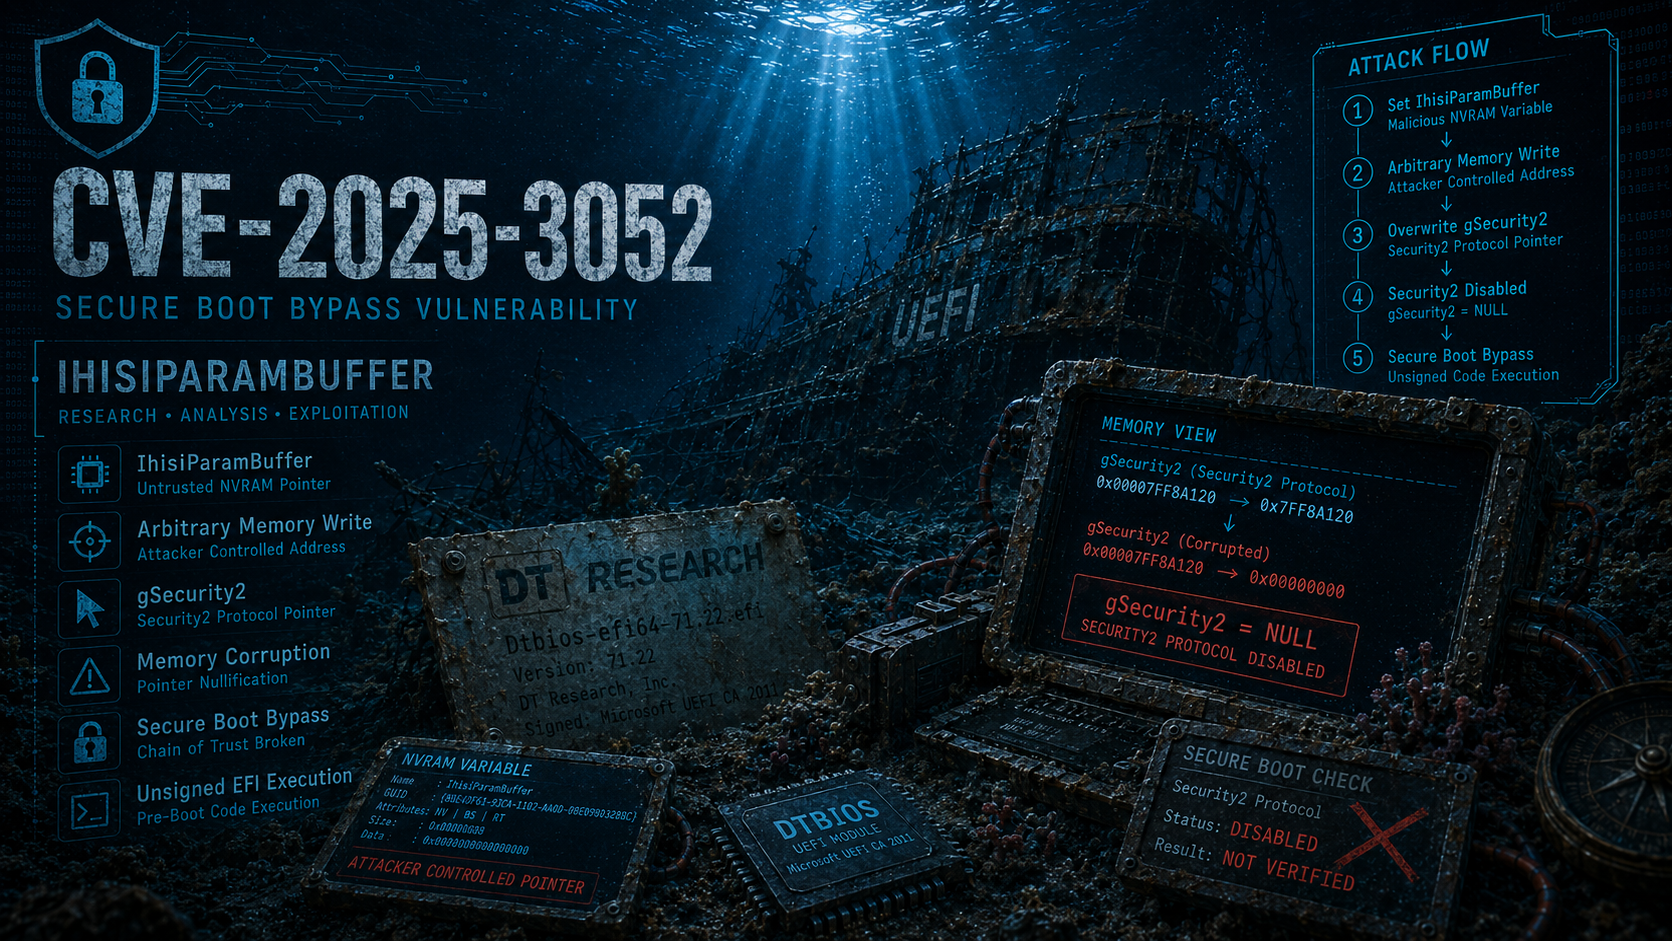 themalwareguardian/cve-2025-3052
Research on CVE-2025-3052, an Insyde firmware vulnerability that exposes an arbitrary write primitive capable of modifying security-critical pointers.
 kikiuuw/cve-2025-68921
Analyze and demonstrate the local privilege escalation vulnerability (CVE-2025-68921) in Nahimic audio software on gaming laptops, with automated…
 somisomair/cve-2026-20698-pf_route-heap-overflow
CVE-2026-20698: XNU kernel heap overflow via PF_ROUTE RTA_GENMASK. PoC and analysis. Independently discovered.
 jnschaeffer/cve-2022-44268-detector
Detect images that likely exploit CVE-2022-44268
 gtgalaxi/electronvulnerableversion
Find Electron Apps Vulnerable to CVE-2023-4863 / CVE-2023-5129
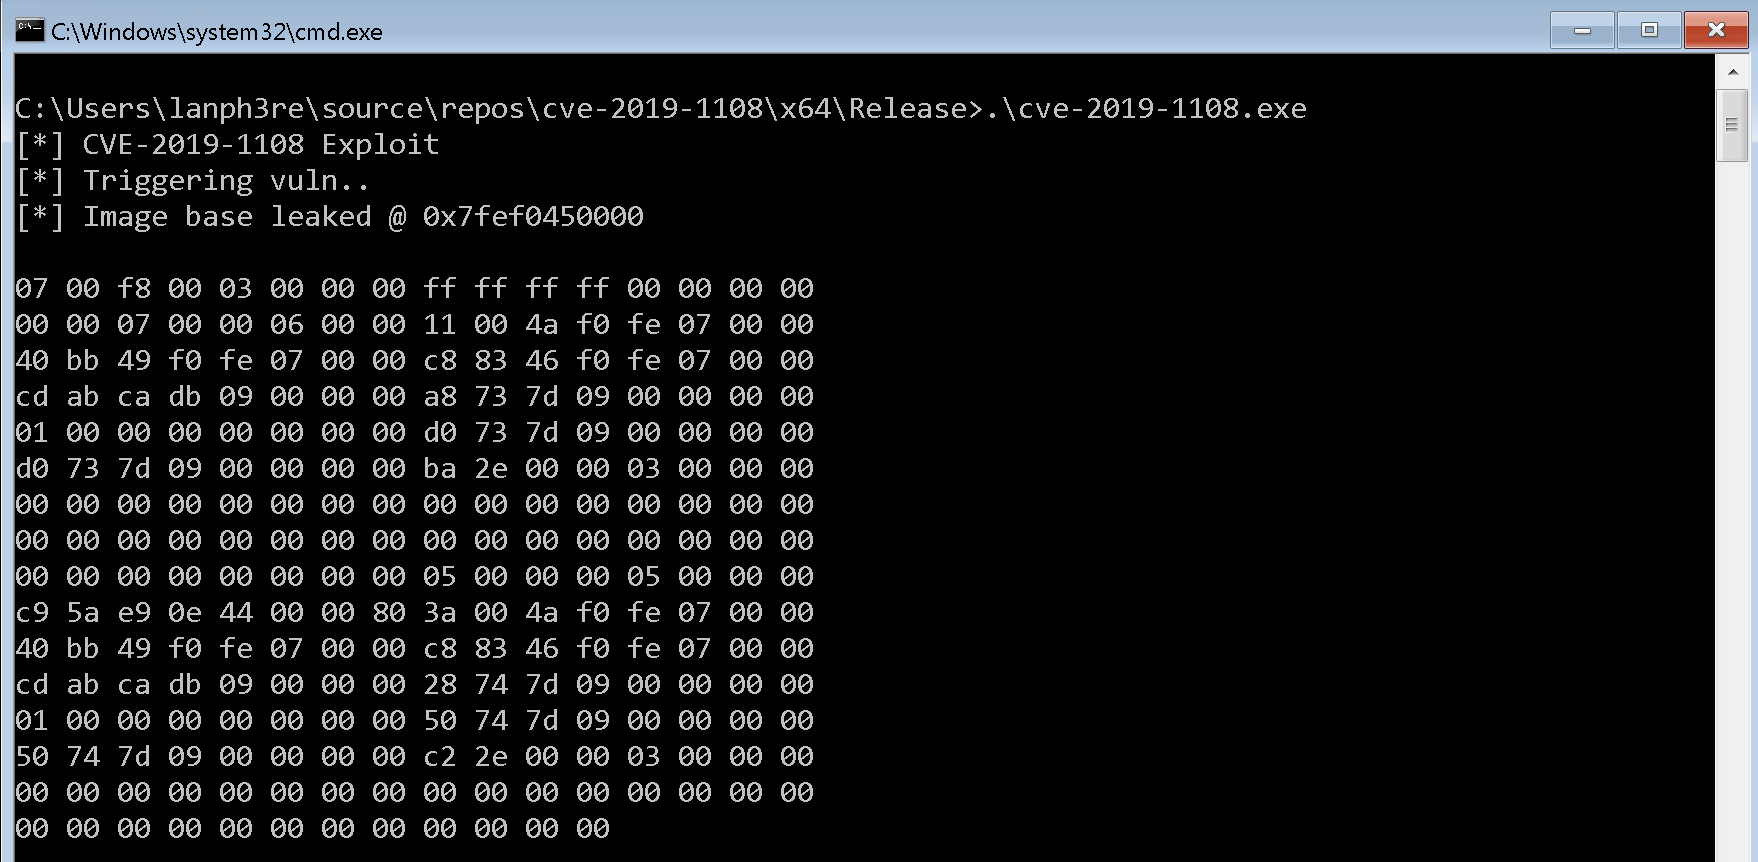 lanph3re/cve-2019-1108
Proof-of-concept exploit for CVE-2019-1108, an RDP client information disclosure vulnerability that leaks memory contents via specially crafted…
 australeo/cve-2021-28476
Proof-of-concept for CVE-2021-28476, a Hyper-V vmswitch.sys arbitrary pointer dereference allowing guest-to-host denial-of-service and potential RCE.