
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
84 results
gdbgui preview

gdbgui

GitHubcs01/gdbgui

Browser-based frontend to gdb (gnu debugger). Add breakpoints, view the stack, visualize data structures, and more in C, C++, Go, Rust, and Fortran.…

binary-analysisdebuggersreverse-engineering+1
10.3k
1 year ago
Vidar-Stealer-Chrome-Injection-Malicious-JS-Targeting-Google-Reddit-Sessions-Analysis preview

Vidar-Stealer-Chrome-Injection-Malicious-JS-Targeting-Google-Reddit-Sessions-Analysis

GitHubkaandemir993/vidar-stealer-chrome-injection-malicious-js-targeting-google-reddit-sessions-analysis

Reverse engineering Vidar Stealer: From obfuscated memory strings to Chrome process injection, malicious JS execution, and active session hijacking…
binary-analysisdigital-forensicsdynamic-analysis-sandboxing+6
511 days ago
Linksys-WRT54GL-Exploitation preview

Linksys-WRT54GL-Exploitation

GitHubumbertodellamonica/linksys-wrt54gl-exploitation

From Solder to Shell: Full Hardware Exploitation of the Linksys WRT54GL Router (CVE-2022-43973)

binary-analysisdebuggerseducation+9
25 months ago
AFLplusplus preview

AFLplusplus

GitHubaflplusplus/aflplusplus

AFL++ is a state-of-the-art fuzzer, and #1 in benchmarks. It was originally based on AFL. Today it comes with qemu 5.1, collision-free coverage,…
binary-analysisdns-fuzzingdynamic-analysis-sandboxing+3
6.7k16 days ago
retdec preview

retdec

GitHubavast/retdec

RetDec is a retargetable machine-code decompiler based on LLVM.

binary-analysismalware-analysisreverse-engineering+1
8.6k5 months ago
mal_unpack preview

mal_unpack

GitHubhasherezade/mal_unpack

Dynamic unpacker based on PE-sieve
binary-analysisdynamic-analysis-sandboxingmalware-analysis+2
8276 months ago
Dna preview

Dna

GitHubcolton1skees/dna

LLVM based static binary analysis framework
binary-analysiscode-analysisdebuggers+5
3656 months ago
Ares preview

Ares

GitHubcerbersec/ares

Project Ares is a Proof of Concept (PoC) loader written in C/C++ based on the Transacted Hollowing technique
binary-analysisdefensive-toolsencryption-decryption-tools+7
3364 years ago
DrSemu preview

DrSemu

GitHubsecrary/drsemu

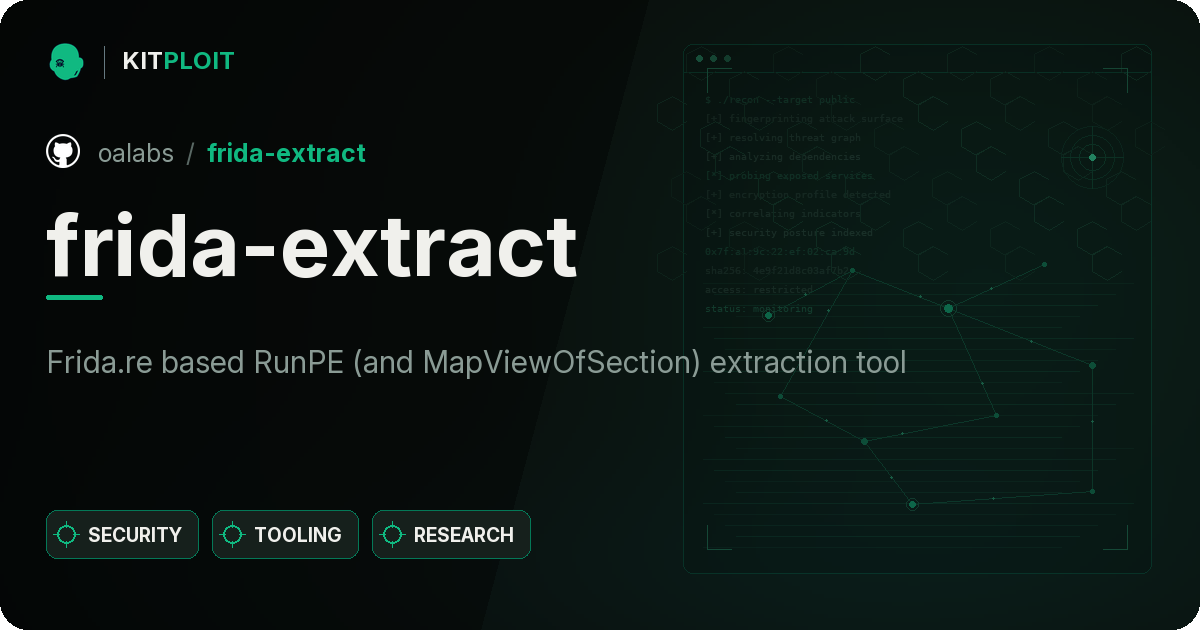
DrSemu - Sandboxed Malware Detection and Classification Tool Based on Dynamic Behavior
binary-analysisdynamic-analysis-sandboxingmalware-analysis+1
2797 years ago
frida-extract preview

frida-extract

GitHuboalabs/frida-extract

Frida.re based RunPE (and MapViewOfSection) extraction tool

binary-analysisdynamic-analysis-sandboxingeducation+3
1149 years ago
pylane preview

pylane

GitHubnteseyes/pylane

An python vm injector with debug tools, based on gdb.
binary-analysisdebuggersdynamic-analysis-sandboxing+1
3593 years ago
hyperpom preview

hyperpom

GitHubimpalabs/hyperpom

AArch64 fuzzer based on the Apple Silicon hypervisor
binary-analysisdynamic-analysis-sandboxingfuzzing+2
2022 years ago
doona preview

doona

GitHubwireghoul/doona

Network based protocol fuzzer

binary-analysisexploitationfuzzing+3
754 years ago
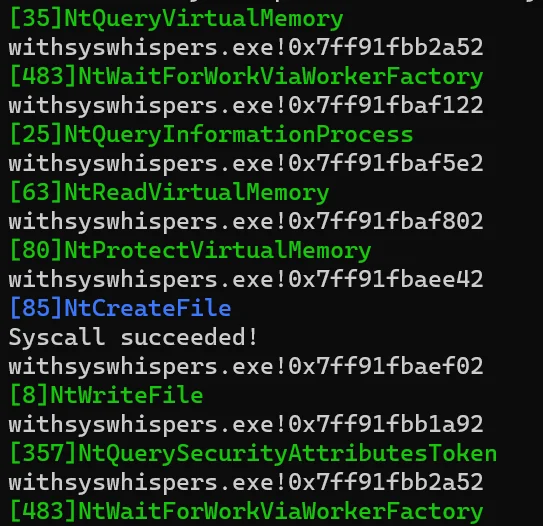
frida-stalker-NtStrace preview

frida-stalker-NtStrace

GitHubgmh5225/frida-stalker-ntstrace

frida-stalker based system call tracer on windows(x64).
binary-analysisdebuggersdynamic-analysis-sandboxing+4
33 years ago
NtStrace preview

NtStrace

GitHubgmh5225/ntstrace

frida-stalker based system call tracer on windows(x64).

binary-analysisdebuggersdynamic-analysis-sandboxing+2
12 years ago
cve-2020-0601-utils preview

cve-2020-0601-utils

GitHub0xxon/cve-2020-0601-utils

C++ based utility to check if certificates are trying to exploit CVE-2020-0601
binary-analysiscryptographyexploitation+1
6 years ago
flashmingo preview
Archived

flashmingo

GitHubmandiant/flashmingo

Automatic analysis of SWF files based on some heuristics. Extensible via plugins.
binary-analysisdynamic-analysis-sandboxingeducation+6
1207 years ago
pyrebox preview
Archived

pyrebox

GitHubcisco-talos/pyrebox

Python scriptable Reverse Engineering Sandbox, a Virtual Machine instrumentation and inspection framework based on QEMU

binary-analysisdebuggersdigital-forensics+5
1.7k2 years ago
Previous12345Next