windows-api-function-cheatsheets

A reference of Windows API function calls, including functions for file operations, process management, memory management, thread management,…

A reference of Windows API function calls, including functions for file operations, process management, memory management, thread management,…

Decrypts Intel Atom microcode updates and unpacks XuCode with recovered RC4 keys, revealing internal CPU microcode structures for hardware security…

☕ GDBFrontend is an easy, flexible and extensible gui debugger.

The repo contains a series of challenges for learning Frida for Android Exploitation.

Python parser for extracting CobaltStrike Beacon configurations from PE files, memory dumps, and C2 URLs using heuristic XOR decryption and…

Minimalistic VT-x hypervisor for Windows x64 providing syscall, MSR, IDT, and kernel inline hooks plus EPT-based page substitution and TLB splitting.

A byte code analyzer for finding deserialization gadget chains in Java applications

LoadLibrary for offensive operations

Windows privilege escalation discovery tool that parses Process Monitor boot logs to identify DLL hijacking, weak ACLs, and other elevation paths,…

Course materials for Advanced Binary Deobfuscation by NTT Secure Platform Laboratories

MCP server exposing a 4,100+ skill game-hacking and reverse-engineering knowledge base with source archives, specialized agents, subagents, plugins…

Utility to find AES keys in running processes

The new bridge between Burp Suite and Frida!

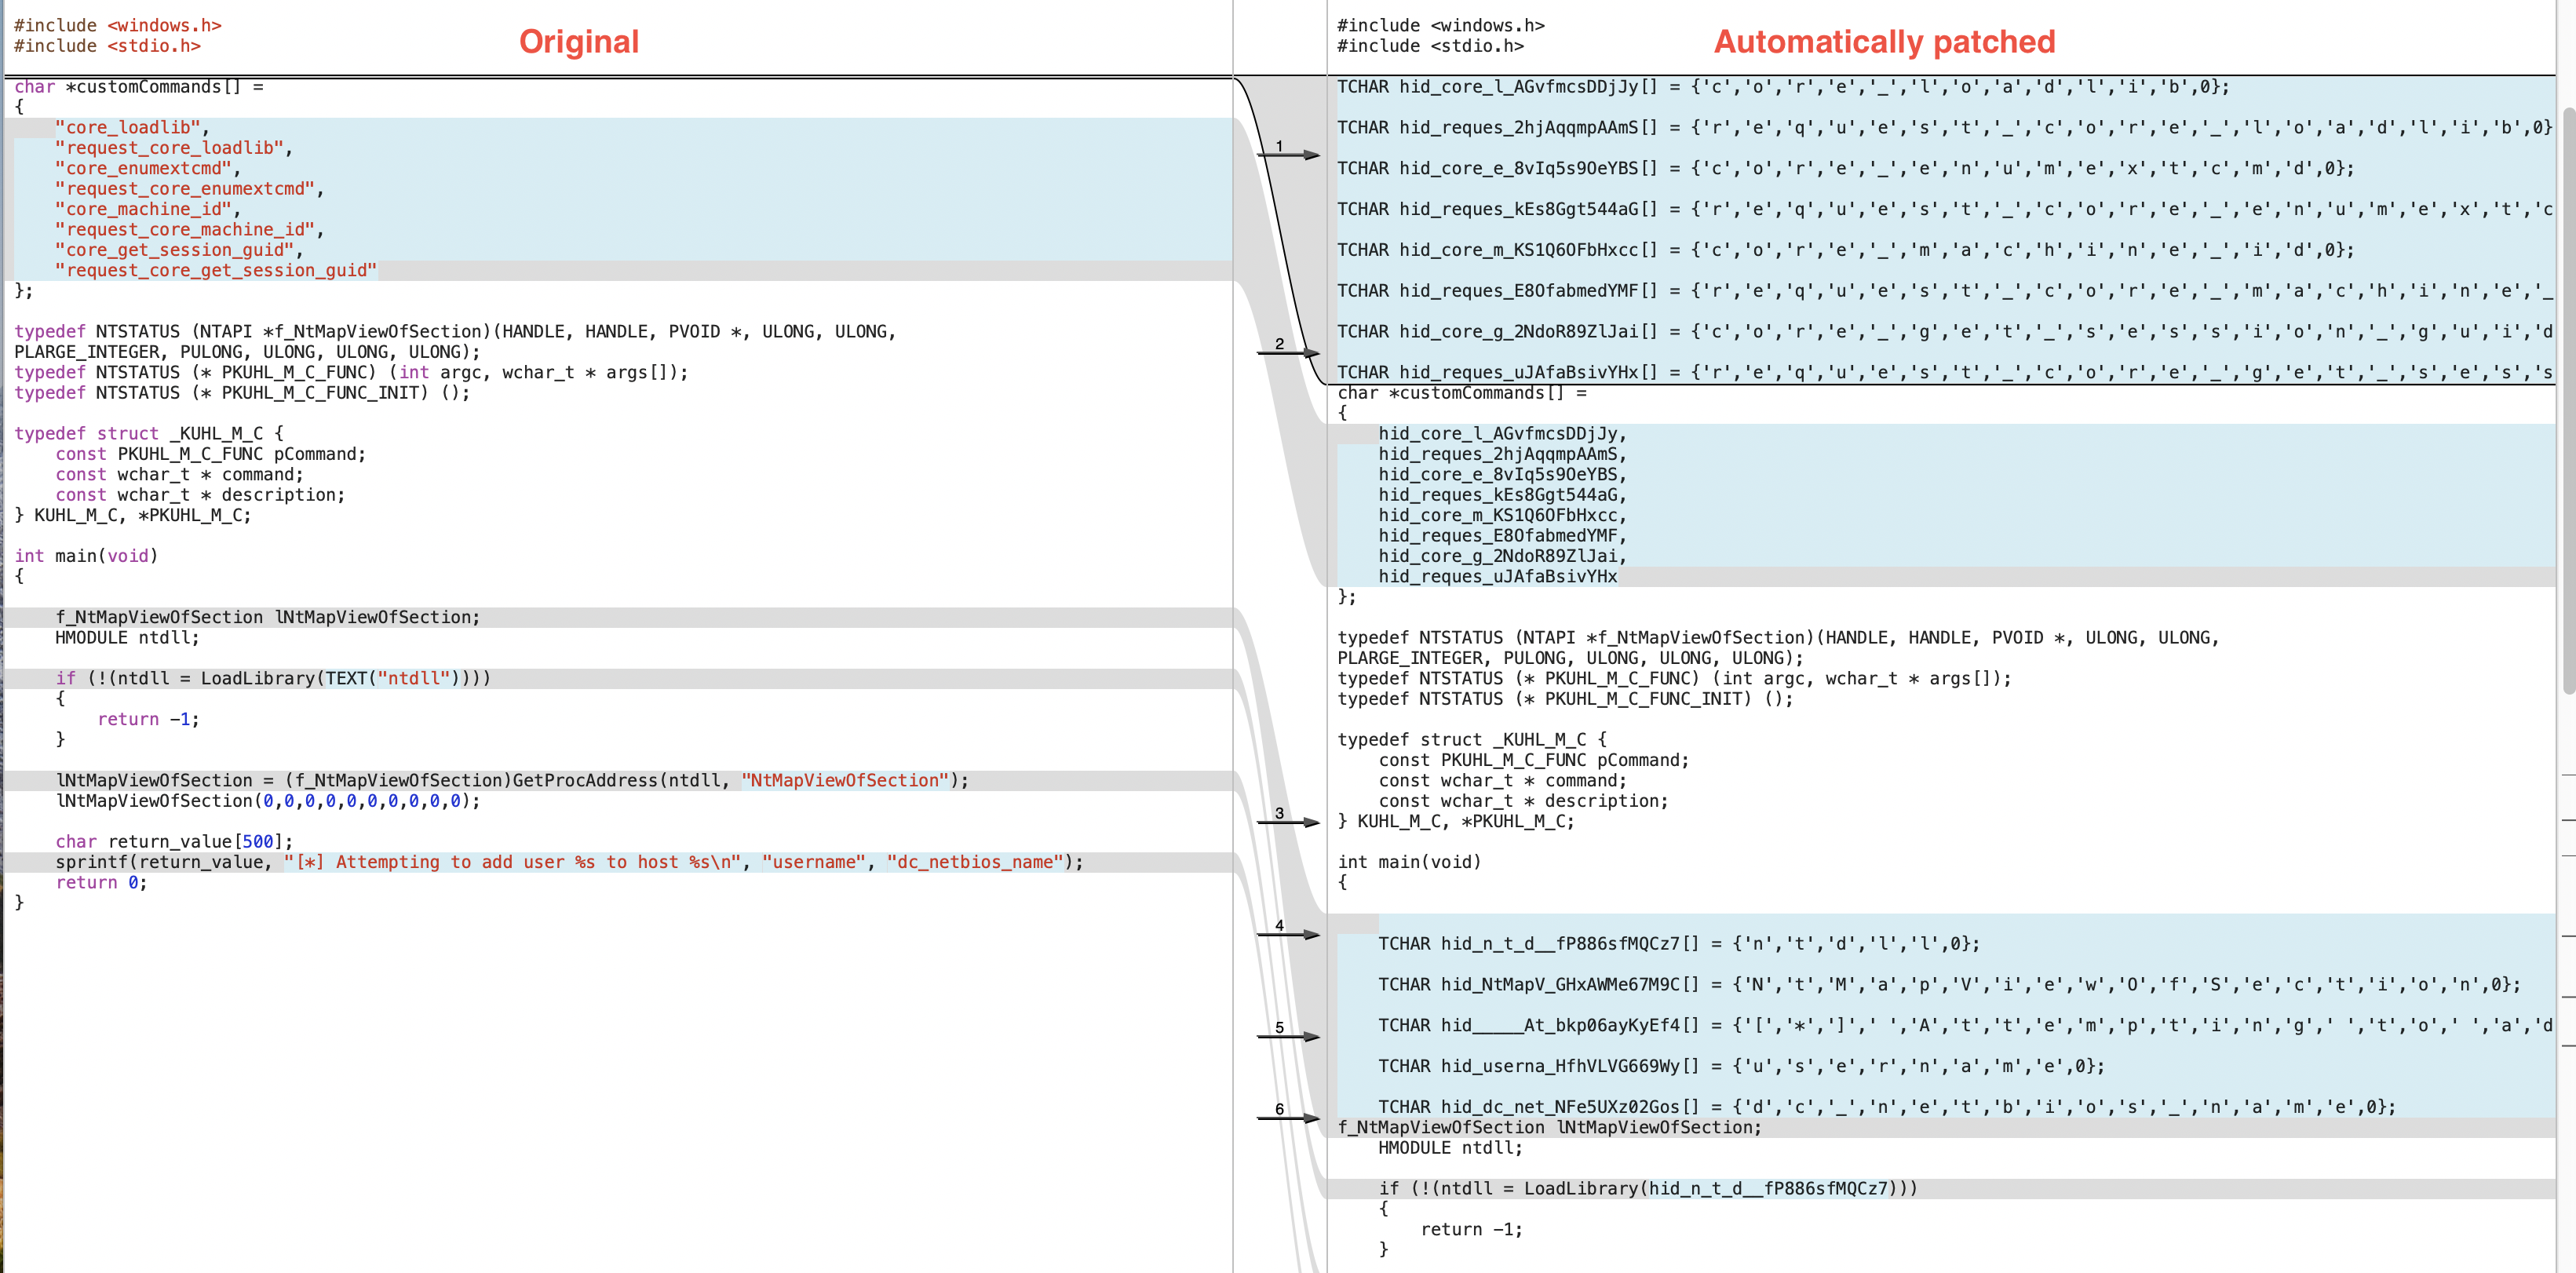
C/C++ source obfuscator for antivirus bypass

Dynamic unpacker and import fixer for Themida/WinLicense 2.x and 3.x.

Multi-Packer wrapper letting us daisy-chain various packers, obfuscators and other Red Team oriented weaponry. Featured with artifacts watermarking,…

A PowerShell Module Dedicated to Reverse Engineering

The unofficial Official FirmWare, a complete latest PSP firmware reverse engineering project