
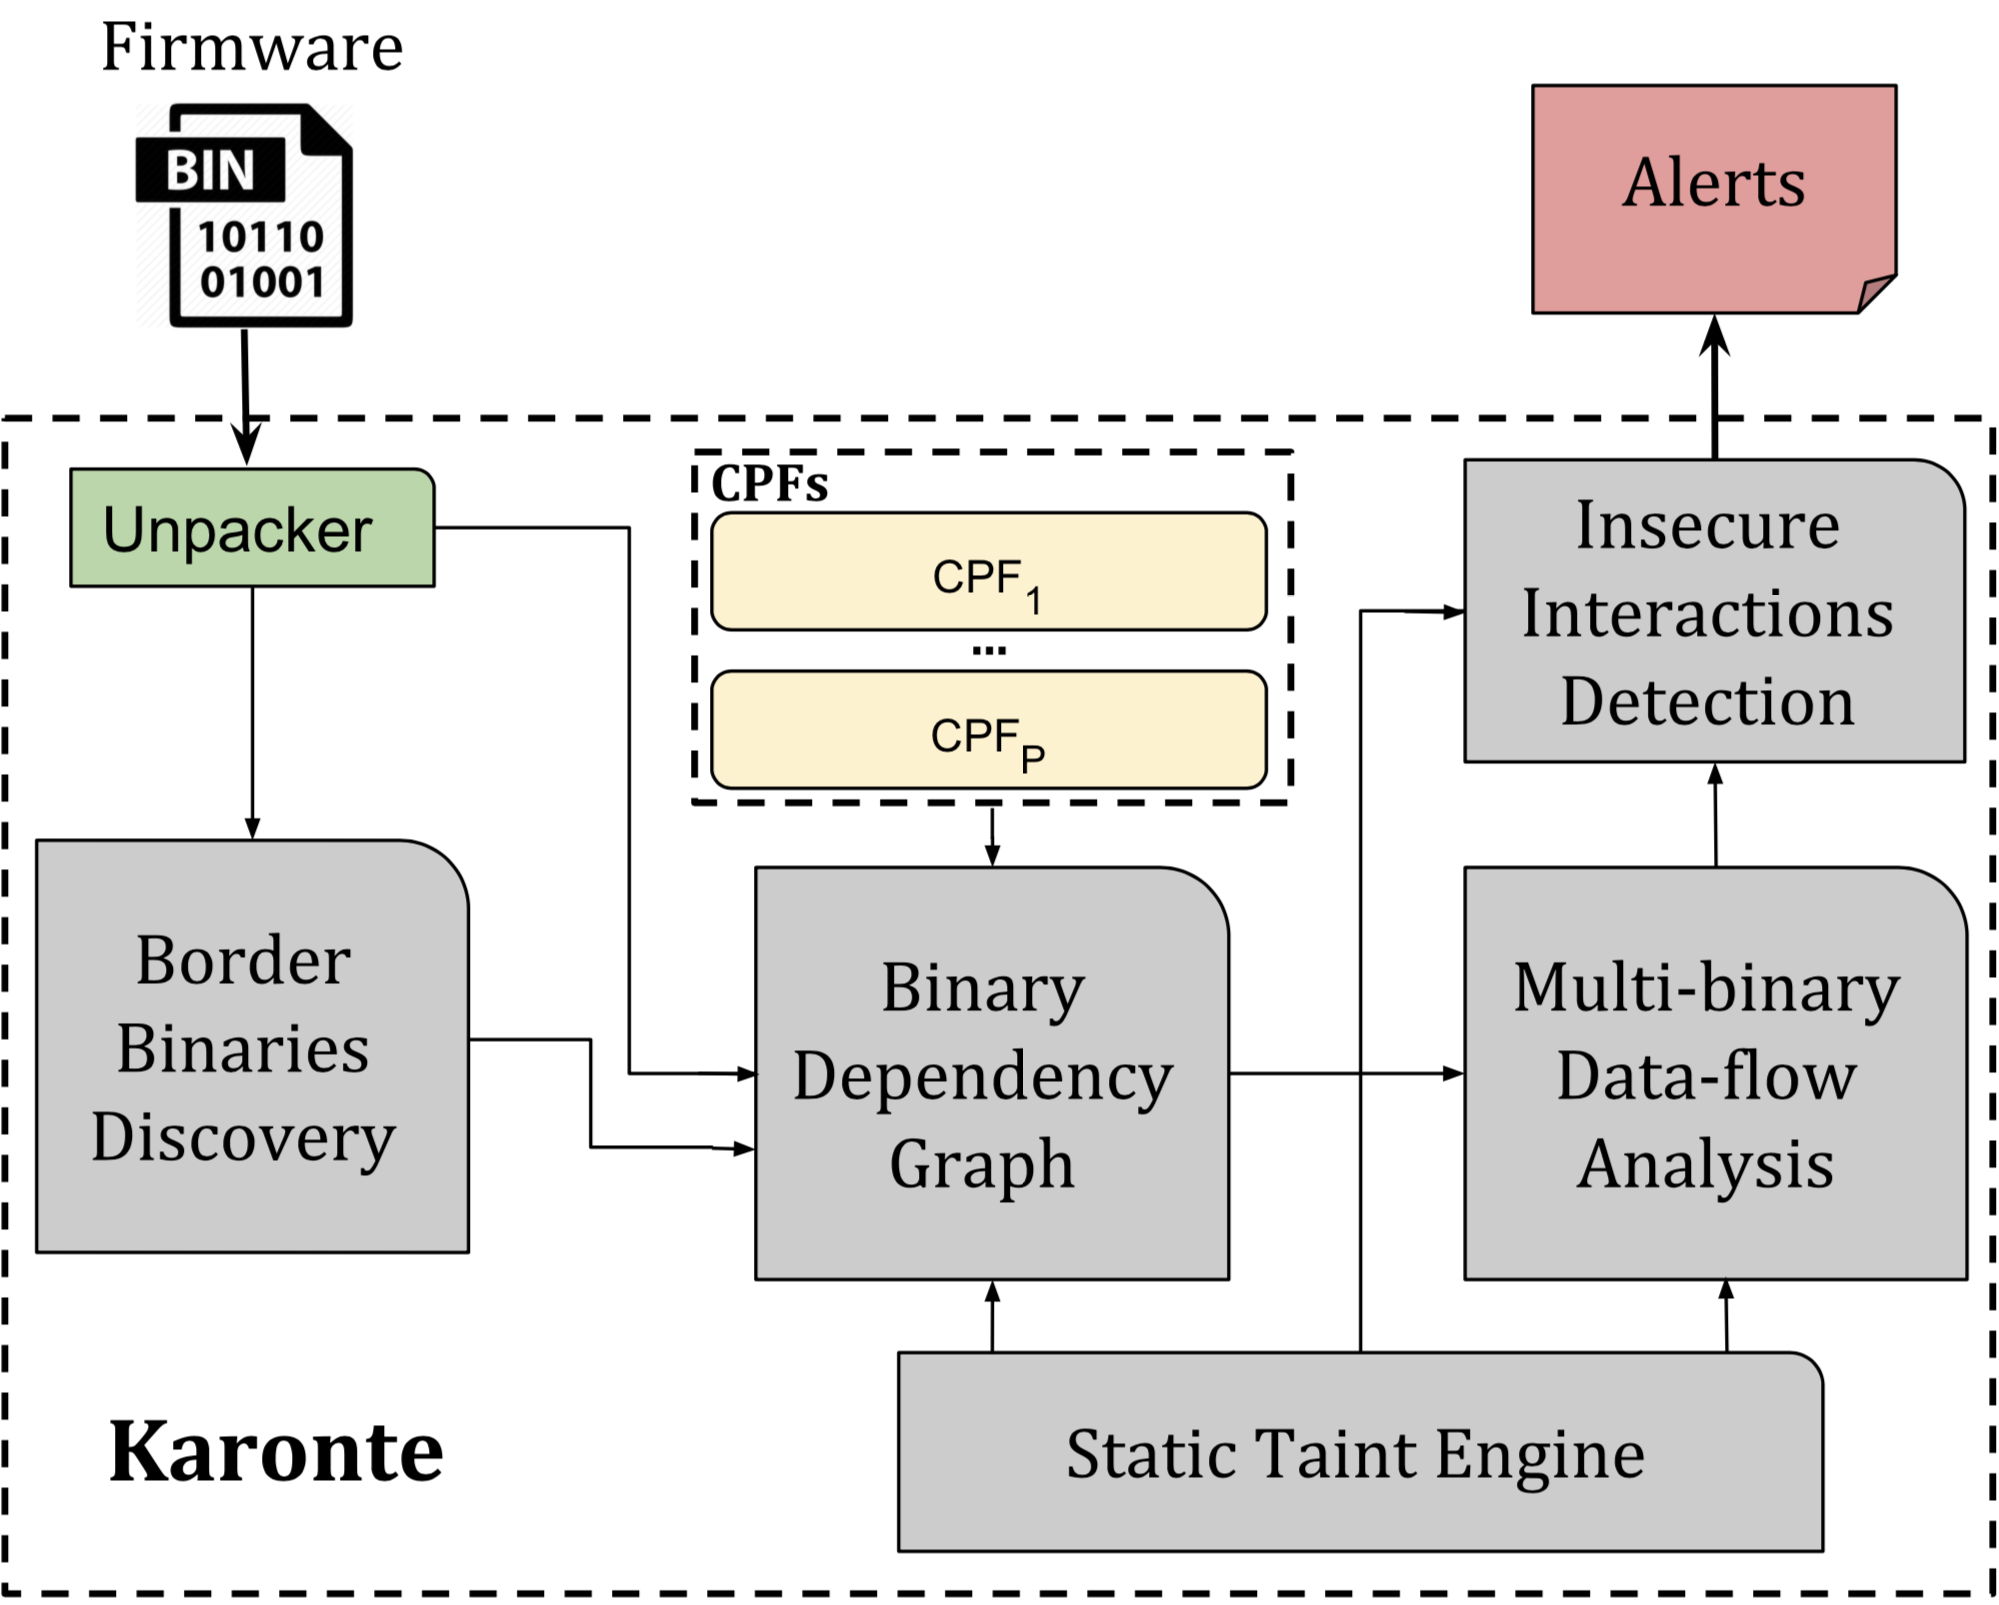
karonte
 ucsb-seclab/karonte
Karonte is a static analysis tool to detect multi-binary vulnerabilities in embedded firmware
binary-analysisembedded-systems-securityfirmware-analysis+2
434
ucsb-seclab/karonteKaronte is a static analysis tool to detect multi-binary vulnerabilities in embedded firmware
 foundryzero/binder-trace
Binder Trace is a tool for intercepting and parsing Android Binder messages. Think of it as "Wireshark for Binder".
 t00sh/rop-tool
A tool to help you write binary exploits
 conscioushacker/wfh
Frida-based dynamic analysis tool that automatically identifies DLL sideloading and COM hijacking vulnerabilities in Windows executables through…
 4w4k3/repy2exe
A Reverse Engineering Tool for py2exe applications.
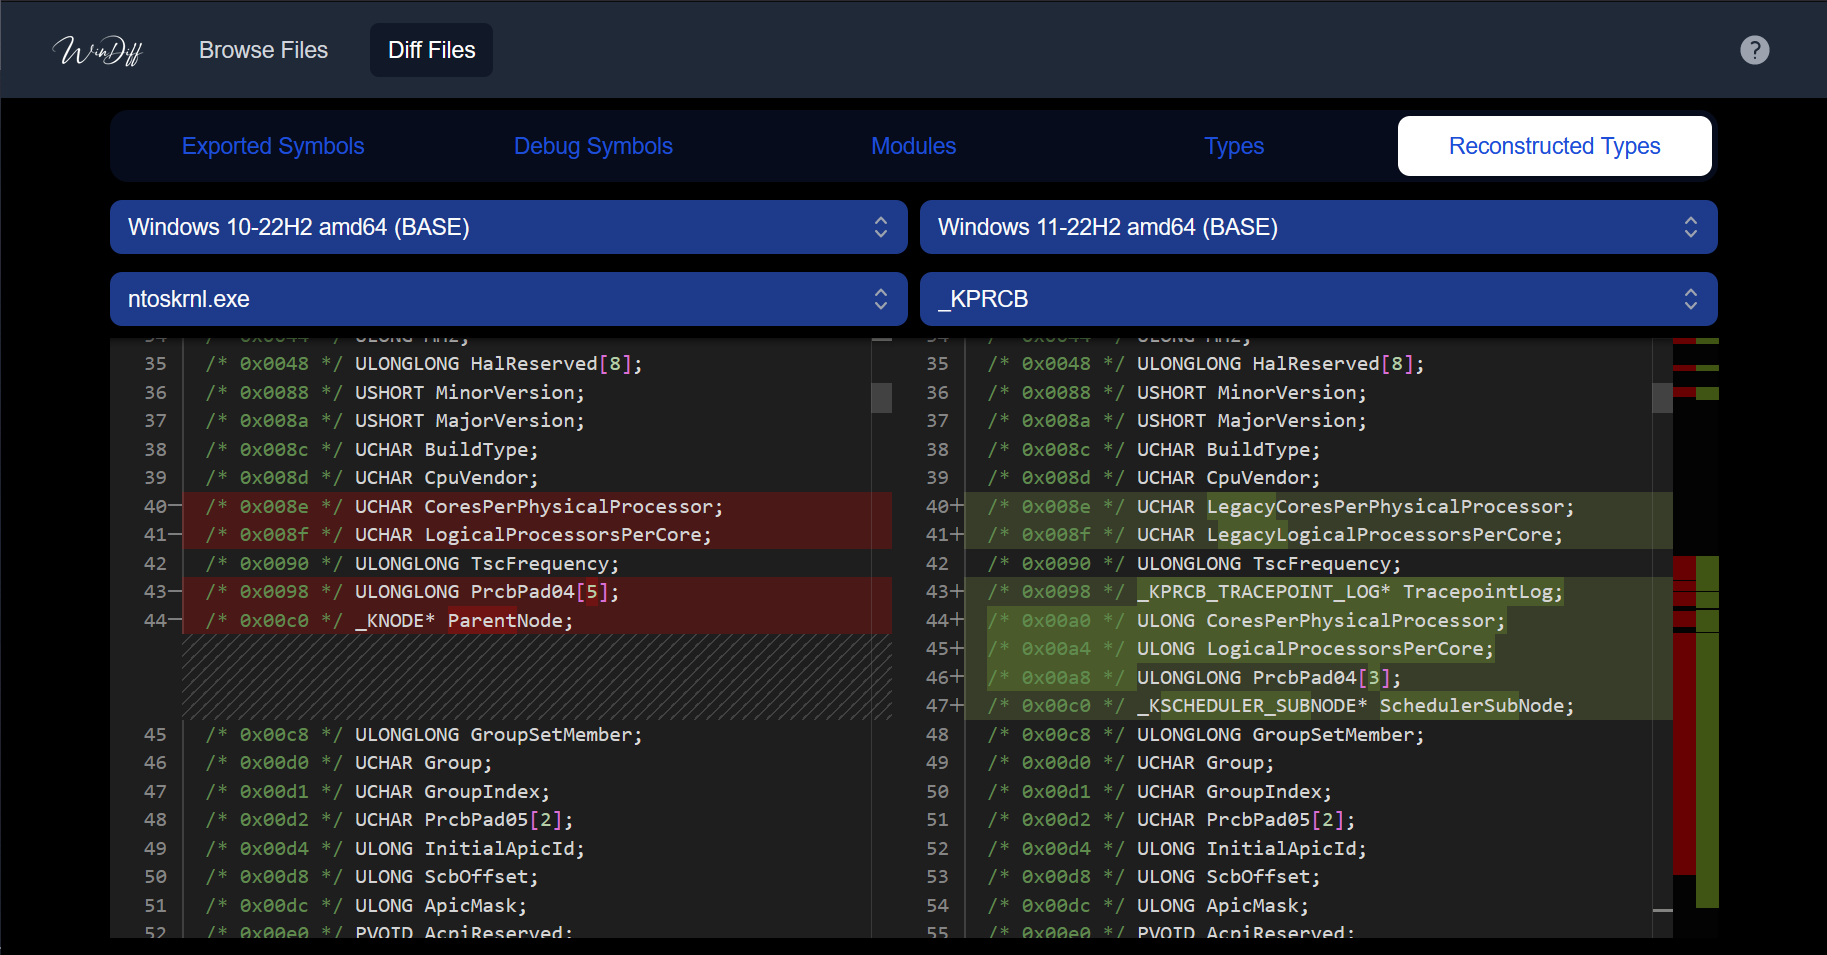 ergrelet/windiff
Tool that allows comparing symbol, type and syscall information of Microsoft Windows binaries across different versions of the OS, using a Web UI…
 pagalaxylab/unifuzzer
A fuzzing tool for closed-source binaries based on Unicorn and LibFuzzer
 sterrasec/apk-medit
memory search and patch tool on debuggable apk without root & ndk
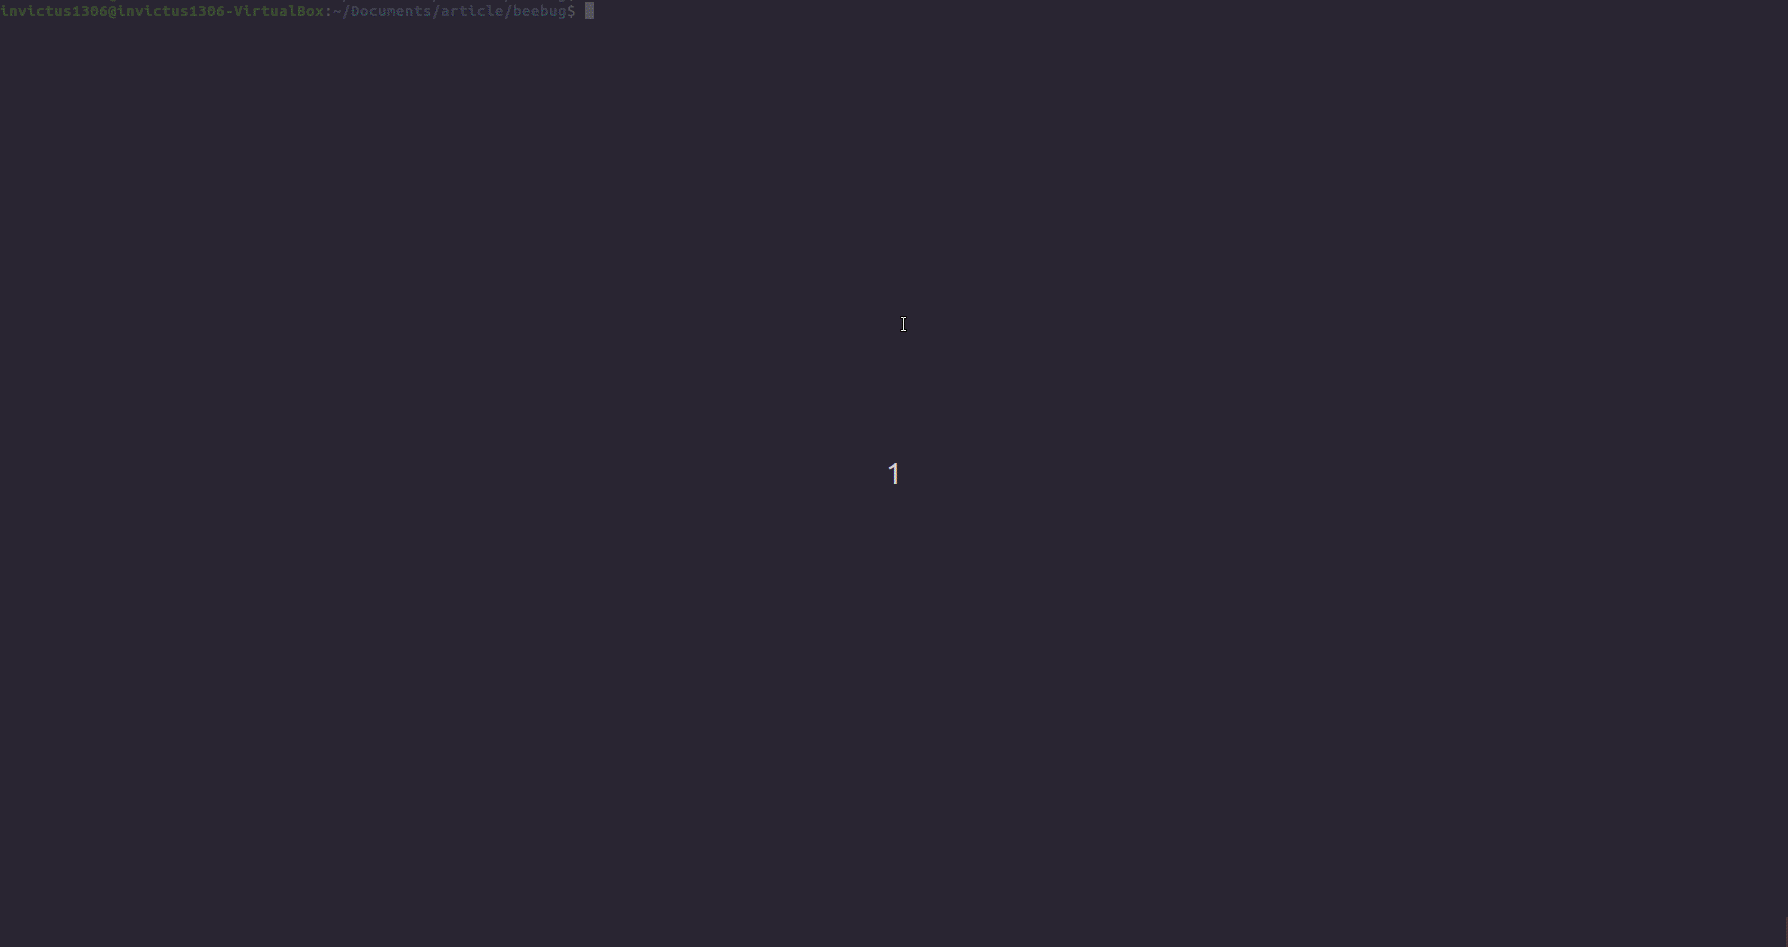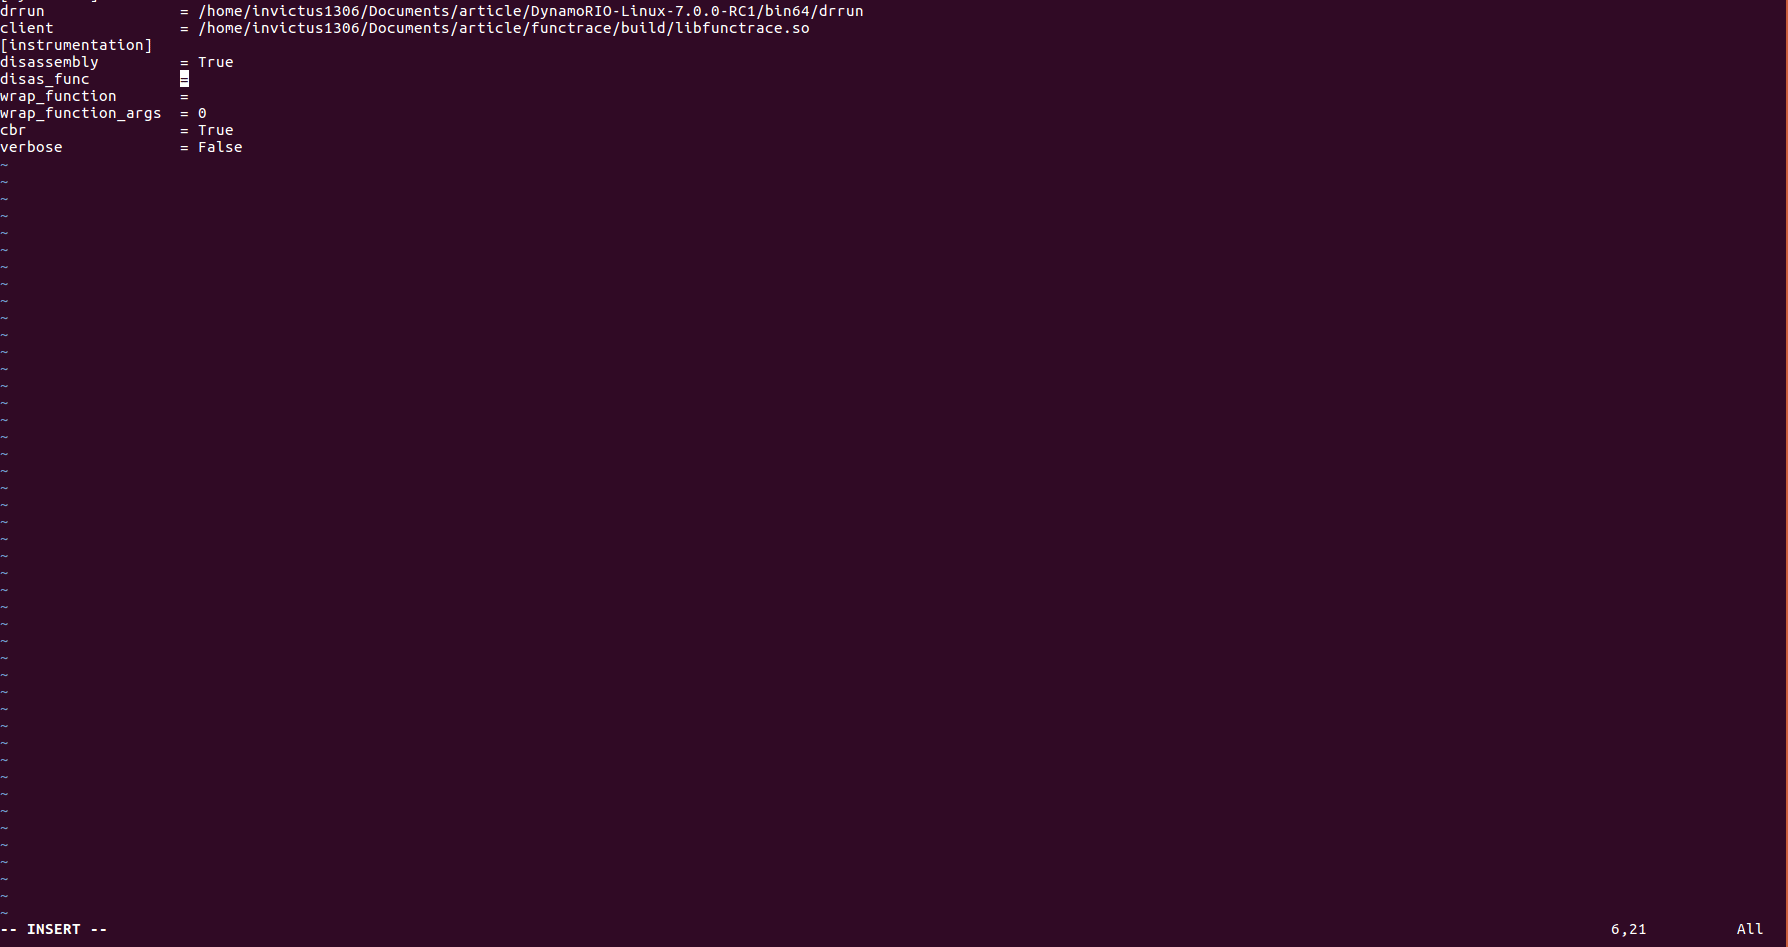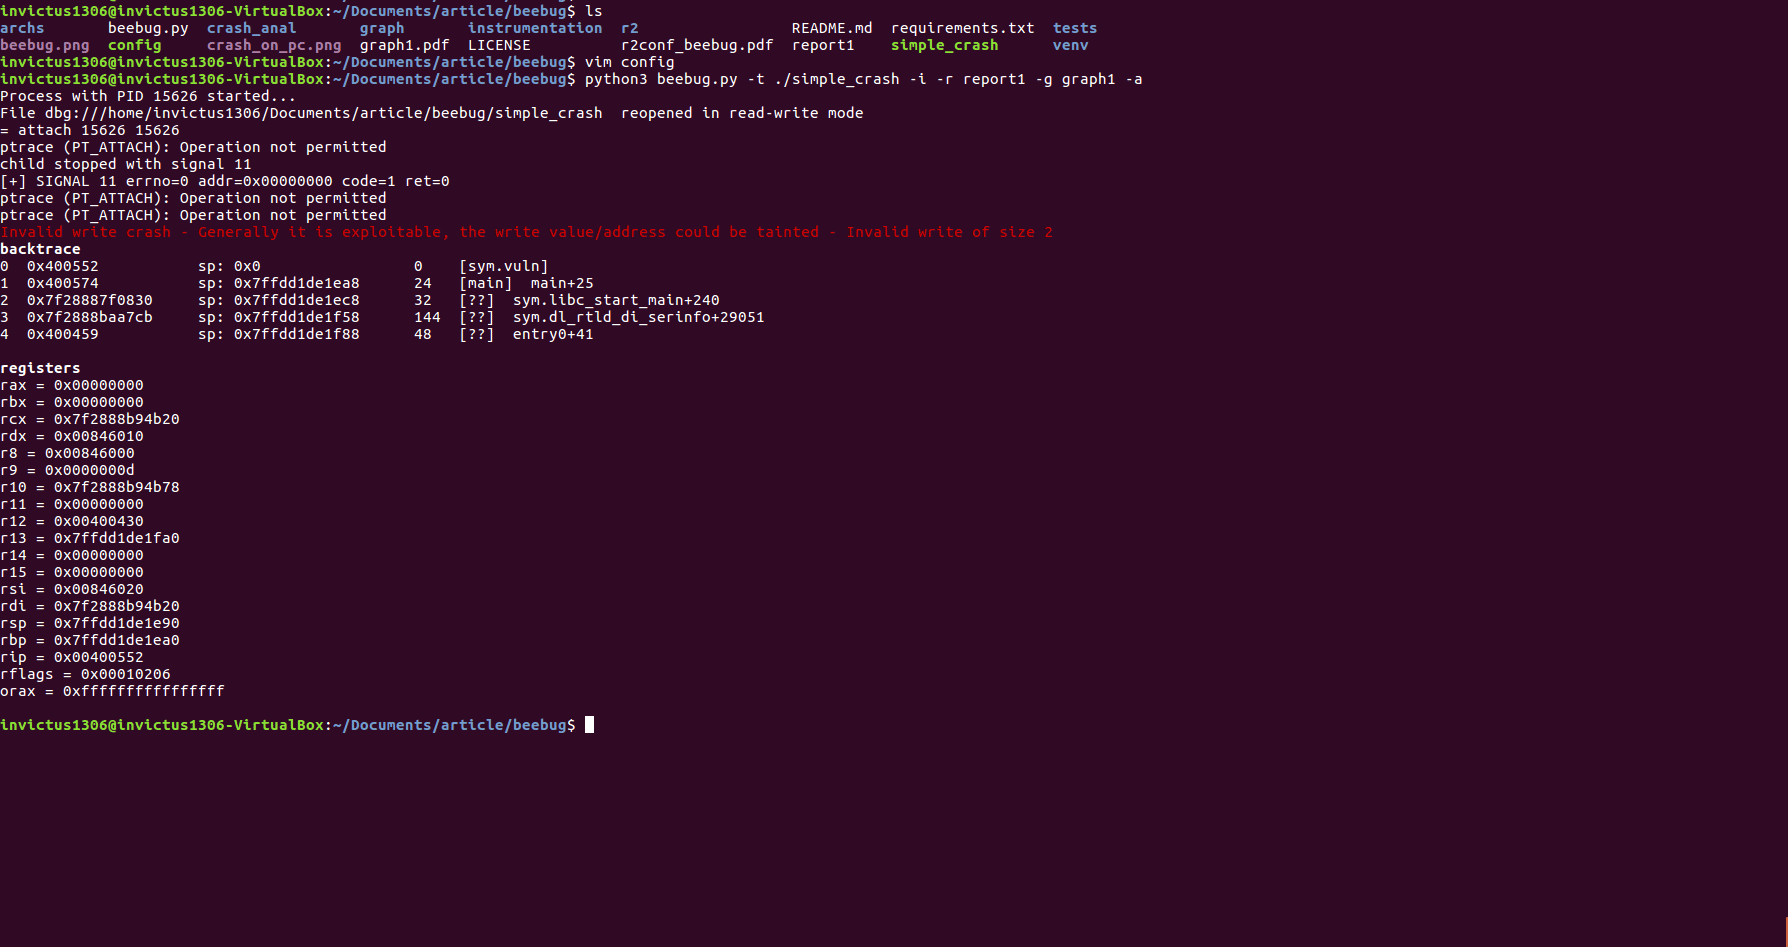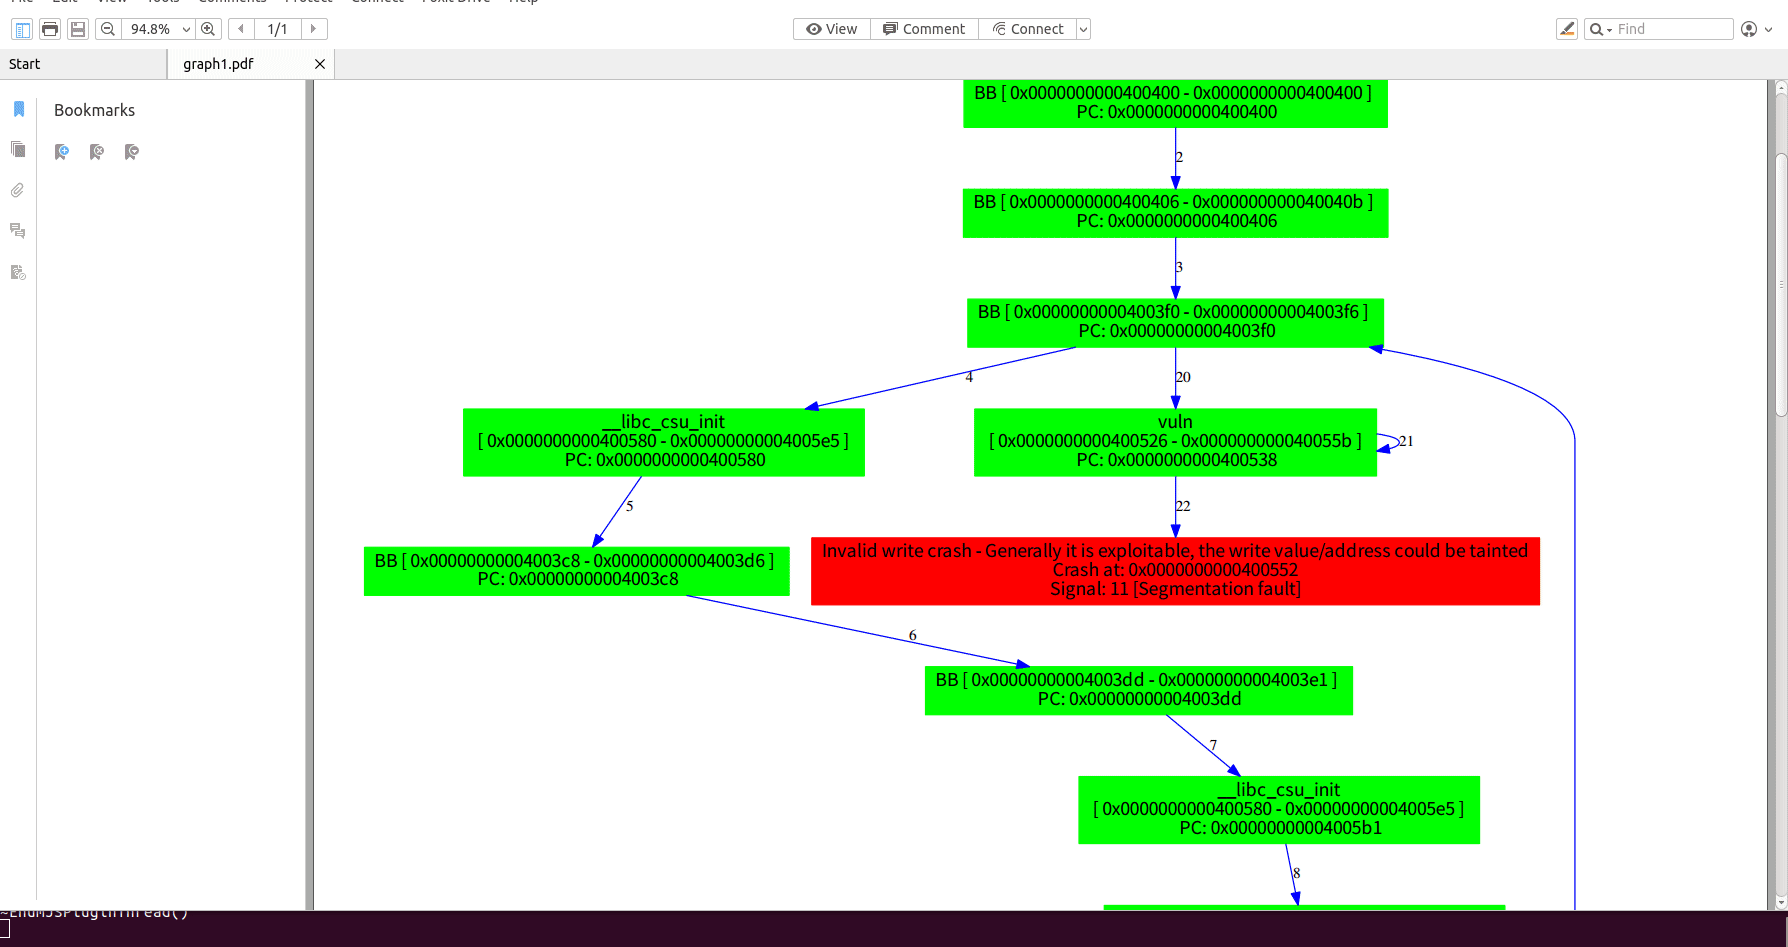
 therealdreg/anticuckoo
A tool to detect and crash Cuckoo Sandbox
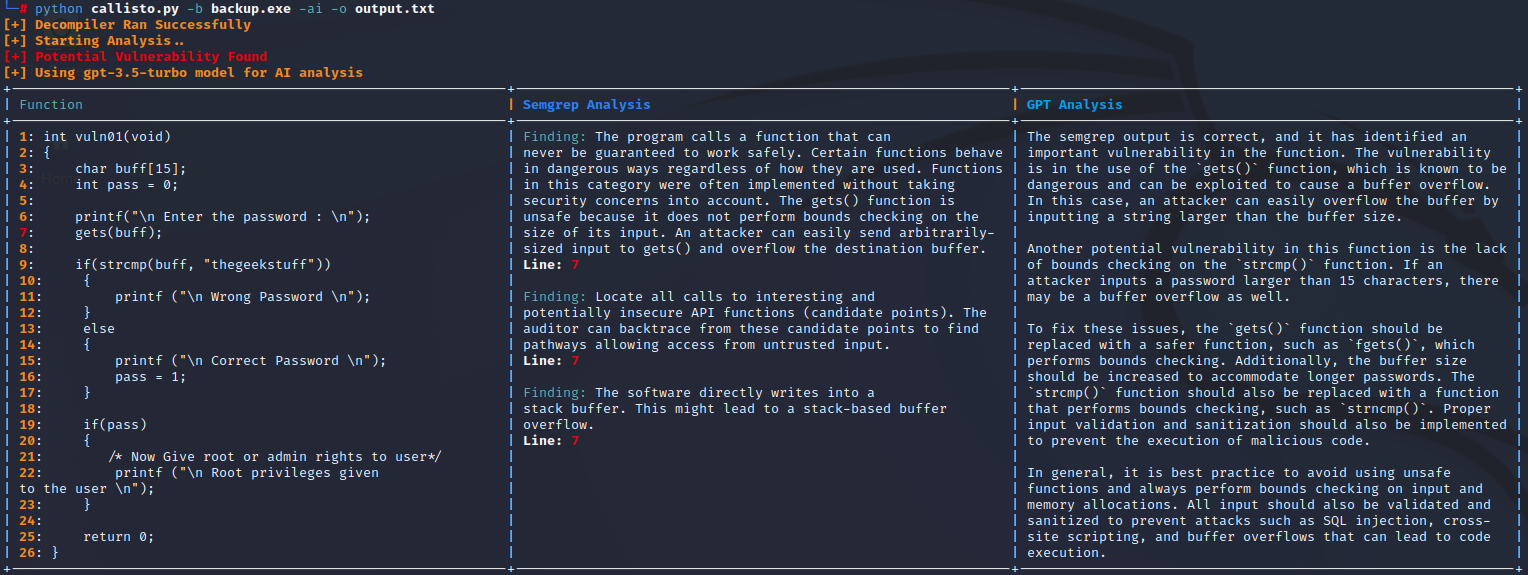 jetp1ane/callisto
Automated binary vulnerability analysis tool that decompiles executables via Ghidra, scans pseudo-C code with Semgrep, and validates findings using…
 netspooky/inhale
A malware analysis and classification tool.
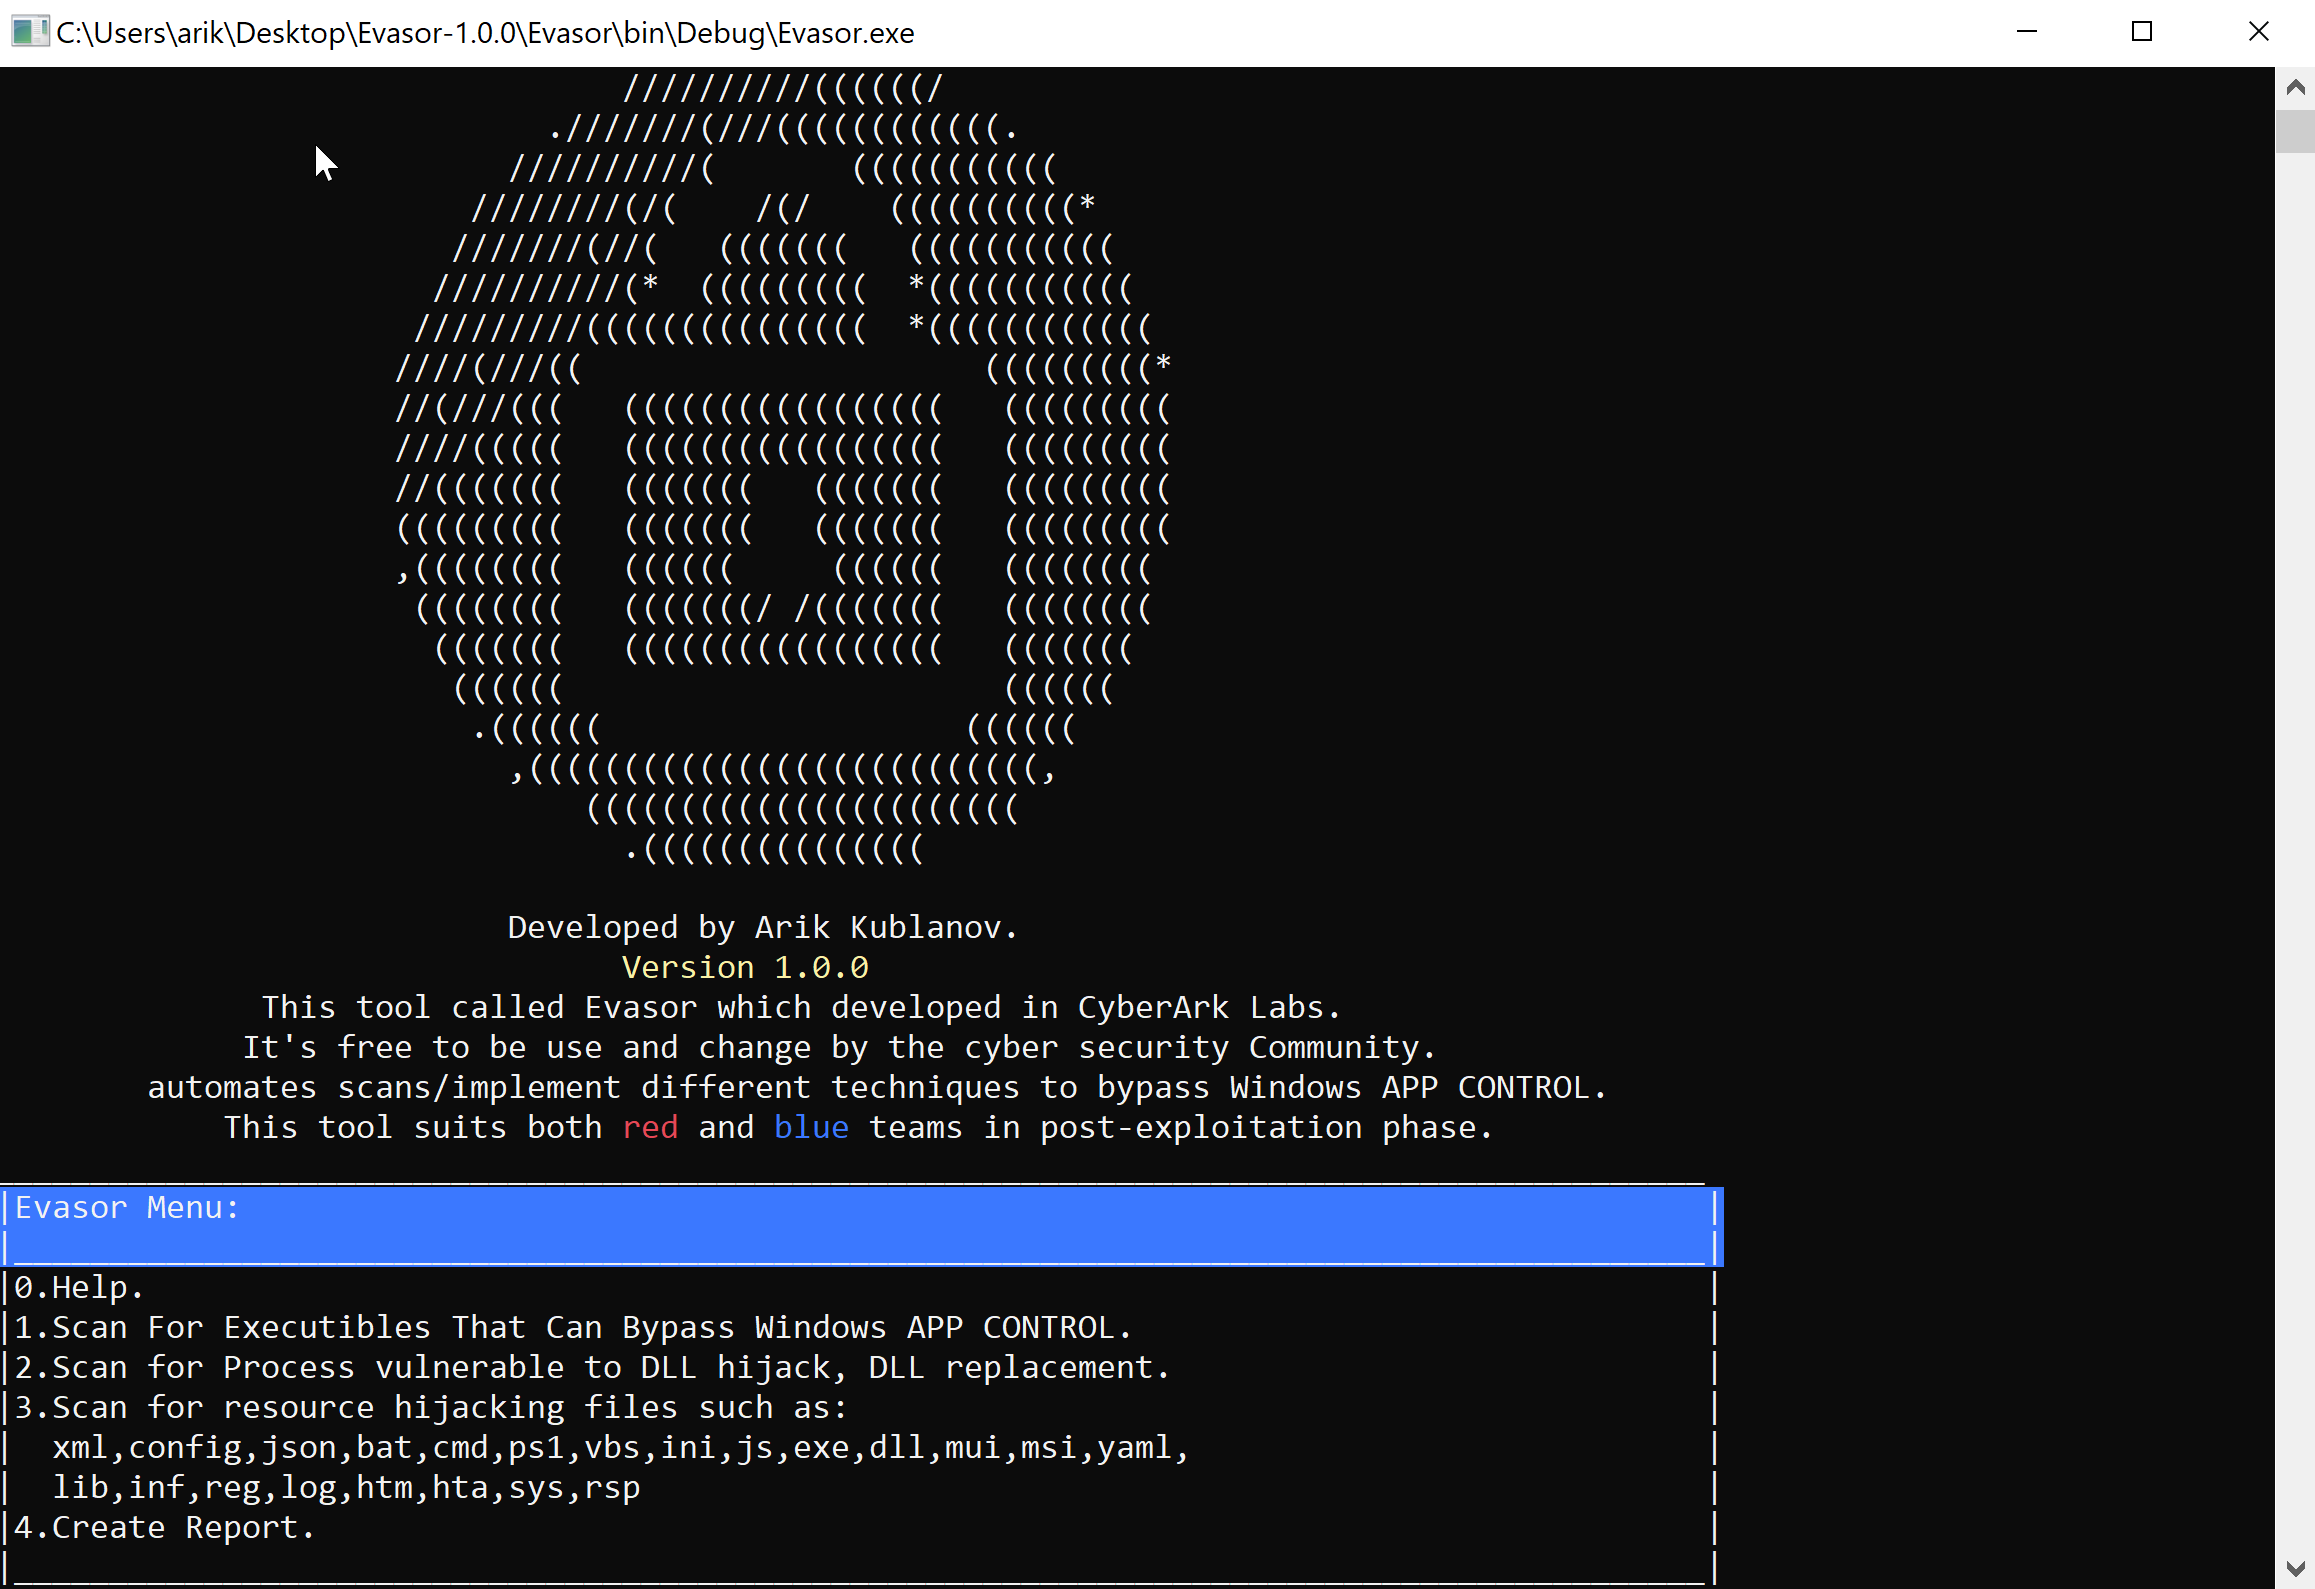 cyberark/evasor
A tool to be used in post exploitation phase for blue and red teams to bypass APPLICATIONCONTROL policies
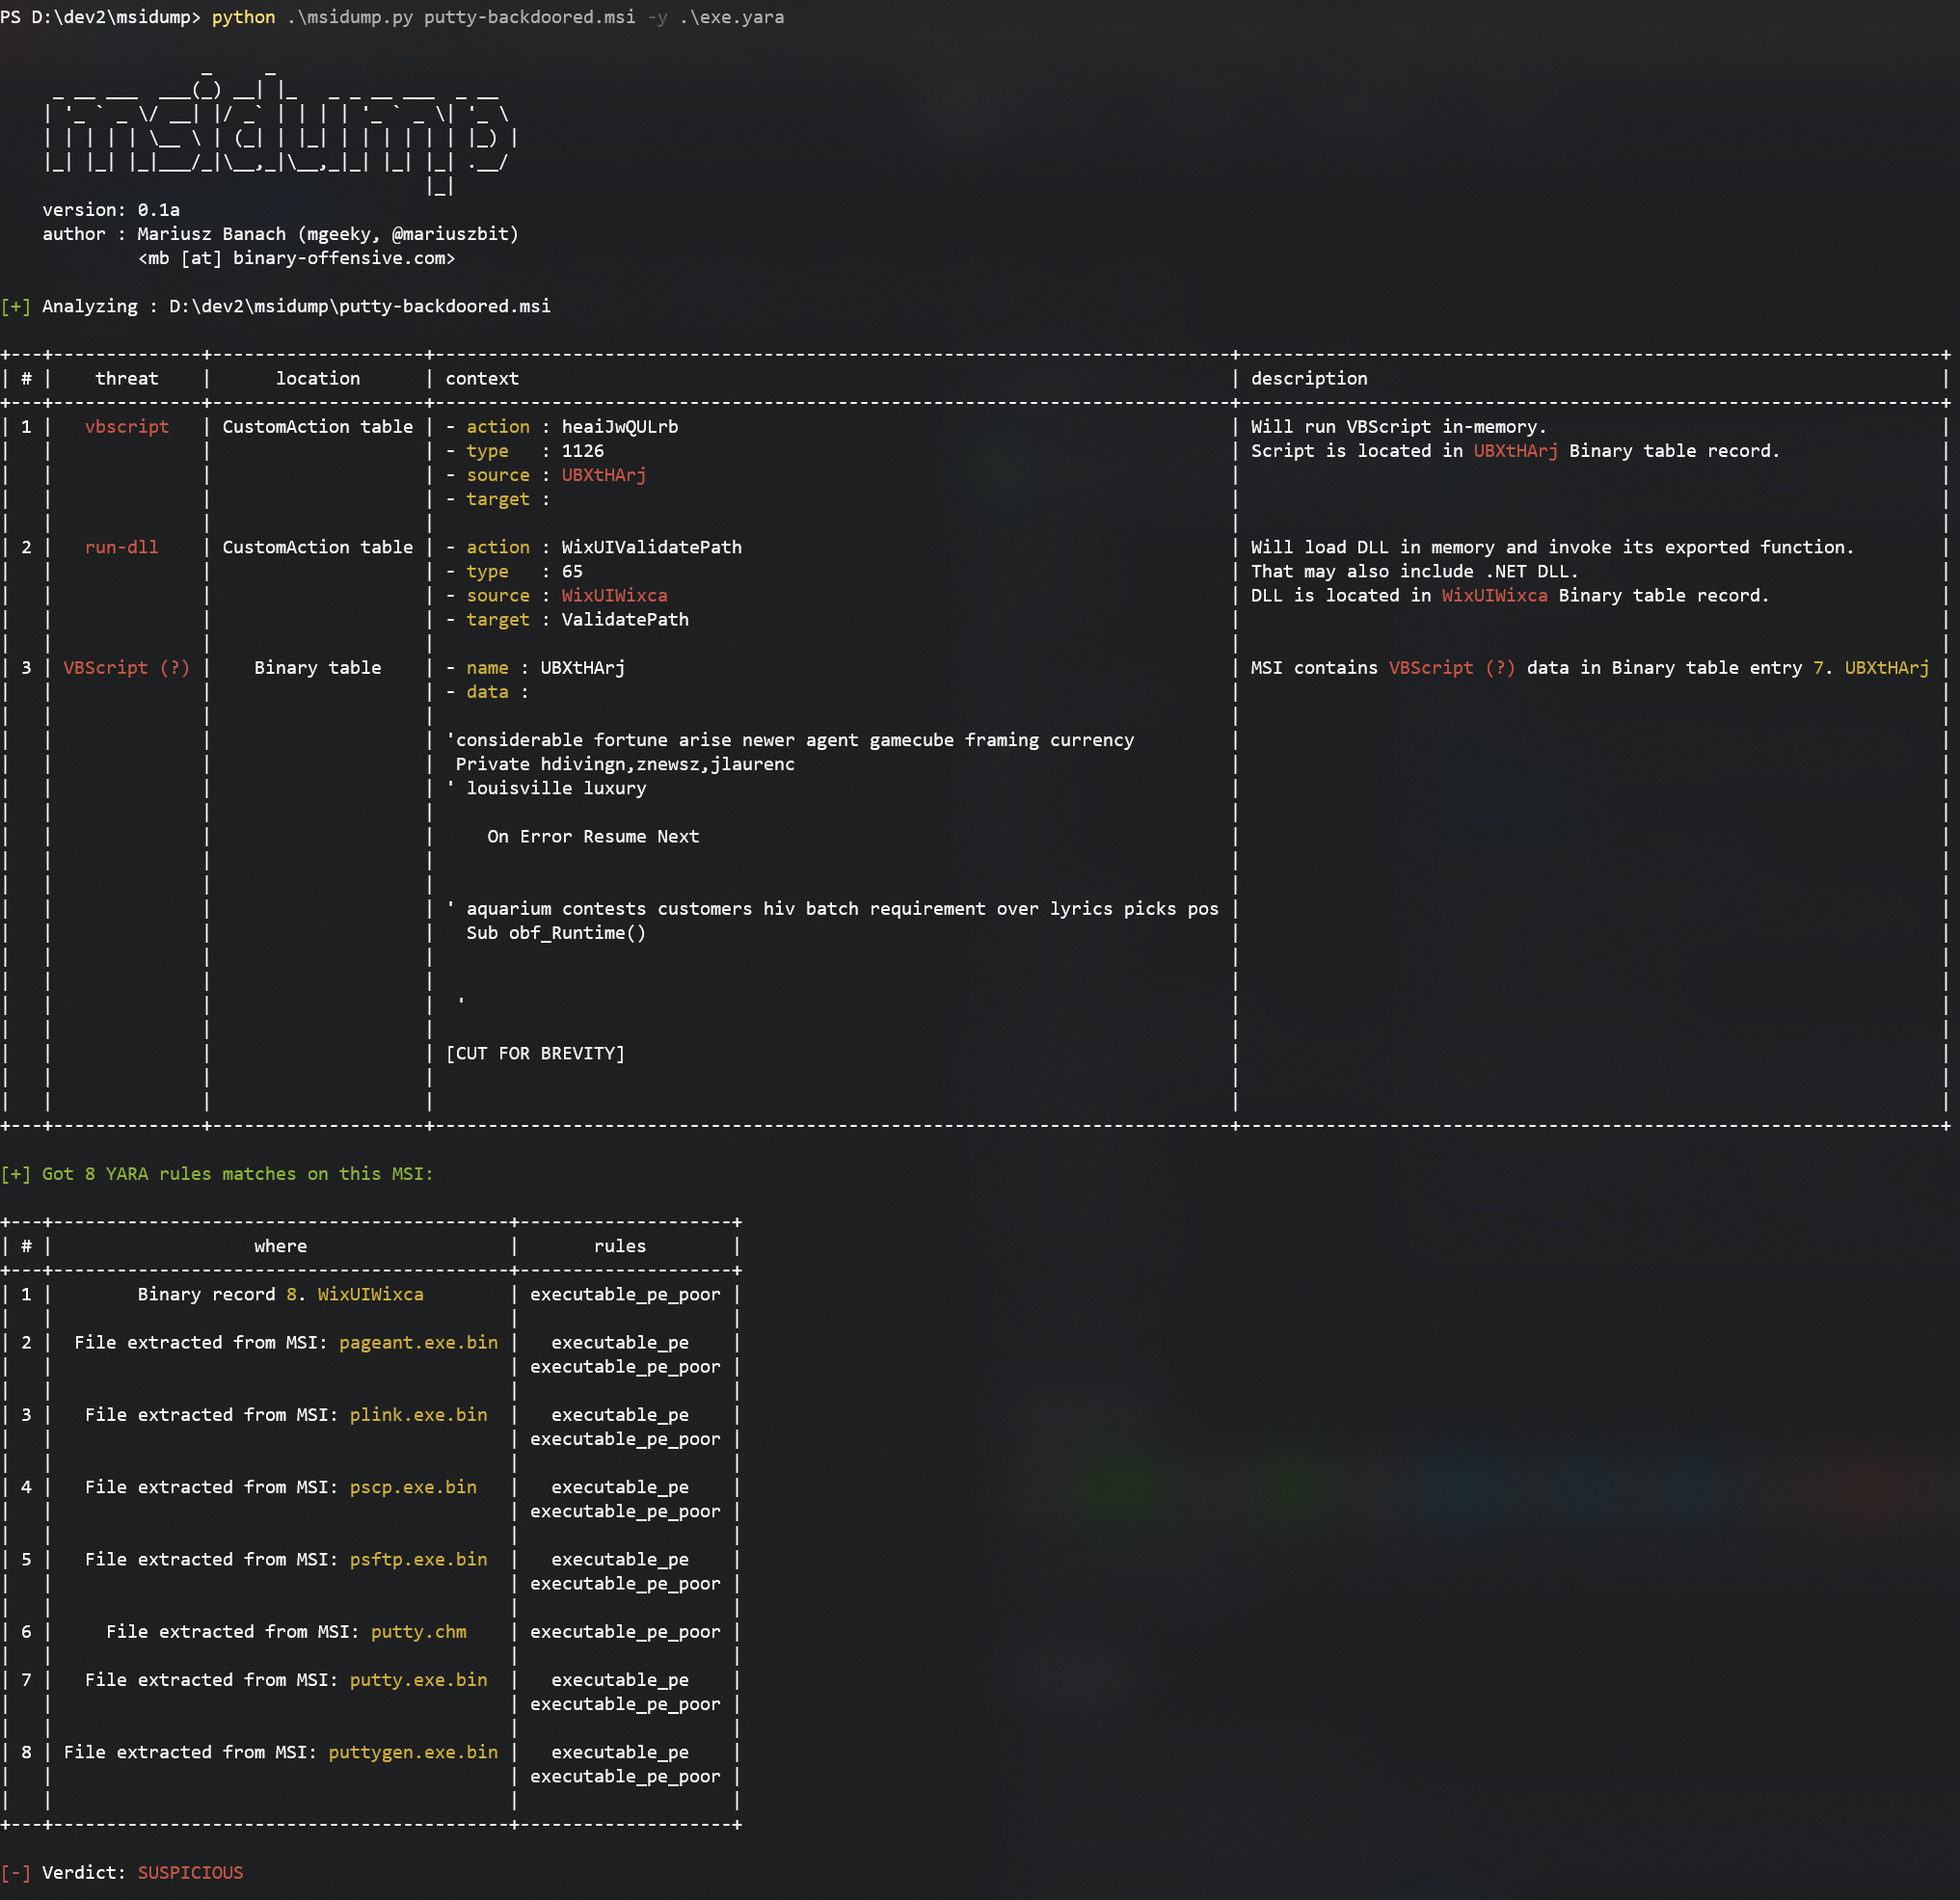 mgeeky/msidump
MSI Dump - a tool that analyzes malicious MSI installation packages, extracts files, streams, binary data and incorporates YARA scanner.
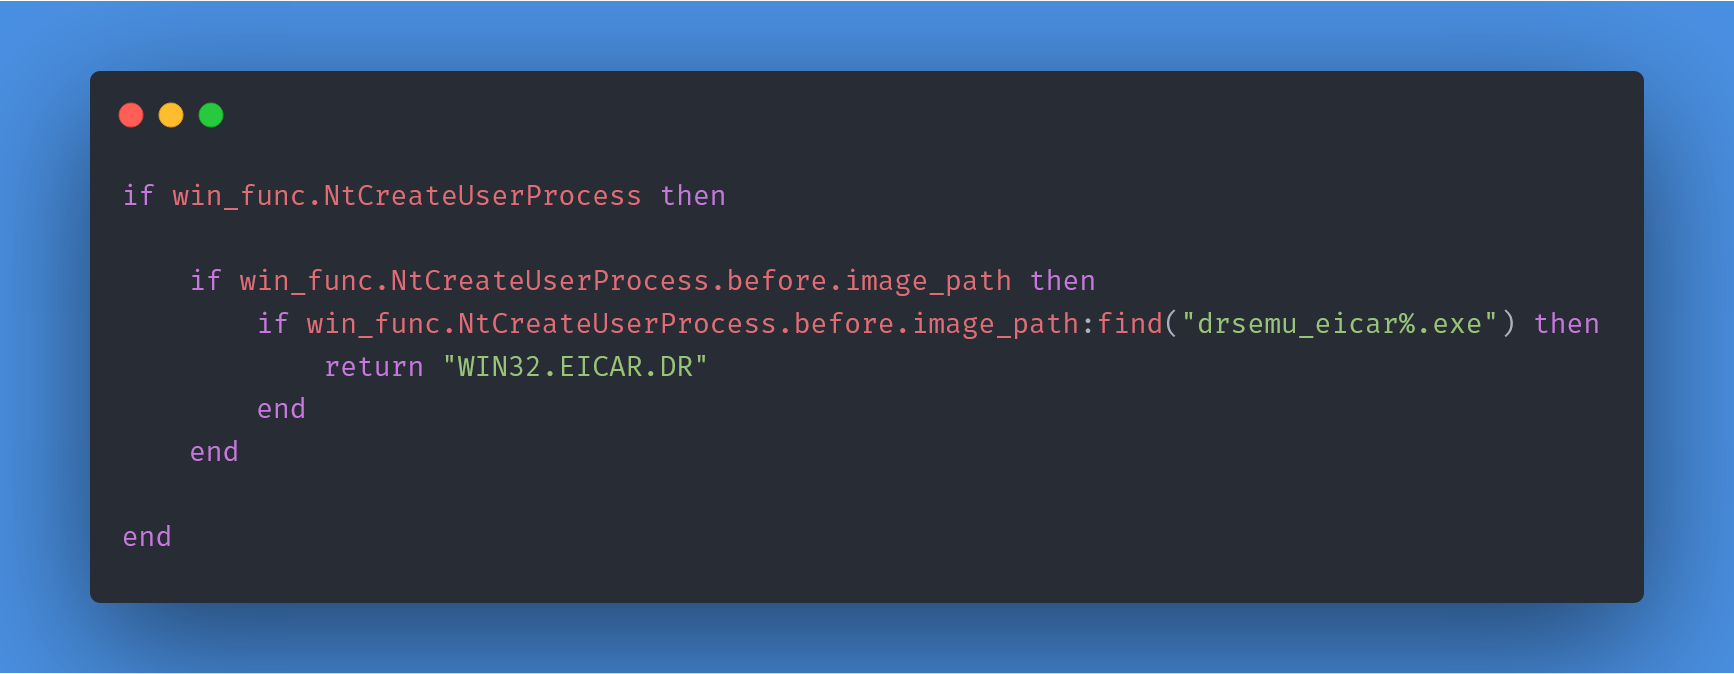 secrary/drsemu
DrSemu - Sandboxed Malware Detection and Classification Tool Based on Dynamic Behavior
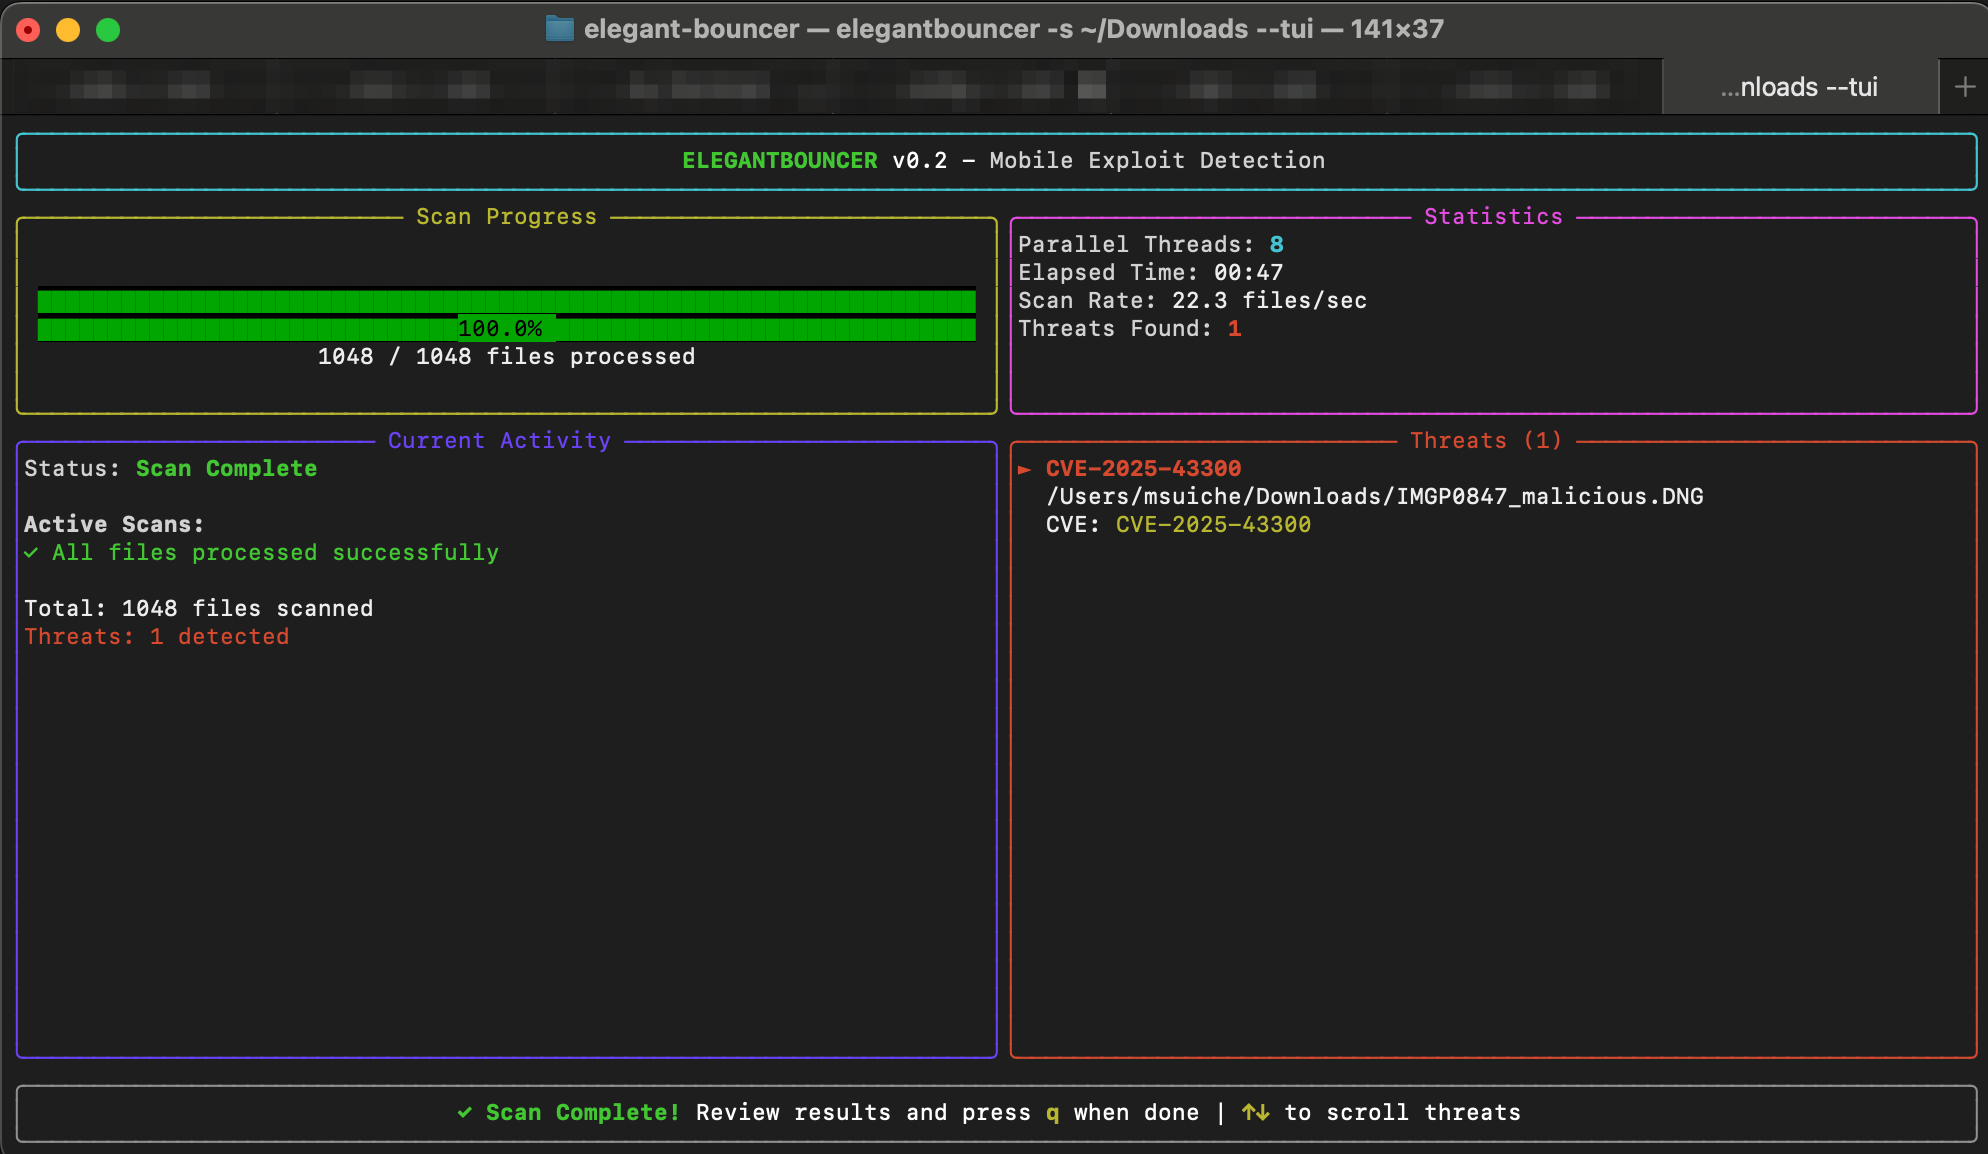 msuiche/elegant-bouncer
ELEGANTBOUNCER is a detection tool for file-based mobile exploits.
 k2/ehtrace
ATrace is a tool for tracing execution of binaries on Windows.