
DECAF
 decaf-project/decaf
DECAF (short for Dynamic Executable Code Analysis Framework) is a binary analysis platform based on QEMU. This is also the home of the DroidScope…
android-securitybinary-analysisdynamic-analysis-sandboxing+2
841
decaf-project/decafDECAF (short for Dynamic Executable Code Analysis Framework) is a binary analysis platform based on QEMU. This is also the home of the DroidScope…
 calebfenton/dex-oracle
A pattern based Dalvik deobfuscator which uses limited execution to improve semantic analysis
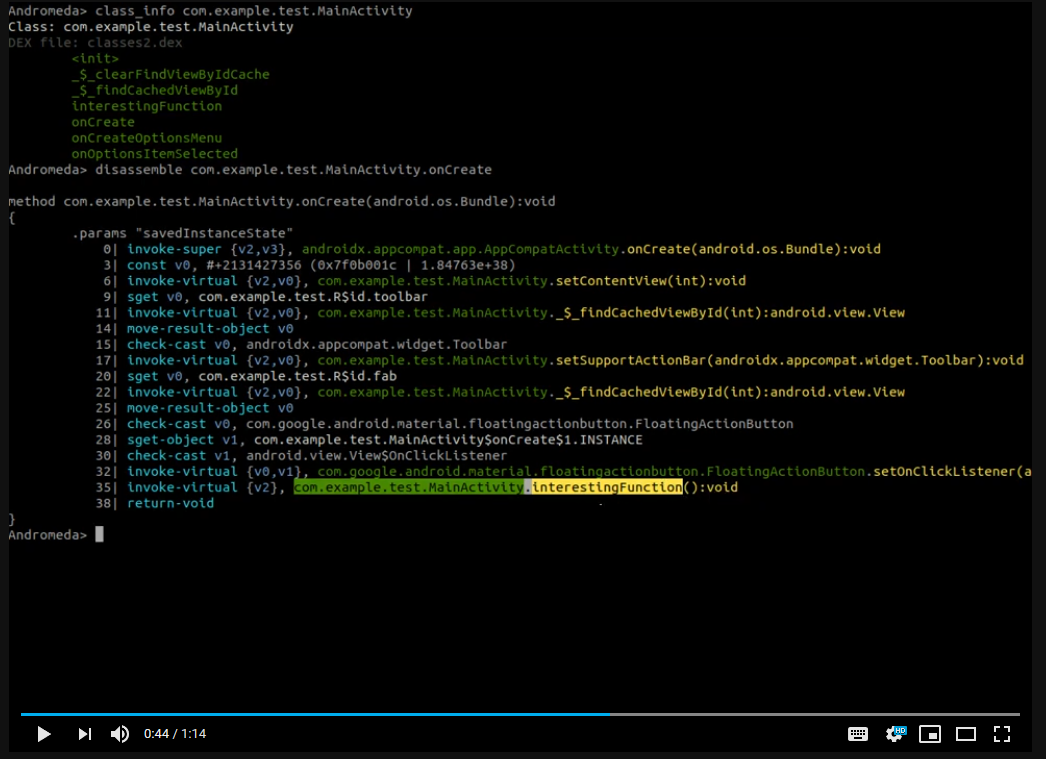 secrary/andromeda
C/C++ interactive reverse engineering tool for Android applications, enabling fast static analysis and binary inspection of APK files.
 yhs0602/android-disassembler
Disassemble ANY files including .so (NDK, JNI), Windows PE(EXE, DLL, SYS, etc), linux binaries, libraries, and any other files such as pictures,…
 theqmaks/phantom-frida
Build anti-detection Frida server from source. ~90 patches covering 16 detection vectors, weekly auto-builds with random names.
 foundryzero/binder-trace
Binder Trace is a tool for intercepting and parsing Android Binder messages. Think of it as "Wireshark for Binder".
 ucsb-seclab/bootstomp
BootStomp: a bootloader vulnerability finder
 fuzzysecurity/fermion
Fermion, an electron wrapper for Frida & Monaco.
 droidefense/engine
Droidefense: Advance Android Malware Analysis Framework
 sterrasec/apk-medit
memory search and patch tool on debuggable apk without root & ndk
 arguslab/argus-saf
Scala-based static analysis framework for Android and Java bytecode with flow analysis, decompilation, and native code analysis via symbolic…
 rovellipaolo/ninjadroid
Ninja Reverse Engineering on Android APK packages
 jakev/pyxamstore
Python utility for parsing Xamarin AssemblyStore blob files
 plum-umd/redexer
The Redexer binary instrumentation framework for Dalvik bytecode
 ch0pin/rdx
A native APK and DEX decompiler written in Rust
 frenchyeti/rasputin
Ressources and papers related to my conferences and work on (un)RASPs. These work is in progress, please be patient :) Don't hesitate to contribute /…