

pyREtic
 mynameismeerkat/pyretic
pyREtic is an extensible framework for in-memory Python 2.x bytecode reverse engineering
binary-analysiscode-analysisdebuggers+5
2683 years ago
mynameismeerkat/pyreticpyREtic is an extensible framework for in-memory Python 2.x bytecode reverse engineering
 ergrelet/themida-unmutate
Static deobfuscator for Themida, WinLicense and Code Virtualizer 3.x's mutation-based obfuscation.
 jakev/pyxamstore
Python utility for parsing Xamarin AssemblyStore blob files
 oalabs/findyara-ida
IDA python plugin to scan binary with Yara rules
 quosecgmbh/grap
Define and match user-defined graph patterns against binary control flow graphs using a Capstone-based disassembler, with CLI, Python bindings, and…
 trolldbois/python-haystack
Process heap analysis framework - Windows/Linux - record type inference and forensics
 idiom/pftriage
Python tool and library to help analyze files during malware triage and analysis.
 synacktiv/bip
Object-oriented Python API to simplify interaction with IDA for reverse engineering, enabling plugin development and automation of disassembly…
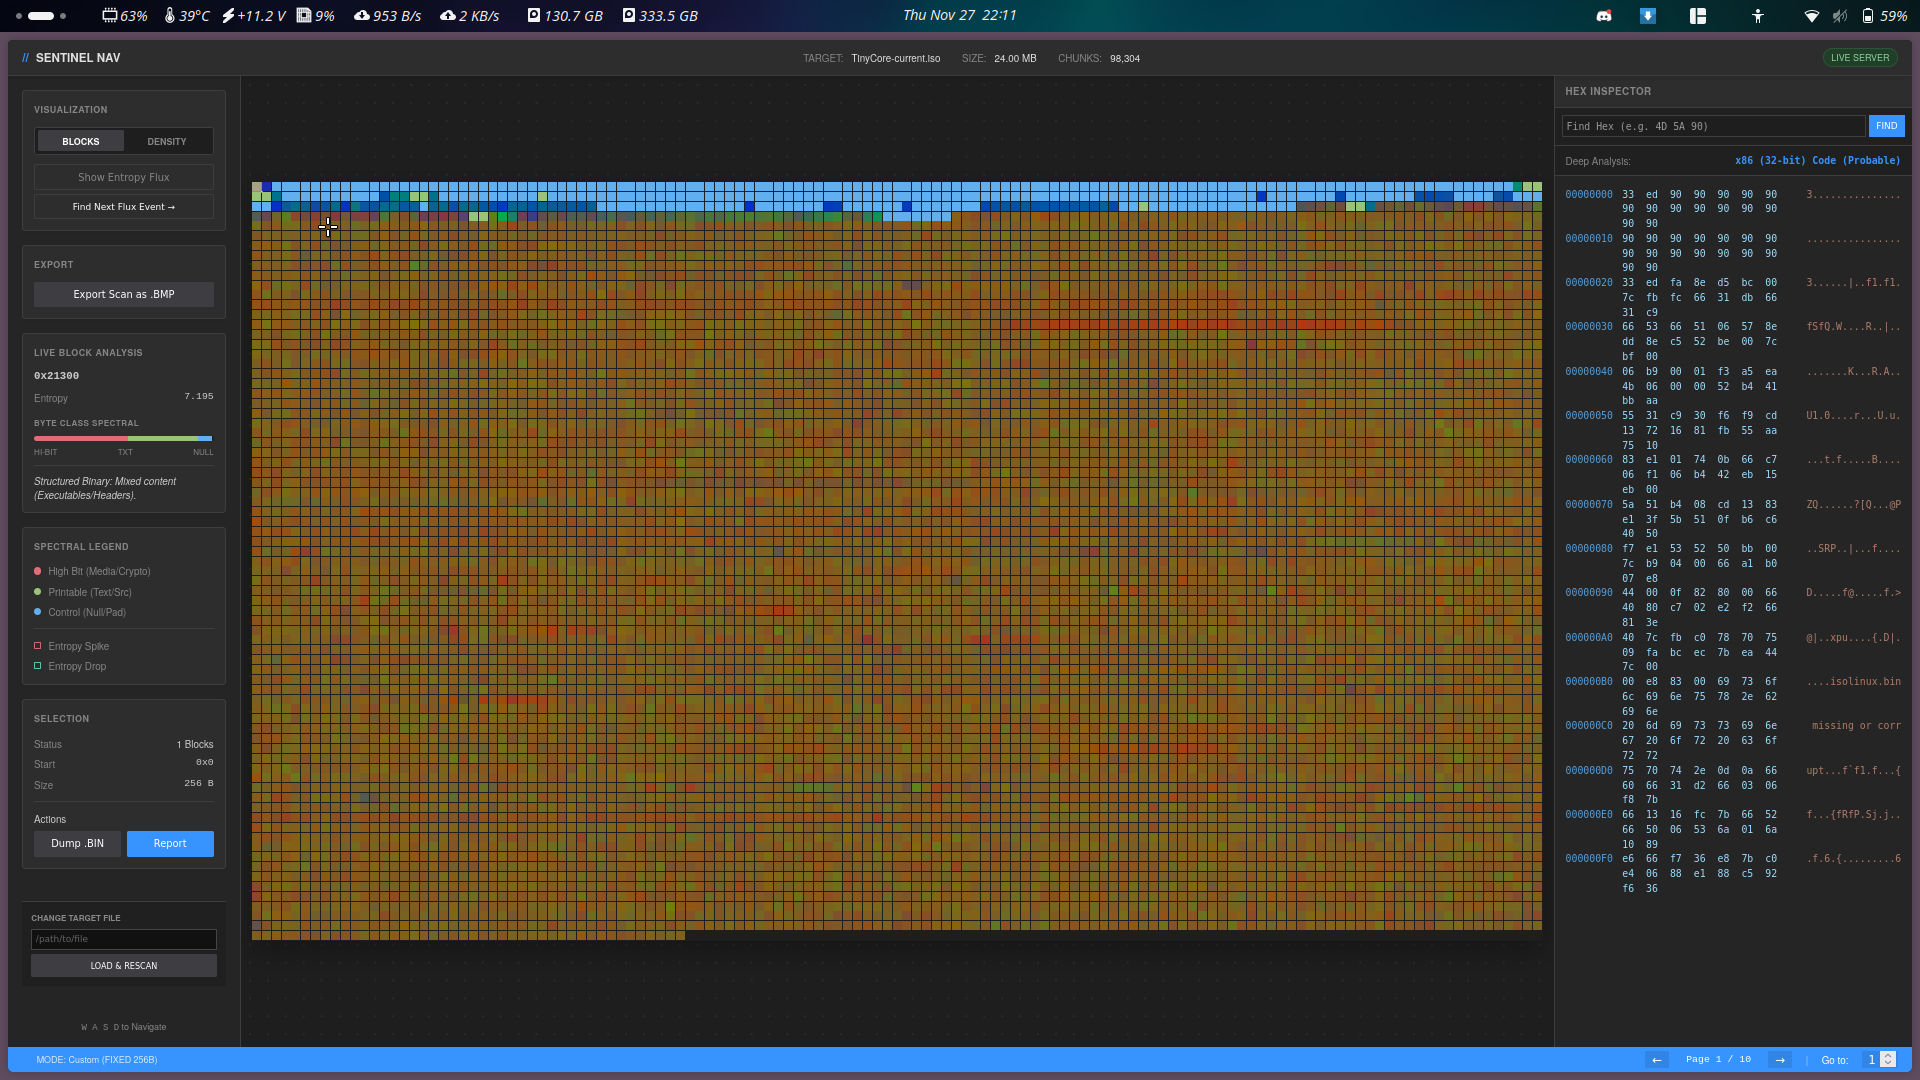 smolfiddle/sentinelnav
SentinelNav: zero-dependency, pure Python binary visualization and forensics tool.
 pan-unit42/dotnetfile
Python library for parsing CLR/PE metadata in .NET assemblies, exposing streams and hash fingerprints to support malware analysis and threat hunting.
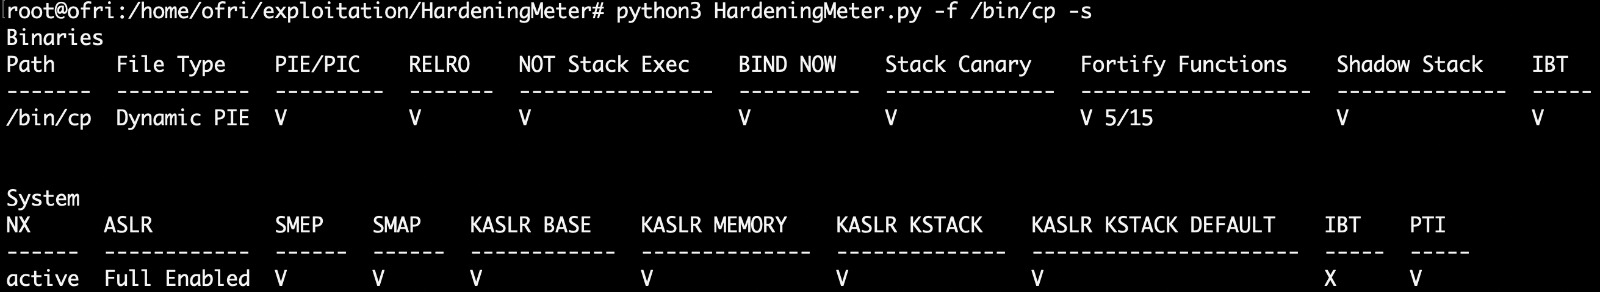 ofriouzan/hardeningmeter
HardeningMeter is an open-source Python tool carefully designed to comprehensively assess the security hardening of binaries and systems.
 pstirparo/machofile
machofile is a module to parse Mach-O binary files
 gmh5225/androiddrivesignity
AndroidDriveSignity is a Python utility designed to bypass driver signature verification in Android kernel(ARMv8.3), facilitating the loading of…
 elastic/die-python
Native Python3 bindings for @horsicq's Detect-It-Easy
 oldboy21/shgenob
Python based tool for generating Shellcode from PIC C
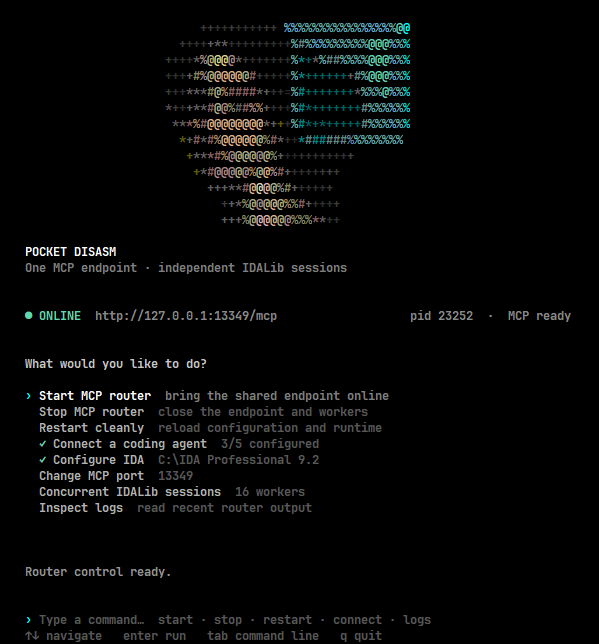 whoisqwerz/pocket_disasm
Multi-session IDALib MCP router for coding agents. Analyze multiple binaries in parallel with IDA-compatible reverse engineering tools.
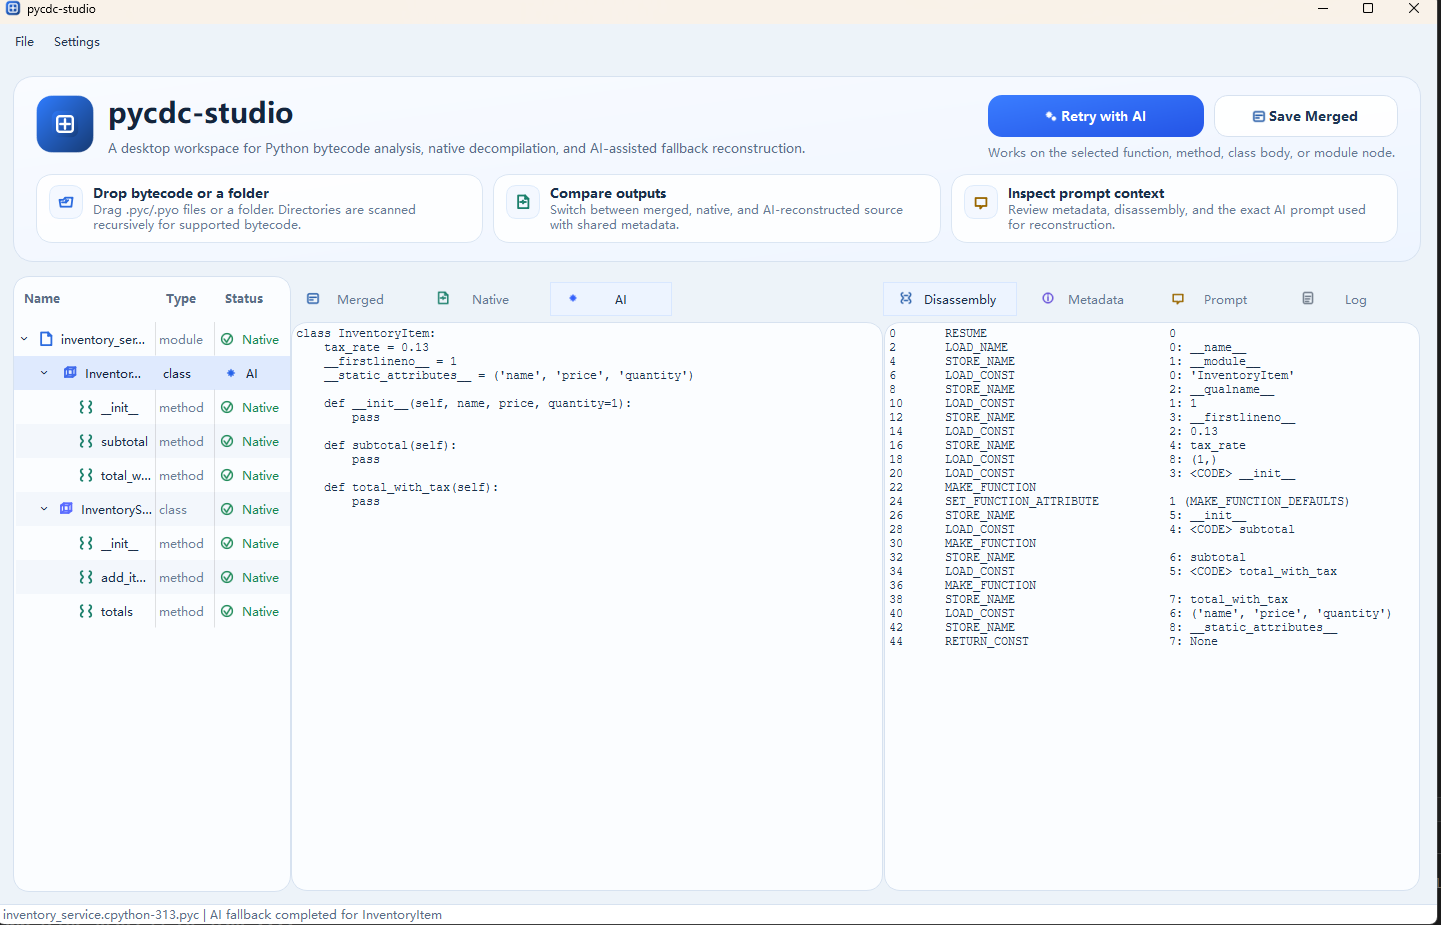 ddouworld/pycdc-studio
A Qt Widgets desktop UI for exploring Python bytecode with pycdc/pycdas, inspecting native decompilation, and using AI fallback for unsupported code…
