

sharem
 bw3ll/sharem
SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…
ai-securitybinary-analysisdebuggers+5
4927 months ago
bw3ll/sharemSHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…
 poppopjmp/vmdragonslayer
Multi-engine framework for unpacking and analyzing VM-protected binaries using dynamic taint tracking, symbolic execution, pattern classification,…
 c3rb3ru5d3d53c/binlex
A Binary Genetic Traits Lexer Framework
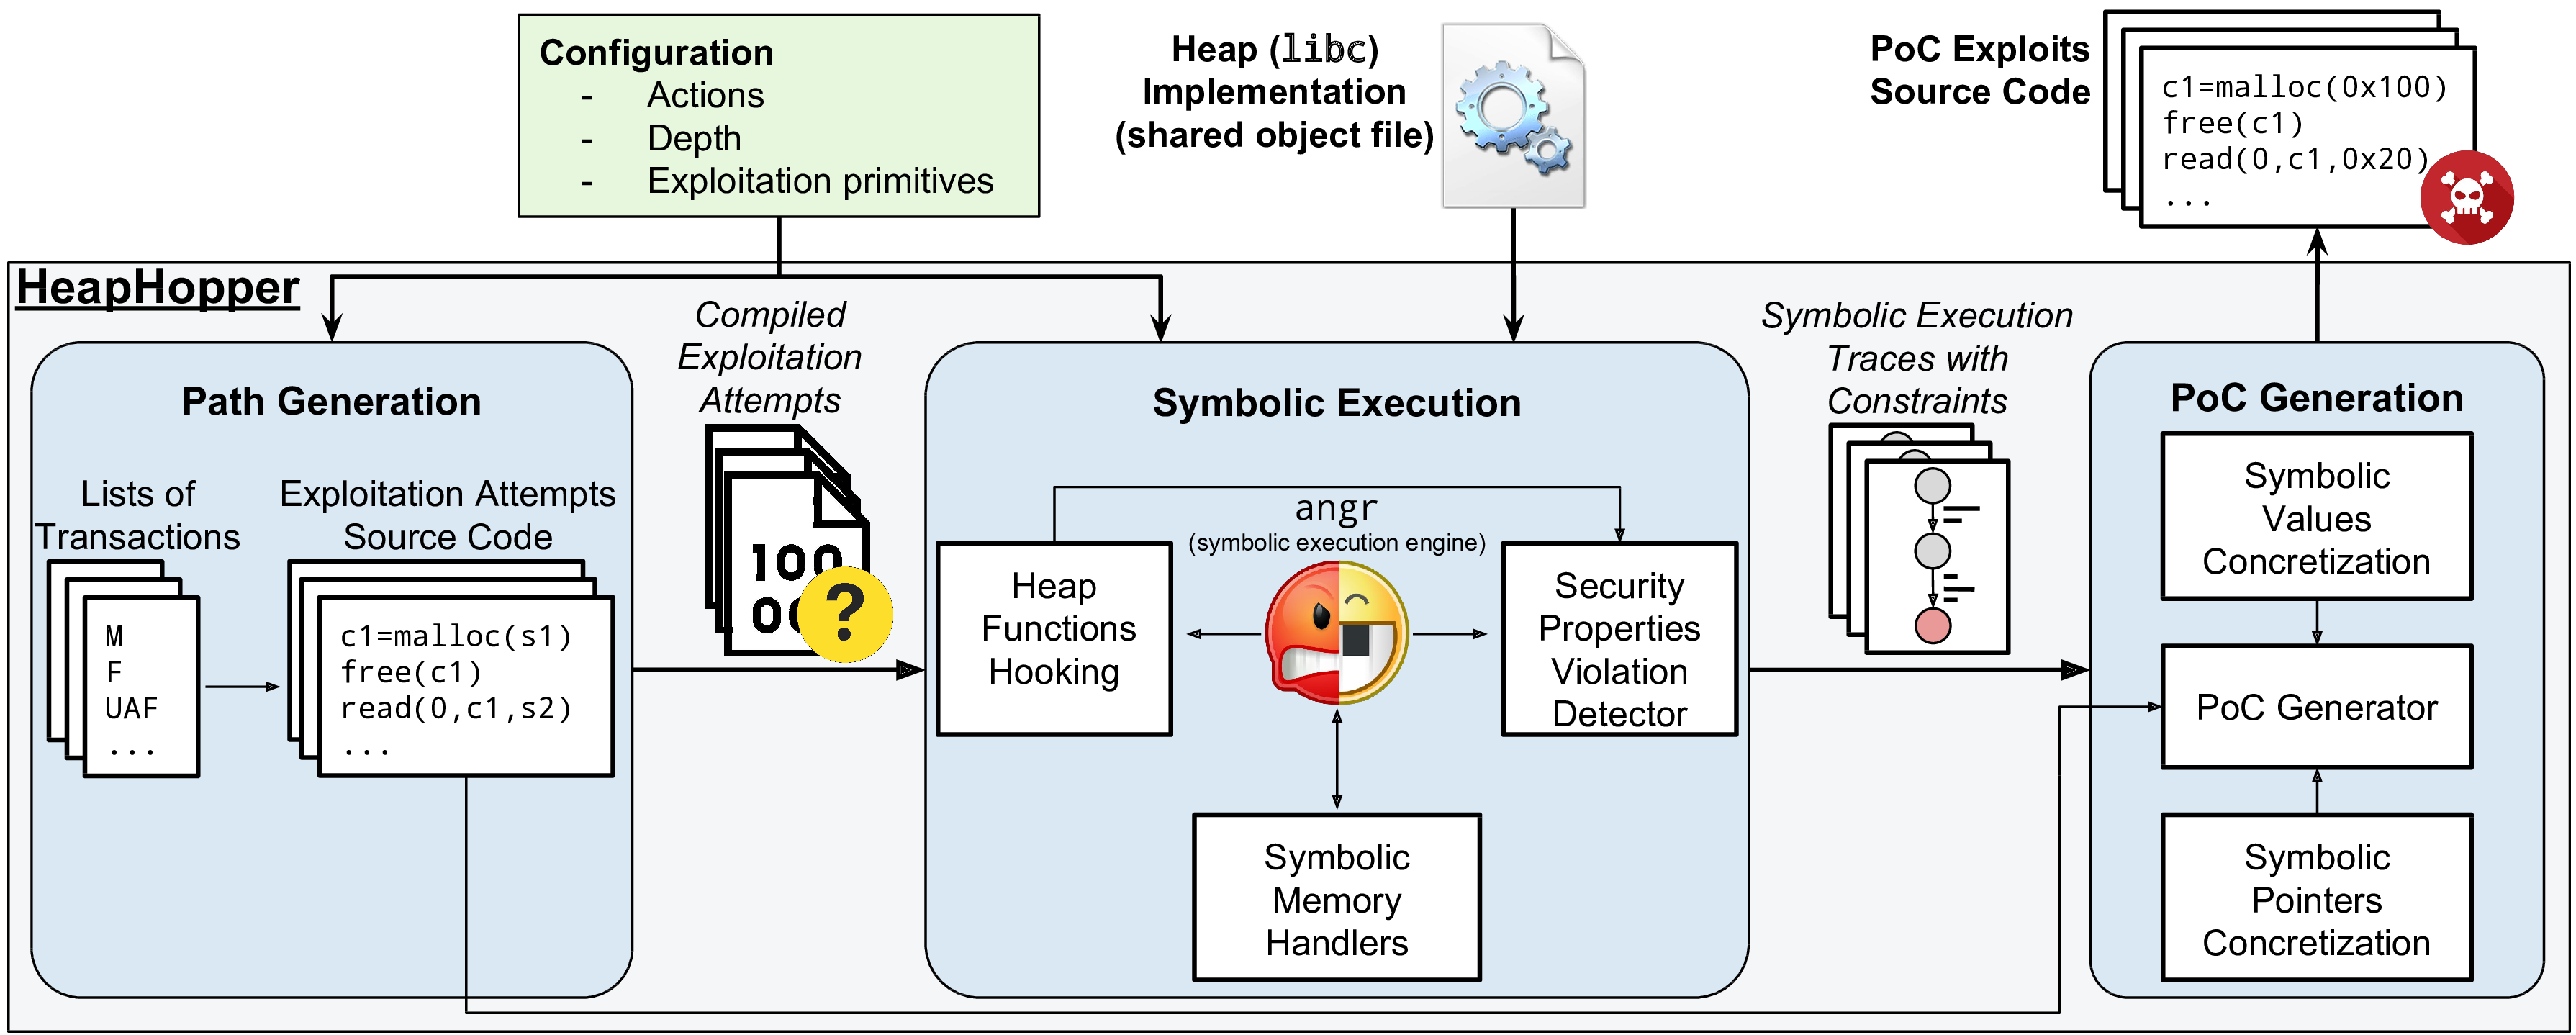 angr/heaphopper
HeapHopper is a bounded model checking framework for Heap-implementations
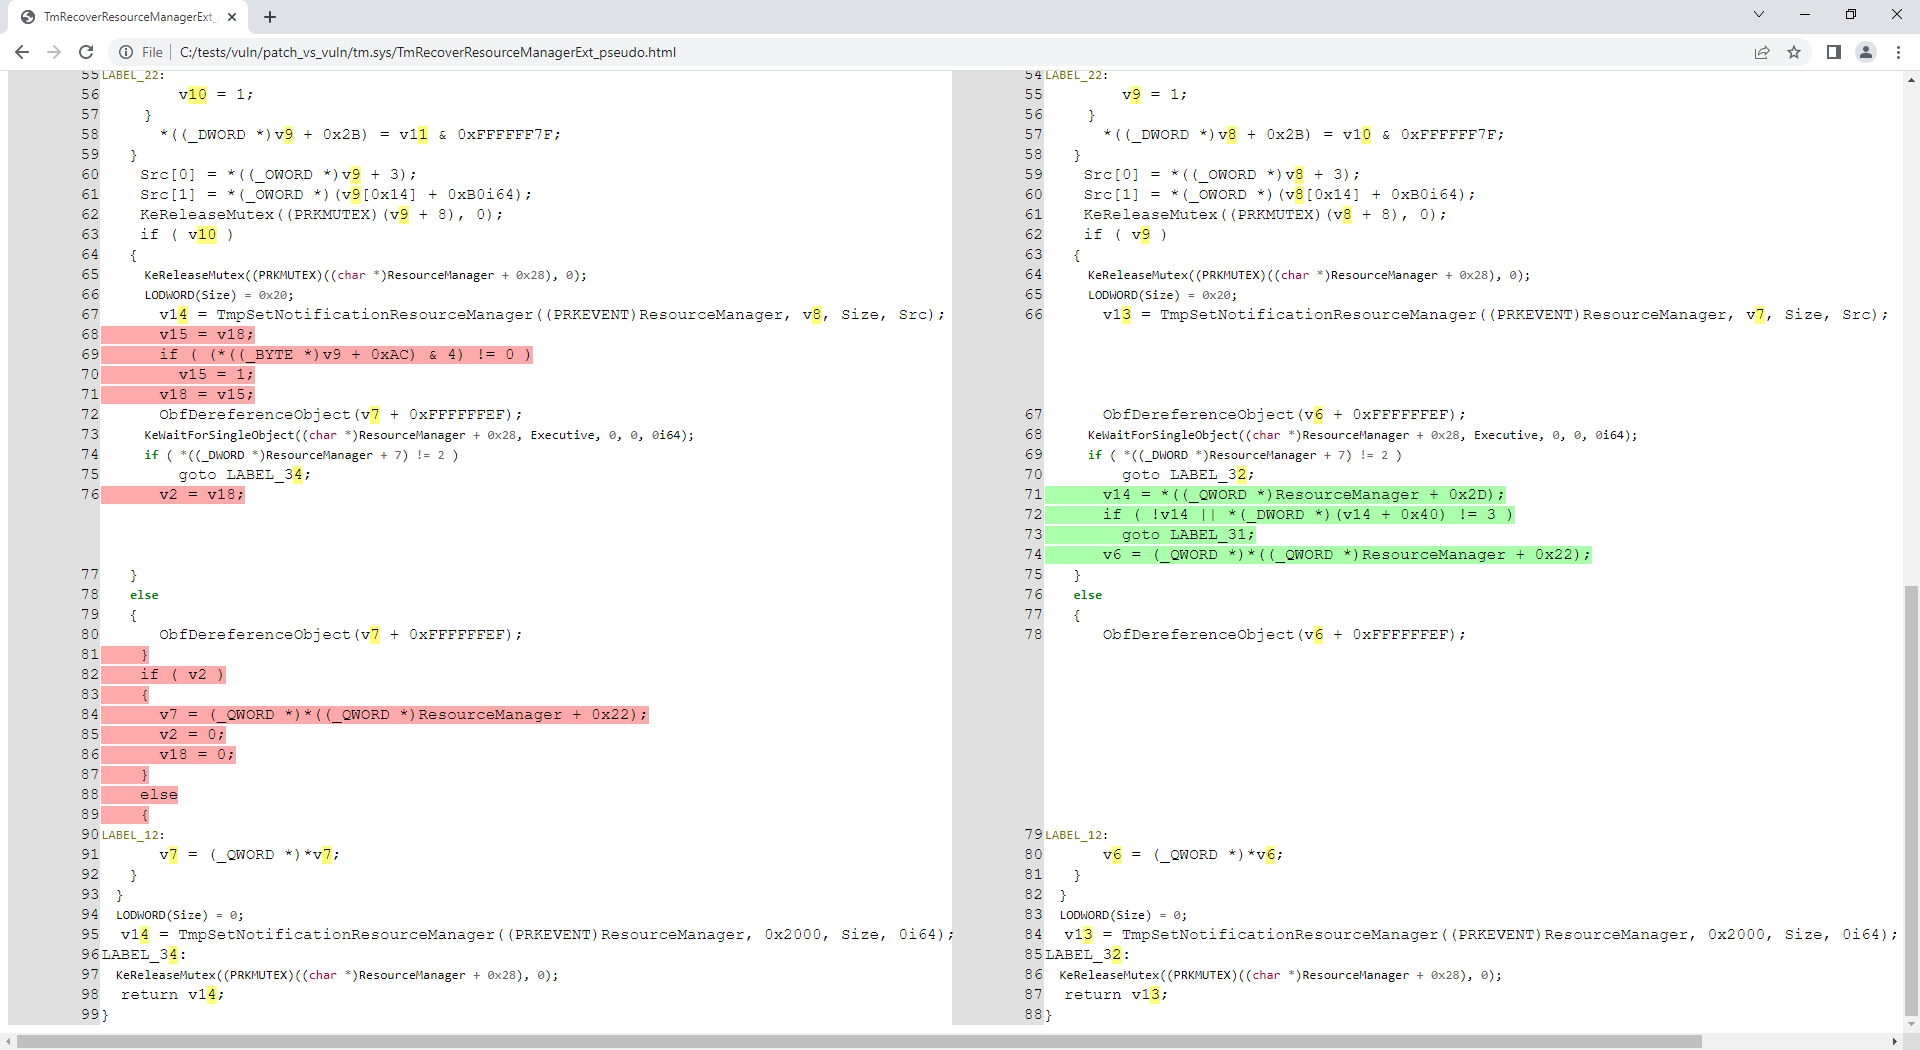 nccgroup/idahunt
idahunt is a framework to analyze binaries with IDA Pro and hunt for things in IDA Pro
 droidefense/engine
Droidefense: Advance Android Malware Analysis Framework
 colton1skees/dna
LLVM based static binary analysis framework
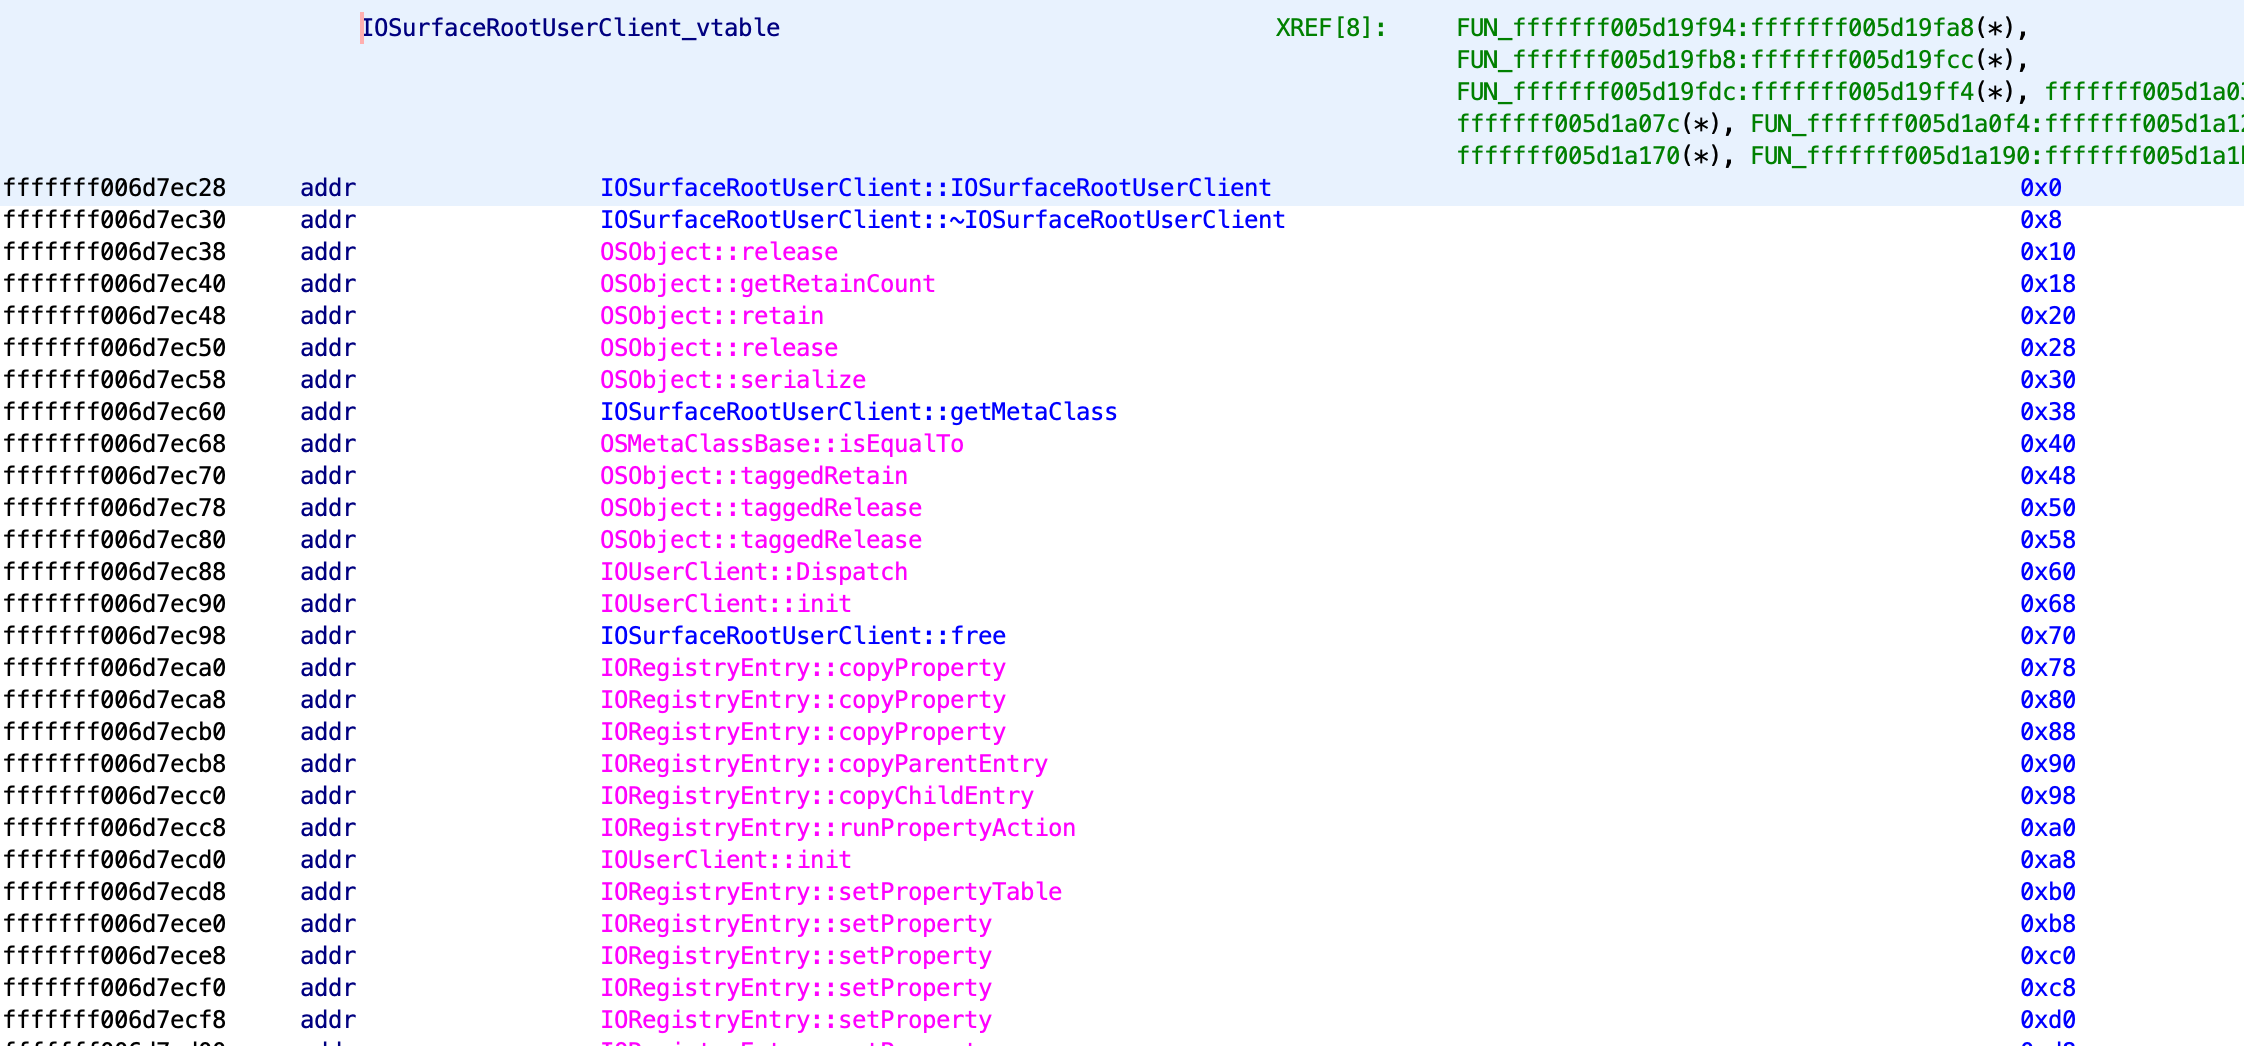 0x36/ghidra_kernelcache
a Ghidra framework for iOS kernelcache reverse engineering
 ablation-tool/ablation
Reverse engineering framework with disassembly, decompilation, taint analysis, version diffing and semantic search, plus LLM-driven autonomous binary…
 arguslab/argus-saf
Scala-based static analysis framework for Android and Java bytecode with flow analysis, decompilation, and native code analysis via symbolic…
 mynameismeerkat/pyretic
pyREtic is an extensible framework for in-memory Python 2.x bytecode reverse engineering
 ropfuscator/ropfuscator
ROPfuscator is a fine-grained code obfuscation framework for C/C++ programs using ROP (return-oriented programming).
 fuzzuf/fuzzuf
Modular fuzzing framework with a DSL (HierarFlow) to compose fuzzing loops from reusable primitives. Supports AFL, libFuzzer, VUzzer, and more for…
 plum-umd/redexer
The Redexer binary instrumentation framework for Dalvik bytecode
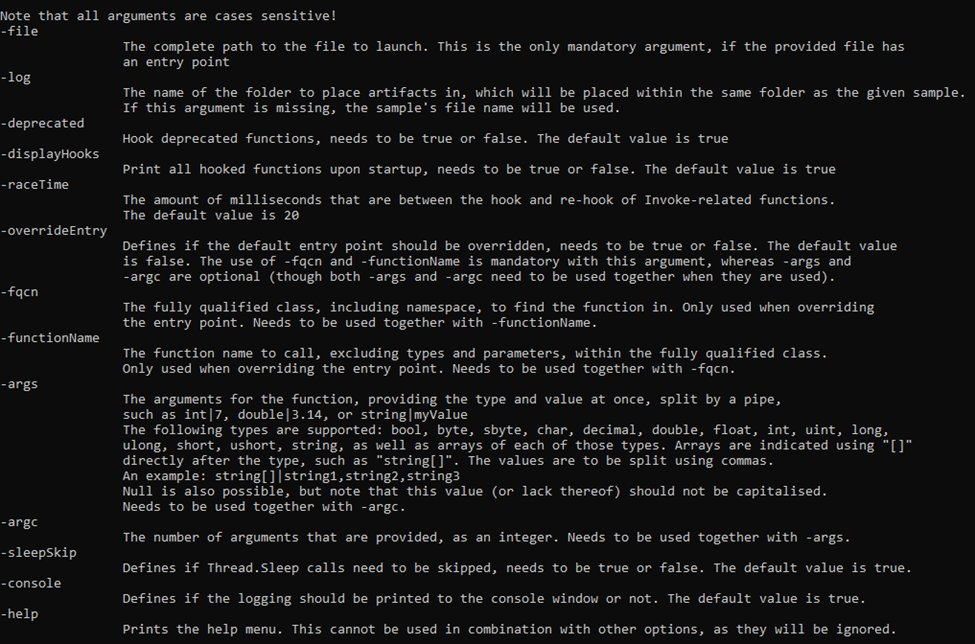 advanced-threat-research/dotdumper
An automatic unpacker and logger for DotNet Framework targeting files
 cmu-sei/kaiju
CERT Kaiju is a binary analysis framework extension for the Ghidra software reverse engineering suite. This repository is a "mirror" -- please file…
 project-artist/artist
Open-source instrumentation framework for Android apps and Java middleware, modifying code during on-device compilation via the ART compiler.…
 ohjeongwook/shellcodeemulator
Shellcode emulator written with Unicorn Framework With Process Dump Emulation Environment