

capa
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
ai-assisted-reversingbinary-analysiscode-analysis+10
6.1k
mandiant/capaRule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
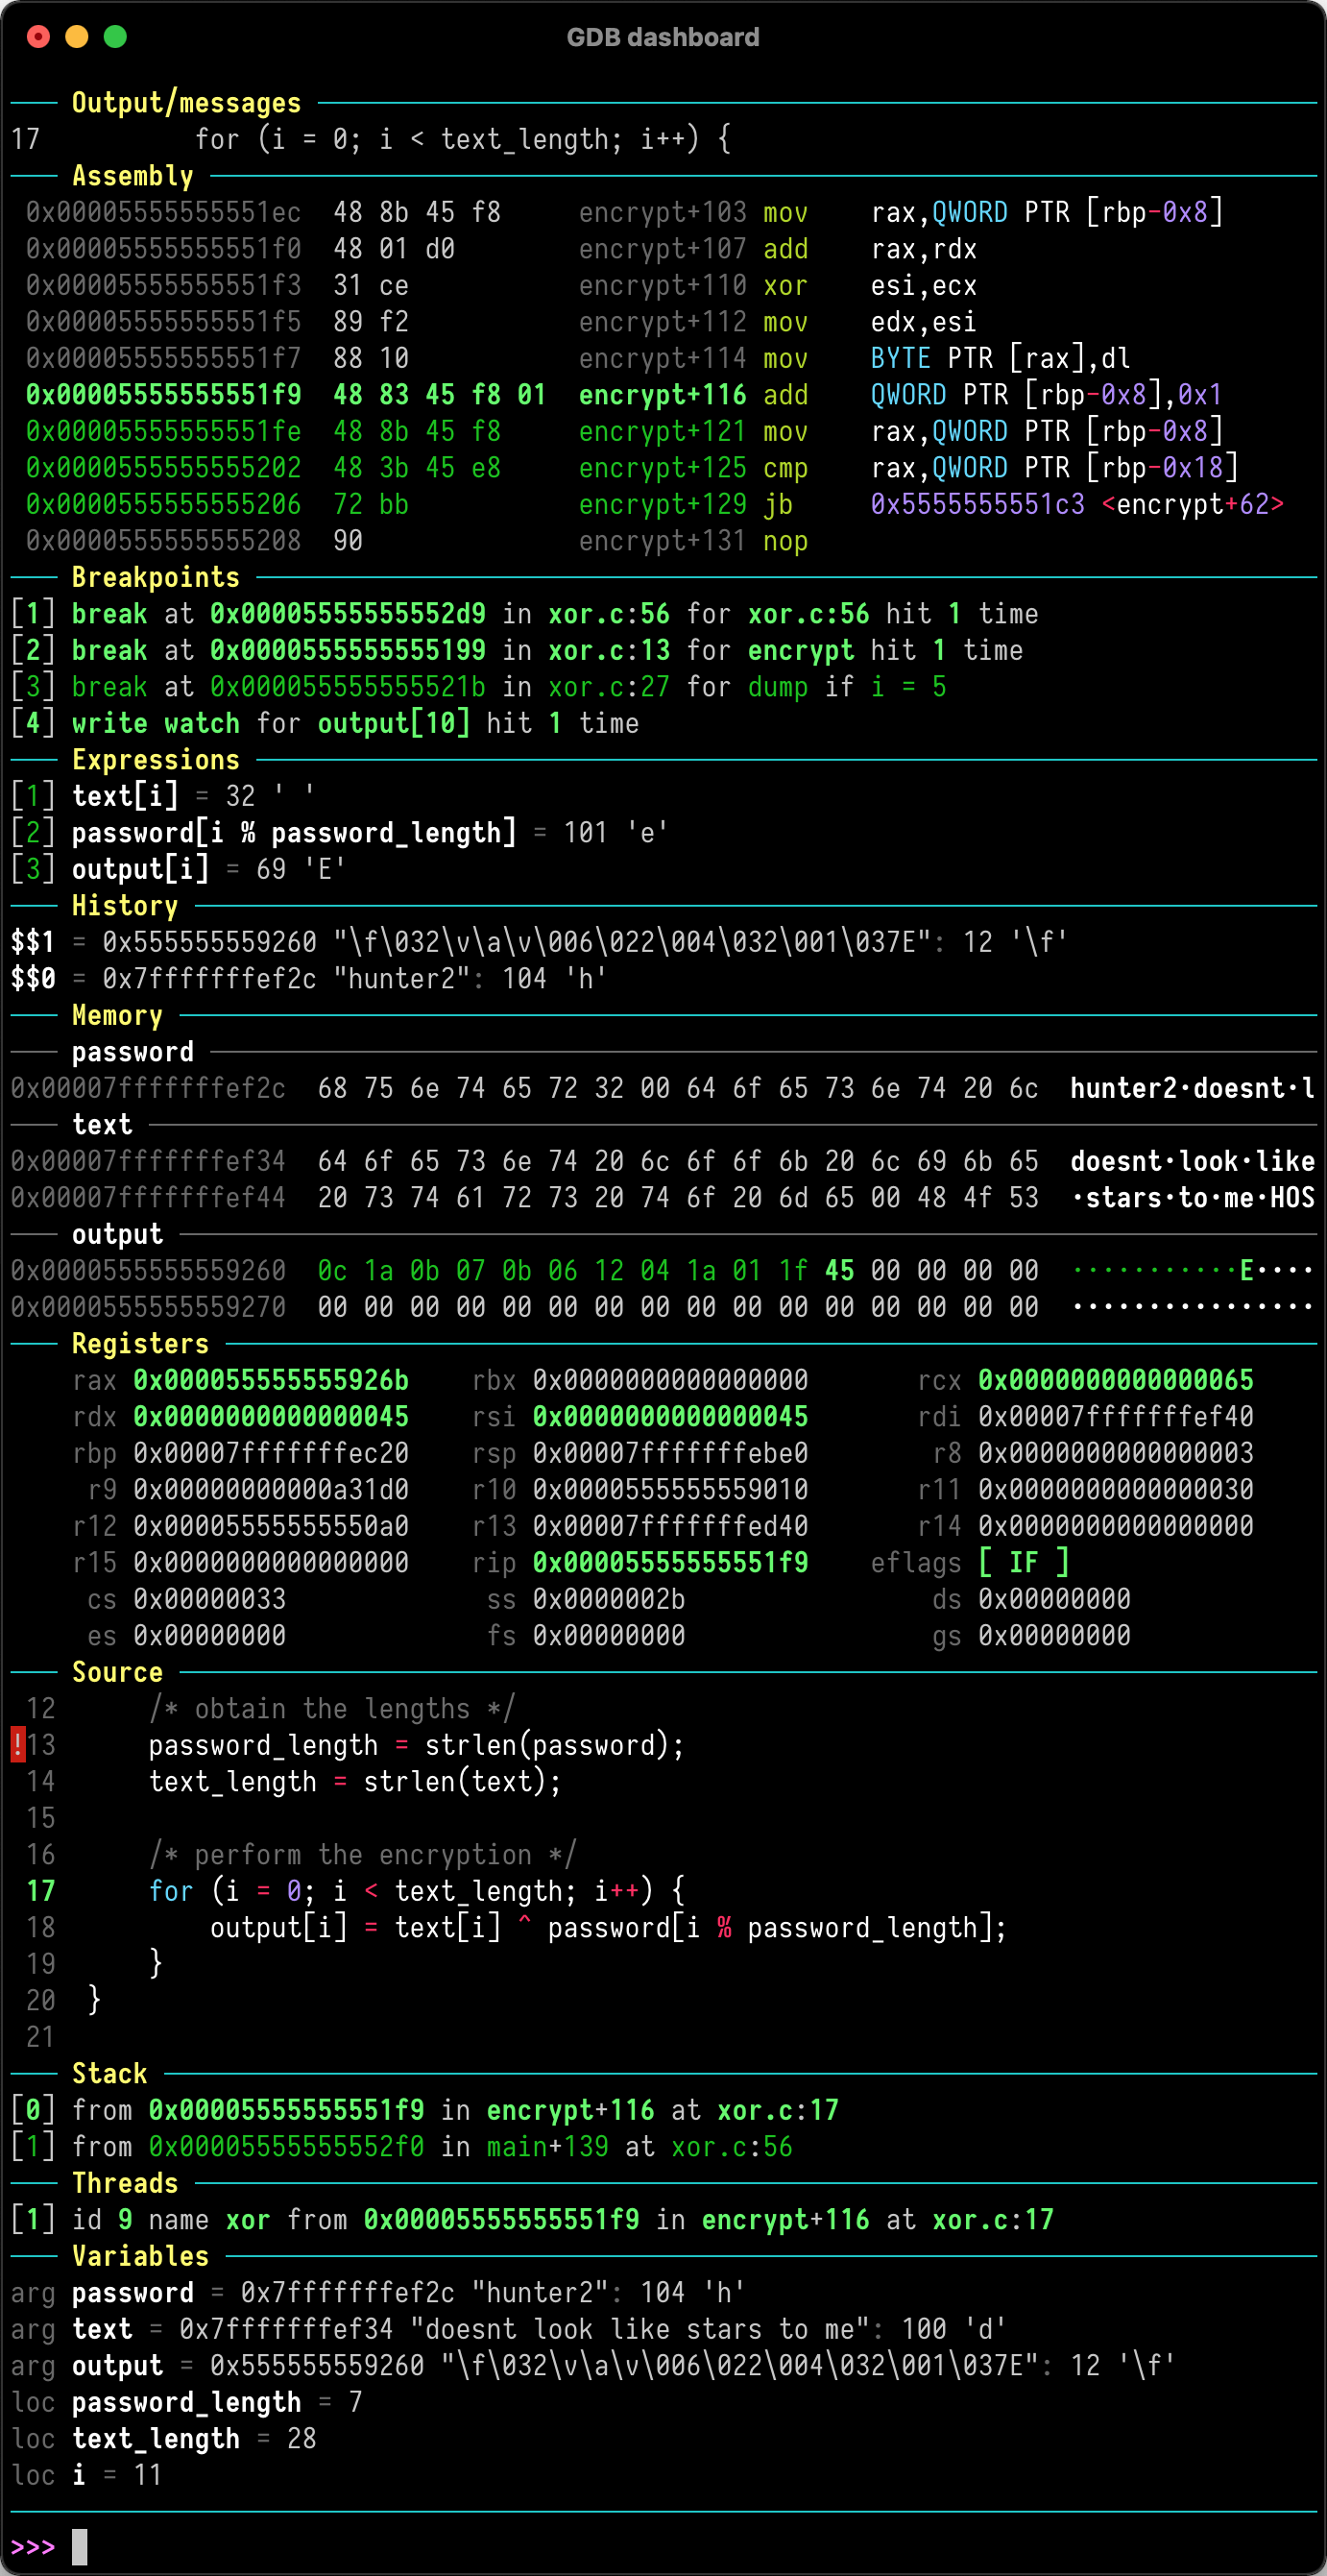 cyrus-and/gdb-dashboard
Modular GDB interface providing a visual dashboard with customizable panels for inspecting registers, source code, assembly, and program state during…
 dynamorio/dynamorio
Runtime instrumentation framework for building dynamic analysis tools: tracing, profiling, code coverage, memory debugging, fuzzing, and disassembly…
 joernio/joern
Open-source code analysis platform for C/C++/Java/Binary/Javascript/Python/Kotlin based on code property graphs. Discord https://discord.gg/vv4MH284Hc
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
 aflplusplus/libafl
Advanced Fuzzing Library - Slot your Fuzzer together in Rust! Scales across cores and machines. For Windows, Android, MacOS, Linux, no_std, ...
 0xz0f/z0fcourse_reverseengineering
Structured reverse engineering course covering x64 Windows binaries, assembly, debugging, and malware analysis. Designed for beginners to…
 revng/revng
Open source binary analysis framework and decompiler built on LLVM and QEMU, lifting binaries to a readable intermediate representation for reverse…
 snare/voltron
Extensible debugger UI toolkit providing customizable register, disassembly, stack, memory, breakpoint, and backtrace views for LLDB, GDB, VDB, and…
 dman95/sasm
SASM - simple crossplatform IDE for NASM, MASM, GAS and FASM assembly languages
 mandiant/speakeasy
Windows malware emulation framework that executes binaries, drivers, and shellcode in a modeled runtime, emulating APIs, process/thread behavior,…
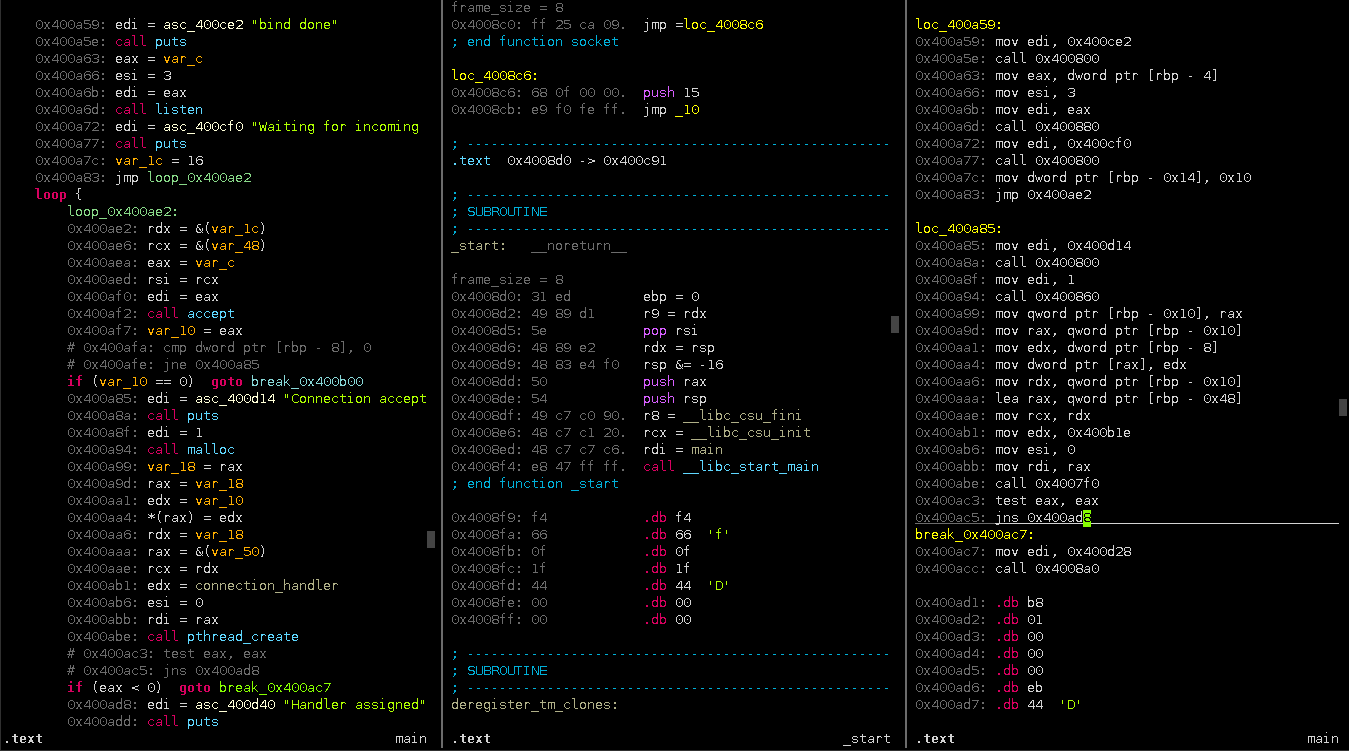 plasma-disassembler/plasma
Plasma is an interactive disassembler for x86/ARM/MIPS. It can generates indented pseudo-code with colored syntax.
 amlweems/xzbot
notes, honeypot, and exploit demo for the xz backdoor (CVE-2024-3094)
 glmcdona/process-dump
Windows tool for dumping malware PE files from memory back to disk for analysis.
 kjcracks/clutch
Jailbreak-only iOS utility that decrypts installed app executables and dumps them as .ipa or raw binary files for security research and…
 vmoranv/jshookmcp
A search-first, profile-aware reverse-engineering workspace for AI agents — 735 tools across 36 domains in one MCP server.
 mrexodia/titanhide
Windows kernel driver that hooks Nt* SSDT functions to hide debuggers and processes from anti-debug checks, with an x64dbg plugin for stealth…
 googleprojectzero/jackalope
Binary, coverage-guided fuzzer for Windows, macOS, Linux and Android