
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
1171 results
PortEx preview

PortEx

GitHubstruppigel/portex

Java library to analyse Portable Executable files with a special focus on malware analysis and PE malformation robustness
anomaly-detectionbinary-analysisforensics+3
5385 months ago
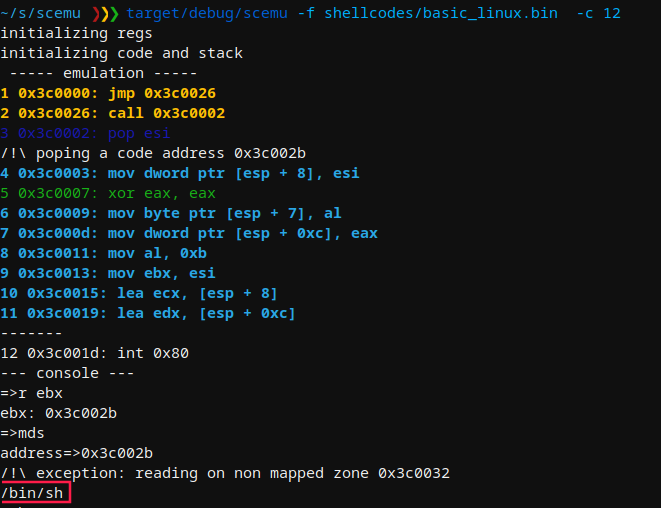
mwemu preview

mwemu

GitHubmwemuorg/mwemu

Pure Rust x86 hardware emulator and Windows process simulator for malware analysis, shellcode emulation, and payload unpacking. Supports 32/64-bit PE…
binary-analysisexploit-frameworksmalware-analysis+2
31515h 27m ago
View8 preview

View8

GitHubsuleram/view8

Decompiles serialized V8 bytecode (JSC files) into high-level readable JavaScript-like code, with support for multiple V8 versions, tree output, and…
binary-analysismalware-analysisreverse-engineering+2
3771 month ago
ghost preview

ghost

GitHubpandaadir05/ghost

Detects process injection and memory manipulation used by malware. Finds RWX regions, shellcode patterns, API hooks, thread hijacking, and process…

binary-analysisdefensive-toolsforensics+6
3911 month ago
how_to_become_a_malware_analyst preview

how_to_become_a_malware_analyst

GitHubpinksawtooth/how_to_become_a_malware_analyst

Curated guide to becoming a malware analyst, covering essential knowledge, reverse engineering, analysis tools, and LLM-assisted learning with…
binary-analysisctfcurated-resources+7
28218 days ago
inhale preview

inhale

GitHubnetspooky/inhale

A malware analysis and classification tool.
binary-analysisforensicshash-analysis+3
1915 years ago
DrSemu preview

DrSemu

GitHubsecrary/drsemu

DrSemu - Sandboxed Malware Detection and Classification Tool Based on Dynamic Behavior

binary-analysisdynamic-analysis-sandboxingmalware-analysis+1
2806 years ago
CrimsonEDR preview

CrimsonEDR

GitHubhelixo32/crimsonedr

Simulate the behavior of AV/EDR for malware development training.
binary-analysisdefensive-toolsdynamic-analysis-sandboxing+3
5662 years ago
Reversecore_MCP preview

Reversecore_MCP

GitHubsjkim1127/reversecore_mcp

A security-first MCP server that empowers AI agents to perform automated reverse engineering, malware analysis, forensics, vulnerability research,…
binary-analysisdigital-forensicsdynamic-analysis-sandboxing+7
2057 days ago
cosa-nostra preview

cosa-nostra

GitHubjoxeankoret/cosa-nostra

Cosa Nostra, a FOSS graph based malware clusterization toolkit.

binary-analysiseducationforensics+3
2312 years ago
malduck preview

malduck

GitHubcert-polska/malduck

🦆 Malduck is your ducky companion in malware analysis journeys
binary-analysiscryptographydynamic-analysis-sandboxing+3
3581 year ago
apk-info preview

apk-info

GitHubdelvinru/apk-info

APK full-featured parser

android-securitybinary-analysisforensics+3
13914 days ago
FileInsight-plugins preview

FileInsight-plugins

GitHubnmantani/fileinsight-plugins

FileInsight-plugins: decoding toolbox of McAfee FileInsight hex editor for malware analysis
binary-analysiscode-analysiscryptography+7
1641 year ago
NixImports preview

NixImports

GitHubdr4k0nia/niximports

A .NET malware loader, using API-Hashing to evade static analysis
binary-analysismalware-analysispayload-development
2083 years ago
recomposer preview

recomposer

GitHubsecretsquirrel/recomposer

Randomly changes Win32/64 PE Files for 'safer' uploading to malware and sandbox sites.

anti-botbinary-analysisids-ips-evasion+2
13212 years ago
PsyloDbg preview

PsyloDbg

GitHubdarkcodersc/psylodbg

User-friendly Microsoft Windows Debugger for Malware Analysts.
binary-analysisdebuggersmalware-analysis+1
2093 years ago
hedgehog-tools preview

hedgehog-tools

GitHubstruppigel/hedgehog-tools

Collection of scripts for malware analysis, deobfuscation, and configuration extraction. Supports static analysis, unpacking, shellcode conversion,…
binary-analysisdynamic-analysis-sandboxingforensics+4
1443 months ago
pftriage preview

pftriage

GitHubidiom/pftriage

Python tool and library to help analyze files during malware triage and analysis.

binary-analysisdigital-forensicsdynamic-analysis-sandboxing+4
796 years ago
Previous1234…66Next