
Andromeda
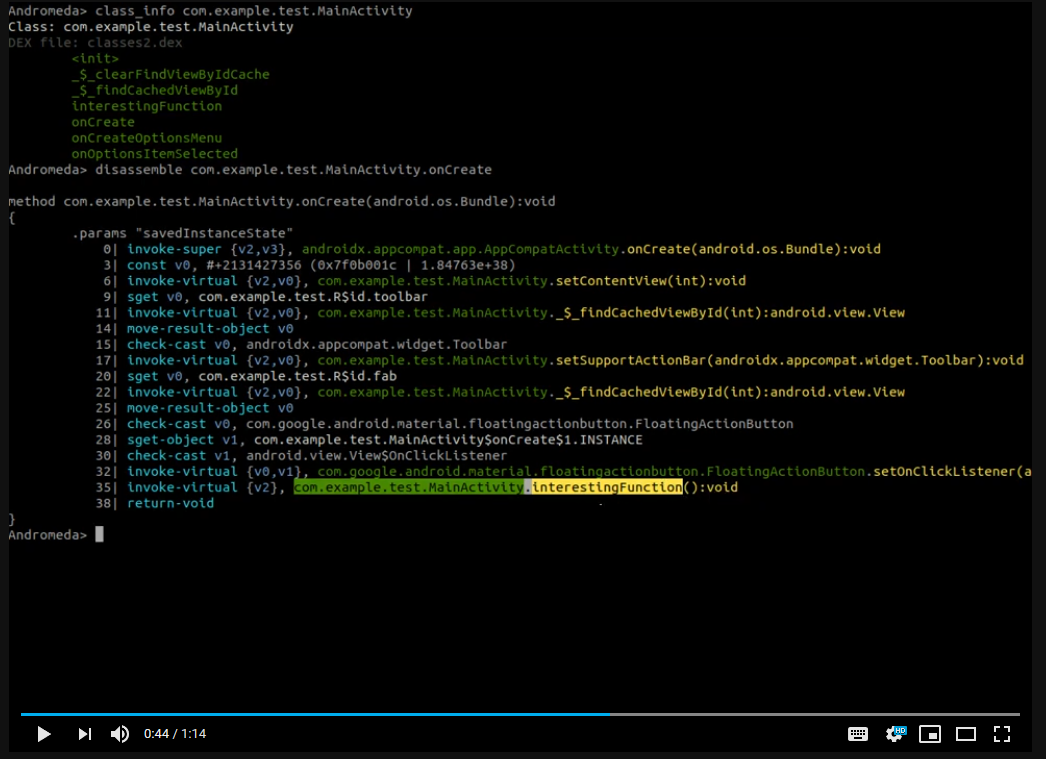
 secrary/andromeda
C/C++ interactive reverse engineering tool for Android applications, enabling fast static analysis and binary inspection of APK files.
android-securitybinary-analysisreverse-engineering+1
714
secrary/andromedaC/C++ interactive reverse engineering tool for Android applications, enabling fast static analysis and binary inspection of APK files.
 foundryzero/binder-trace
Binder Trace is a tool for intercepting and parsing Android Binder messages. Think of it as "Wireshark for Binder".
 ejfkdev/ddc
Android DEX → Java decompiler in Rust, built for speed — full apps in seconds, queries in milliseconds. Progressive analysis, javac-verified output,…
 fuzzysecurity/fermion
Fermion, an electron wrapper for Frida & Monaco.
 arguslab/argus-saf
Scala-based static analysis framework for Android and Java bytecode with flow analysis, decompilation, and native code analysis via symbolic…
 jakev/pyxamstore
Python utility for parsing Xamarin AssemblyStore blob files
 plum-umd/redexer
The Redexer binary instrumentation framework for Dalvik bytecode
 project-artist/artist
Open-source instrumentation framework for Android apps and Java middleware, modifying code during on-device compilation via the ART compiler.…
 user1342/obfu-de-scate
Fuzzy comparison tool for deobfuscating Android APKs by identifying renamed functions across versions, generating mapping files and interactive HTML…
 michalbednarski/reparcelbug2
Writeup and exploit for installed app to system privilege escalation on Android 12 Beta through CVE-2021-0928, a `writeToParcel`/`createFromParcel`…
 dzmitry-savitski/android-pentest-tool
Android penetration testing tool for Kali linux
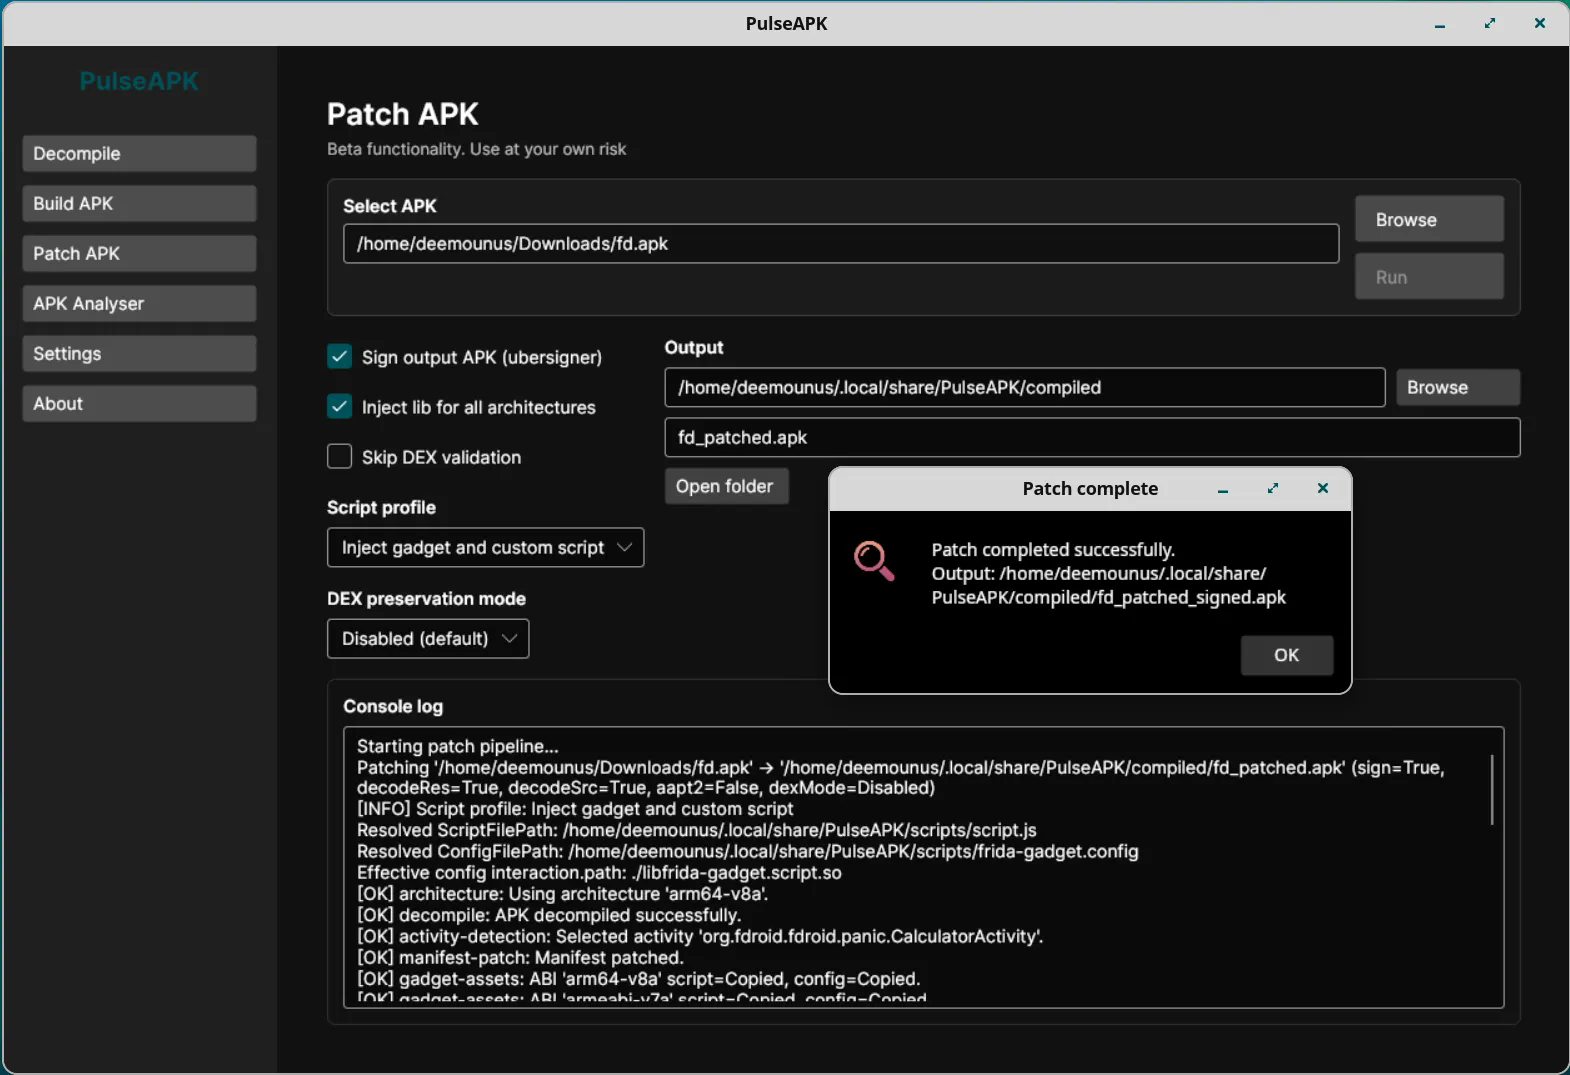 deemoun/pulseapk-core
PulseAPK Core: Cross-Platform tool for working with APK files: Decompilation, Analysis, Building
 michalbednarski/thelastbundlemismatch
Writeup and exploit for CVE-2023-45777, bypass for Intent validation inside AccountManagerService on Android 13 despite "Lazy Bundle" mitigation
 federicodotta/ghidra2frida
Ghidra extension bridging static and dynamic analysis via Frida, enabling scriptable runtime instrumentation for reverse engineering binaries on…
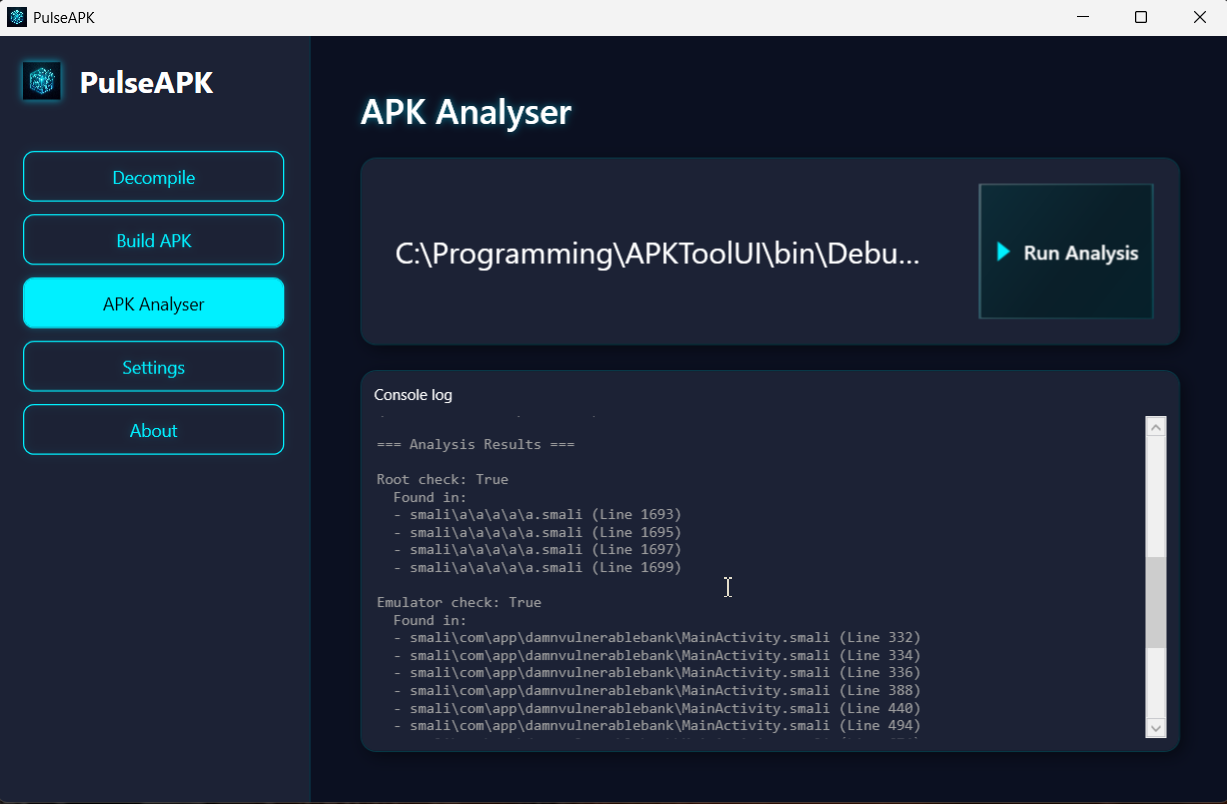 deemoun/pulseapk
PulseAPK is a WPF frontend for apktool and uber-signer with drag-and-drop support, live decompilation output, smali analysis, and integrated APK…
 metaredteam/rtx-cve-2023-45779
Proof-of-concept code for Android APEX key reuse vulnerability
 lyravoid/kernelpatch
Patches and hooks the Linux kernel using only a stripped kernel image, extracting symbols and injecting code for inline and syscall hooking on arm64.