
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
106 results
barf-project preview

barf-project

GitHubprograma-stic/barf-project

BARF : A multiplatform open source Binary Analysis and Reverse engineering Framework
binary-analysisdynamic-analysis-sandboxingeducation+5
1.5k
6 years ago
paimei preview

paimei

GitHubopenrce/paimei

A reverse engineering framework written in Python.
binary-analysiscode-analysisdebuggers+6
50814 years ago
pydbg preview

pydbg

GitHubopenrce/pydbg

A pure-python win32 debugger interface.

binary-analysisdebuggersexploitation+2
46114 years ago
idacode preview

idacode

GitHubioncodes/idacode

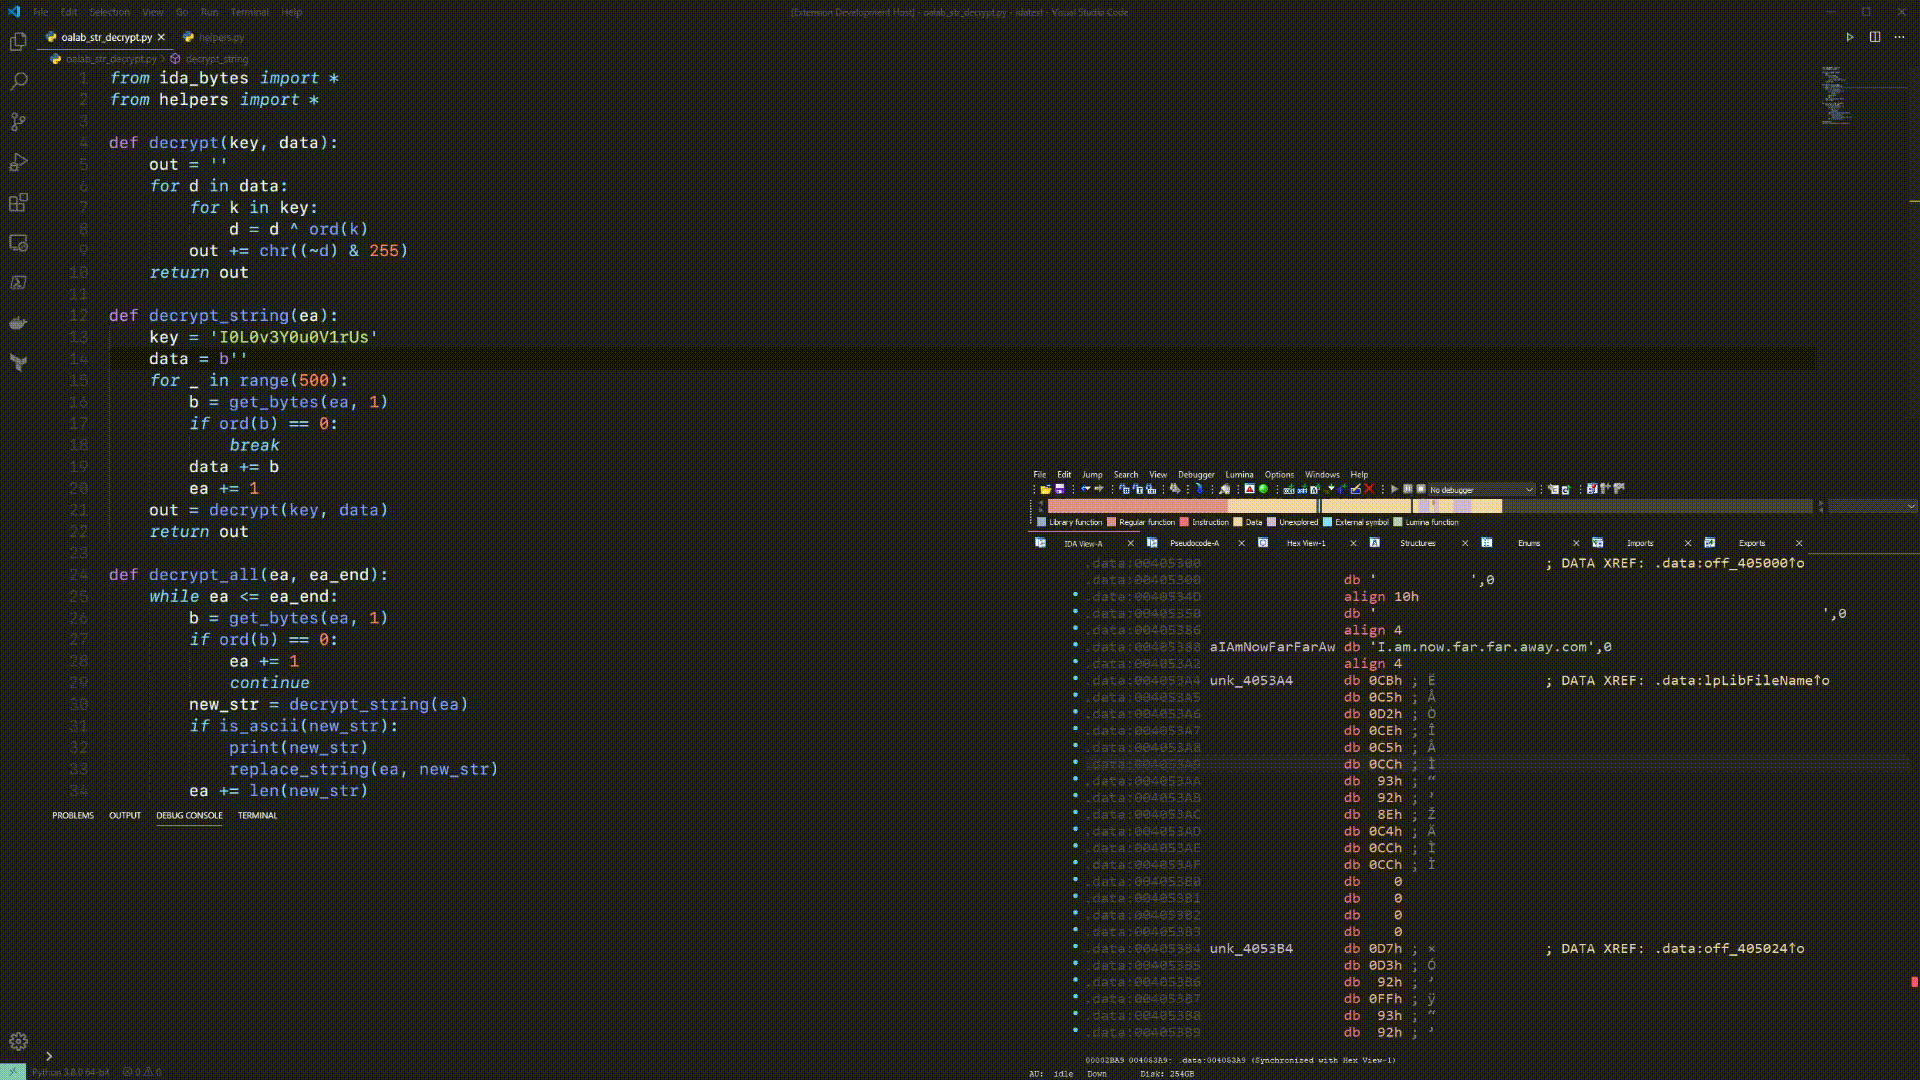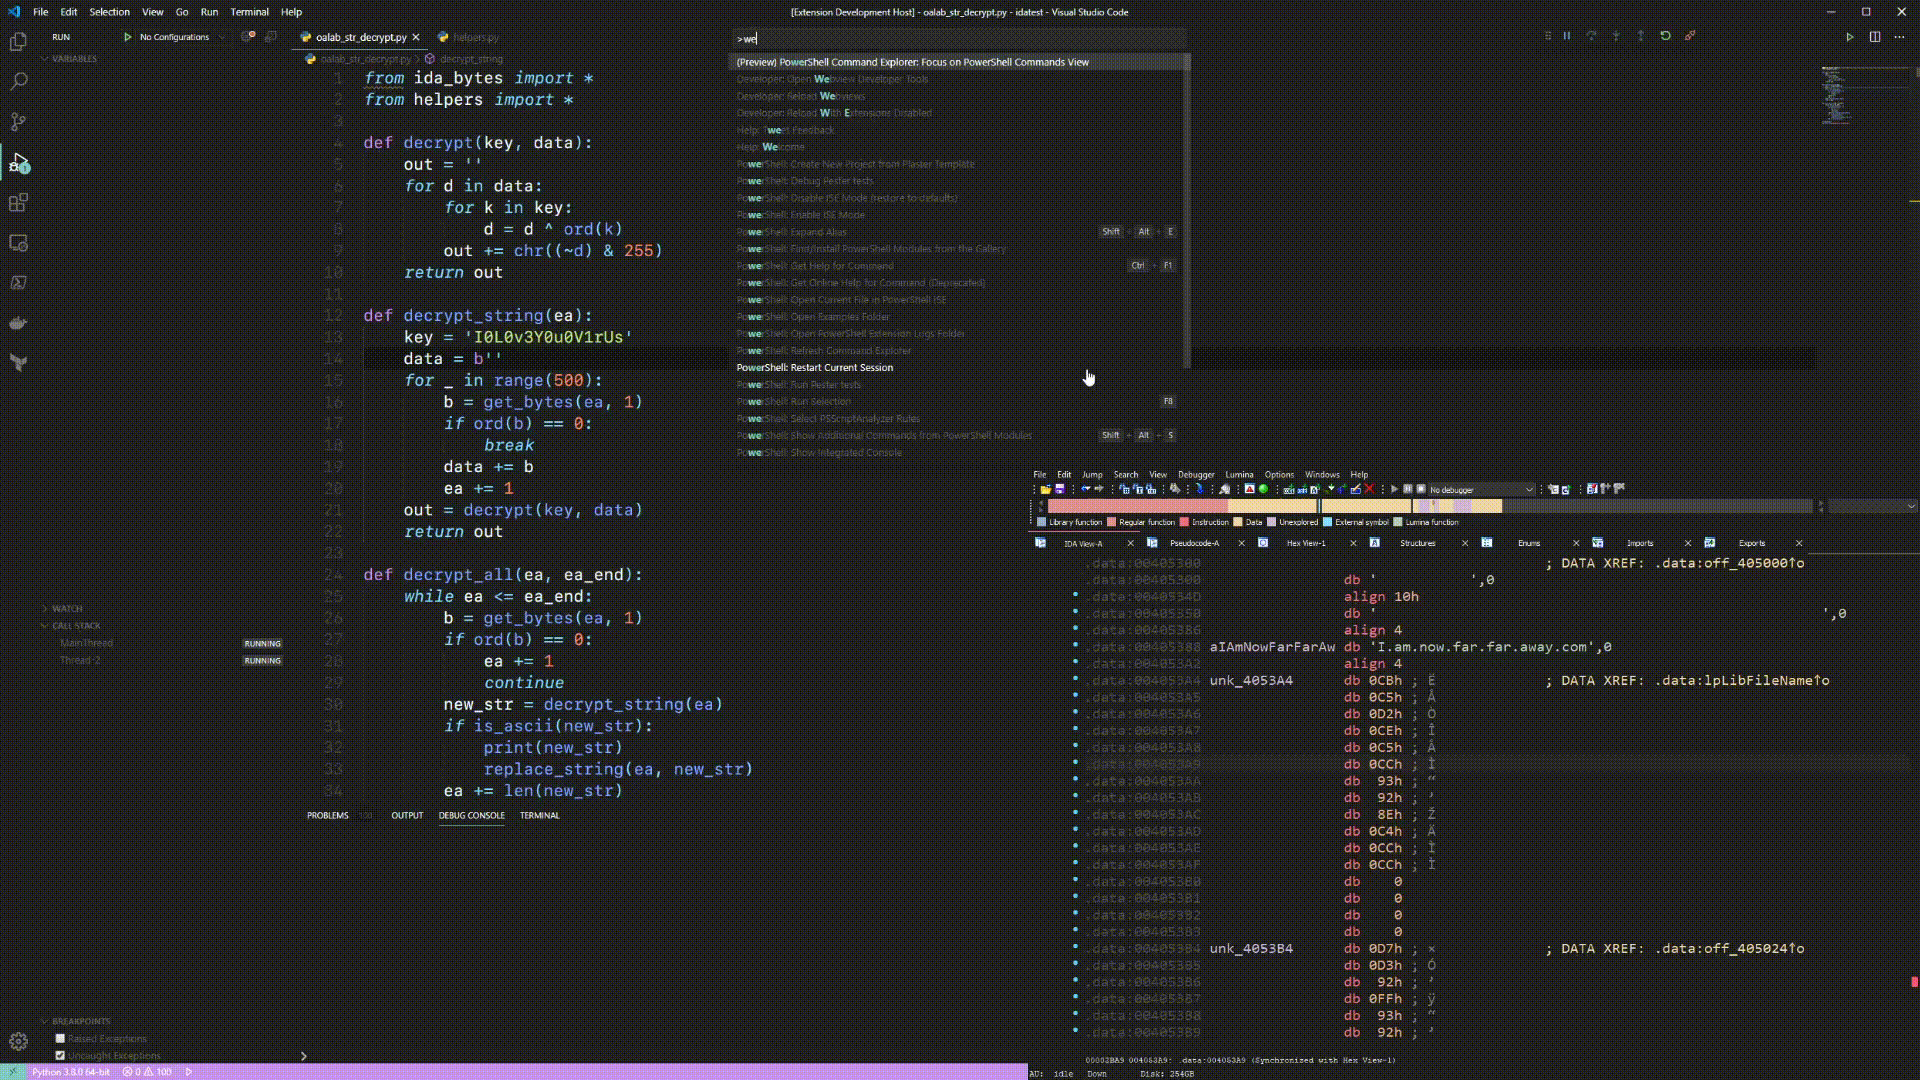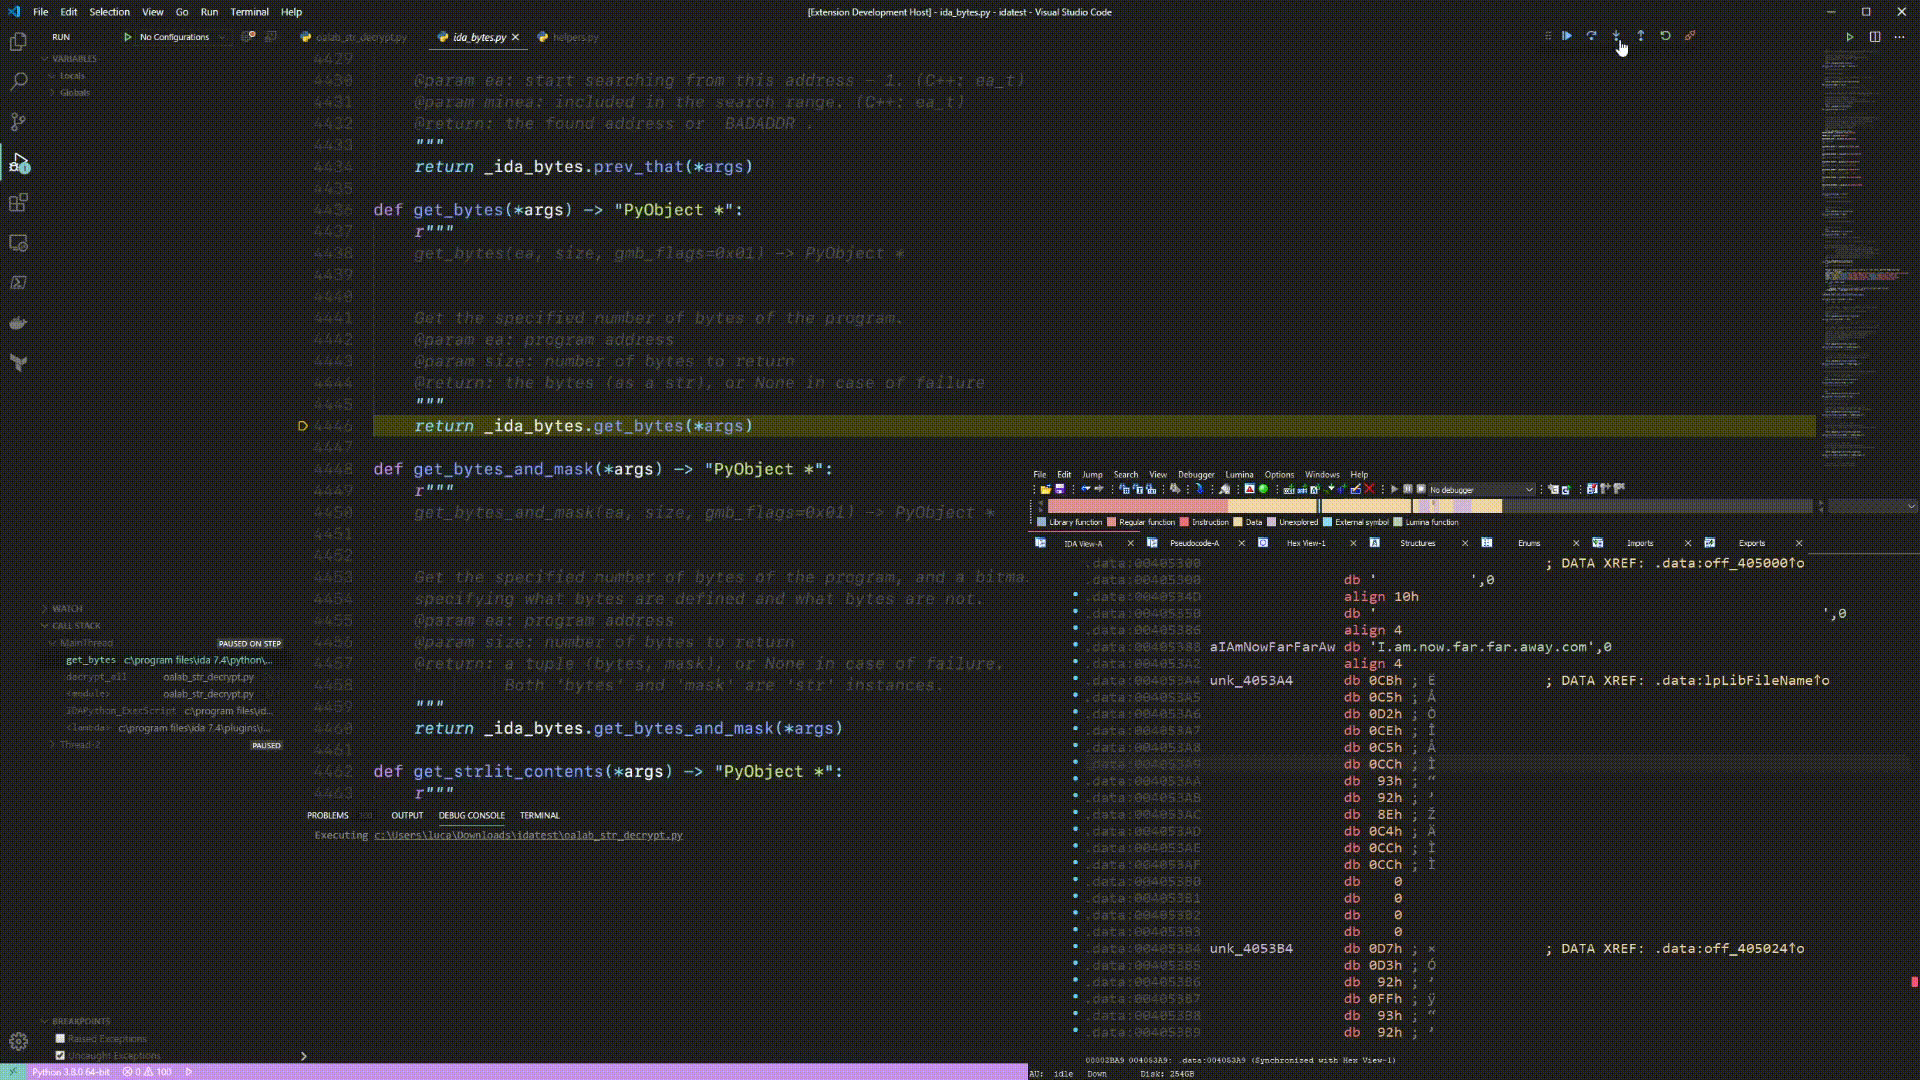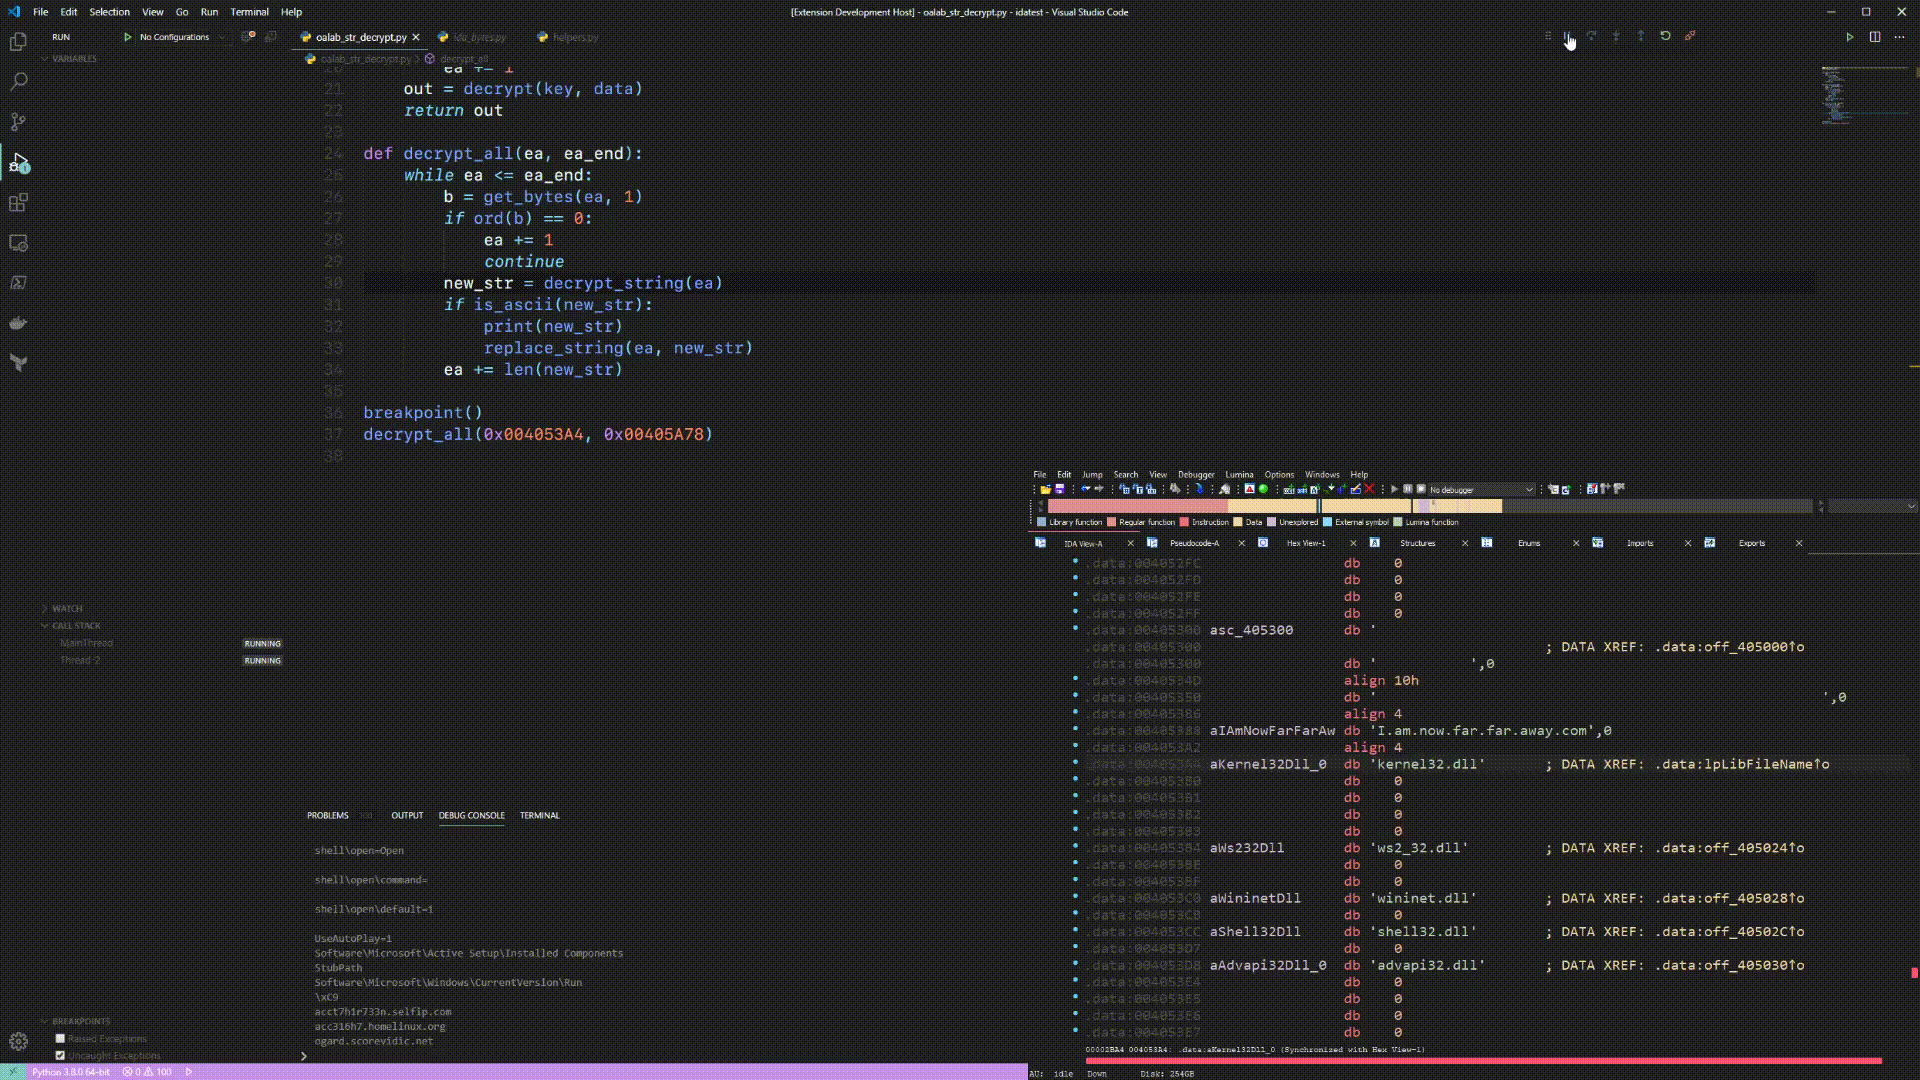
An integration for IDA and VS Code which connects both to easily execute and debug IDAPython scripts.
binary-analysisdebuggersreverse-engineering+1
9961 year ago
maat preview

maat

GitHubtrailofbits/maat

Dynamic symbolic execution and binary analysis framework with taint analysis, constraint solving, multi-arch emulation via Ghidra's Sleigh, and…
binary-analysisdynamic-analysis-sandboxingfuzzing+1
6515 months ago
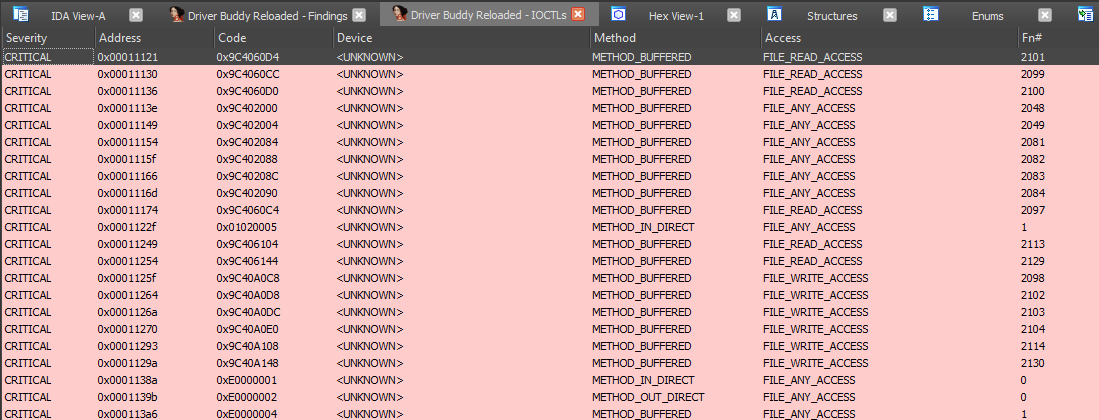
DriverBuddyReloaded preview

DriverBuddyReloaded

GitHubvoidsec/driverbuddyreloaded

Driver Buddy Reloaded is an IDA Pro Python plugin that helps automate some tedious Windows Kernel Drivers reverse engineering tasks

binary-analysisdebuggersreverse-engineering+2
4729 days ago
pyREtic preview

pyREtic

GitHubmynameismeerkat/pyretic

pyREtic is an extensible framework for in-memory Python 2.x bytecode reverse engineering

binary-analysiscode-analysisdebuggers+5
2673 years ago
shellex preview

shellex

GitHubtherealdreg/shellex

C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…
binary-analysisdebuggersexploitation+5
1133 years ago
grap preview

grap

GitHubquosecgmbh/grap

Define and match user-defined graph patterns against binary control flow graphs using a Capstone-based disassembler, with CLI, Python bindings, and…
binary-analysisdebuggersmalware-analysis+2
1554 years ago
windbg-mcp preview

windbg-mcp

GitHubgengstah/windbg-mcp

An MCP (Model Context Protocol) server that turns all pybag Windows debugger functions into native MCP tools. It lets MCP-compatible clients (Claude…
binary-analysisdebuggersdynamic-analysis-sandboxing+7
945 months ago
pocket_disasm preview

pocket_disasm

GitHubwhoisqwerz/pocket_disasm

Multi-session IDALib MCP router for coding agents. Analyze multiple binaries in parallel with IDA-compatible reverse engineering tools.
ai-assisted-reversingbinary-analysisdebuggers+5
413 months ago
pycdc-studio preview

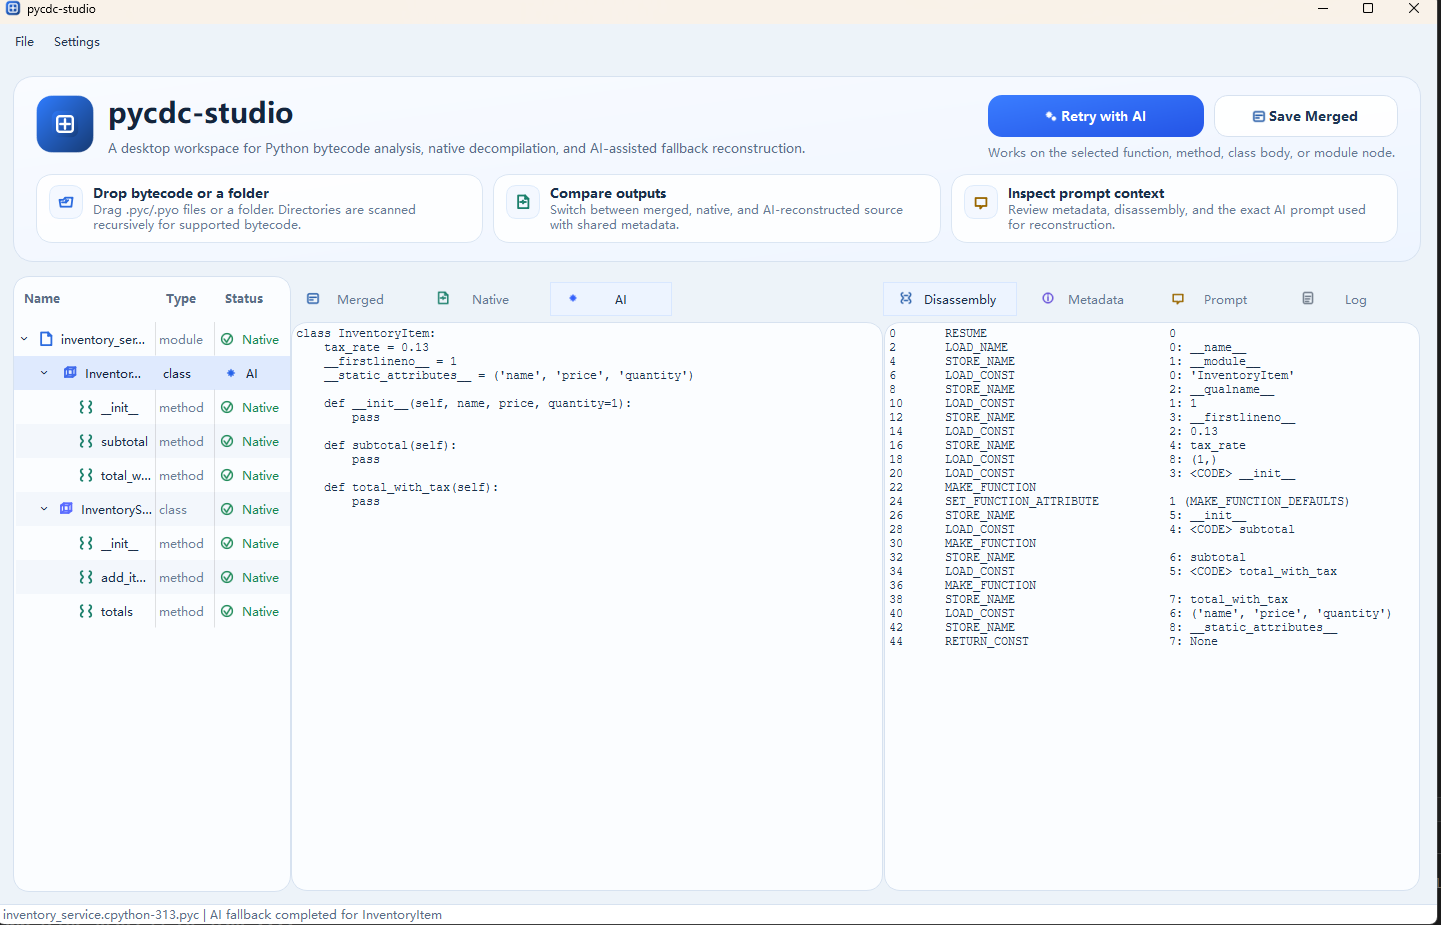
pycdc-studio

GitHubddouworld/pycdc-studio

A Qt Widgets desktop UI for exploring Python bytecode with pycdc/pycdas, inspecting native decompilation, and using AI fallback for unsupported code…
ai-assisted-reversingbinary-analysisdebuggers+4
436 months ago
bochscpu-python preview

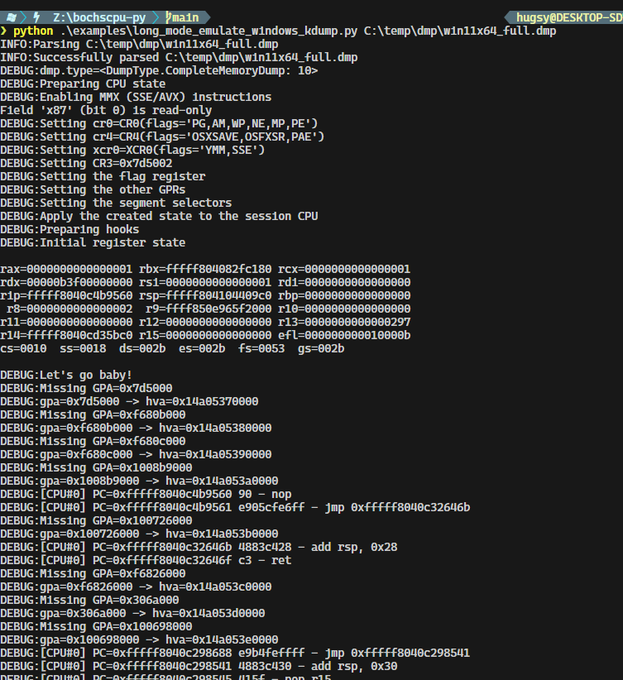
bochscpu-python

GitHubhugsy/bochscpu-python

Python bindings for BochsCPU
binary-analysisdynamic-analysis-sandboxingmalware-analysis+1
391 year ago
libtalloc preview

libtalloc

GitHubnccgroup/libtalloc

libtalloc is a python script for use with GDB that can be used to analyse the "trivial allocator" (talloc)
binary-analysisdebuggersmemory-forensics+2
1711 years ago
pyrebox preview
Archived

pyrebox

GitHubcisco-talos/pyrebox

Python scriptable Reverse Engineering Sandbox, a Virtual Machine instrumentation and inspection framework based on QEMU
binary-analysisdebuggersdigital-forensics+5
1.7k2 years ago
pe_tree preview
Archived

pe_tree

GitHubblackberry/pe_tree

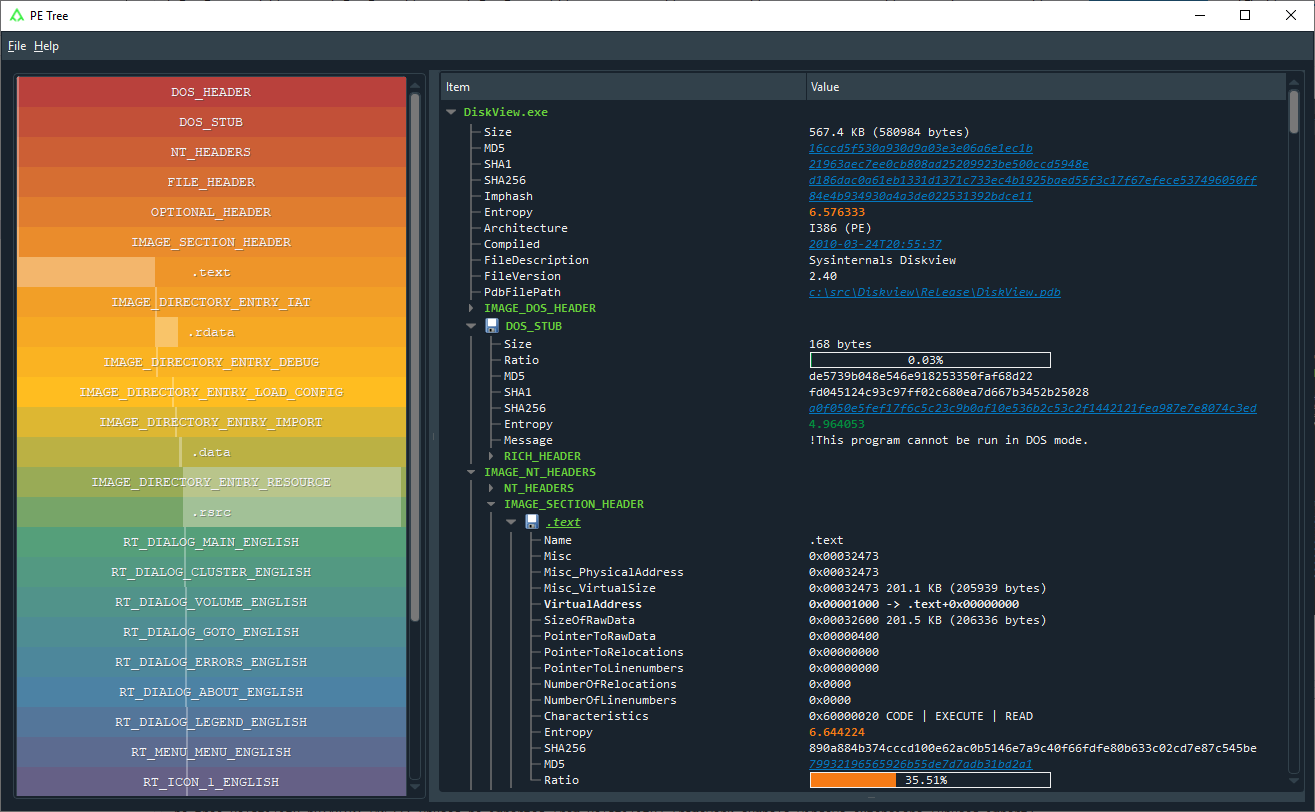
Python module for viewing Portable Executable (PE) files in a tree-view using pefile and PyQt5. Can also be used with IDA Pro and Rekall to dump…

binary-analysisdebuggersdigital-forensics+5
1.3k4 years ago
cutter preview

cutter

GitHubrizinorg/cutter

Free and Open Source Reverse Engineering Platform powered by rizin

ai-assisted-reversingbinary-analysisbinary-exploitation+4
20.1k1 month ago
ghidra-mcp preview

ghidra-mcp

GitHubbethington/ghidra-mcp

MCP server bridging Ghidra's reverse engineering with AI tools: 256 tools for decompilation, P-code emulation, live debugging, data flow analysis,…

ai-assisted-reversingbinary-analysisdebuggers+7
6.0k19h 59m ago
Previous123456Next