

magic-extractor
 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
binary-analysisdata-recoverydigital-forensics+8
43
xchwarze/magic-extractorUniversal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
 0x11dfe/file-unpumper
Tool that can be used to trim useless things from a PE file such as the things a file pumper would add.
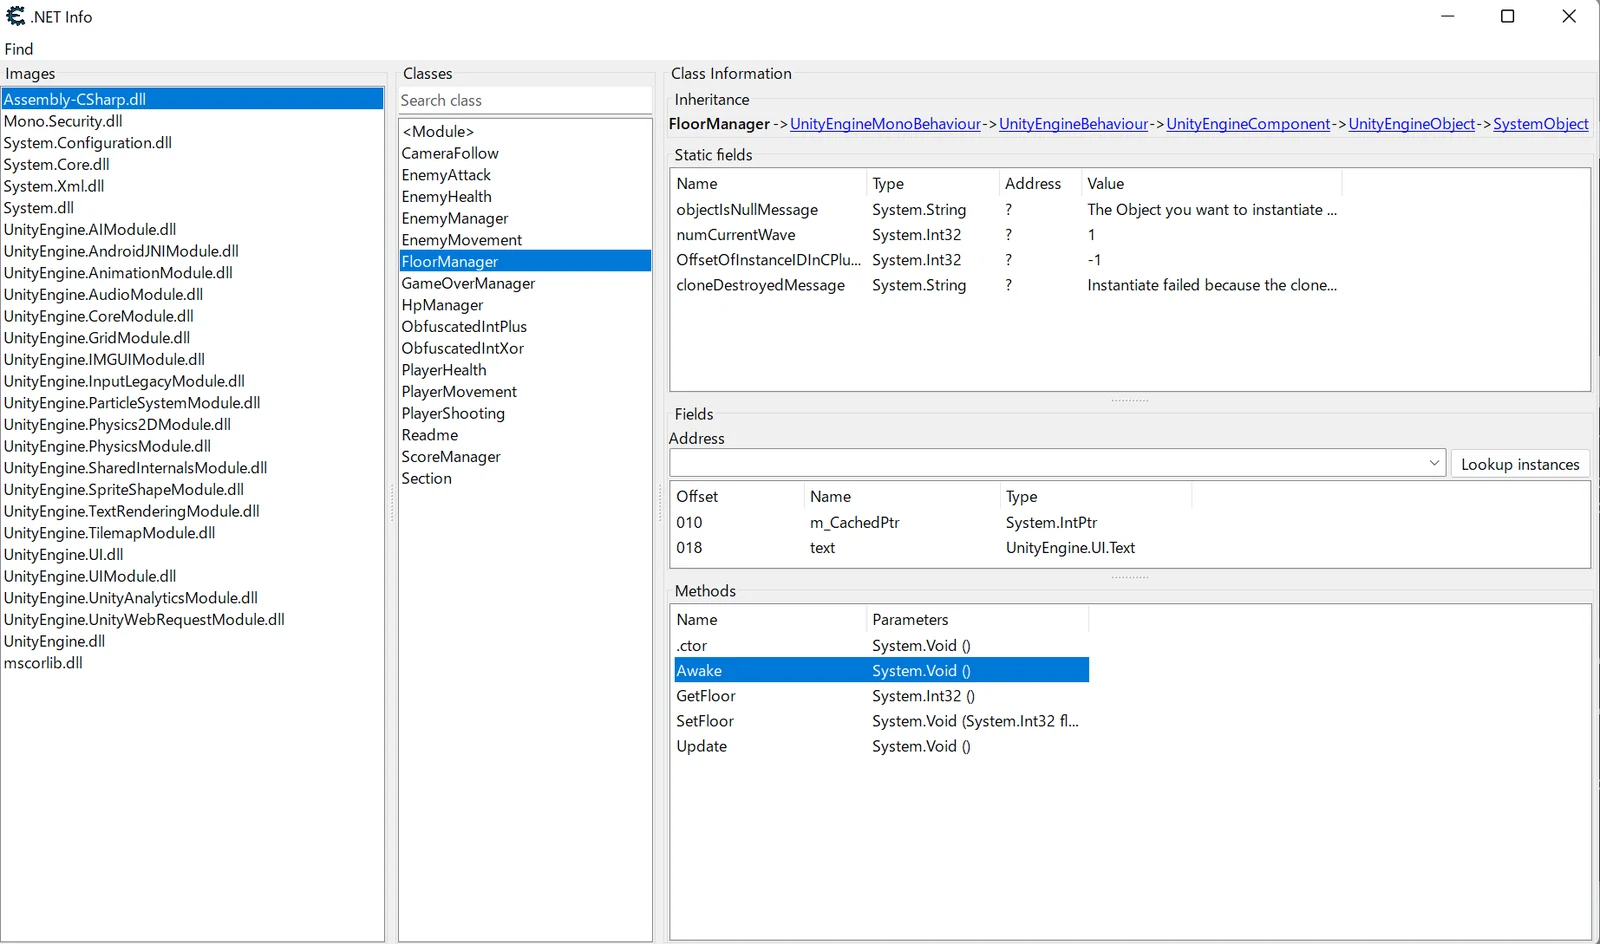 gmh5225/frida-il2cpp-datacollector
Frida-based tool that ports Cheat Engine's MonoDataCollector to Android and iOS, enabling runtime Mono/IL2CPP data collection and memory inspection…
 0x574r/darkcloak
Linux process identity cloaking tool that spoofs comm, argv, cmdline, environ, exe path, and VMAs via an 11-phase prctl pipeline to impersonate…
 yasharote/dll-injector
A desktop tool that allows injecting DLLs, hooking WinAPI functions like CreateFileW, and modifying process behavior at runtime — designed for…
 optiv/mangle
Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from EDRs
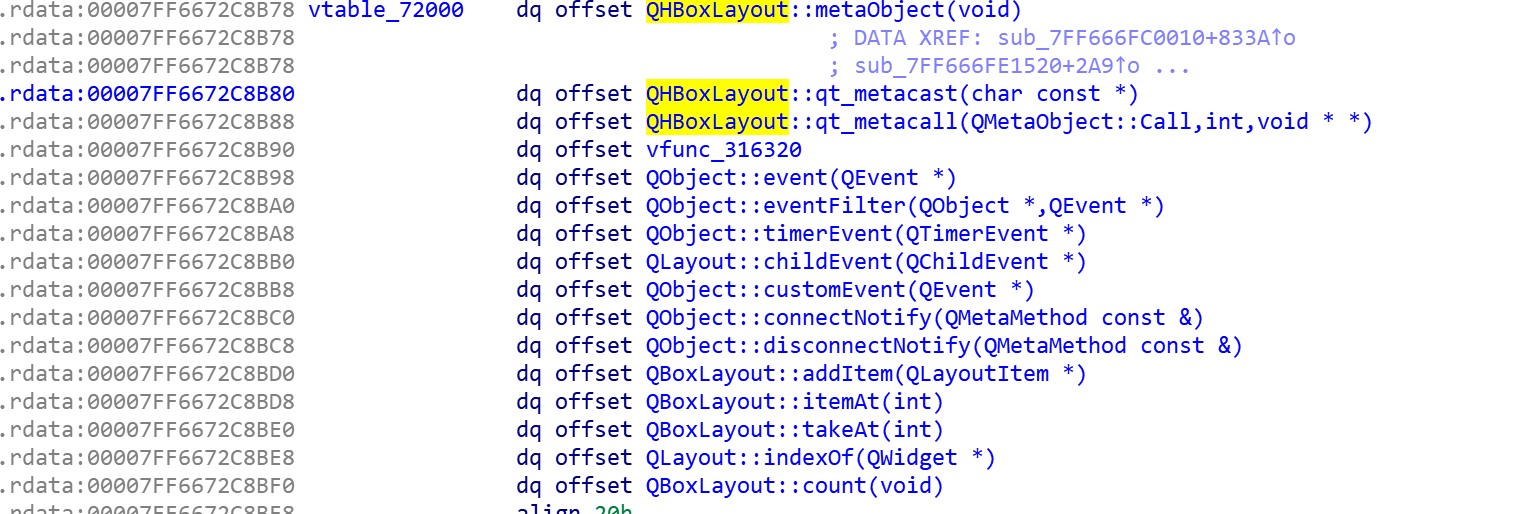 0xgalz/virtuailor
IDAPython tool for creating automatic C++ virtual tables in IDA Pro
 netspooky/inhale
A malware analysis and classification tool.
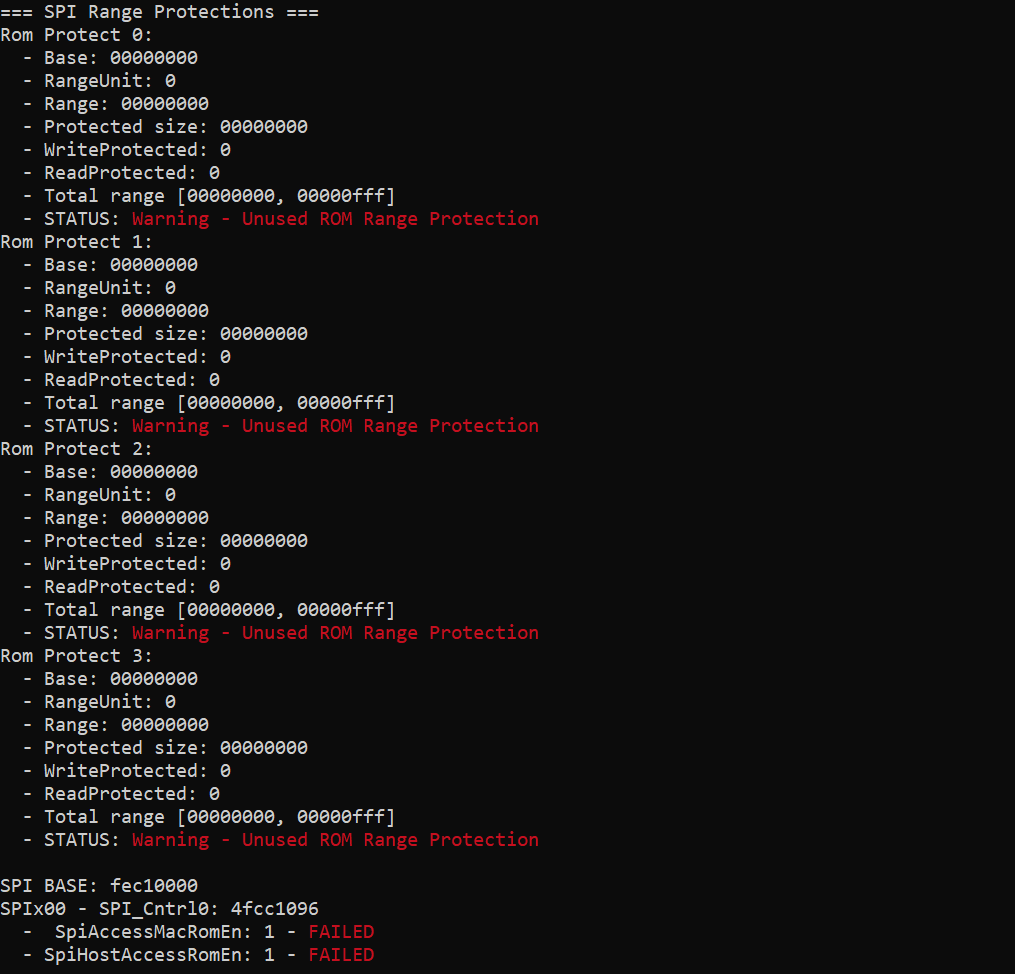 ioactive/platbox
Platform security assessment tool for dumping and analyzing UEFI/SMM registers, PCI config space, physical memory, SPI flash, and S3 bootscripts with…
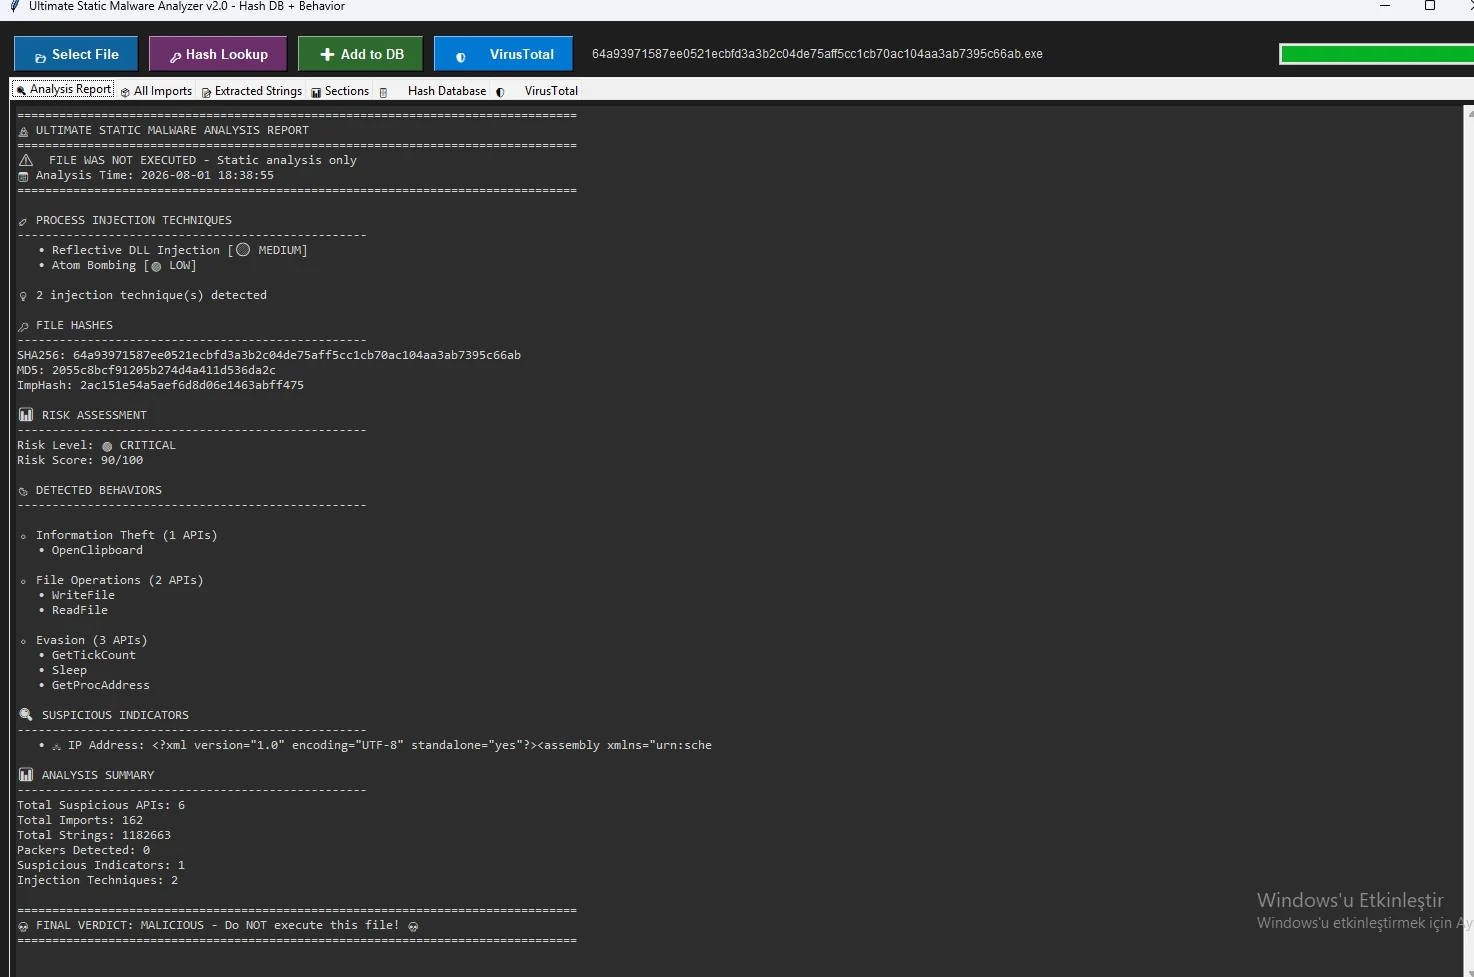 kaandemir993/malwareforge---advanced-static-malware-analyzer
Advanced Static malware analyzer that reveals 8 injection techniques, critical API calls, hidden strings, exports PE sections (.text, .rdata) as…
 hasherezade/pe-sieve
Scans a given process. Recognizes and dumps a variety of potentially malicious implants (replaced/injected PEs, shellcodes, hooks, in-memory patches).
 plum-umd/redexer
The Redexer binary instrumentation framework for Dalvik bytecode
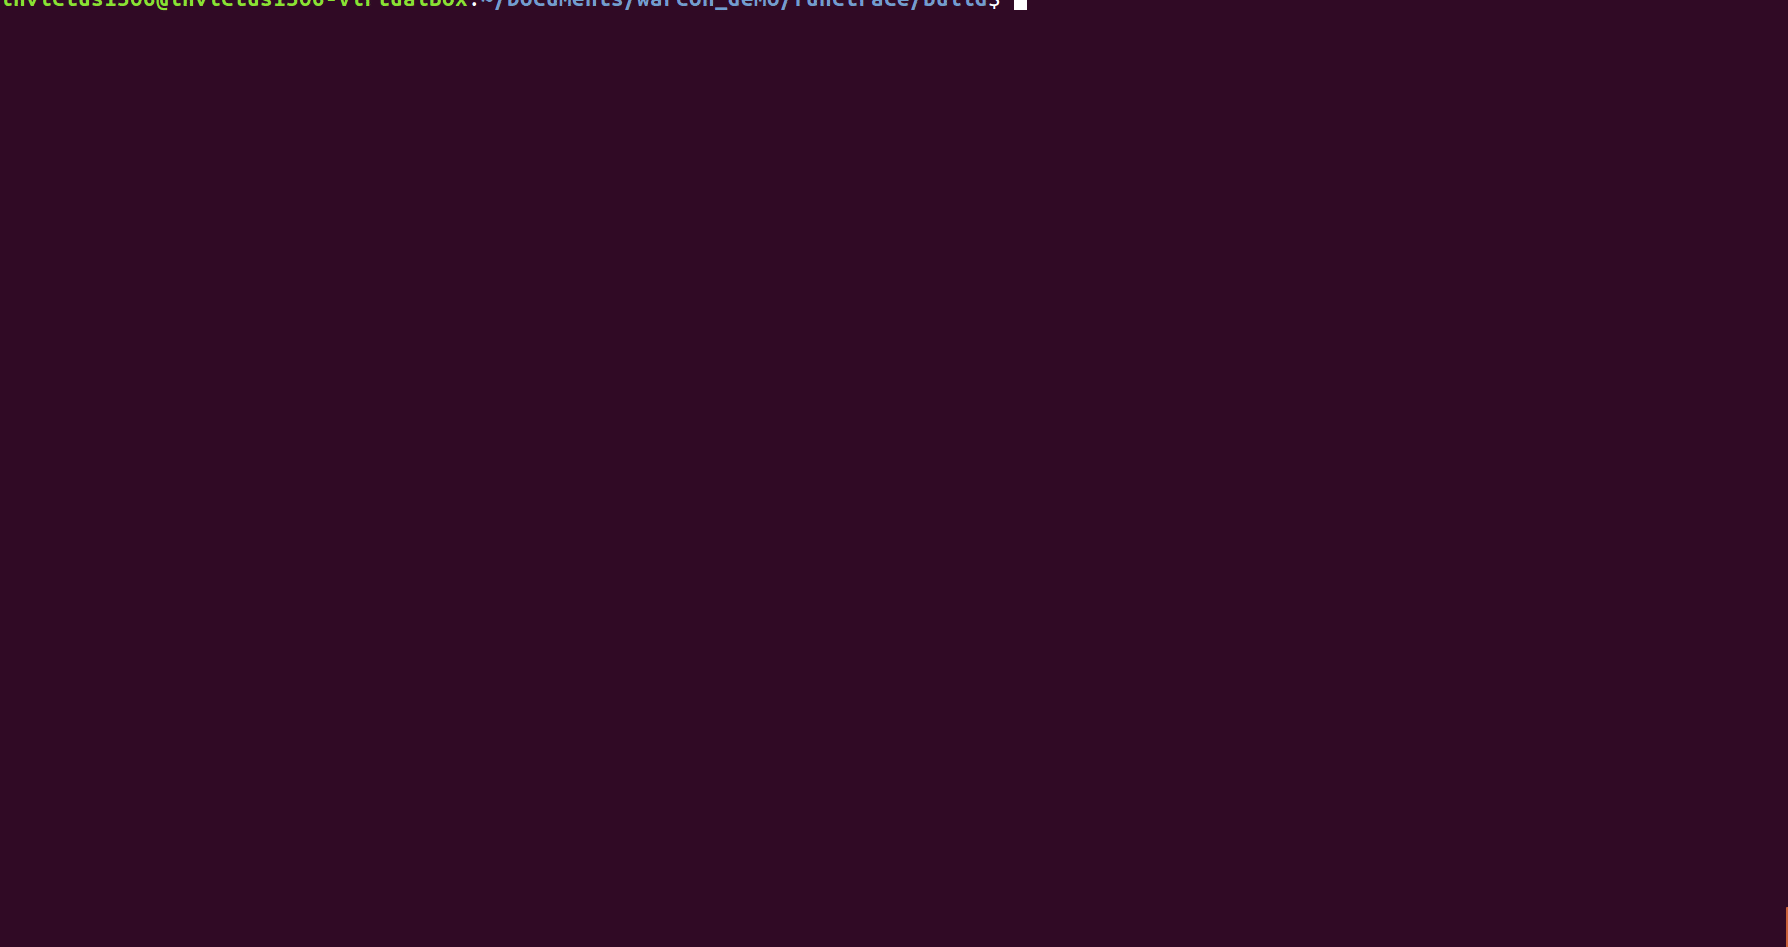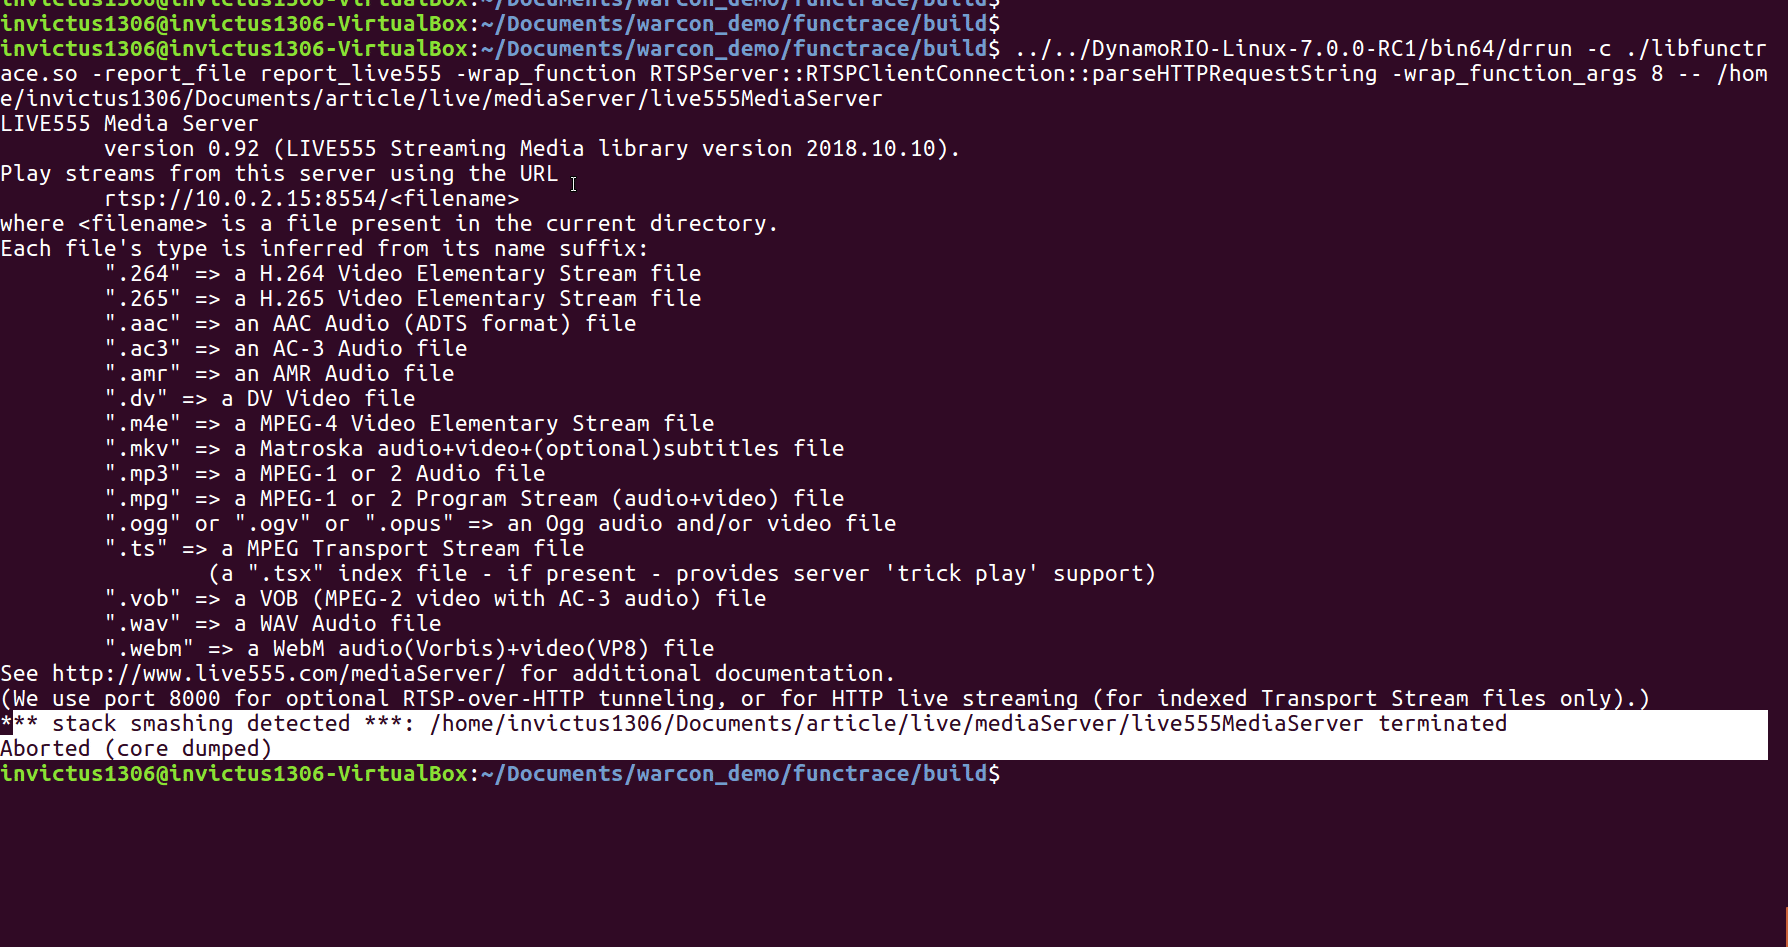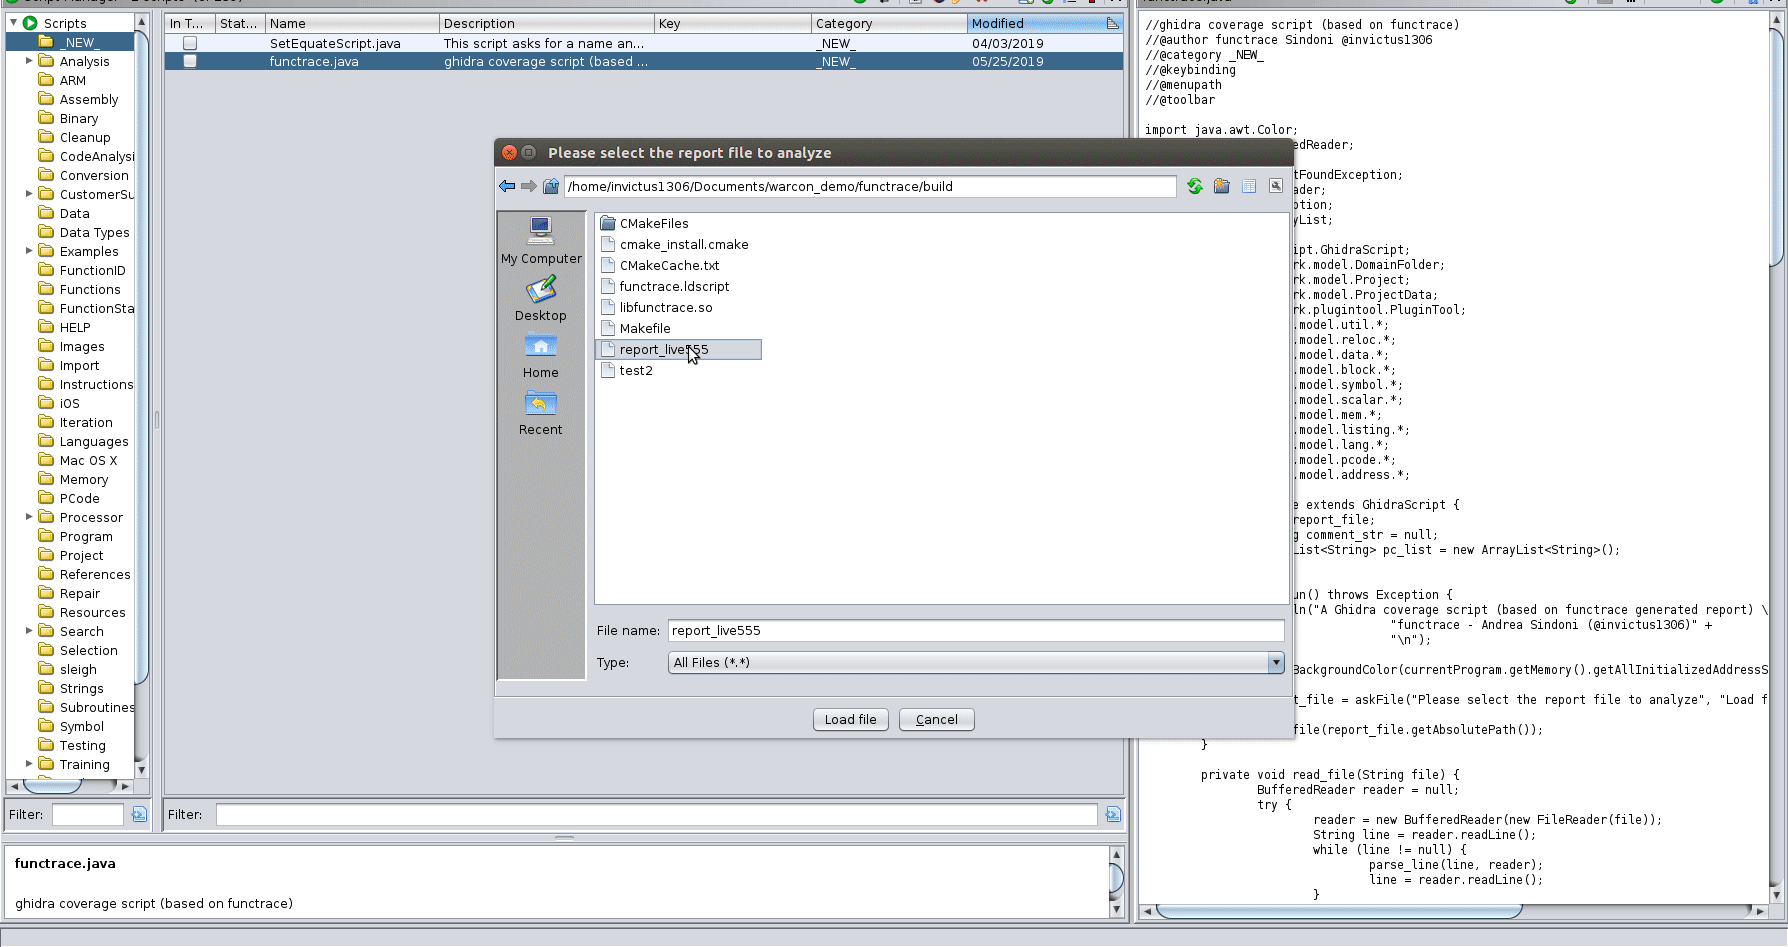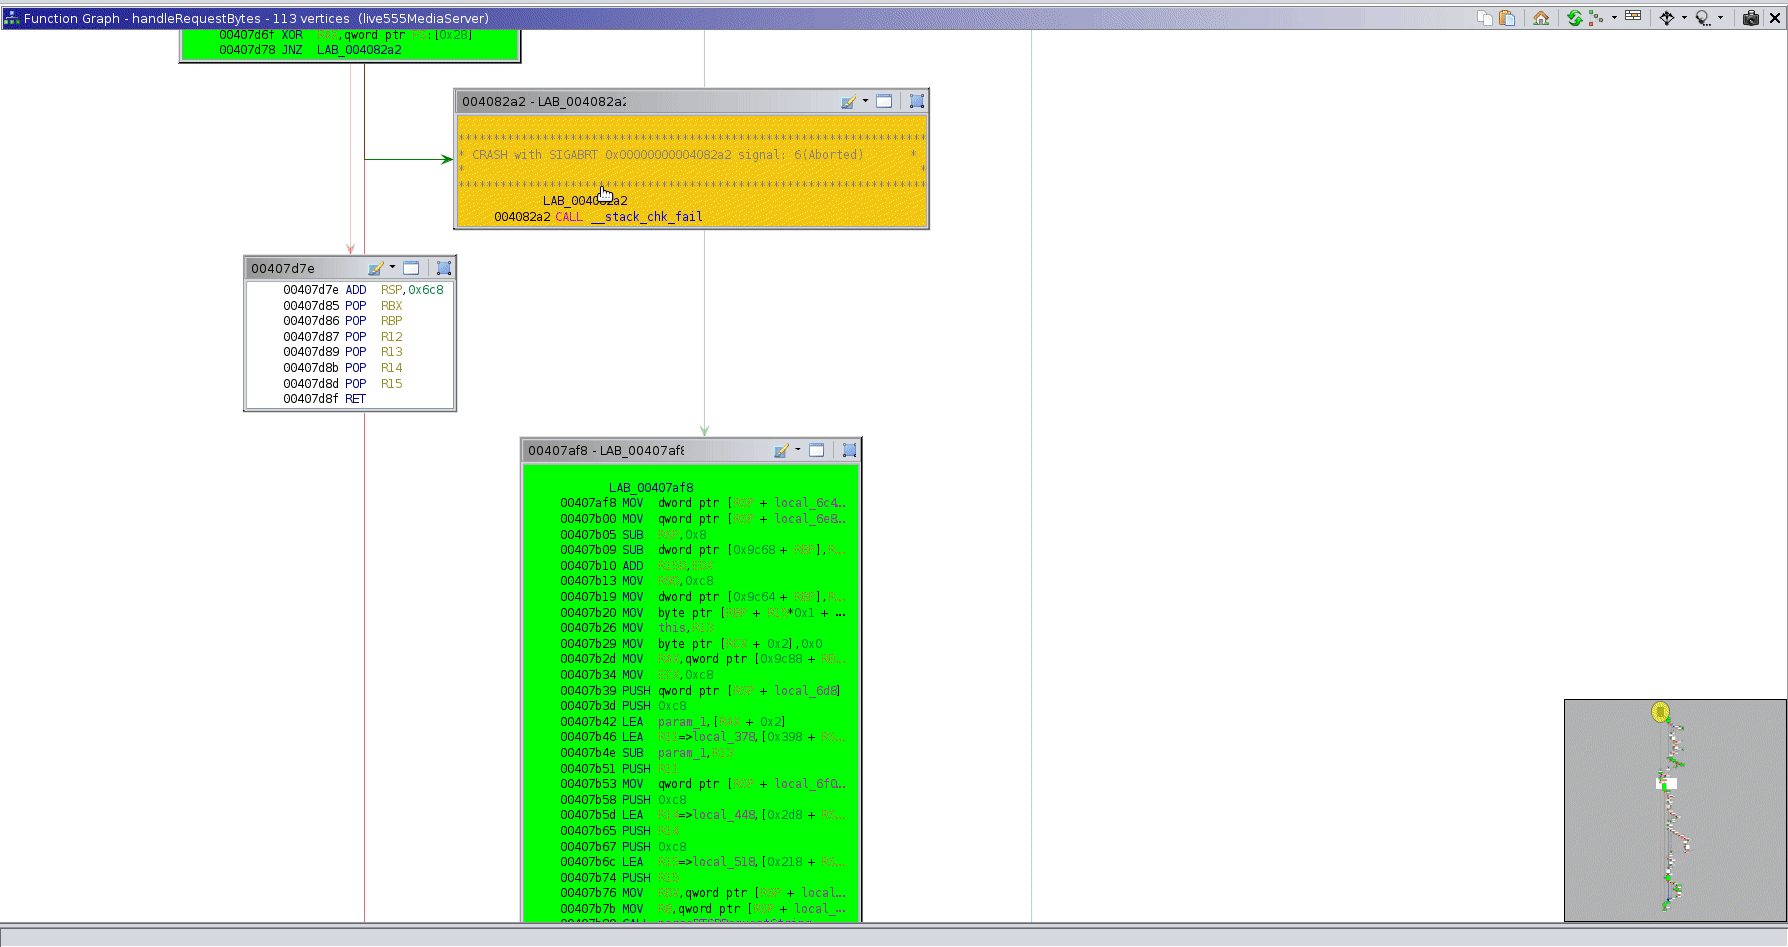 invictus1306/functrace
A function tracer
 n1ght-w0lf/uchihash
A small utility to deal with malware embedded hashes.
 fergarrui/custom-bytecode-analyzer
Java bytecode analyzer customizable via JSON rules
 codeshield-security/log4jshell-bytecode-detector
Local Bytecode Scanner for the Log4JShell Vulnerability (CVE-2021-44228)
 ret5et/watchguard_webui_unpacker
Watchguard Sysa-dl file format