

Jackalope
 googleprojectzero/jackalope
Binary, coverage-guided fuzzer for Windows, macOS, Linux and Android
binary-analysisdebuggersdynamic-analysis-sandboxing+6
1.4k
googleprojectzero/jackalopeBinary, coverage-guided fuzzer for Windows, macOS, Linux and Android
 nccgroup/asadbg
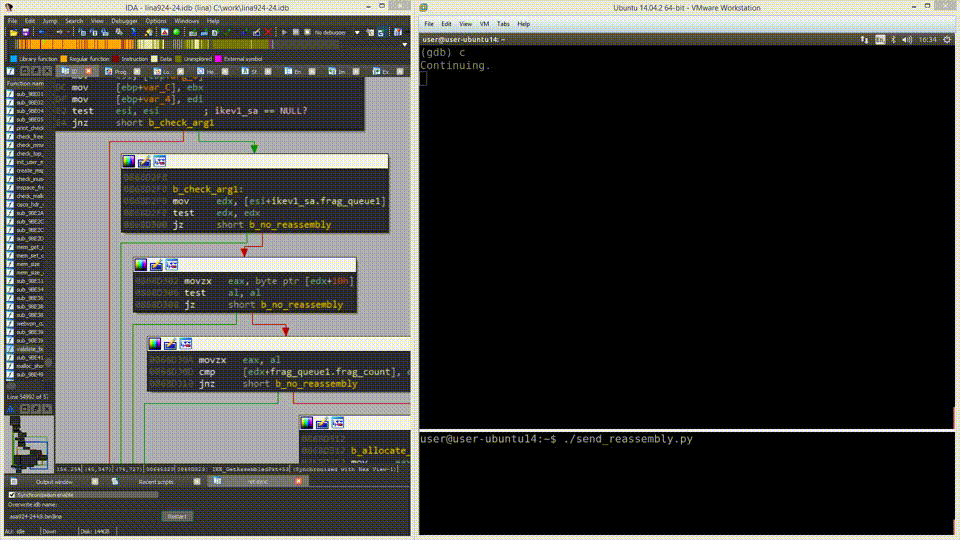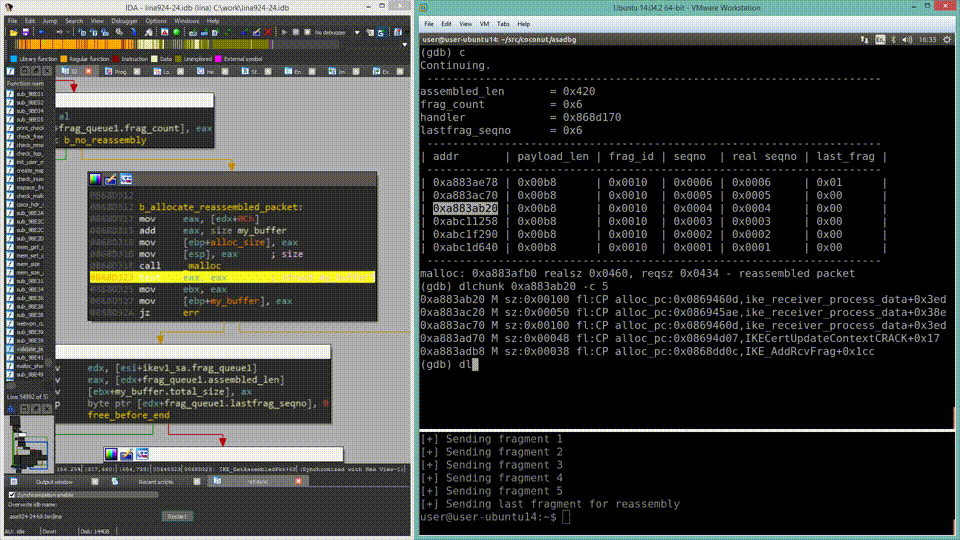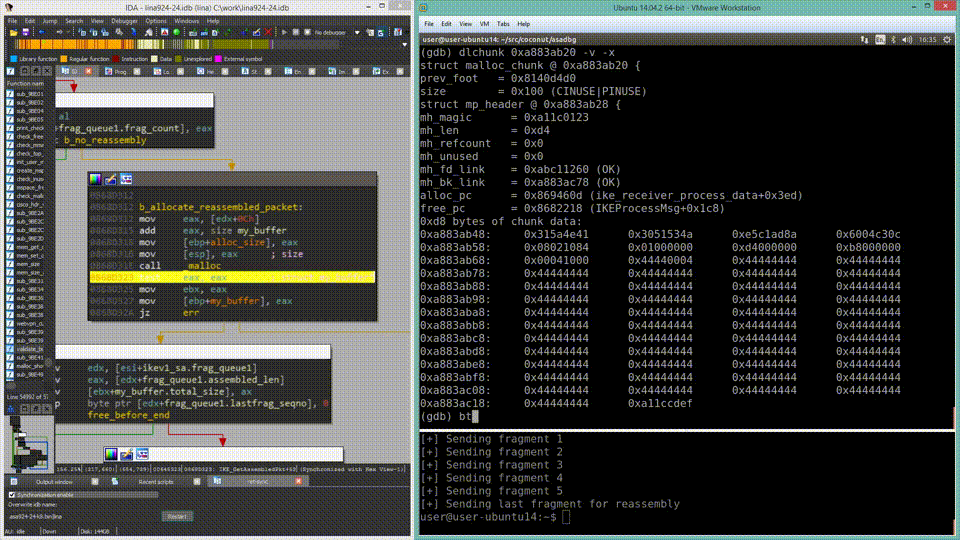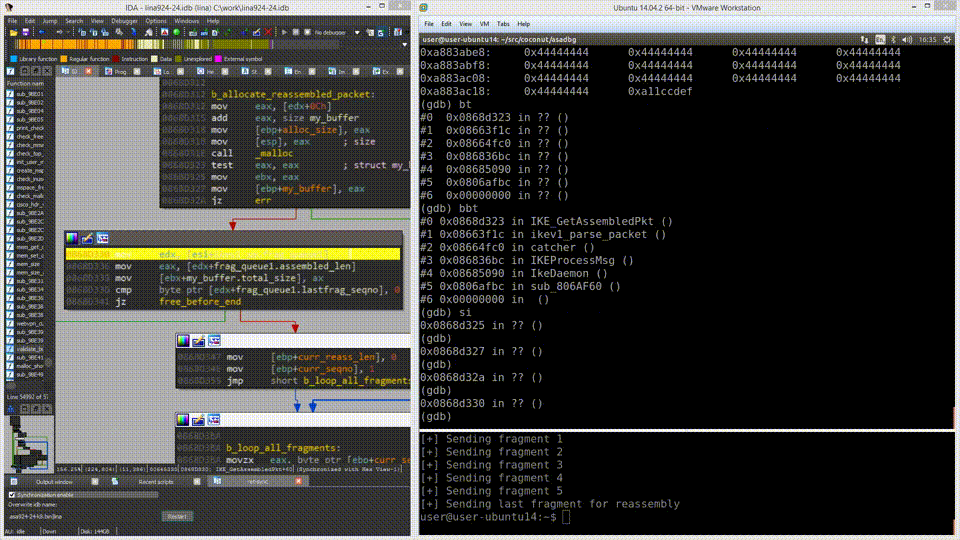
asadbg is a framework of tools to aid in automating live debugging of Cisco ASA devices
 kashithecomfy/comfyengine
ComfyEngine is a memory exploration toolkit built for people who need to monitor, patch, and script a running process.
 tarunyadav/fix-cve-2013-2094
Generates portable SystemTap kernel modules to mitigate CVE-2013-2094 on Enterprise Linux systems, with automated build and deployment scripts for…
 volatilityfoundation/dwarf2json
convert ELF/DWARF symbol and type information into vol3's intermediate JSON
 vvirei333/abrake27
iOS 27 kernelcache RE: SEP dispatch map, AMFI diff, Ghidra workflow
 gallopsled/pwntools
CTF framework and exploit development library
 rr-debugger/rr
Record and replay framework for deterministic debugging of multi-threaded applications, enabling reverse execution, hardware watchpoints, and…
 unicorn-engine/unicorn
Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)
 trolldbois/python-haystack
Process heap analysis framework - Windows/Linux - record type inference and forensics
 aethervm/aethervm
LLVM-native binary analysis and emulation platform that lifts AArch64 and x86_64 machine code to LLVM IR for instrumentation, deobfuscation, and…
 iss4cf0ng/elfina
Multi-architecture ELF loader and analysis toolkit with probing, disassembly, hexdump, entropy calculation, and mmap/memfd execution for x86 and…
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
 gadievron/raptor
Autonomous security research framework integrating static analysis, binary analysis, fuzzing, LLM-powered vulnerability validation, exploit…
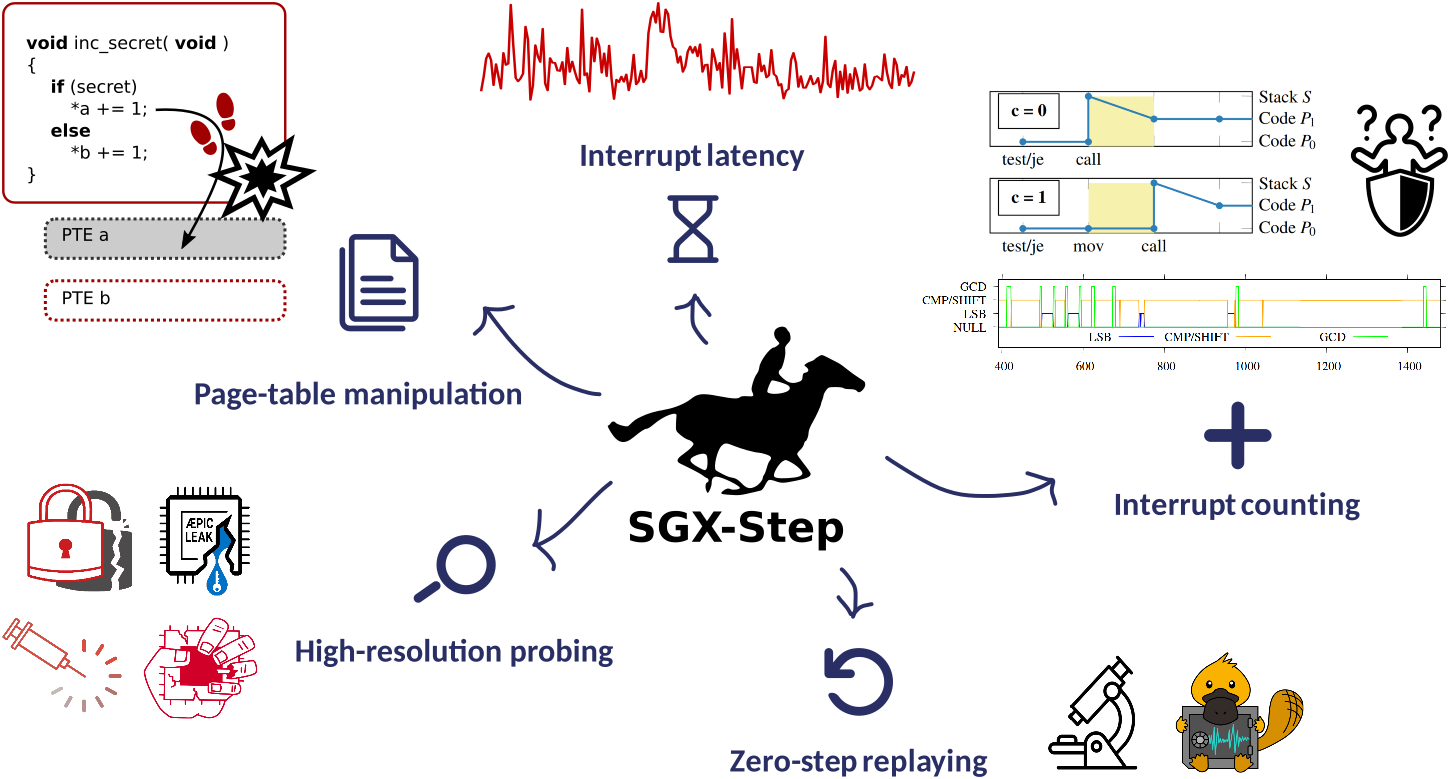 jovanbulck/sgx-step
A practical attack framework for precise enclave execution control
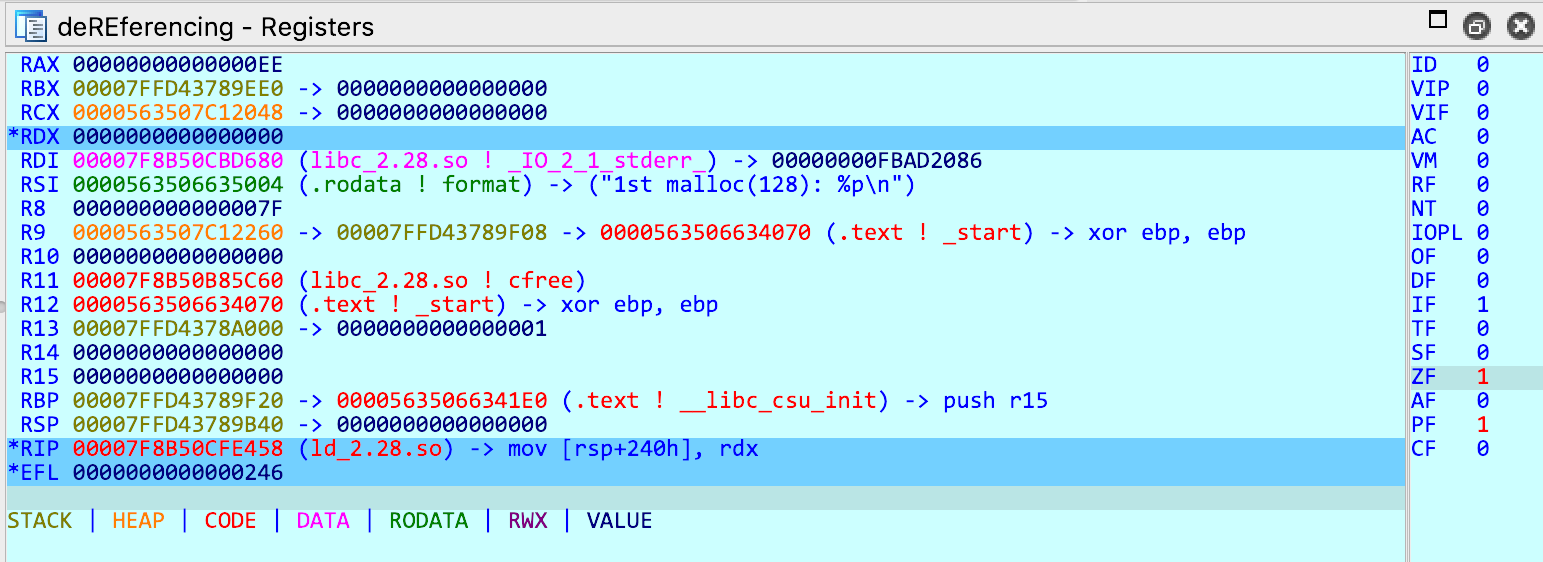 danigargu/dereferencing
IDA Pro plugin that implements more user-friendly register and stack views
 bw3ll/sharem
SHAREM is a shellcode analysis framework, capable of emulating more than 45,000 WinAPIs and virutally all Windows syscalls. It also contains its own…
 c3rb3ru5d3d53c/binlex
A Binary Genetic Traits Lexer Framework