
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
300 results
aixcc-afc-atlantis preview

aixcc-afc-atlantis

GitHubteam-atlanta/aixcc-afc-atlantis

Automated cyber reasoning system that discovers and analyzes software vulnerabilities through fuzzing, binary analysis, and program reasoning for…

binary-analysisfuzzingvulnerability-analysis
63311 months ago
frida-ios-hook preview

frida-ios-hook

GitHubnoobpk/frida-ios-hook

A tool that helps you easy trace classes, functions, and modify the return values of methods on iOS platform

binary-analysisdynamic-analysis-sandboxingios-security+3
1.2k8 months ago
deREferencing preview

deREferencing

GitHubdanigargu/dereferencing

IDA Pro plugin that implements more user-friendly register and stack views

binary-analysisdebuggersreverse-engineering+1
7681 month ago
DriverBuddyReloaded preview

DriverBuddyReloaded

GitHubvoidsec/driverbuddyreloaded

Driver Buddy Reloaded is an IDA Pro Python plugin that helps automate some tedious Windows Kernel Drivers reverse engineering tasks

binary-analysisdebuggersreverse-engineering+2
43512 days ago
Hunt-Sleeping-Beacons preview

Hunt-Sleeping-Beacons

GitHubtheflink/hunt-sleeping-beacons

Callstack scanner that identifies IOCs of unpacked or injected C2 agents by analyzing thread idle behavior, unbacked memory, module stomping, APCs,…

binary-analysisdefensive-toolsforensics+3
6789 months ago
ioctlance preview

ioctlance

GitHubzeze-zeze/ioctlance

A tool that is used to hunt vulnerabilities in x64 WDM drivers

binary-analysisdynamic-analysis-sandboxingexploit-frameworks+4
4694 months ago
stringsifter preview

stringsifter

GitHubmandiant/stringsifter

A machine learning tool that ranks strings based on their relevance for malware analysis.

binary-analysismachine-learningmalware-analysis+2
7673 years ago
PrivKit preview

PrivKit

GitHubmertdas/privkit

PrivKit is a simple beacon object file that detects privilege escalation vulnerabilities caused by misconfigurations on Windows OS.

binary-analysisexploitationpenetration-testing+4
6119 months ago
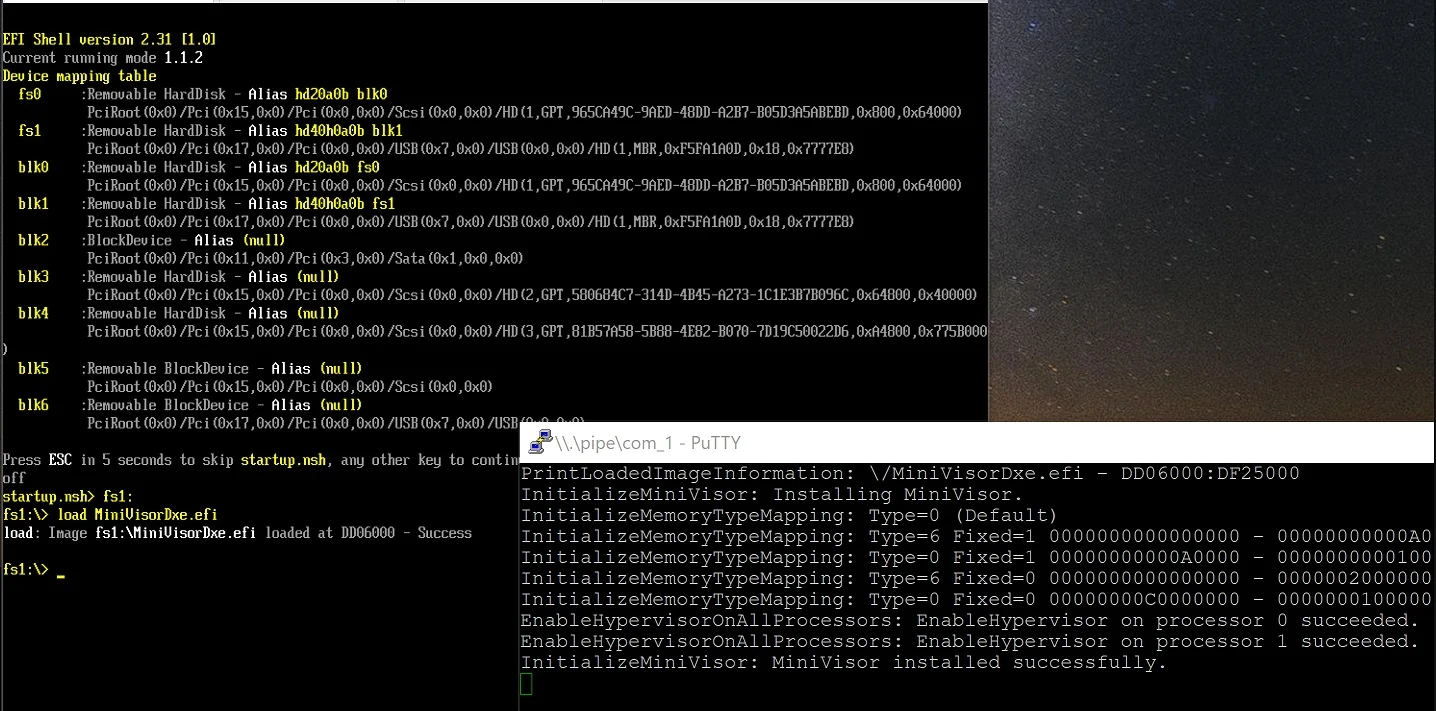
MiniVisorPkg preview

MiniVisorPkg

GitHubtandasat/minivisorpkg

The research UEFI hypervisor that supports booting an operating system.

binary-analysisdefensive-toolseducation+5
7652 years ago
smack preview

smack

GitHubsmackers/smack

Modular software verification toolchain that translates LLVM IR into Boogie intermediate verification language for bounded and experimental unbounded…

binary-analysiscode-analysisdynamic-code-analysis+1
4483 months ago
windiff preview

windiff

GitHubergrelet/windiff

Tool that allows comparing symbol, type and syscall information of Microsoft Windows binaries across different versions of the OS, using a Web UI…

binary-analysisinformation-gatheringreverse-engineering+1
3922h 21m ago
WFH preview

WFH

GitHubconscioushacker/wfh

Frida-based dynamic analysis tool that automatically identifies DLL sideloading and COM hijacking vulnerabilities in Windows executables through…

binary-analysisdynamic-analysis-sandboxingexploitation+1
4364 years ago
dsync preview

dsync

GitHubpatois/dsync

IDAPython plugin that synchronizes disassembler and decompiler views

binary-analysisdebuggersreverse-engineering
4585 years ago
zkar preview

zkar

GitHubphith0n/zkar

Go-based Java serialization protocol analyzer that parses, dumps, and generates deserialization payloads with ysoserial gadget support and a library…

binary-analysisexploitationpayload-generation+1
6536 months ago
efiSeek preview

efiSeek

GitHubdsecurity/efiseek

Ghidra plugin that automates UEFI firmware analysis by identifying known GUIDs, protocols, SMI handlers, and interrupt functions, with headless…

binary-analysisembedded-systems-securityfirmware-analysis+3
4104 years ago
HyperDeceit preview

HyperDeceit

GitHubxyrem/hyperdeceit

HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…

adversarial-attackbinary-analysisids-ips-evasion+3
3853 years ago
fuzzable preview

fuzzable

GitHubex0dus-0x/fuzzable

Static analysis framework that identifies fuzzable function targets in source code and binaries, generates harness templates, and integrates with…

binary-analysisfuzzingreverse-engineering+2
5492 years ago
PyMemoryEditor preview

PyMemoryEditor

GitHubjeanextreme002/pymemoryeditor

A pure-Python library, app and MCP that lets you inspect, modify and search the memory of any running process in a few lines of Python :snake: .

binary-analysisdebuggerseducation+3
20619 days ago
Previous123…17Next