
stringsifter
 mandiant/stringsifter
A machine learning tool that ranks strings based on their relevance for malware analysis.
binary-analysismachine-learningmalware-analysis+2
767
mandiant/stringsifterA machine learning tool that ranks strings based on their relevance for malware analysis.
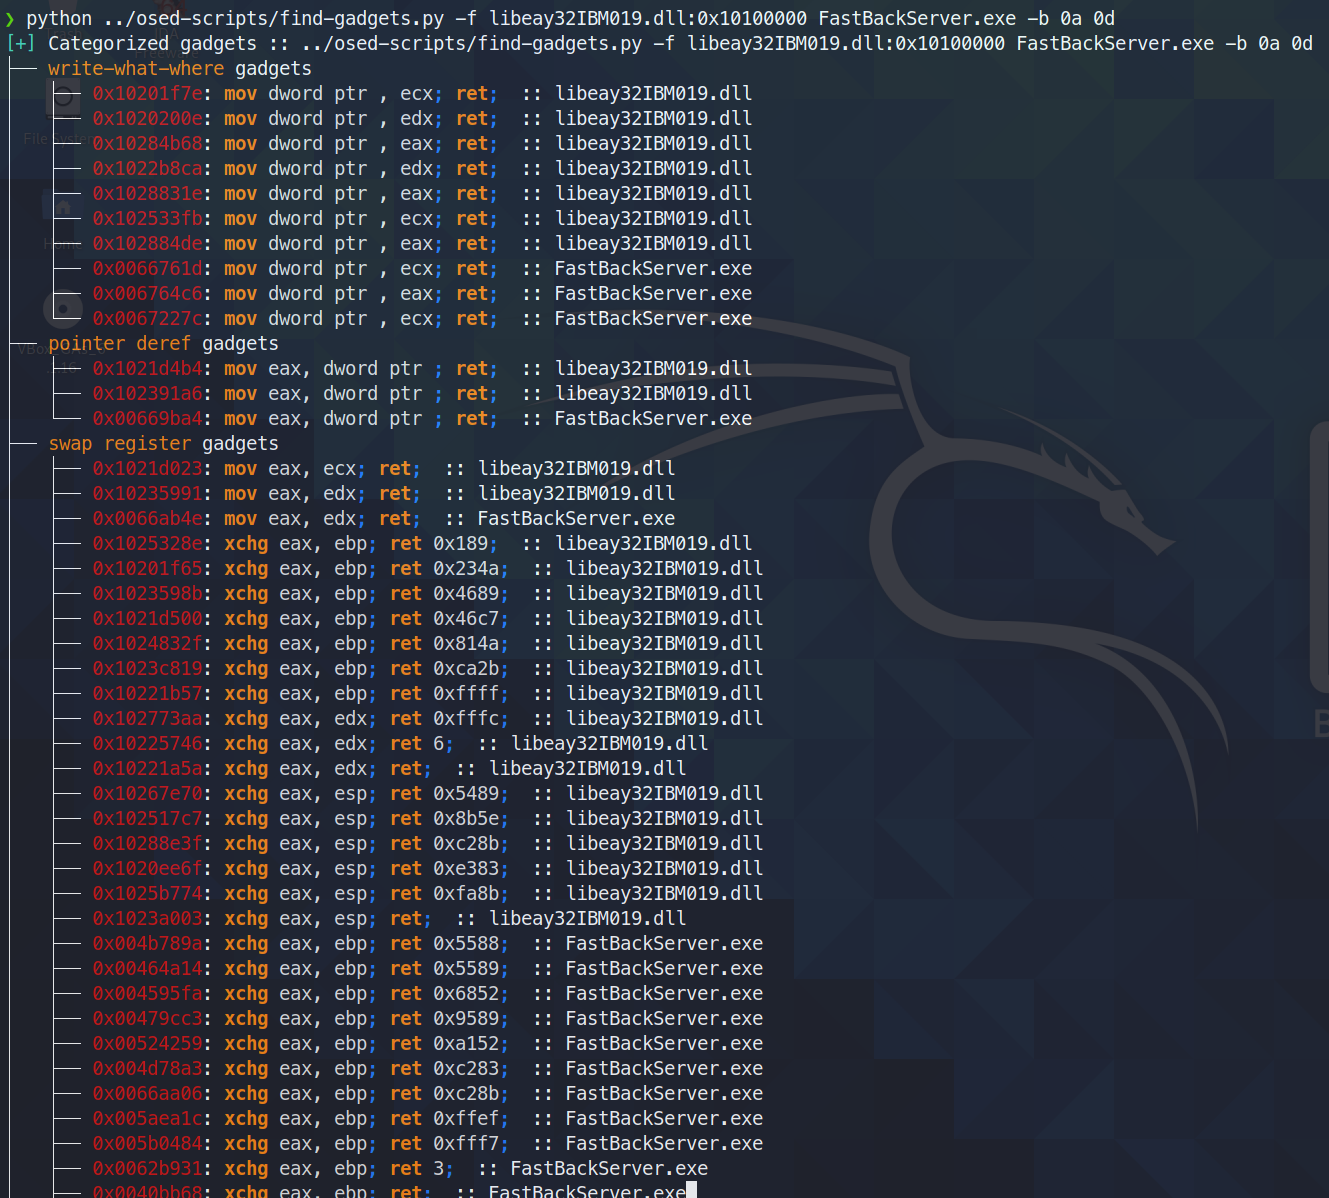 epi052/osed-scripts
bespoke tooling for offensive security's Windows Usermode Exploit Dev course (OSED)
 ridhinva/linux-kernel-algif-aead-checker
Scanner: CVE-2026-31431 Linux kernel algif_aead Copy Fail vulnerability checker — Python PoC for heap overflow path
 beardypig/ghidra-emotionengine
Ghidra Processor for the Play Station 2's Emotion Engine MIPS based CPU
 asherdll/r2gopclntabparser
A radare2 script to parse the gopclntab to facilitate Reverse Engineering Go binaries.
 coldzer0/cmulator
Cmulator is ( x86 - x64 ) Scriptable Reverse Engineering Sandbox Emulator for shellcode and PE binaries . Based on Unicorn & Zydis Engine &…
 x86rc/vmp-lazy-unpack
Emulation-based unpacker and import resolver for Windows x86/x64 VMProtect 3.x binaries, using Unicorn to emulate syscalls and rebuild the IAT…
 cloudflare/filterforge
Tool for solving BPF filters and crafting packets based on these.
 airbus-seclab/gustave
GUSTAVE is a fuzzing platform for embedded OS kernels. It is based on QEMU and AFL (and all of its forkserver siblings). It allows to fuzz OS kernels…
 airbus-cyber/ghidralligator
Multi-architecture pcode emulator using Ghidra/Sleigh for AFL++ fuzzing of binaries, firmware, and embedded targets; detects memory-corruption bugs…
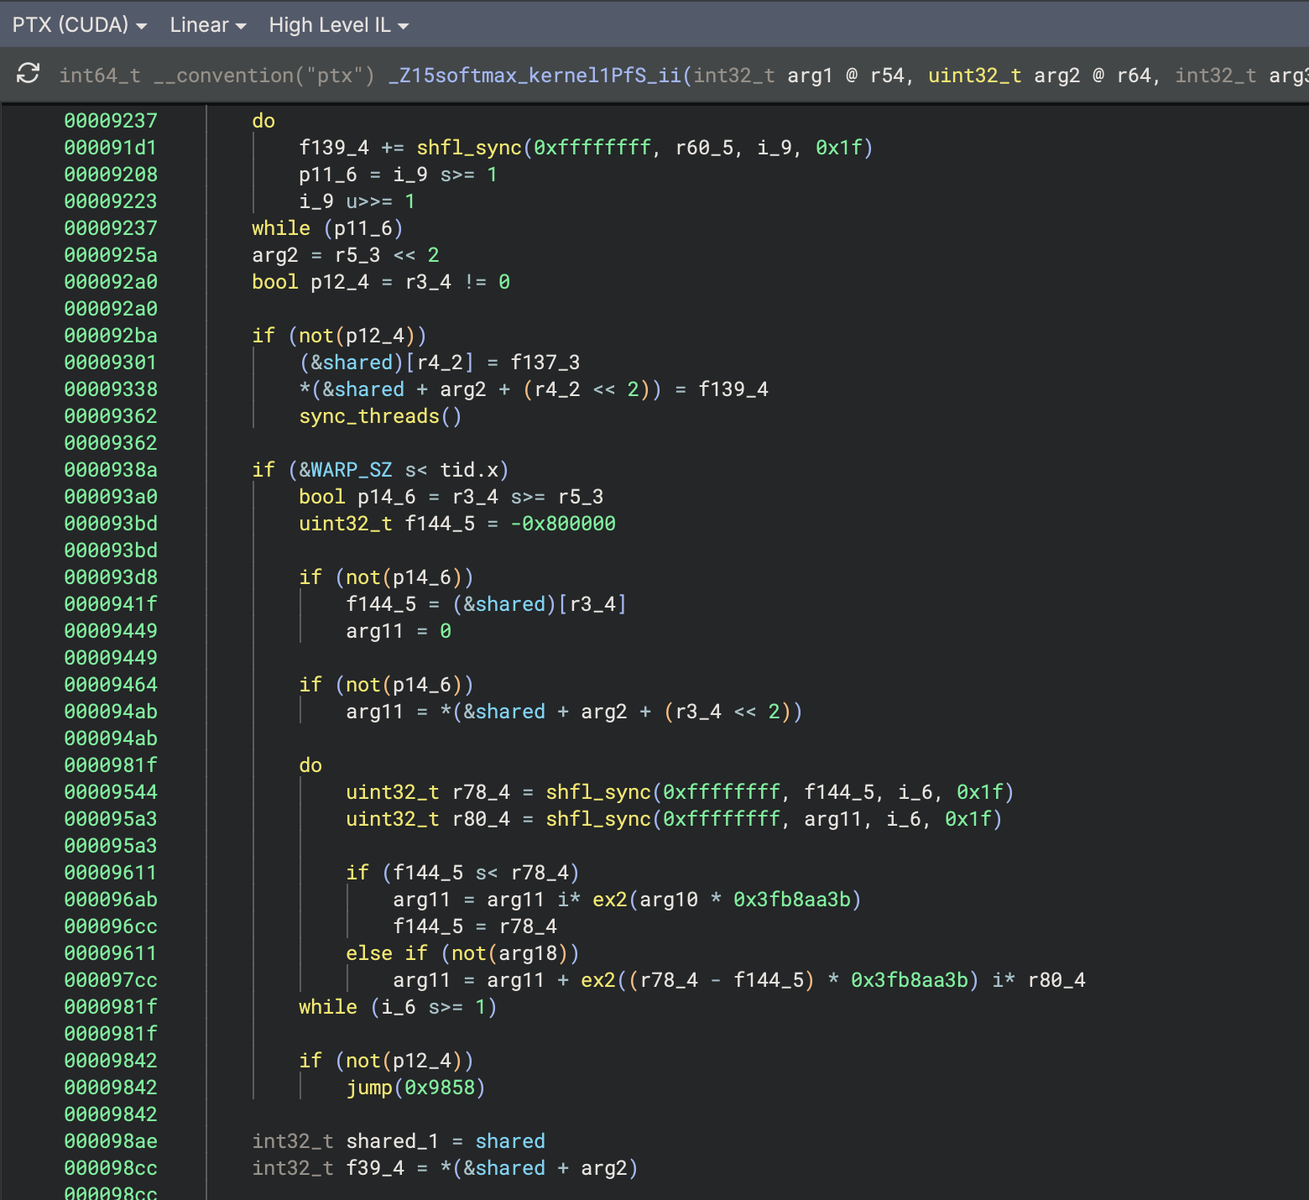 seekbytes/ptxninja
Binary Ninja plugin for reverse engineering PTX -- the virtual instruction set architecture of CUDA-based GPUs.
 abhi-r3v0/adhrit
Android Security Suite for in-depth reconnaissance and static bytecode analysis based on Ghera benchmarks.
 nccgroup/mtk_bp
Tools for analyzing and reverse engineering MediaTek baseband firmware, including file extraction, symbol parsing, and Ghidra integration for modem…
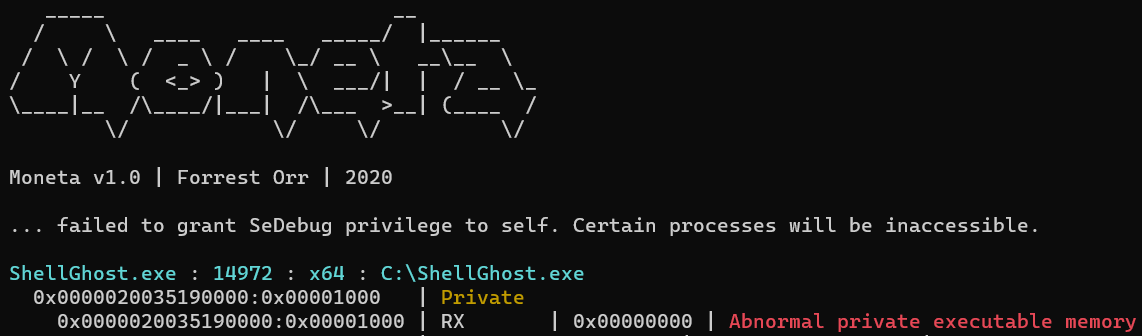 lem0nsec/shellghost
A memory-based evasion technique which makes shellcode invisible from process start to end.
 nnonickreal/openqore
unleash the full power of your BES-based headphones! :)
 adikso/cve-2024-5633
PoC for CVE-2024-5633
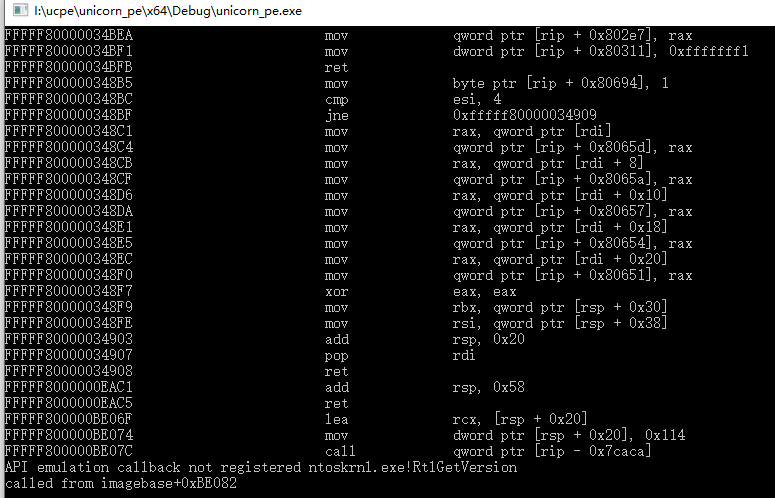 hzqst/unicorn_pe
Emulates Windows PE execution using Unicorn engine for malware analysis, unpacking packed binaries, and decrypting VMProtect strings and imports.