

lightkeeper
 worksbutnottested/lightkeeper
Maps execution-coverage data onto Ghidra disassembly to highlight visited code paths and accelerate reverse-engineering workflows.
binary-analysiscode-analysisdynamic-code-analysis+1
76
worksbutnottested/lightkeeperMaps execution-coverage data onto Ghidra disassembly to highlight visited code paths and accelerate reverse-engineering workflows.
 1rhino2/fnprint
match functions in binaries by what they do, not what their bytes look like. behavioral function fingerprinting via microexecution.
 nccgroup/winstrument
Winstrument is a framework of modular scripts to aid in instrumenting Windows software using Frida for reverse engineering and attack surface…
 robertdfrench/ifuncd-up
GNU IFUNC is the real culprit behind CVE-2024-3094
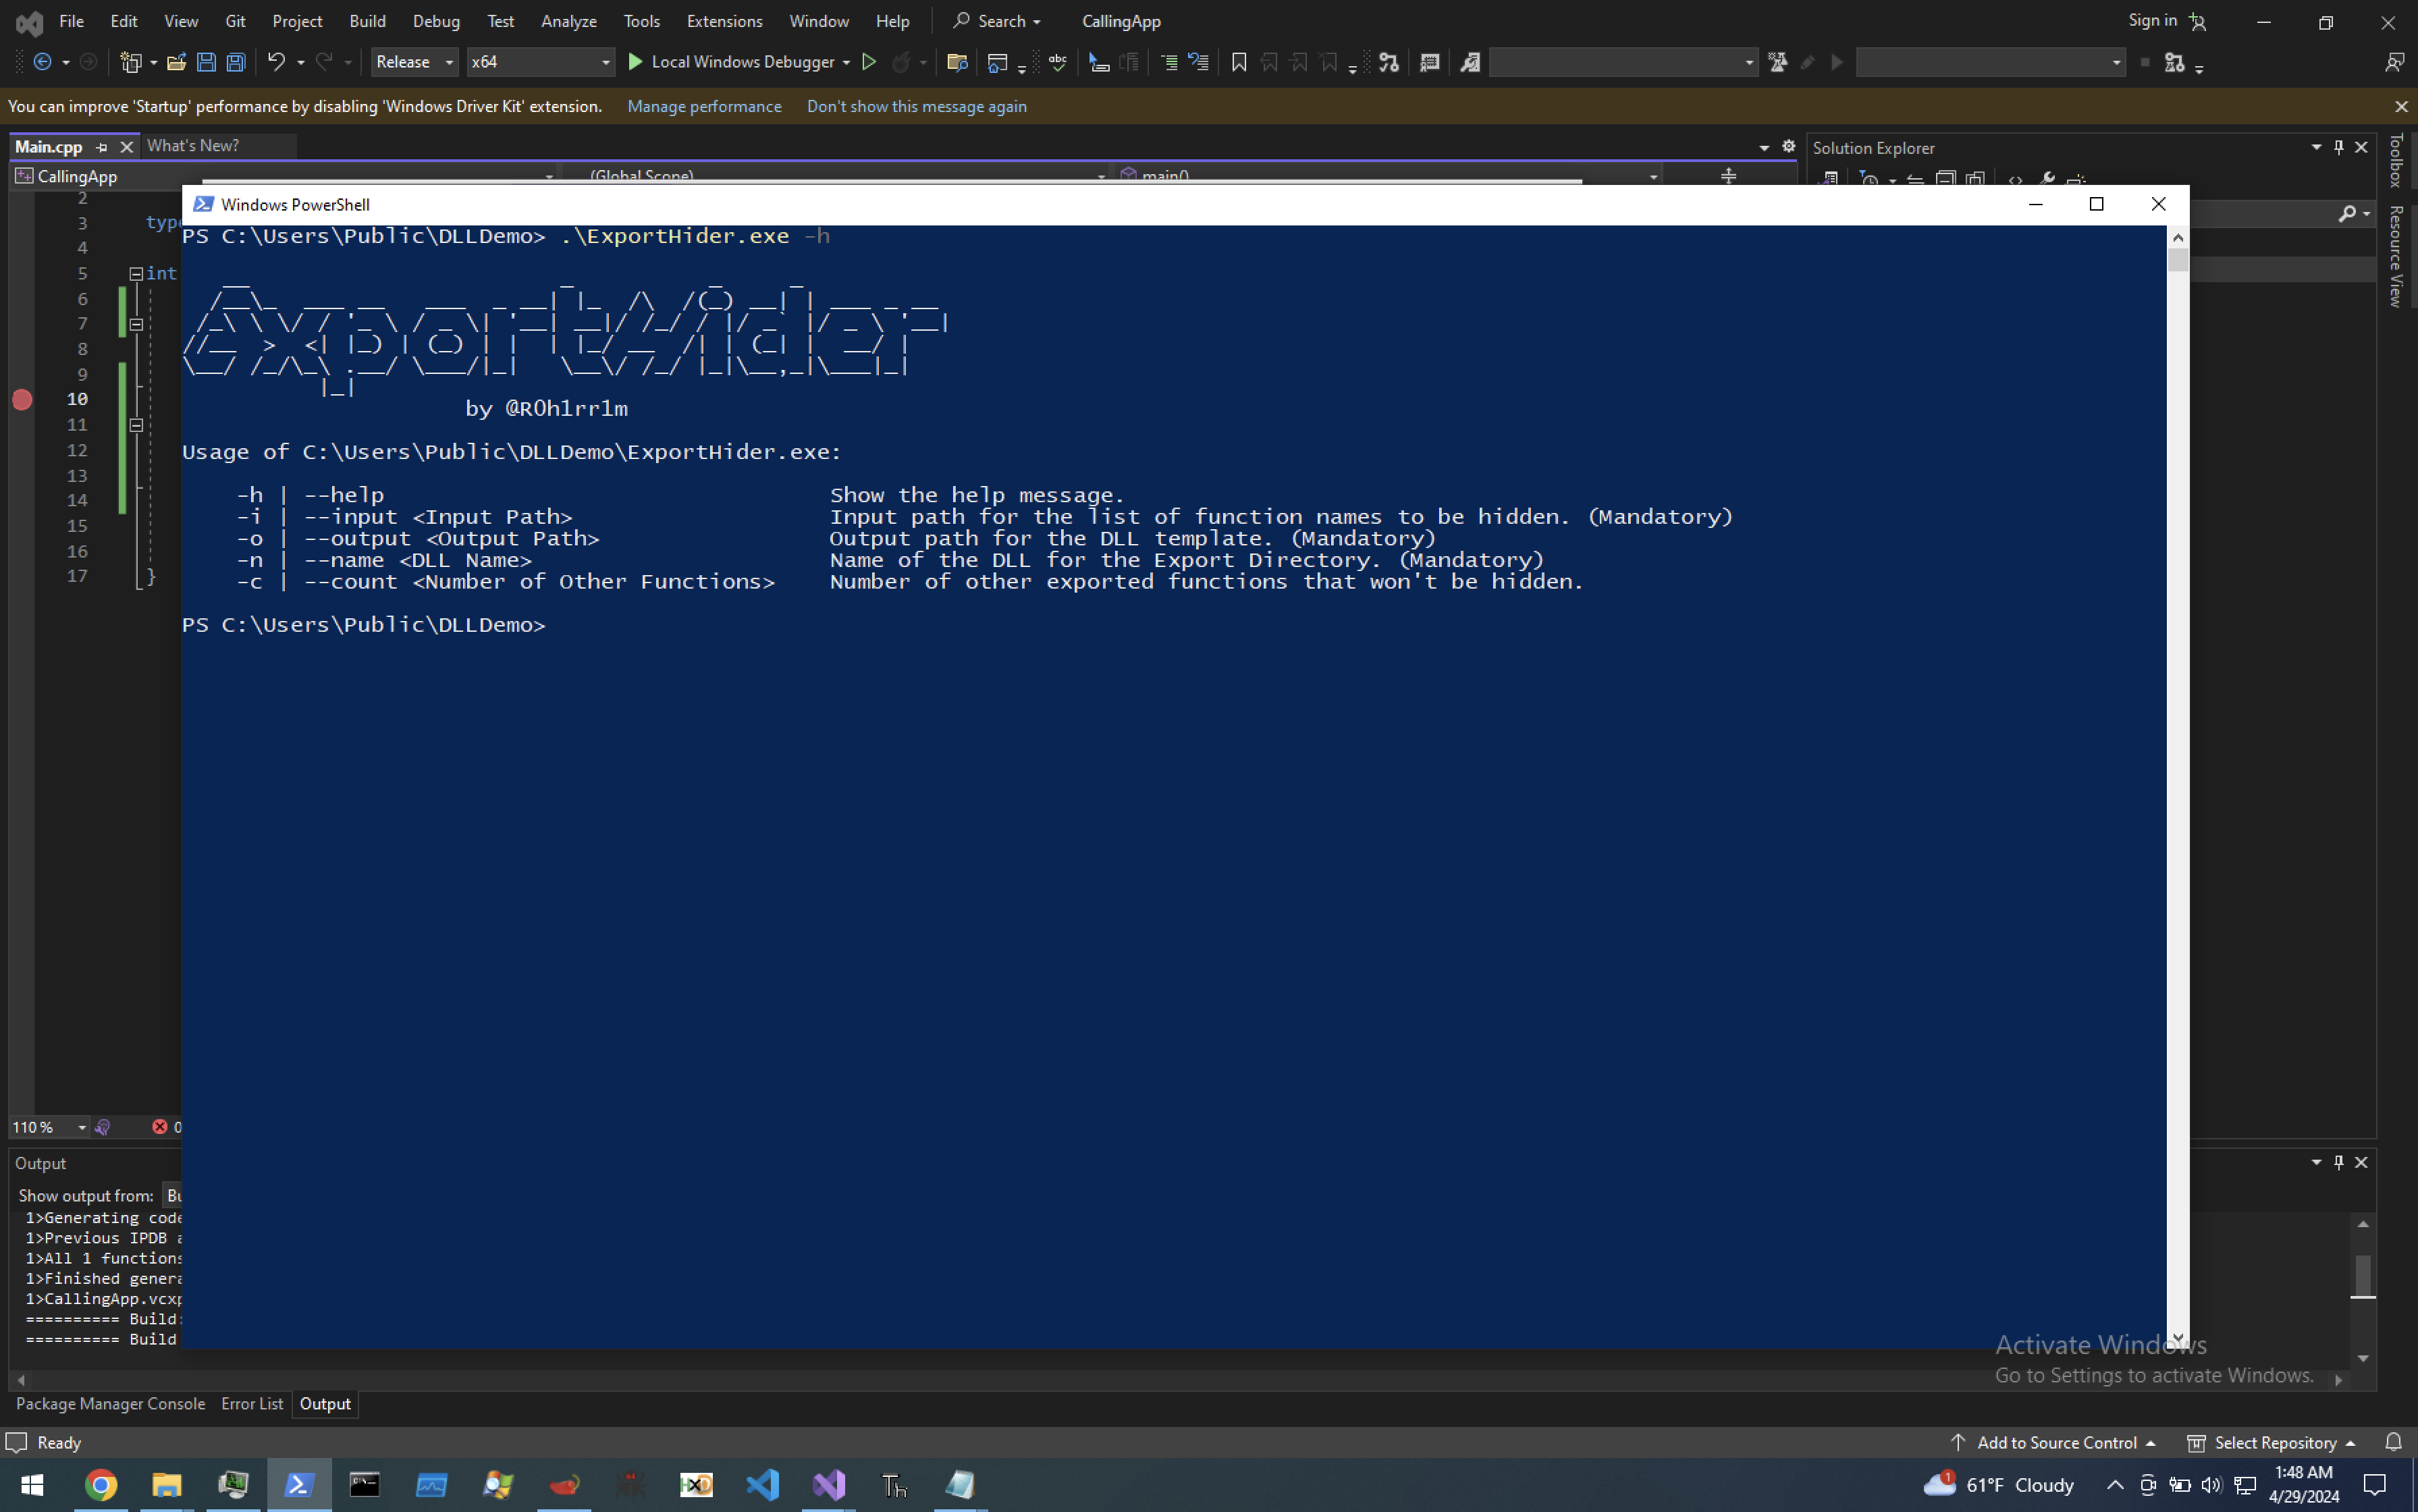 frkngksl/exporthider
ExportHider: Generating Export Table during Runtime to Hide the Exported Functions from the DLL File.
 zxgio/ghidra_stack_strings
A script to detect stack-strings by using emulation (leveraging Unicorn)
 hasherezade/pesieve-go
Golang bindings for PE-sieve
 de4dot/de4dot
.NET deobfuscator and unpacker.
 aftermathlabs/vmp2
Unpack and deobfuscate VMProtect 2 protected binaries with an emulation-based VM explorer, handler profiler, and experimental LLVM recompiler for…
 sentinel-one/peafl64
Static Binary Instrumentation tool for Windows x64 executables
 google/path-auditor
Runtime libc function auditor that detects file access race conditions and symlink vulnerabilities by hooking filesystem syscalls via LD_PRELOAD,…
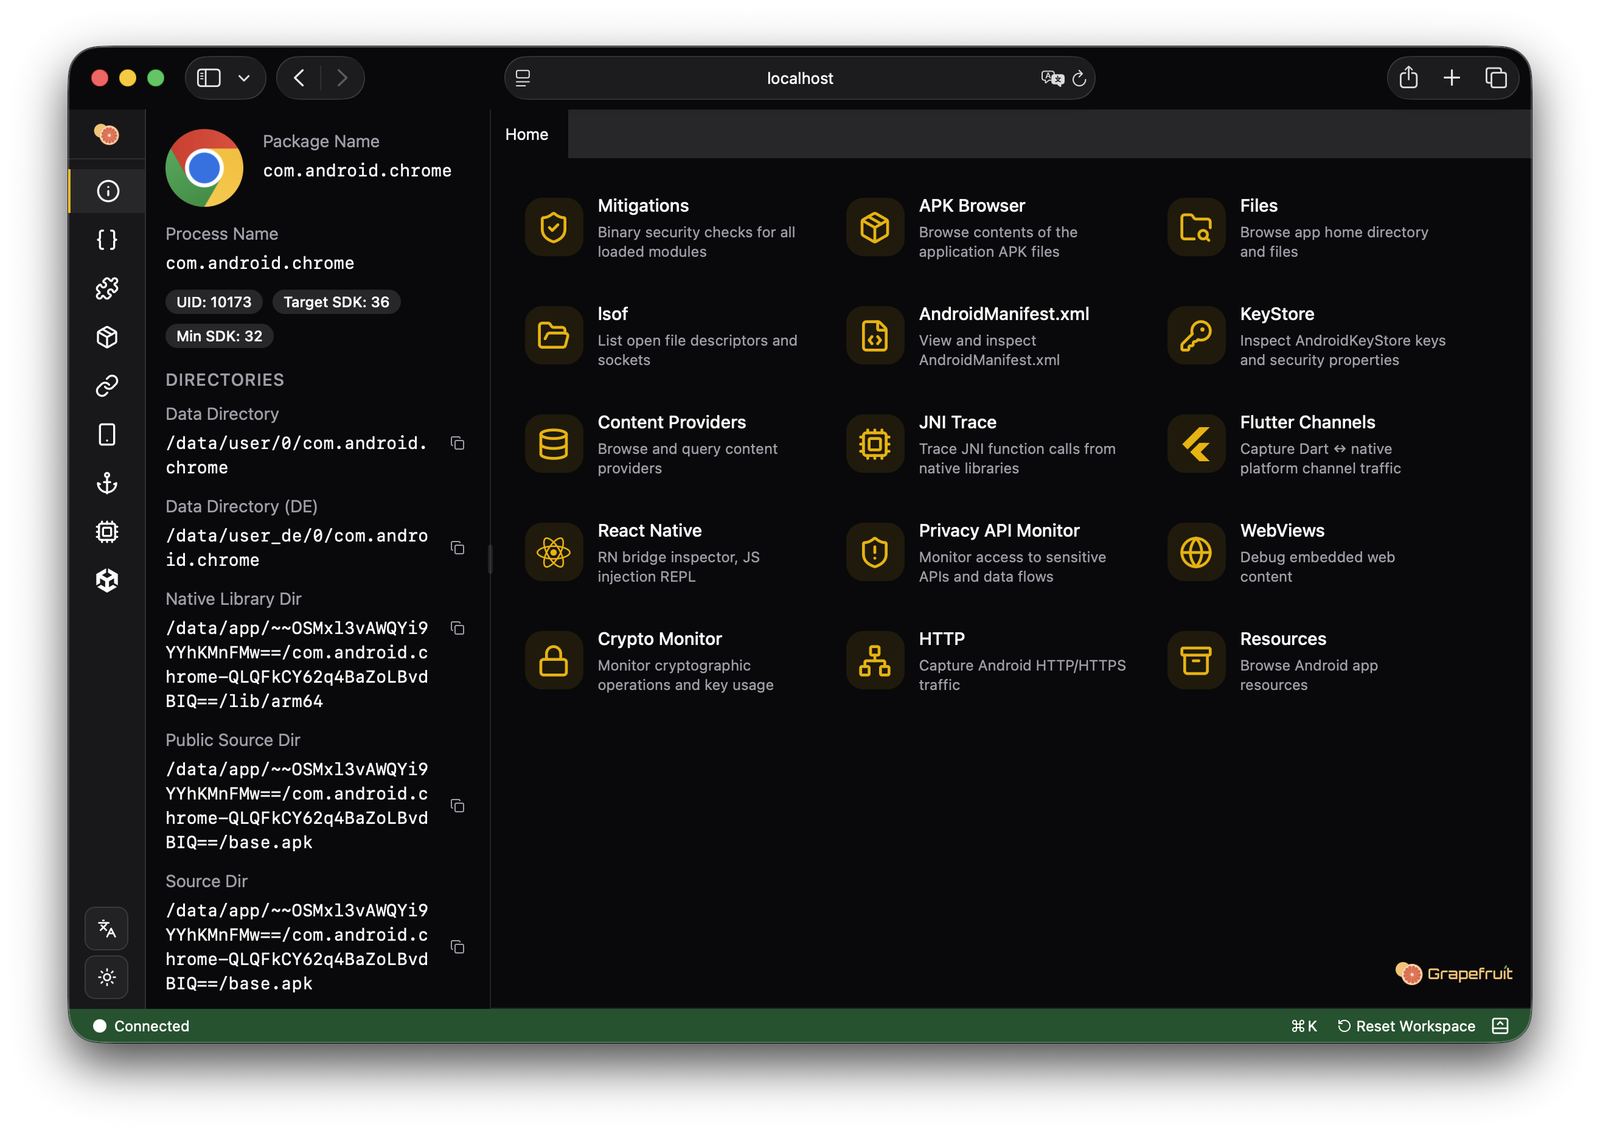 chichou/grapefruit
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
 isecpartners/introspy-ios
Security profiling for blackbox iOS
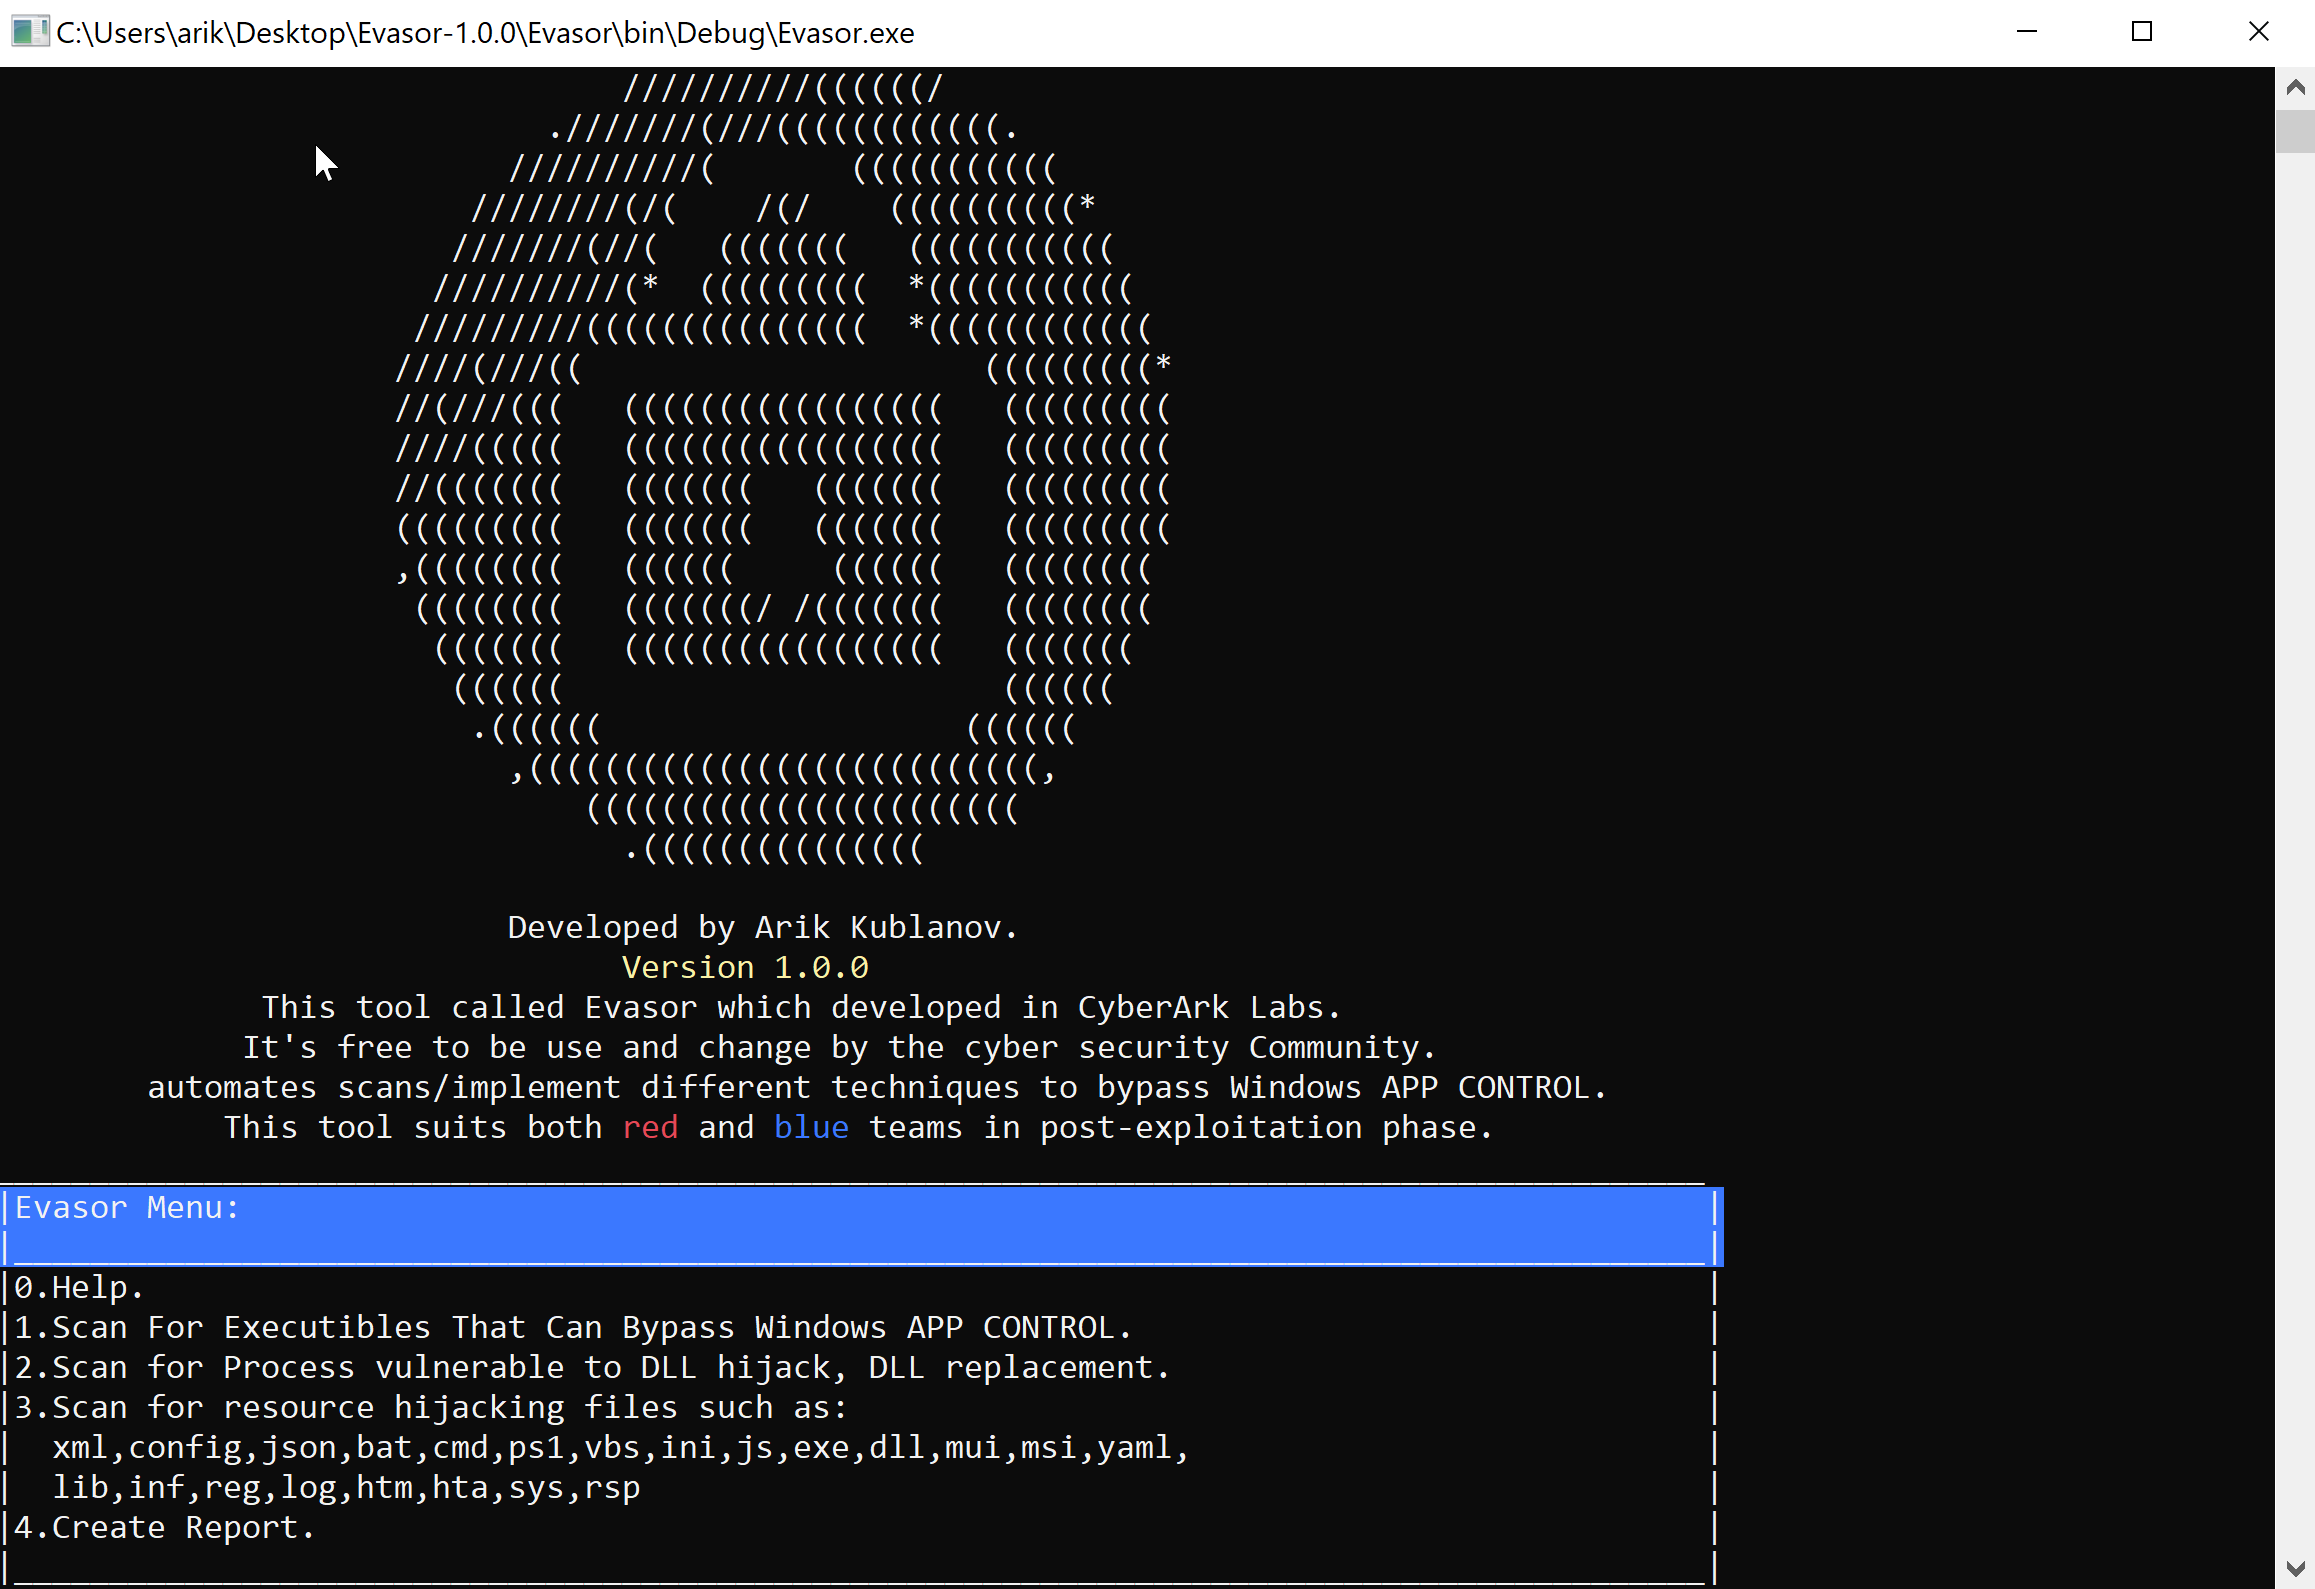 cyberark/evasor
A tool to be used in post exploitation phase for blue and red teams to bypass APPLICATIONCONTROL policies
 fkie-cad/fact_core
Firmware Analysis and Comparison Tool
 fuzzysecurity/fermion
Fermion, an electron wrapper for Frida & Monaco.
 hari-prasaanth/thick-client-pentest-checklist
A OWASP Based Checklist With 80+ Test Cases
 skylined/bugid
Detect, analyze and uniquely identify crashes in Windows applications