

pythia
 nccgroup/pythia
A tool to extract RTTI information from Delphi executables, written in pure Python
binary-analysismalware-analysisreverse-engineering
nccgroup/pythiaA tool to extract RTTI information from Delphi executables, written in pure Python
 0p4n1k/noctyra
AST-based Python code transformation & deobfuscation framework
 ridhinva/linux-kernel-algif-aead-checker
Scanner: CVE-2026-31431 Linux kernel algif_aead Copy Fail vulnerability checker — Python PoC for heap overflow path
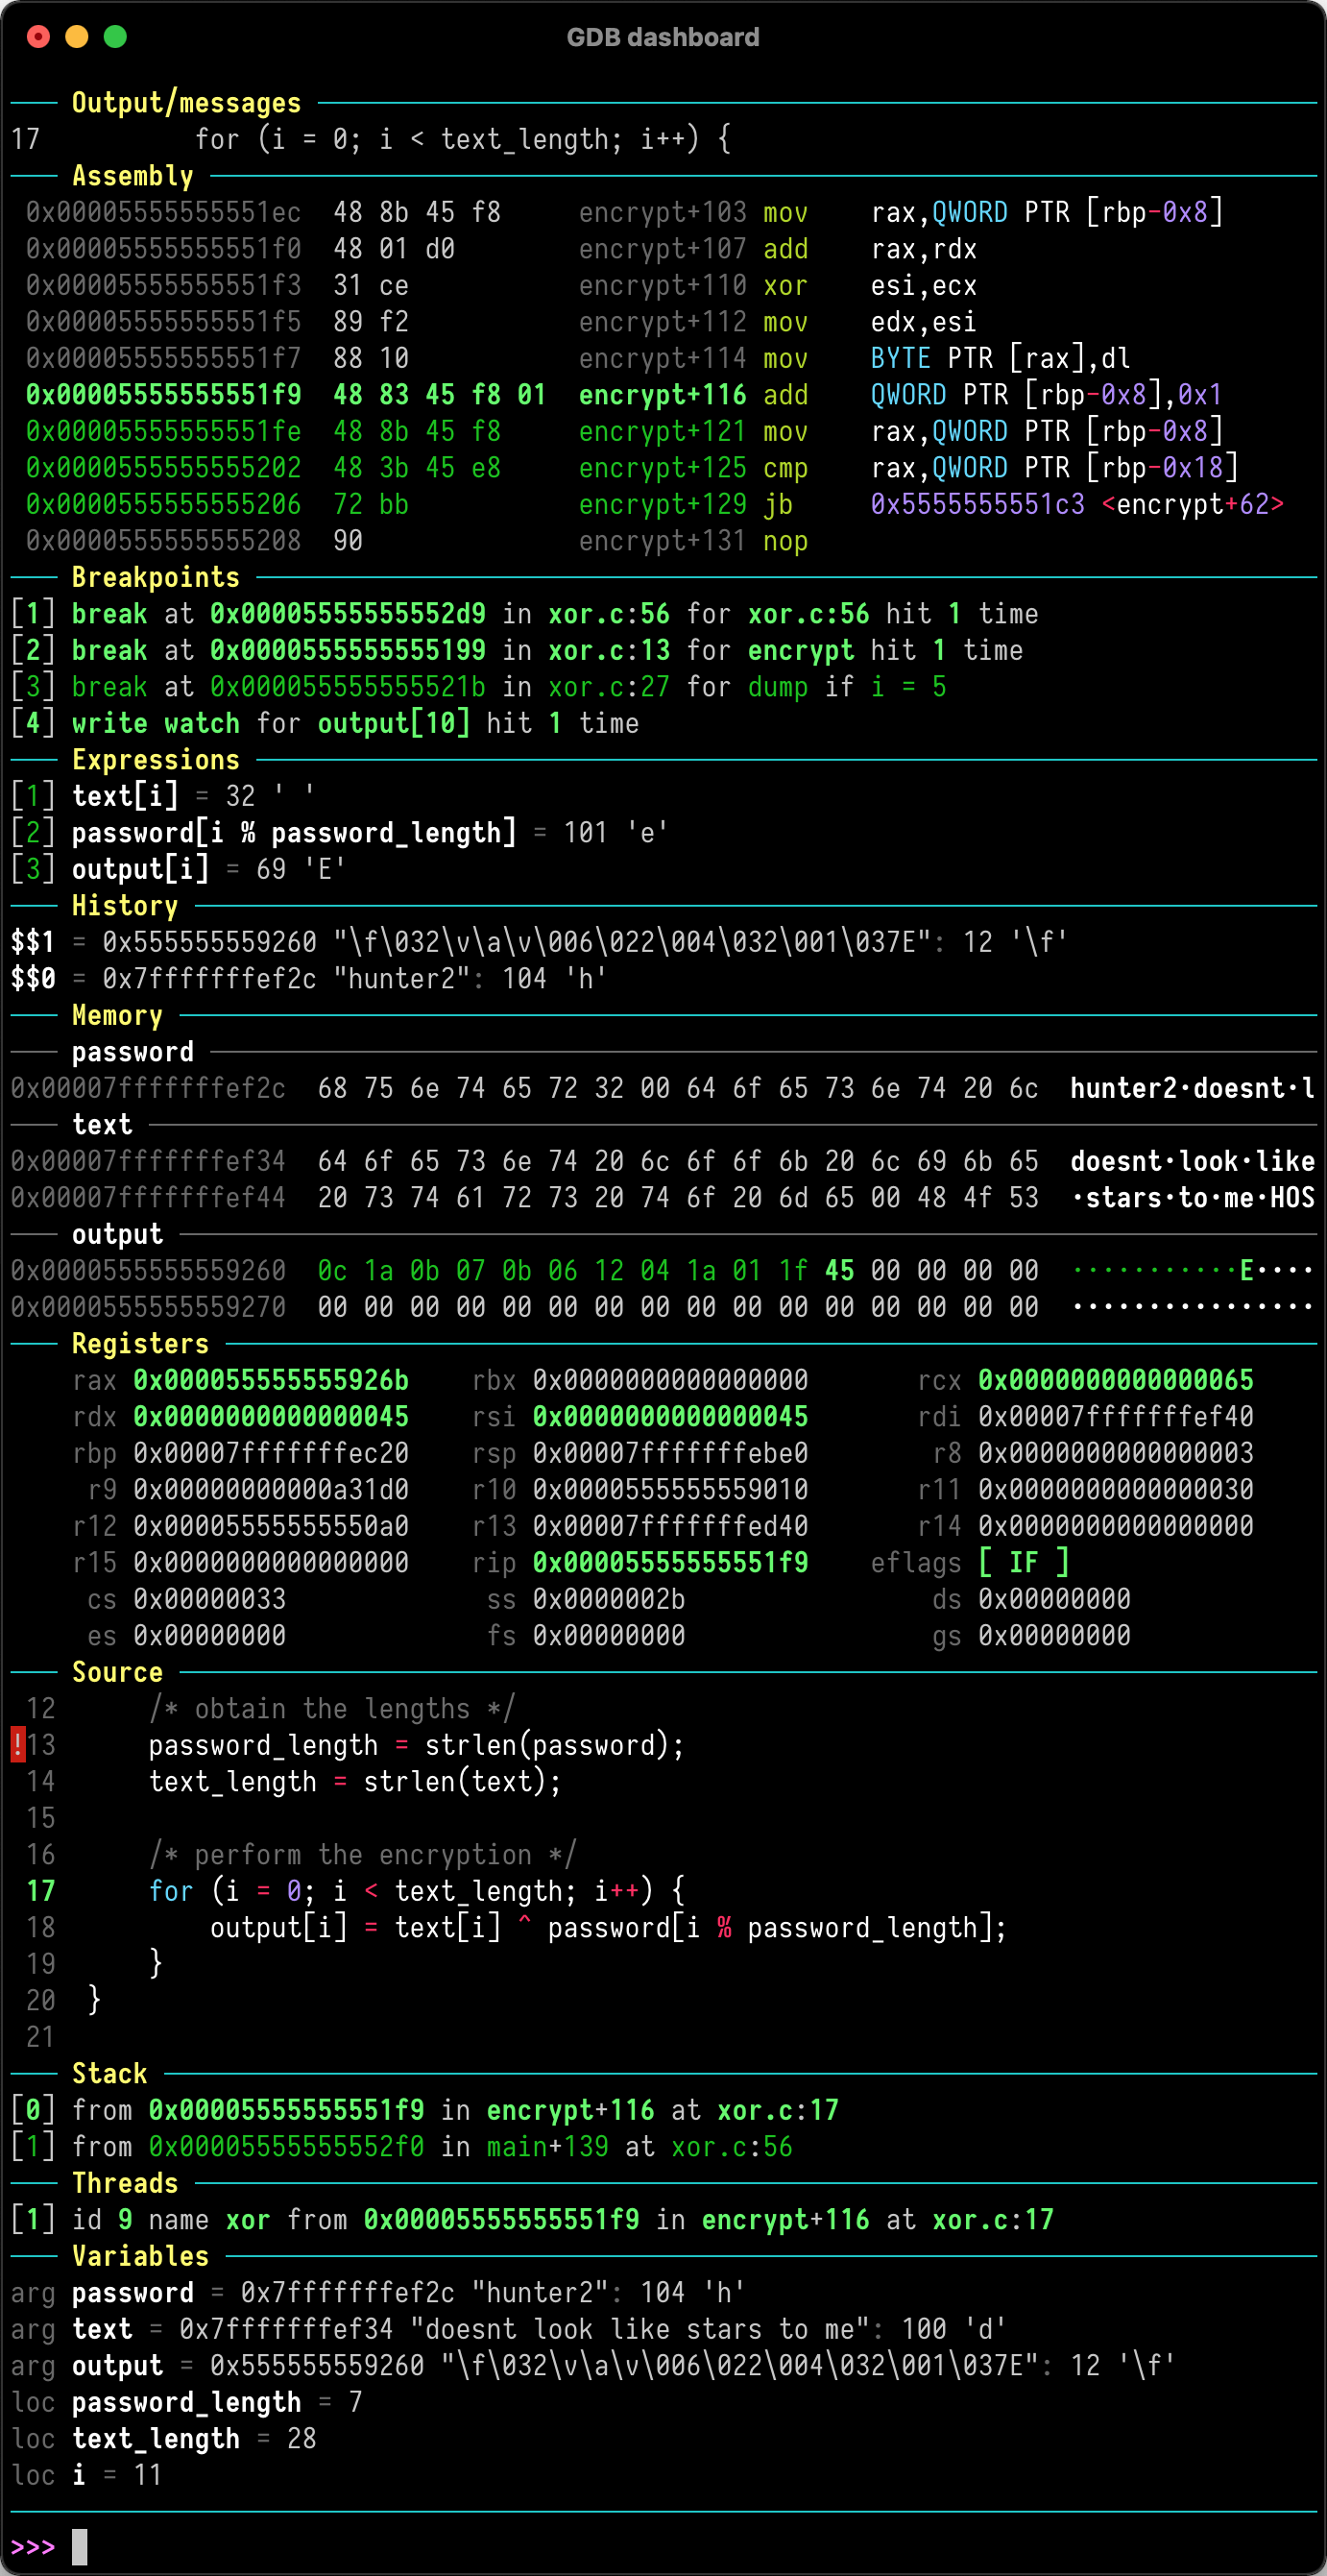 cyrus-and/gdb-dashboard
Modular GDB interface providing a visual dashboard with customizable panels for inspecting registers, source code, assembly, and program state during…
 qybaihe/bla
Hardens binaries, Electron ASAR, JS, WASM, Python, and model files against AI reverse-engineering agents using decoy metadata, budget exhaustion, and…
 erocarrera/pefile
pefile is a Python module to read and work with PE (Portable Executable) files
 snare/voltron
Extensible debugger UI toolkit providing customizable register, disassembly, stack, memory, breakpoint, and backtrace views for LLDB, GDB, VDB, and…
 redballoonsecurity/ofrak
Binary analysis and modification platform for unpacking, analyzing, modifying, and repacking firmware and executable formats via GUI and Python API.
 marin-m/pbtk
A toolset for reverse engineering and fuzzing Protobuf-based apps
 justicerage/gepetto
IDA plugin which queries language models to speed up reverse-engineering
 withsecurelabs/python-exe-unpacker
A helper script for unpacking and decompiling EXEs compiled from python code.
 sentinel-one/cobaltstrikeparser
Python parser for extracting CobaltStrike Beacon configurations from PE files, memory dumps, and C2 URLs using heuristic XOR decryption and…
 eset/ipyida
IPython console integration for IDA Pro
 programa-stic/barf-project
BARF : A multiplatform open source Binary Analysis and Reverse engineering Framework

 openrce/paimei
A reverse engineering framework written in Python.
 clearbluejar/pyghidra-mcp
Python Command-Line Ghidra MCP
 lunixbochs/patchkit
binary patching from Python