dezlock-dump
 dougwithseismic/dezlock-dump
Runtime schema + RTTI extraction tool for Deadlock, CS2, Dota, and others (Source 2). No source2gen required.
binary-analysisdebuggersdynamic-code-analysis+6
97
dougwithseismic/dezlock-dumpRuntime schema + RTTI extraction tool for Deadlock, CS2, Dota, and others (Source 2). No source2gen required.
 pr0me/xtride
N-gram-based type recovery tool for binaries, recovering structures and function signatures from decompiled code with high throughput and actionable…
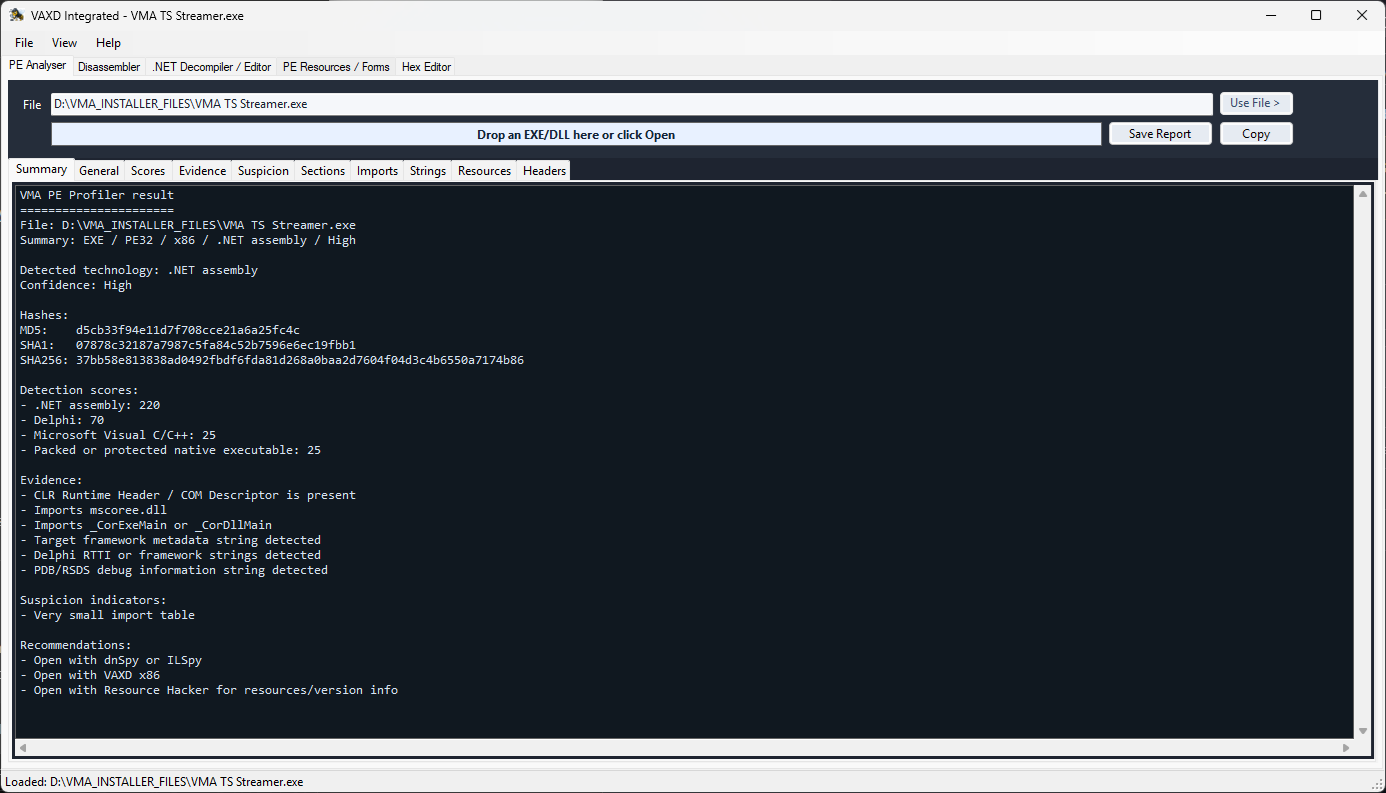 bicurico/vaxd
Lightweight Windows disassembler, PE inspection and patch-assistance tool for native EXE/DLL files.
 malwaretech/phasedump
Python tool for decrypting W32/Phase modules
 prophetcraft/jarhunter
JAR analysis tool for exploring, searching, and extracting specific classes from large JAR files with bytecode search, multi-selection extraction,…
 nikitapbst/cve-2019-6260
Low-level hardware debugging and security assessment tool for ASPEED BMC AHB interfaces. Probes PCIe, LPC, and UART interfaces to read/write…
 sentinel-one/peafl64
Static Binary Instrumentation tool for Windows x64 executables
 yeggor/uefi_retool
A tool for UEFI firmware reverse engineering
 horsicq/detect-it-easy
Program for determining types of files for Windows, Linux and MacOS.
 rr-debugger/rr
Record and replay framework for deterministic debugging of multi-threaded applications, enabling reverse execution, hardware watchpoints, and…
 lcbower33/stegoscan
Automated steganography detection tool that scans websites, web servers, and local directories using AI-driven object/text recognition and deep file…
 madmin3r/unconfuserex
Deobfuscator for ConfuserEx 2.
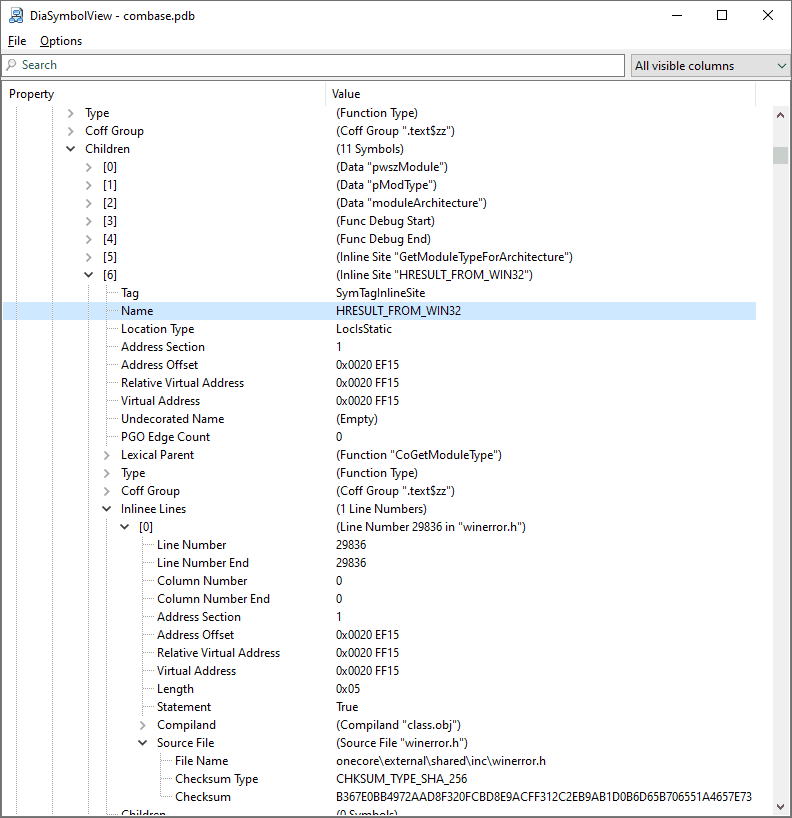 diversenok/diasymbolview
PDB file inspection tool
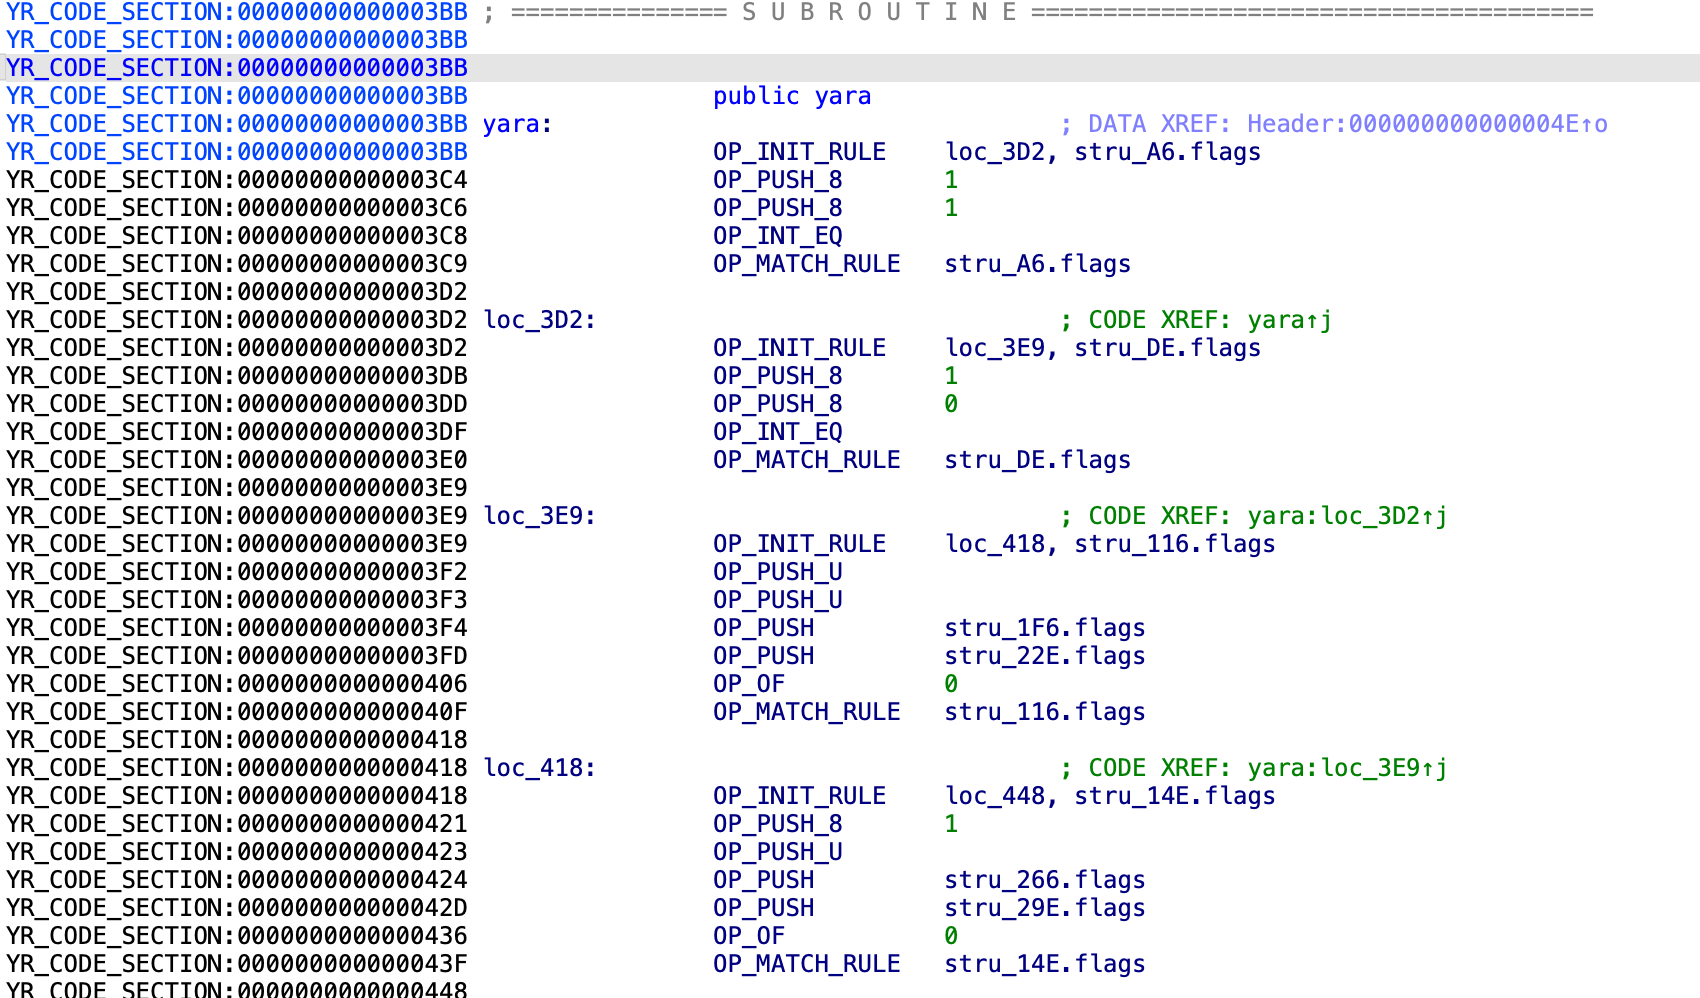 milankovo/yaravm
This repository contains an IDA processor for loading and disassembling compiled yara rules.
 xchwarze/magic-extractor
Universal Windows extraction tool that detects unknown files and routes them to the right bundled extractor.
 deepquantum/dconstruct
A disassembler & experimental decompiler for TLOU2 DC Scripts.
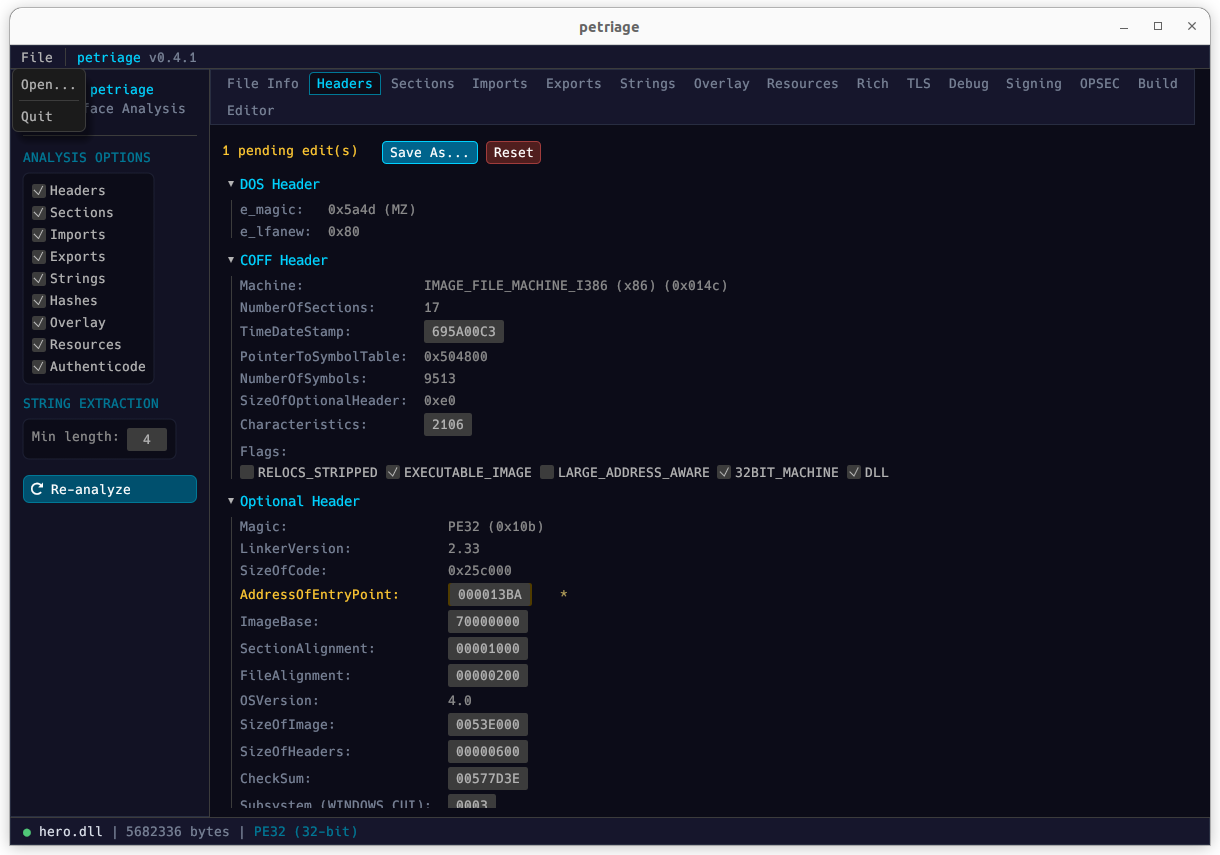 uky007/petriage
PETriage: A symbol-unified PE file reader for triage, built for multi-platform and multi-interface use.