

flopz
 flopz-project/flopz
Pure Python assembler toolkit for creating shellcode, dynamically patching binaries, and instrumenting firmware images for debugging and fuzzing on…
binary-analysisembedded-systems-securityfirmware-analysis+3
14
flopz-project/flopzPure Python assembler toolkit for creating shellcode, dynamically patching binaries, and instrumenting firmware images for debugging and fuzzing on…
 theopolis/uefi-firmware-parser
Parse BIOS/Intel ME/UEFI firmware related structures: Volumes, FileSystems, Files, etc
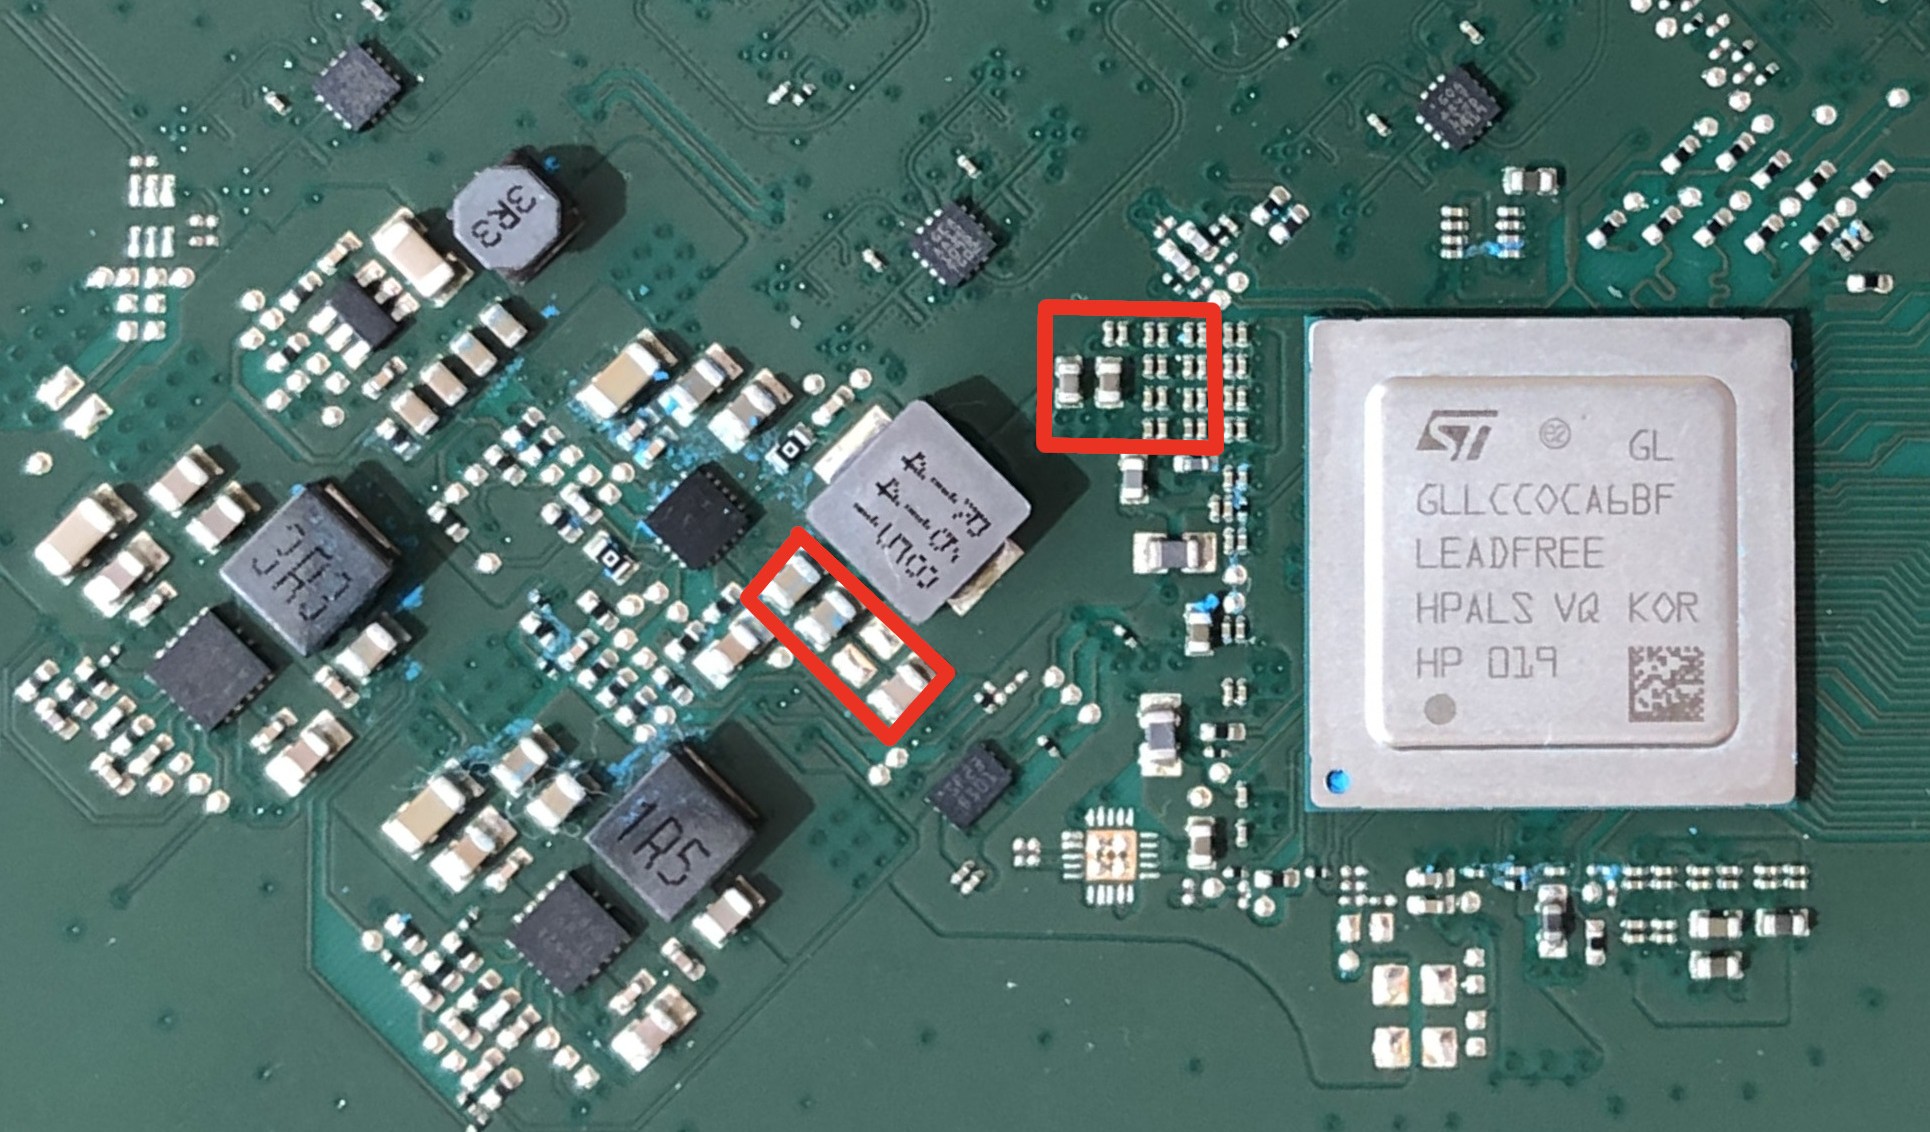 kuleuven-cosic/starlink-fi
Voltage fault-injection modchip for black-box security evaluation of Starlink terminals, bypassing bootloader signature verification to execute…
 tothi/pwn-hisilicon-dvr
Proof-of-concept exploit and vulnerability disclosure for HiSilicon hi3520d DVR/NVR devices. Demonstrates RCE via web interface, backdoor…
 binarly-io/fwhunt
The Binarly Firmware Hunt (FwHunt) rule format was designed to scan for known vulnerabilities in UEFI firmware.
 binarly-io/fwhunt-scan
Tools for analyzing UEFI firmware and checking UEFI modules with FwHunt rules
 seemoo-lab/polypyus
Binary-only firmware historian that learns to locate functions in raw binaries by extracting known functions from similar binaries, enabling fast…
 nccgroup/mtk_bp
Tools for analyzing and reverse engineering MediaTek baseband firmware, including file extraction, symbol parsing, and Ghidra integration for modem…
 mzakocs/qualcomm_baseband_scripts
Collection of scripts for reversing Qualcomm Hexagon baseband / modem firmware
 gdbinit/efiswissknife
IDA plugin to enhance (U)EFI binary reversing with batch analysis, GUID database, and service usage statistics for firmware security research.
 zznop/bn-uefi-helper
Helper plugin for analyzing UEFI firmware
 nnonickreal/openqore
unleash the full power of your BES-based headphones! :)
 superkhung/luadec-tplink
Modified luadec version to decompile TP-Link Archer C7 LUA firmware.
 duality084/cve-2023-33381-mitrastar-gpt-2741gnac
Proof-of-concept exploit for OS command injection (CVE-2023-33381) in MitraStar GPT-2741GNAC routers. Demonstrates bypass of restricted shell via…
 vl4dr/cve-2024-42642
Proof-of-concept exploits for three vulnerabilities in Crucial MX500 SSD firmware update mechanism, enabling buffer overflows and potential code…
 nccgroup/ghidra-mtk-loader
Ghidra loader for the MediaTek md1img modem firmware image format
 badnack/d_link_880_bug
CVE-2017-14948 for D-Link 880 Firmware
 themalwareguardian/uefi-security-research-howyar-sysreturn-netcopy
Post CVE-2024-7344 analysis of Howyar SysReturn NetCopy - reverse engineering notes, vulnerable binaries, vendor correspondence, and proof-of-concept…