
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
44 results
shellex preview

shellex

GitHubtherealdreg/shellex

C-shellcode to hex converter, handy tool for paste & execute shellcodes in IDA PRO, gdb, windbg, radare2, ollydbg, x64dbg, immunity debugger & 010…

binary-analysisdebuggersexploitation+5
113
3 years ago
apkinspector preview

apkinspector

GitHubhoneynet/apkinspector

APKinspector is a powerful GUI tool for analysts to analyze the Android applications.
android-securitybinary-analysiscode-analysis+7
85213 years ago
binder-trace preview

binder-trace

GitHubfoundryzero/binder-trace

Binder Trace is a tool for intercepting and parsing Android Binder messages. Think of it as "Wireshark for Binder".

android-securitybinary-analysisdynamic-analysis-sandboxing+3
7691 year ago
debloat preview

debloat

GitHubsquiblydoo/debloat

A GUI and CLI tool for removing bloat from executables
binary-analysisdigital-forensicsmalware-analysis+1
4563 months ago
octopus preview
Archived

octopus

GitHubfuzzinglabs/octopus

Security Analysis tool for WebAssembly module (wasm) and Blockchain Smart Contracts (BTC/ETH/NEO/EOS)
binary-analysisdynamic-analysis-sandboxingfuzzing+2
4932 years ago
rr preview

rr

GitHubrr-debugger/rr

Record and replay framework for deterministic debugging of multi-threaded applications, enabling reverse execution, hardware watchpoints, and…

binary-analysisdebuggersdynamic-code-analysis
10.7k5 days ago
pe-bear preview

pe-bear

GitHubhasherezade/pe-bear

Portable Executable reversing tool with a friendly GUI
binary-analysisforensicsmalware-analysis+3
3.8k15h 16m ago
Manalyze preview

Manalyze

GitHubjusticerage/manalyze

Static analyzer for PE executables with plugin-based detection of packers, compilers, suspicious imports, cryptographic constants, and ClamAV…

binary-analysismalware-analysisreverse-engineering+2
1.1k23 days ago
tiny_tracer preview

tiny_tracer

GitHubhasherezade/tiny_tracer

Intel Pin-based tracer for API calls, syscalls, and instructions with anti-debug evasion, used for malware analysis and reverse engineering of packed…

api-securitybinary-analysisdynamic-analysis-sandboxing+2
1.7k3 months ago
ReArk preview

ReArk

GitHublkimuk/reark

An intelligent reverse engineering analysis tool designed for multiple target platforms, currently supporting HarmonyOS (HAP/APP/ABC) and Android…
ai-assisted-reversingandroid-securitybinary-analysis+6
4143 days ago
ecdsa-private-key-recovery preview

ecdsa-private-key-recovery

GitHubyadyvazifeh1oz92/ecdsa-private-key-recovery

Perform ECDSA and DSA nonce reuse private key recovery attacks to analyze signature vulnerabilities and recover private keys from blockchain…
binary-analysiscryptographyeducation+1
52111 days ago
applepie preview

applepie

GitHubgamozolabs/applepie

A hypervisor for fuzzing built with WHVP and Bochs
binary-analysisdynamic-analysis-sandboxingfuzzing+2
3857 years ago
vmprotect-research preview

vmprotect-research

GitHubrasetsuu/vmprotect-research

Generalized VMProtect devirtualizer supporting versions 1.x–3.x. Standalone CLI tool and Ghidra plugin for automated bytecode decoding, handler…
binary-analysisbinary-exploitationdebuggers+6
613 months ago
gobee preview

gobee

GitHubboratanrikulu/gobee

Write your BPF programs in Go, not C. gobee transpiles a Go subset to BPF C and generates typed cilium/ebpf bindings.
binary-analysiscode-analysisdevsecops+3
3484 months ago
vmlinux-to-elf preview

vmlinux-to-elf

GitHubmarin-m/vmlinux-to-elf

A tool to recover a fully analyzable .ELF from a raw kernel, through extracting the kernel symbol table (kallsyms)

binary-analysisembedded-systems-securityfirmware-analysis+1
1.8k3 months ago
keystone preview

keystone

GitHubkeystone-engine/keystone

Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…

binary-analysisbinary-exploitationgeneral-purpose-utilities+4
2.6k2 months ago
FACT_core preview

FACT_core

GitHubfkie-cad/fact_core

Firmware Analysis and Comparison Tool
binary-analysisdynamic-analysis-sandboxingembedded-systems-security+9
1.5k10 days ago
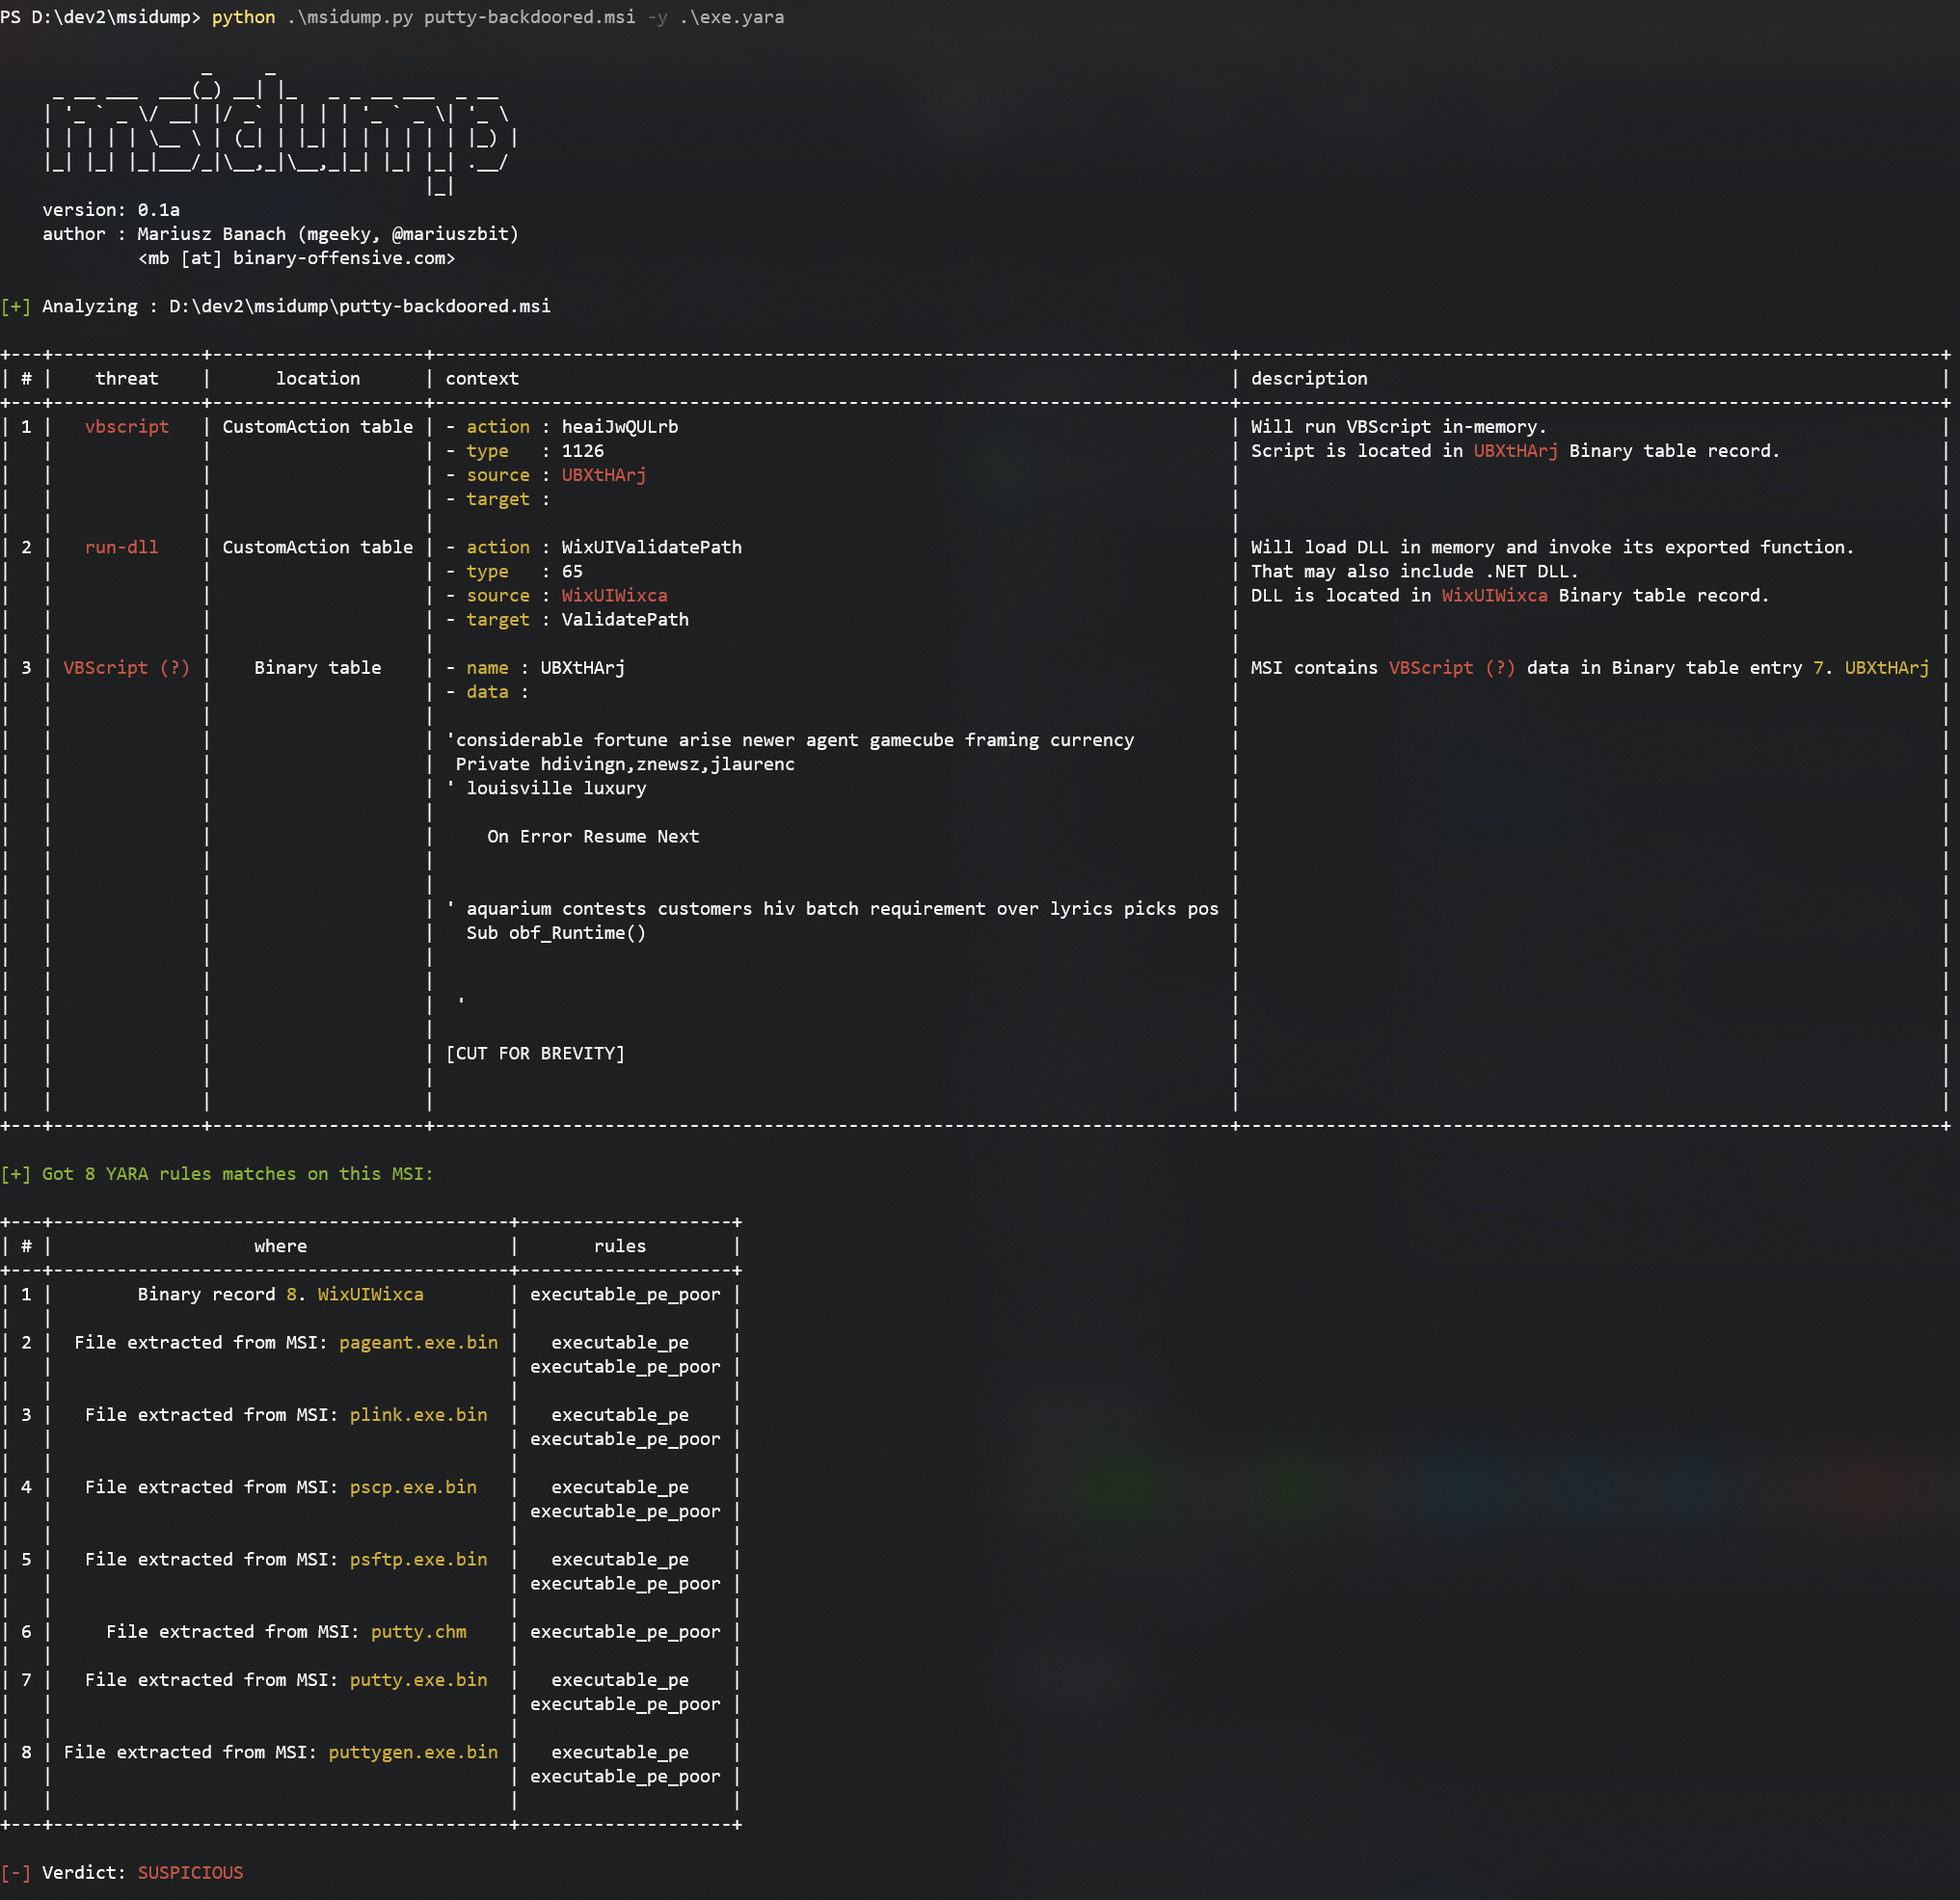
msidump preview

msidump

GitHubmgeeky/msidump

MSI Dump - a tool that analyzes malicious MSI installation packages, extracts files, streams, binary data and incorporates YARA scanner.

binary-analysisforensicsmalware-analysis+1
2323 years ago
Previous123Next