Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
1171 results
Bypass-Sandbox-Evasion preview

Bypass-Sandbox-Evasion

GitHubzeromemoryex/bypass-sandbox-evasion

C++ tool that patches Windows API calls to bypass sandbox RAM size checks, enabling malware to evade detection in isolated analysis environments.

anti-botbinary-analysisids-ips-evasion+1
141
3 years ago
wslink-vm-analyzer preview

wslink-vm-analyzer

GitHubeset/wslink-vm-analyzer

WslinkVMAnalyzer is a tool to facilitate analysis of code protected by a virtual machine featured in Wslink malware
binary-analysiscode-analysismalware-analysis+1
494 years ago
GoRedOps preview
Archived

GoRedOps

GitHubkiexitdispatcher/goredops

🦫 | GoRedOps is a repository dedicated to gathering and sharing advanced techniques and offensive malware for Red Team, with a specific focus on…

anti-botbinary-analysiscommand-and-control+9
6701 year ago
x64dbg preview

x64dbg

GitHubx64dbg/x64dbg

An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.

ai-assisted-reversingbinary-analysisbinary-exploitation+7
49.6k8h 56m ago
capstone preview

capstone

GitHubcapstone-engine/capstone

Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…

ai-assisted-reversingbinary-analysisbinary-exploitation+7
9.0k1 day ago
capa preview

capa

GitHubmandiant/capa

Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…

ai-assisted-reversingbinary-analysiscode-analysis+10
6.2k17 days ago
Z0FCourse_ReverseEngineering preview

Z0FCourse_ReverseEngineering

GitHub0xz0f/z0fcourse_reverseengineering

Structured reverse engineering course covering x64 Windows binaries, assembly, debugging, and malware analysis. Designed for beginners to…
binary-analysisdebuggerseducation+3
5.9k2 months ago
speakeasy preview

speakeasy

GitHubmandiant/speakeasy

Windows malware emulation framework that executes binaries, drivers, and shellcode in a modeled runtime, emulating APIs, process/thread behavior,…
binary-analysisdynamic-analysis-sandboxingmalware-analysis+1
2.1k10 days ago
malware_training_vol1 preview

malware_training_vol1

GitHubhasherezade/malware_training_vol1

Materials for Windows Malware Analysis training (volume 1)
binary-analysiseducationforensics+4
2.1k2 years ago
libpeconv preview

libpeconv

GitHubhasherezade/libpeconv

Custom PE loading and manipulation library for manual mapping, IAT hooking, memory dumping, and rebuilding imports for malware analysis and reverse…

binary-analysismalware-analysismemory-forensics+4
1.4k5 months ago
tiny_tracer preview

tiny_tracer

GitHubhasherezade/tiny_tracer

Intel Pin-based tracer for API calls, syscalls, and instructions with anti-debug evasion, used for malware analysis and reverse engineering of packed…
api-securitybinary-analysisdynamic-analysis-sandboxing+2
1.7k3 months ago
Process-Dump preview

Process-Dump

GitHubglmcdona/process-dump

Windows tool for dumping malware PE files from memory back to disk for analysis.

binary-analysisforensicsmalware-analysis+2
1.9k3 years ago
Malware-analysis-and-Reverse-engineering preview

Malware-analysis-and-Reverse-engineering

GitHubdump-guy/malware-analysis-and-reverse-engineering

Some of my publicly available Malware analysis and Reverse engineering.

binary-analysisctfcurated-resources+8
9632 years ago
hashdb preview

hashdb

GitHuboalabs/hashdb

Assortment of hashing algorithms used in malware
binary-analysishash-analysismalware-analysis+2
41116 days ago
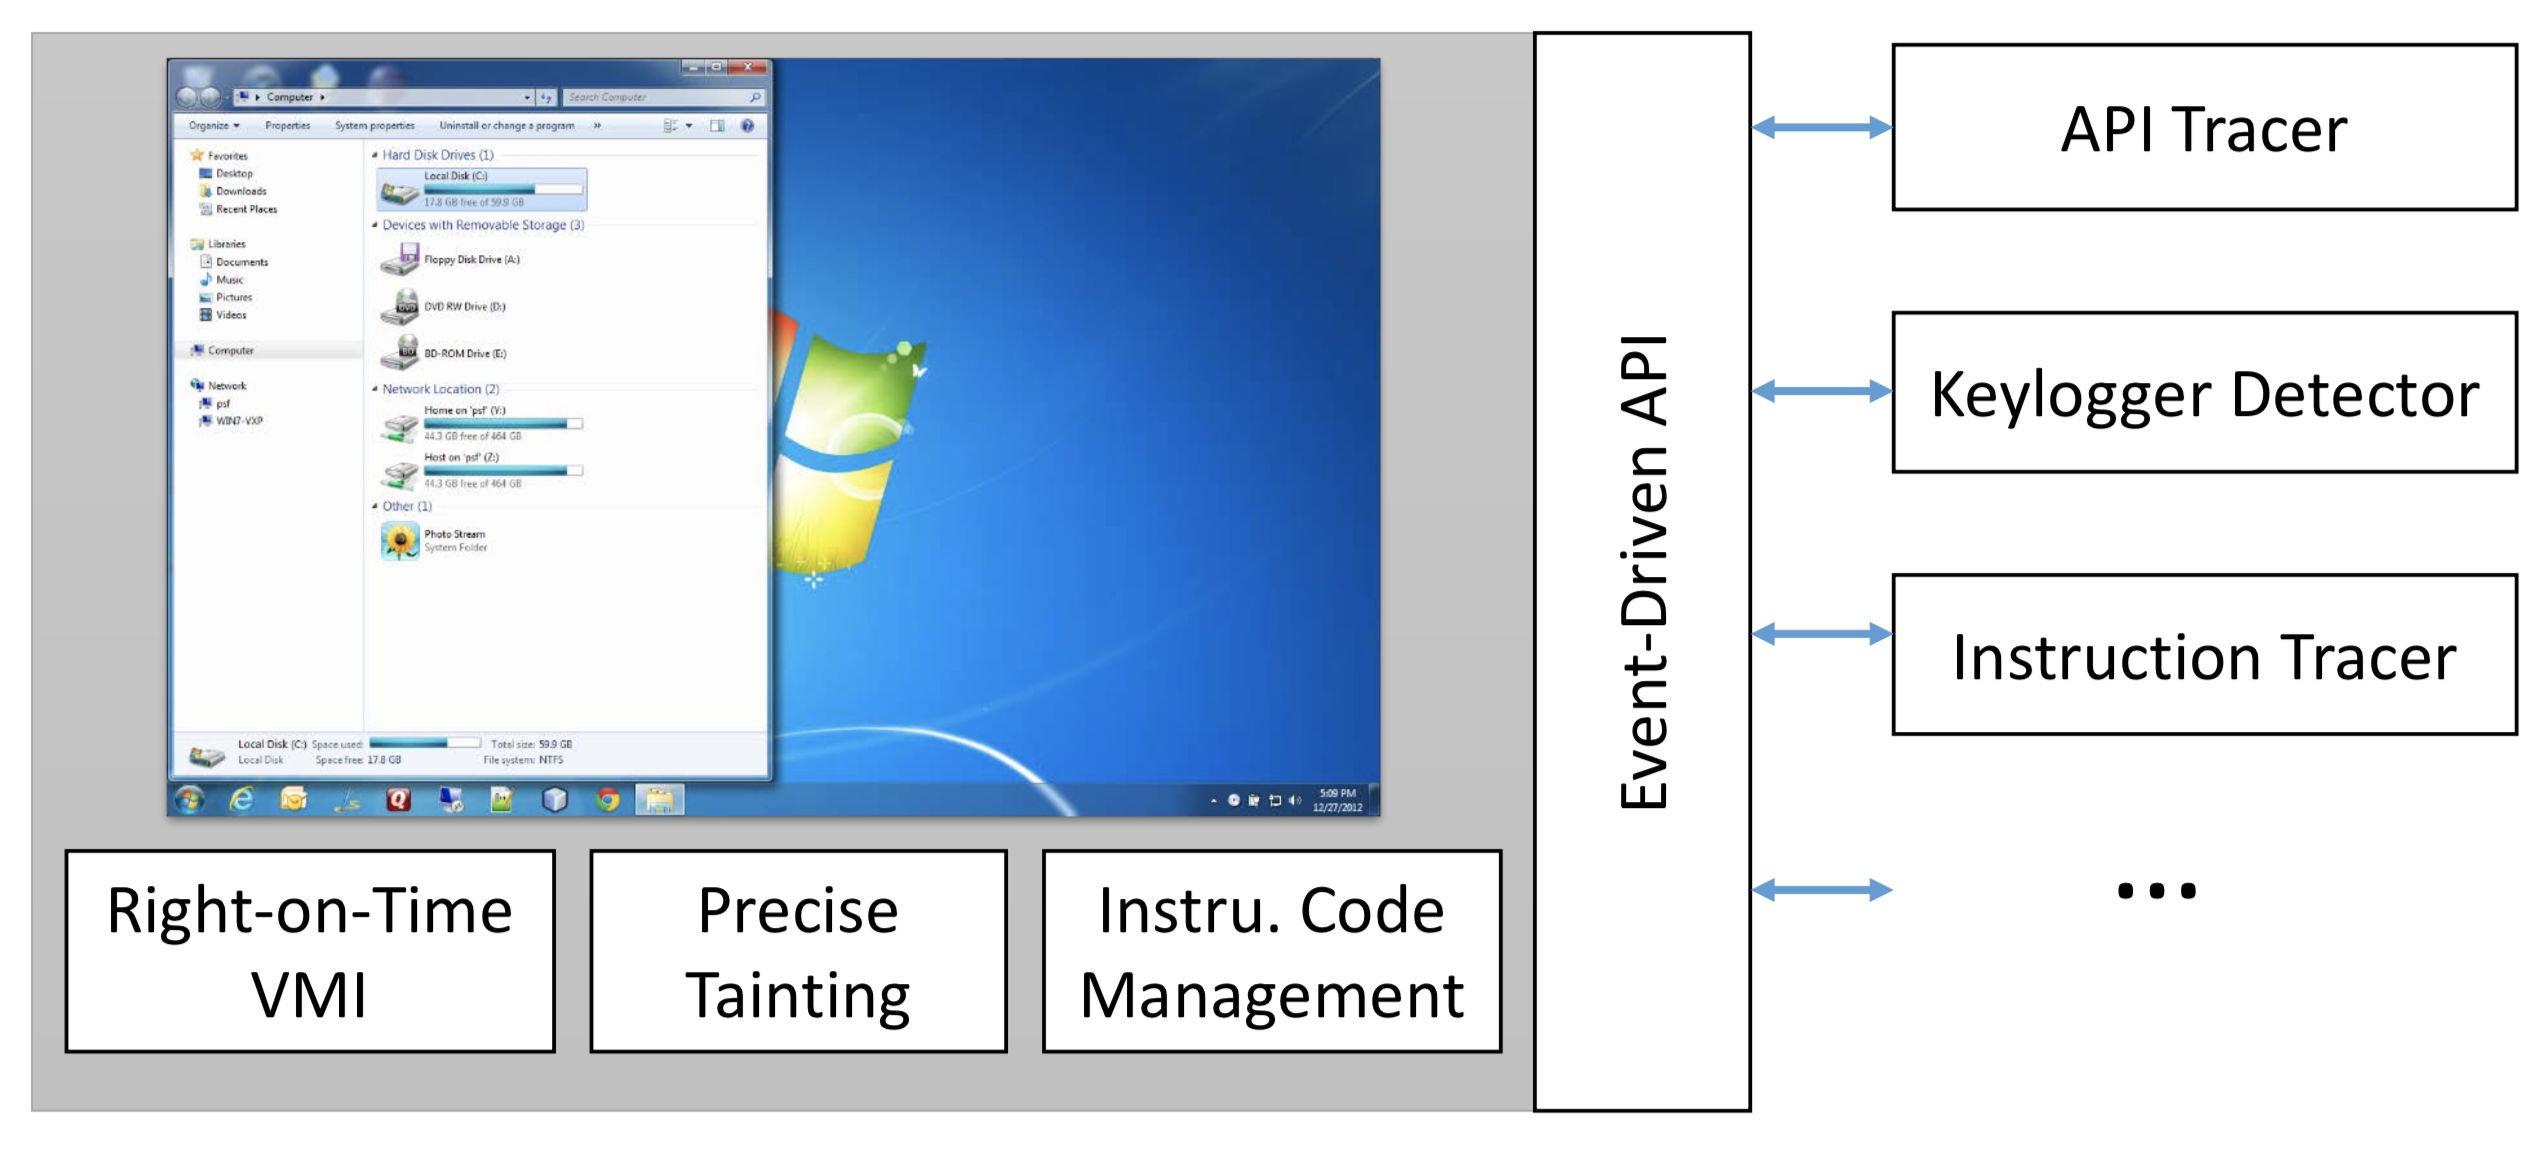
DECAF preview

DECAF

GitHubdecaf-project/decaf

DECAF (short for Dynamic Executable Code Analysis Framework) is a binary analysis platform based on QEMU. This is also the home of the DroidScope…
android-securitybinary-analysisdynamic-analysis-sandboxing+2
8415 years ago
flare-emu preview

flare-emu

GitHubmandiant/flare-emu

Scriptable binary emulation framework integrating IDA Pro/Radare2 with Unicorn engine for automated malware analysis, string decryption, and code…

binary-analysisdynamic-analysis-sandboxingmalware-analysis+1
9551 year ago
Karta preview

Karta

GitHubcheckpointsw/karta

IDA Python plugin for fast, location-driven matching of open-source library symbols in binaries, enabling efficient reverse engineering and…
binary-analysisreverse-engineeringstatic-analysis+1
9114 years ago
stringsifter preview

stringsifter

GitHubmandiant/stringsifter

A machine learning tool that ranks strings based on their relevance for malware analysis.

binary-analysismachine-learningmalware-analysis+2
7633 years ago
Previous123…66Next