

blutter
 worawit/blutter
Flutter Mobile Application Reverse Engineering Tool
android-securitybinary-analysismobile-security+1
worawit/blutterFlutter Mobile Application Reverse Engineering Tool
 yukonga/ghostlock-app
GhostLock One-Tap Execution App (CVE-2026-43499)
 codinggay/blackdex
Android APK unpacker that dumps DEX files from running or installed apps on Android 5.0–12 without root, Xposed, or Frida, supporting deep unpacking…
 mg1937/asc
Fast Android APK decompiler front-end that queries compiled DEX artifacts directly, extracting classes and cross-references in milliseconds without…
 iddoeldor/frida-snippets
Hand-crafted Frida examples
 amlweems/xzbot
notes, honeypot, and exploit demo for the xz backdoor (CVE-2024-3094)
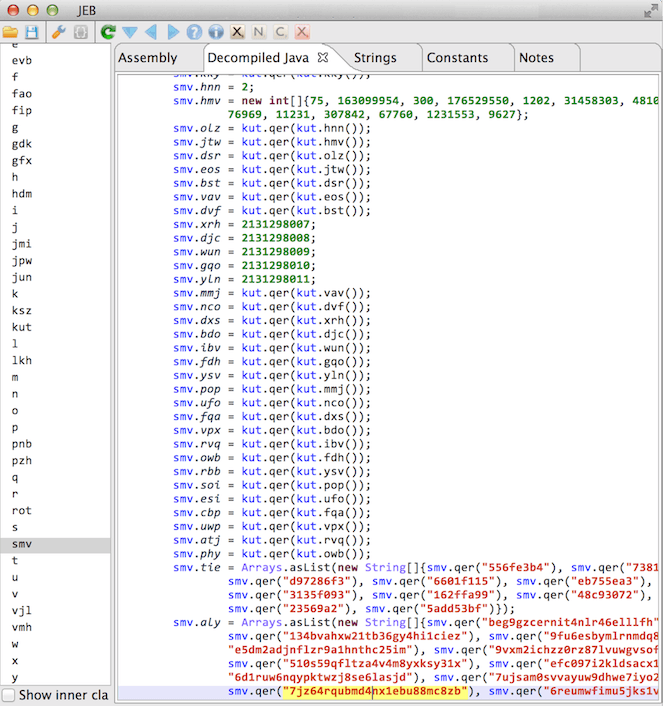 calebfenton/simplify
Android virtual machine and deobfuscator
 bmax121/kernelpatch
Patching and hooking the Linux kernel with only a stripped Linux kernel image.
 apklab/apklab
Android Reverse-Engineering Workbench for VS Code
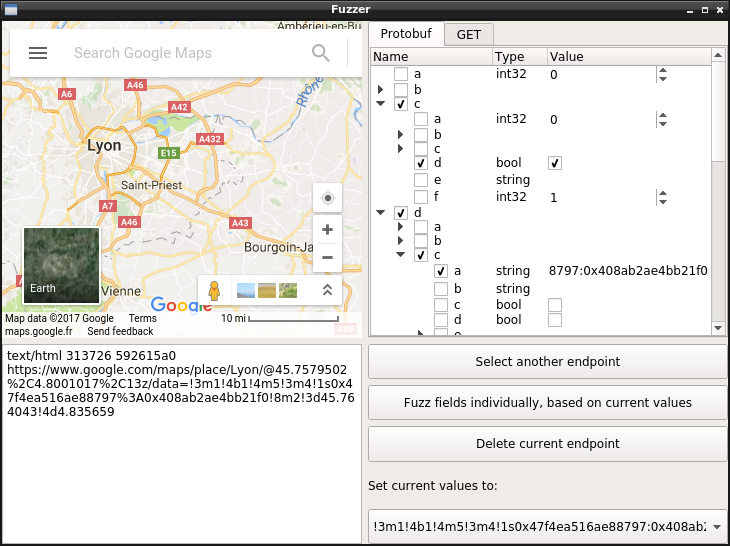 marin-m/pbtk
A toolset for reverse engineering and fuzzing Protobuf-based apps
 0xdea/frida-scripts
A collection of my Frida instrumentation scripts to reverse engineer mobile apps and more.
 nowsecure/r2frida
Radare2 and Frida better together.
 ax/apk.sh
Makes reverse engineering Android apps easier, automating repetitive tasks like pulling, decoding, rebuilding and patching an APK.
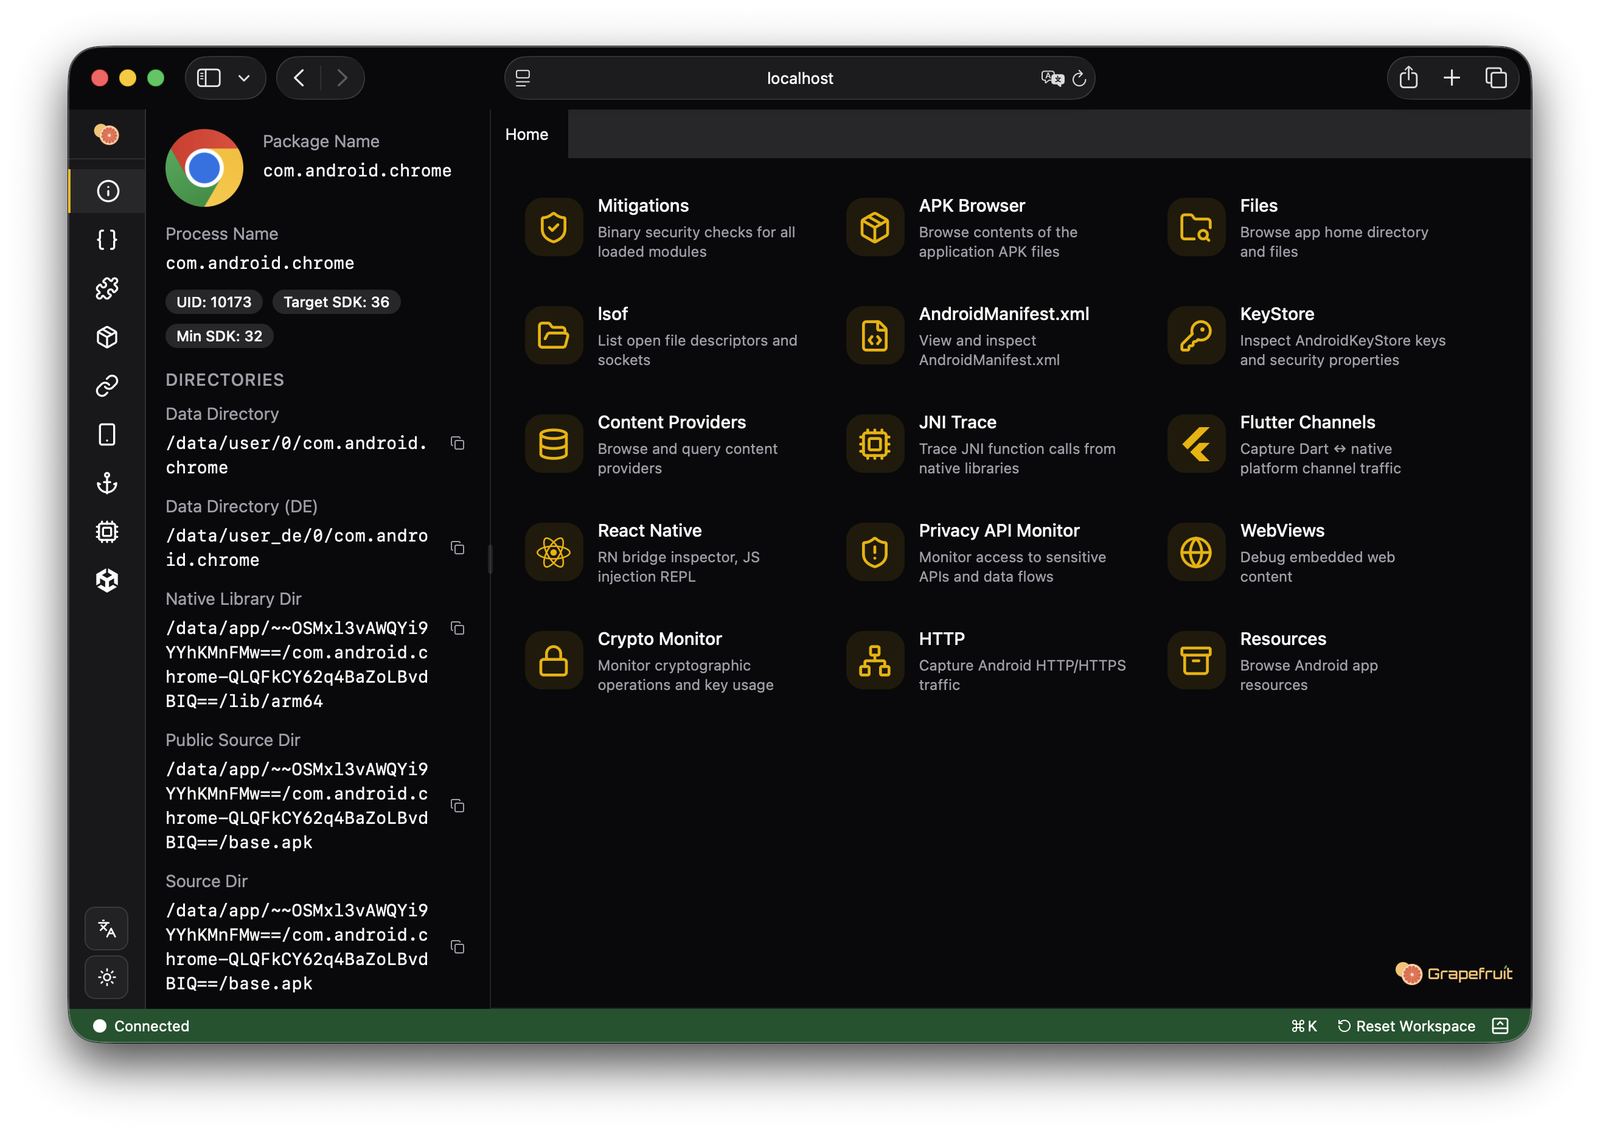 chichou/grapefruit
Open-source mobile security testing suite for iOS and Android. Previously Passionfruit
 igio90/dwarf
Full featured multi arch/os debugger built on top of PyQt5 and frida
 dere-ad2001/frida-labs
The repo contains a series of challenges for learning Frida for Android Exploitation.
 lkimuk/reark
An intelligent reverse engineering and AI-assisted analysis tool for HarmonyOS NEXT (HAP/APP/ABC), Android (APK/AAB), iOS (IPA), and native…
 reversenseorg/dexcalibur
[Official] Android reverse engineering tool focused on dynamic instrumentation automation leveraging Frida. It disassembles dex, analyzes it…