

GateX
 abraxas/gatex
FortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…
binary-analysisbinary-exploitationcryptography+8
1
abraxas/gatexFortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…
 murf-xd/cve-2023-20768
Android kernel CVE analysis and PoC for a MediaTek ION allocator type confusion, covering root-cause diffing, unprivileged trigger, and…
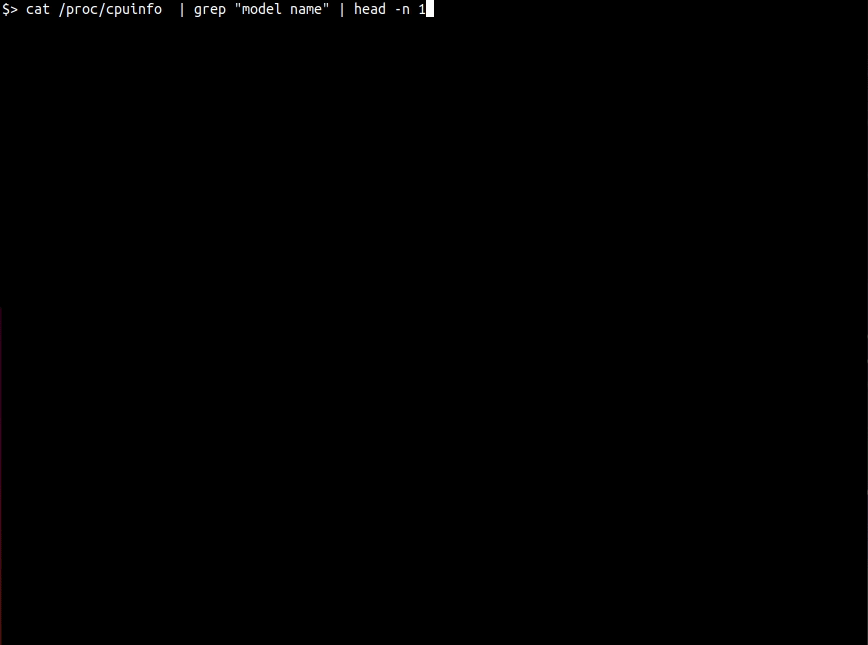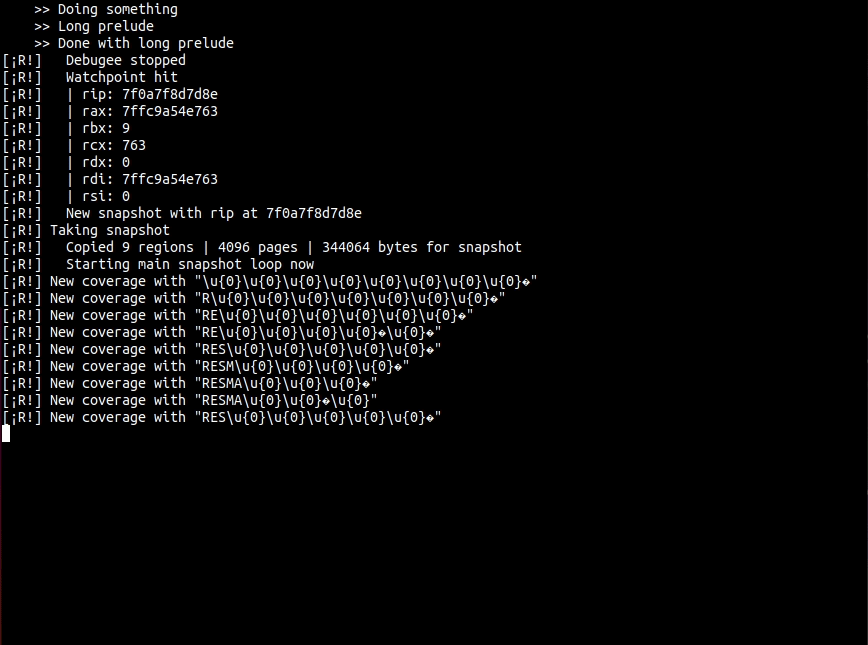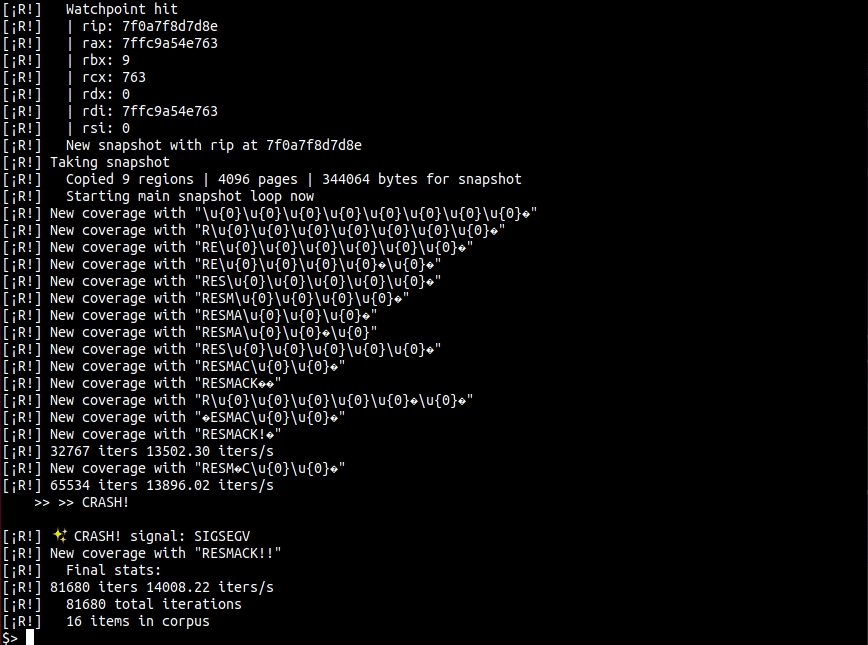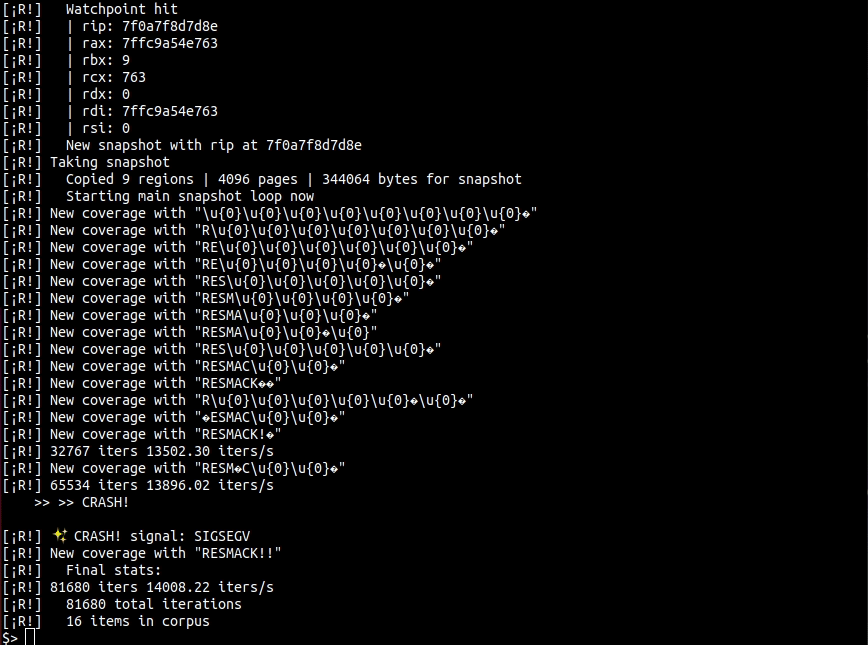
 d0c-s4vage/resmack-fuzz-test
This is an experimental project for [resmack](https://gitlab.com/d0c-s4vage/resmack) to figure out the best methods for instrumenting target…
 vivianuba/grandstream-cve-2026-2329-analysis
Defensive vulnerability-research project comparing vulnerable and patched Grandstream GXP1600 firmware for CVE-2026-2329, using SquashFS extraction,…
 gavmor/x86-cpp-reversing-skill
Claude Code skill for reverse-engineering 32-bit little-endian x86 C++ binaries (vtables, RTTI, inheritance recovery)
 gmh5225/gmh5225
LLVM-based security research toolchain: NeverC, a C23 cross-compiler, and NeverD, a binary analysis and decompilation engine that lifts PE, ELF,…
 shcesama/cve-2023-4863-analysis
Educational analysis of CVE-2023-4863 (libwebp heap buffer overflow) with Blue Team detection tools, static WebP scanner, defensive Java validator,…
 yeahhbean/cve-2026-45729
ThorVG NULL pointer dereference via malformed SVG — AFL++ fuzzing writeup
 gardeniawhite/fuzzing
fuzzing with libFuzzer,inlude openssl heartbleed (CVE-2014-0160)
 darioi/droidcarve
Android Reverse Engineering Framework
 halcy0nic/cve-2023-40294-and-cve-2023-40295
Proof of concept for CVE-2023-40294 and CVE-2023-40295
 claesmnyberg/sdc
Self Decrypting Binary Generator
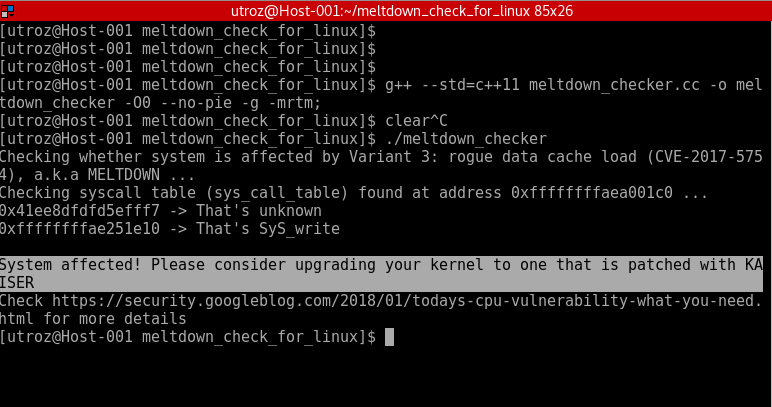 speecyy/am-i-affected-by-meltdown
Proof-of-concept / Exploit / checks whether system is affected by Variant 3: rogue data cache load (CVE-2017-5754), a.k.a
 chenqin231/cve-2026-42945
Local risk assessment script for CVE-2026-42945 (nginx-rift). Checks version, vulnerable rewrite+set config, ASLR status, and compile hardening to…
 sneakynachos/cve-2026-74936-gc-potato
Reproduction of a WebAssembly use-after-free vulnerability in Mozilla's JavaScript engine, demonstrating a deterministic race condition and providing…
 gmh5225/linux-kernel-debugger
Kernel hardware debugger module for dumping rootkit operations and inspecting kernel-level activity for malware analysis and reverse engineering.
 cyhe50/cve-2025-54874-poc
Proof-of-concept demonstrating a memory leak in OpenJPEG 2.5.1 via crafted JP2 files, triggering opj_read_header failure and heap leak, with valgrind…