

scan
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)
binary-analysiscode-analysisdefensive-tools+9
22211h 14m ago
atomdrift-project/scan0-day malware detection for binaries, source & scripts (that doesn't suck)
 gmh5225/awesome-game-security
Curated index of game security research: anti-cheat internals, DMA attacks, reverse engineering, kernel/mobile protections, and graphics API hooking…
 abraxas/sqlite-values-union
SQLite 3.53.4 - High - Local - Crash - VALUES UNION ALL fallback cleanup stack overflow
 lolbas-project/lolbas
Living Off The Land Binaries And Scripts - (LOLBins and LOLScripts)
 0x574r/darkcloak
Linux process identity cloaking tool that spoofs comm, argv, cmdline, environ, exe path, and VMAs via an 11-phase prctl pipeline to impersonate…
 malpedia/malpedia-flossed
FLARE floss applied to all unpacked+dumped samples in Malpedia, pre-processed for further use.
 clearbluejar/ghidrecomp
Python Command-Line Ghidra Decompiler
 kiexitdispatcher/goredops
🦫 | GoRedOps is a repository dedicated to gathering and sharing advanced techniques and offensive malware for Red Team, with a specific focus on…
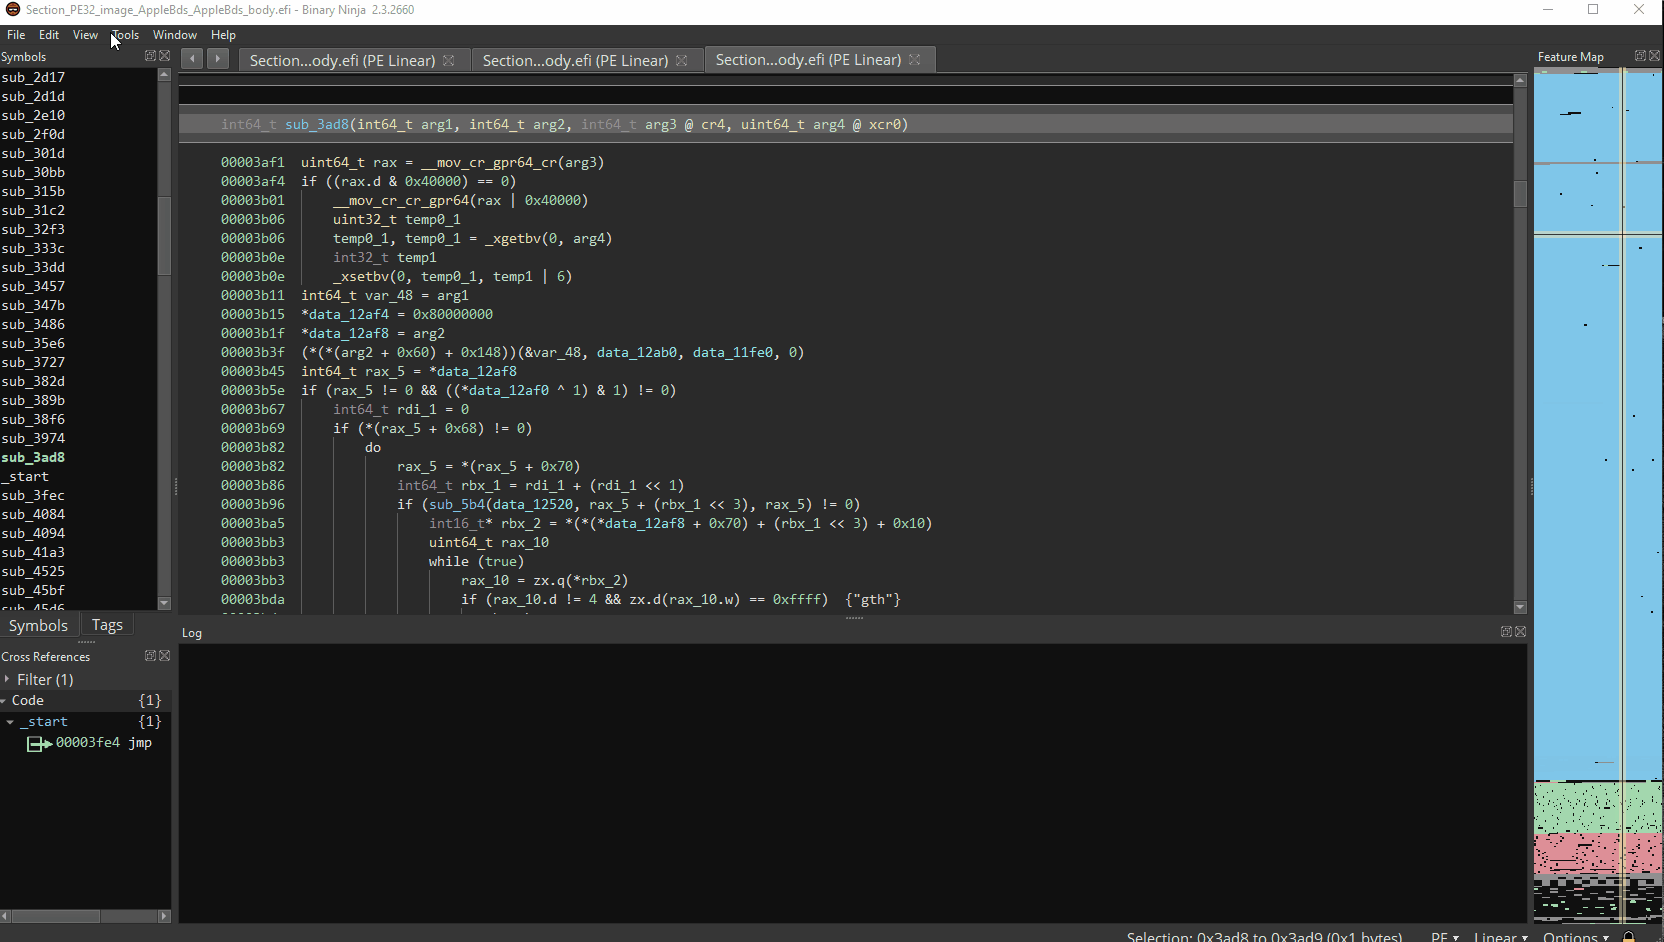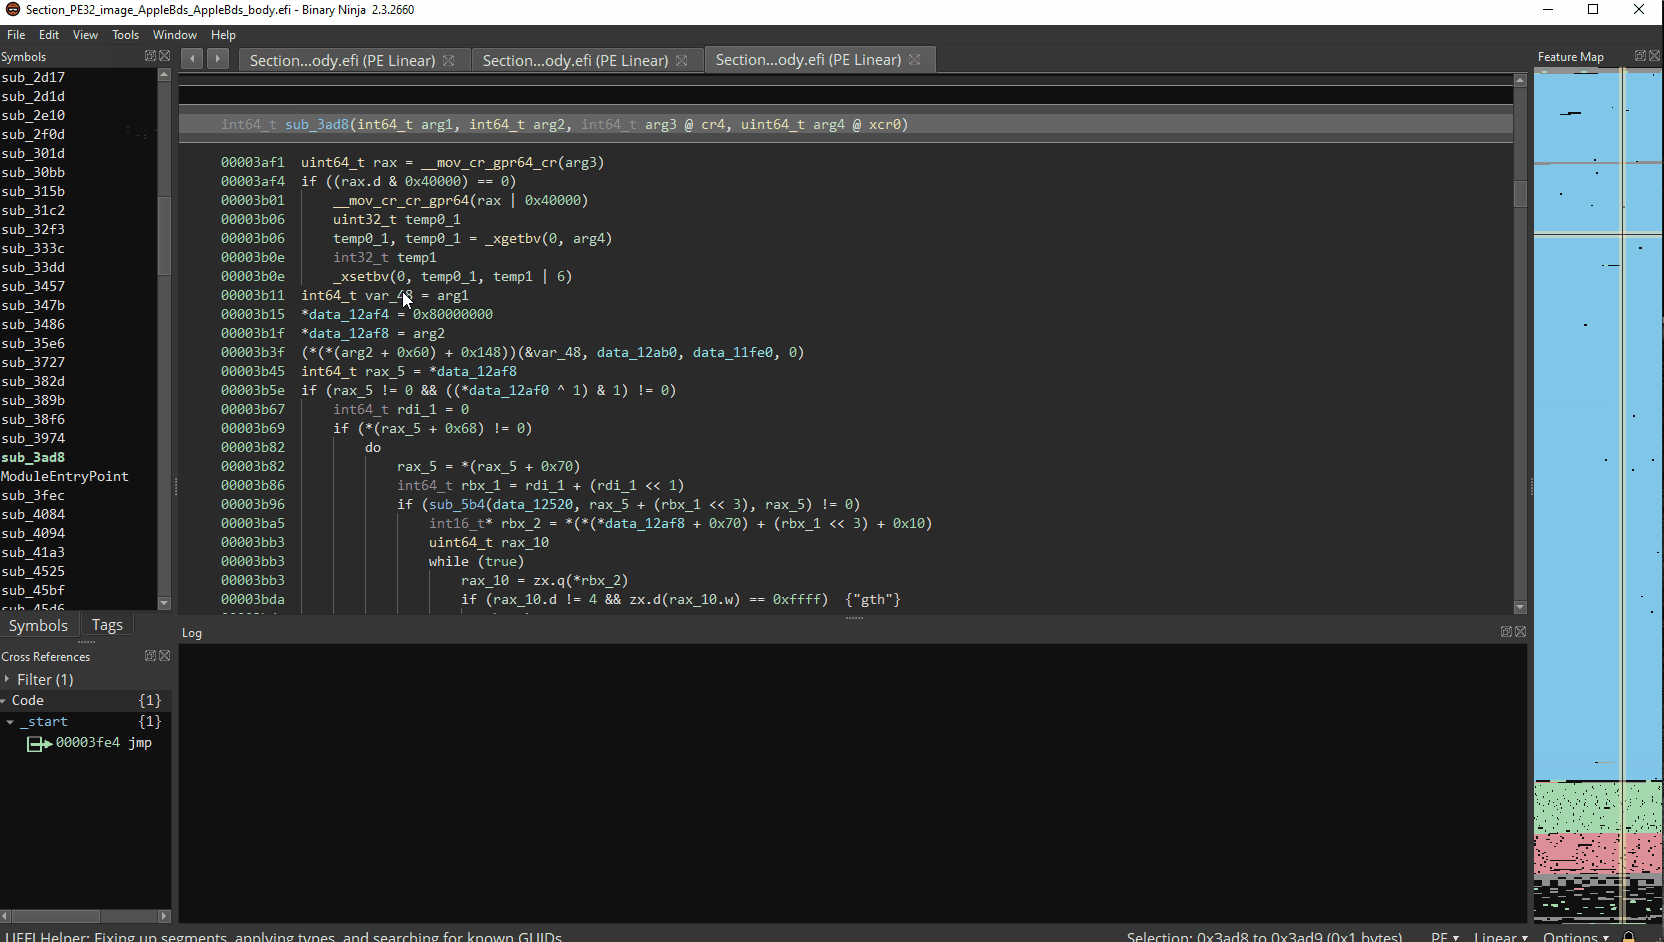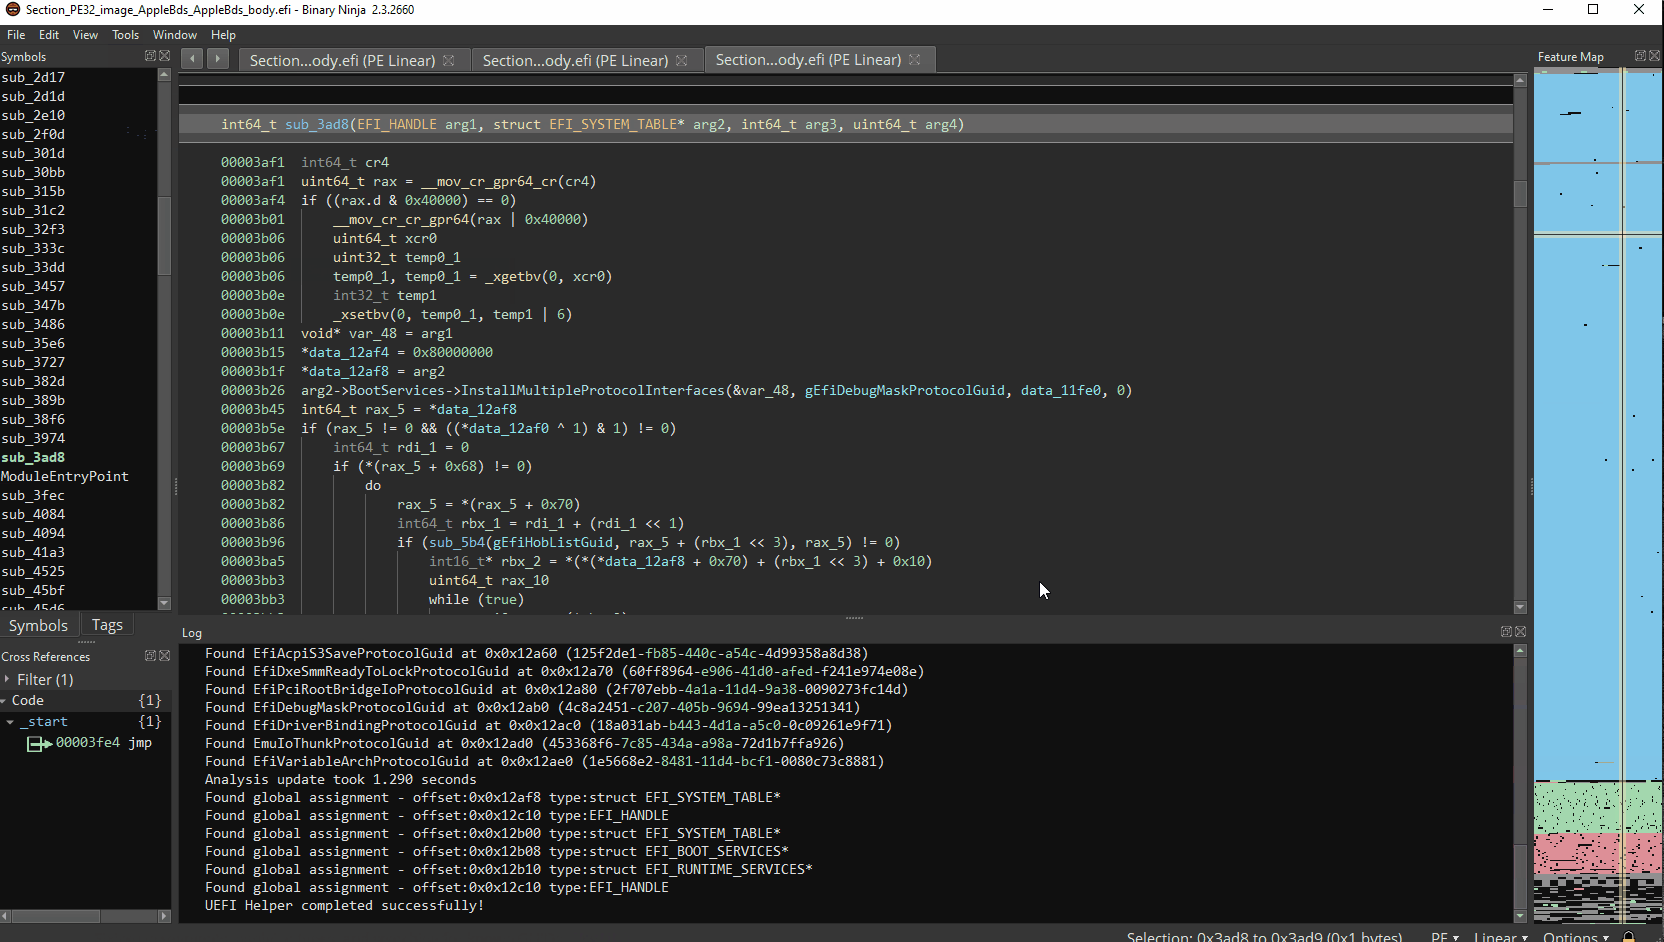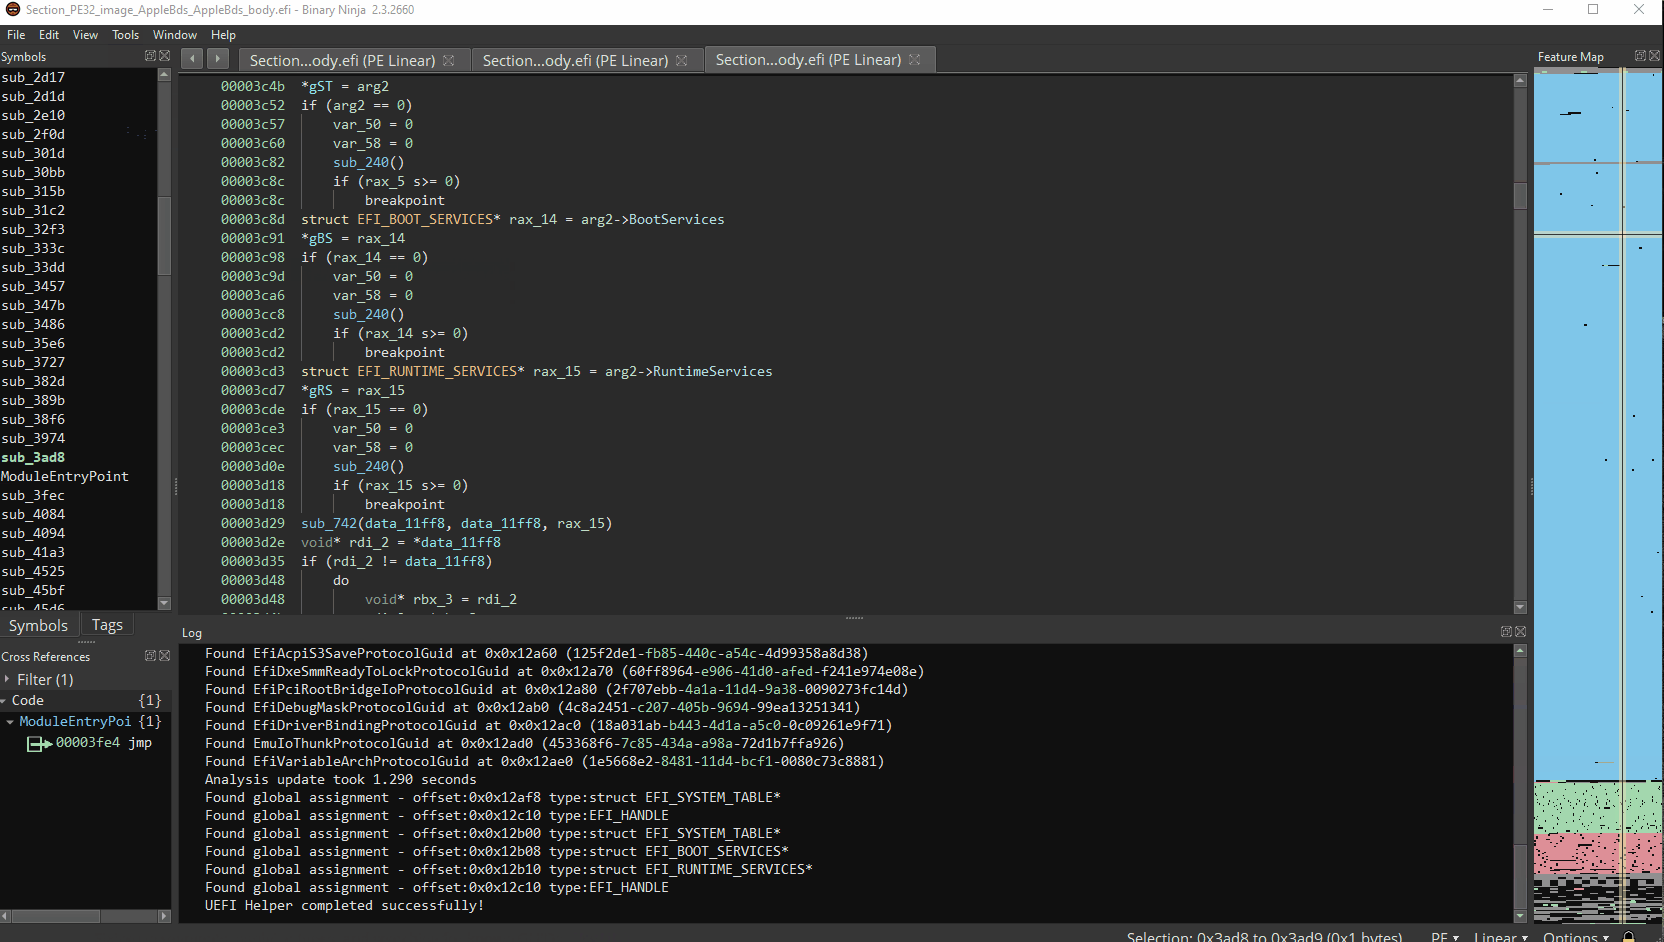 zznop/bn-uefi-helper
Helper plugin for analyzing UEFI firmware
 trailofbits/rpcinvestigator
Windows RPC interface discovery and analysis tool with visual endpoint enumeration, PE parsing, symbol resolution, real-time ETW sniffing, and…
 boku7/bokuloader
A proof-of-concept Cobalt Strike Reflective Loader which aims to recreate, integrate, and enhance Cobalt Strike's evasion features!
 zimawhit3/bitmancer
Nim Library for Offensive Security Development
 airbus-seclab/gustave
GUSTAVE is a fuzzing platform for embedded OS kernels. It is based on QEMU and AFL (and all of its forkserver siblings). It allows to fuzz OS kernels…
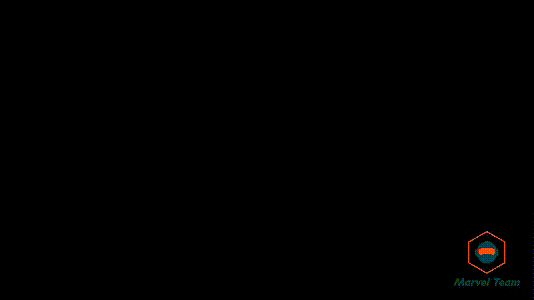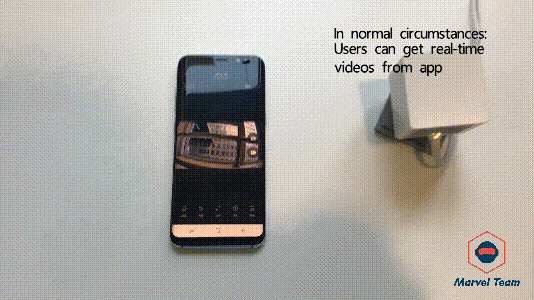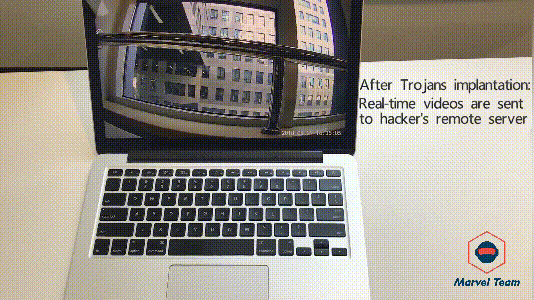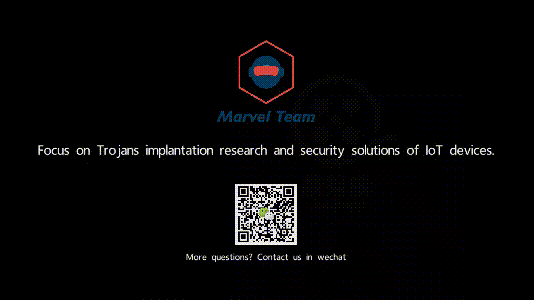 arthastang/iot-implant-toolkit
Toolkit for implant attack of IoT devices