

capstone
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
ai-assisted-reversingbinary-analysisbinary-exploitation+7
9.1k
capstone-engine/capstoneMulti-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 division-36/z-jail
A lightweight, multi-layer Linux sandbox combining namespaces, pivot_root, seccomp-bpf, capability dropping, and an evidence-based verdict engine…
 rr-debugger/rr
Record and replay framework for deterministic debugging of multi-threaded applications, enabling reverse execution, hardware watchpoints, and…
 oscarsantanaarias/ida-ghidra-bridge
TCP JSON bridge servers for IDA Pro and Ghidra exposing decompilation, xrefs, symbols, vtables, RTTI and memory patching to external scripts and…
 googleprojectzero/tinyinst
A lightweight dynamic instrumentation library
 keystone-engine/keystone
Multi-architecture assembler framework that converts assembly source into machine code for Arm, x86, MIPS, PowerPC, RISC-V, and more, with a…
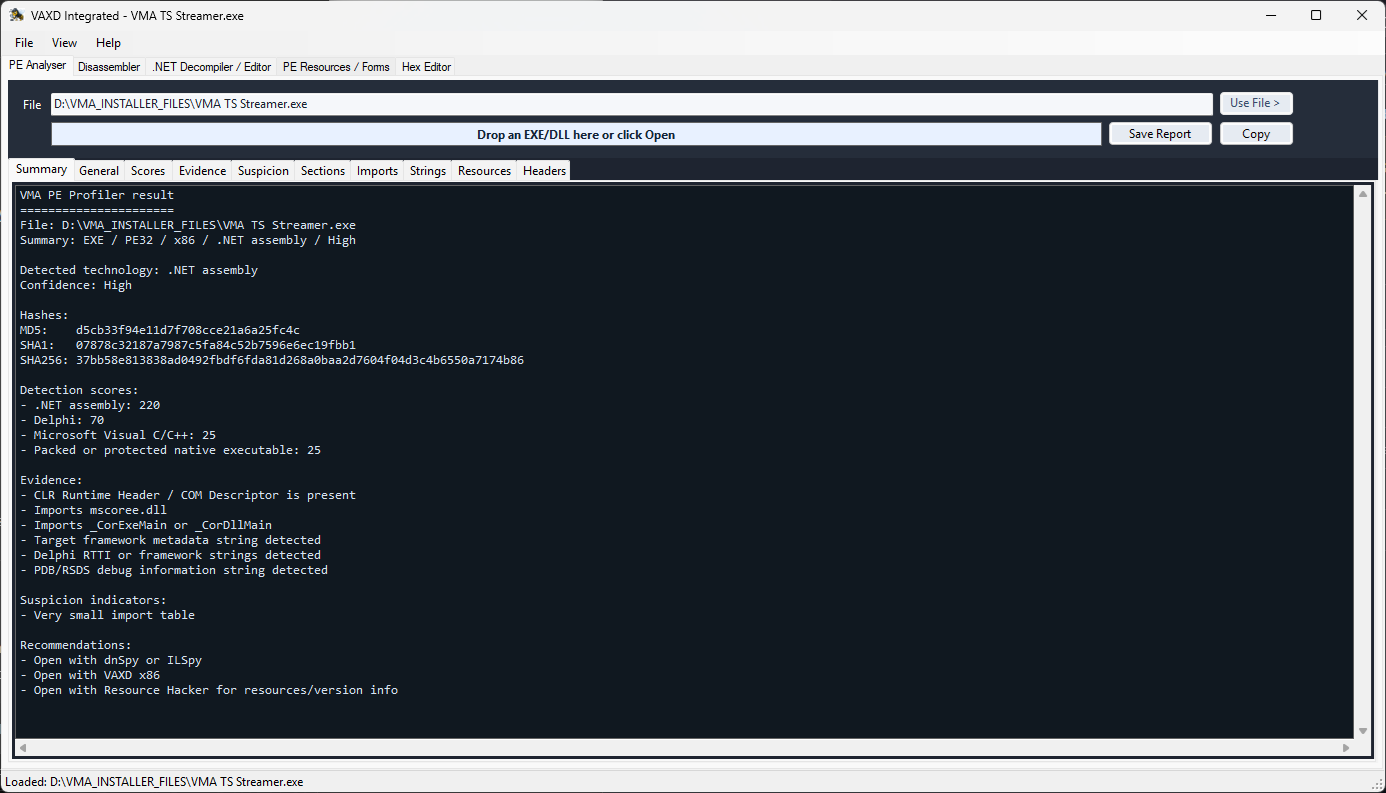 bicurico/vaxd
Lightweight Windows disassembler, PE inspection and patch-assistance tool for native EXE/DLL files.
 euva-project/euva
A lightweight hex editor and decompiler to solve your binary file analysis problems.
 fatmike-gh/mcpdebugger
A MCP Debugger Server for Windows executables (x86 and x64). Exposes debugger functionality as MCP Tools for static / dynamic analysis of the…
 unicorn-engine/unicorn
Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)
 lfi-project/lfi
Top-level repository for LFI: Practical, Efficient, and Secure Software-based Sandboxing
 adem-hosni/mappedimagesdetector
Lightweight native Windows memory scanner for AV/EDR platforms, detecting suspicious mapped images and manual DLL injection techniques by IAT thunk
 renukaselvar/lua_cve-2020-24370_afterpatch
Lightweight embeddable scripting language with a C API, supporting procedural, functional, and data-driven programming.
 renukaselvar/lua_cve-2020-24370
Lightweight, embeddable scripting language with a fast interpreter, supporting procedural, functional, and object-oriented programming.
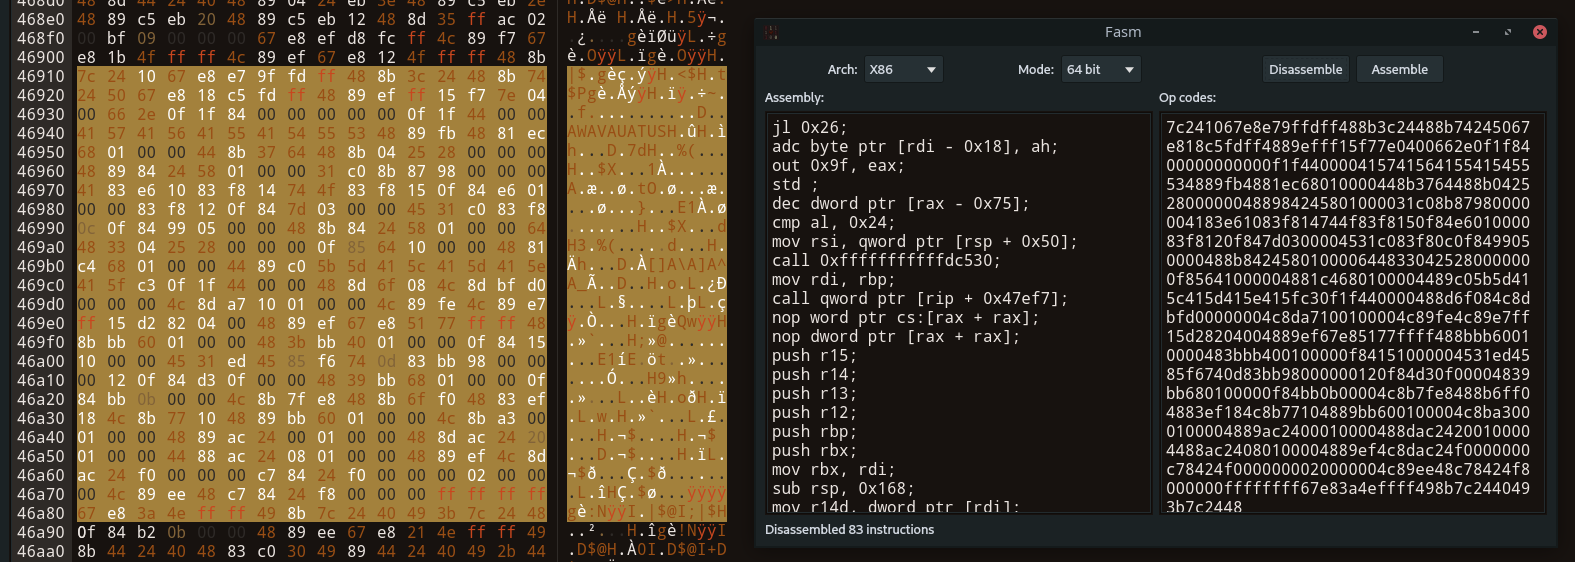 echo-devim/fhex
A Full-Featured HexEditor compatible with Linux/Windows/MacOS
 jasondrawdy/memorymapper
Lightweight library which allows the ability to map both native and managed assemblies into memory by either using process injection of a process…
 0xm3r/cgpwn
A lightweight VM for hardware hacking, RE (fuzzing, symEx, exploiting etc) and wargaming tasks